Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Reddit, X et contributions
Index sélectionnés
Listes et tendances
Trier et sélectionner
Classification
Enrichissement
Traduction
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
v1.0.1 owner/tool
Découvrez les actifs et
vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k

Outils

ToutSécurité AndroidAuthentification et AutorisationSécurité de l'Infrastructure CloudOutils DéfensifsCriminalistique DisqueSécurité des Systèmes EmbarquésUtilitaires GénérauxGestion des Indicateurs de Compromission (IOC)OSINT (Renseignement de Sources Ouvertes)Sniffing et Analyse de PaquetsCassage de Mots de PasseFrameworks de Tests d'IntrusionOutils de PhishingEscalade de PrivilègesReconnaissanceAnalyse StatiqueScanners de VulnérabilitésScanners de Vulnérabilités WebAudit Wi-FiSécurité BluetoothSécurité des ConteneursAnalyse Dynamique (Sandboxing)Outils de Chiffrement/DéchiffrementFrameworks d'ExploitationGestion des IdentitésSécurité iOSSécurité IoTCriminalistique MémoireCartographie RéseauOSINT pour l'Ingénierie SocialeAttaques de Mots de PasseGénération de PayloadsMécanismes de PersistanceScan de PortsAnalyse Statique de Code (SAST)Flux et Agrégateurs de MenacesAnalyse des VulnérabilitésProxies Web et InterceptionAnalyse de CodeÉnumération DNS et Sous-domaineAnalyse Dynamique de Code (DAST)ExploitationAnalyse de HachageÉvasion IDS/IPSOutils d'ImpersonationMouvement LatéralPentesting d'Applications MobilesCriminalistique RéseauRétro-ingénierieOutils RFID/NFCSécurité SCADA/ICSScripting et AutomatisationSécurité ServerlessShellcodeExploitation d'Applications WebTests de Sécurité des APIAudit de ConfigurationExfiltration de DonnéesDébogueursAnalyse ForensiqueCollecte d'InformationsCriminalistique MobileContrôle d'Accès RéseauPost-ExploitationVirtualisation de SécuritéHameçonnageContournement de WAFSécurité WebFuzzingSécurité RéseauStéganographieSécurité Sans FilRécupération de DonnéesAnalyse de MalwareCriminalistique NumériqueHacking MatérielCryptographieCTFTests d'IntrusionSécurité CloudDevSecOpsSécurité MobileProtection de la Vie PrivéeCommandement et ContrôleIngénierie SocialeSécurité MatérielleUtilitaires et FrameworksSécurité Matériel et IoTDétection de SecretsAnalyse de BinairesRenseignement sur les MenacesGestion des Identités et des Accès (IAM)Sécurité de la Chaîne LogistiqueAuthentificationApprentissage AutomatiqueDétection d'IntrusionArticles et RechercheMauvaise ConfigurationÉnumération de Sous-domainesCollecte d'EmailsApprentissage et ÉducationRétro-Ingénierie Assistée par IAFuzzing DNSRed TeamingRéponse aux IncidentsCrawlerRessources OrganiséesOutil d'Accès à DistanceGénération de ShellcodeDéveloppement de Charges UtilesCheval de Troie d'Accès à DistanceSécurité des APIAnti-BotUsurpation d'Empreinte NumériqueContournement de CAPTCHASécurité des EmailsAnalyse DNSIngénierie du ChaosParcours et CoursÉvasion de ConteneurSécurité de l'IASécurité des Bases de DonnéesAnalyse de MicrologicielDétection d'AnomaliesAnalyse de JournauxAttaque AdversarialeExploitation de BinairesLabs et Pratique
Plus récentsPertinencePlus populairesMis à jour récemment
598 résultats
Research_Successful_Errors preview

Research_Successful_Errors

GitHubvladko312/research_successful_errors

Livre blanc présentant les techniques aveugles basées sur les erreurs et booléennes pour SSTI et l'injection de code, avec des payloads universels…

vulnerability-analysiscode-analysisweb-application-exploitation+6
121
il y a 9 mois
tetsuo-pulse preview

tetsuo-pulse

GitHub7etsuo/tetsuo-pulse

Tetsuo Socket Library

packet-sniffing-analysisencryption-decryption-toolsweb-security+6
72il y a 9 mois
maps_scanner preview

maps_scanner

GitHubhackinglz/maps_scanner

MAPS - scanner cloud et analyseur de réponses pour la recherche sur Microsoft Defender.

reconnaissancedynamic-analysis-sandboxingvulnerability-analysis+6
94il y a 9 mois
unicorn preview

unicorn

GitHubunicorn-engine/unicorn

Framework d'émulateur CPU Unicorn (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)

embedded-systems-securityreverse-engineeringdebuggers+7
9.2kil y a 9 mois
restler-fuzzer preview

restler-fuzzer

GitHubmicrosoft/restler-fuzzer

RESTler est le premier outil de fuzzing d'API REST stateful pour tester automatiquement les services cloud via leurs API REST et trouver des bugs de…

vulnerability-scannersapi-security-testingweb-security+2
2.9kil y a 9 mois
clusterfuzzlite preview

clusterfuzzlite

GitHubgoogle/clusterfuzzlite

Solution de fuzzing continue intégrée dans les workflows d'intégration continue (CI) pour trouver des vulnérabilités dans les modifications de code…

vulnerability-analysisfuzzingdevsecops
531il y a 9 mois
cook preview

cook

GitHubglitchedgitz/cook

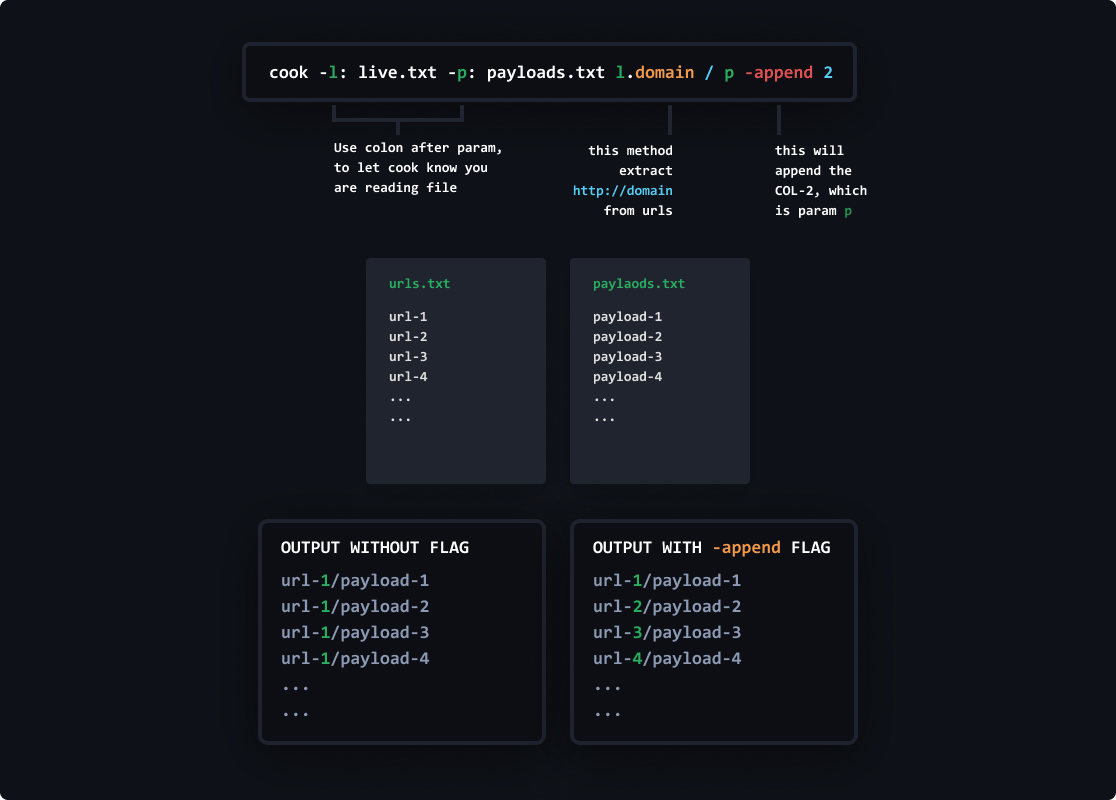
Un framework de wordlists pour satisfaire vos envies avec vos wordlists. Pour les chercheurs en sécurité, chasseurs de bugs et hackers.

password-crackingfuzzingpenetration-testing+1
1.4kil y a 9 mois
anamnesis-release preview

anamnesis-release

GitHubseanheelan/anamnesis-release

Cadre d'évaluation pour étudier les agents LLM qui génèrent automatiquement des exploits fonctionnels à partir de rapports de vulnérabilité,…

penetration-testing-frameworksexploit-frameworksvulnerability-analysis+9
628il y a 9 mois
fuzzbench preview

fuzzbench

GitHubgoogle/fuzzbench

FuzzBench - Benchmarking de fuzzers en tant que service.

vulnerability-analysisfuzzingeducation
1.2kil y a 9 mois
OmniScan preview

OmniScan

GitHubd3ckx1/omniscan

Scanner de vulnérabilités multi-moteur avec les moteurs intégrés Nuclei Lite, Afrog et XRay. Fonctionnalités de découverte d'actifs via FOFA/Shodan,…

osintreconnaissancevulnerability-scanners+6
9il y a 10 mois
BypassFuzzer preview
Archived

BypassFuzzer

GitHubintrudir/bypassfuzzer

Fuzzer les pages 401/403/404 pour trouver des contournements

vulnerability-scannersids-ips-evasionweb-application-exploitation+3
430il y a 10 mois
wfuzz preview

wfuzz

GitHubxmendez/wfuzz

Fuzzer web modulaire pour les tests de sécurité automatisés. Injecte des charges utiles dans n'importe quel champ de requête HTTP pour découvrir des…

web-vulnerability-scannersvulnerability-analysisweb-security+2
6.5kil y a 10 mois
ClaimJumper preview

ClaimJumper

GitHubfevra-dev/claimjumper

Kit de test professionnel de sécurité JWT. Analysez, craquez, forgez et exploitez les jetons Web JSON avec plus de 15 vérifications de…

password-crackingvulnerability-scannersexploitation+6
1il y a 10 mois
rep-chrome preview

rep-chrome

GitHubrepplus/rep-chrome

rep+ — Burp-style HTTP Repeater pour Chrome DevTools avec IA intégrée pour expliquer les requêtes et suggérer des attaques

vulnerability-scannersweb-proxies-interceptionapi-security-testing+6
1.6kil y a 10 mois
C-Game-Modding-Utility preview

C-Game-Modding-Utility

GitHubc0mposer/c-game-modding-utility

Un utilitaire de modding de jeu qui facilite l'injection de code C/C++.

embedded-systems-securityreverse-engineeringdebuggers+5
67il y a 10 mois
gobuster preview

gobuster

GitHuboj/gobuster

Outil de busting de répertoires/fichiers, DNS et VHost écrit en Go

dns-subdomain-enumerationinformation-gatheringweb-security+3
14.0kil y a 10 mois
feroxfuzz preview

feroxfuzz

GitHubepi052/feroxfuzz

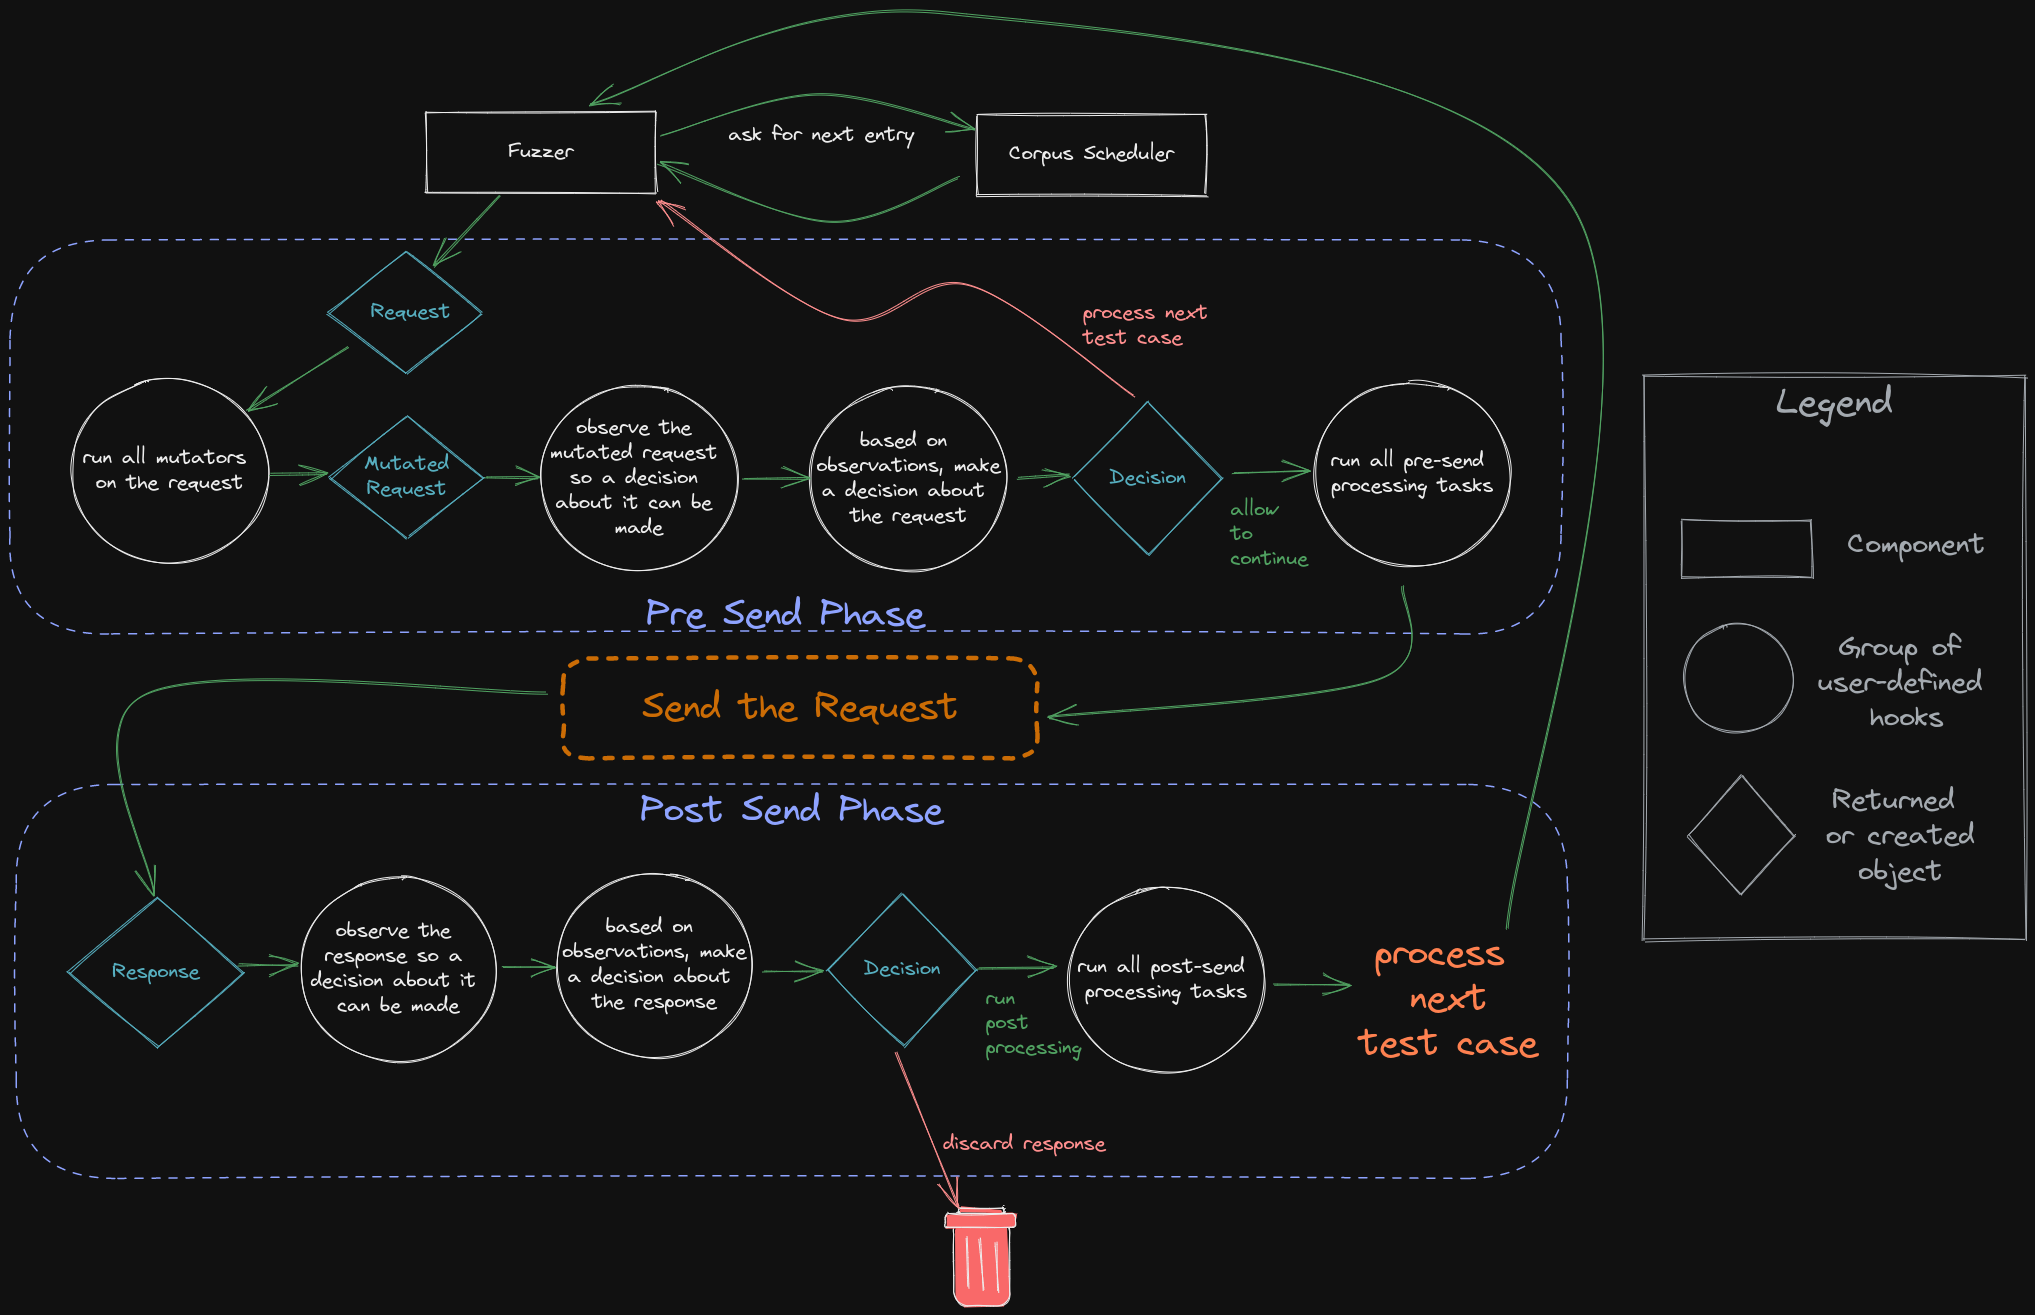
Développez des fuzzers HTTP black-box conscients de la structure en Rust, avec des mutateurs, planificateurs, observateurs, décideurs et processeurs…

api-security-testingweb-securityfuzzing+1
223il y a 10 mois
wordlist.rb preview

wordlist.rb

GitHubpostmodern/wordlist.rb

Une bibliothèque Ruby et un CLI pour générer et travailler avec des listes de mots.

password-attacksfuzzingpenetration-testing+1
48il y a 10 mois
Précédent1…131415…34Suivant
Des sources sélectionnées à une fiche d’outil Dépôts, flux, communautés et index passent par la sélection, la classification, l’enrichissement et la traduction pour former une fiche d’outil illustrative. ISC License Copyright (c) 2026 Lucide Icons and Contributors Permission to use, copy, modify, and/or distribute this software for any purpose with or without fee is hereby granted, provided that the above copyright notice and this permission notice appear in all copies. THE SOFTWARE IS PROVIDED "AS IS" AND THE AUTHOR DISCLAIMS ALL WARRANTIES WITH REGARD TO THIS SOFTWARE INCLUDING ALL IMPLIED WARRANTIES OF MERCHANTABILITY AND FITNESS. IN NO EVENT SHALL THE AUTHOR BE LIABLE FOR ANY SPECIAL, DIRECT, INDIRECT, OR CONSEQUENTIAL DAMAGES OR ANY DAMAGES WHATSOEVER RESULTING FROM LOSS OF USE, DATA OR PROFITS, WHETHER IN AN ACTION OF CONTRACT, NEGLIGENCE OR OTHER TORTIOUS ACTION, ARISING OUT OF OR IN CONNECTION WITH THE USE OR PERFORMANCE OF THIS SOFTWARE. --- The following Lucide icons are derived from the Feather project: airplay, alert-circle, alert-octagon, alert-triangle, aperture, arrow-down-circle, arrow-down-left, arrow-down-right, arrow-down, arrow-left-circle, arrow-left, arrow-right-circle, arrow-right, arrow-up-circle, arrow-up-left, arrow-up-right, arrow-up, at-sign, calendar, cast, check, chevron-down, chevron-left, chevron-right, chevron-up, chevrons-down, chevrons-left, chevrons-right, chevrons-up, circle, clipboard, clock, code, columns, command, compass, corner-down-left, corner-down-right, corner-left-down, corner-left-up, corner-right-down, corner-right-up, corner-up-left, corner-up-right, crosshair, database, divide-circle, divide-square, dollar-sign, download, external-link, feather, frown, hash, headphones, help-circle, info, italic, key, layout, life-buoy, link-2, link, loader, lock, log-in, log-out, maximize, meh, minimize, minimize-2, minus-circle, minus-square, minus, monitor, moon, more-horizontal, more-vertical, move, music, navigation-2, navigation, octagon, pause-circle, percent, plus-circle, plus-square, plus, power, radio, rss, search, server, share, shopping-bag, sidebar, smartphone, smile, square, table-2, tablet, target, terminal, trash-2, trash, triangle, tv, type, upload, x-circle, x-octagon, x-square, x, zoom-in, zoom-out The MIT License (MIT) (for the icons listed above) Copyright (c) 2013-present Cole Bemis Permission is hereby granted, free of charge, to any person obtaining a copy of this software and associated documentation files (the "Software"), to deal in the Software without restriction, including without limitation the rights to use, copy, modify, merge, publish, distribute, sublicense, and/or sell copies of the Software, and to permit persons to whom the Software is furnished to do so, subject to the following conditions: The above copyright notice and this permission notice shall be included in all copies or substantial portions of the Software. THE SOFTWARE IS PROVIDED "AS IS", WITHOUT WARRANTY OF ANY KIND, EXPRESS OR IMPLIED, INCLUDING BUT NOT LIMITED TO THE WARRANTIES OF MERCHANTABILITY, FITNESS FOR A PARTICULAR PURPOSE AND NONINFRINGEMENT. IN NO EVENT SHALL THE AUTHORS OR COPYRIGHT HOLDERS BE LIABLE FOR ANY CLAIM, DAMAGES OR OTHER LIABILITY, WHETHER IN AN ACTION OF CONTRACT, TORT OR OTHERWISE, ARISING FROM, OUT OF OR IN CONNECTION WITH THE SOFTWARE OR THE USE OR OTHER DEALINGS IN THE SOFTWARE.
Dépôts
GitHub & GitLab
Veille sécurité
Blogs, RSS et Atom
Communautés
Réseaux et contributions
Index sélectionnés
Listes et tendances
Trier et classer
Enrichir et traduire
Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. Outil et dépôt fictifs. Description, catégories, étoiles, forks et vues sont des exemples, pas des données réelles ou vérifiées. {"fictional":true,"name":"Tool","version":"1.0.1","repository":"owner/tool","live_metrics":false,"example_metrics":{"stars":1200,"forks":128,"views":8600}}
Outil
owner/tool v1.0.1
Découvrez les actifs et vérifiez les en-têtes HTTP.
Reconnaissance
Sécurité web
1,200 étoiles — Exemple fictif1.2k 128 forks — Exemple fictif128 8,600 vues — Exemple fictif8.6k