 pr0fes0r-x/php2shell-checker-v-2.0-cve-2026-115560-
Version 2.0 — ajoute un balayage des hôtes distants via HTTP à la v1.0. Lorsqu'il est exécuté sans arguments, il affiche un menu interactif.





Envoie un HTTP HEAD à l'hôte et lit les en-têtes X-Powered-By: PHP/x.y.z ou Server: ... PHP/x.y.z ... pour détecter la version à distance. Repli automatique HTTP → HTTPS si le premier échoue.
python3 php2shell_check_v2.0.py --host ejemplo.com
python3 php2shell_check_v2.0.py --host ejemplo.com --https --port 8443
Analyse une liste d'IP/noms d'hôtes et affiche un rapport consolidé avec les vulnérables mis en évidence.
python3 php2shell_check_v2.0.py --hosts 192.168.1.10 192.168.1.11 srv-web-01.local
Lit une liste d'hôtes depuis un fichier texte (un par ligne, # pour les commentaires).
python3 php2shell_check_v2.0.py --scan hosts.txt
python3 php2shell_check_v2.0.py --scan hosts.txt --https --port 8443
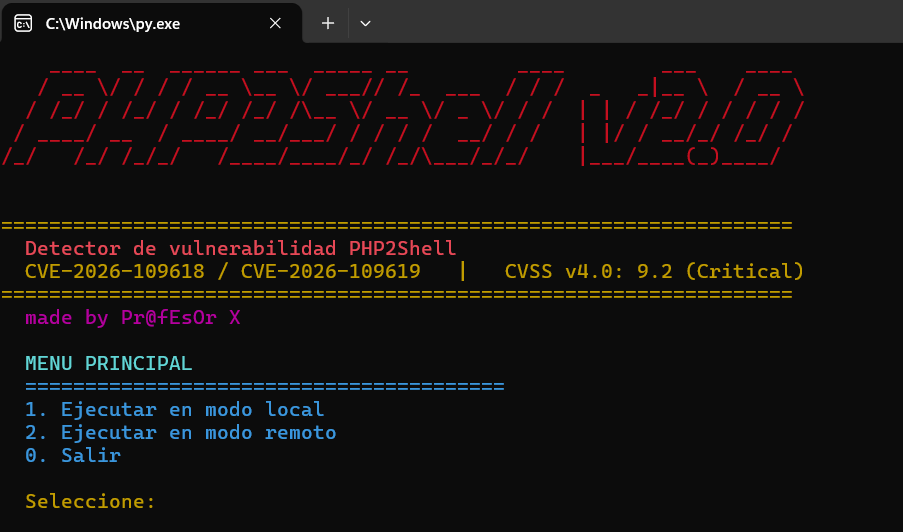
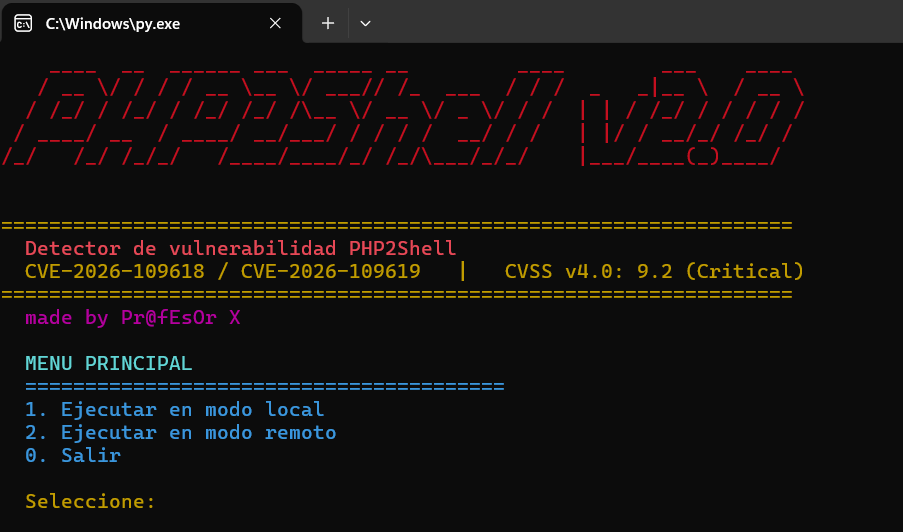
Si vous exécutez le script sans arguments, un menu s'ouvre :
python3 php2shell_check_v2.0.py
  MENU PRINCIPAL
  ========================================
  1. Ejecutar en modo local
  2. Ejecutar en modo remoto
  0. Salir
Pr@fEsOr X
Licence MIT — voir ../LICENSE.