
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Catégories

Rétro-ingénierie

Outils pour la décompilation, le désassemblage et la compréhension des mécanismes internes des malwares et des binaires complexes.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
ghidra preview#1

ghidra

GitHubnationalsecurityagency/ghidra
71.1kil y a 4h 59m
radare2 preview#2

radare2

GitHubradareorg/radare2
24.5kil y a 14h 17m
cutter preview#3

cutter

GitHubrizinorg/cutter
19.4kil y a 1 jour
rizin preview#4

rizin

GitHubrizinorg/rizin
4.1kil y a 6h 41m
x64dbg preview#5

x64dbg

GitHubx64dbg/x64dbg
49.1kil y a 7 jours
ImHex preview#6

ImHex

GitHubwerwolv/imhex
54.4kil y a 28 jours
angr preview#7

angr

GitHubangr/angr
9.0kil y a 6h 23m
unicorn preview#8

unicorn

GitHubunicorn-engine/unicorn
9.2kil y a 8 mois
capstone preview#9

capstone

GitHubcapstone-engine/capstone
8.9kil y a 0 jours
keystone preview#10

keystone

GitHubkeystone-engine/keystone
2.7kil y a 3 mois
Plus récentsPertinencePlus populairesMis à jour récemment
1868 résultats
archivo-syxe05-snat preview

archivo-syxe05-snat

GitHubshow0ne/archivo-syxe05-snat

Archive historique de tutoriels de rétro-ingénierie et de dépaquetage couvrant les protecteurs commerciaux (Armadillo, ASProtect, Themida) avec des…
reverse-engineeringdebuggersmalware-analysis+3
29il y a 7 mois
ghidra_stack_strings preview

ghidra_stack_strings

GitHubzxgio/ghidra_stack_strings

Un script permettant de détecter les stack-strings grâce à l'émulation (en s'appuyant sur Unicorn)
dynamic-code-analysisreverse-engineeringmalware-analysis+1
35il y a 11 mois
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Analyse de rétro-ingénierie du RAT PureRAT abusant de msbuild.exe, extraction de l'infrastructure C2, des API d'évasion .NET, de la manipulation du…
defensive-toolsdynamic-analysis-sandboxingpersistence-mechanisms+6
19il y a 1 mois
AIDebug preview

AIDebug

GitHubanpa1200/aidebug

Analyse de logiciels malveillants axée sur les preuves avec inspection approfondie des PE/.NET, reconstruction Ghidra, vérifications croisées par IA,…

static-analysisdynamic-analysis-sandboxingreverse-engineering+7
15il y a 27 jours
copy-as-yara preview

copy-as-yara

GitHubald3ns/copy-as-yara

Ceci est un petit plugin pour copier le désassemblage d'une manière utilisable dans les règles YARA !
static-analysisreverse-engineeringmalware-analysis+1
48il y a 1 an
CVE-2020-1054 preview

CVE-2020-1054

GitHubkalendsi/cve-2020-1054

Analyse et code de preuve de concept pour CVE-2020-1054, une vulnérabilité d'élévation de privilèges du noyau Windows, avec un article technique lié.
vulnerability-analysisexploitationreverse-engineering+1
20il y a 6 ans
Elfina preview

Elfina

GitHubiss4cf0ng/elfina

Chargeur ELF multi-architecture et boîte à outils d'analyse avec sondage, désassemblage, hexdump, calcul d'entropie, et exécution mmap/memfd pour les…
reverse-engineeringdebuggersmalware-analysis+3
52il y a 7 mois
Config-Extractors preview

Config-Extractors

GitHubfarghlymal/config-extractors

Extrait et déchiffre les données de configuration des logiciels malveillants à partir d'échantillons capturés, automatisant la découverte des points…

encryption-decryption-toolsreverse-engineeringmalware-analysis+2
27il y a 1 an
mtk-su-reverse-cve-2020-0069 preview

mtk-su-reverse-cve-2020-0069

GitHubtherealjunior/mtk-su-reverse-cve-2020-0069

rétro-ingénierie de mtk-su
android-securityvulnerability-analysisexploitation+3
17il y a 6 ans
CVE-2026-20700 preview

CVE-2026-20700

GitHubr3n3r0/cve-2026-20700

Preuve de concept démontrant dyld comme oracle de signature PAC via des fixups chaînés Mach-O spécialement conçus sur arm64e, permettant des…
vulnerability-analysisexploitationreverse-engineering+8
10il y a 5 mois
pixma preview

pixma

GitHubleecher1337/pixma

Outils d'analyse du firmware des imprimantes Canon Pixma
embedded-systems-securityencryption-decryption-toolsreverse-engineering+3
23il y a 1 an
logitech-ipc-protocol preview

logitech-ipc-protocol

GitHubsaimanish1/logitech-ipc-protocol

Protocole IPC de l'agent Logi Options+ rétro-conçu. Basculer les périphériques multi-hôtes Logitech par programmation via socket Unix (macOS) ou tube…
embedded-systems-securitybluetooth-securityreverse-engineering+5
17il y a 1 mois
hyperhives-macos-infostealer-analysis preview

hyperhives-macos-infostealer-analysis

GitHubdarksp33d/hyperhives-macos-infostealer-analysis

Analyse statique complète du voleur d'informations HyperHives macOS Rust — 571 valeurs de configuration déchiffrées, infrastructure C2, attribution…
ioc-managementosintreverse-engineering+6
31il y a 7 mois
WHFB-PinCapture preview

WHFB-PinCapture

GitHubivancabrera02/whfb-pincapture

Capture les codes PIN Windows Hello à la saisie en injectant une DLL dans LogonUI.exe qui place un point d'arrêt matériel CPU sur…
privilege-escalationmemory-forensicspassword-attacks+5
10il y a 19 jours
ABrake27 preview

ABrake27

GitHubvvirei333/abrake27

iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow.
ios-securityvulnerability-analysisexploitation+8
10il y a 19h 55m
CVE-2020-0022 preview

CVE-2020-0022

GitHubthemmokhtar/cve-2020-0022

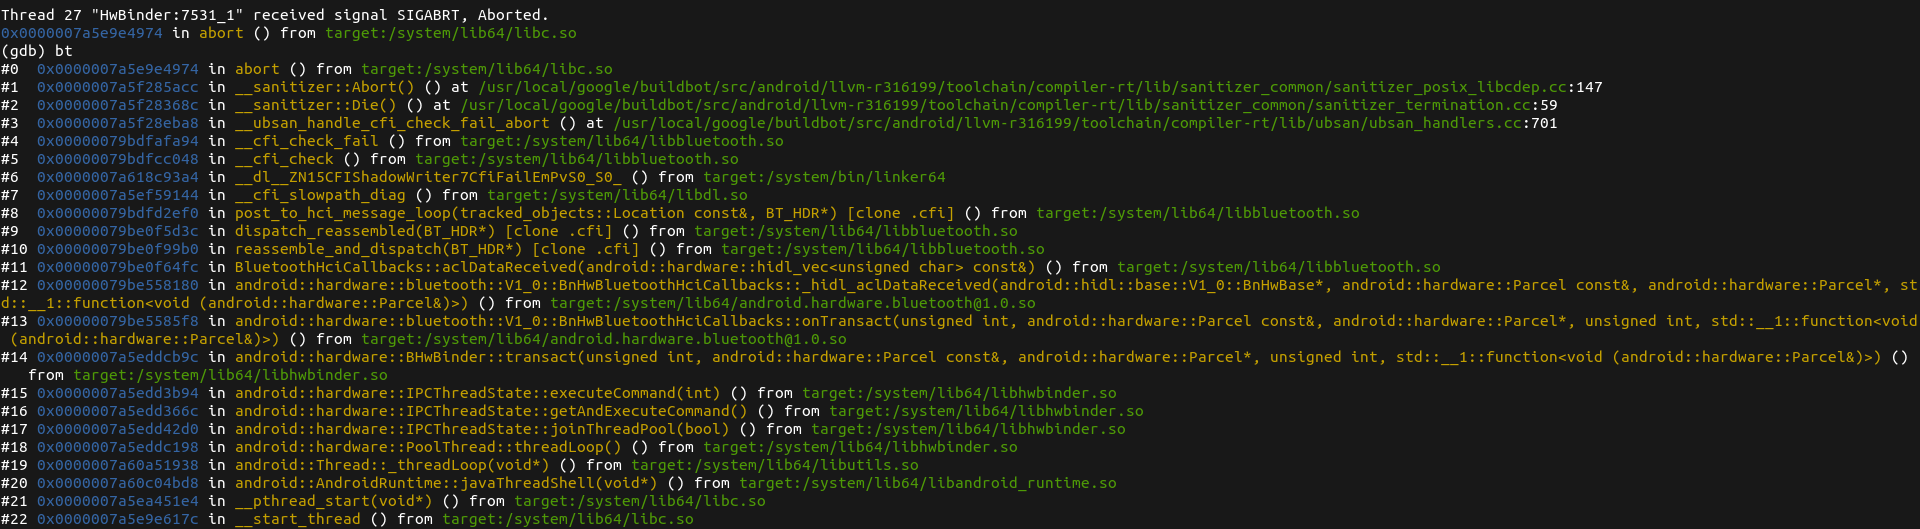
Un exploit entièrement public de la vulnérabilité RCE Android CVE-2020-0022 BlueFrag (testé sur Pixel 3 XL)
android-securitybluetooth-securityexploit-frameworks+7
22il y a 2 ans
bochscpu-python preview

bochscpu-python

GitHubhugsy/bochscpu-python

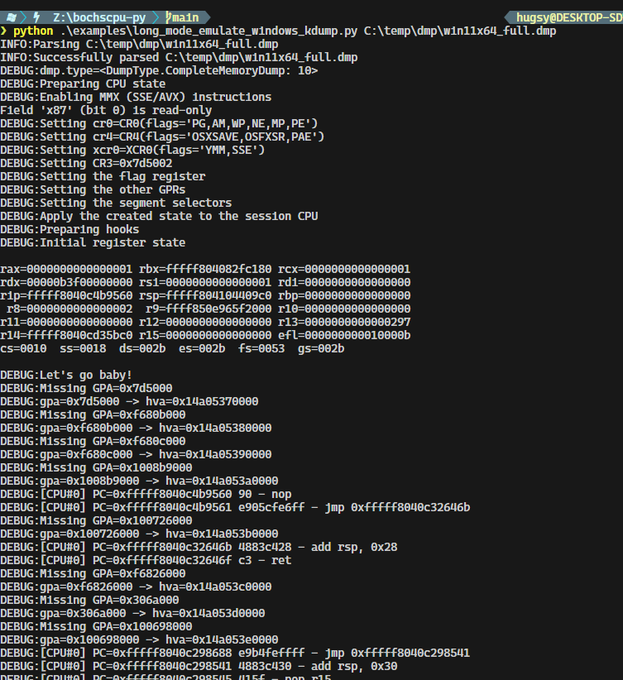
Bindings Python pour BochsCPU

dynamic-analysis-sandboxingreverse-engineeringmalware-analysis+1
39il y a 1 an
apiscope preview

apiscope

GitHubkaisonox/apiscope

Un framework de hooking d'API pour intercepter et surveiller les applications Windows

dynamic-analysis-sandboxingdynamic-code-analysisreverse-engineering+4
20il y a 4 mois
Précédent1…626364…100Suivant








