
Skip to content
KitploitKITPLOIT
OutilsExploitsBlog
Log in
Soumettre
OutilsExploitsBlog
Soumettre

Outils de Hacking, PenTest et Cybersécurité pour votre Arsenal de Sécurité !

Kitploit est un répertoire d'outils de hacking, de cybersécurité et de pentesting. Découvrez les dernières mises à jour des projets pour trouver des vulnérabilités, analyser des systèmes, automatiser les tests et renforcer votre sécurité.

FluxContactConfidentialité© 2026 Kitploit

Répertoire d'outils

Catégories

Voir toutes les catégories
Loading categories
Analyse Dynamique (Sandboxing) — Page 37 | Kitploit
Catégories

Analyse Dynamique (Sandboxing)

Outils pour l'observation du comportement des logiciels malveillants dans des environnements isolés afin de comprendre leurs actions et leur impact.

Recommandé par Kitploit
Meilleurs outils

10 sélectionnés
cuckoo3 preview#2

cuckoo3

GitHubcert-ee/cuckoo3
822il y a 10 mois
IntelOwl preview#4

IntelOwl

GitHubintelowlproject/intelowl
4.7kil y a 1 mois
flare-vm preview#5

flare-vm

GitHubmandiant/flare-vm
8.9kil y a 16 jours
distro preview#6

distro

GitHubremnux/distro
119il y a 9 jours
commando-vm preview#7

commando-vm

GitHubmandiant/commando-vm
7.8kil y a 1 an
metasploitable3 preview#8

metasploitable3

GitHubrapid7/metasploitable3
5.7kil y a 1 an
firecracker preview#9

firecracker

GitHubfirecracker-microvm/firecracker
37.6kil y a 1 jour
gvisor preview#10

gvisor

GitHubgoogle/gvisor
19.8kil y a 9h 58m
kata-containers preview#11

kata-containers

GitHubkata-containers/kata-containers
8.5kil y a 10h 31m
yara-x preview#13

yara-x

GitHubvirustotal/yara-x
1.2kil y a 12h 13m
Plus récentsPertinencePlus populairesMis à jour récemment
679 résultats
detux preview

detux

GitHubdetuxsandbox/detux

Le sandbox Linux multiplateforme
dynamic-analysis-sandboxingnetwork-forensicsforensics+1
266il y a 8 ans
bfinject preview

bfinject

GitHubbishopfox/bfinject

Injection de Dylib pour iOS 11.0 - 11.1.2 avec les jailbreaks LiberiOS et Electra
dynamic-analysis-sandboxingios-securityexploitation+3
641il y a 8 ans
psr preview

psr

GitHubnccgroup/psr

Pointer Sequence Reverser - vous permet de voir comment une application Windows C++ accède à un membre de données ou à un objet particulier.
dynamic-analysis-sandboxingreverse-engineeringdebuggers+1
75il y a 8 ans
python-exe-unpacker preview

python-exe-unpacker

GitHubwithsecurelabs/python-exe-unpacker

Un script utilitaire pour dépaqueter et décompiler les EXE compilés à partir de code python.
dynamic-analysis-sandboxingreverse-engineeringforensics+2
1.0kil y a 8 ans
TriforceOpenBSDFuzzer preview

TriforceOpenBSDFuzzer

GitHubnccgroup/triforceopenbsdfuzzer

Fuzzing des appels système d'OpenBSD amd64 à l'aide de TriforceAFL (c.-à-d. AFL et QEMU)
dynamic-analysis-sandboxingvulnerability-analysisfuzzing
47il y a 8 ans
idasec preview

idasec

GitHubrobindavid/idasec

Plugin IDA pour la rétro-ingénierie et les interactions dynamiques avec la plateforme Binsec
dynamic-analysis-sandboxingreverse-engineeringdebuggers+1
117il y a 8 ans
FrisbeeLite preview

FrisbeeLite

GitHubnccgroup/frisbeelite

Un fuzzer de périphériques USB basé sur une interface graphique
embedded-systems-securitydynamic-analysis-sandboxingvulnerability-analysis+2
65il y a 9 ans
bradamsa preview

bradamsa

GitHubikkisoft/bradamsa

Extension Burp Suite pour générer des payloads Intruder avec Radamsa
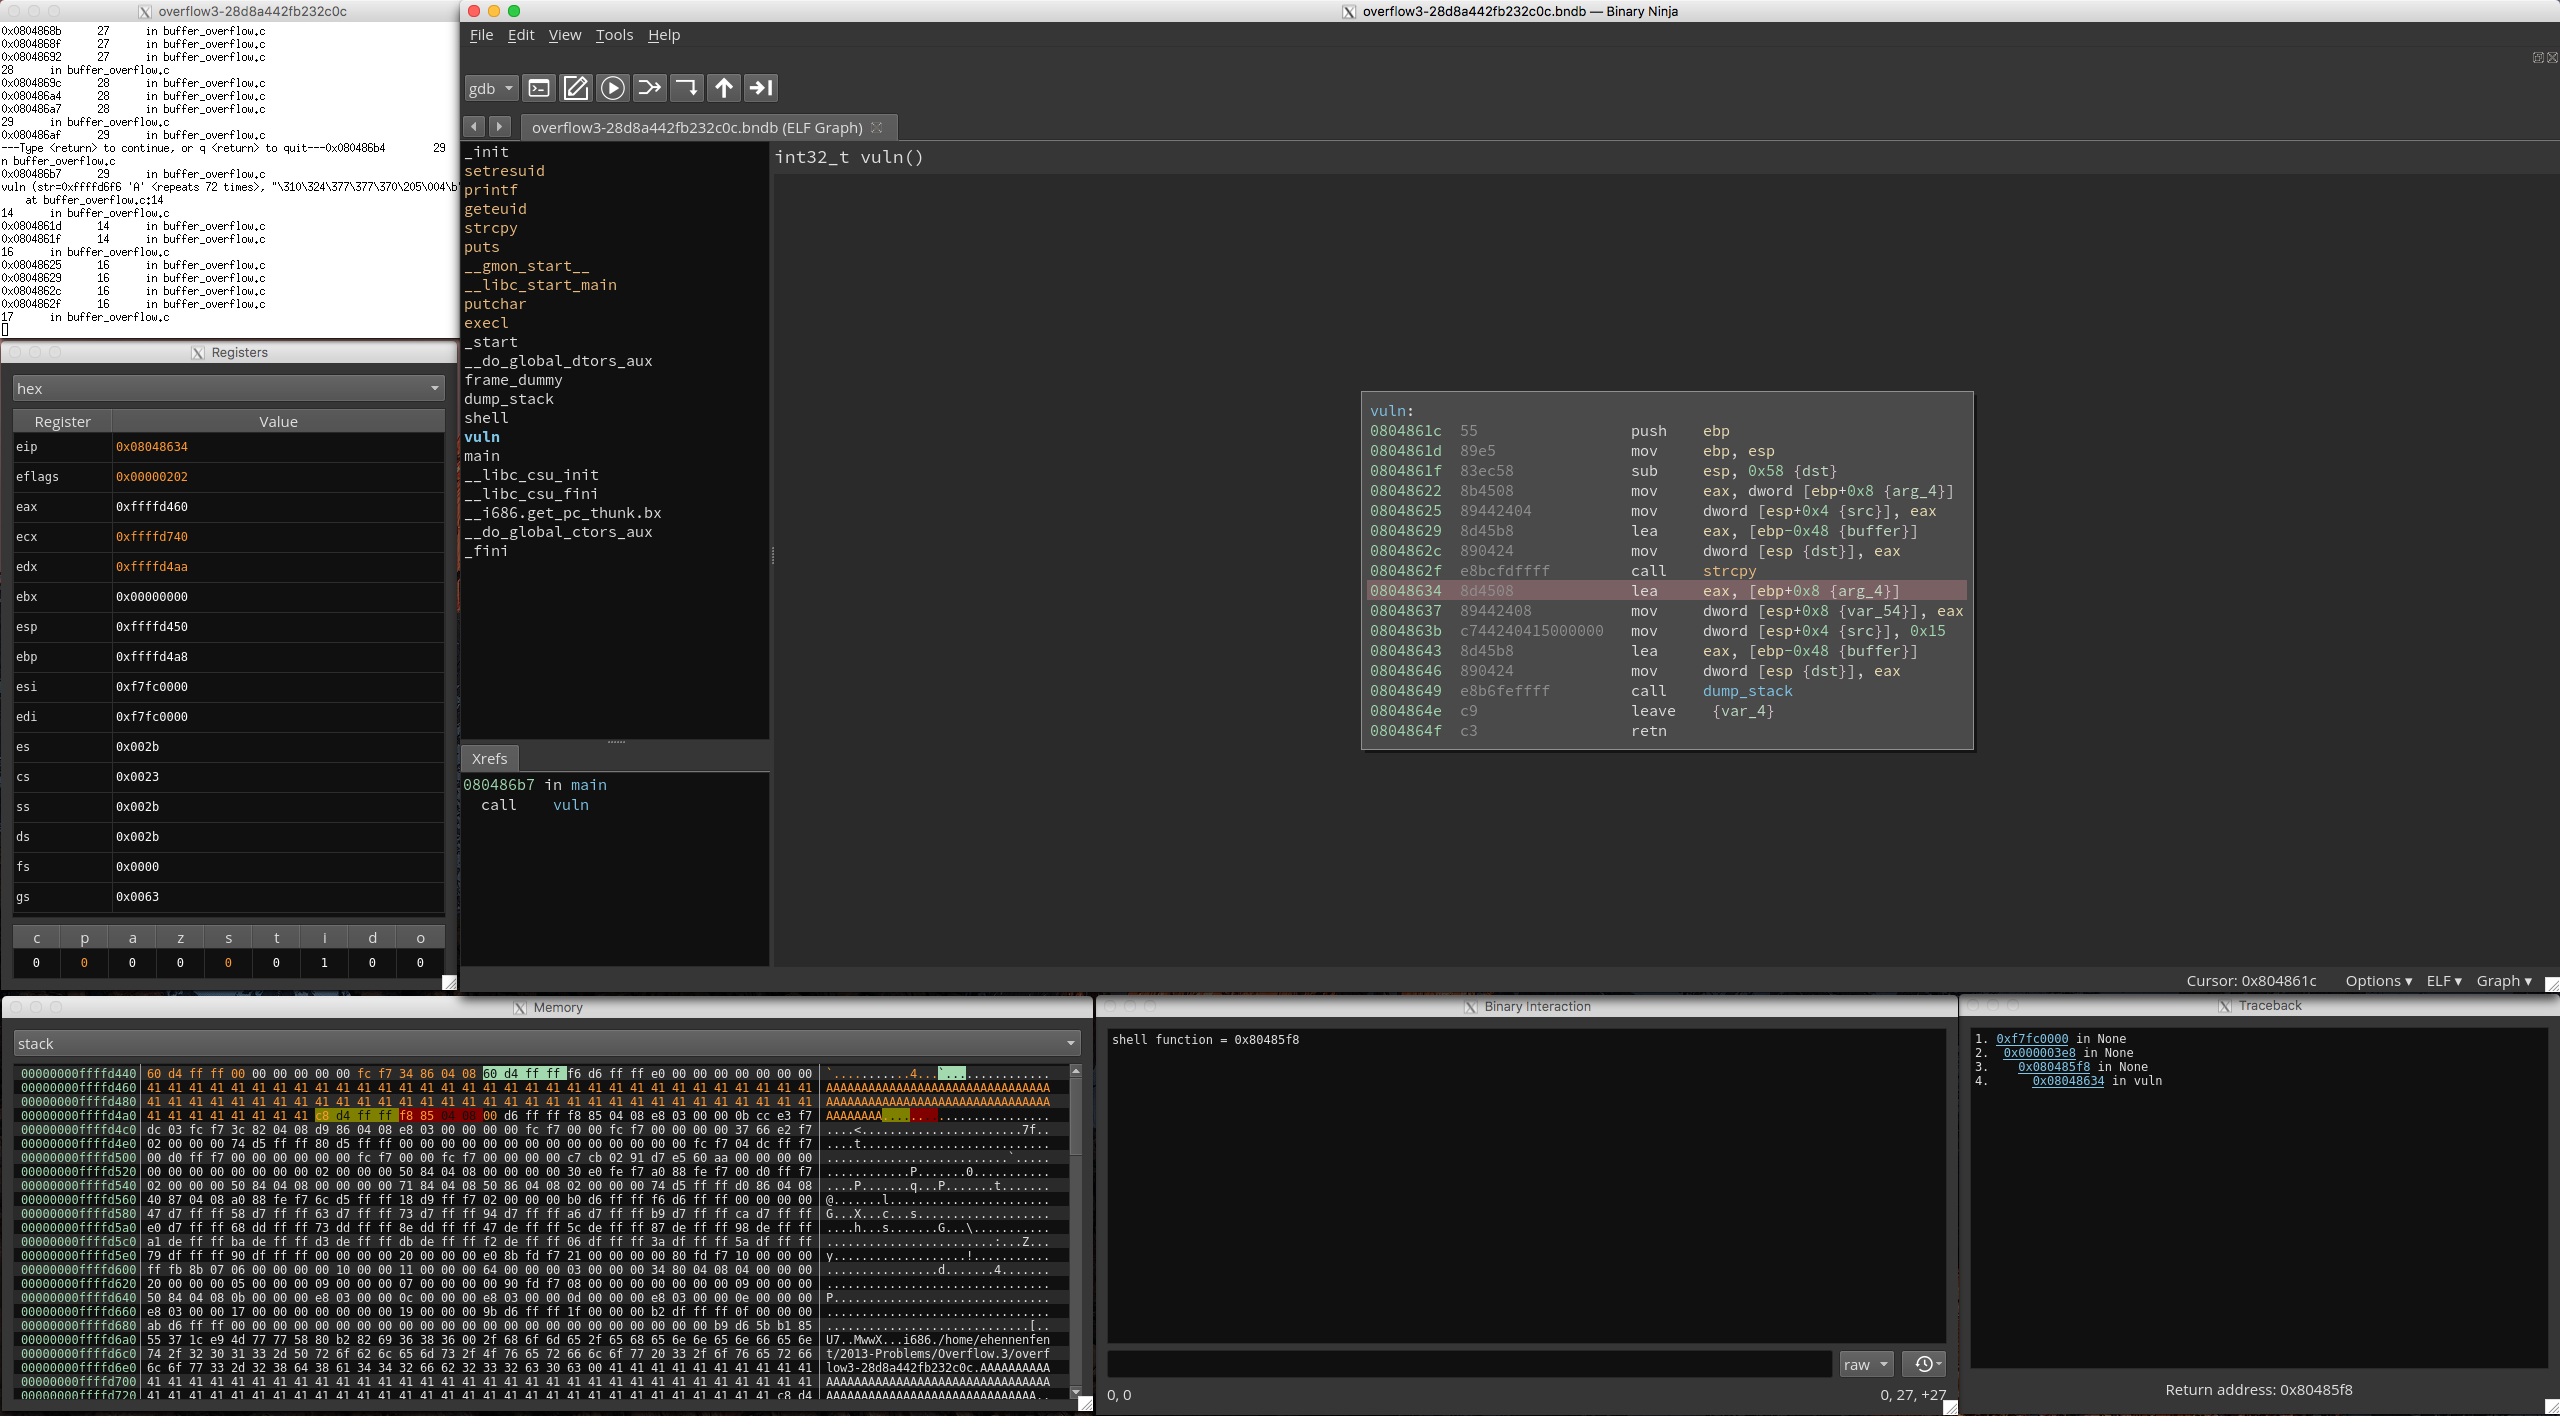
dynamic-analysis-sandboxingpayload-generationvulnerability-analysis+3
91il y a 9 ans
binja_dynamics preview

binja_dynamics

GitHubnccgroup/binja_dynamics

Une interface PyQt5 pour le plugin binjatron de Binary Ninja qui inclut des fonctionnalités de surlignage conçues pour faciliter l'apprentissage de…
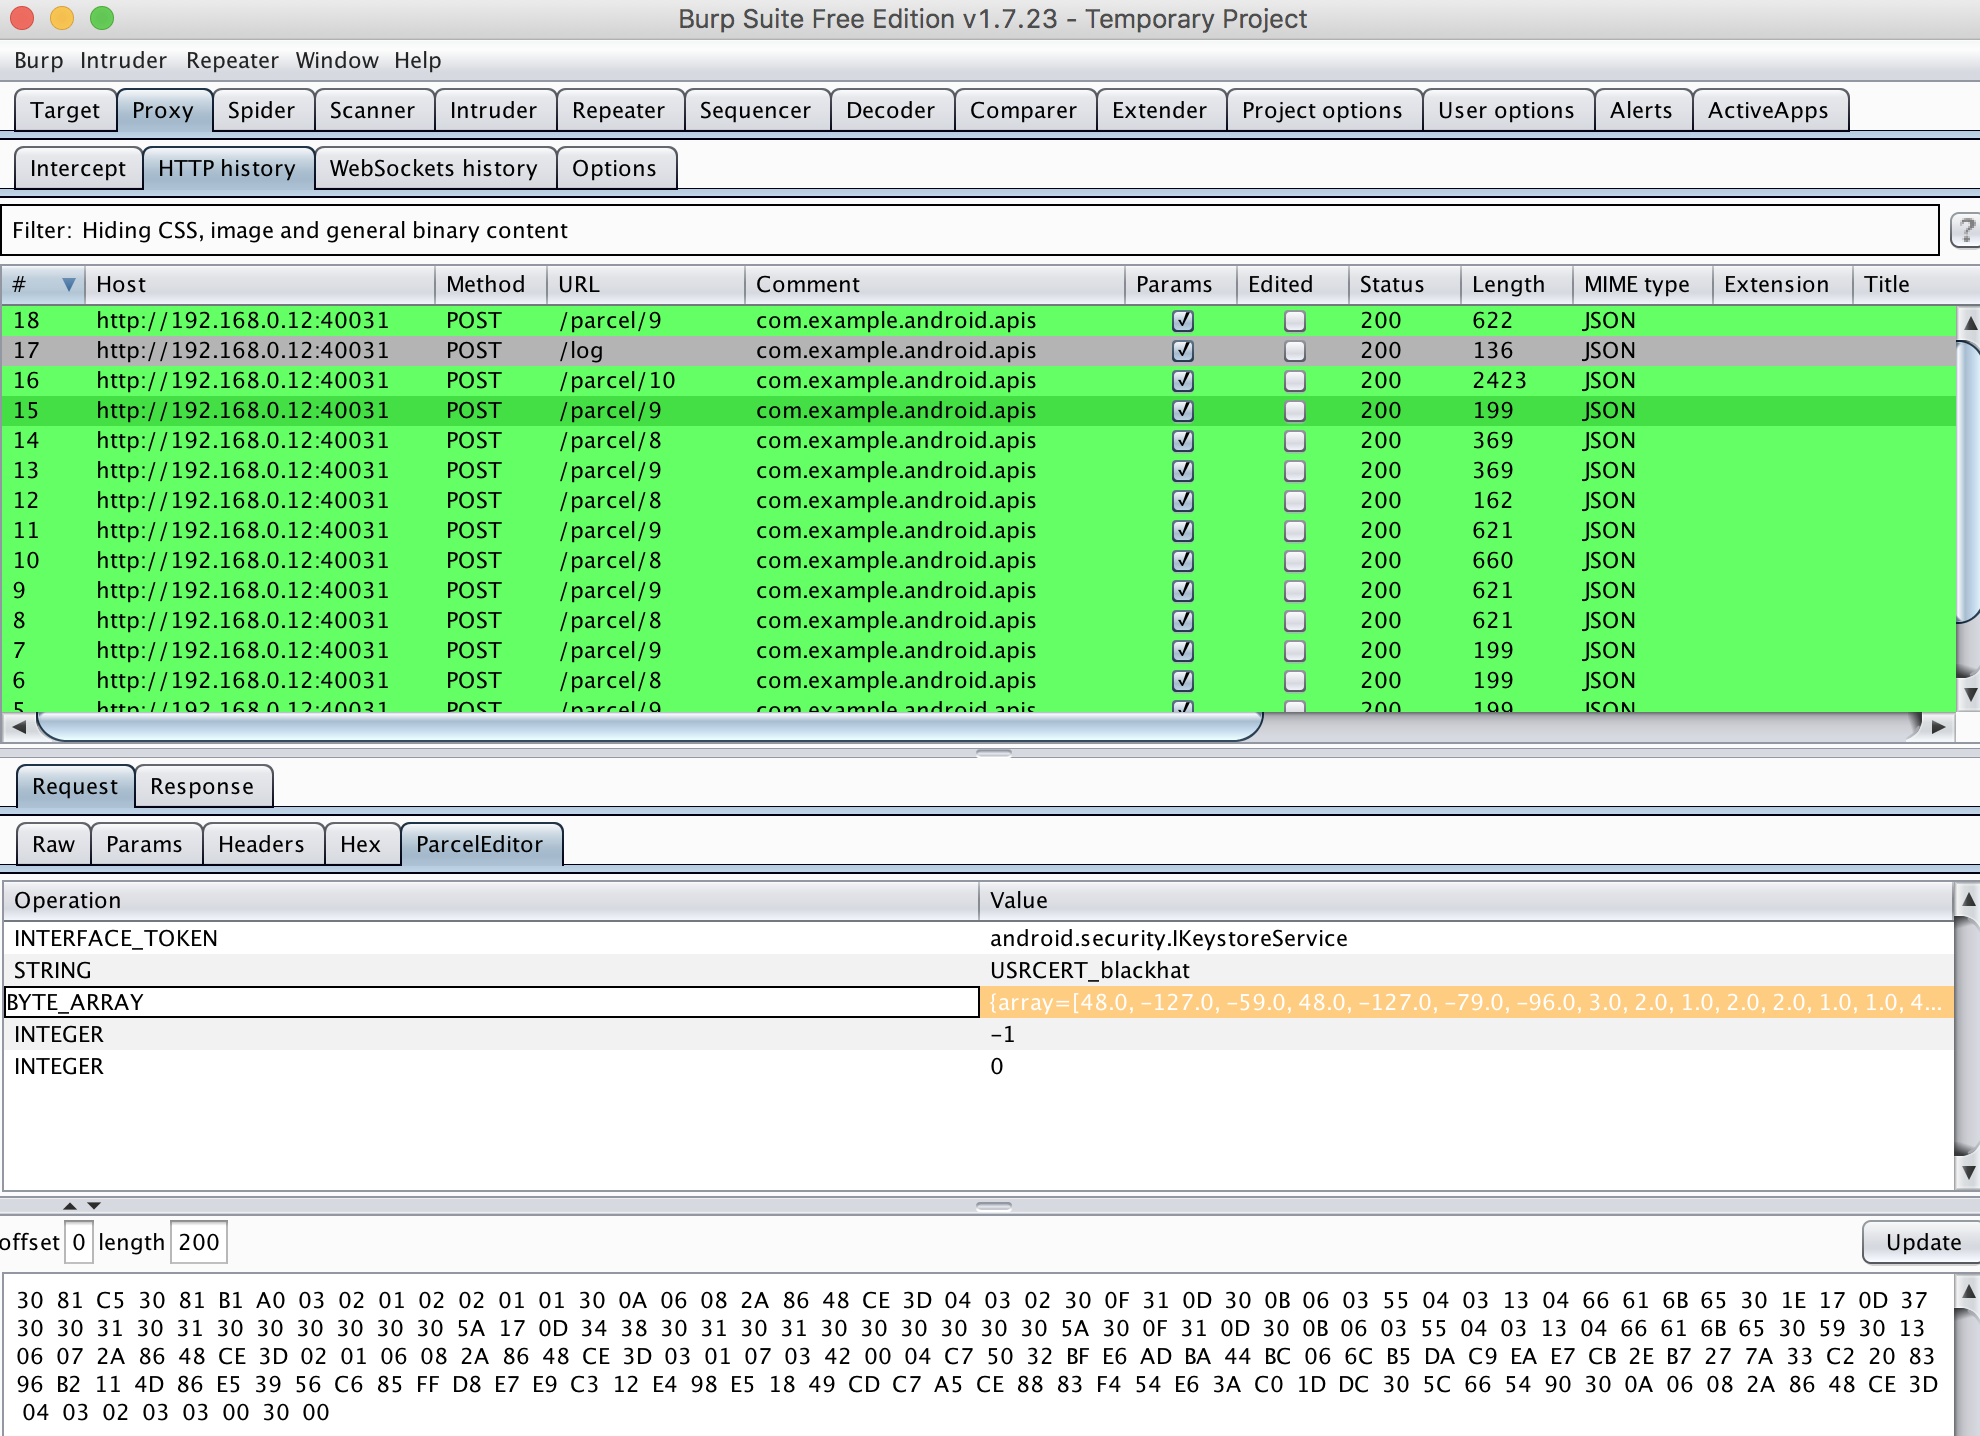
dynamic-analysis-sandboxingreverse-engineeringdebuggers+2
25il y a 9 ans
BadIntent preview
Archived

BadIntent

GitHub1ultimat3/badintent

Intercepter, modifier, répéter et attaquer les transactions Binder d'Android en utilisant Burp Suite
android-securitydynamic-analysis-sandboxingweb-proxies-interception+4
322il y a 9 ans
cuckoo-droid preview

cuckoo-droid

GitHubidanr1986/cuckoo-droid

CuckooDroid - Analyse automatisée des malwares Android avec Cuckoo Sandbox.
android-securitydynamic-analysis-sandboxingmalware-analysis+1
608il y a 9 ans
TriforceAFL preview

TriforceAFL

GitHubnccgroup/triforceafl

AFL/QEMU fuzzing avec émulation du système complet.
dynamic-analysis-sandboxingvulnerability-analysisfuzzing+2
644il y a 9 ans
frida-wshook preview

frida-wshook

GitHuboalabs/frida-wshook

Outil d'analyse de scripts basé sur Frida.re
dynamic-analysis-sandboxingscripting-automationmalware-analysis
130il y a 9 ans
assethook preview

assethook

GitHubnccgroup/assethook

Magie de LD_PRELOAD pour l'AssetManager d'Android
android-securitydynamic-analysis-sandboxingmobile-app-pentesting+3
82il y a 9 ans
mnemosyne preview

mnemosyne

GitHubnccgroup/mnemosyne

Un outil générique de récupération de mémoire Windows
dynamic-analysis-sandboxingmemory-forensicsinformation-gathering+2
69il y a 9 ans
vUSBf preview

vUSBf

GitHubschumilo/vusbf

Un framework de fuzzing USB basé sur QEMU/KVM qui détecte les bugs de pilotes de périphériques grâce à une exécution de VM reproductible, au…
dynamic-analysis-sandboxingvulnerability-analysissecurity-virtualization+2
170il y a 9 ans
frida-extract preview

frida-extract

GitHuboalabs/frida-extract

Outil d'extraction basé sur Frida.re pour RunPE (et MapViewOfSection)
dynamic-analysis-sandboxingreverse-engineeringforensics+3
114il y a 9 ans
ollydbg-binary-execution-visualizer preview

ollydbg-binary-execution-visualizer

GitHubehabhussein/ollydbg-binary-execution-visualizer

rétro-ingénierie, analyse visuelle de binaires

static-analysisdynamic-analysis-sandboxingreverse-engineering+3
24il y a 9 ans
Précédent1…363738Suivant








