 z4nzu/hackingtool
All-in-one penetration testing toolkit aggregating 185+ tools across 20 categories including information gathering, web & wireless attacks, phishing, exploitation, forensics, and cloud security.

219 curated tools across 21 categories — recon, OSINT, web, wireless, phishing, forensics, post-exploitation and more — with an AI layer that turns plain English into the right tool and the exact command.
Built for penetration testers · red teamers · blue-team/SOC and DFIR analysts · OSINT researchers · bug-bounty hunters · CTF players · security researchers and students — all working legally, on systems they own or are authorised to test.





/find searches your catalog first, then the
GitHub API, and shows real maintained projects with the reason each was ranked.curl | bash, downloads pinned +
SHA-256 verified, list-form subprocess, no forced sudo, and
signed releases with an SBOM.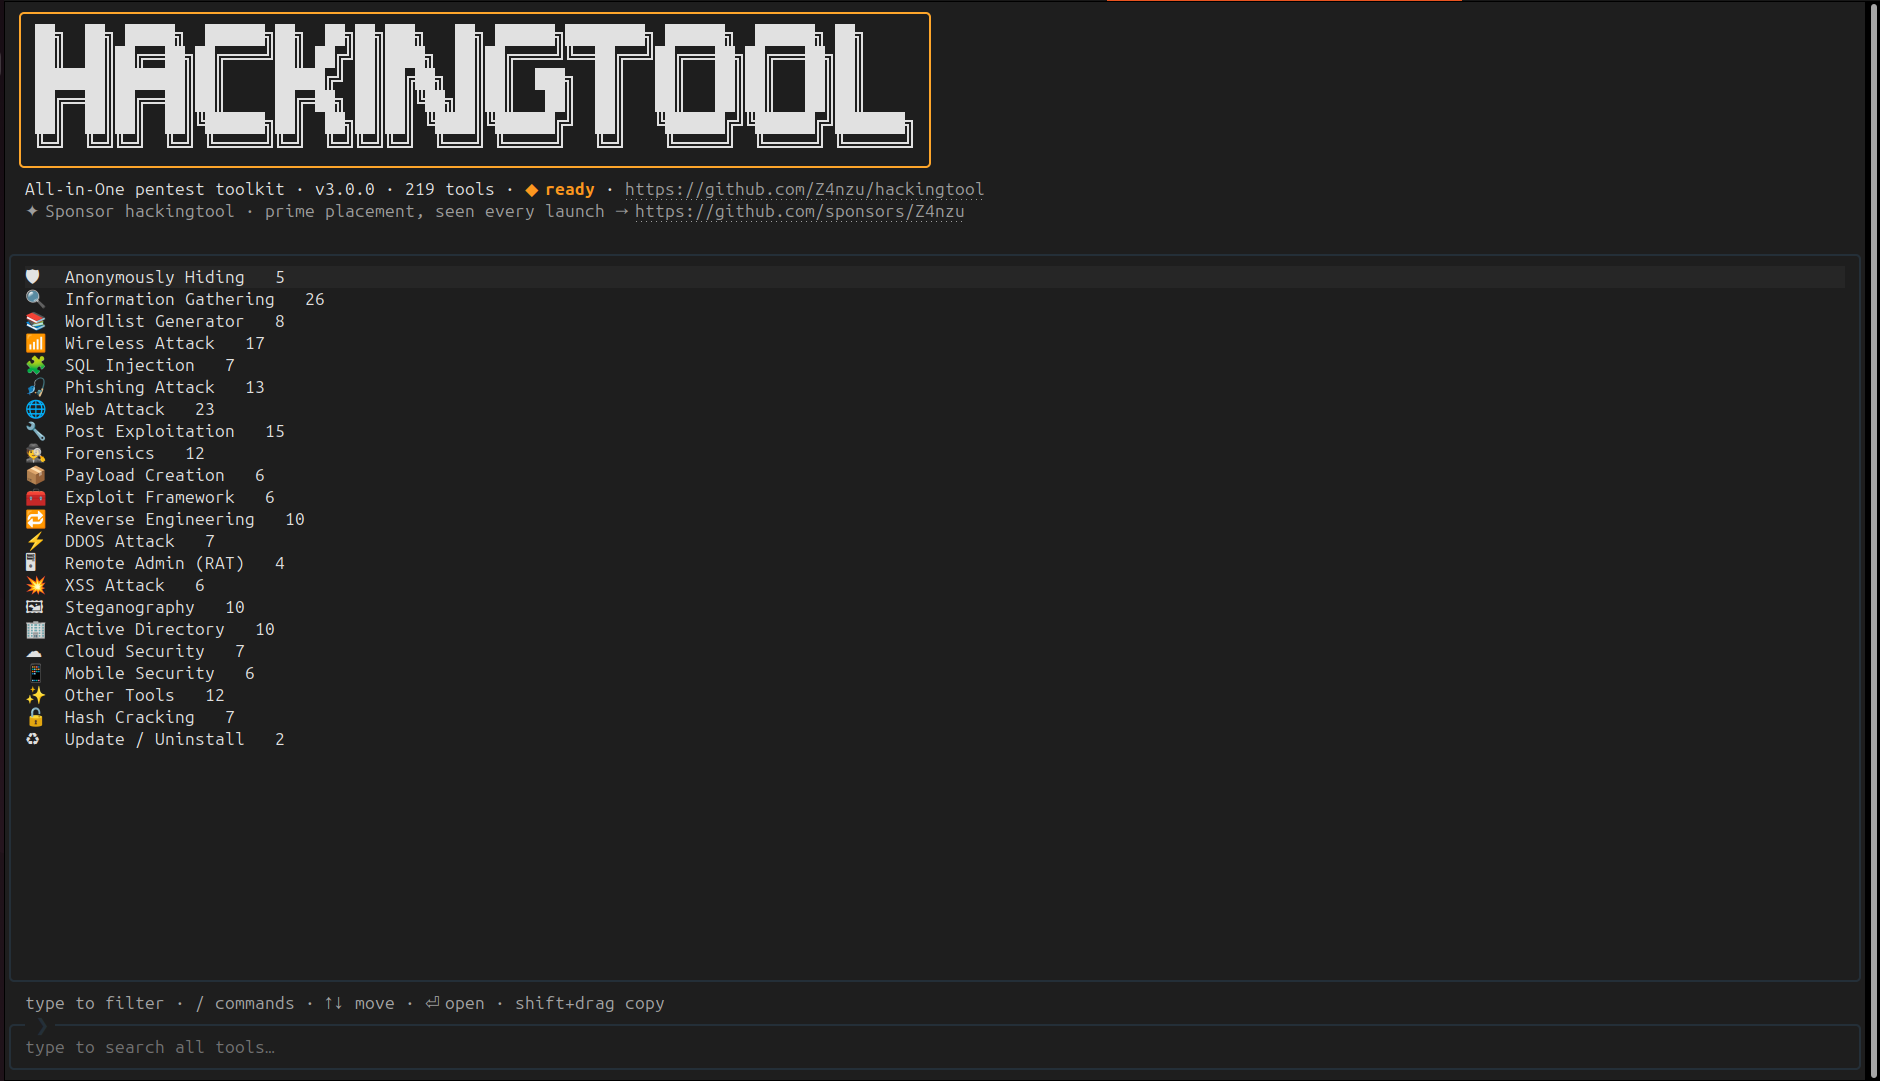
/ opens the command palette.
219 tools across 21 categories — the full list, with links and tags, is in docs/TOOLS.md.