Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
xalgorix — Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF reports. Self-hosted, bring your own LLM, or run fully local with Ollama. | Kitploit
Herramientas/GitHubGitHub/xalgord/xalgorix
ReconnaissanceVulnerability ScannersDynamic Analysis (Sandboxing)Exploit FrameworksInformation GatheringWeb SecurityPenetration TestingDevSecOpsRed TeamingAI Security
GitHub
851152138hace 1 díaRevisado por Kitploit
Compartir
xalgord/xalgorix

xalgorix

Open-source AI penetration testing agent that exploit-verifies every finding. Autonomous 22-phase pentests of web apps & APIs with CVSS-scored PDF reports. Self-hosted, bring your own LLM, or run fully local with Ollama.
Ver RepositorioSitio web
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.
Xalgorix — open-source autonomous AI penetration testing agent with exploit-verified findings

Go License Platform Xalgorix Cloud GitHub stars GitHub forks GitHub release

Xalgorix — Open-source AI pentester that proves vulnerabilities

Most scanners detect. Xalgorix proves. An autonomous AI penetration testing agent works a full 22-phase pentest methodology against your web apps and APIs, then an independent verifier re-exploits every finding before it's reported — so you get proof, not a pile of maybes to triage. Self-hosted, private, and bring-your-own-LLM (or fully local with Ollama). Built in Go + TypeScript.

🚀 Quick Start · 💡 Why Xalgorix · ✨ Features · 🎯 Use Cases · ☁️ Self-host or Cloud · ❓ FAQ · 📖 Docs · 💬 Discussions

🖥️ Self-host — this repo☁️ Xalgorix Cloud — nothing to install
Free and Apache-2.0. Runs on your machine with your own LLM key, or fully local with Ollama. Findings and reports stay on your infrastructure.The same exploit-verified engine in your browser. Model, out-of-band callbacks and scheduling are managed for you. Packs from $10; credits never expire.
Install in two commands ↓Compare self-hosted vs Cloud →

🤖 Only need PR reviews? The free Xalgorix GitHub App comments a security review on every pull request — no account, no API key.


📸 Screenshots

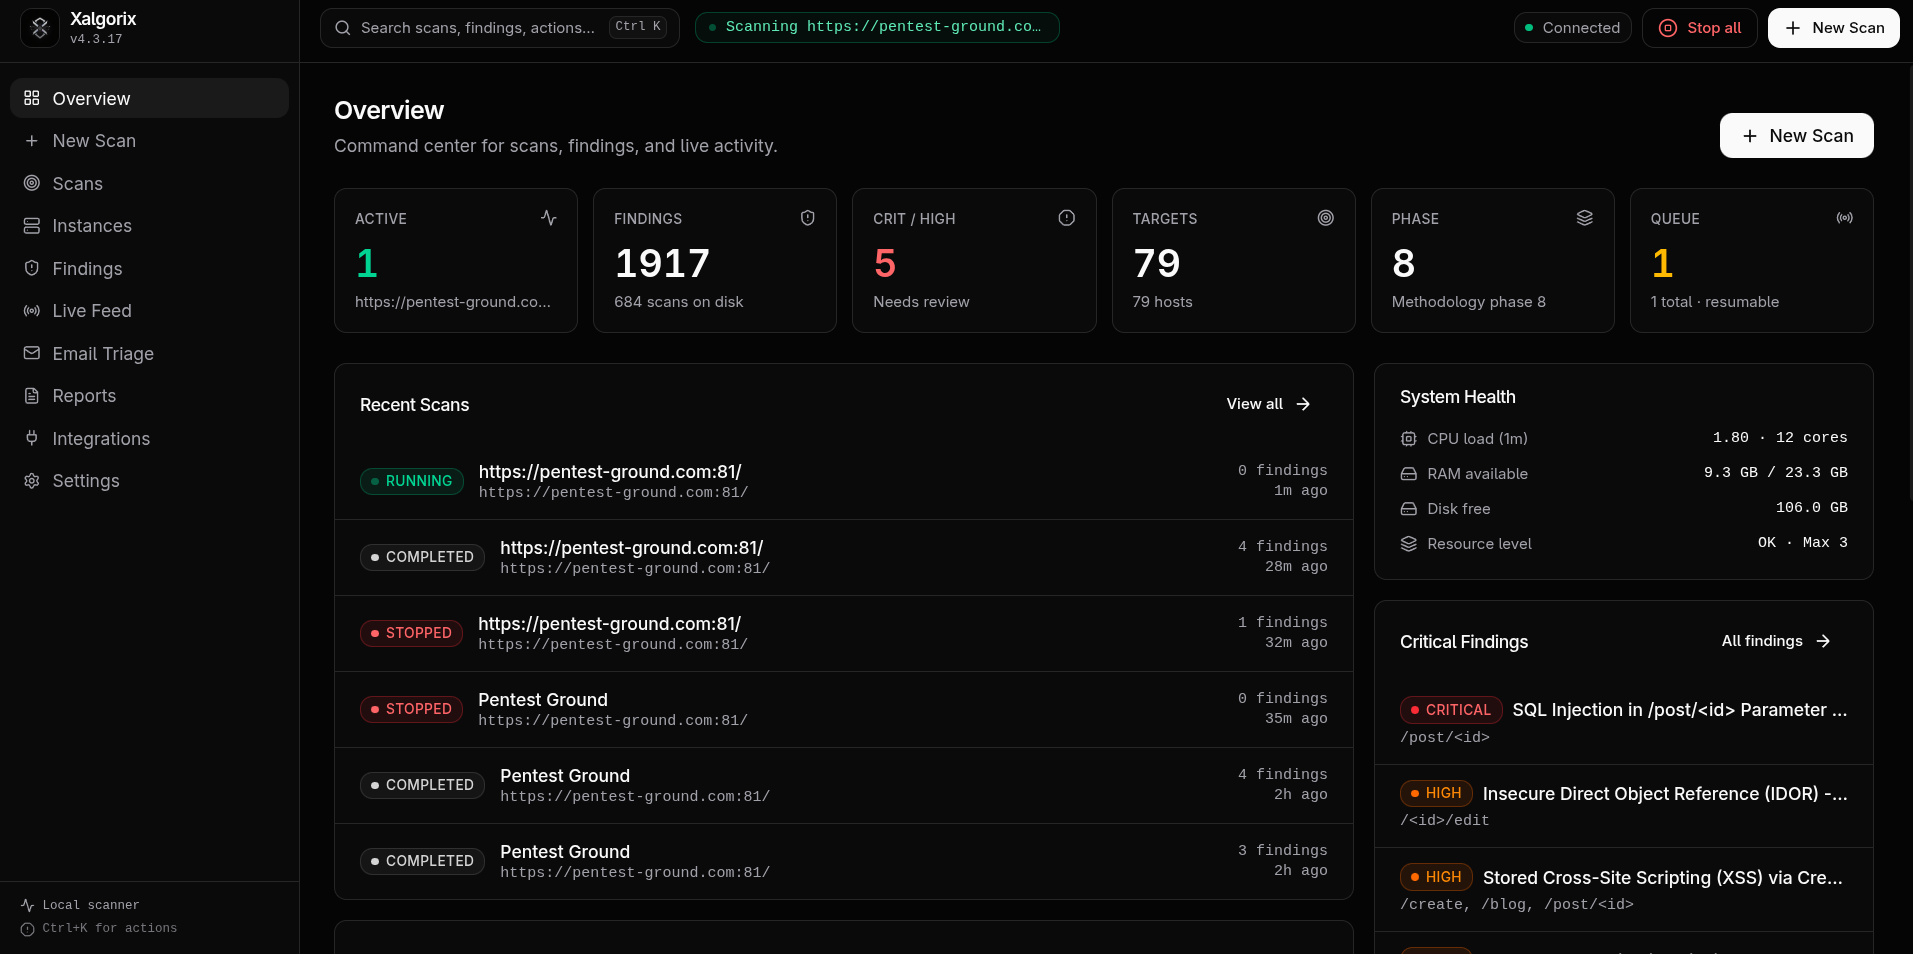
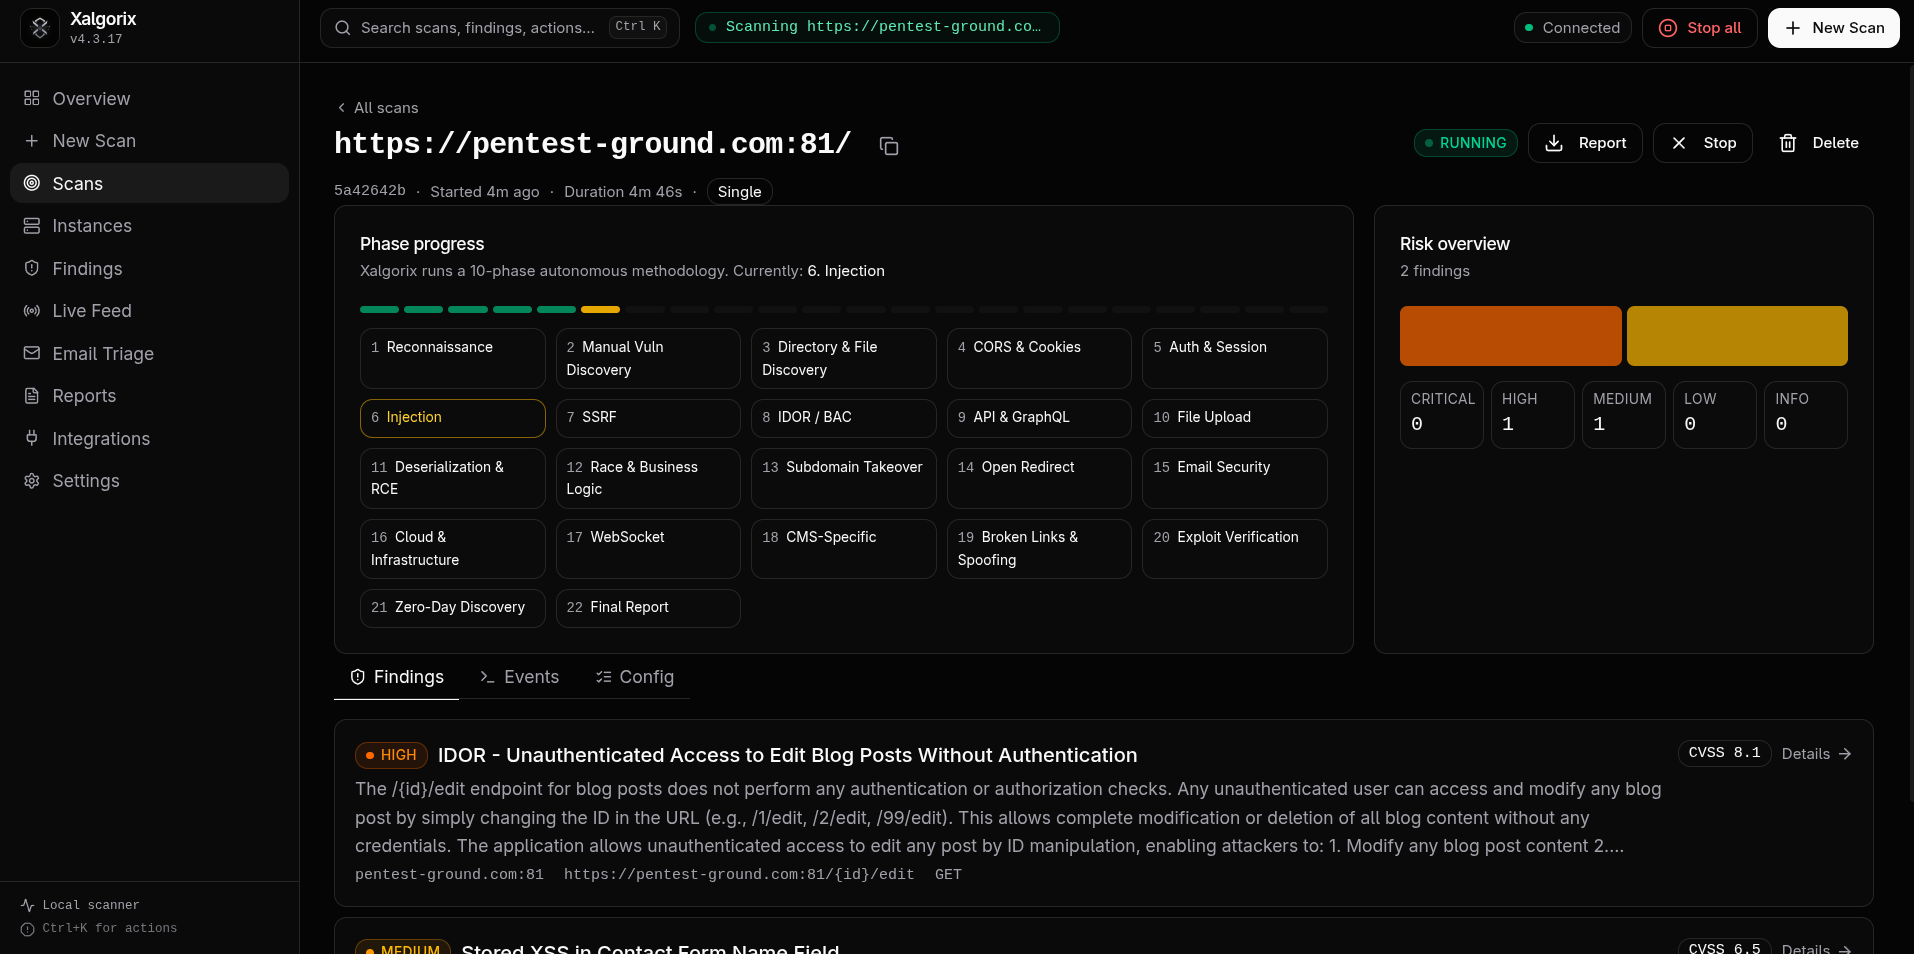
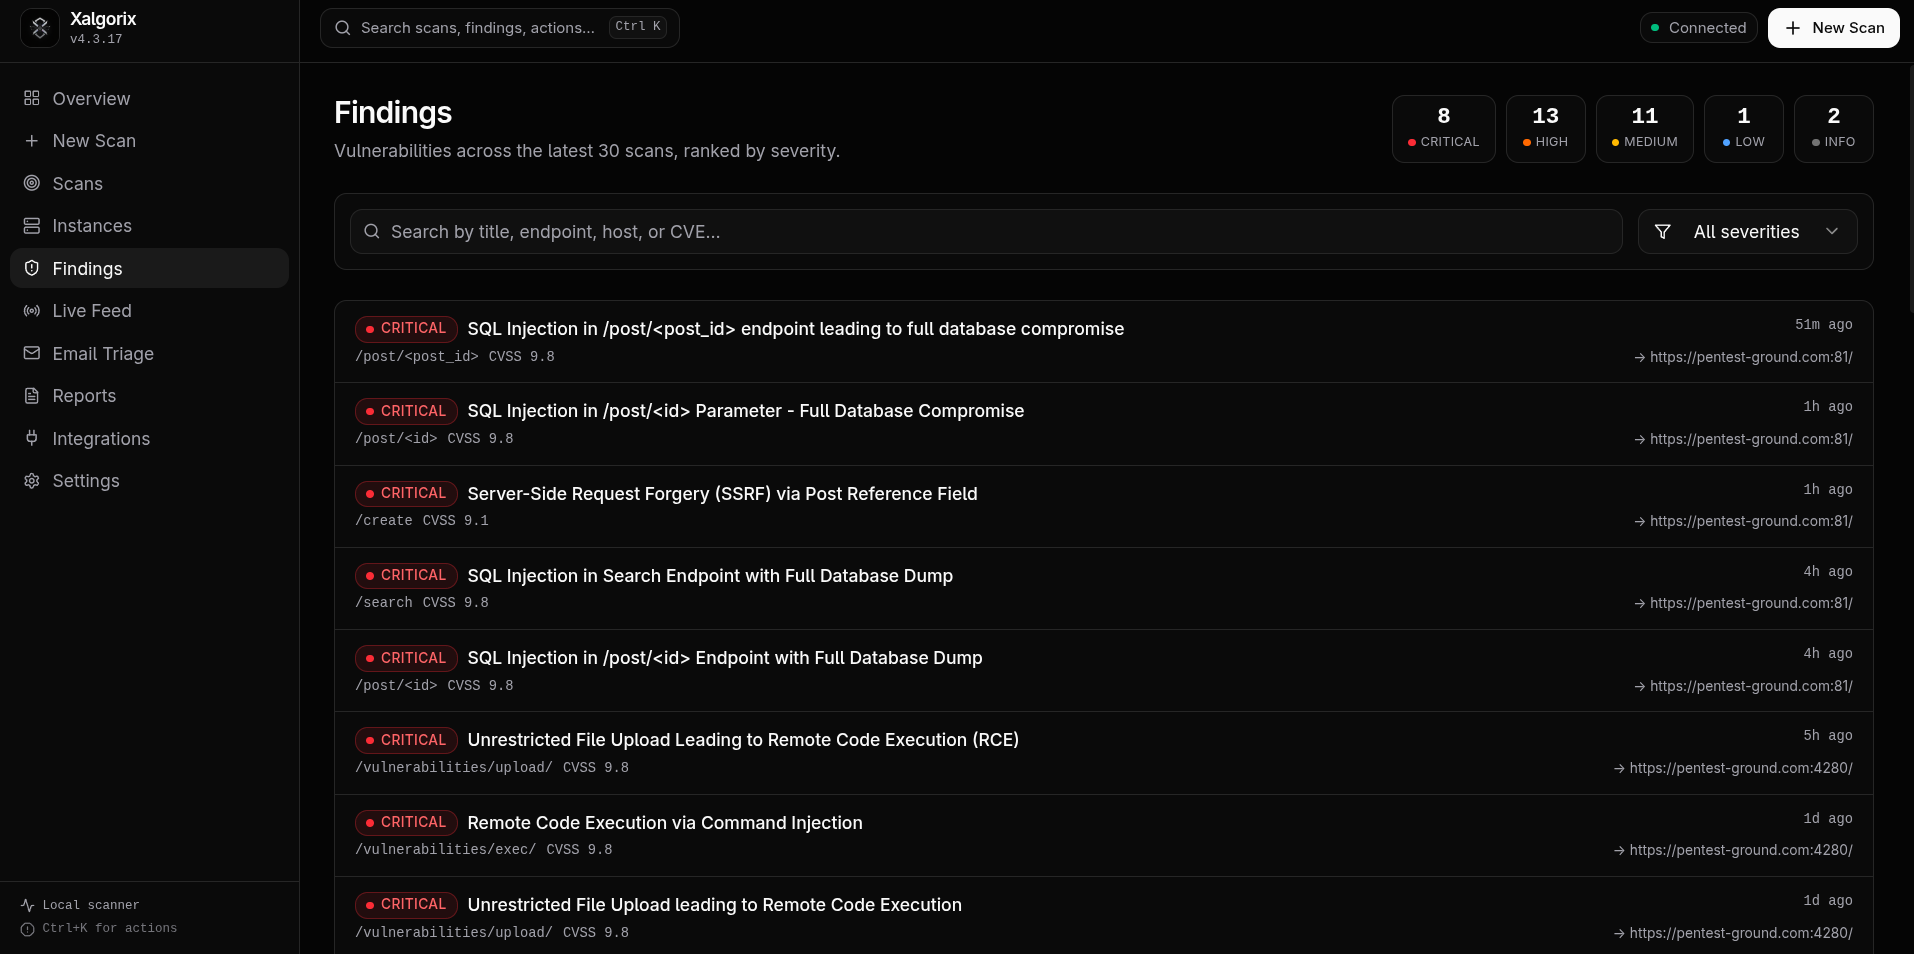
🖥️ Self-hosted dashboard — runs locally on 127.0.0.1:9137

Overview dashboardScan detailFindings
Xalgorix self-hosted AI pentesting dashboard: active scans, recent findings and system healthXalgorix scan detail: 22-phase methodology progress, risk overview and findingsXalgorix findings: SQL injection, SSRF and RCE ranked by severity with CVSS scores

☁️ Xalgorix Cloud dashboard — the managed version at www.xalgorix.com

Xalgorix Cloud dashboard showing security score, vulnerability trends, remediation metrics, and open issues by category


🤝 Sponsors

Xalgorix is supported by proxy-infrastructure partners — handy for checking how your own apps behave across regions. Proxy-Seller speaks HTTP(S) and SOCKS5, the protocols Xalgorix uses.
Proxy-Seller
Proxy-Seller
47M+ residential IPs · 220+ locations · residential, mobile, ISP & datacenter
Xalgorix users get 15% off with XALGORIX

🚀 Quick Start

Install (one line):

curl -sSL https://www.xalgorix.com/install | bash

This downloads the prebuilt binary for your platform (Linux or macOS, amd64/arm64) from the latest release.

Or install with Go 1.26 or newer:

go install github.com/xalgord/xalgorix/v4/cmd/xalgorix@latest

Ensure $(go env GOPATH)/bin (or your GOBIN) is on your PATH before running xalgorix.

Then run the interactive setup wizard:

xalgorix --setup

Choose your provider, confirm a model, and enter the API key when prompted. For best results, use a current frontier model with strong reasoning, long-context performance, and reliable tool calling—such as the latest capable GPT, Claude, or Gemini model available to you. Smaller or local models remain supported, but may require more supervision during long autonomous scans. Xalgorix stores the key privately in ~/.xalgorix.env (mode 0600) and can launch the dashboard for you. Local Ollama needs no API key.

If you choose not to launch immediately, start later with xalgorix --web and open http://127.0.0.1:9137. You can change providers or advanced options at any time under Settings → LLM, or rerun xalgorix --setup.

Or run with Docker — batteries included, no toolchain needed:

docker run --rm -p 9137:9137 \
  --privileged \
  -v xalgorix-data:/data \
  xalgord/xalgorix:latest

Descargar herramienta

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 El kit de herramientas OSINT definitivo: grafo de investigación, puntuación de confianza, familias de alias, mapa, línea de tiempo e informes. 49 módulos, más de 400 sitios, sin necesidad de claves API.

    806
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicación de Ejecución con un Solo Toque GhostLock (CVE-2026-43499)

    523
  • 3

    ARTEX

    baarai/artex

    Plataforma de pruebas de penetración autónoma multiagente basada en LLM con agentes planificadores/trabajadores, grafos de activos y de exploración, registro de tráfico MITM y reevaluación de vulnerabilidades.

    441
  • 4

    redforge

    cybersecurity91/redforge

    Kit de herramientas de red team del lado del navegador con 102 herramientas offline para reconocimiento, generación de payloads, ataques de credenciales, criptografía, codificación y elaboración de informes de compromiso.

    346
  • 5

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingiere informes de Shadowserver en MongoDB y los reproduce como mapas interactivos, análisis, hallazgos, avisos y paneles ejecutivos.

    270
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    El sistema de acción para la ciberseguridad nativa de IA—donde la intención se convierte en ejecución gobernada, la evidencia se convierte en memoria operativa y cada operación mejora la siguiente.

    264

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →