

Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
dep-scan — Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD integration. | Kitploit
Herramientas/GitHubGitHub/owasp-dep-scan/dep-scan
Vulnerability ScannersContainer SecurityDevSecOpsSupply Chain Security
GitHubowasp-dep-scan/dep-scan

dep-scan

Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD integration.

Ver Repositorio
1.3k13758hace 9h 43mRevisado por Kitploit
Sitio web
Compartir
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.

Introduction

OWASP dep-scan is a next-generation security and risk audit tool based on known vulnerabilities, advisories, and license limitations for project dependencies. Both local repositories and container images are supported as the input, and the tool is ideal for integration with ASPM/VM platforms and in CI environments.
SBOM release

Contents

  • Features
    • Precise reachable data-flows
    • Reachability matrix
    • Rust reachability (via rusi)
    • Go reachability (via golem)
    • .NET reachability (via dosai)
    • JVM, JavaScript, Python, and PHP reachability (via atom)
    • Vulnerability Data sources
    • Linux distros
  • Quick Start
    • Scanning projects locally (Python version)
    • Homebrew (macOS and Linux)
    • Standalone binaries (no Python or Node.js required)
    • Scanning containers locally (Python version)
    • Scanning projects locally (Docker container)
    • Server mode
  • Local development
  • Documentation (depscan.readthedocs.io)
  • License

Features

  • Scan most application code (local repos, Linux container images, Kubernetes manifests, and OS) to identify known CVEs with prioritization
  • Perform advanced reachability analysis for multiple languages (see the reachability matrix below)
  • Package vulnerability scanning is performed locally and is quite fast. No server is used
  • Generate Software Bill-of-Materials (SBOM) with Vulnerability Disclosure Report (VDR) information
  • Generate a Common Security Advisory Framework (CSAF) 2.0/2.1 VEX document (check out the CSAF Readme)
  • Perform deep packages risk audit for dependency confusion attacks and maintenance risks (see the risk audit docs)

Precise Reachable data-flows

Detailed data flows to identify both reachable and non-reachable paths in your application based on the full context.
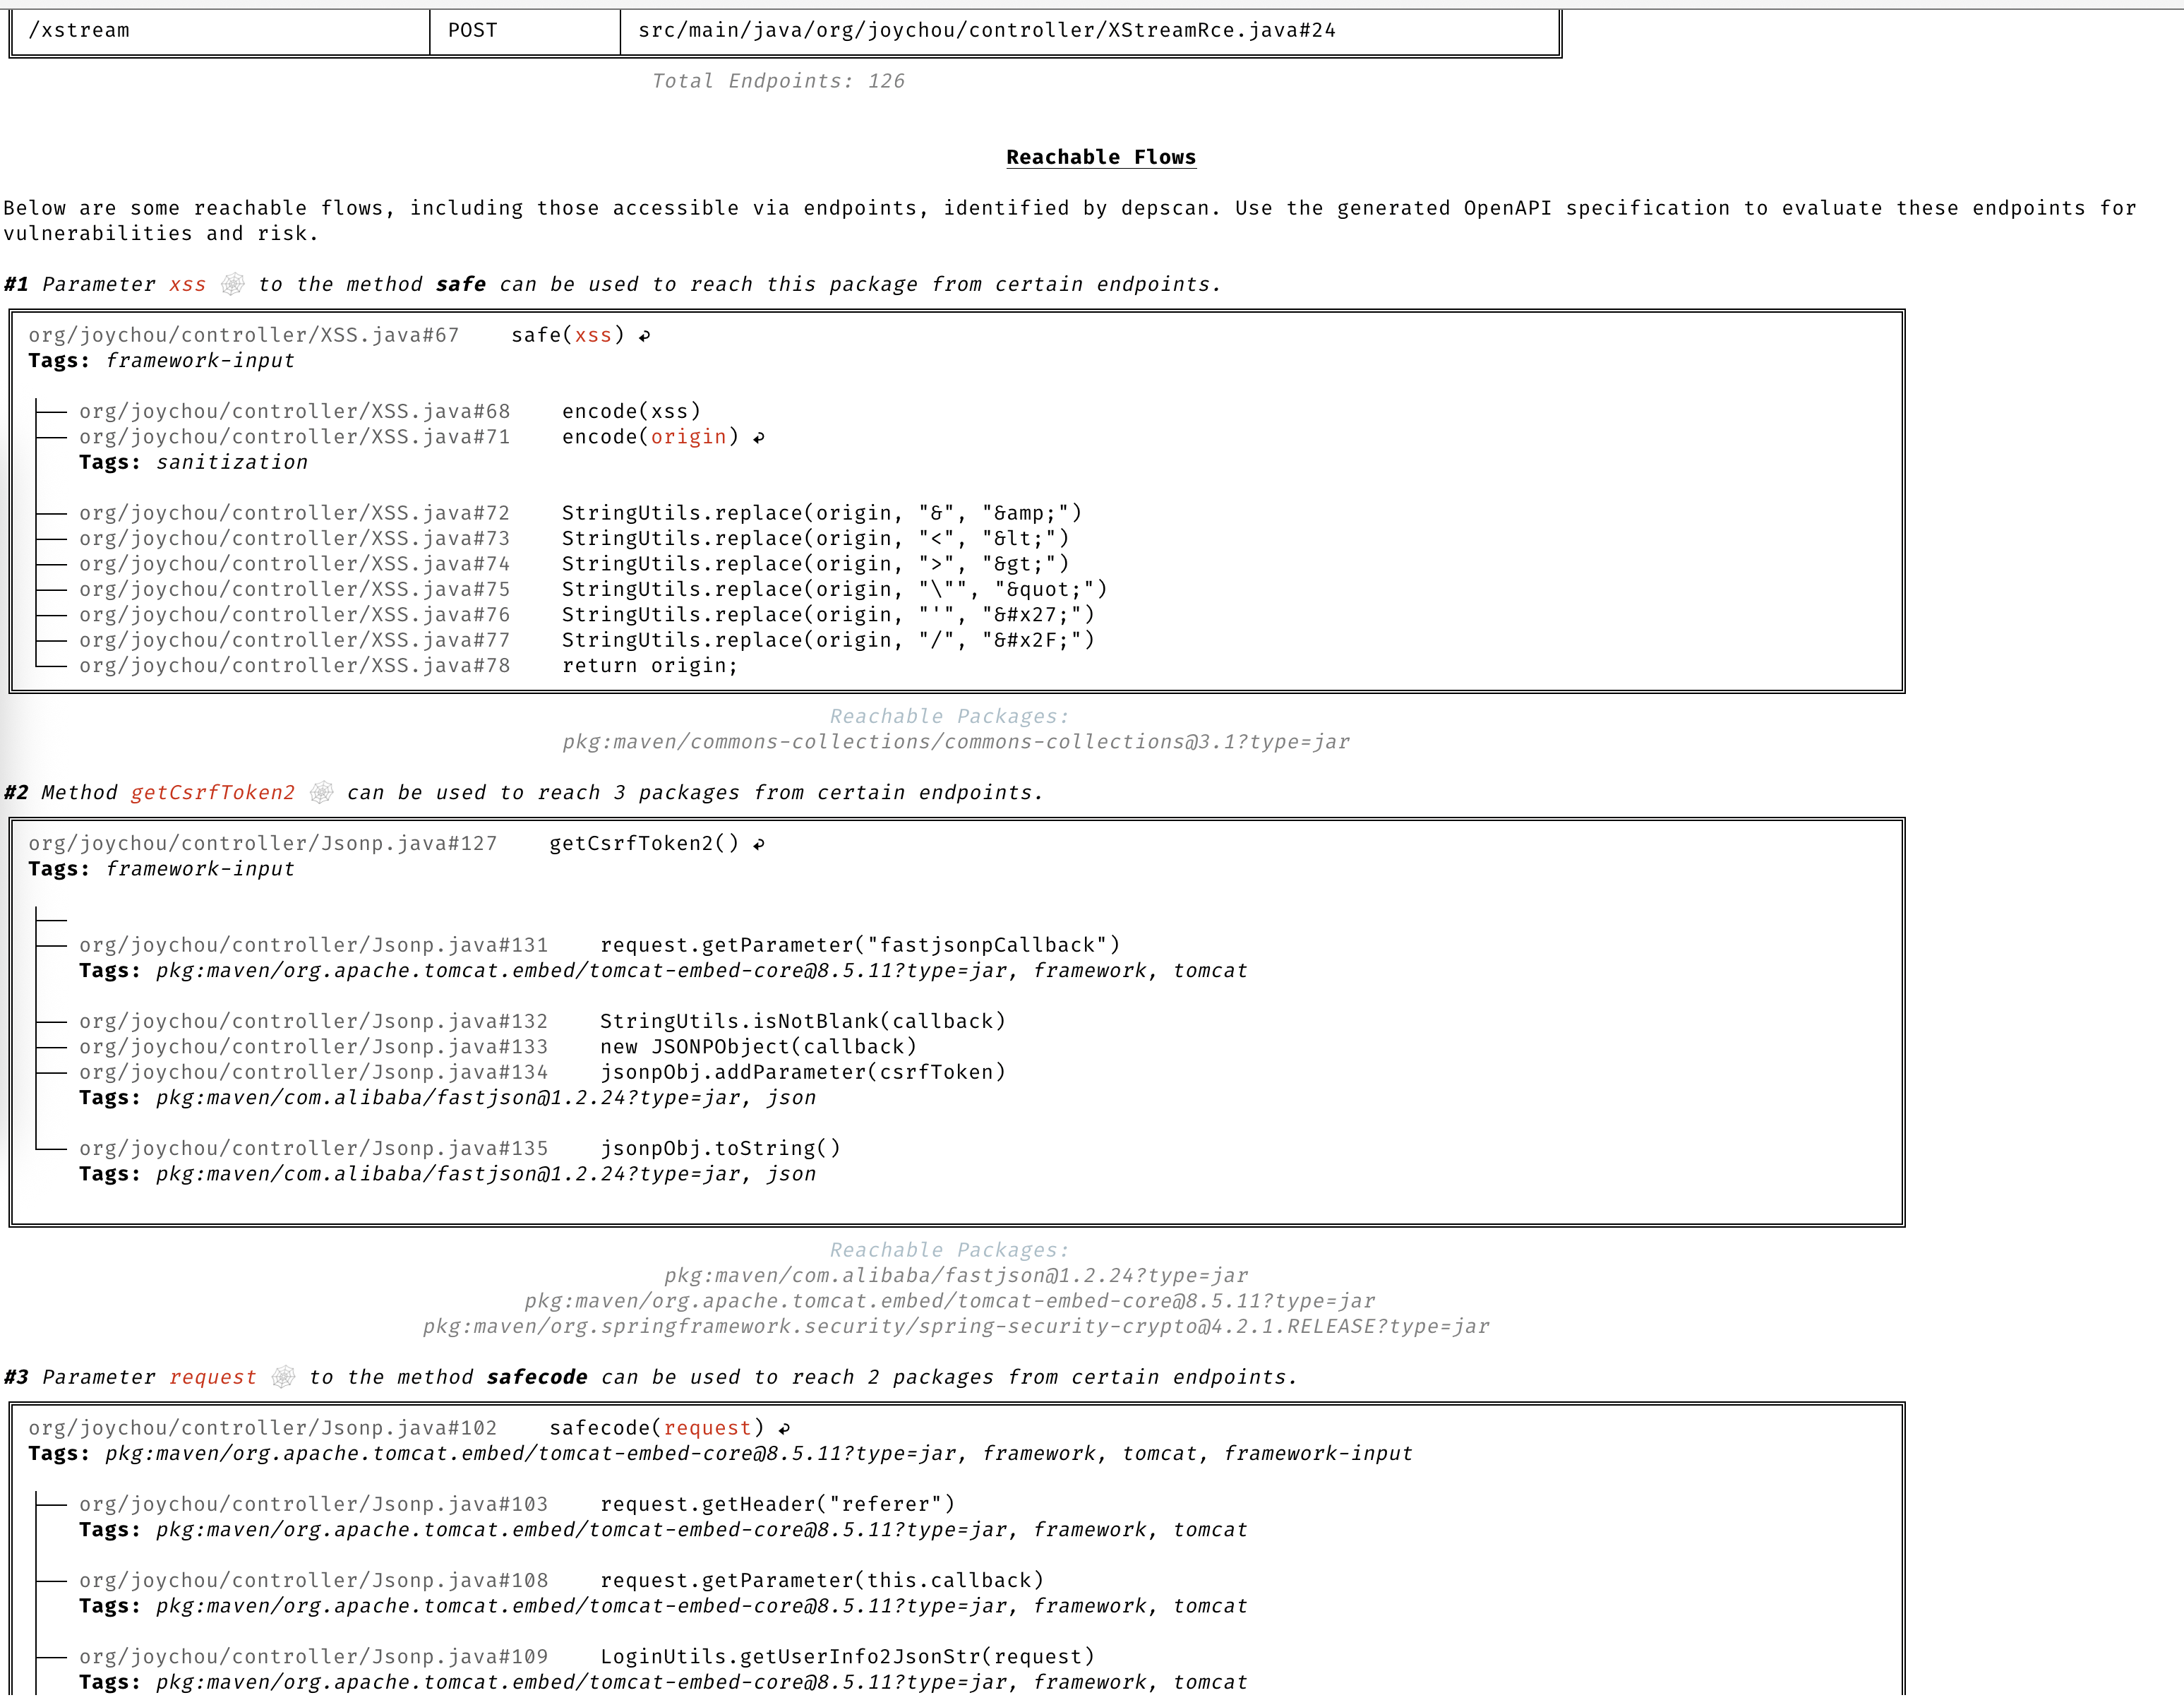
Reachable Flows

Reachability matrix

dep-scan computes reachability for seven language ecosystems through four slicers. A vulnerable package whose code is actually on an executed path is marked Reachable, while a package that is merely declared in the BOM but never called is not. Every slicer feeds the same shared, purl-keyed reachability engine, so the behavior is uniform across languages. Reachability is on by default (--reachability-analyzer FrameworkReachability); SemanticReachability additionally attributes reached services, endpoints, and post-build (binary/container) reachability.

Language / ecosystemReachability engineDefault analyzer
Java / JVM (Groovy, Kotlin, Scala)atomFrameworkReachability
JavaScript / TypeScriptatomFrameworkReachability
PythonatomFrameworkReachability
PHPatomFrameworkReachability
RustrusiFrameworkReachability
GogolemFrameworkReachability
.NET (C#, VB, F#, R)dosaiFrameworkReachability

For the concepts behind reachability and prioritization, read the reachability model and prioritization chapters. For per-language worked examples, see the Language Guides. For the compliance story (VDR and CSAF VEX), see the VDR guide and the CSAF VEX guide.

Reachability is on by default: dep-scan asks cdxgen for its research BOM profile, which writes the slices the analyzers read. The commands below are enough to get started; the per-language guides cover binary resolution, backend and network safety, restore requirements, and worked examples on the in-repo fixtures.

Rust (rusi). cdxgen runs rusi and persists its report, which dep-scan converts into the shared pipeline, so a crate that is actually called (for example time::now() for RUSTSEC-2020-0071) is Reachable while one merely present is not. See the Rust reachability guide.

depscan scan ./my-rust-app -o ./reports --bom-profile research

Go (golem). dep-scan invokes golem directly for Go projects (needs go on PATH), marking a module Reachable when its functions are on a traced path. golem runs with cgo off, so packages that need cgo are not loaded and their reachability is missing; pass --go-analyzer-cgo for trusted input. Use --go-analyzer-network offline for untrusted repos with a warm module cache. See the Go reachability guide.

depscan scan ./my-go-app -o ./reports -t go

.NET (dosai). cdxgen runs dosai, which emits an explicit per-package reachability verdict (PackageReachability with ReachabilityKind and Confidence) that dep-scan treats as authoritative, so a NuGet package actually called (for example JsonConvert.DeserializeObject on a controlled input) is Reachable. Scan a restored tree for versioned purls. See the .NET reachability guide.

depscan scan ./my-dotnet-app -o ./reports -t dotnet

JVM, JavaScript/TypeScript, Python, and PHP (atom). These four ecosystems share the atom slicer, which builds a language-agnostic intermediate representation and performs static slicing. See the JVM, JS, Python, and PHP reachability guide.

depscan scan ./my-java-app --bom-profile research -t java -o ./reports --explain

Descargar herramienta

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 El kit de herramientas OSINT definitivo: grafo de investigación, puntuación de confianza, familias de alias, mapa, línea de tiempo e informes. 49 módulos, más de 400 sitios, sin necesidad de claves API.

    546
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicación de Ejecución con un Solo Toque GhostLock (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    Plataforma de pruebas de penetración autónoma multiagente basada en LLM con agentes planificadores/trabajadores, grafos de activos y de exploración, registro de tráfico MITM y reevaluación de vulnerabilidades.

    377
  • 4

    redforge

    cybersecurity91/redforge

    Kit de herramientas de red team del lado del navegador con 102 herramientas offline para reconocimiento, generación de payloads, ataques de credenciales, criptografía, codificación y elaboración de informes de compromiso.

    324
  • 5

    estorides

    grisuno/estorides

    Agrega más de 99 fuentes OSINT gratuitas en paralelo, resuelve entidades en un grafo de conocimiento y exporta STIX 2.1, MISP o GraphML con análisis asistido por LLM.

    269
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    El sistema de acción para la ciberseguridad nativa de IA—donde la intención se convierte en ejecución gobernada, la evidencia se convierte en memoria operativa y cada operación mejora la siguiente.

    252

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →





