Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
Guardrails — Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask sensitive data. | Kitploit
Herramientas/GitHubGitHub/nvidia-nemo/guardrails
Defensive ToolsVulnerability AnalysisPrivacyMachine LearningAI SecurityAnomaly DetectionTop en AI Security #10
GitHubnvidia-nemo/guardrails

Guardrails

Programmable guardrails for LLM chat apps: enforce input/output rails, block jailbreaks and prompt injections, detect hallucination, and mask sensitive data.

7.5k903172hace 11h 58mRevisado por Kitploit
Compartir
Ver RepositorioSitio web
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.

NVIDIA NeMo Guardrails Library

License PyPI Python Tests/Linux Tests/Windows Tests/macOS Lint Documentation Total downloads Monthly downloads

Documentation · Quickstart · Use cases · Integrations · Guardrail catalog · Examples · Community · Security · Releases · Changelog

NeMo Guardrails is an open-source library for applying programmable safety and security controls to LLM and agentic applications. Agents run commands, call APIs, query your data, and read the web. Conversational applications apply input and output checks; retrieval-augmented generation (RAG) systems filter retrieved content and check answers against evidence.

You use the NeMo Guardrails library to declare what each agent may do in a policy, combining low-latency local rules with model-backed checks for jailbreaks, injected instructions, and unsafe tool calls. Your application or agent harness runs these checks and uses their results to decide whether to continue.

pip install nemoguardrails

Requires Python 3.11–3.13. Refer to the installation guide for optional packages and setup.

[!NOTE] Version 0.25.0 deprecates LLMRails, with removal planned no earlier than 0.27.0. Use Guardrails for new integrations and follow the migration guide.
What You Can Build

  • AI agents and coding assistants: Check proposed tool calls and returned results with tool rails, or connect an agent through the hooks server.
  • Conversational applications: Apply input and output checks.
  • Retrieval-augmented generation (RAG): Detect or mask sensitive data in retrieved content and check whether answers are grounded in evidence.

How It Works

  • Define your policy. Configure rails, models, and prompts in YAML. Use Python actions for custom logic.
  • Run the checks. Invoke rails at the points where your application needs a policy decision.
  • Read the result. Handle blocked or modified content before executing a tool or returning a response. You can also route generation through Guardrails.

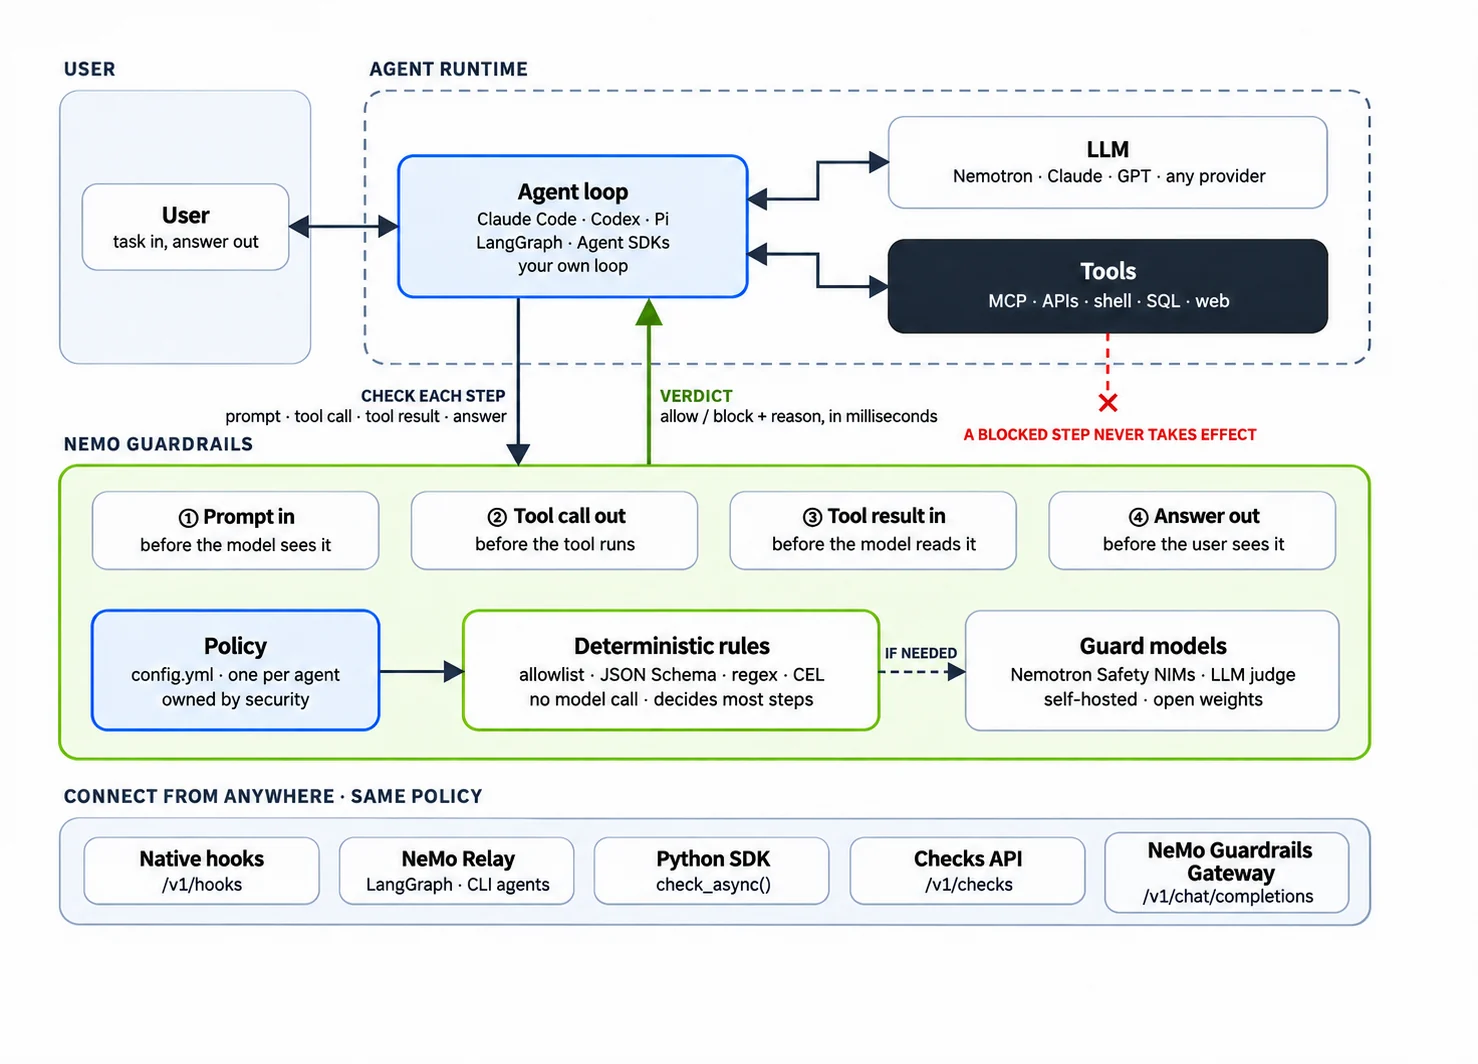
Agent runtime connected to NeMo Guardrails: configurable checks for prompts, tool calls, tool results, and answers, with policy rules, optional guard models, and integration options.

Tool-call checks run before execution, while tool-result checks run after the tool has executed. Latency depends on the configured rules, models, and services.

Integrations support different checks. Rail support varies by engine; refer to rail engine support and configuration.

Why NeMo Guardrails

  • Govern what agents do. Validate tool names and argument schemas before execution. Check tool results and apply per-tool policies before returning them to the model.
  • Keep your model and agent loop. Use checks without main-model generation to add guardrails to an existing application. Model-backed checks still call their configured model or service.
  • Compose the policy you need. Combine local regex and CEL rules with safety models and third-party checks.
  • Connect your runtime. Choose an integration for your application, shared service, or coding agent.
  • Open and yours to run. The library is Apache 2.0 licensed. Choose supported model providers and run checks with local detectors or hosted inference endpoints.

Quickstart

Check a support agent's proposed refund against a $500 limit, without a model or API key. Install the optional CEL extra for this example:

pip install "nemoguardrails[cel]"

The example validates the tool's argument schema and blocks calls over the limit. Expand it and save it as check_refund.py:

Complete Python example
import asyncio
import json

from nemoguardrails import Guardrails, RailsConfig
from nemoguardrails.rails.llm.options import RailStatus, RailType

config = RailsConfig.from_content(yaml_content="""
models: []
rails:
  tool_call:
    flows: [tool call validation]
    per_tool:
      issue_refund: [cel check tool call]
  config:
    cel:
      tool_call:
        issue_refund:
          expressions: ["args.amount > 500"]
""")

TOOLS = [{
    "type": "function",
    "function": {
        "name": "issue_refund",
        "parameters": {
            "type": "object",
            "properties": {"amount": {"type": "number", "minimum": 0}},
            "required": ["amount"],
            "additionalProperties": False,
        },
    },
}]

Descargar herramienta

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 El kit de herramientas OSINT definitivo: grafo de investigación, puntuación de confianza, familias de alias, mapa, línea de tiempo e informes. 49 módulos, más de 400 sitios, sin necesidad de claves API.

    565
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicación de Ejecución con un Solo Toque GhostLock (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    Plataforma de pruebas de penetración autónoma multiagente basada en LLM con agentes planificadores/trabajadores, grafos de activos y de exploración, registro de tráfico MITM y reevaluación de vulnerabilidades.

    383
  • 4

    redforge

    cybersecurity91/redforge

    Kit de herramientas de red team del lado del navegador con 102 herramientas offline para reconocimiento, generación de payloads, ataques de credenciales, criptografía, codificación y elaboración de informes de compromiso.

    327
  • 5

    estorides

    grisuno/estorides

    Agrega más de 99 fuentes OSINT gratuitas en paralelo, resuelve entidades en un grafo de conocimiento y exporta STIX 2.1, MISP o GraphML con análisis asistido por LLM.

    258
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    El sistema de acción para la ciberseguridad nativa de IA—donde la intención se convierte en ejecución gobernada, la evidencia se convierte en memoria operativa y cada operación mejora la siguiente.

    256

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →