
Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
rustinel — Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required. | Kitploit
Herramientas/GitHubGitHub/karib0u/rustinel
Indicator of Compromise (IOC) ManagementIncident Response
GitHubkarib0u/rustinel

rustinel

Endpoint detection for Windows, Linux, and macOS. Sigma, YARA, and IOC rules on native telemetry. Written in Rust. No cloud account required.

Ver RepositorioSitio web
4505562hace 17h 58mRevisado por Kitploit
Compartir
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.

Rustinel

Open-source endpoint detection. Three platforms. Your rules.
Run Sigma, YARA, and IOC detections on native Windows, Linux, and macOS telemetry.
Written in Rust, with local alerts and no cloud account required.

CI Latest release Downloads Apache 2.0 license

Download | Documentation | Detection packs | Website

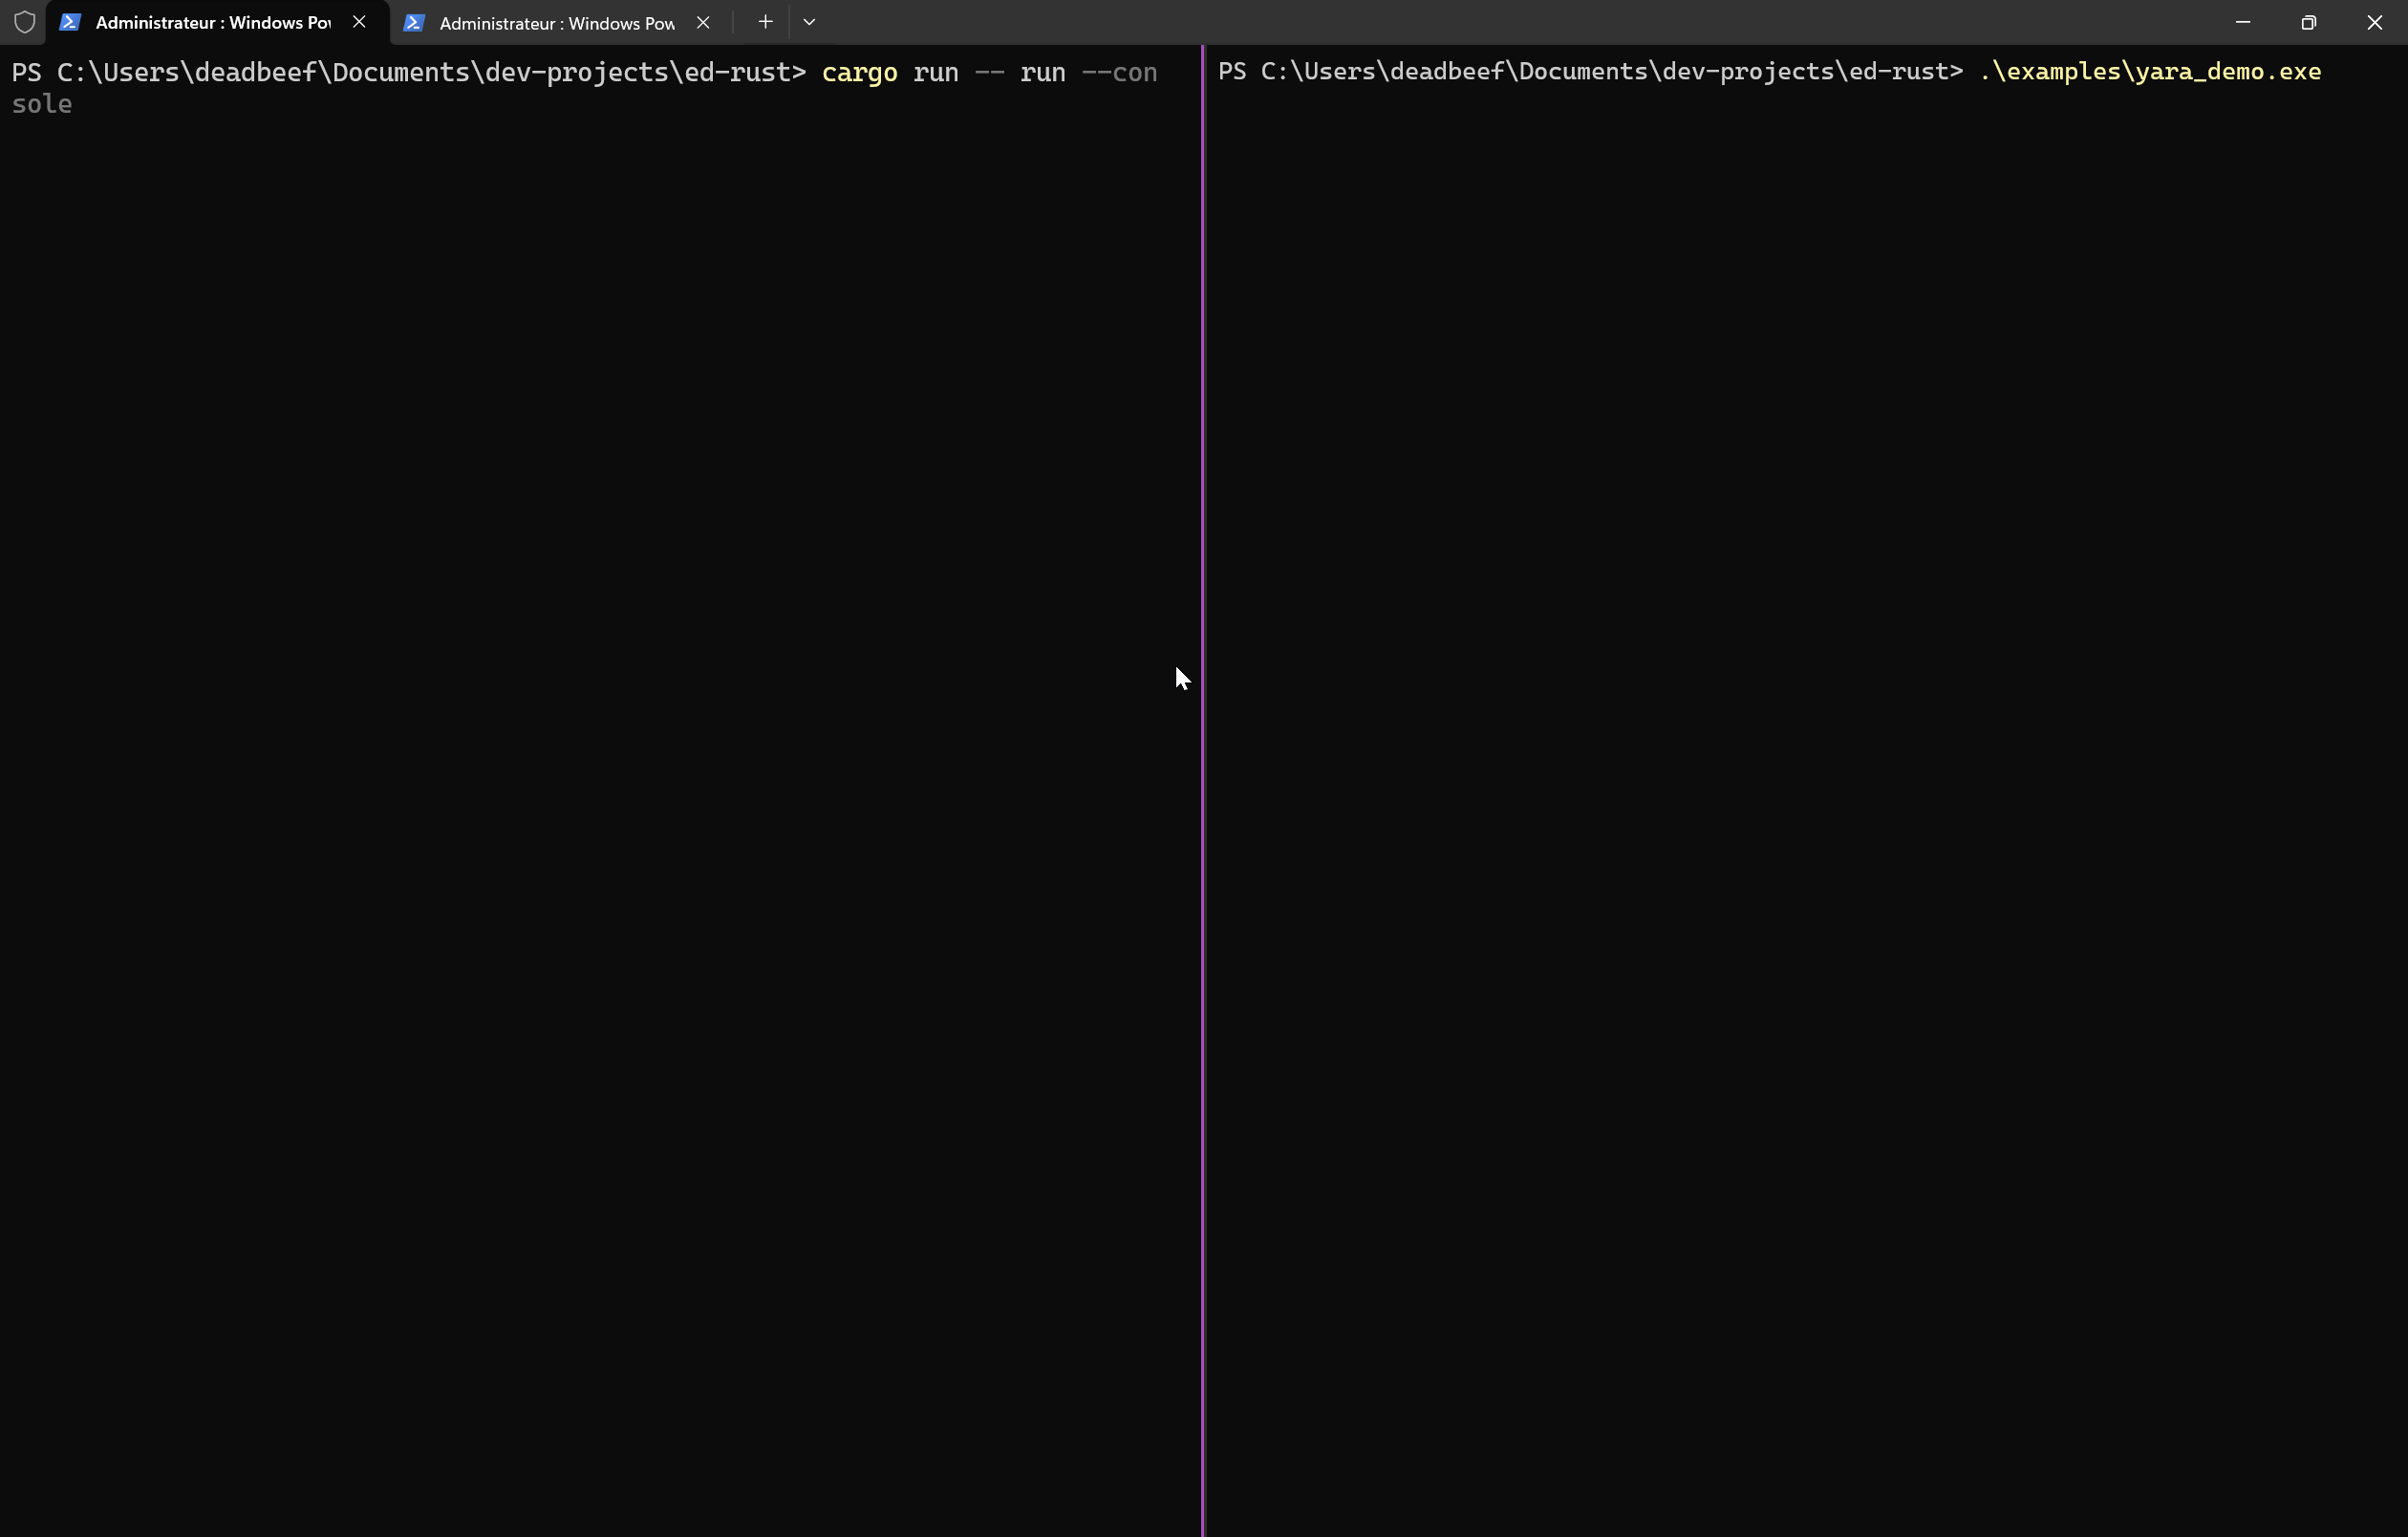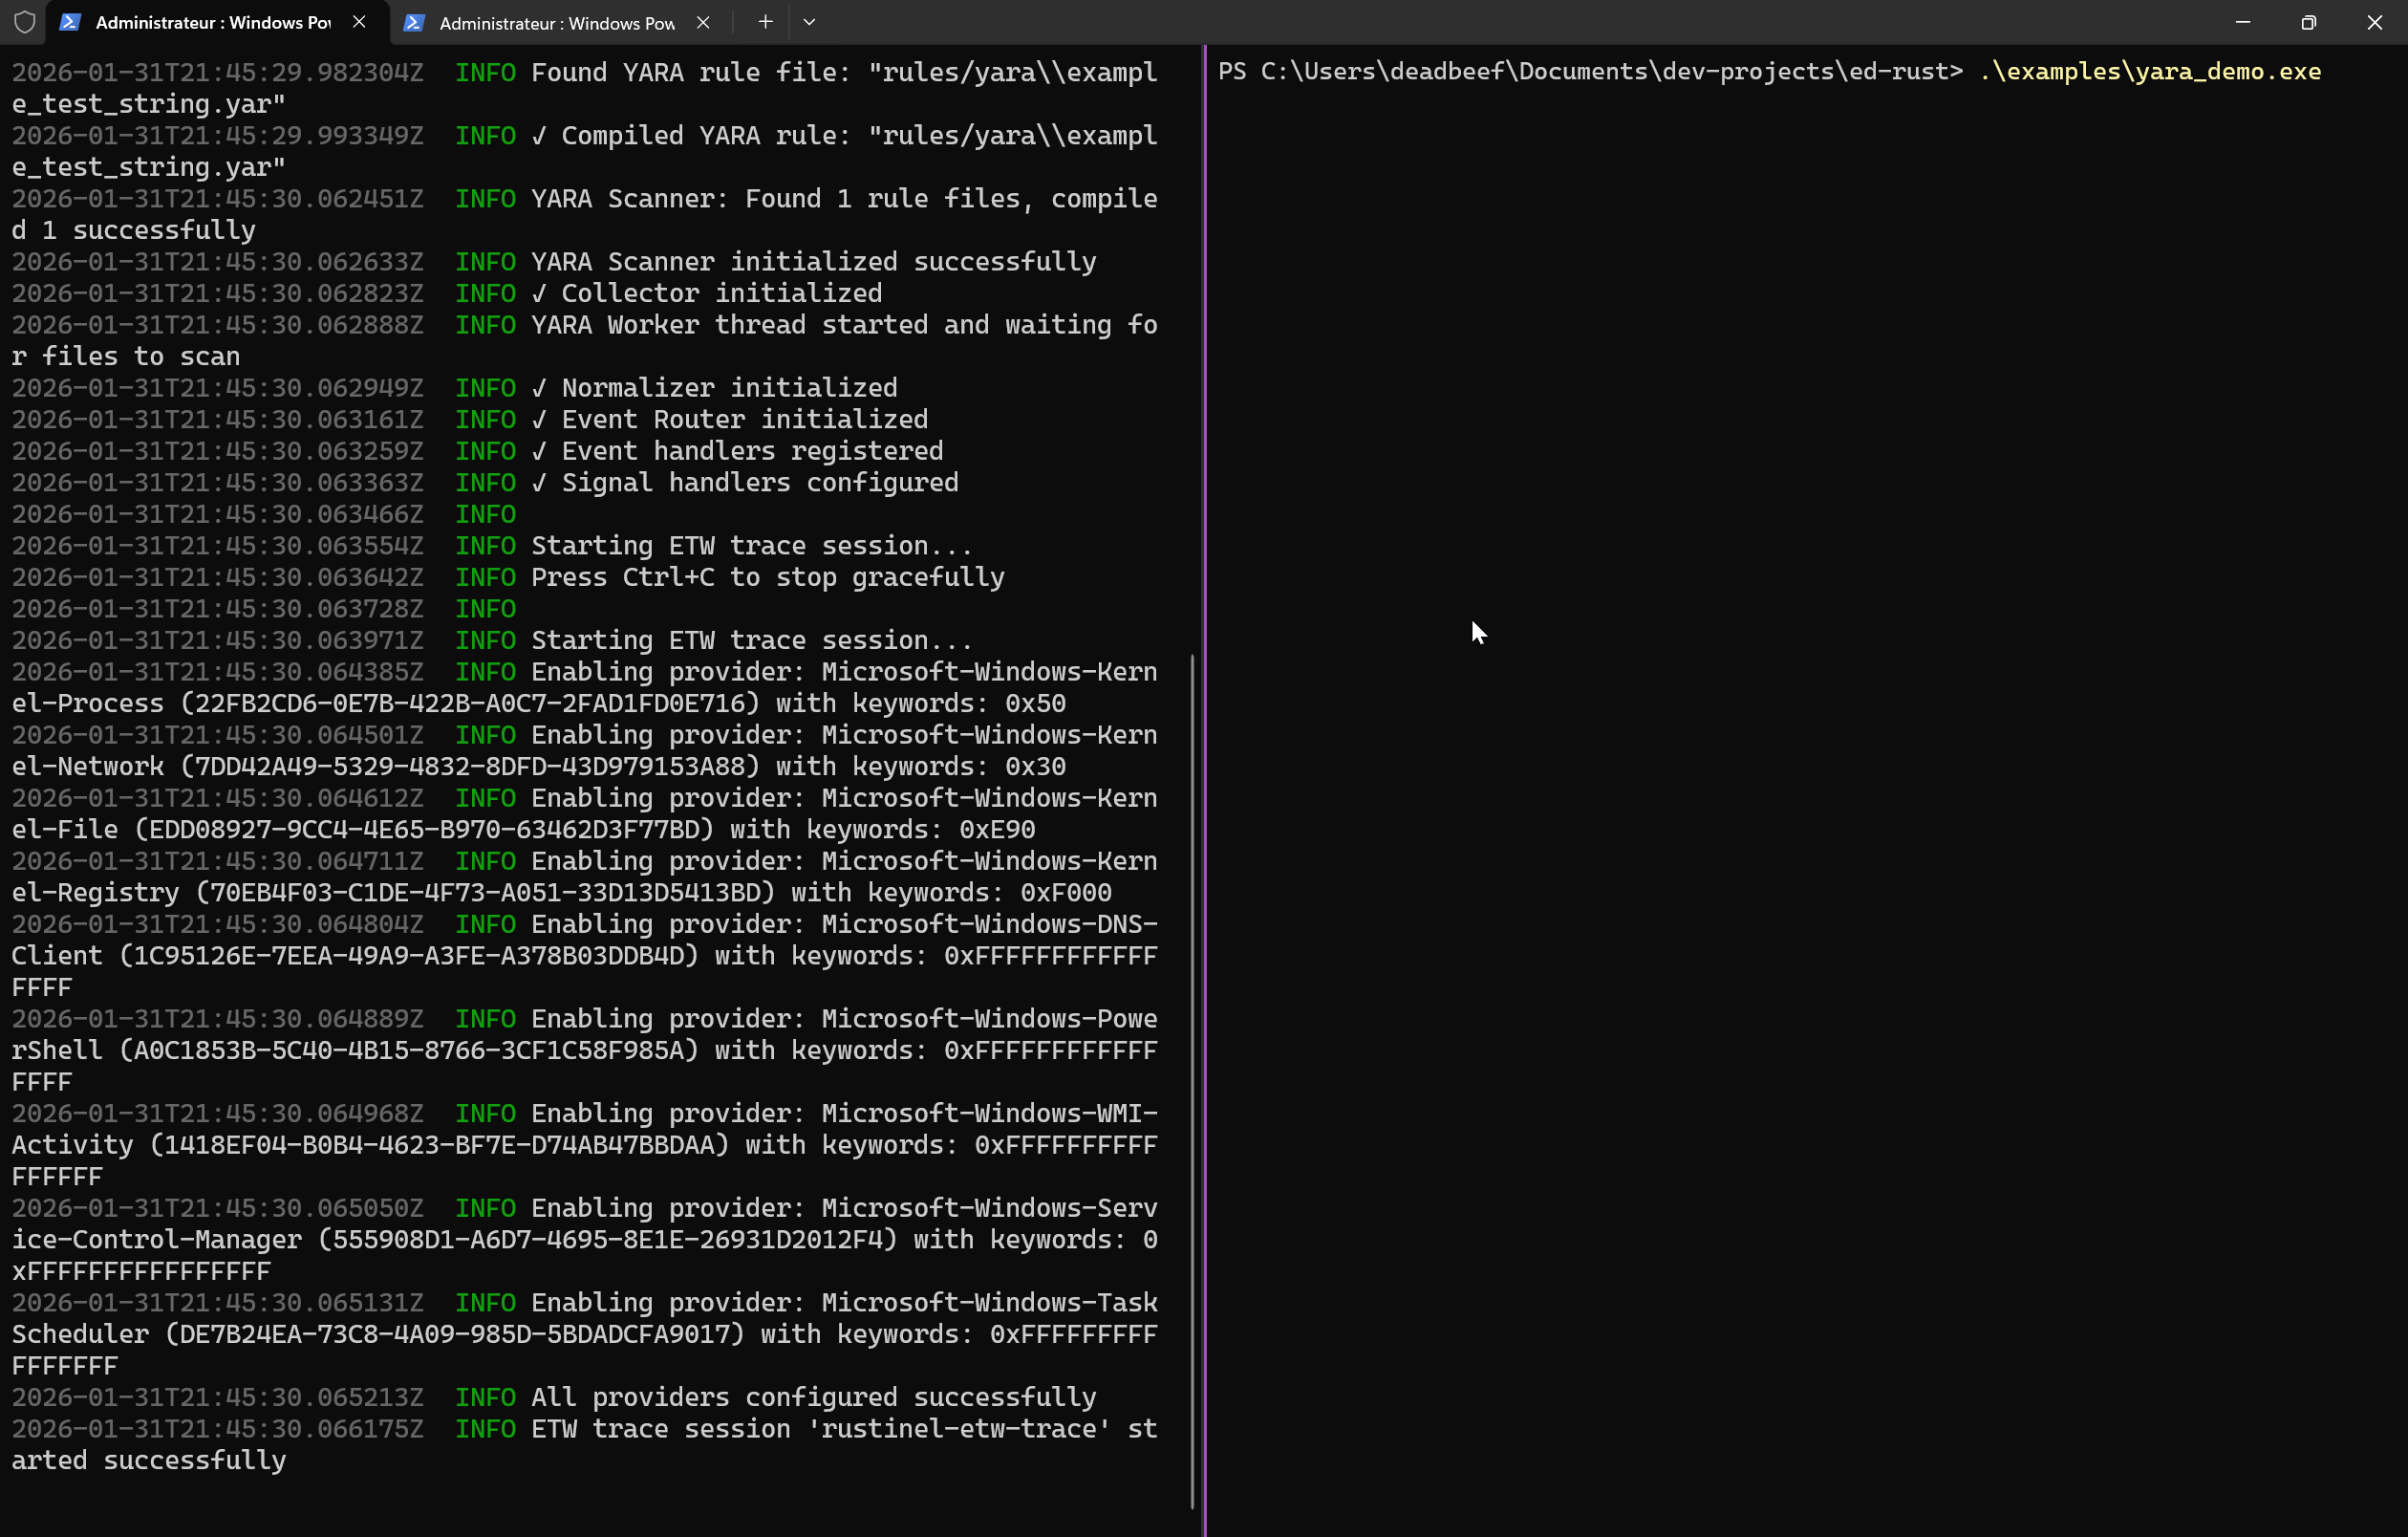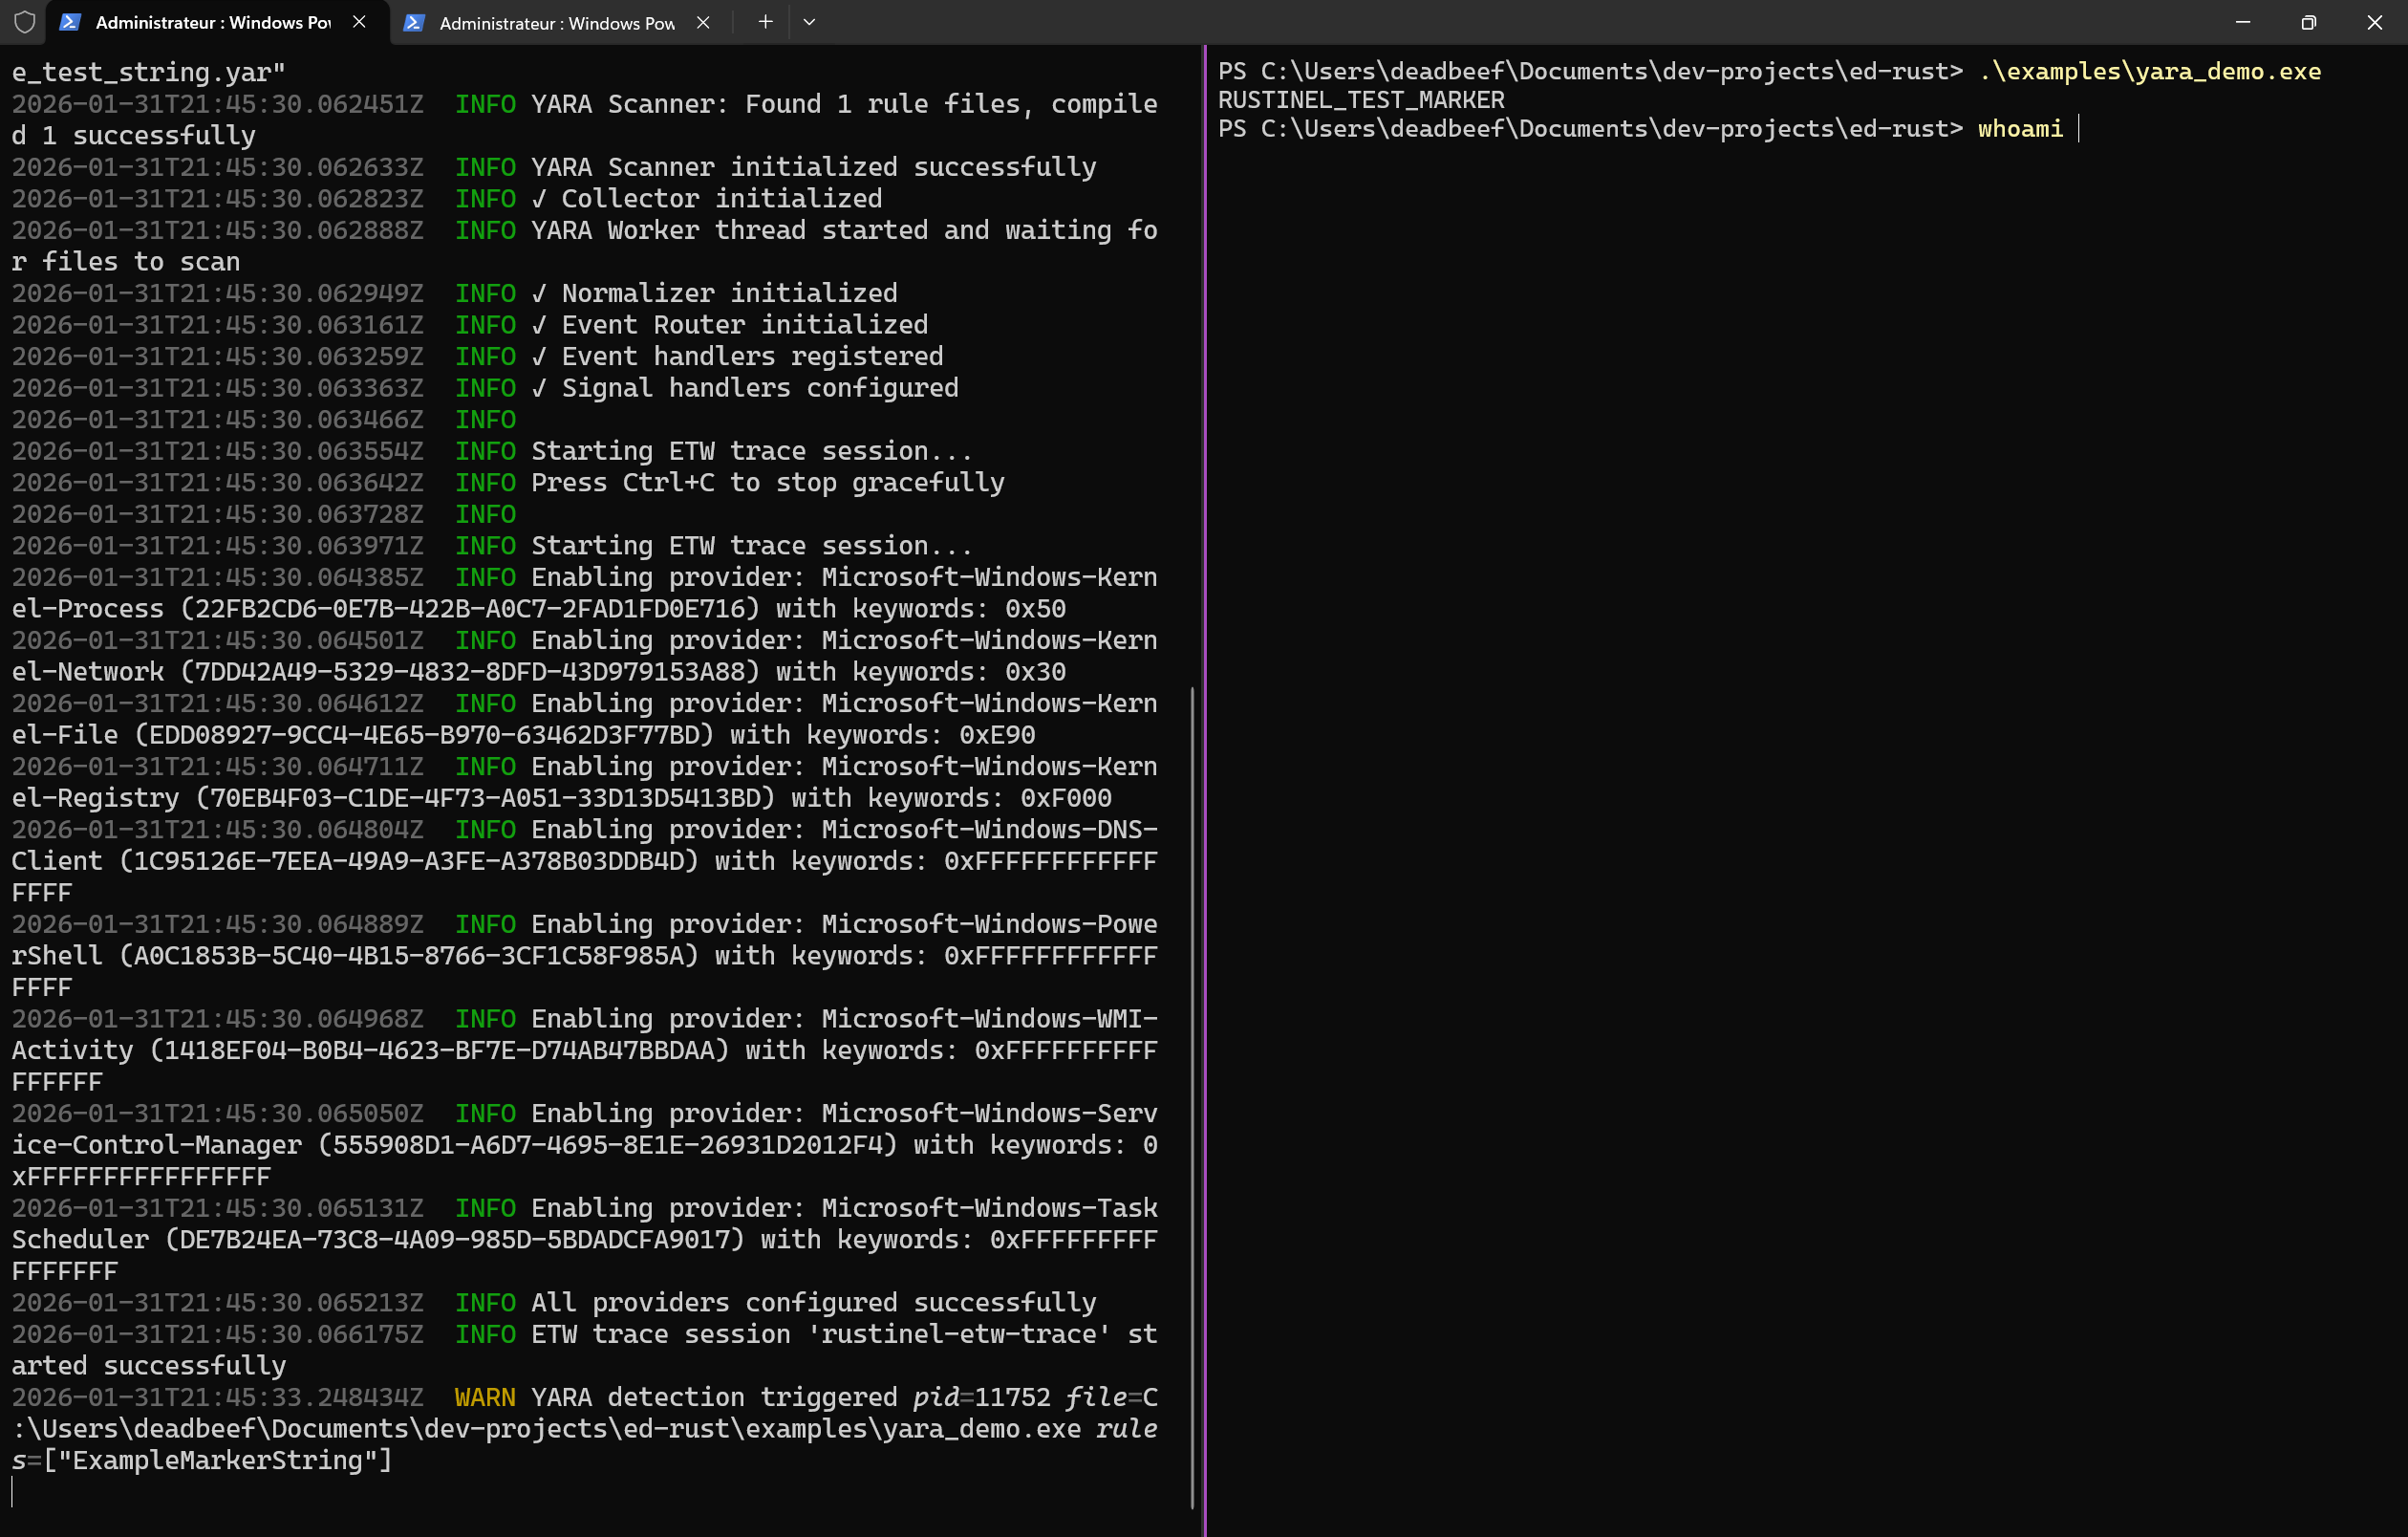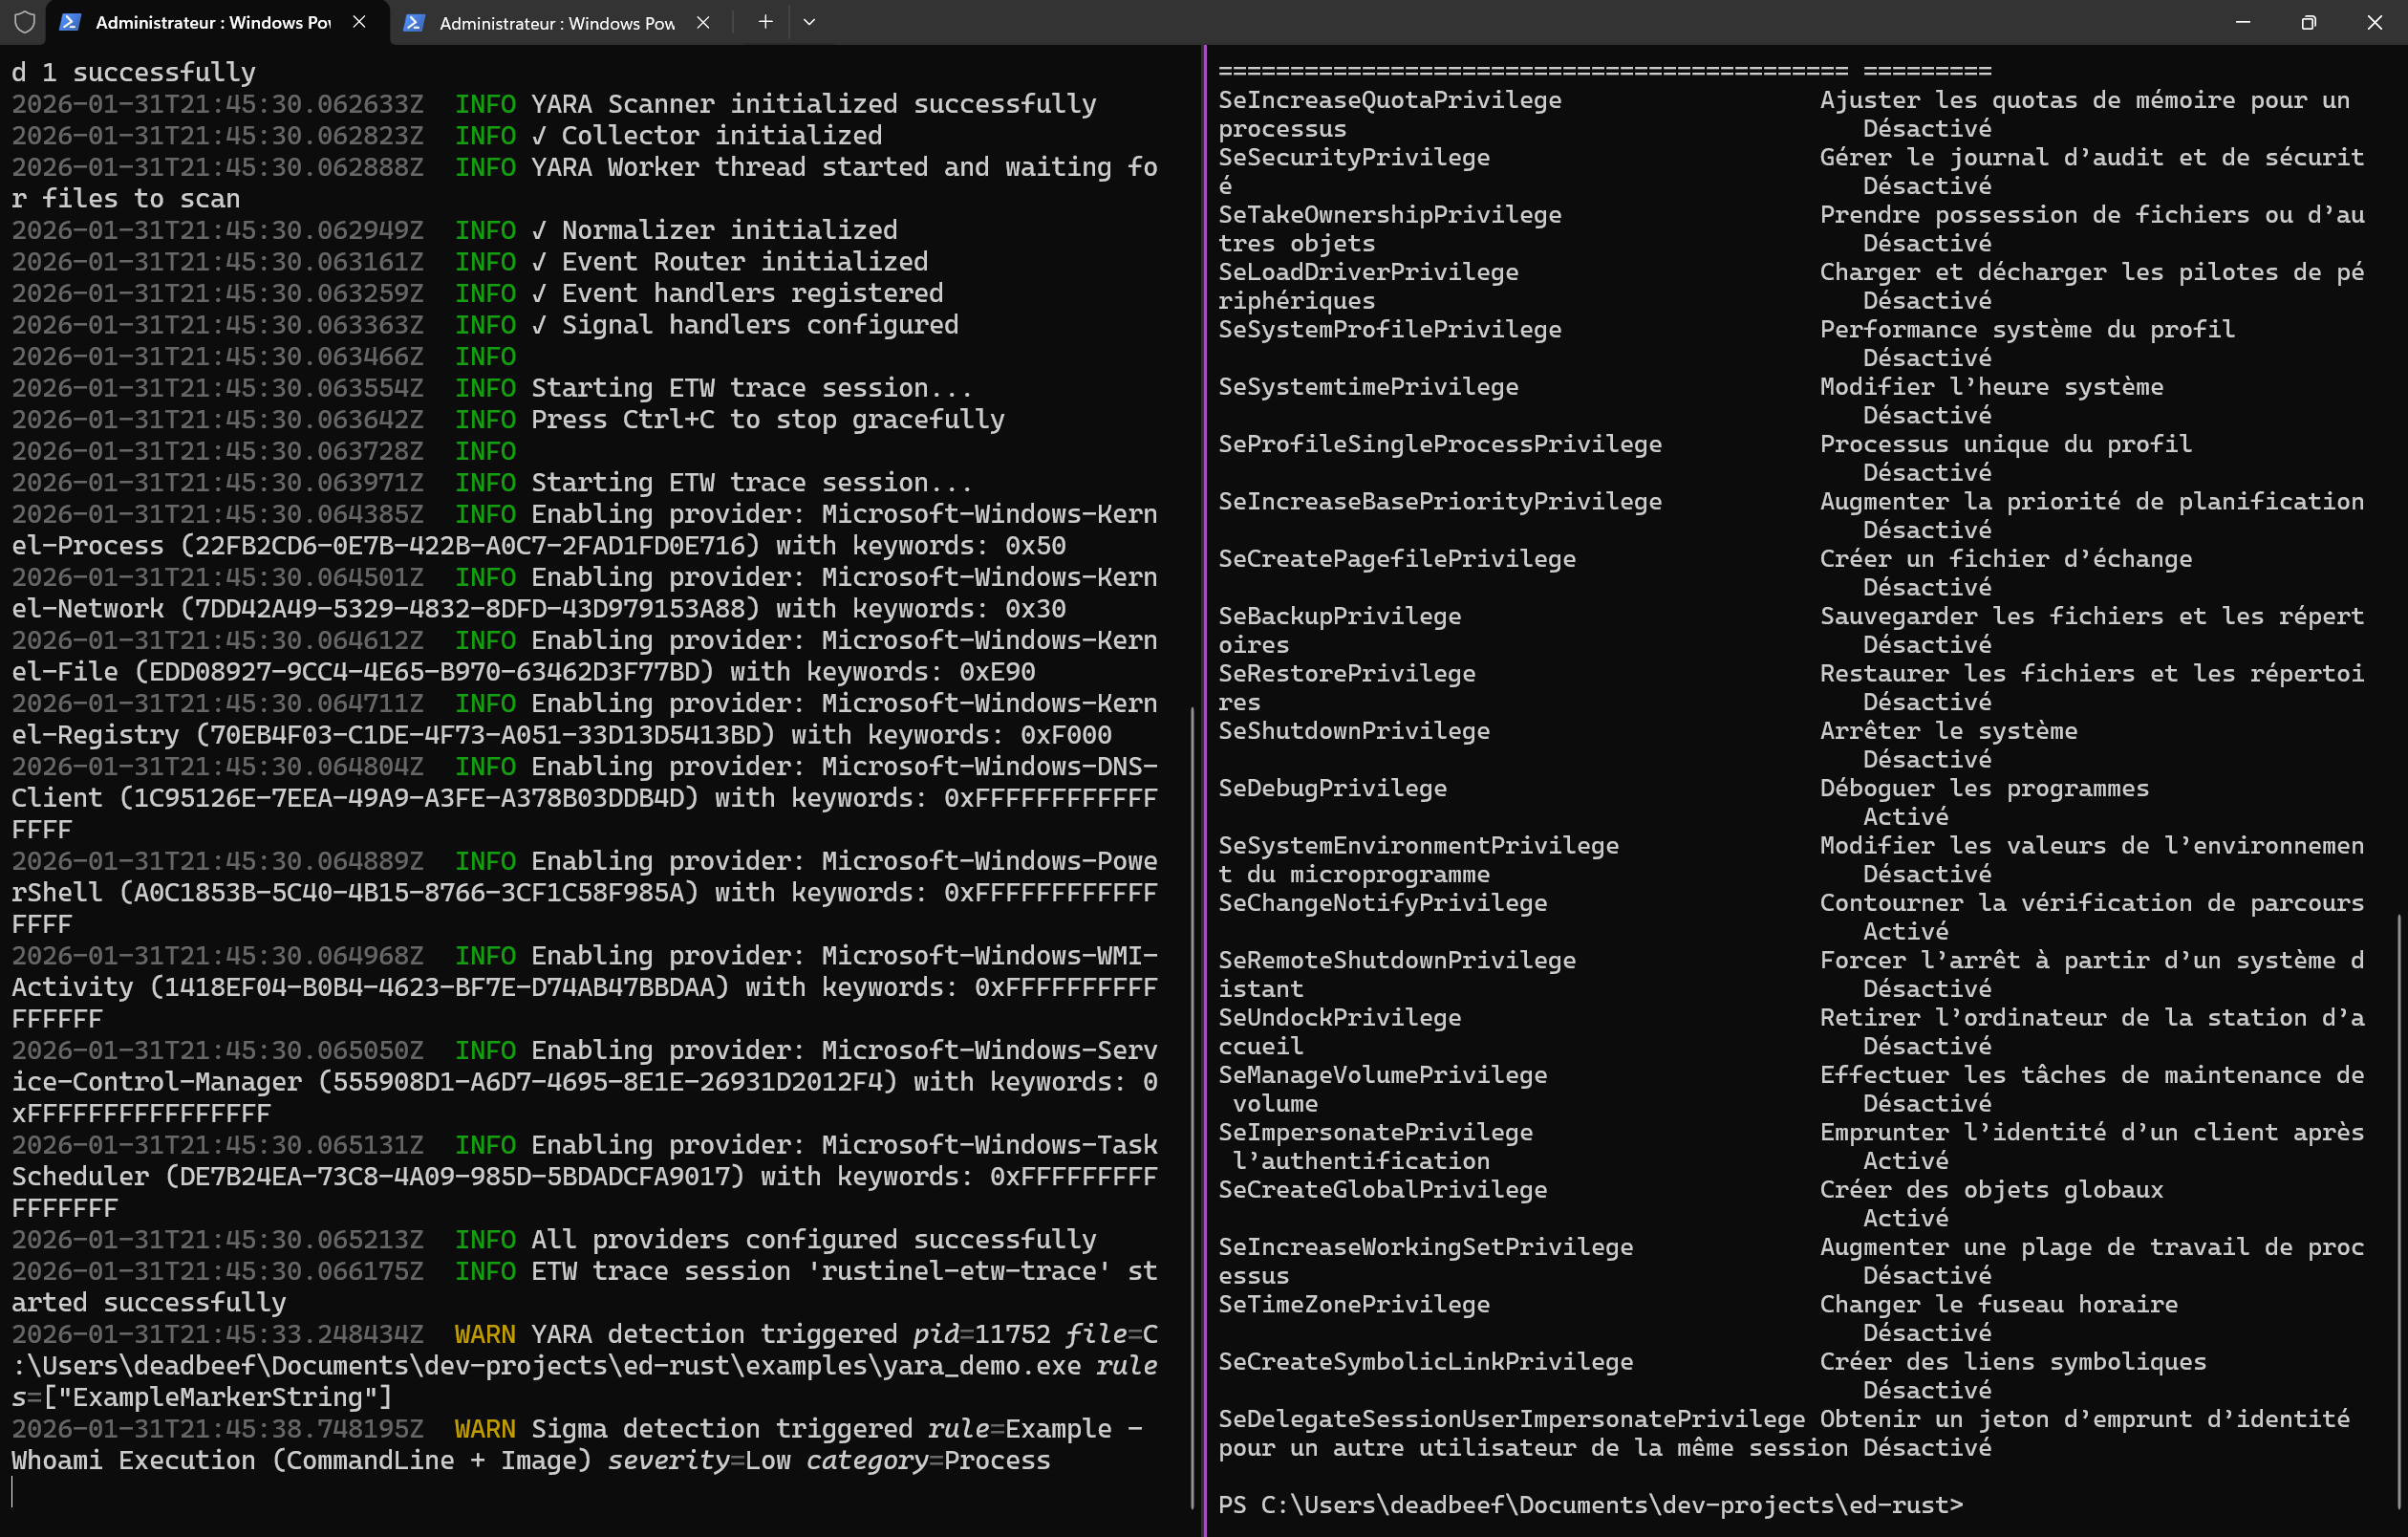
Rustinel demo

Why Rustinel?

  • Use Sigma and YARA rules. Sigma for behavior, YARA for executables and process memory, and IOC lists for hashes, IPs, domains, and paths.
  • Run on Windows, Linux, and macOS. One engine, one config format, and the same Sysmon-style field names everywhere. Coverage varies by platform.
  • Keep your data. The agent sends nothing home. Alerts are local ECS NDJSON files that Elastic, Splunk, or any log pipeline can ingest.
  • Test rules against recorded behavior. Capture activity once, then replay it on any machine as your rules change.
  • See the gaps. rustinel sigma doctor explains which rules can fire, while rustinel doctor reports runtime health and events dropped under load.

Quickstart

Install into a local rustinel folder, then start it.

Linux (kernel 5.8+):

curl -fsSL https://rustinel.io/install.sh | sh
cd rustinel && sudo ./rustinel run

Windows, in an elevated PowerShell:

irm https://rustinel.io/install.ps1 | iex
Set-Location rustinel; .\rustinel.exe run

macOS (experimental) needs Full Disk Access first, see macOS permissions:

curl -fsSL https://rustinel.io/install.sh | sh
cd rustinel && sudo ./rustinel run

Run whoami in another terminal. The demo rule fires and the alert lands in rustinel/logs/alerts.json.<date>.

To install it as a service with a real rules pack, stop it with Ctrl-C and run sudo ./rustinel setup --yes from the rustinel folder (.\rustinel.exe setup --yes on Windows). See Deploy on an endpoint.

Capture once, replay as your rules improve

sudo ./rustinel capture --output ~/captures/session.ndjson   # Ctrl-C when done
sudo chown -R "$USER" ~/captures
./rustinel replay ~/captures/session.ndjson
./rustinel replay ~/captures/session.ndjson --config candidate.toml

Replay needs no privileges and works across platforms: a Windows recording replays on Linux. See Test rules with replay.

Platform support

PlatformSensorsTelemetryStatus
Windows 10/11, Server 2016+ETW + Windows Event LogProcess, image load, network, file, registry, DNS, PowerShell, WMI, service, task, Security audit eventsStable
Linux 5.8+eBPFProcess, network, file, DNSStable
macOS 11+Endpoint Security + /dev/bpfProcess, file, network, DNSExperimental

Details: Platform coverage and Limitations.

Know the boundaries

Rustinel is built for endpoint monitoring, detection engineering, labs, and SIEM pipeline testing. It is not a replacement for a commercial EDR: it has no anti-tamper, no pre-execution blocking, and no management console. See the Security model.

Code signing policy

Free code signing for the Windows binary is provided by SignPath.io, certificate by SignPath Foundation. See the Code signing policy for roles and privacy.

Contribute

Bug reports, detection tests, and platform work are welcome. Tell us what you monitor and where you get stuck.

Contributing | Issues | Development guide | Roadmap

License

Apache 2.0.

Descargar herramienta

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 El kit de herramientas OSINT definitivo: grafo de investigación, puntuación de confianza, familias de alias, mapa, línea de tiempo e informes. 49 módulos, más de 400 sitios, sin necesidad de claves API.

    546
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicación de Ejecución con un Solo Toque GhostLock (CVE-2026-43499)

    477
  • 3

    ARTEX

    baarai/artex

    Plataforma de pruebas de penetración autónoma multiagente basada en LLM con agentes planificadores/trabajadores, grafos de activos y de exploración, registro de tráfico MITM y reevaluación de vulnerabilidades.

    377
  • 4

    redforge

    cybersecurity91/redforge

    Kit de herramientas de red team del lado del navegador con 102 herramientas offline para reconocimiento, generación de payloads, ataques de credenciales, criptografía, codificación y elaboración de informes de compromiso.

    324
  • 5

    estorides

    grisuno/estorides

    Agrega más de 99 fuentes OSINT gratuitas en paralelo, resuelve entidades en un grafo de conocimiento y exporta STIX 2.1, MISP o GraphML con análisis asistido por LLM.

    269
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    El sistema de acción para la ciberseguridad nativa de IA—donde la intención se convierte en ejecución gobernada, la evidencia se convierte en memoria operativa y cada operación mejora la siguiente.

    252

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →