
Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
ssh-audit — SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc) | Kitploit
Herramientas/GitHubGitHub/jtesta/ssh-audit
Vulnerability ScannersNetwork MappingPort ScanningVulnerability AnalysisConfiguration AuditingInformation GatheringNetwork SecurityCryptographyPenetration TestingTop en Network Mapping #13Top en Port Scanning #16
GitHubjtesta/ssh-audit

ssh-audit

SSH server & client security auditing (banner, key exchange, encryption, mac, compression, compatibility, security, etc)

Ver Repositorio
4.3k23344hace 7 díasRevisado por Kitploit

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →
Compartir
Contenido no disponible en el idioma solicitado. Mostrando versión en inglés.

ssh-audit

License Build Status PRs Welcome

PyPI Downloads Homebrew Downloads Docker Pulls Snap Downloads

Github Sponsors

ssh-audit is a tool for ssh server & client configuration auditing.

jtesta/ssh-audit (v2.0+) is the updated and maintained version of ssh-audit forked from arthepsy/ssh-audit (v1.x) due to inactivity.

  • Features
  • Usage
  • Screenshots
    • Server Standard Audit Example
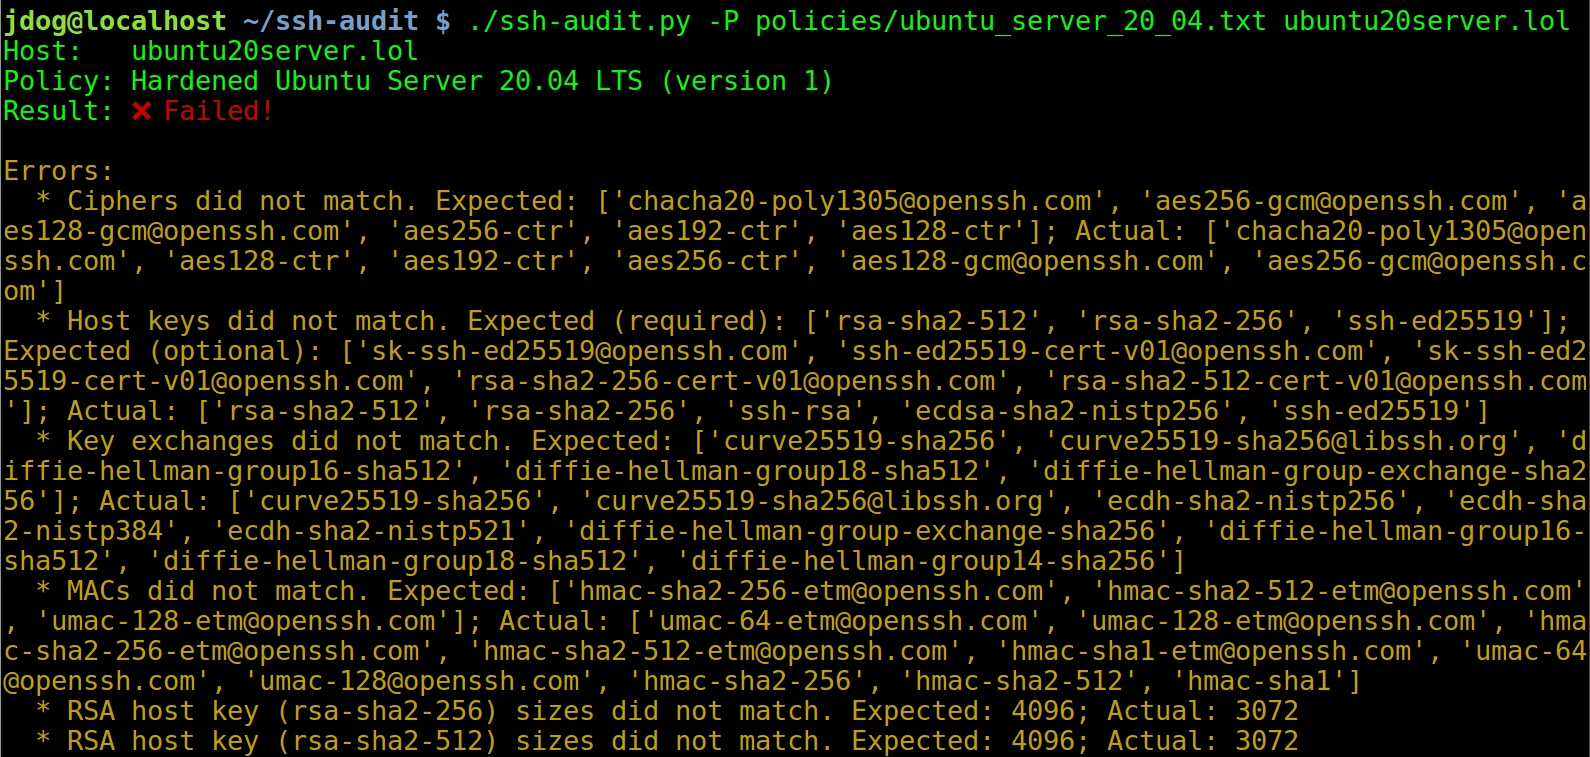
    • Server Policy Audit Example
    • Client Standard Audit Example
  • Hardening Guides
  • Pre-Built Packages
  • Web Front-End
  • ChangeLog

Features

  • analyze SSH both server and client configuration;
  • grab banner, recognize device or software and operating system, detect compression;
  • gather key-exchange, host-key, encryption and message authentication code algorithms;
  • output algorithm security information (available since, removed/disabled, unsafe/weak/legacy, etc);
  • output algorithm recommendations (append or remove based on recognized software version);
  • analyze SSH version compatibility based on algorithm information;
  • historical information from OpenSSH, Dropbear SSH and libssh;
  • policy scans to ensure adherence to a hardened/standard configuration;
  • runs on Linux and Windows;
  • supports Python 3.10 - 3.14;
  • no dependencies

Usage

usage: ssh-audit.py [-h] [-4] [-6] [-b] [-c] [-d]
                    [-g <min1:pref1:max1[,min2:pref2:max2,...]> / <x-y[:step]>]
                    [-j] [-l {info,warn,fail}] [-L] [-M custom_policy.txt]
                    [-m] [-n] [-P "Built-In Policy Name" / custom_policy.txt]
                    [-p N] [-T targets.txt] [-t N] [-v]
                    [--conn-rate-test N[:max_rate]] [--dheat N[:kex[:e_len]]]
                    [--get-hardening-guide platform] [--list-hardening-guides]
                    [--lookup alg1[,alg2,...]] [--skip-rate-test]
                    [--socks5 host:port] [--threads N]
                    [host]

# ssh-audit.py v3.4.1-dev, https://github.com/jtesta/ssh-audit

positional arguments:
  host                  target hostname or IPv4/IPv6 address
Descargar herramienta