 fr0gger/iatelligence
IATelligence es un script de Python que extrae el IAT de un archivo PE y solicita a GPT más información sobre la API y la matriz ATT&CK relacionada

IATelligence es un script de Python que extrae la Tabla de Direcciones de Importación (IAT) de un archivo PE y utiliza el modelo GPT-3 de OpenAI para proporcionar detalles sobre cada API de Windows importada por el archivo. El script también busca técnicas relacionadas de MITRE ATT&CK y explica cómo los atacantes podrían utilizar potencialmente la API.
También muestra los hashes del archivo y estima el costo de las solicitudes a GPT-3. IATelligence es una prueba de concepto para usar GPT-3 en el análisis de malware y evaluar rápidamente el comportamiento de un malware basándose en su IAT.
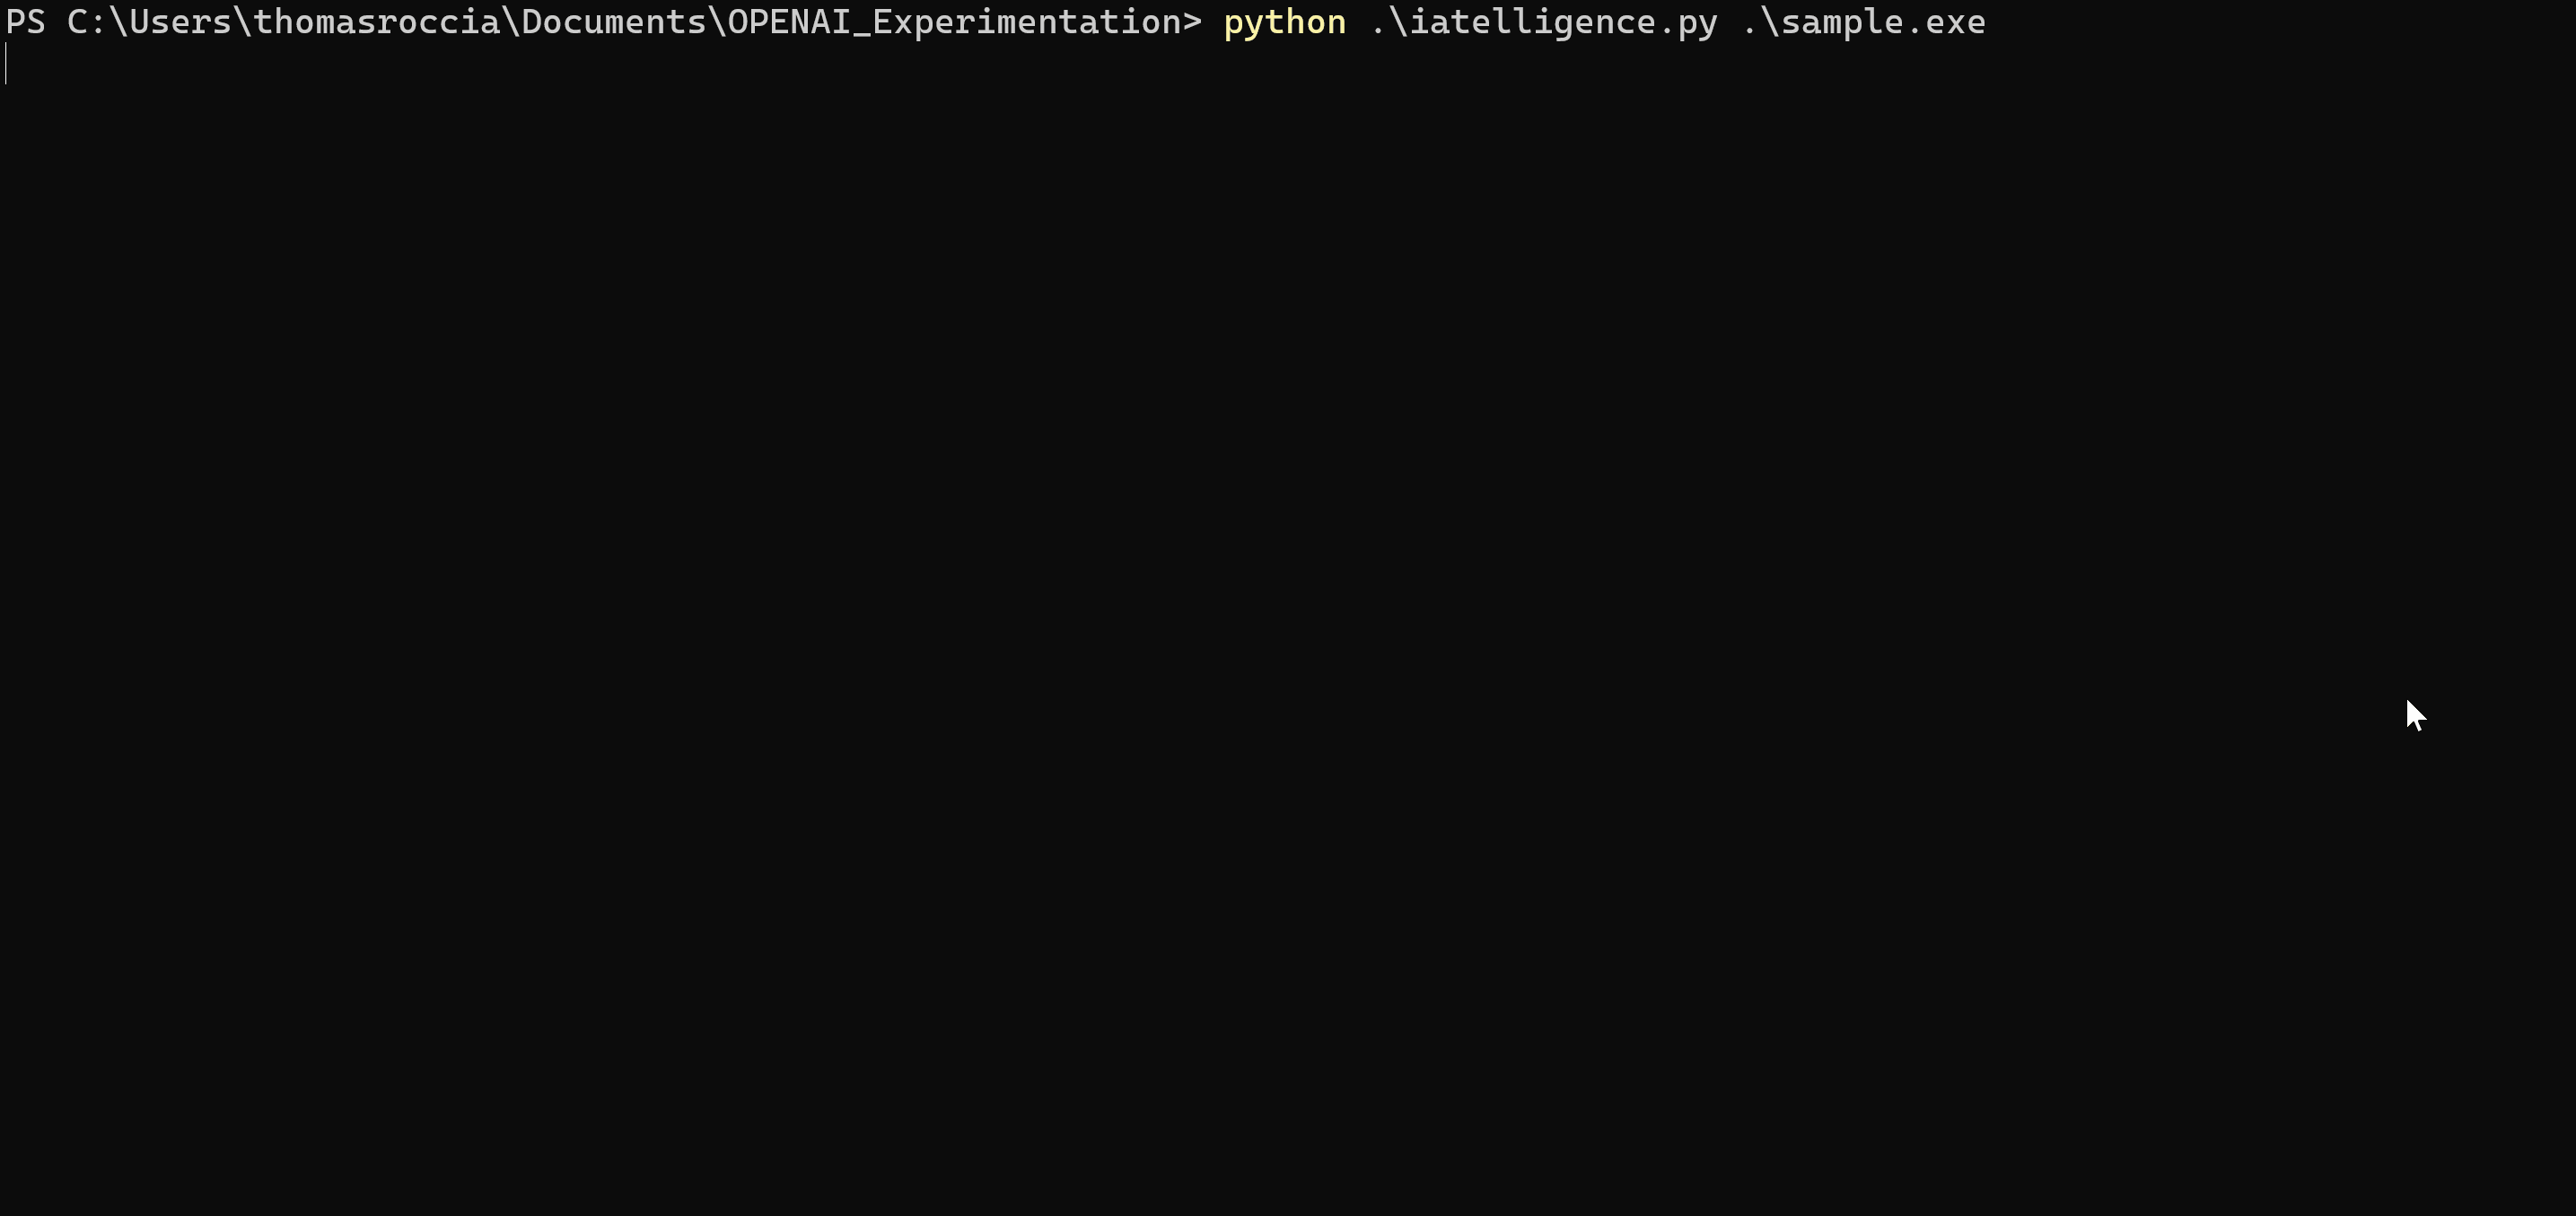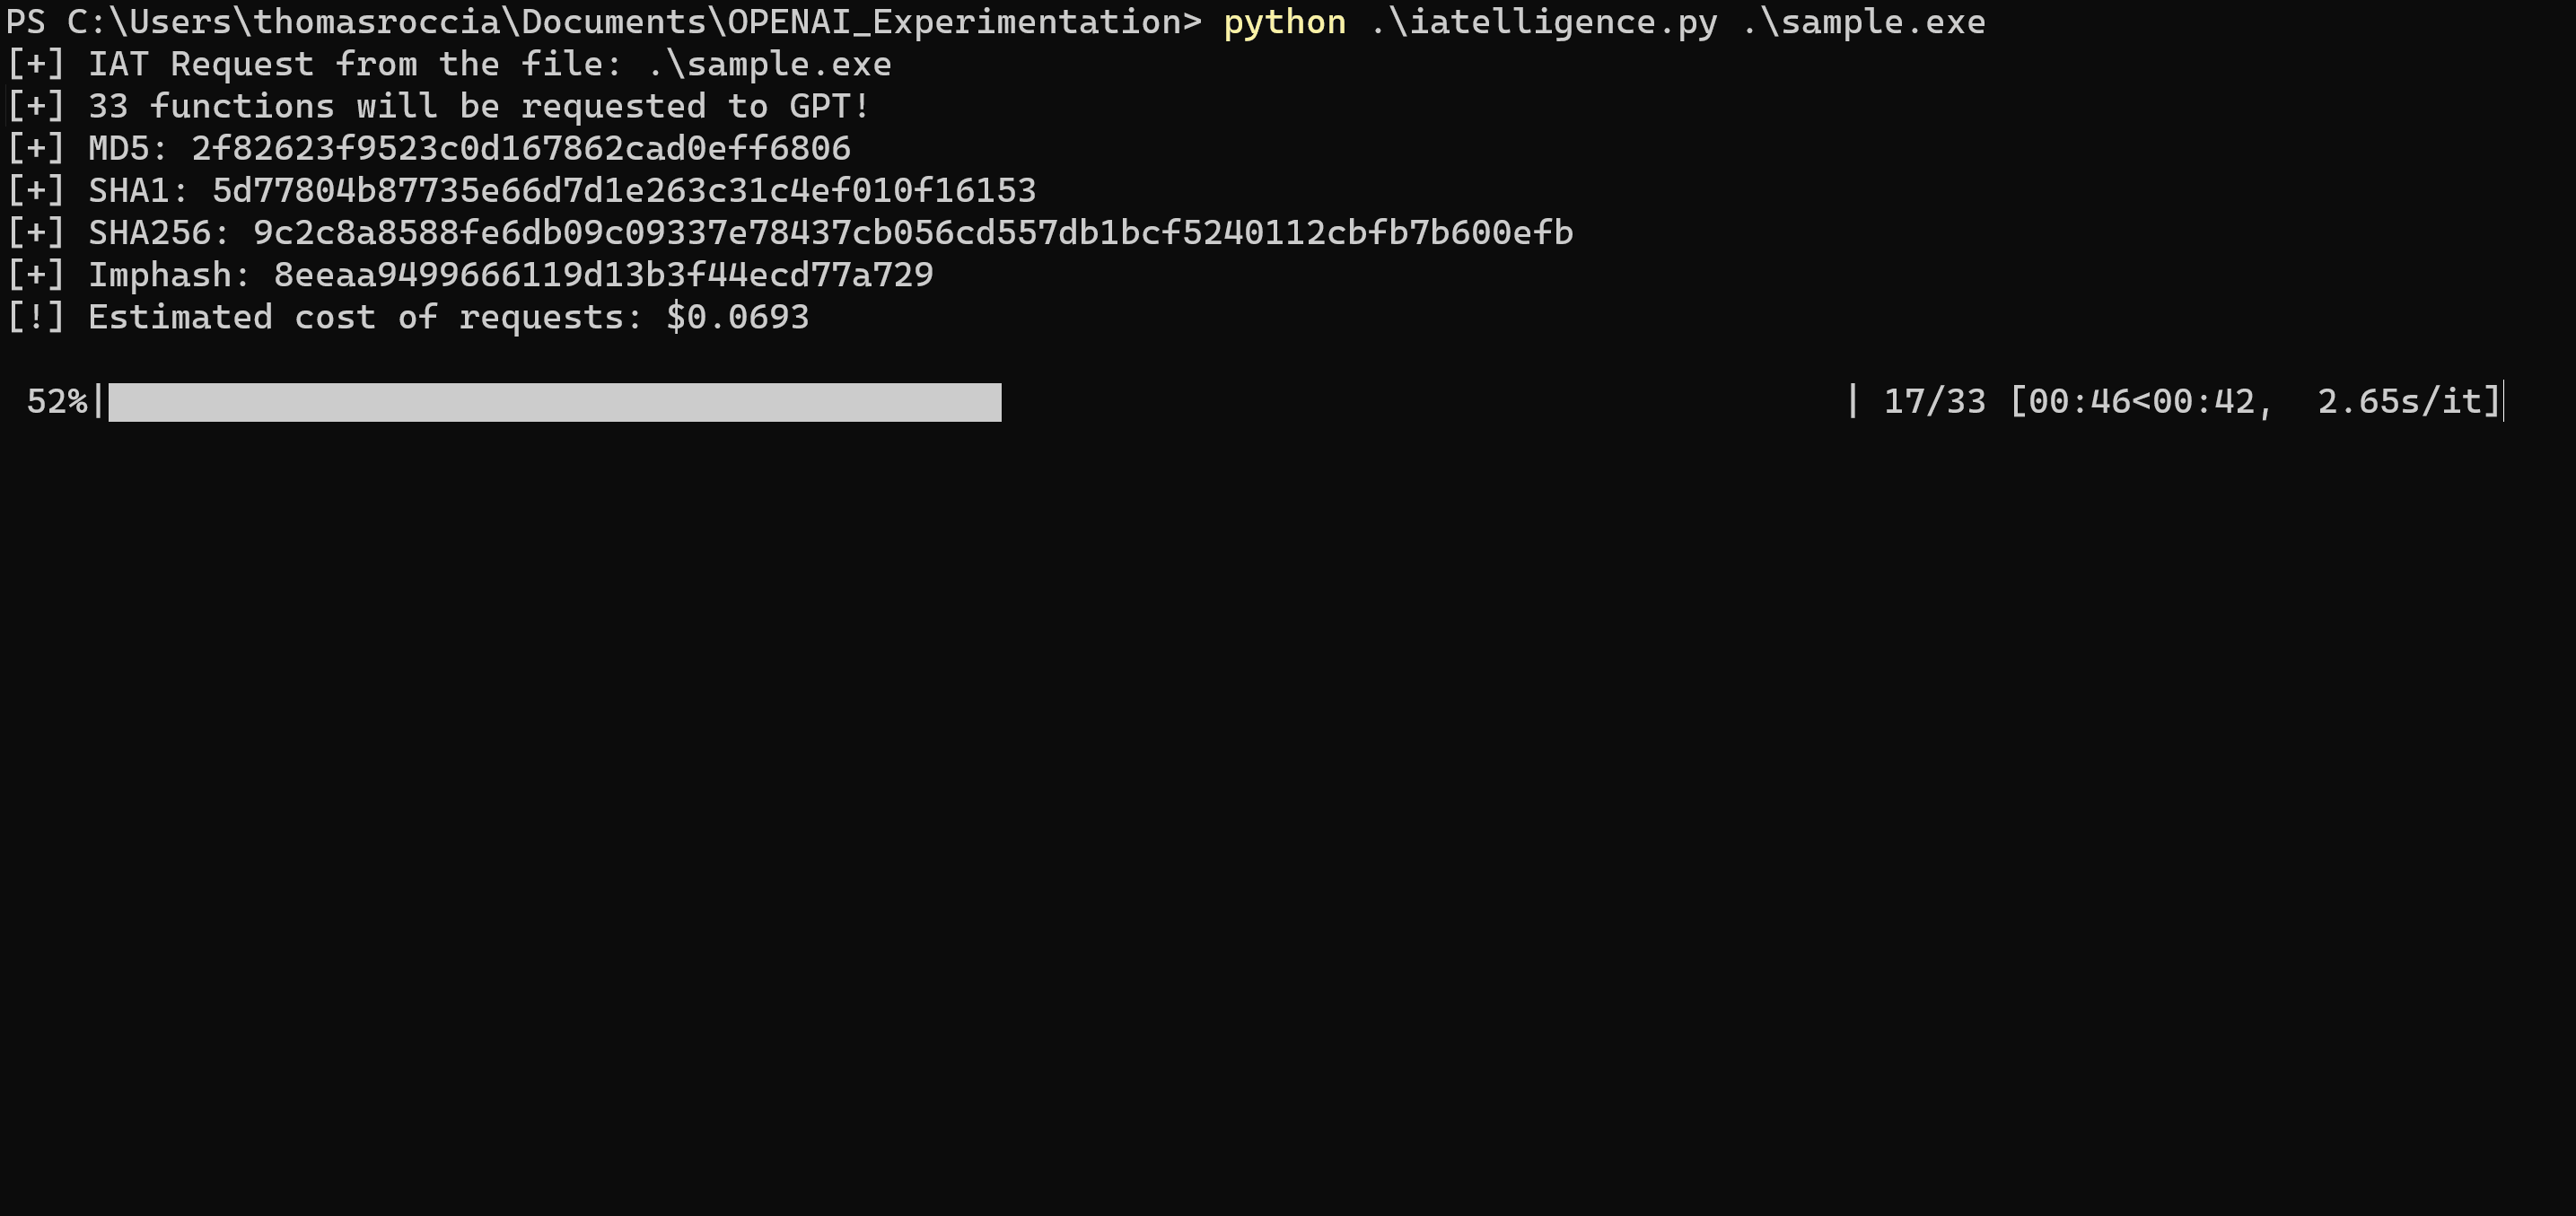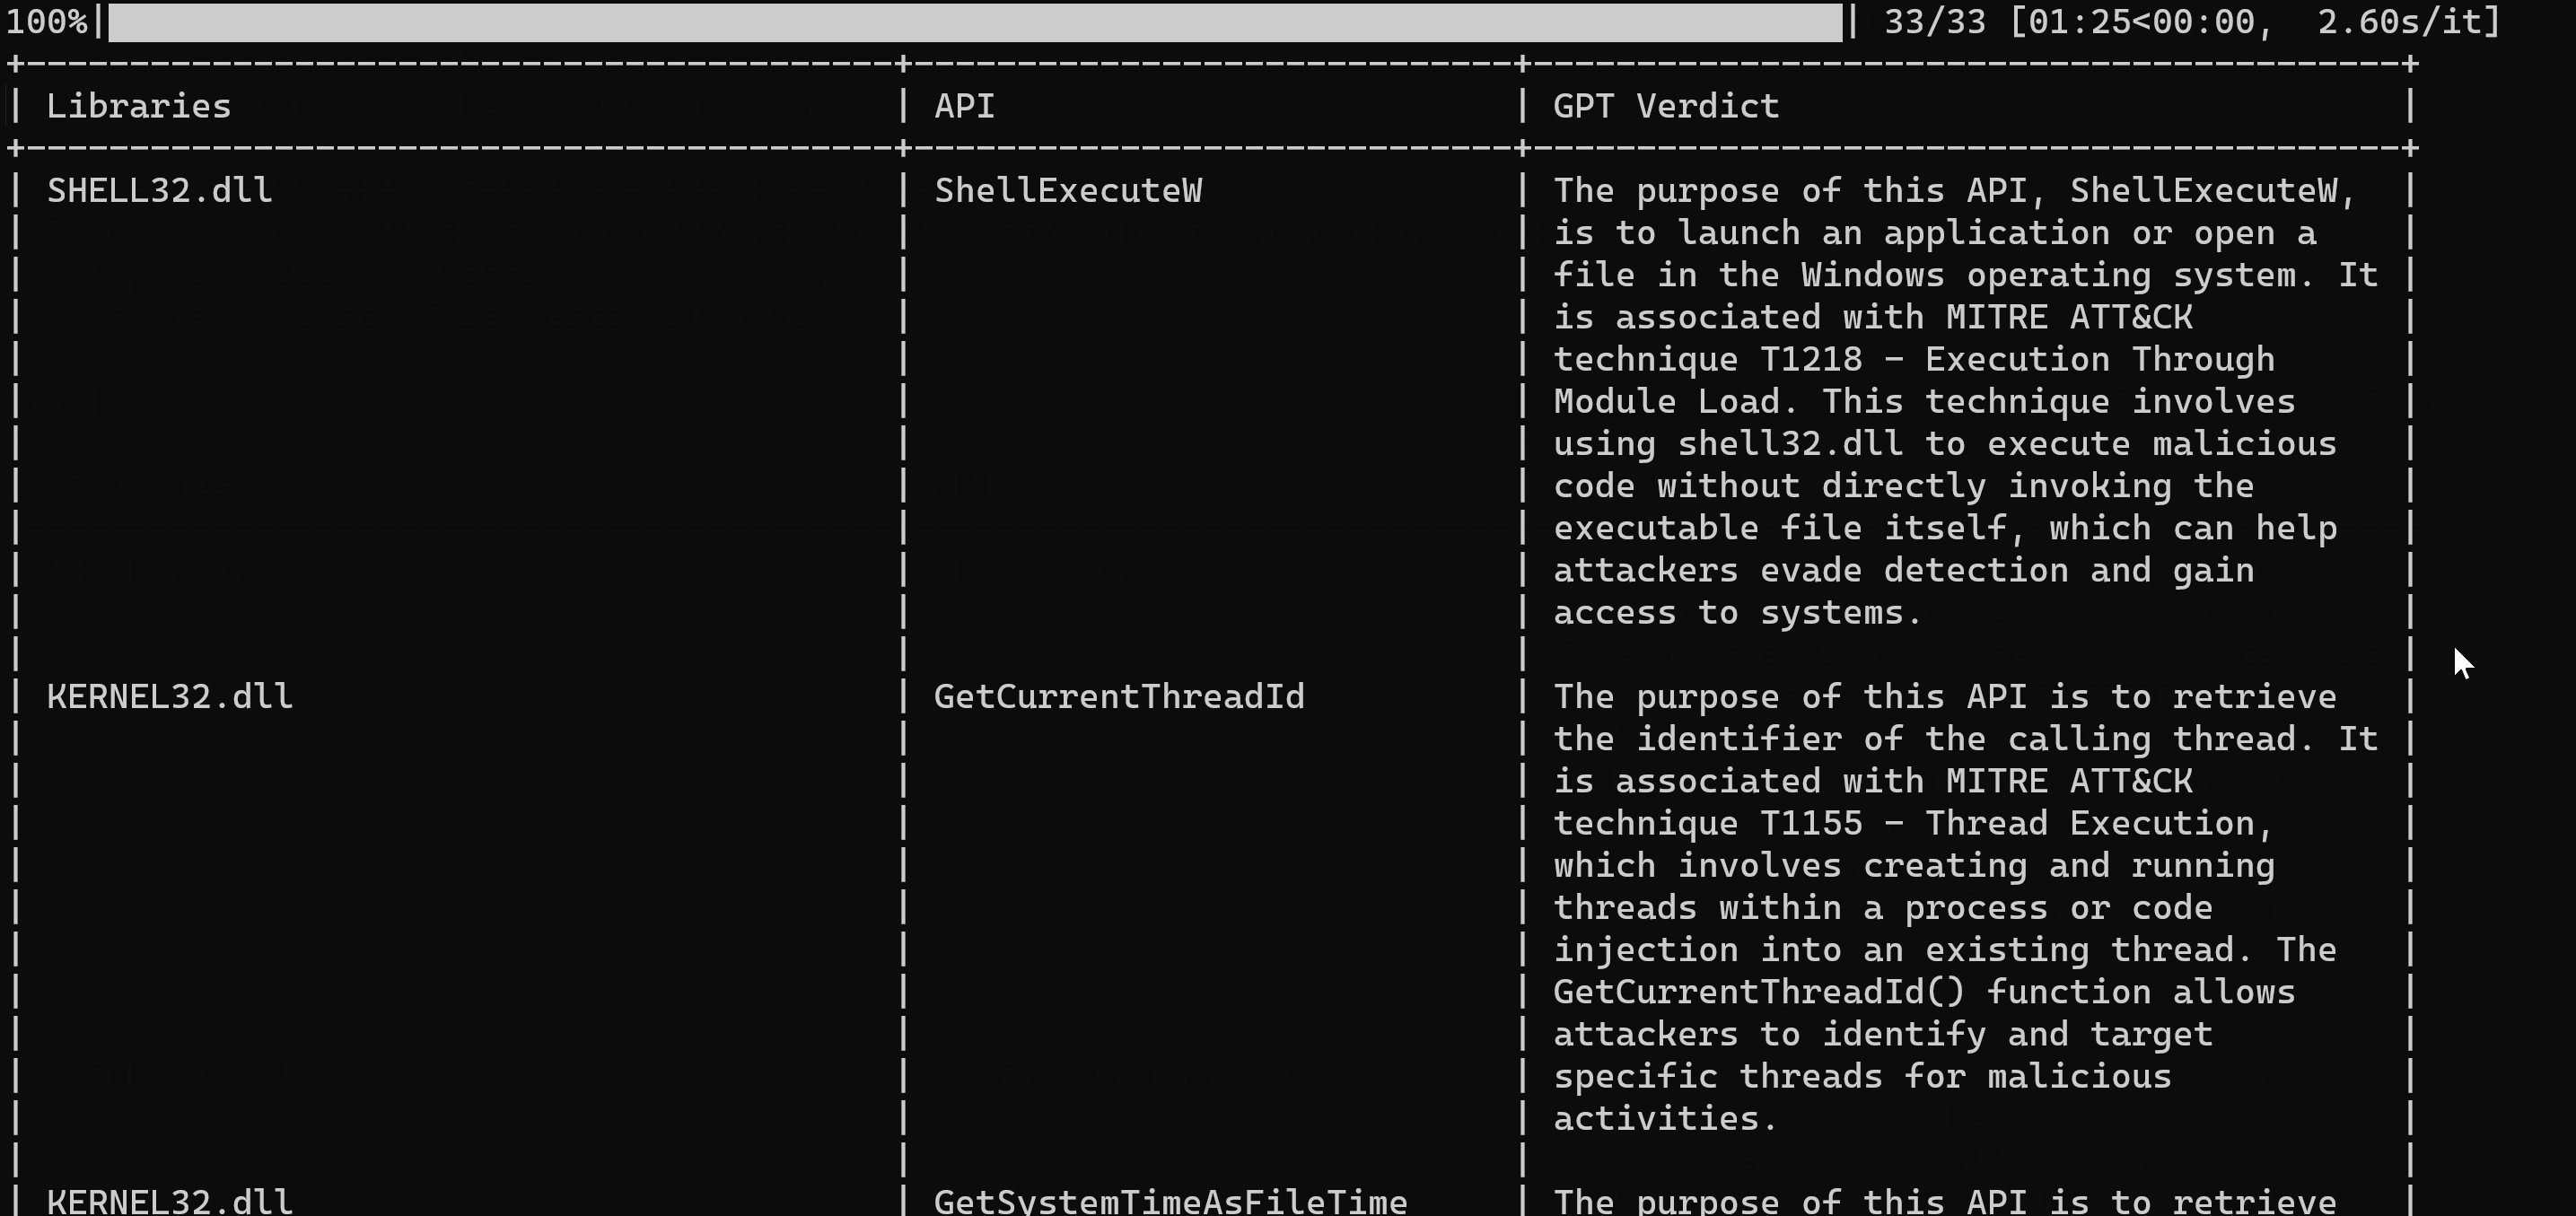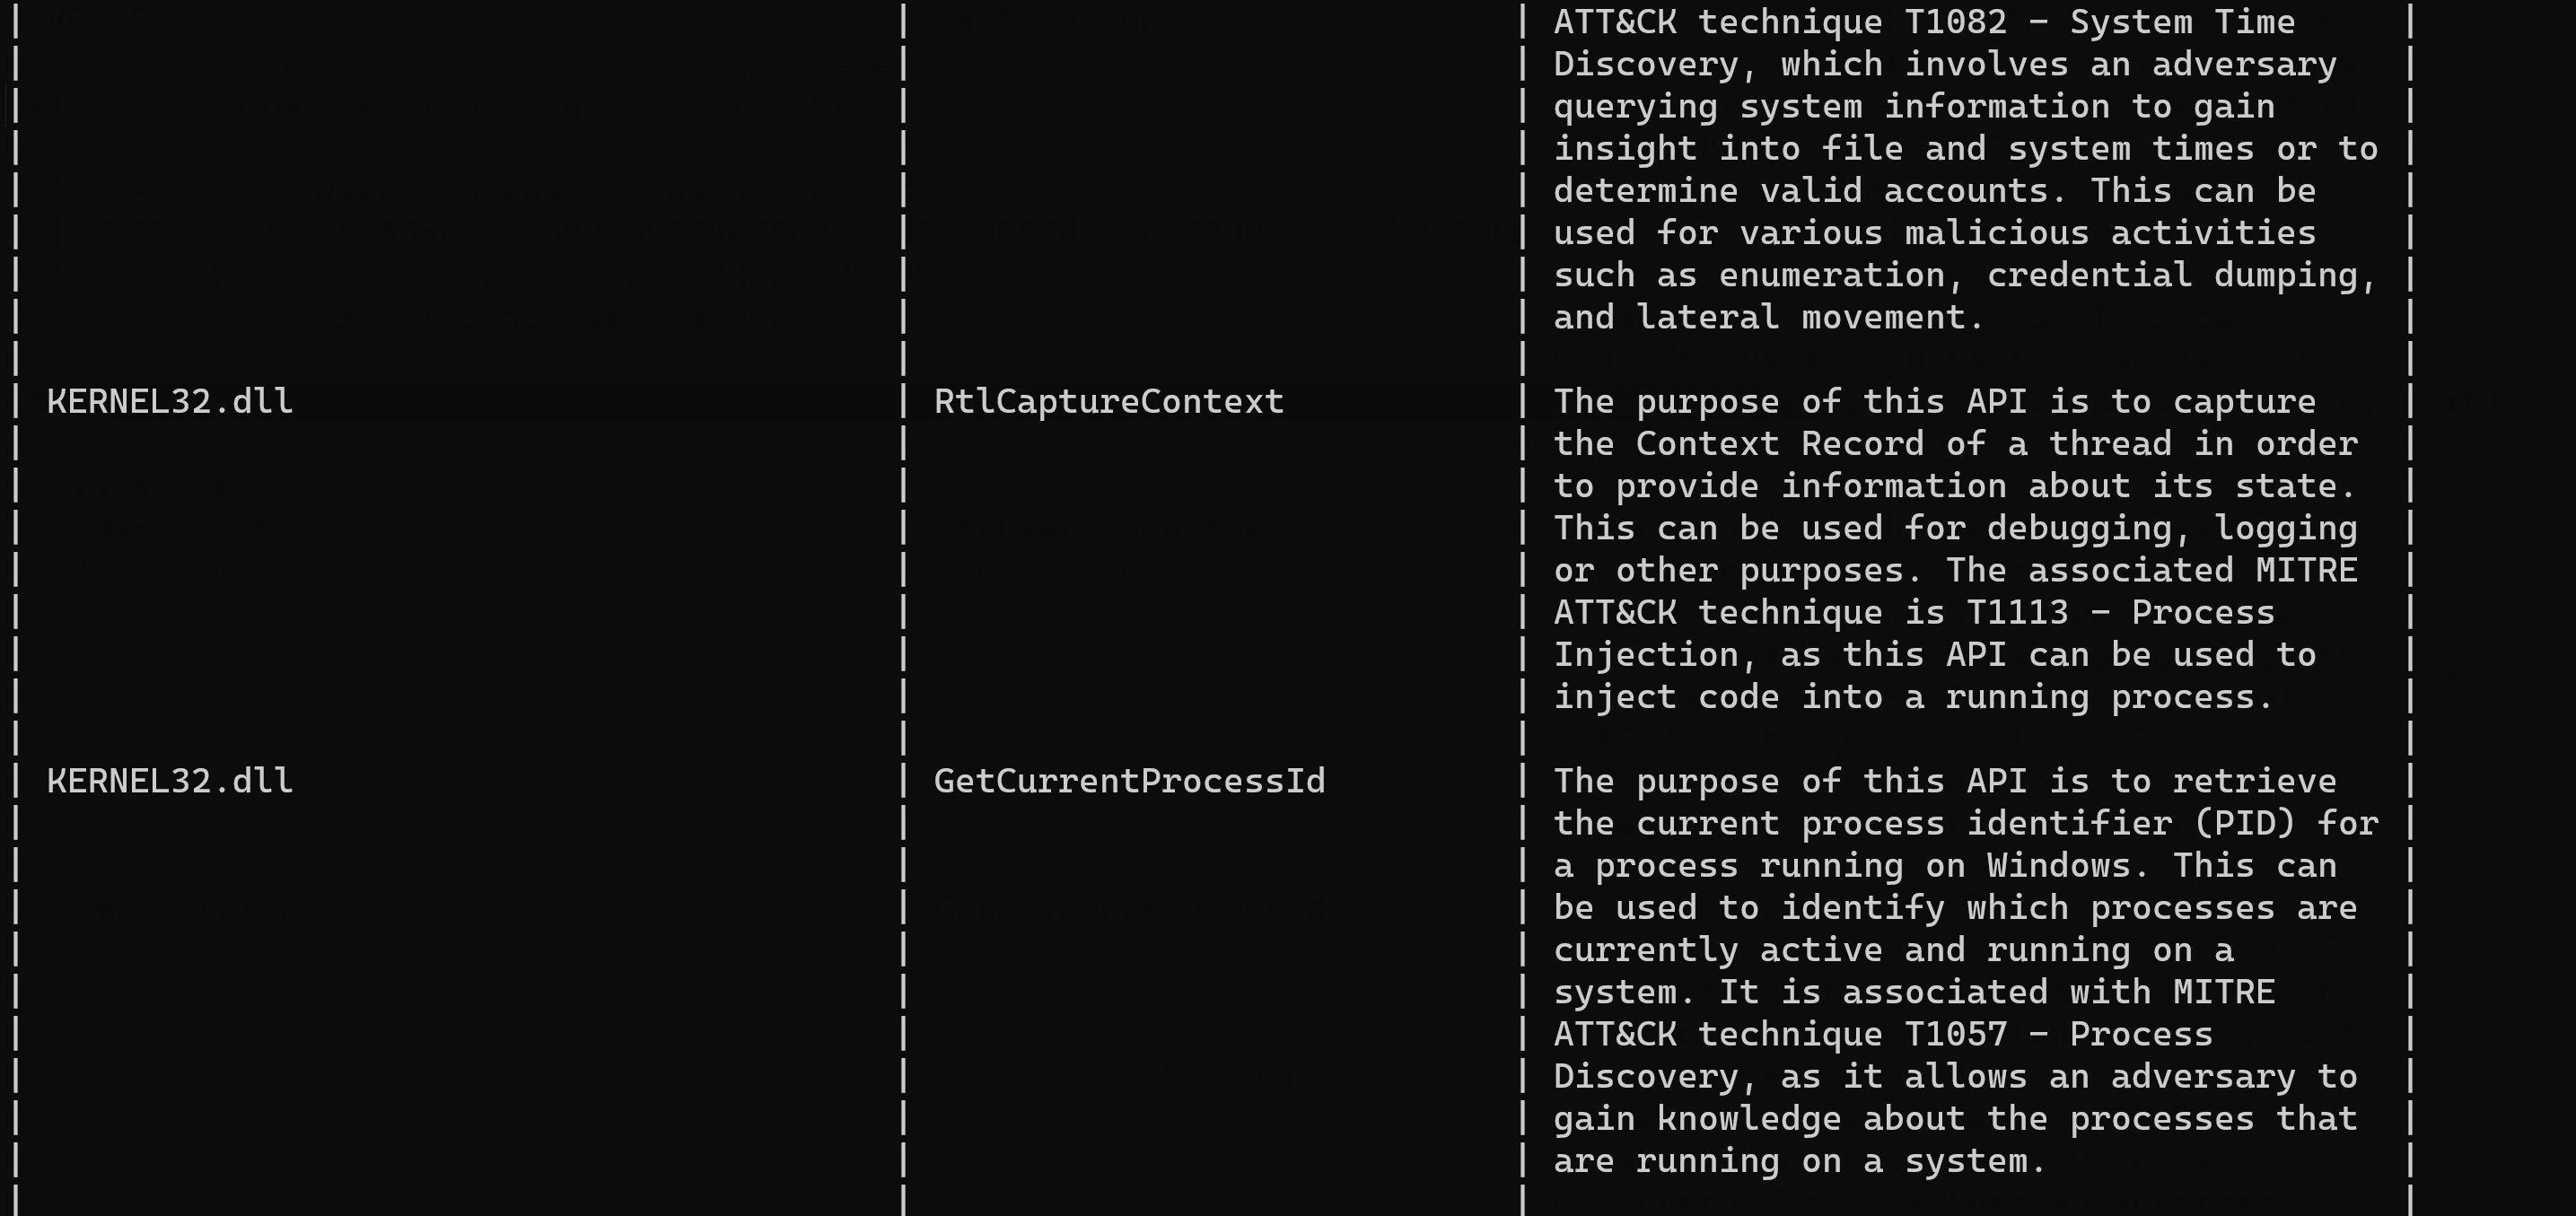
A continuación se muestra un ejemplo rápido del resultado que obtendrás. Ten en cuenta que la solicitud puede tardar más dependiendo del tamaño de la IAT.
Para ejecutar esta herramienta necesitarás acceso a la API de OpenAI; luego tendrás que modificar el script para añadir tu propia API.
# Authenticate with the OpenAI API
openai.api_key = ""
También necesitarás instalar los requisitos.
pip install -r requirements.txt
Para ejecutar la herramienta, simplemente especifica un archivo PE como argumento del script.
python iatelligence.py sample.exe
El script también calculará los hashes, así como el costo estimado de la solicitud.
[+] IAT Request from the file: .\sample.exe
[+] 33 functions will be requested to GPT!
[+] MD5: 2f82623f9523c0d167862cad0eff6806
[+] SHA1: 5d77804b87735e66d7d1e263c31c4ef010f16153
[+] SHA256: 9c2c8a8588fe6db09c09337e78437cb056cd557db1bcf5240112cbfb7b600efb
[+] Imphash: 8eeaa9499666119d13b3f44ecd77a729
[!] Estimated cost of requests: $0.0693
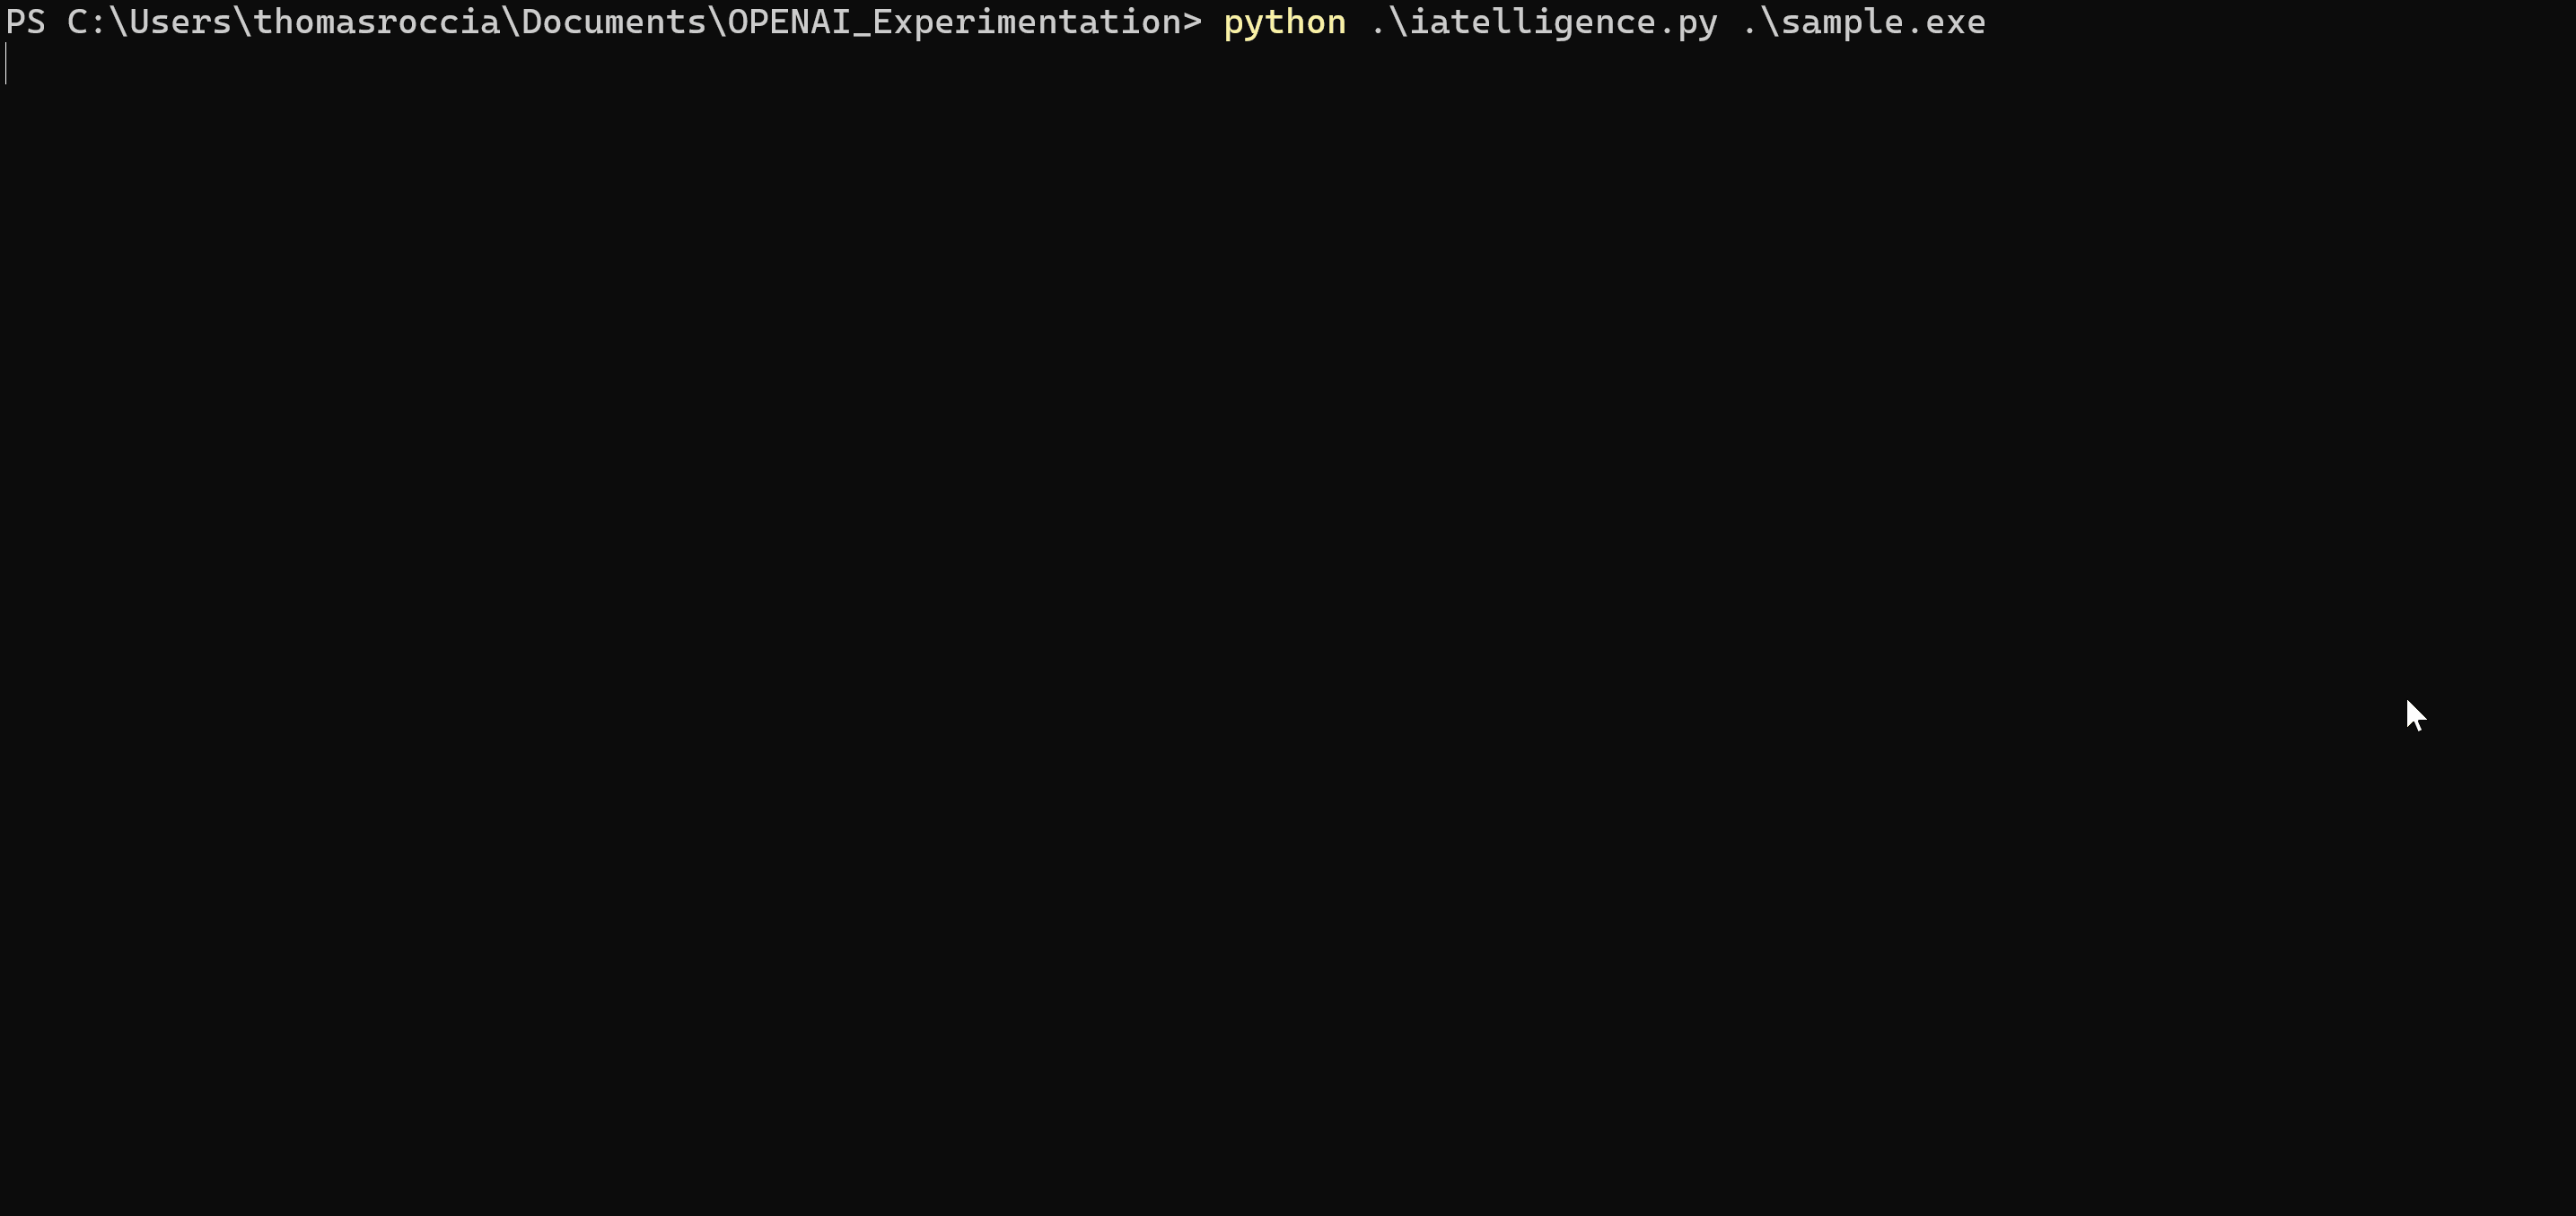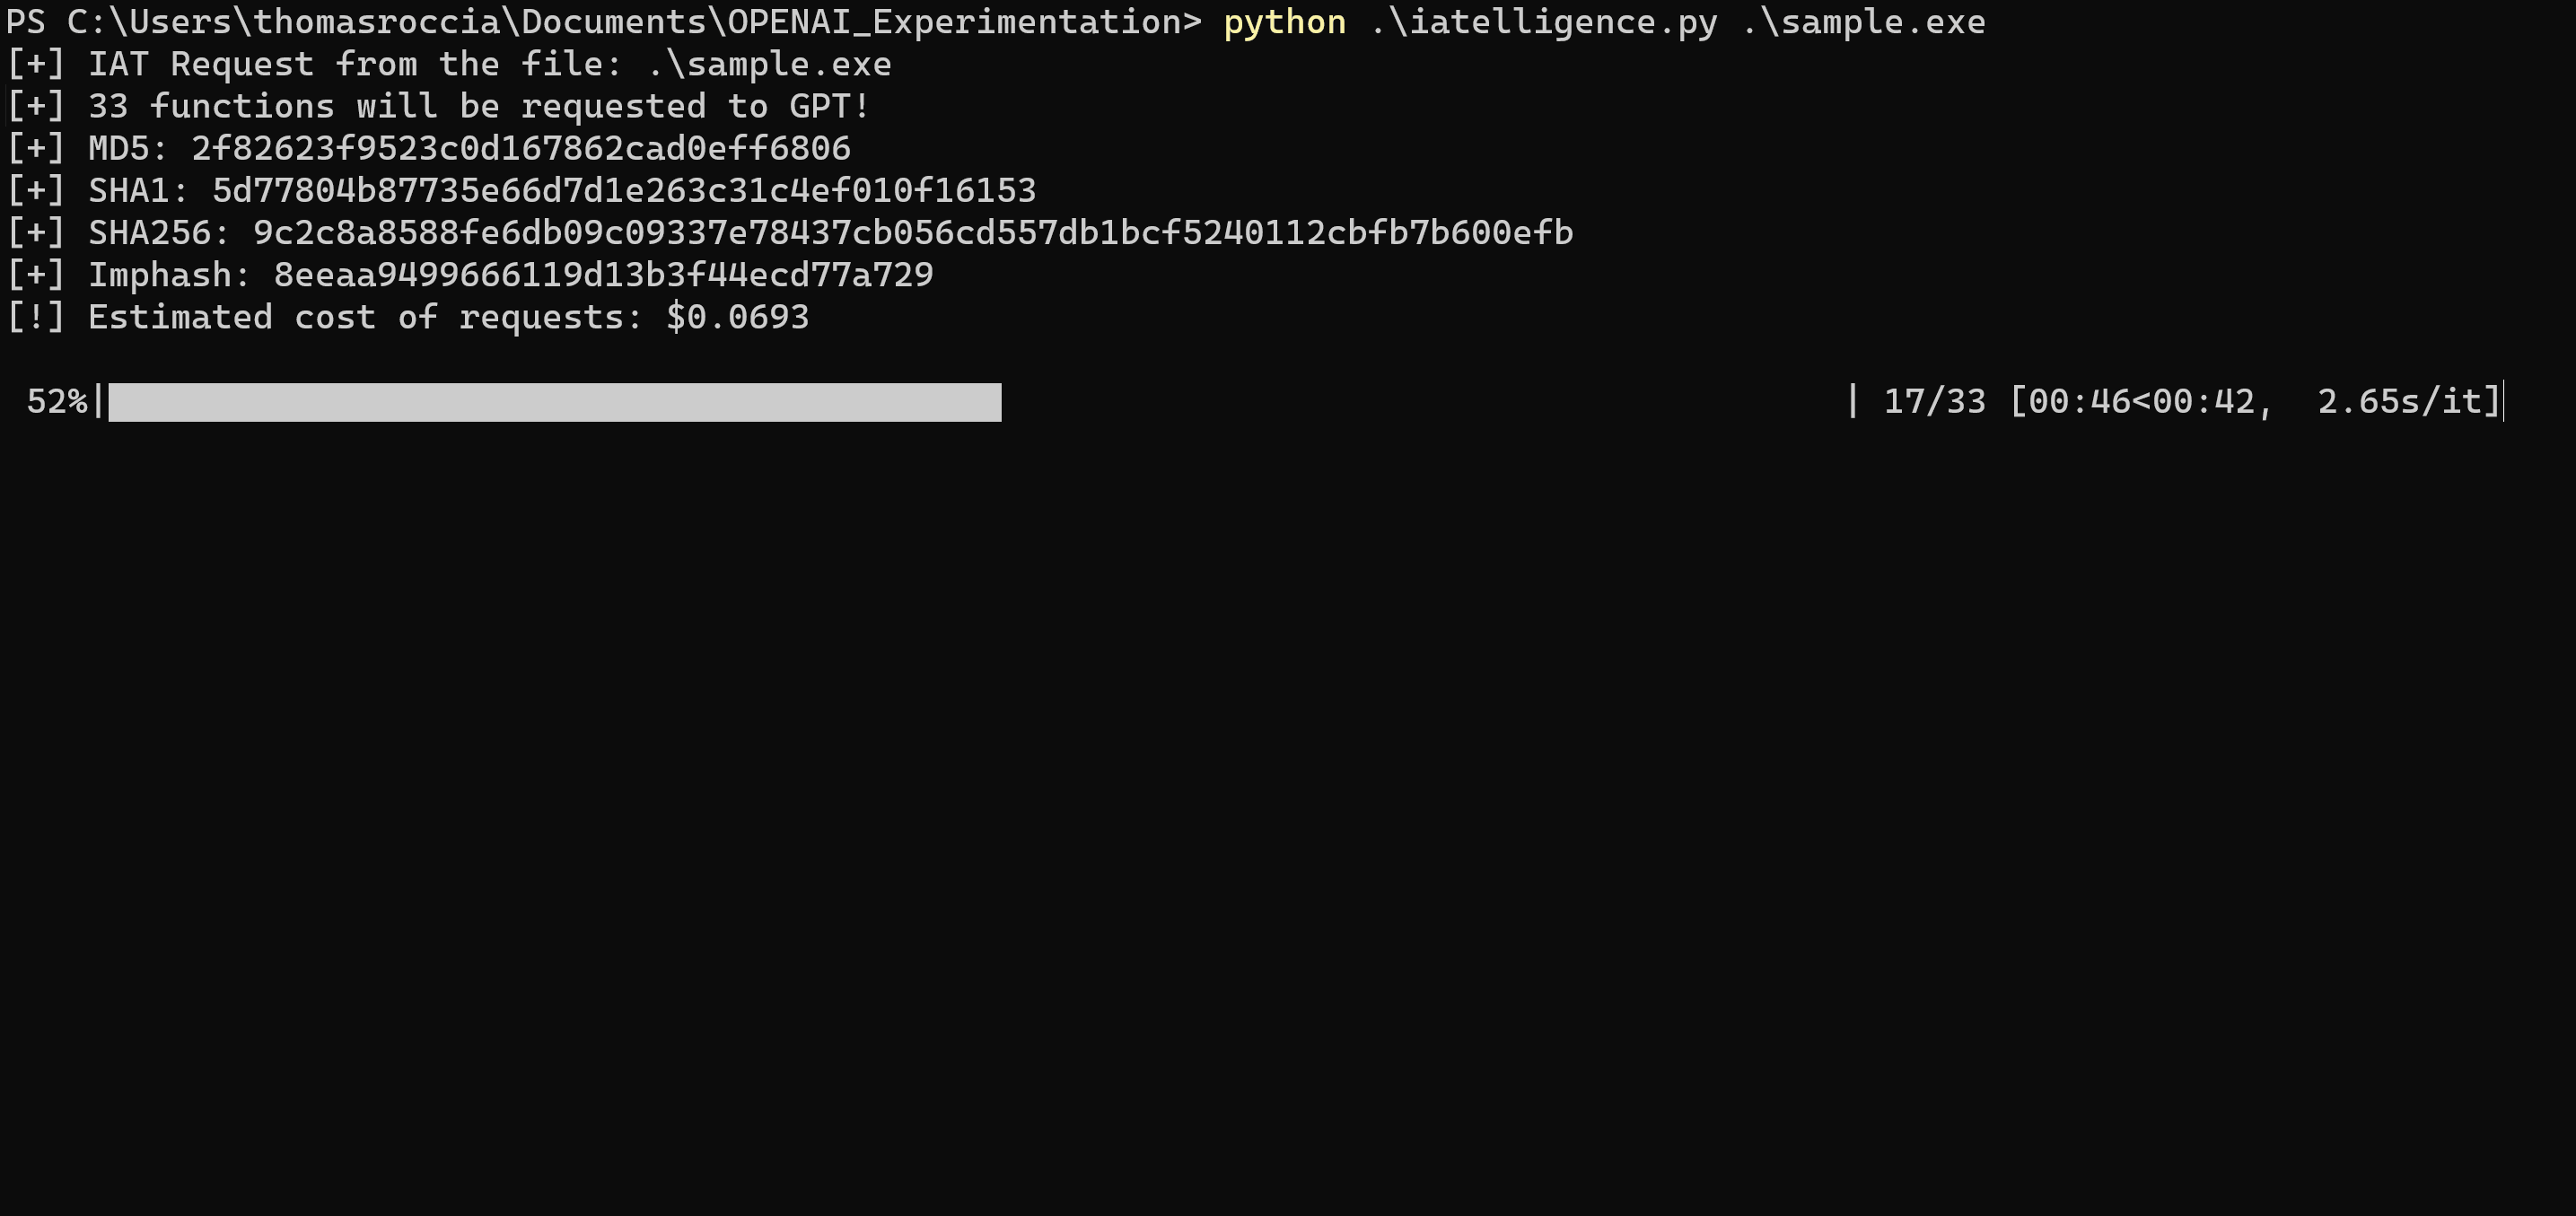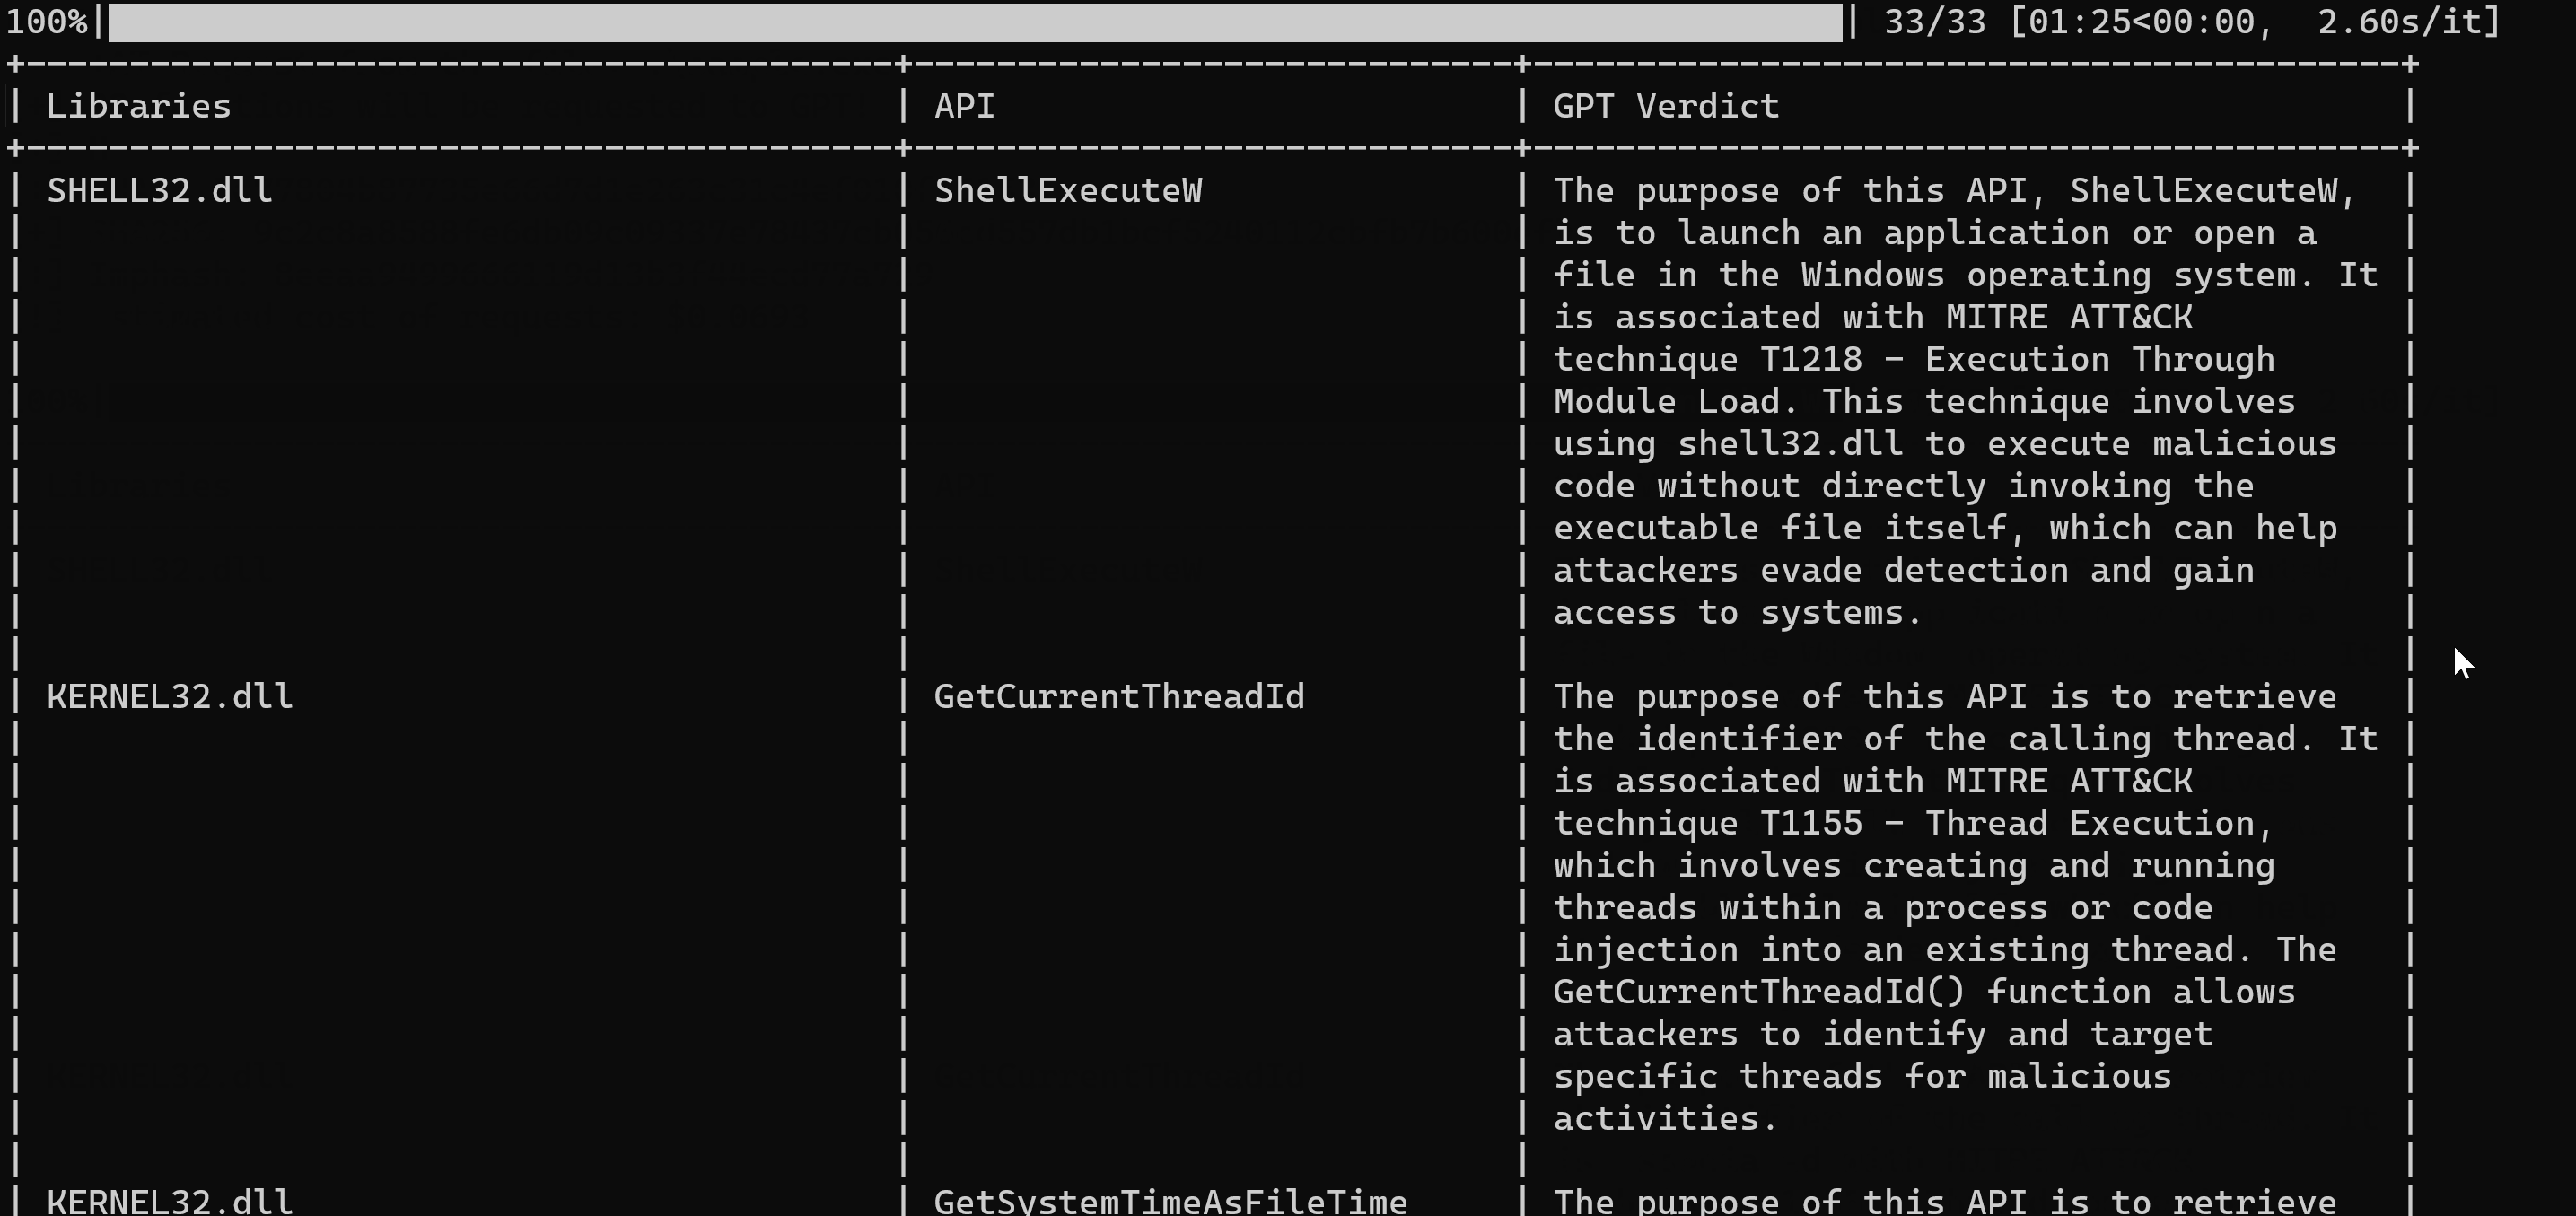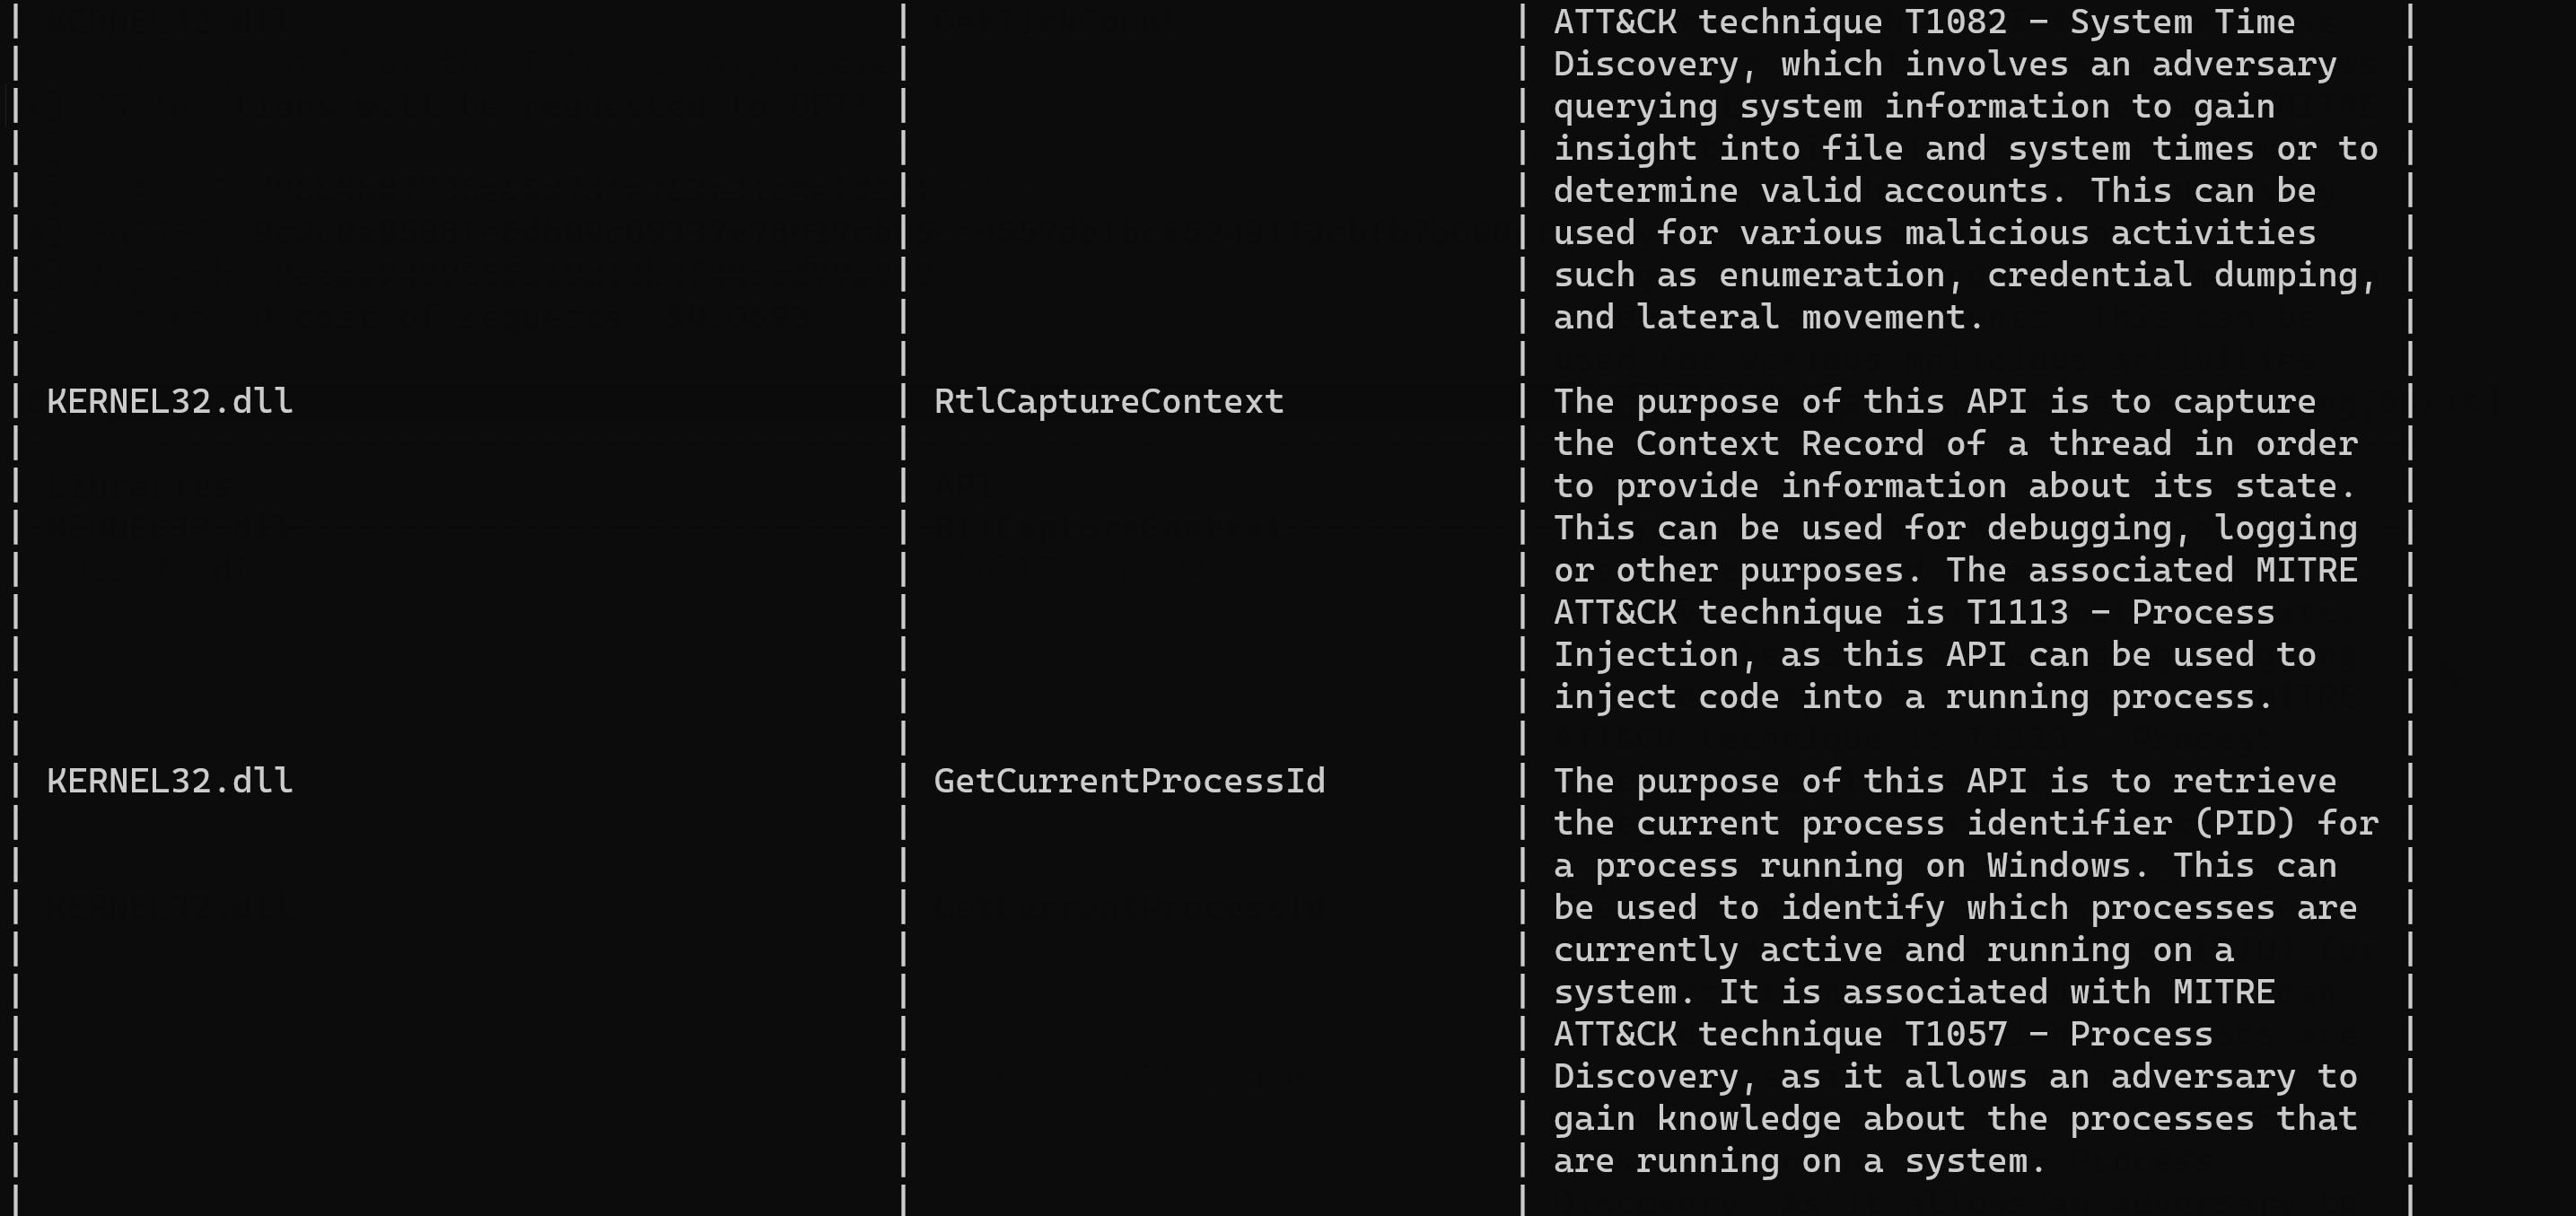
El resultado se puede visualizar en una tabla. A continuación se muestra un extracto truncado.
+------------------------------------------+-----------------------------+------------------------------------------+
| Libraries                                | API                         | GPT Verdict                              |
+------------------------------------------+-----------------------------+------------------------------------------+
| SHELL32.dll                              | ShellExecuteW               | The purpose of this API, ShellExecuteW,  |
|                                          |                             | is to launch an application or open a    |
|                                          |                             | file in the Windows operating system. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1218 - Execution Through      |
|                                          |                             | Module Load. This technique involves     |
|                                          |                             | using shell32.dll to execute malicious   |
|                                          |                             | code without directly invoking the       |
|                                          |                             | executable file itself, which can help   |
|                                          |                             | attackers evade detection and gain       |
|                                          |                             | access to systems.                       |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetCurrentThreadId          | The purpose of this API is to retrieve   |
|                                          |                             | the identifier of the calling thread. It |
|                                          |                             | is associated with MITRE ATT&CK          |
|                                          |                             | technique T1155 - Thread Execution,      |
|                                          |                             | which involves creating and running      |
|                                          |                             | threads within a process or code         |
|                                          |                             | injection into an existing thread. The   |
|                                          |                             | GetCurrentThreadId() function allows     |
|                                          |                             | attackers to identify and target         |
|                                          |                             | specific threads for malicious           |
|                                          |                             | activities.                              |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetSystemTimeAsFileTime     | The purpose of this API is to retrieve   |
|                                          |                             | the current system time as a file time   |
|                                          |                             | format. It is associated with the MITRE  |
|                                          |                             | ATT&CK technique T1124 - System Time     |
|                                          |                             | Discovery, which is used by adversaries  |
|                                          |                             | to gain insight into when certain        |
|                                          |                             | activities occurred or are scheduled to  |
|                                          |                             | occur. This allows them to perform       |
|                                          |                             | timing-based attacks and evade           |
|                                          |                             | detection.                               |
|                                          |                             |                                          |
| KERNEL32.dll                             | GetTickCount                | The purpose of this API is to retrieve   |
|                                          |                             | the number of milliseconds since Windows |
|                                          |                             | was started. It is associated with MITRE |
|                                          |                             | ATT&CK technique T1082 - System Time     |
|                                          |                             | Discovery, which involves an adversary   |
|                                          |                             | querying system information to gain      |
|                                          |                             | insight into file and system times or to |
|                                          |                             | determine valid accounts. This can be    |
|                                          |                             | used for various malicious activities    |
|                                          |                             | such as enumeration, credential dumping, |
|                                          |                             | and lateral movement.                    |
|                                          |                             |                                          |
| KERNEL32.dll                             | RtlCaptureContext           | The purpose of this API is to capture    |
