
 arinerron/heaptrace
Ayuda a visualizar operaciones de heap para pwn y depuración.

heaptrace es un depurador de heap para rastrear operaciones de heap de glibc en binarios ELF64 (x86_64). Su propósito es ayudar a visualizar las operaciones de heap al depurar binarios o realizar heap pwn.
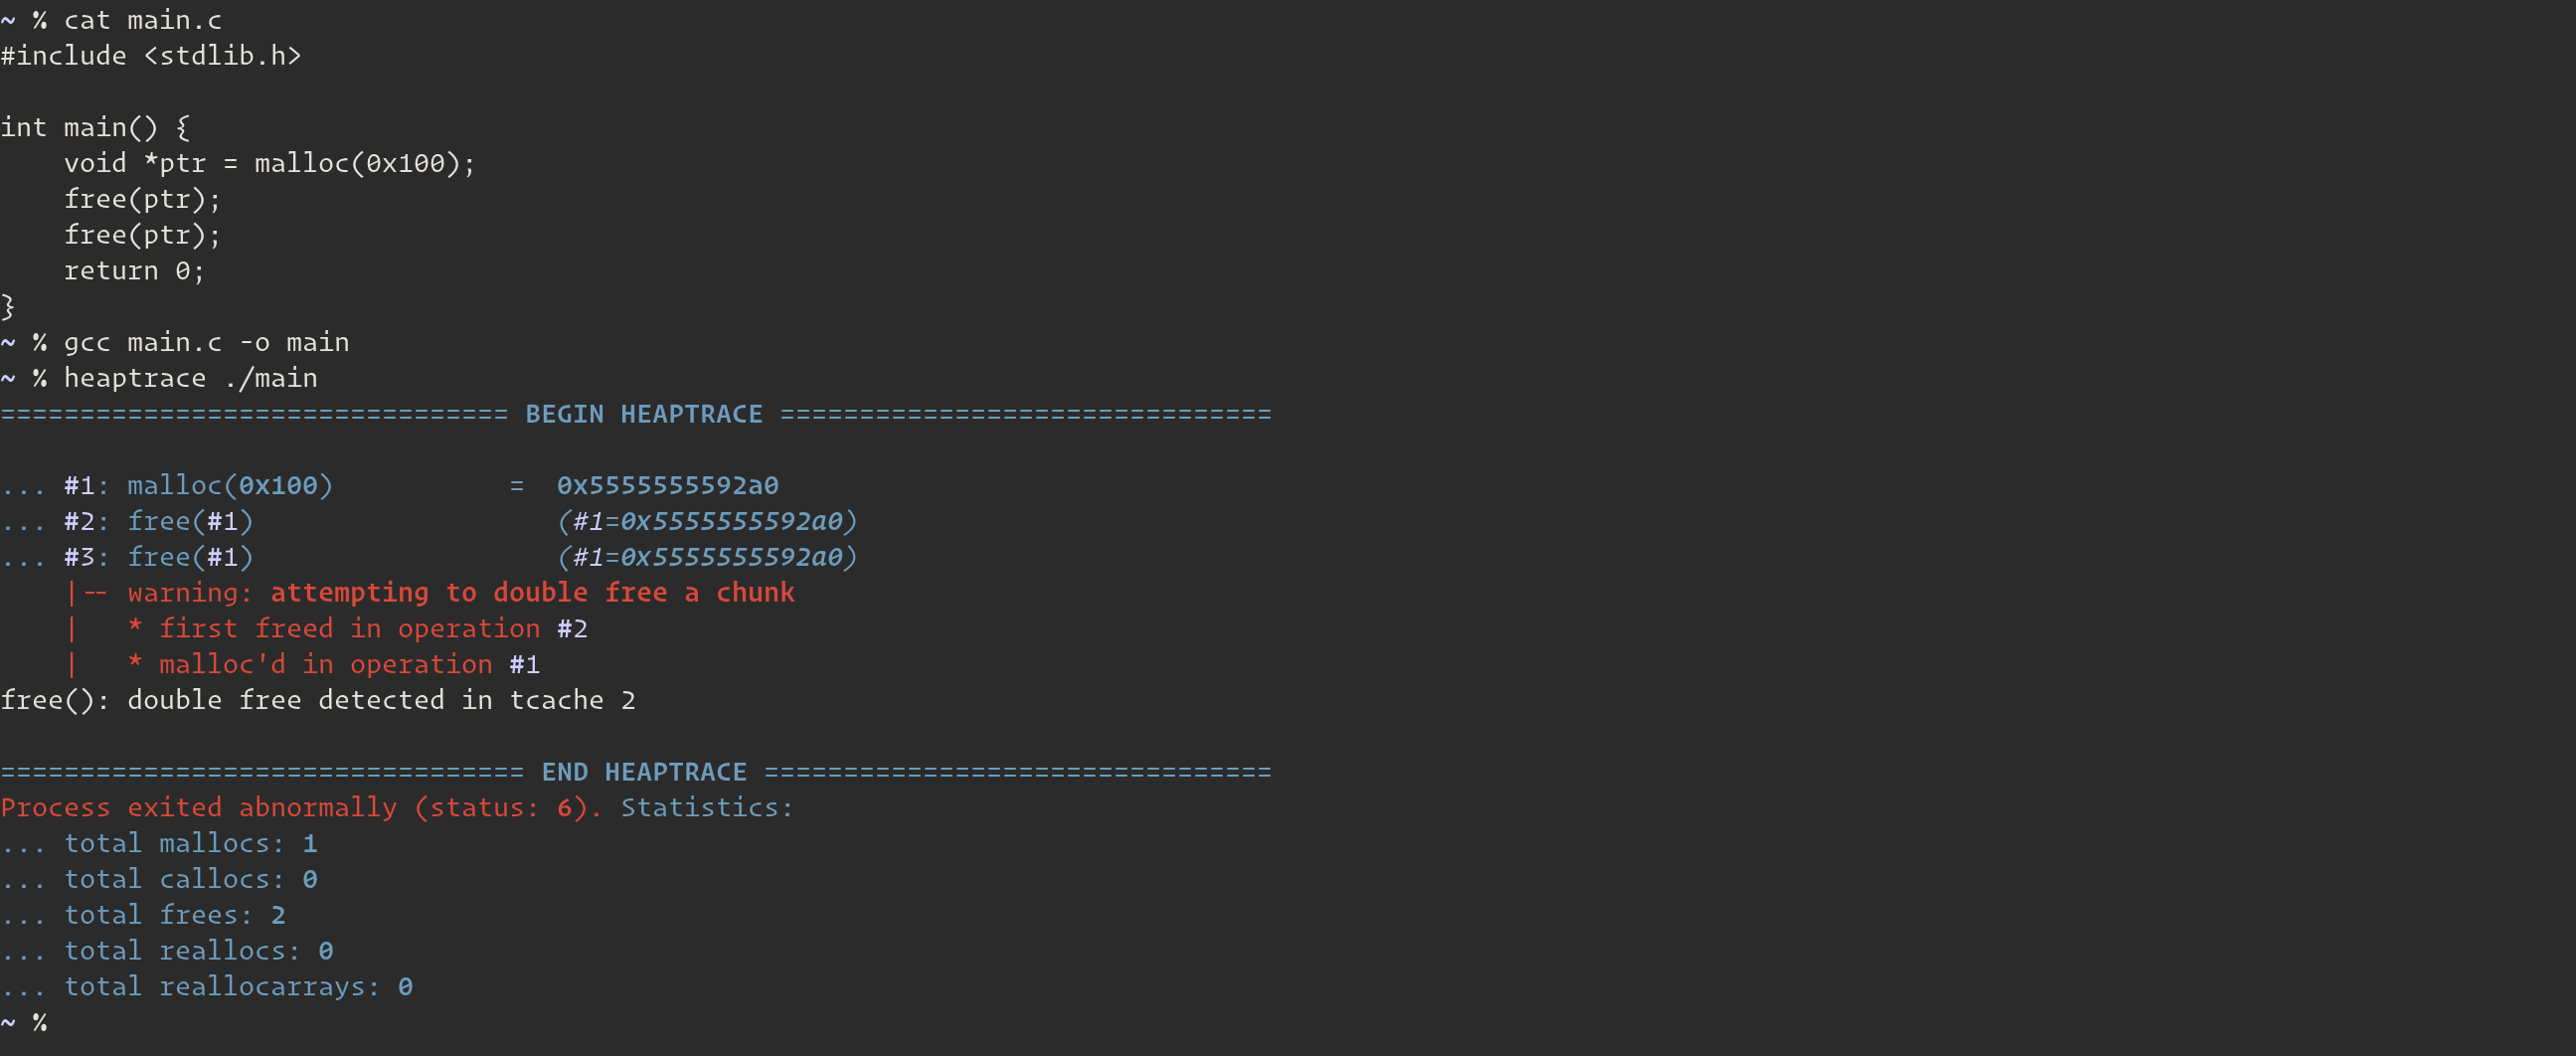
--break)¿En qué se diferencian heaptrace y valgrind?
Vea los archivos de lanzamiento .deb y .rpm, y un binario precompilado en la página de Lanzamientos.
$ sudo add-apt-repository ppa:arinerron/heaptrace
$ sudo apt-get update
$ sudo apt-get install heaptrace
Use su ayudante AUR preferido para instalar uno de los dos siguientes paquetes:
heaptrace-git — paquete fuente (PKGBUILD)heaptrace — paquete binario (PKGBUILD)$ trizen -S heaptrace-git
... O ...
$ trizen -S heaptrace
$ git clone https://github.com/Arinerron/heaptrace.git && cd heaptrace
$ make
$ sudo make install
...
$ heaptrace ./target
Puede especificar argumentos a heaptrace antes de especificar el nombre del binario:
Usage:
  heaptrace [options...] <target> [args...]
  heaptrace [options...] --attach <pid>

Options:
  -p <pid>, --attach <pid>, --pid <pid>
	 Tells heaptrace to attach to the specified pid
	 instead of running the binary from the `target`
	 argument. Note that if you specify this argument
	 you do not have to specify `target`.


  -b <expression>, --break=<expression>, --break-at=<expression>
	 Send SIGSTOP to the process when the specified
	 `expression` is satisfied and attach the GNU debugger
	 (gdb) to the process.

	 This argument supports complex expressions. Please
	 See the documentation for more information:
	 https://github.com/Arinerron/heaptrace/wiki/How-to-Create-Breakpoints


  -B <expression>, --break-after=<expression>
	 Similar to `--break`. Replaces the tracer
	 process with gdb, but only after the heap function
	 returns. See the documentation for more information:
	 https://github.com/Arinerron/heaptrace/wiki/How-to-Create-Breakpoints


  -e <name=value>, --environ=<name=value>, --environment=<name=value>
	 Sets a single environmental variable. Useful for
	 setting runtime settings for the target such as
	 LD_PRELOAD=./libc.so.6 without having them affect
	 heaptrace's runtime configuration. This option can
	 be used multiple times.


  -s <sym_defs>, --symbols=<sym_defs>
	 Override the values heaptrace detects for the
	 malloc/calloc/free/realloc/reallocarray symbols.
	 Useful if heaptrace fails to automatically
	 identify heap functions in a stripped binary. See
	 the wiki for more info.


  -F, --follow-fork, --follow
	 Tells heaptrace to detach the parent and follow
	 the child if the target calls fork(), vfork(), or
	 clone().

	 The default behavior is to detach the child and
	 only trace the parent.


  -G <path>, --gdb-path <path>
	 Tells heaptrace to use the path to gdb specified
	 in `path` instead of /usr/bin/gdb (default).


  -w <width>, --width=<width>, --term-width=<width>
	 Force a certain terminal width.


  -o <file>, --output=<file>
	 Write the heaptrace output to `file` instead of
	 /dev/stderr (which is the default output path).


  -v, --verbose
	 Prints verbose information such as line numbers in
	 source code given the required debugging info is
	 stored in the ELF.


  -V, --version
	 Displays the current heaptrace version.


  -h, --help
	 Shows this help menu.
heaptrace --break=3 ./my-binary. Consulte la documentación del wiki para más información sobre cómo usar este argumento.-s/--symbol para depurar binarios sin símbolos que heaptrace no pudo identificar automáticamente.$NO_COLOR para eliminar los códigos de color ANSI de la salida. Esta opción aún está en desarrollo y se convertirá en un argumento pronto.Estoy feliz de ayudar si encuentra un error o tiene algún comentario. Por favor, vea la página de Issues de GitHub.






