detection-rules dev-v2.1.0
Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…
Short editorial updates from published cybersecurity tools.

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…

Toolkit for decoding, inspecting, and modifying UEFI firmware volumes and variable stores. Supports secure boot certificate enrollment, PE binary…

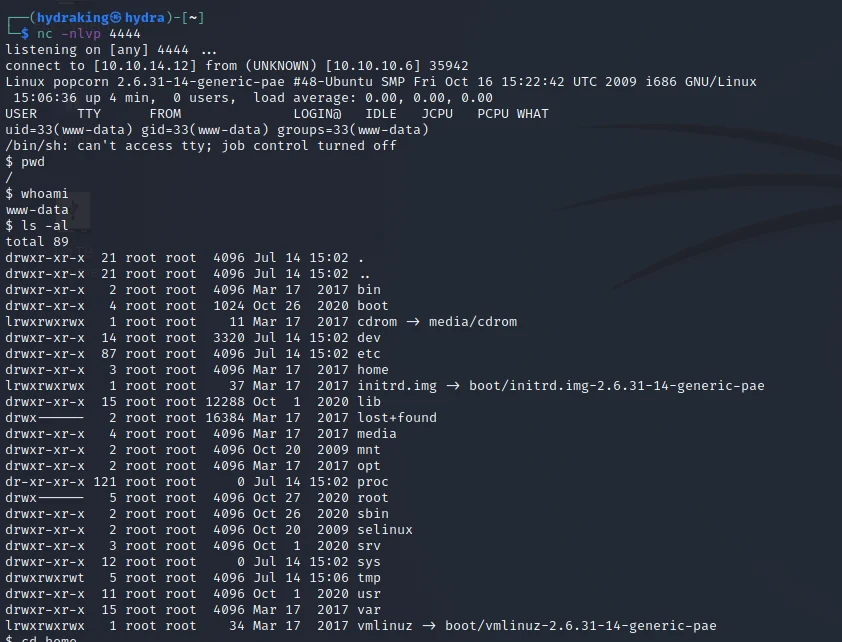
Simple PHP reverse shell script for establishing remote command execution on target systems. Ideal for penetration testing and security assessments.

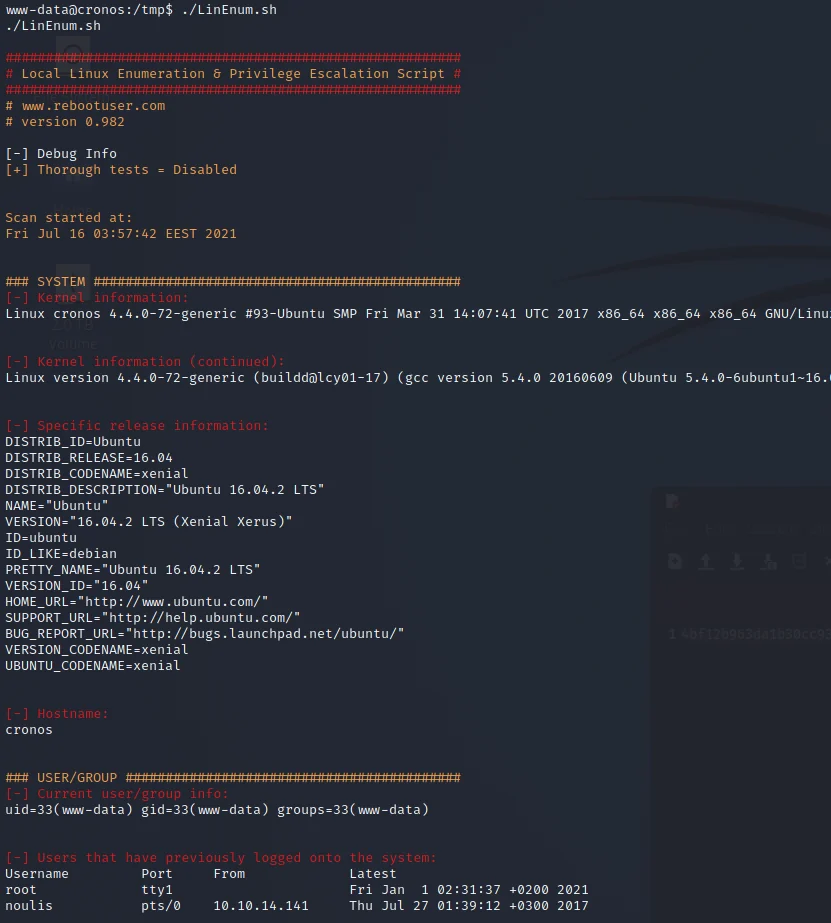
Shell script for automated enumeration of Linux systems to identify privilege escalation vectors and configuration weaknesses.

Linux enumeration script for automated system information gathering to identify potential privilege escalation vectors during penetration testing.

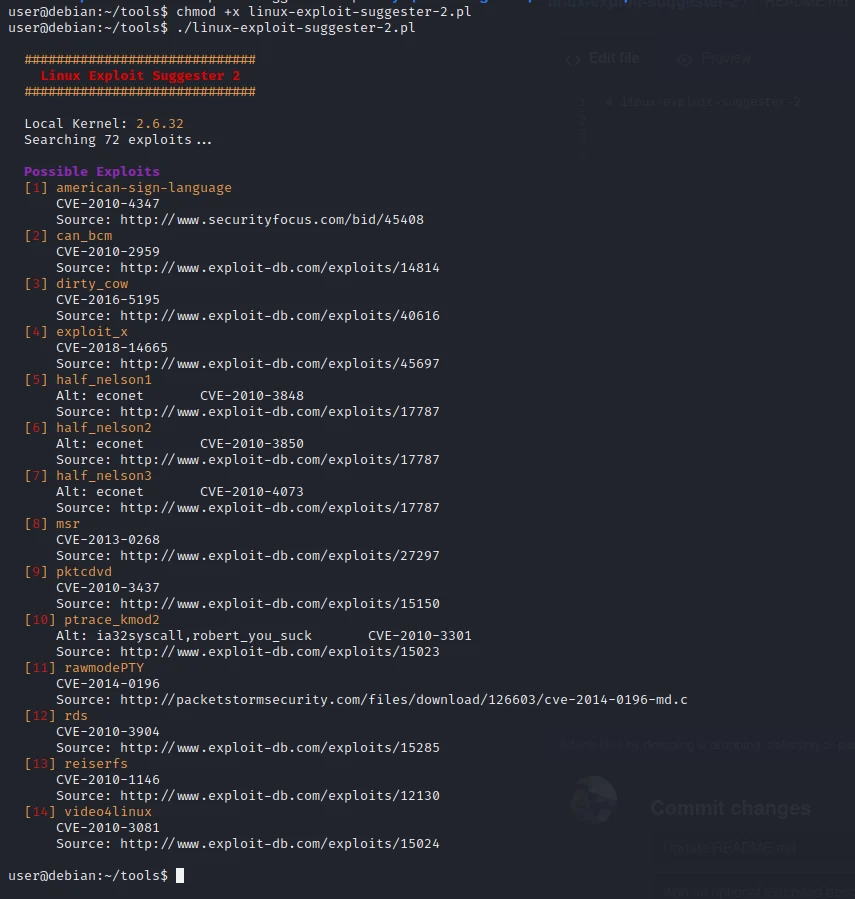
Post-exploitation utility that scans kernel/OS version and configuration to suggest applicable local privilege escalation exploits.

Run Firefox in a rootless Podman container with dropped capabilities, isolated networking, and ephemeral storage to contain sandbox escapes and…

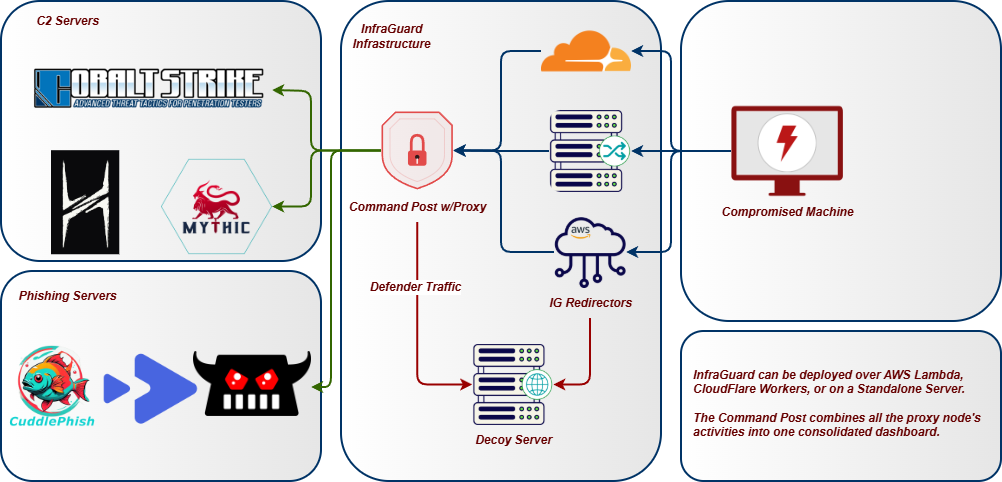
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

Run applications through VPN tunnels with temporary network namespaces

A Windows domain authentication library for testing credentials

Obfuscation module for Cobalt Strike Beacon sleep states, enabling evasion of memory-based detection and endpoint security controls.

A rootless Android app that boots Alpine Linux: run containers (Podman/Docker/LXC) and GUI desktop apps.