
New releaseAug 22, 2026
InfraGuard v0.4.3
InfraGuard is a Command & Control Redirection Proxy and Manager which protects your Red Team Infrastructure against threat attribution

Red team infrastructure tracker and C2 redirector -- a modern alternative to RedWarden.
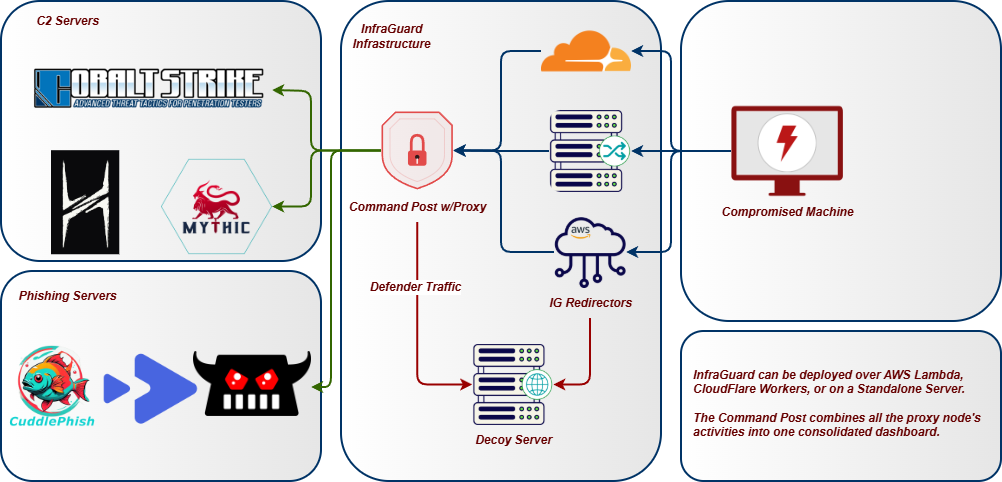
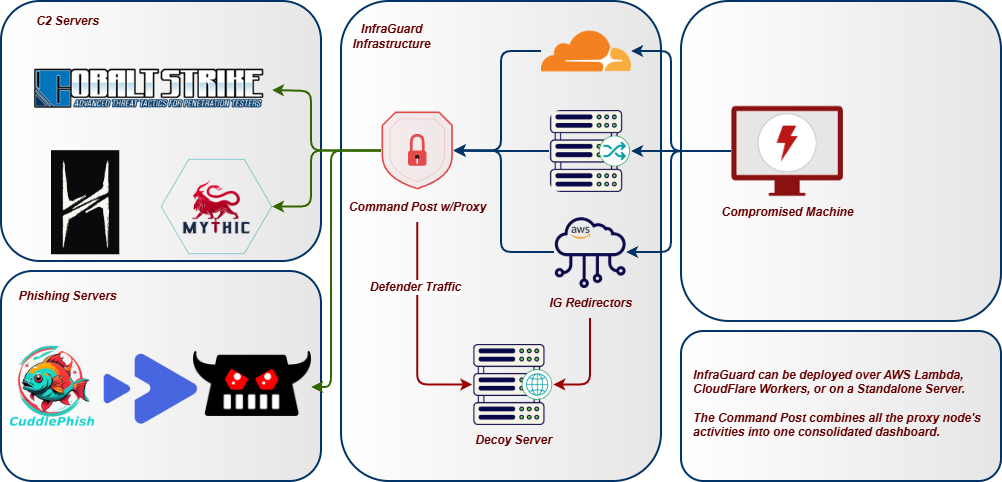
InfraGuard sits between the internet and your C2 teamserver, validating every inbound request against your malleable C2 profile and blocking anything that doesn't conform. Scanners, bots, and blue team probes get redirected to a decoy site while legitimate beacon traffic passes through to your teamserver.
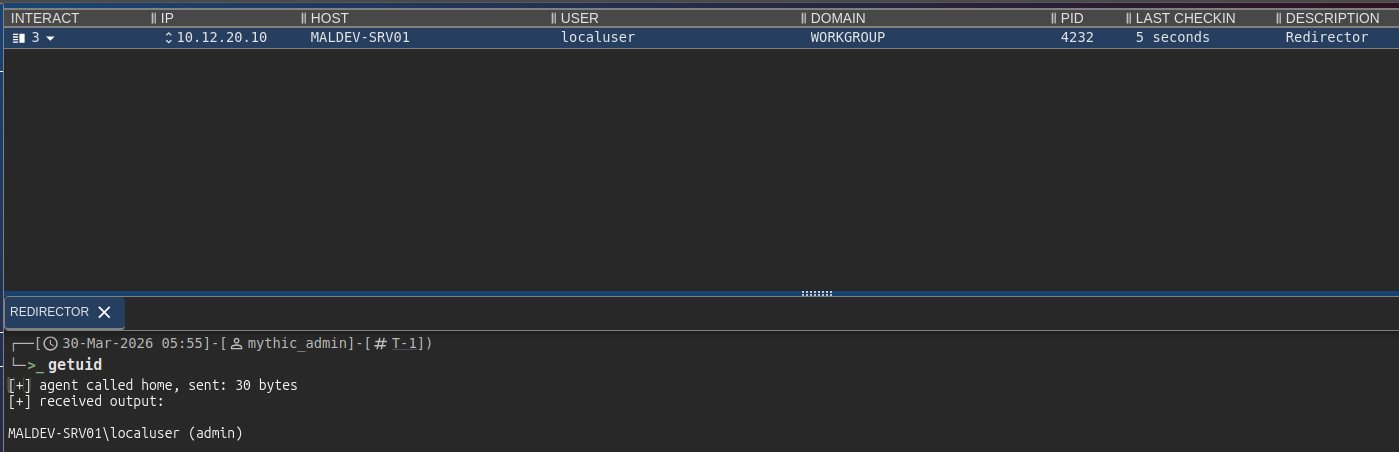
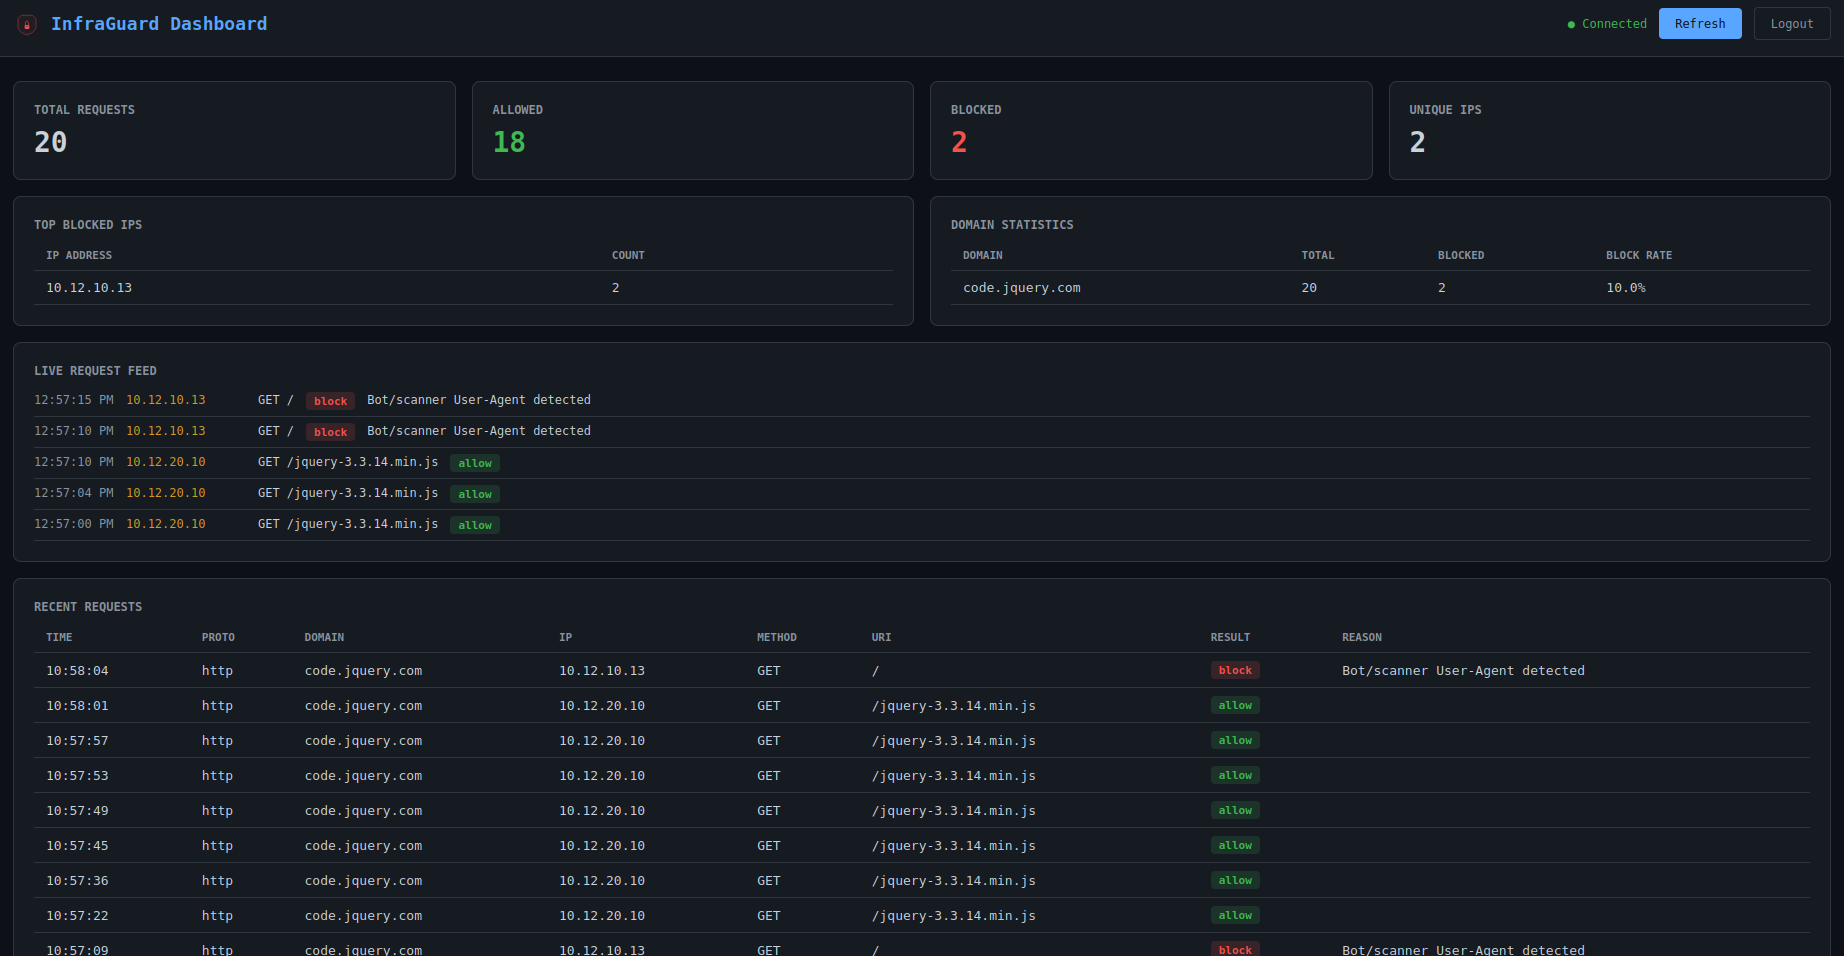
Architecture
Features
Proxying & Listeners
- Multi-domain proxying -- proxy multiple domains simultaneously, each with independent C2 profiles, upstreams, and rules
- Multi-protocol listeners -- HTTP/HTTPS, HTTP/3 (QUIC), WebSocket, gRPC, DNS, MQTT, and TCP-tunnel listeners running simultaneously with shared IP intelligence and event tracking
- Circuit breaker -- per-upstream failure protection with closed/open/half-open states; falls through to the domain's drop action when backends are unreachable
- Protocol failover -- automatic failover and failback between listener protocols ranked by priority
C2 Profile Support
- C2 profile validation -- parse and enforce Cobalt Strike, Mythic, Brute Ratel C4, Sliver, Havoc, Nighthawk, and PoshC2 profiles as redirector rules
- Hot-swappable profiles -- swap a domain's active C2 profile at runtime from the dashboard without restarting the proxy
- Profile generation wizard -- generate new C2 profiles from scratch for all 8 supported types via a guided form, or import and upload existing profiles with automatic type detection and validation
- AI-assisted profile generation -- optional Ollama integration provides a chat panel in the dashboard for profile creation help and OPSEC advice
Filter Pipeline
- Scoring-based filter pipeline -- 10 filters each contribute a 0.0--1.0 score; configurable threshold determines block/allow. Filters: JA3, IP, bot, header, DNS, geo, profile, replay, enumeration, sandbox.
- JA3 TLS fingerprint filtering -- block Masscan, ZGrab2, Shodan, curl, Python requests, and Nmap at the TLS handshake layer before any HTTP data is exchanged; works via reverse-proxy header or custom asyncio protocol; optional allowlist mode enforces beacon JA3
- Sandbox and headless browser detection -- score-accumulation across HTTP signals: HeadlessChrome UA, missing Accept-Language, Chrome without sec-ch-ua, Safe Links and msnbot scanner UAs, non-browser Accept ordering
- Path enumeration detection -- per-IP unique URI tracking in a sliding window; blocks dirbuster/ffuf/gobuster before they map URI space
- DNS subdomain enumeration detection -- tracks NXDOMAIN responses per client IP; auto-blocks source IPs on threshold breach
- Anti-bot / anti-crawling -- 40+ known scanner/bot User-Agent patterns, header anomaly detection
- Replay protection -- reject duplicate requests by content hash; hashes persisted to SQLite so protection survives restarts
- Drop actions -- redirect, TCP reset, proxy to decoy site, or tarpit (slow-drip response to waste scanner time)
Intelligence
- IP intelligence -- built-in CIDR blocklists for 19 security vendor ranges (Shodan, Censys, Rapid7, etc.), GeoIP filtering, reverse DNS keyword matching
- Threat intel feeds -- auto-update blocklists from public sources (abuse.ch, Emerging Threats, Spamhaus DROP, Binary Defense) with configurable refresh interval and disk caching
- Dynamic IP blocking -- block IPs outside whitelisted ranges; auto-whitelist IPs after N valid C2 requests
- Whitelist enrichment -- whitelisted CIDRs are auto-enriched with ASN, organization, country, and continent data on startup via GeoIP databases
- Burn detection -- Certificate Transparency log monitoring via crt.sh, domain reputation self-monitoring via URLhaus/OpenPhish/Google Safe Browsing, and cross-domain analyst detection when a single IP accesses multiple operator domains
- Burn confidence scoring -- continuous 0--100 score from 6 weighted signals: JA3 diversity, volume spikes, new ASNs, CT log exposure, reputation hits, and failed auth attempts. Includes recommended actions: monitor, rotate, or immediate burn.
- Canary token injection -- tracking pixels, honeypot links, and honeypot forms auto-injected into decoy pages to detect blue team investigation
- Passive DNS monitoring -- polls CIRCL PDNS for external resolution of your domains; detects new records, NXDOMAIN spikes, and first-seen exposure
Payload Delivery
- Content delivery routes -- serve payloads, decoys, and static files at specific paths via PwnDrop, Mythic file store, local filesystem, or HTTP proxy backends; optional conditional delivery to serve real content to targets and decoys to scanners
- Mythic file staging --
mythic_filebackend proxies Mythic's/direct/download/{uuid}at clean URLs; fixed UUID or proxy mode; access control provided by InfraGuard's filter stack - One-time payload tokens -- tokens issued automatically when a beacon is dynamically whitelisted; atomic single-use SQLite enforcement prevents URL replay by analysts or sandboxes; configurable TTL and max-use count
- Per-route rate limiting -- sliding-window per-IP download rate limiter on content routes; exceeding the limit serves the configured scanner decoy or 429
- Delivery guards -- environment keying for content routes: require beacon IP, UA allowlist, required header values, forbidden headers; failed checks serve domain drop action, not a raw 403
- Phishing campaign tokens -- gate phishing pages behind per-campaign tokens embedded in email links; static token list or HMAC-signed self-validating tokens with configurable TTL
Resilience
- Infrastructure rotation -- one-click blue-green Terraform rotation across 5 cloud providers with pre-flight checks, rollback, and age-encrypted state
- Rotation scheduling -- automated rotation policies: fixed interval, burn-triggered, request-count threshold, and staggered rolling
- Auto-rotation watchdog -- polls burn score and cert expiry on an interval; auto-rotates when the burn threshold trips or a cert has under N days left, or falls back to alert-only mode with a cost cap
- Circuit breakers -- per-upstream failure tracking with HEALTHY / PROBING / TRIPPED states and configurable recovery timeout, surfaced live in the dashboard's Upstreams widget
- Domain fronting -- CDN-based C2 routing via SNI/Host header split with CDN header stripping and SSRF protection
- Dead man's switch -- operator heartbeat TTL that auto-stops C2 forwarding if the operator fails to check in
- Purple-team mirror -- fire-and-forget duplicate of allowed events to a blue-team collector for engagement scoring
- Shared state backend (Redis) -- optional cross-node replay cache, dynamic whitelist, beacon session bag, and drop rate-limit so horizontally scaled replicas see the same state
- Edge proxies -- Cloudflare Worker and AWS Lambda for domain fronting through CDN infrastructure, edge country blocking, and host rewriting