cve-lite-cli v1.30.0
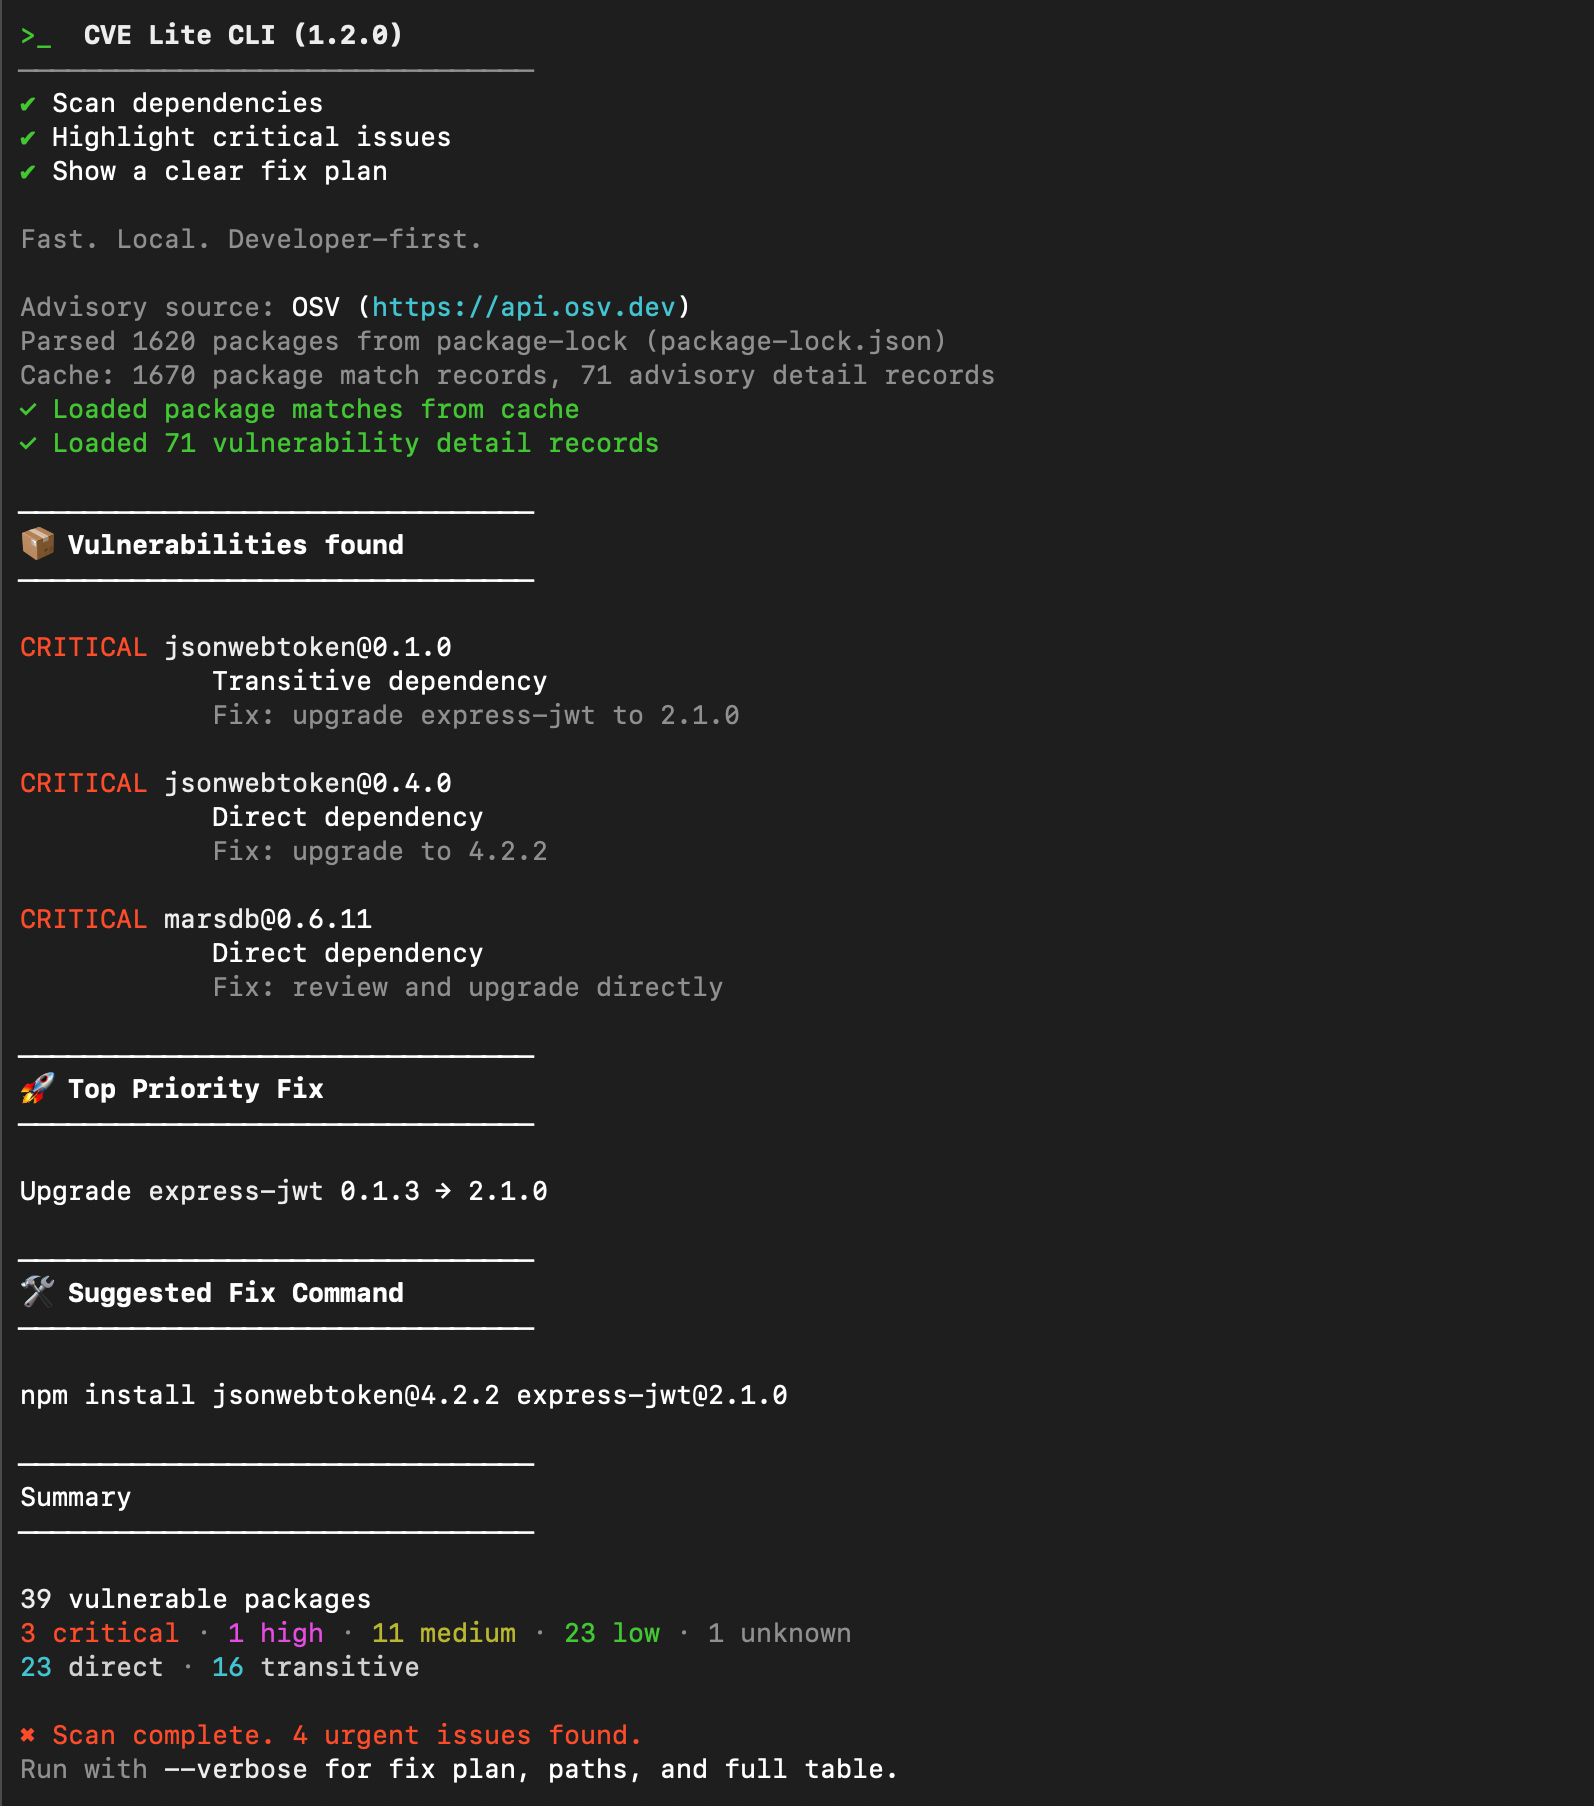
Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…
Short editorial updates from published cybersecurity tools.

Fast, developer-friendly JS/TS dependency vulnerability scanner with local lockfile scanning, OSV matching, direct vs transitive visibility, --fix,…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…

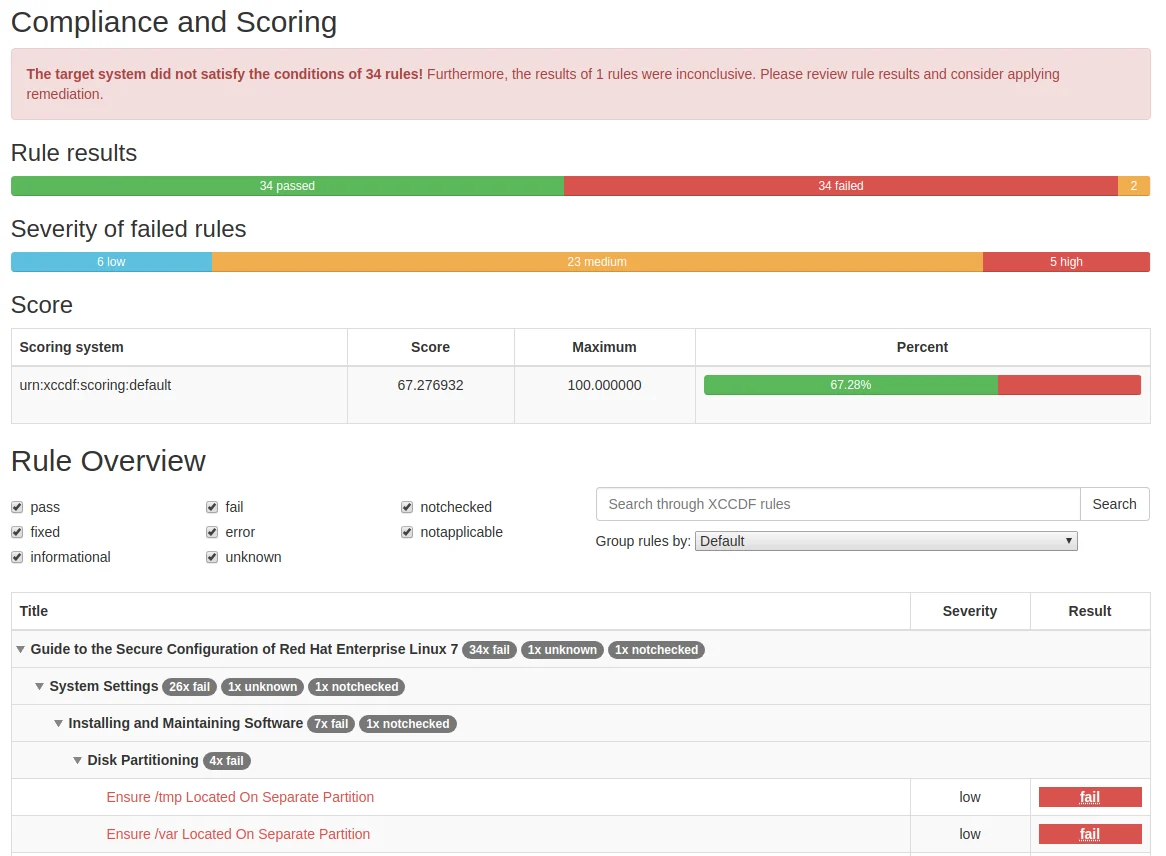
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…

Write tests against structured configuration data using the Open Policy Agent Rego query language

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…

✨ A Swiss Army Knife for Zsh - Unix Shell

Plugin for integrating Trivy with Aqua Security platform to scan IaC, pipelines, and dependencies for vulnerabilities and misconfigurations.

Vendor-neutral OWASP project mapping quantum-era security risks with a Top 10 risk list, mitigation guidance, and threat models for post-quantum…

Low-observability Active Directory security enumeration tool using native ADSI/COM interfaces. Enumerates ACLs, delegation, trusts, ADCS, Kerberoast…

Fast passive subdomain enumeration tool.

Develop, validate, and publish SIEM detection rules for Elastic Security, with Python CLI tooling, KQL parsing, Kibana integration, and packaged…