rzweb
 indalok/rzweb
A complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
binary-analysisdebuggersdynamic-analysis-sandboxing+5
760
indalok/rzwebA complete browser-based reverse engineering platform built on Rizin, running entirely client-side via WebAssembly.
 borahll/cve-2021-21220
Educational presentation detailing the exploitation of CVE-2021-21220, a V8 JIT type confusion leading to OOB access and RCE via WebAssembly, with…
 victorns69/cve-2024-12381
Exploit for Chrome V8 type confusion (CVE-2024-12381) with JSPI sandbox bypass, delivering RCE via a Flask server that fingerprints browsers and…
 capsulerun/capsule
Secure runtime to sandbox AI agent tasks. Run untrusted code in isolated WebAssembly environments.
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 adityabhatt3010/cve-2025-10585-the-chrome-v8-zero-day
Google patched CVE-2025-10585, a Chrome V8 zero-day under active exploitation — here’s what it is, why it matters, and how to stay safe.
 sneakynachos/cve-2024-29943-but-with-wasm
CVE-2024-29943, but with wasm
 paras98/cve-2021-38297-go-wasm-replication
Educational proof-of-concept replicating CVE-2021-38297, a Go WASM buffer overflow leading to stored XSS. Includes vulnerable app setup, exploit…
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 notasithlord/peerd
The first AI agent harness native to the browser. A browser extension that runs a full agent loop where you already work: it drives your tabs, spins…
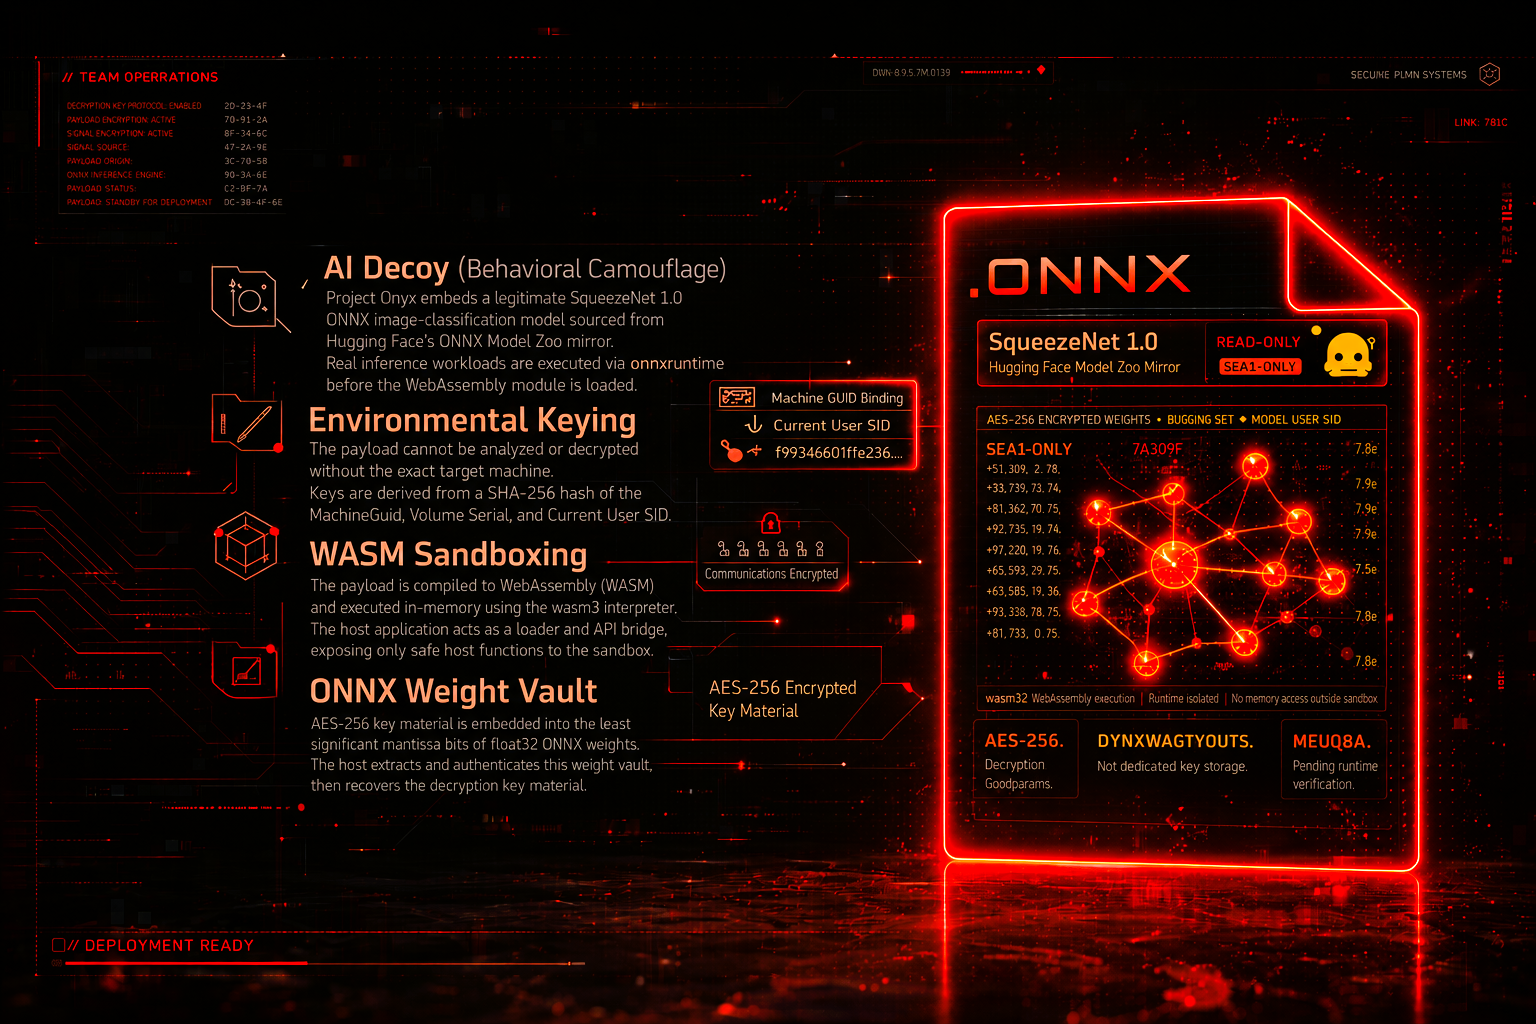 x-3306/project-onyx
Advanced EDR Evasion via AI Telemetry Spoofing & WASM Sandboxing. Project Onyx is a PoC Red Team pipeline designed to demonstrate advanced evasion…
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 sneakynachos/cve-2026-74936-gc-potato
Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…
 george0papasotiriou/cve-2026-21001-webassembly-linear-memory-oob-via-table-index-confusion
Demonstrates a critical WebAssembly OOB read/write via table index confusion, leaking host memory and potentially enabling code execution in WASM…
 jezzus/cve-2018-4121
Proof-of-concept remote code execution exploit targeting Safari 11.0.3 on macOS 10.13.3 via a WebAssembly section vulnerability (CVE-2018-4121).…
 likekabin/cve-2018-4121
Proof-of-concept remote code execution exploit for Safari 11.0.3 on macOS 10.13.3, leveraging a WebAssembly section vulnerability with heap spray and…