
BlackDir-Framework
 jehadalqurashi/blackdir-framework
Web Application Vulnerability Scanner
encryption-decryption-toolshash-analysisinformation-gathering+5
138
jehadalqurashi/blackdir-frameworkWeb Application Vulnerability Scanner
 punk-security/dnsreaper
Fast subdomain takeover scanner with 50+ signatures, supporting cloud provider integrations (AWS, Azure, Cloudflare) and CI/CD pipeline mode for…
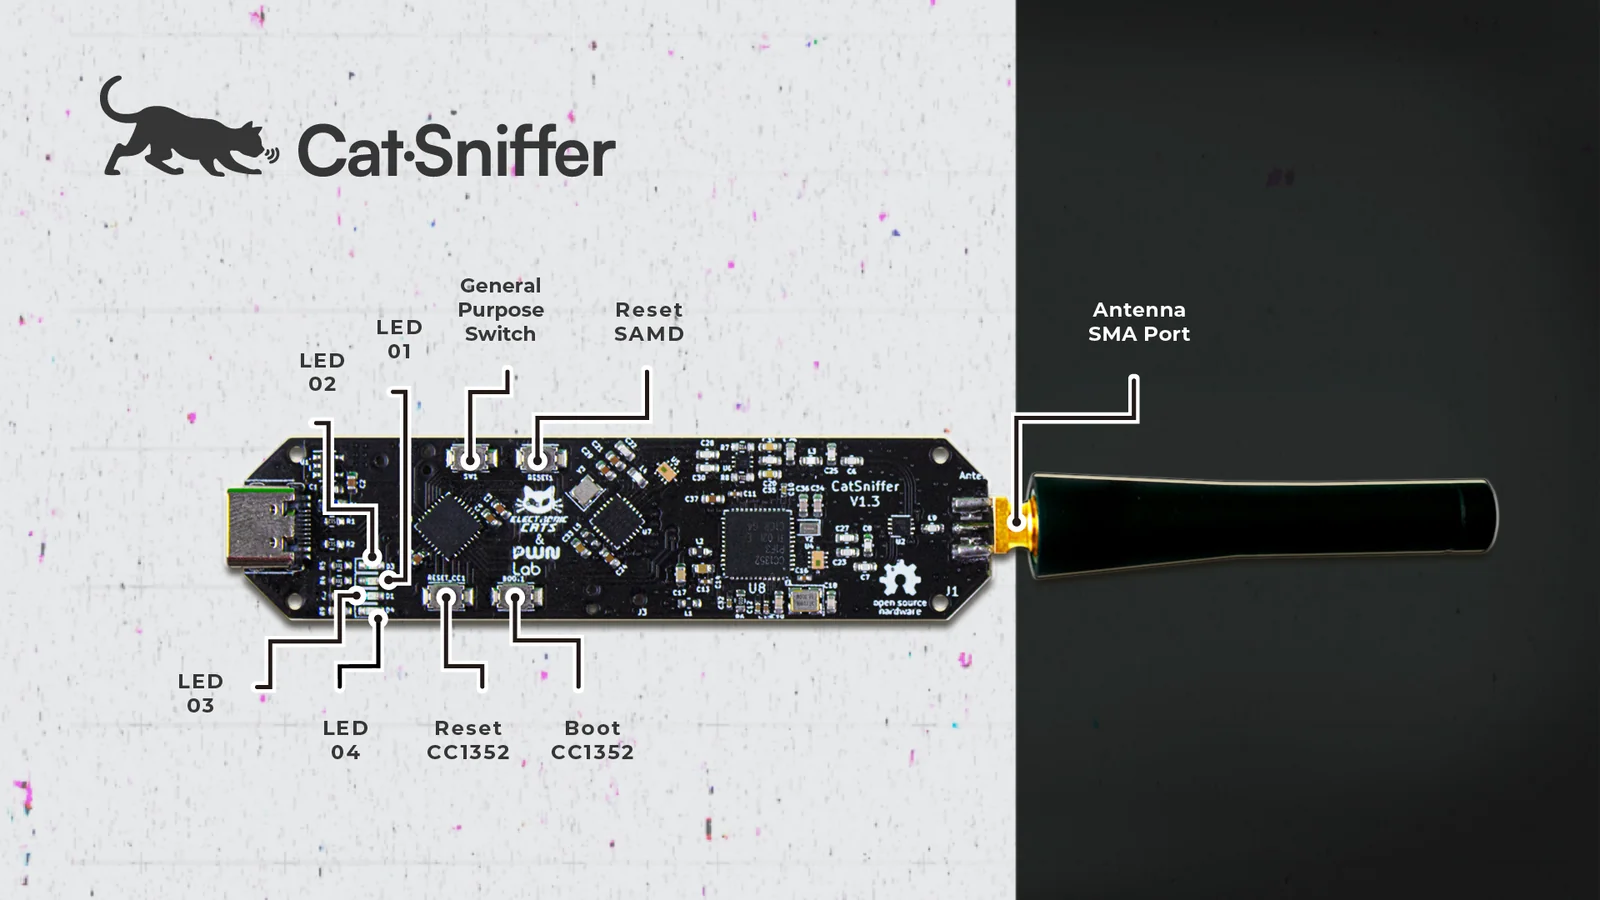 electroniccats/catsniffer-firmware
Firmware repository for CatSniffer, a multi-protocol IoT security research board supporting BLE, Zigbee, Sub-1 GHz, and more, with version-specific…
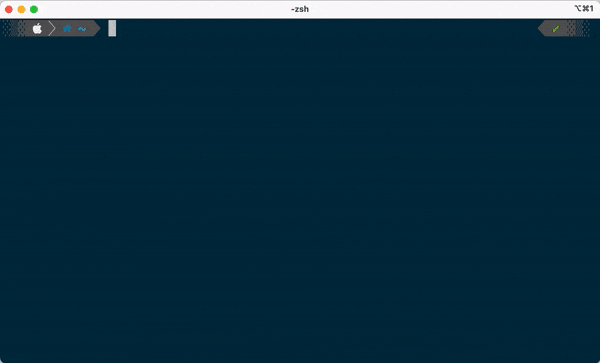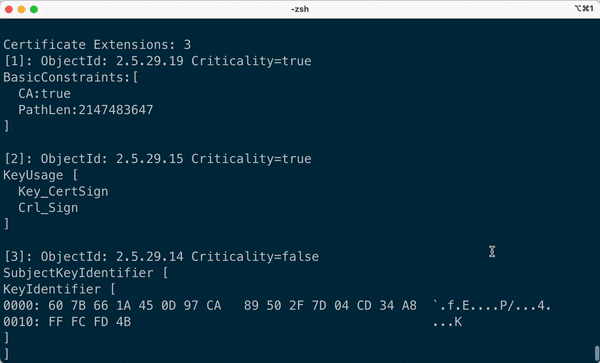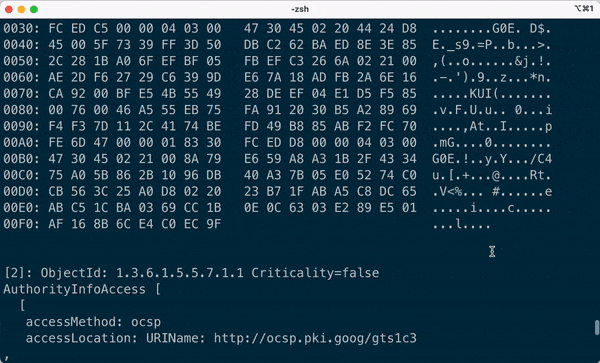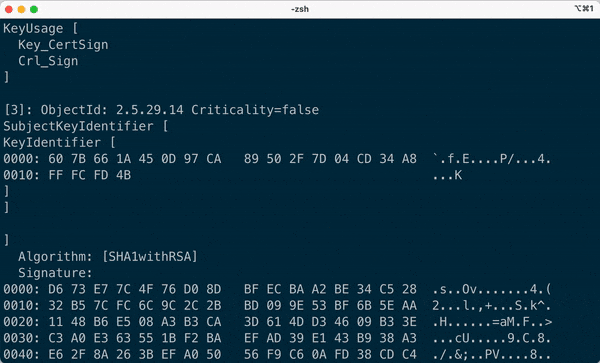 hakky54/certificate-ripper
🔐 A CLI tool to extract server certificates
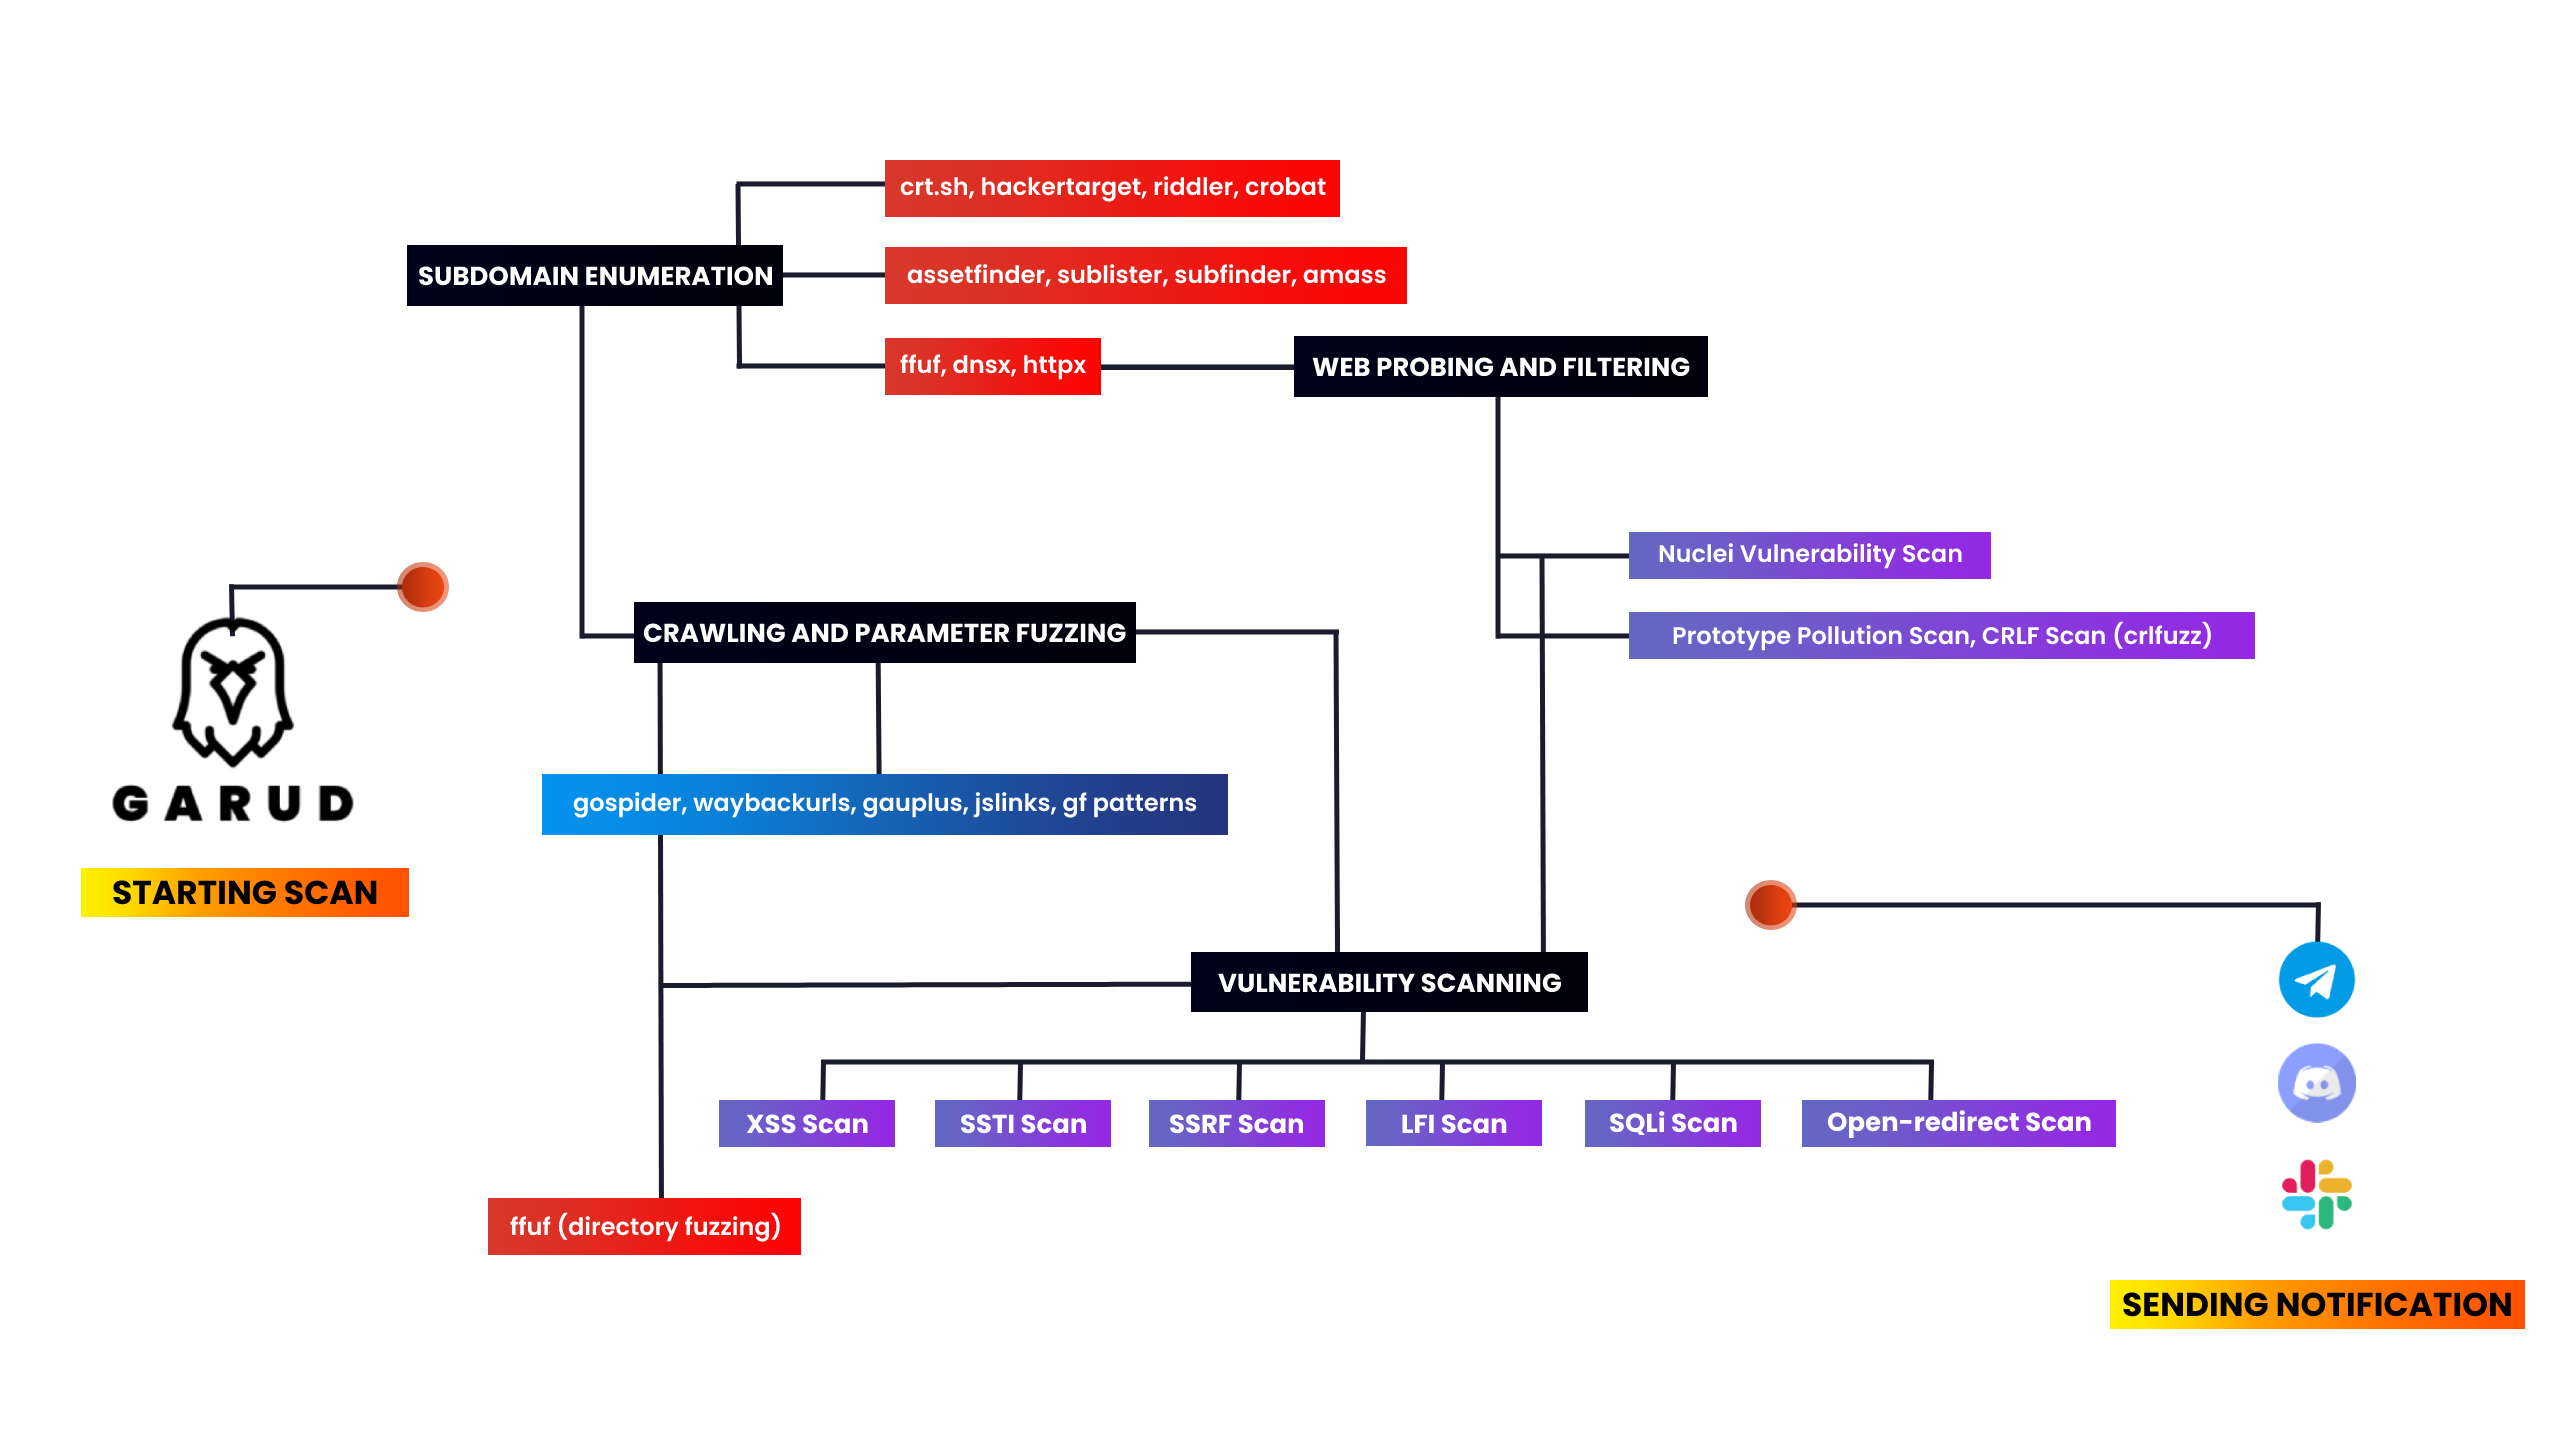 r0x4r/garud
An automation tool that scans sub-domains, sub-domain takeover, then filters out XSS, SSTI, SSRF, and more injection point parameters and scans for…
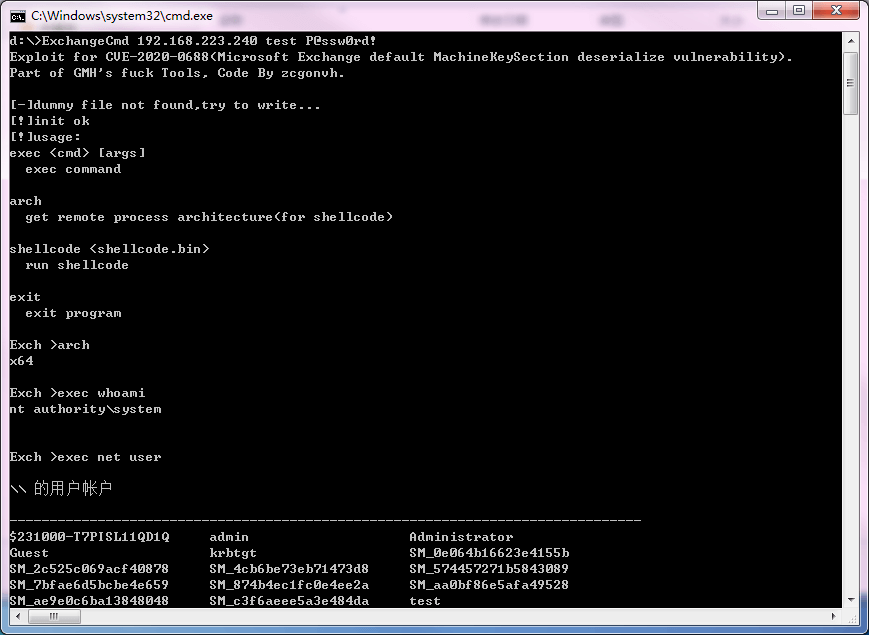 zcgonvh/cve-2020-0688
Exploit and detect tools for CVE-2020-0688
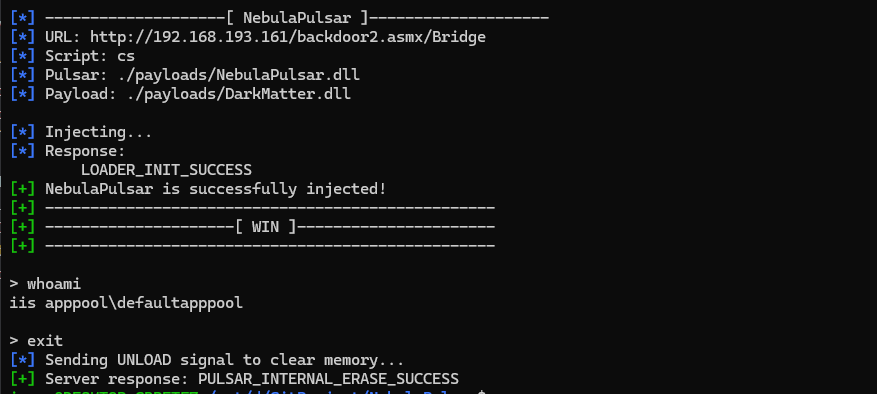 iss4cf0ng/nebulapulsar
NebulaPulsar is a proof-of-concept in-memory implant framework for Java (JSP) and ASP.NET (ASPX/ASHX/ASMX) webshells, originally developed as part of…
 spiralbl0ck/linux-kernel-infoleak-6.12.-leveraged-to-do-cross-container-info-leak.-
POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20
 kal1gh0st/mylog4shell
Simple Python 3 script to detect the "Log4j" Java library vulnerability (CVE-2021-44228) for a list of URLs with multithreading
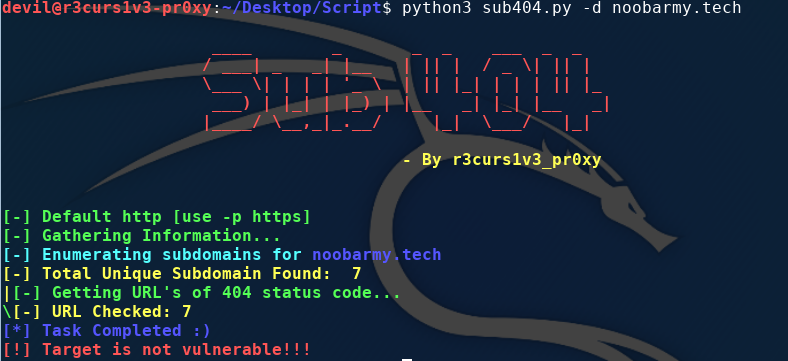 r3curs1v3-pr0xy/sub404
A python tool to check subdomain takeover vulnerability
 qazbnm456/awesome-web-security
🐶 A curated list of Web Security materials and resources.
 darkcodersc/subseven
SubSeven Legacy Official Source Code Repository
 kudaes/split
Apply a divide and conquer approach to bypass EDRs
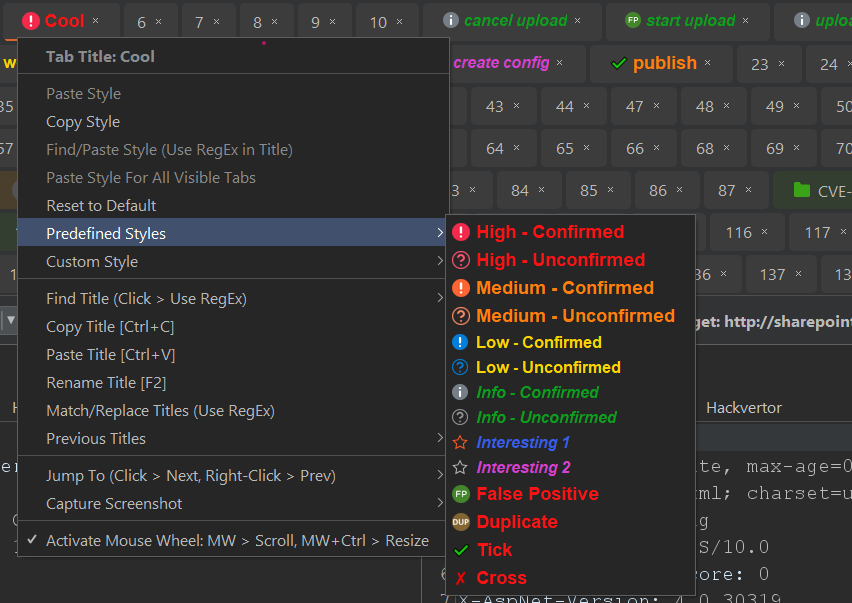 irsdl/burpsuitesharpenerex
This extension enhances Burp Suite by adding several UI and functional features, making it more user-friendly.
 pigeonlabshq/pigeon
Enforce least-privilege delegation for AI agents with signed, scoped credentials. Grant sub-agents narrow capabilities and resources, verify actions…
 j4k0m/cve-2018-11235
Automated creation of malicious Git repositories to exploit CVE-2018-11235, a remote code execution vulnerability in Git submodules.
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain