
CSS-Keylogging
 maxchehab/css-keylogging
Chrome extension and Express server that exploits keylogging abilities of CSS.
exploitationinformation-gatheringpenetration-testing+1
3.2k
maxchehab/css-keyloggingChrome extension and Express server that exploits keylogging abilities of CSS.
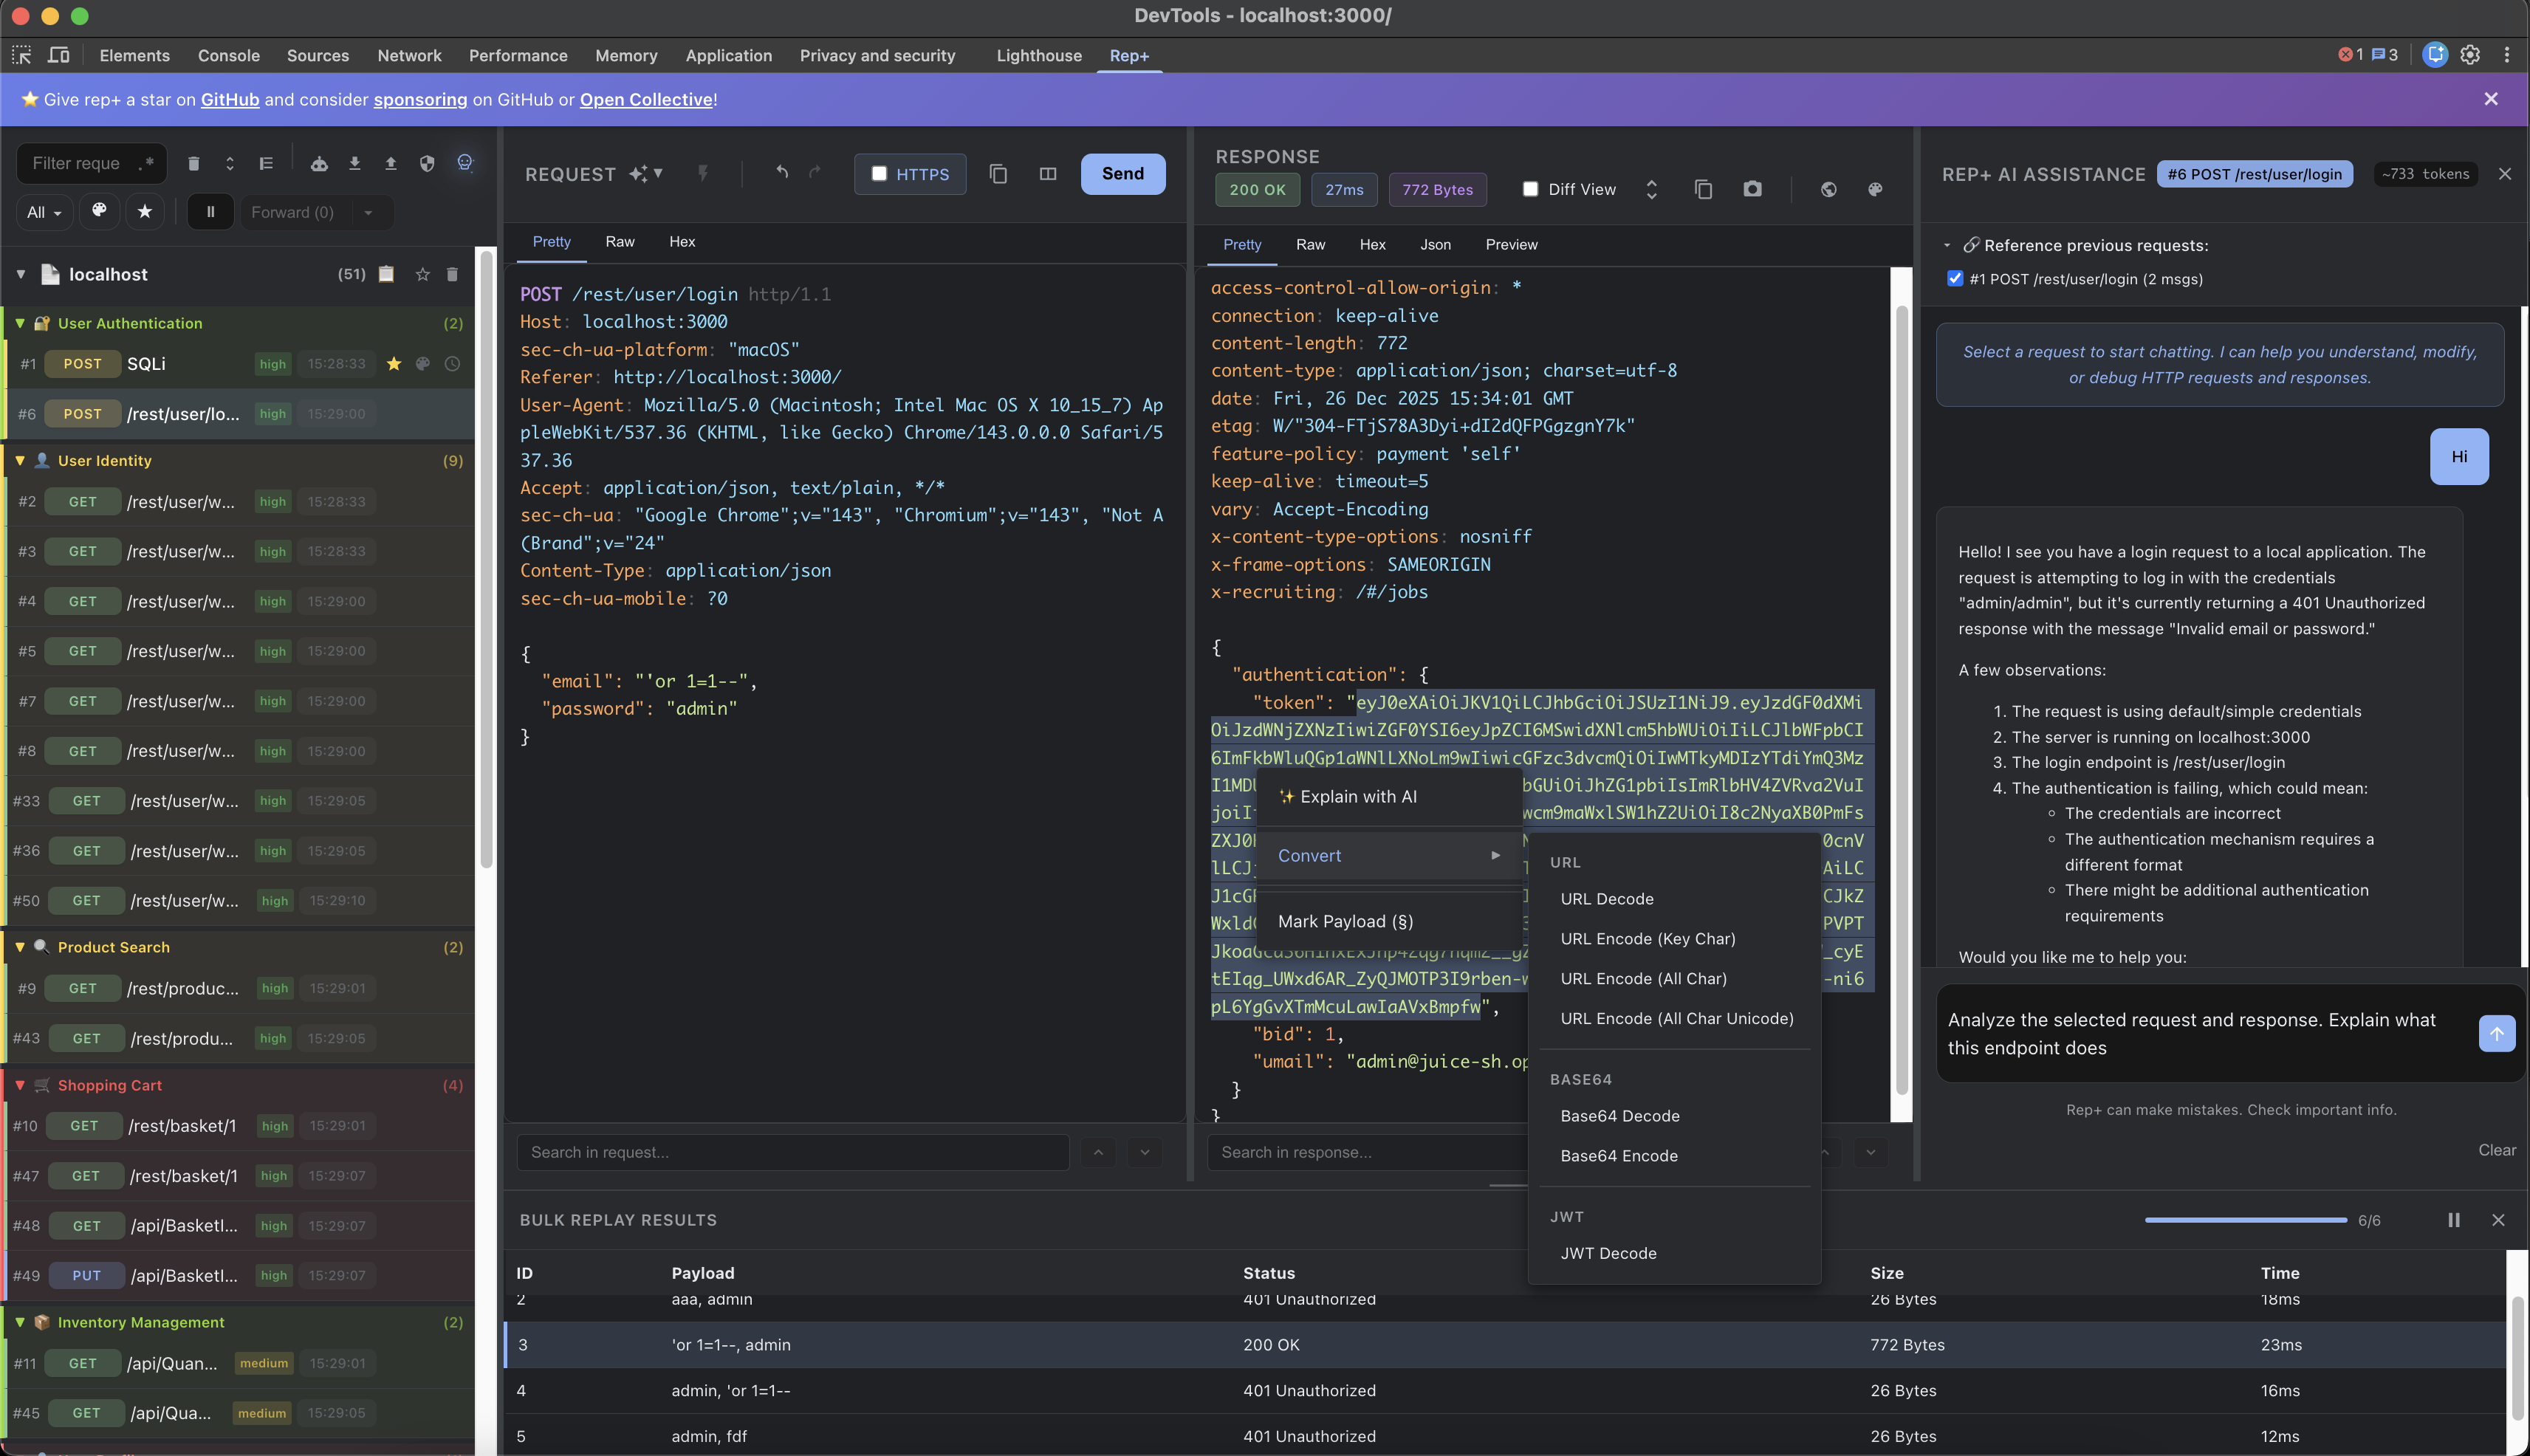 repplus/rep-chrome
rep+ — Burp-style HTTP Repeater for Chrome DevTools with built‑in AI to explain requests and suggest attacks
 martinastarone/cve-2026-2441
Detailed proof-of-concept and technical analysis for CVE-2026-2441, a Chrome CSS use-after-free vulnerability enabling sandboxed renderer RCE via…
 theemperorspath/cve-2026-2441-poc
Proof-of-concept exploit for CVE-2026-2441, a Chrome CSS Use-After-Free in Blink CSSFontFeatureValuesMap, achieving renderer RCE via V8…
 d3b0j33t/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a Chrome CSS use-after-free leading to sandboxed renderer RCE. Includes three trigger methods, heap grooming, and…
 momika233/cve-2024-3400
Proof-of-concept exploit for CVE-2024-3400, demonstrating command injection in Palo Alto PAN-OS with a Python-based backdoor, persistence via…
 ktn1990/cve-2024-43160
The BerqWP – Automated All-In-One PageSpeed Optimization Plugin for Core Web Vitals, Cache, CDN, Images, CSS, and JavaScript plugin for WordPress is…
 anandjogawade/cve-2026-48849-roundcube-webmail-stored-xss
This repository documents CVE-2026-48849, a Stored Cross-Site Scripting (XSS), HTML Injection, and CSS Injection vulnerability discovered in…
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 shoucheng3/nahsra__antisamy_cve-2017-14735_1-5-6
Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…
 ymuraki-csc/cve-2024-3435
Standard Next.js project scaffold with TypeScript, Tailwind CSS, and development server configuration. No security or CVE-related functionality…
 caesarovich/rome-webshell
A powerful and delightful PHP WebShell
 portswigger/splitting-the-email-atom
Research materials and tooling for exploiting email address parser discrepancies to bypass access controls, including fuzzers, Hackvertor tags, CSS…
 itinerisltd/trellis-cve-2018-6389
Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks
 huseyinstif/cve-2026-2441-poc
Proof-of-concept for CVE-2026-2441, a use-after-free in Chrome's CSS engine, demonstrating renderer crash and potential sandboxed code execution via…
 tdonaworth/firefox-cve-2024-9680
Educational analysis of CVE-2024-9680, a use-after-free vulnerability in Firefox's CSS Animation Timeline, with detailed exploit mechanics and…
 segunakinsoyinu/cve-2024-42009-roundcube-xss
Stored XSS exploit for Roundcube Webmail ≤1.6.6 (CVE-2024-42009) with zero-click email exfiltration via CSS animation event handlers. Includes SMTP…