

cli
 httpie/cli
🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.
api-security-testinggeneral-purpose-utilitiesweb-security
httpie/cli🥧 HTTPie CLI — modern, user-friendly command-line HTTP client for the API era. JSON support, colors, sessions, downloads, plugins & more.
 emo-crab/slinger
An HTTP client specifically developed for security researchers
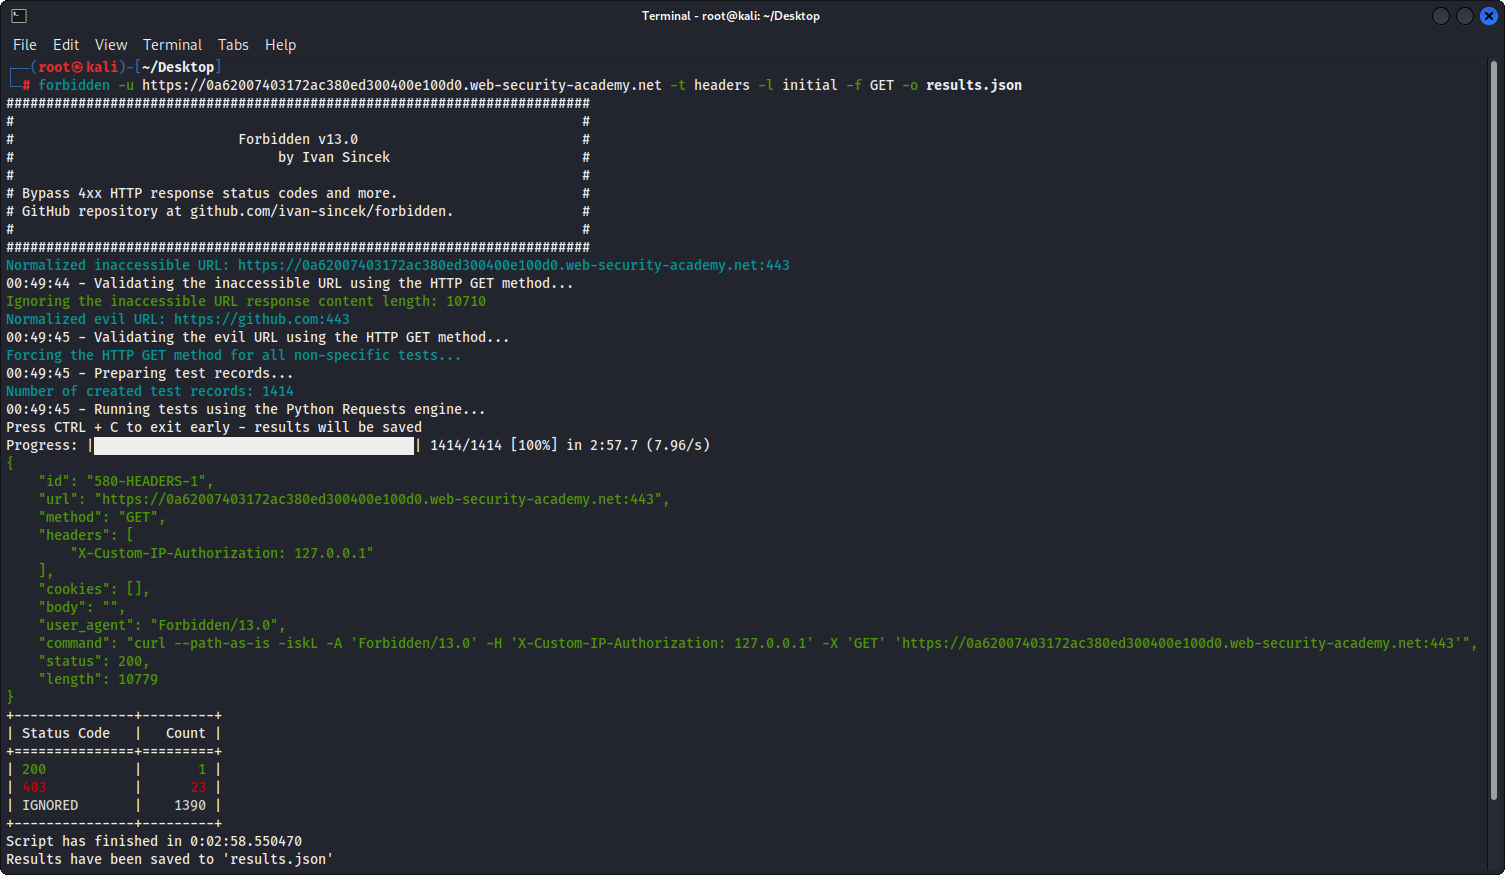 ivan-sincek/forbidden
Bypass 4xx HTTP response status codes and more. The tool is based on Python Requests, PycURL, and HTTP Client.
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 oscerd/cve-2026-49365
PoC reproducer for CVE-2026-49365 (Apache Camel camel-netty-http / camel-undertow): muteException defaults to false, so an uncaught exception's full…
 d0rb/rusttlsx
🦀 Stealth HTTP client for Rust . mimics real browser TLS fingerprints for undetectable requests. Fast, type-safe, and built for precision networking.
 davidblakecoe/axios-cve-2025-27152-poc
Proof-of-concept exploit for CVE-2025-27152 in Axios, demonstrating a server-side request forgery vulnerability in the popular HTTP client library.
 shoucheng3/dromara__hutool_cve-2018-17297_4-1-1111
Comprehensive Java utility library providing modules for cryptography, HTTP client, caching, JSON, scripting, and captcha generation, simplifying…
 shoucheng3/square__retrofit_cve-2018-1000850_2-4-0
Type-safe HTTP client library for Android and Java, enabling REST API communication with annotation-based request configuration and converter support.
 epicosy/retrofit-1
Type-safe HTTP client for Android and Java with annotation-based API binding, converter support, and integration with OkHttp for network…
 forse01/cve-2019-17638-jetty
Exploit for CVE-2019-17638 targeting Jetty Java HTTP server, enabling remote code execution via crafted HTTP requests for security testing and…
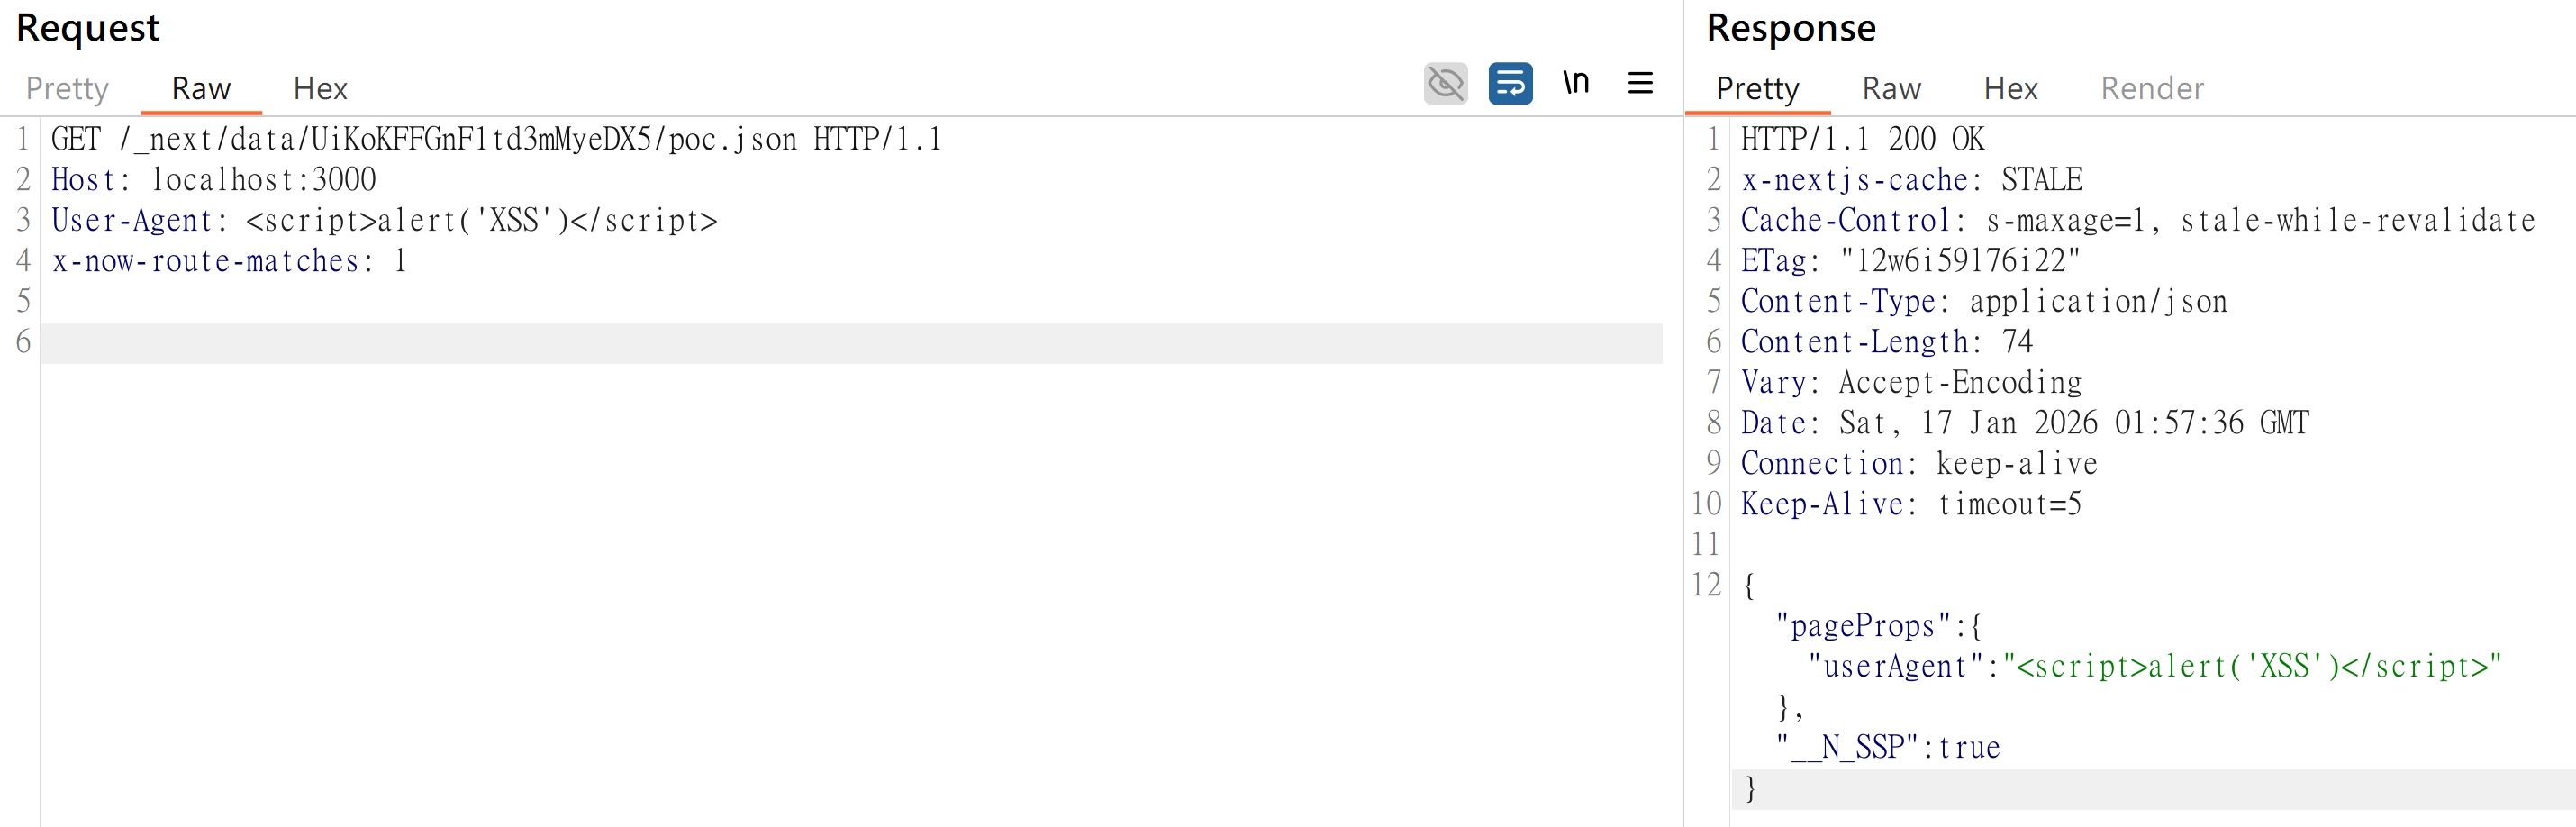 samuel871211/cve-2024-46982-reproduction
Reproduction of CVE-2024-46982
 xiaoqimikko/async-http-client-check
Self-hosted AI workspace with agents, skills, and tools (Gmail, Calendar) that runs entirely on your own provider API keys (BYOK). Bring your own…
 unkn0wn-root/resterm
Terminal API client for HTTP, GraphQL and gRPC. Plain .http files you can diff and version, with workflows, mocks, profiling, tracing, OpenAPI…
 soltanali0/cve-2025-4476-exploit
Python test client that sends HTTP GET requests with oversized Authorization headers to trigger header-parsing bugs like CVE-2025-4476. For…
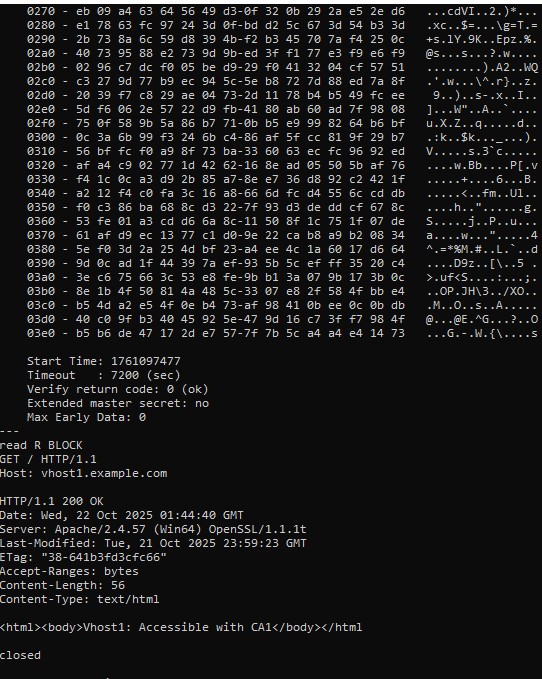 absholi7ly/cve-2025-23048-poc
Apache HTTP Server versions 2.4.35 – 2.4.63 are vulnerable to a client certificate authentication bypass when TLS 1.3 session resumption is used…
 coana-tech/cve-2022-0155-poc
Proof-of-concept demonstrating CVE-2022-0155 cookie theft via HTTP redirect in follow-redirects npm package, including Express server and client…
 jpillora/chisel
Fast TCP/UDP tunnel over HTTP with SSH encryption, supporting reverse port forwarding, SOCKS5 proxy, and client authentication for secure network…