
sqlipy
 codewatchorg/sqlipy
SQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
api-security-testingpenetration-testingvulnerability-scanners+2
262
codewatchorg/sqlipySQLiPy is a Python plugin for Burp Suite that integrates SQLMap using the SQLMap API.
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 ngalongc/openapi_security_scanner
Automated authorization security scanner for OpenAPI-based APIs. Tests GET endpoints with multiple credential sets to detect privilege escalation and…
 hahwul/smugglex
Rust-powered HTTP Request Smuggling Scanner.
 moopinger/smugglefuzz
A rapid HTTP downgrade smuggling scanner written in Go.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 nicholasaleks/crackql
GraphQL penetration testing tool that exploits weak rate limits and cost analysis to brute-force credentials, bypass 2FA, enumerate users, and fuzz…
 hahwul/gori
A fast, keyboard-driven HTTP intercepting proxy and hacking & pentesting toolkit for the terminal.
 appsecco/dvcsharp-api
Damn Vulnerable C# Application (API)
 sech0us3/waf-checker
Automated WAF assessment tool that detects firewall vendors, tests 19 attack categories with advanced evasion payloads, and provides color-coded…
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
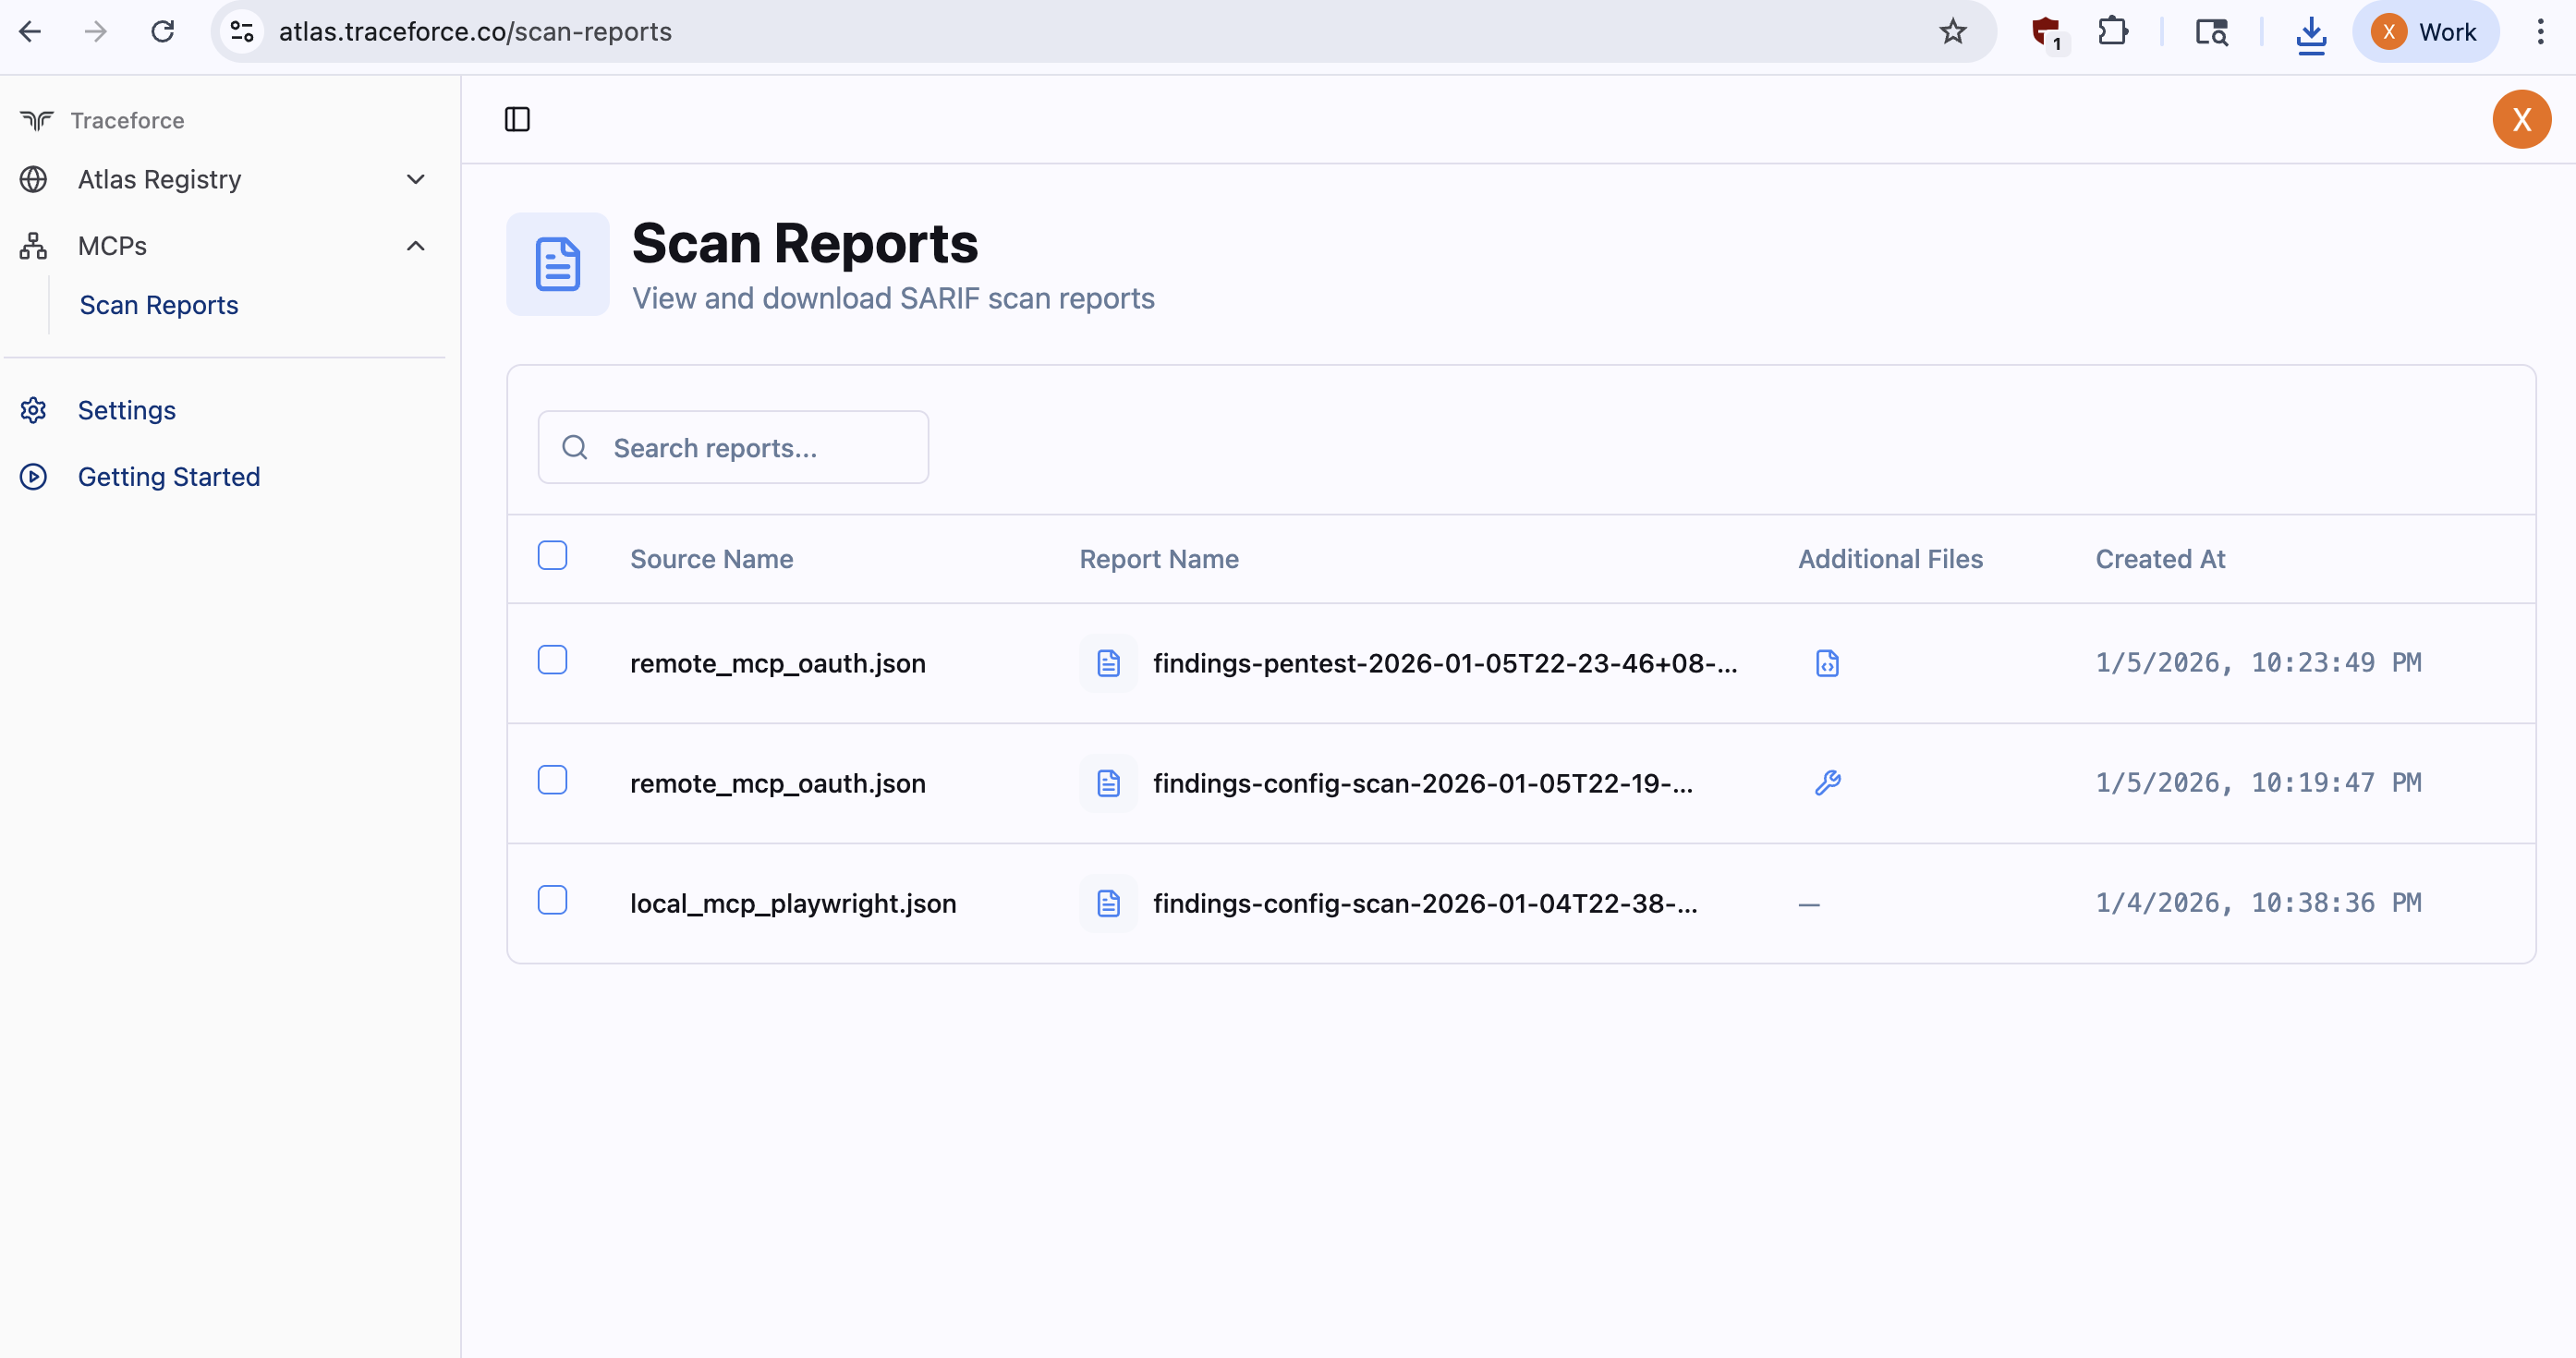 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
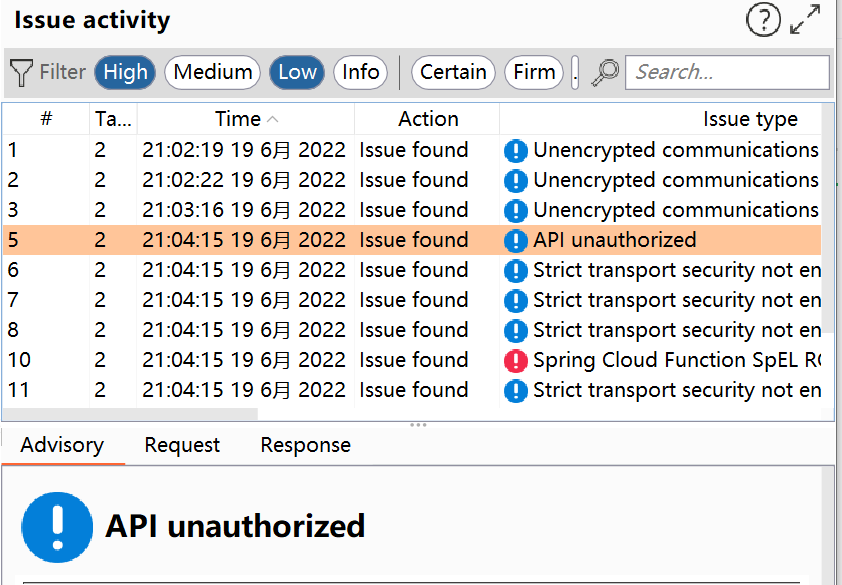 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 shaniidev/bug-reaper
Web2 bug bounty Agent Skill — evidence-based, no AI slop. Covers 18 vulnerability classes across HackerOne, Bugcrowd, Intigriti, and YesWeHack.
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.