frameworks_opt_net_wifi_CVE-2021-0390

Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.

Android Wi-Fi framework patch for CVE-2021-0390, addressing a remote code execution vulnerability in the Wi-Fi subsystem.

about CVE-2018-14667 from RichFaces Framework 3.3.4

Android framework vulnerability analysis and exploitation demonstration for CVE-2023-21285, providing a no-patch test case for security researchers.

PoC for CVE-2022-26134, a Confluence Server OGNL injection vulnerability, built on the pocsuite3 framework for authorized security testing.

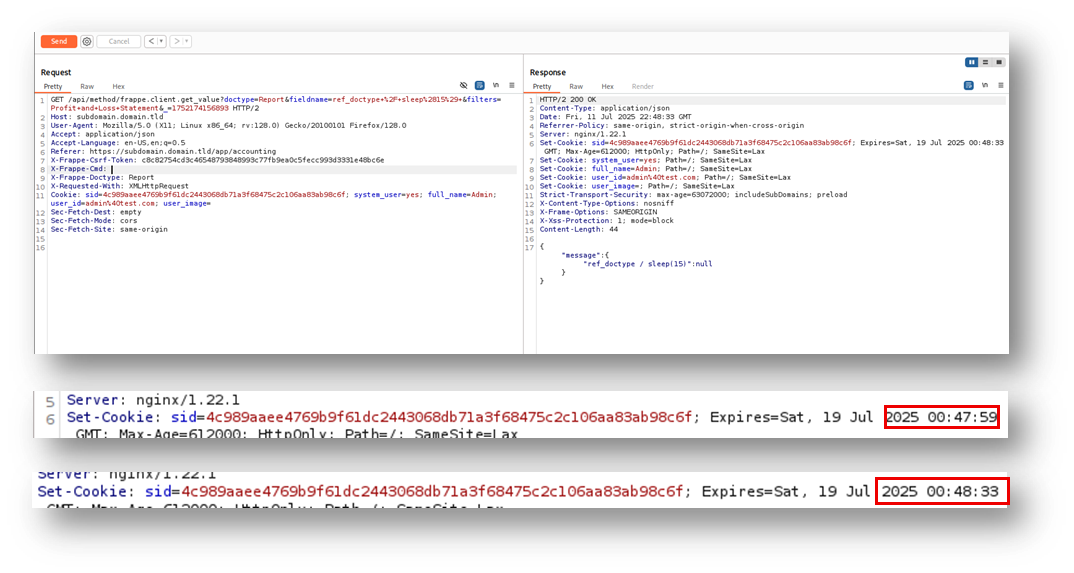
Frappe Framework v15.72.4 was discovered to contain a SQL injection vulnerability via the fieldname parameter in the frappe.client.get_value API…

Spring has Confirmed the RCE in Spring Framework. The team has just published the statement along with the mitigation guides for the issue. Now, this…

Docker container providing a vulnerable environment for CVE-2019-10678, designed for security training and exploitation practice within the Cved…

Advanced network penetration testing toolkit with SSH vulnerability assessment, CVE-2018-15473 exploitation, stealth brute force capabilities, and…

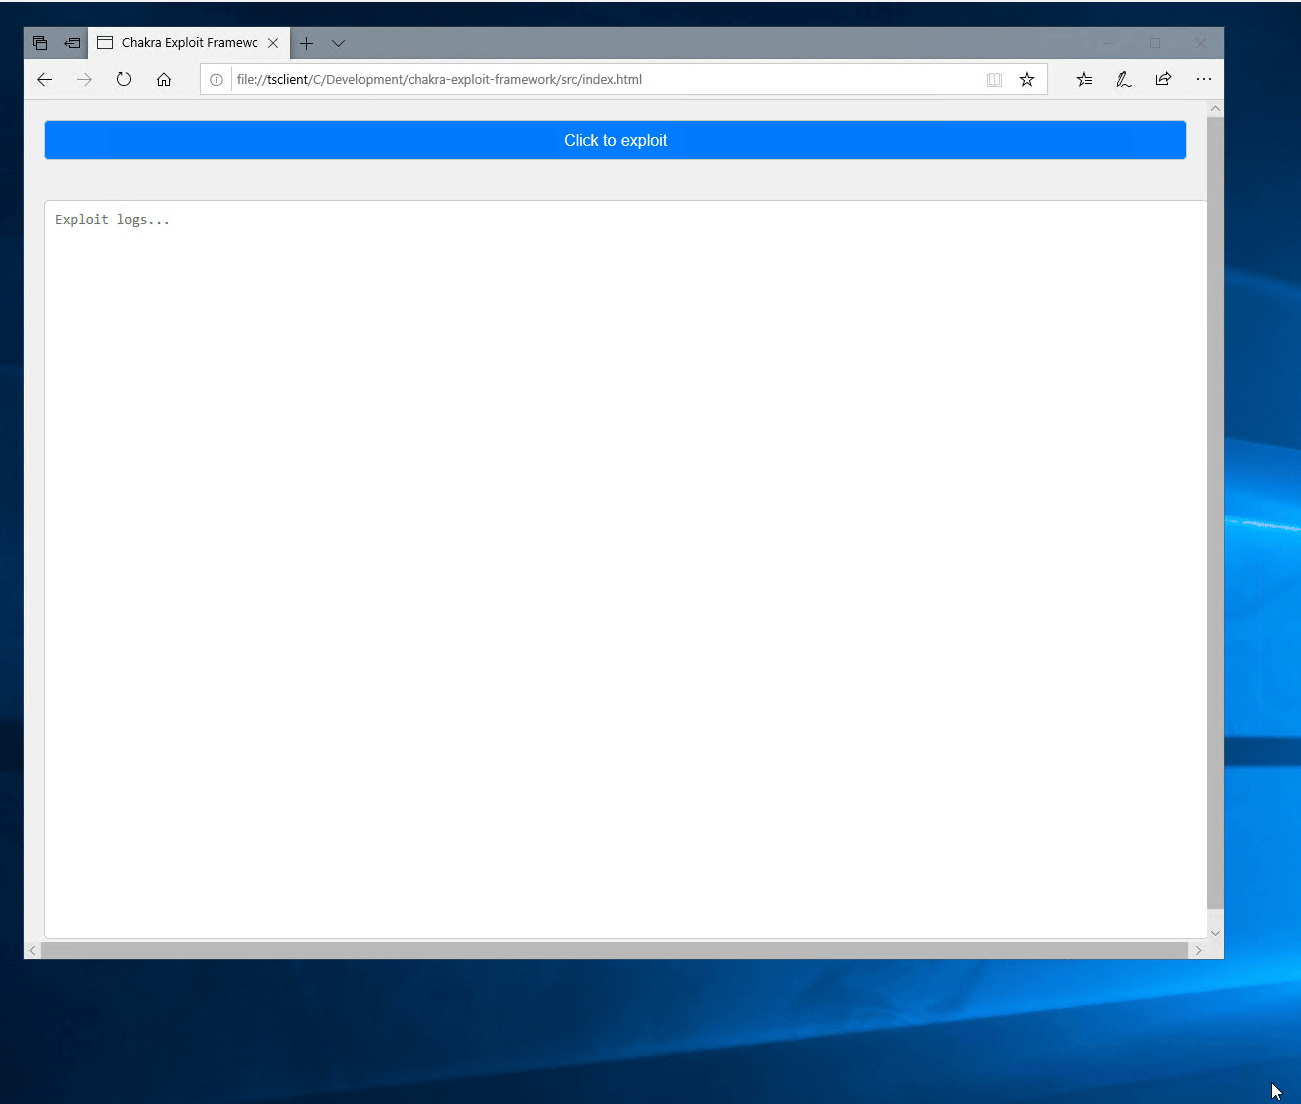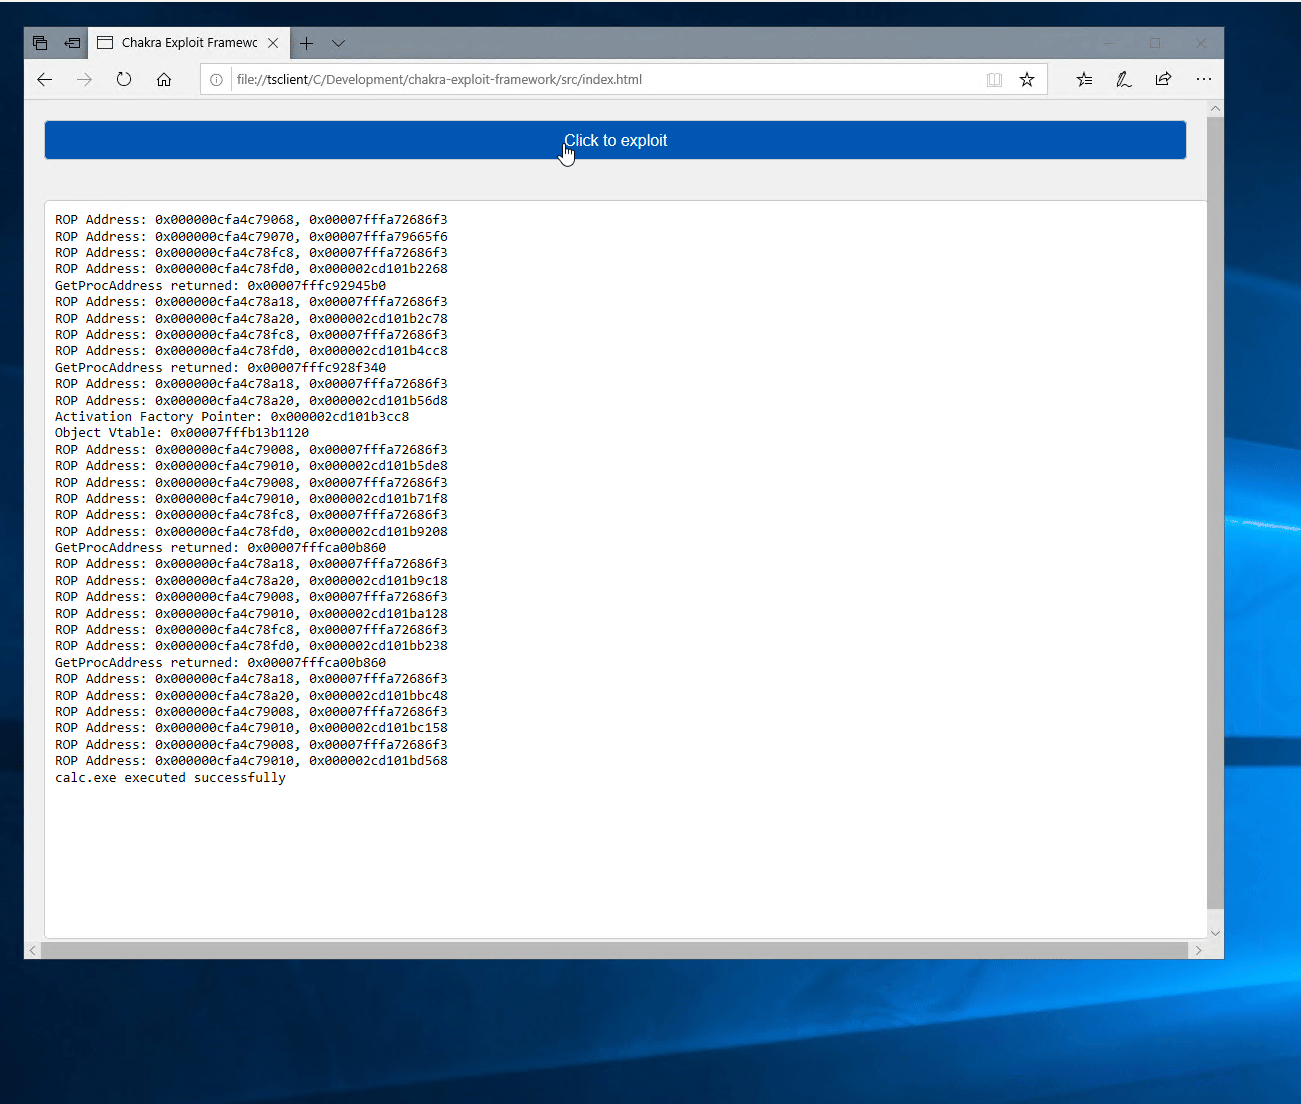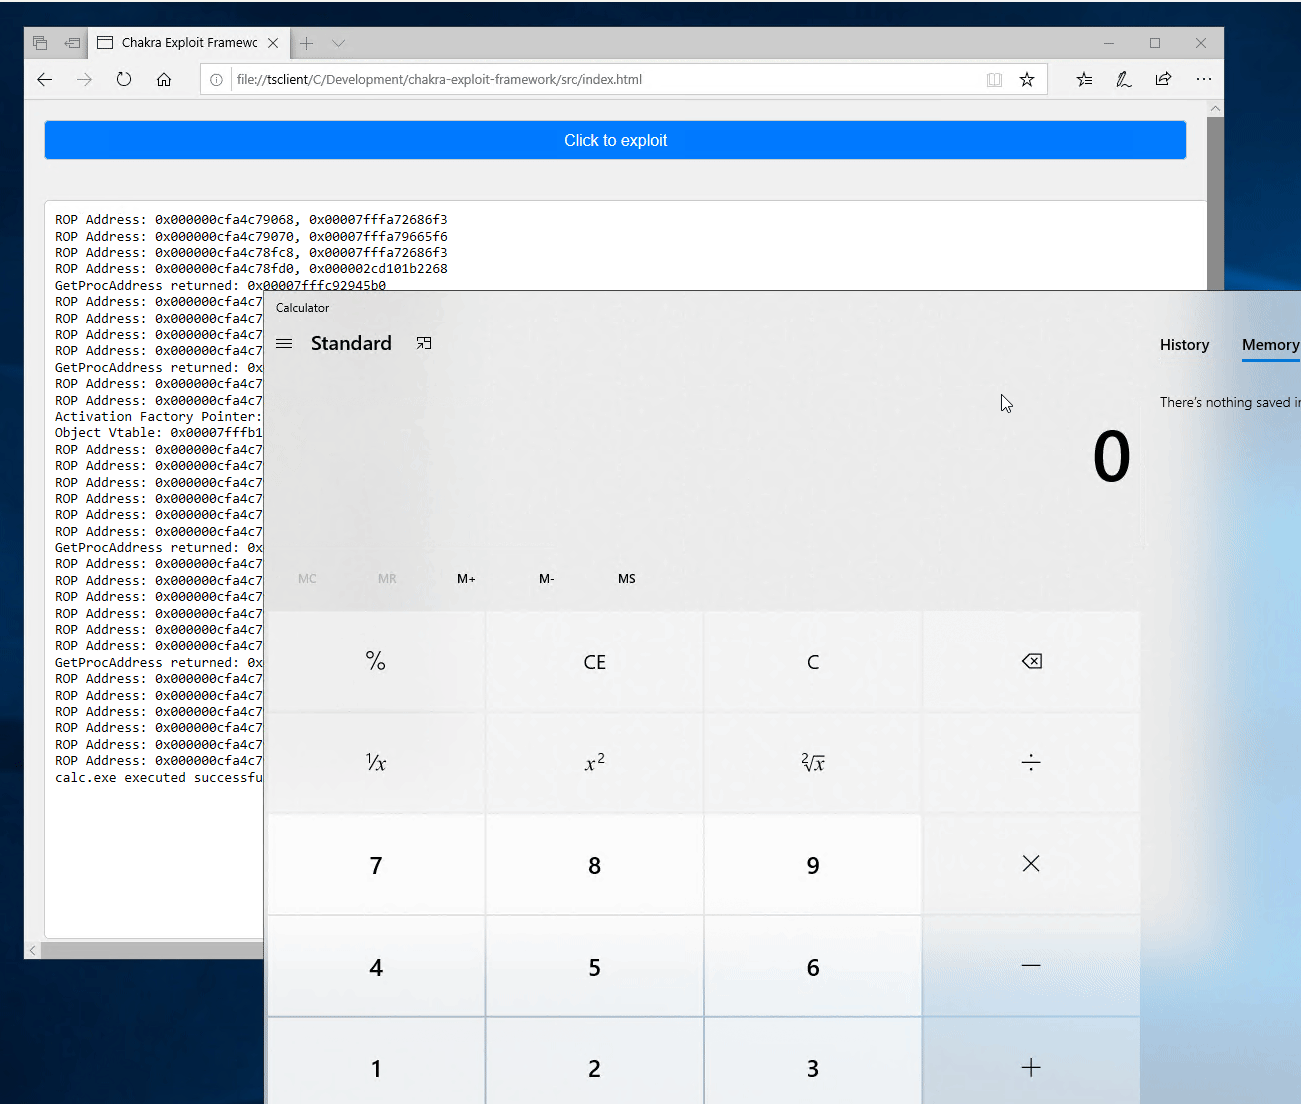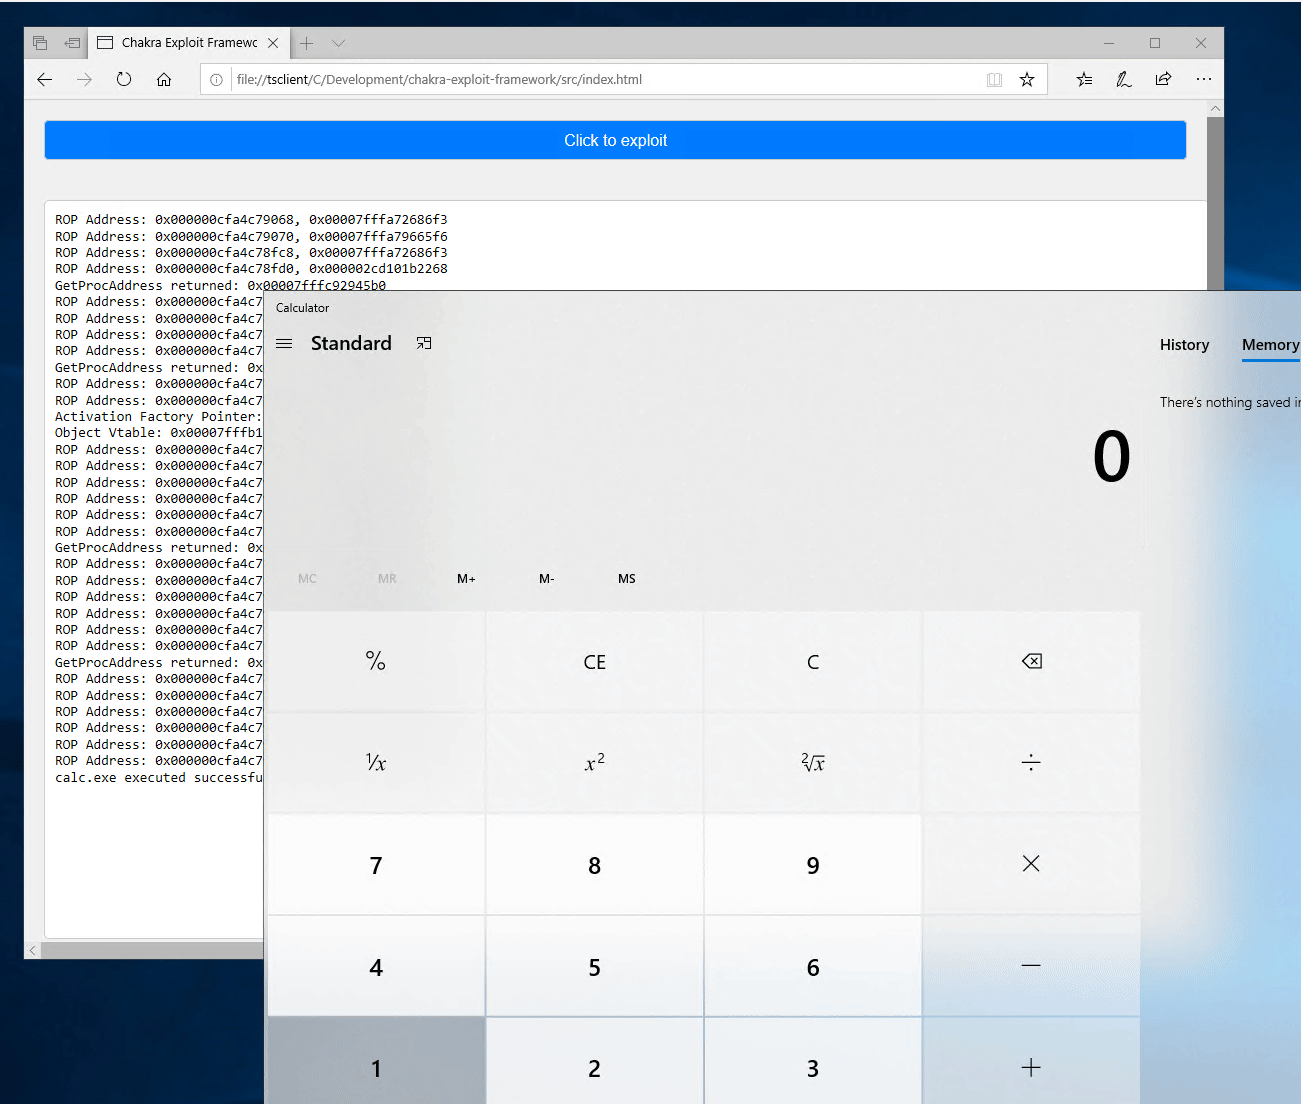
Browser exploitation framework for Chakra (Edge). Written as part of OSEE preparation. Demo bug: CVE-2019-0567

Fully automated Spring4Shell (CVE-2022-22965) + GitLab RCE framework

R2S is a comprehensive exploitation and post-exploitation framework targeting the Next.js React Server Components vulnerability (CVE-2025-55182). It…

LlamaStack-RCE: Deterministic Supply Chain Exploitation & Hardening Framework [CVE-2024-50050] Focus on AI Security Research…

Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…

Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…

Sneeit Framework <= 8.3 - Unauthenticated Remote Code Execution in sneeit_articles_pagination_callback

A XSS vulnerability exists in in React Router's meta()/<Meta> APIs in Framework Mode when generating script:ld+json tags which could allow arbitrary…

Docker-based vulnerable environment for CVE-2018-15473 exploitation, part of the Cved framework for managing and testing against known…

CVE-2025-64328 FreePBX Authenticated Command Injection in the framework module.