
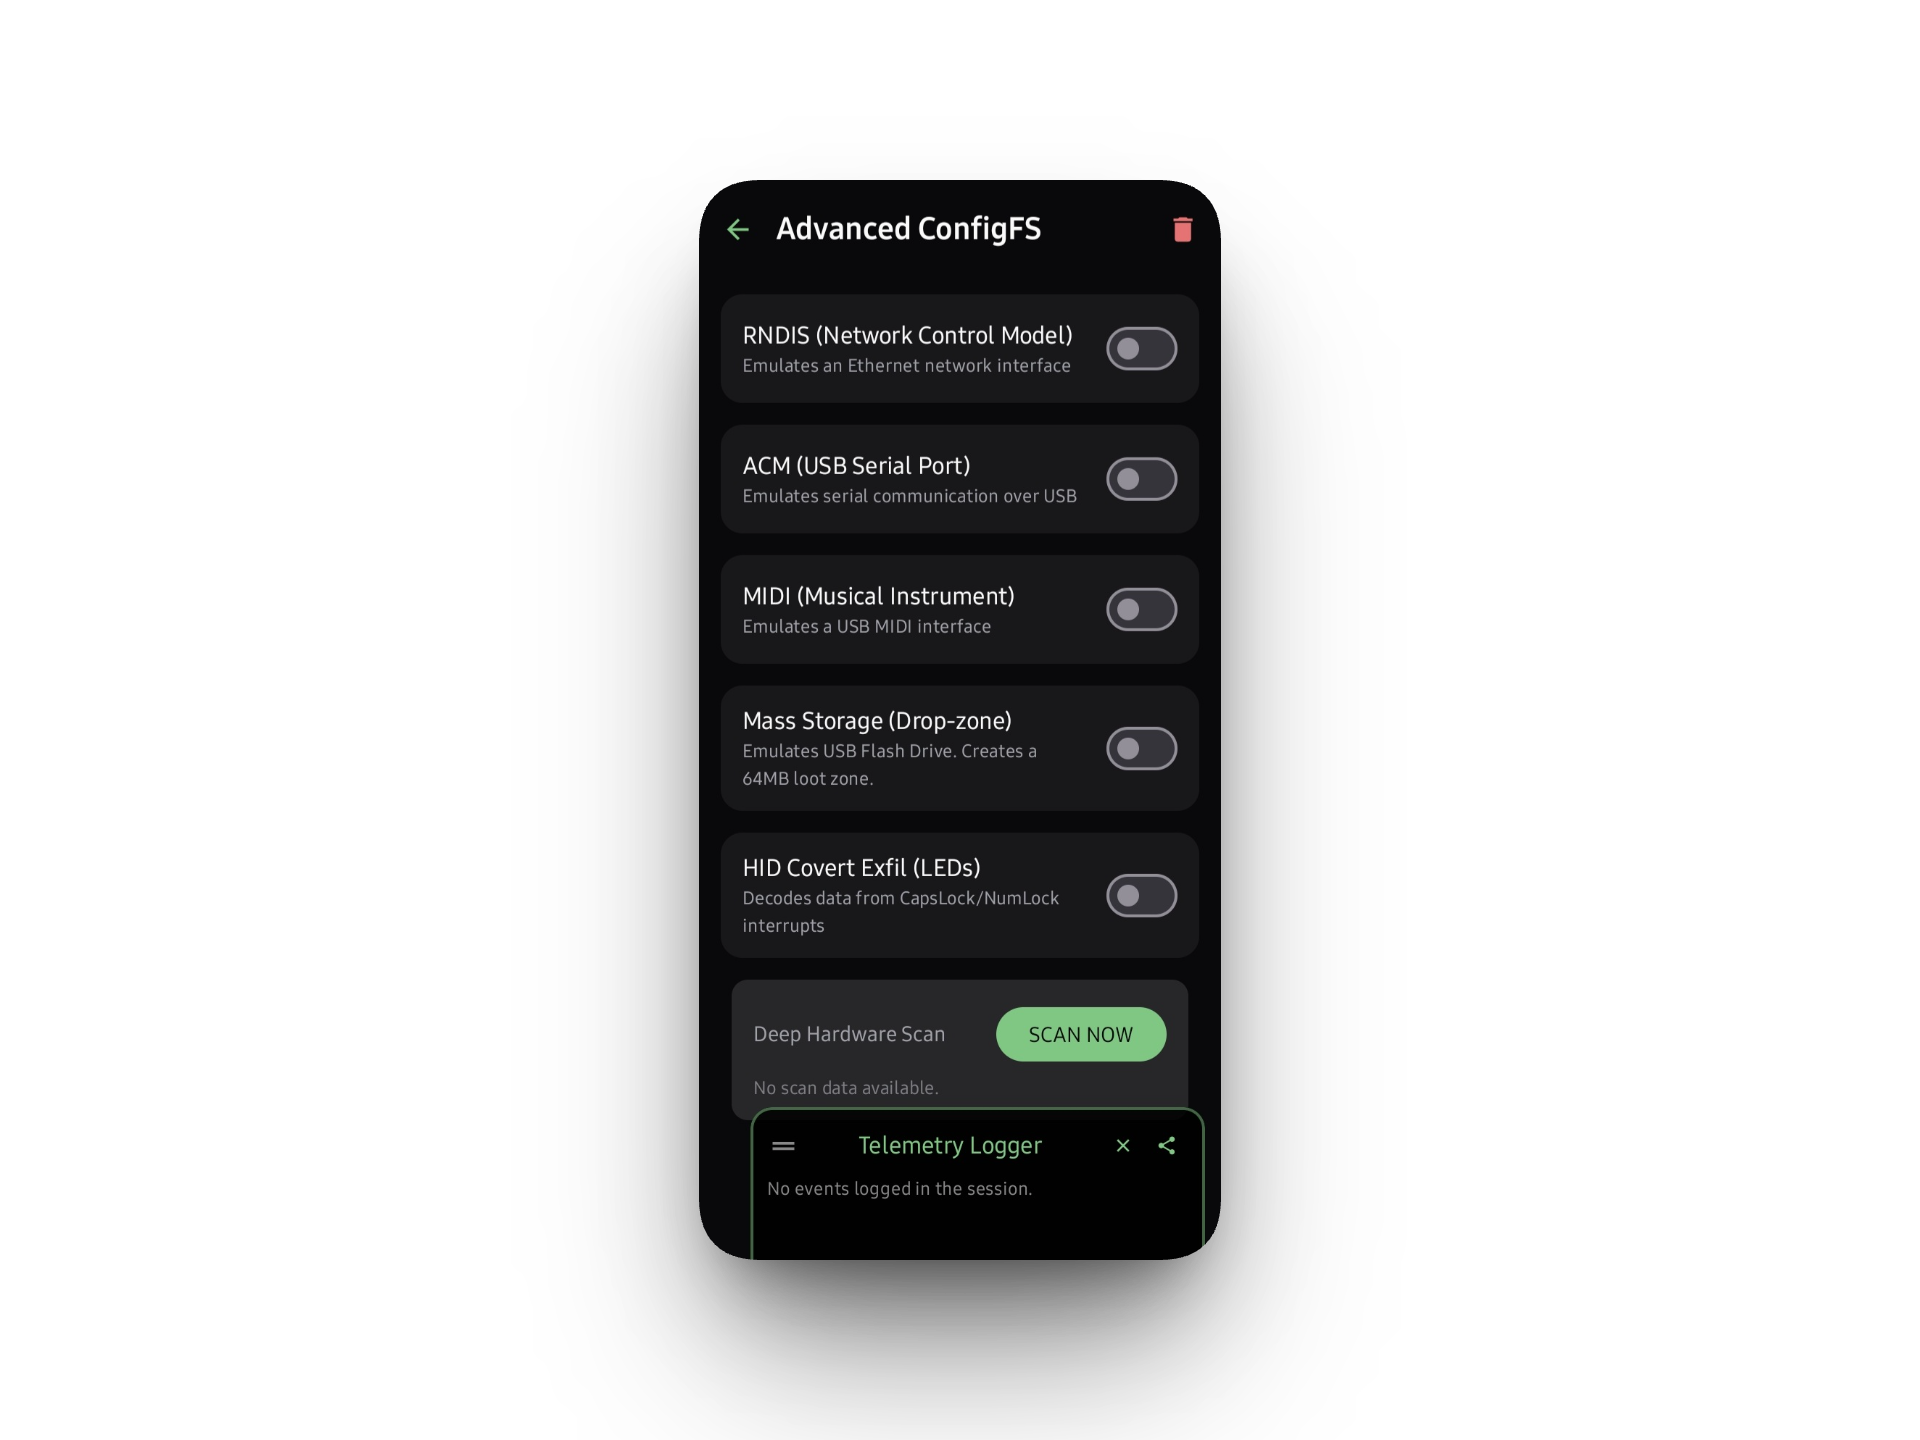
Chimera
 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
android-securitybluetooth-securitycommand-and-control+4
284 months ago
cipher-attack/chimeraPayload injector and HID emulator for Android like Hak5 and rubber ducky
 alw1ez/arkhota
Arkhota, a web brute forcer for Android.
 demining/pixnapping-attack-on-android
Pixnapping Attack: Compromising private keys and seed phrases through vulnerability CVE-2025-48561 represents a new critical threat to the Bitcoin…
 sterrasec/apk-interceptor
Android deeplink, Intent, and WebView bridge assessment helper for ethical hacking
 a2333c/dfroot
Android root tool for Samsung Galaxy S25 Ultra (SM-S938B) that chains DirtyFrag CVE-2026-43284 and CVE-2026-43499 to gain root automatically at boot…
 41yn14/cve-2024-0039-exploit
Эксплойт для уязвимости CVE-2024-0039 на Android, который позволяет выполнять произвольный код через MP4 файл. Этот репозиторий создан для…
 pushkarreddyy/radioguard
Zero-Trust Cellular Defense Sub-Service for Android (IMSI-Catcher, 2G SMS Blaster, and 4G aLTEr Detection & Safe Routing)
 wzhdgithub/ghostlock
CVE-2026-43499 futex PI stack UAF ???????? - Android GKI 6.1~6.12 ??????? pselect() + futex PI ????????????,??? root ??? SELinux??? OPPO Find…
 humoud/apksneeze
A tool that automates the mundane tasks of pentesting Android apps. It uses APKTool and Dex2Jar.
 nighthawkk/audioserver-voip-recorder
🔬 An advanced Android research tool for real-time VoIP audio capture (Uplink/Downlink) by dynamically hooking libaudioflinger.so. Tested and built…
 ejfkdev/avdroot
Root an Android Studio emulator by patching its ramdisk with Magisk — in pure Go.
 wadingporque/apkprobe
APK decompiler & secrets scanner for Android security research! Extract leaked API keys, hardcoded credentials, endpoints from APK files. apk2url,…
 wonjj6768/lenovo-tb365fc-ghostlock-cve-2026-43499
GhostLock (CVE-2026-43499) root + KernelSU LKM for the Lenovo TB365FC (ZUXOS / Android 16, kernel 5.15.170)
 l0lsec/cve-2026-12960
CVE-2026-12960 - Improper Export of Android Application Components in the ASUS Router app (com.asus.aihome). PoC, exploit APK, video, and vendor…
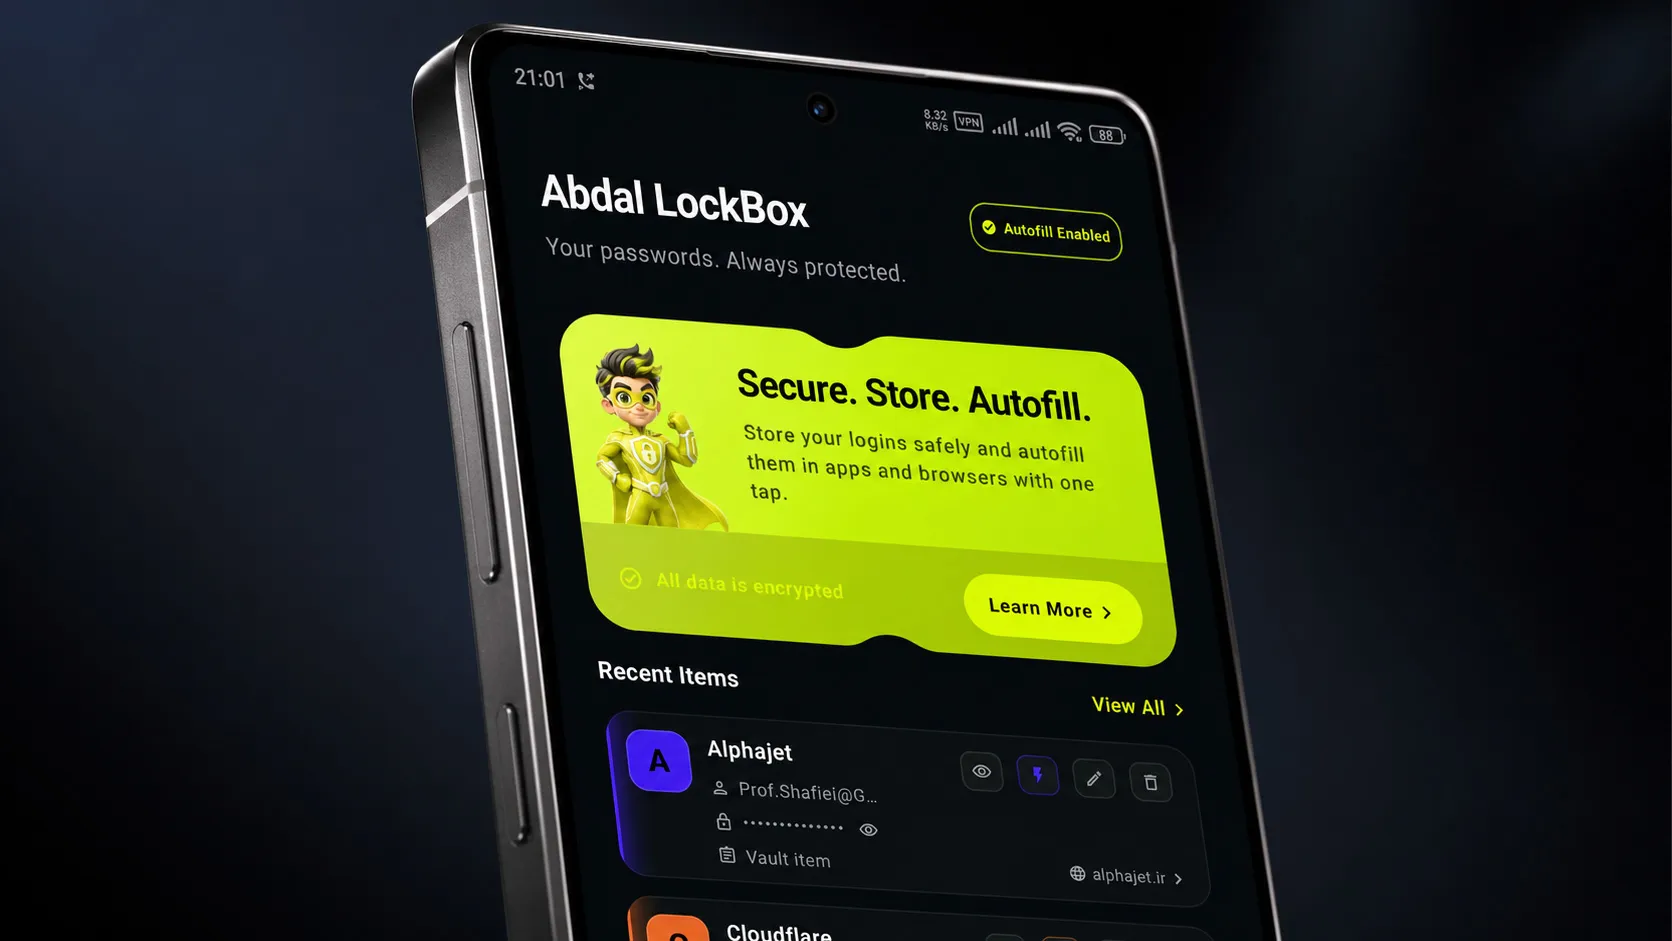
 prof.shafiei/abdal-lockbox
Local-first encrypted password vault for Android with Master Password access, Recovery Key support, Autofill integration, and portable encrypted…
 valentineus/hp-slate7-root-kit
HP Slate 7 2800 Android 4.1.1 rooting kit using CVE-2015-1805.
 bfurkanyildiz/android-rce-analizi
Android CVE-2024-0044, 43093, 23706 zafiyet analizi ve PoC lab ortamı
 actuator/ekoparty
Ekoparty Miami | Interface Anti-Patterns: Exploiting Insecure Navigation in 3rd Party Android App Lockers