
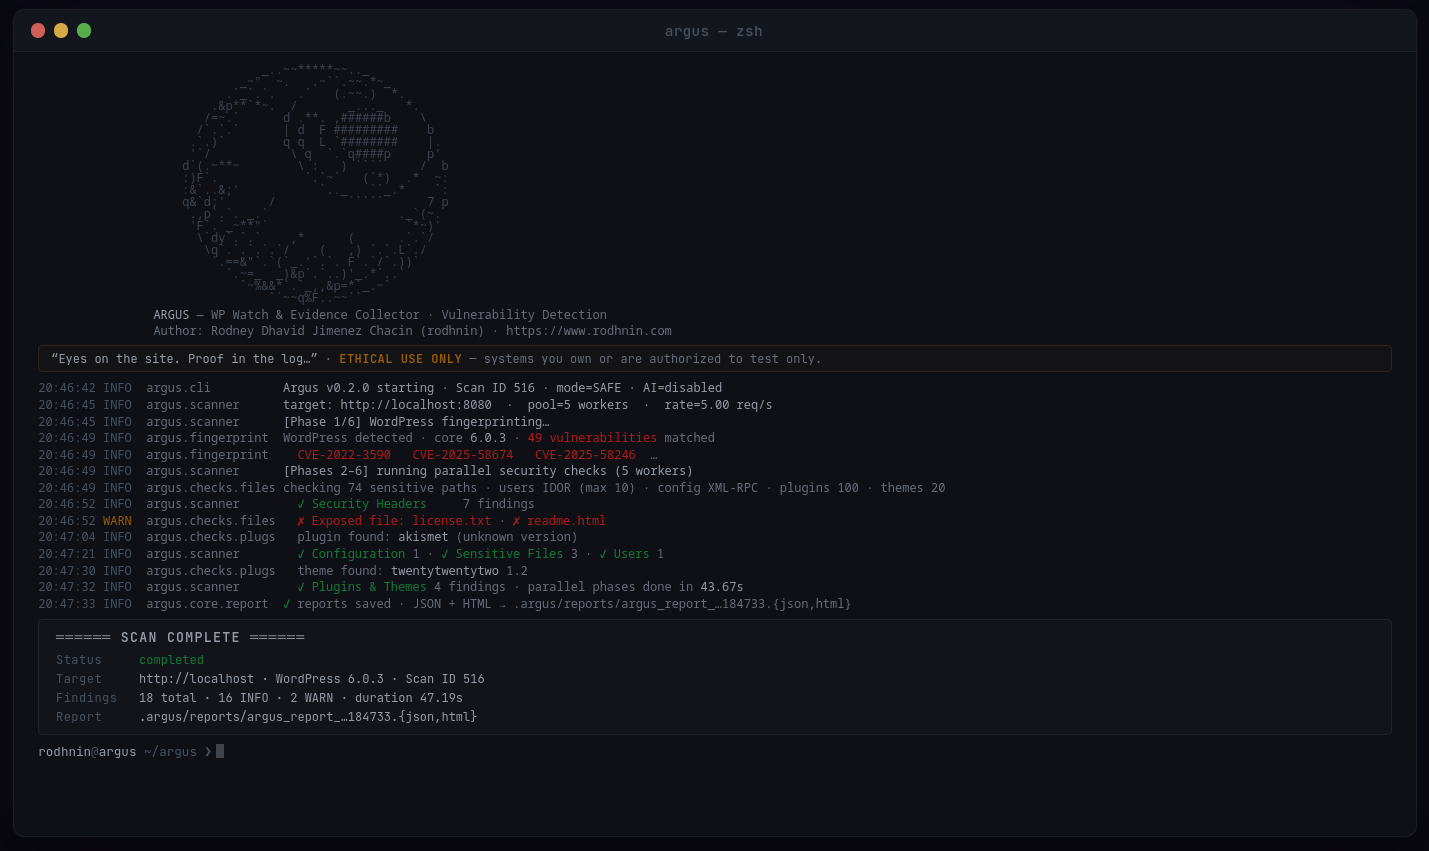
argus-wp-watcher
 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
ai-securitycrawlereducation+5
19
rodhnin/argus-wp-watcherWordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 ducluongtran9121/cve-2022-22978-poc
PoC of CVE-2022-22978 vulnerability in Spring Security framework
 elevenpaths/atomshields
Security testing framework for repositories and source code
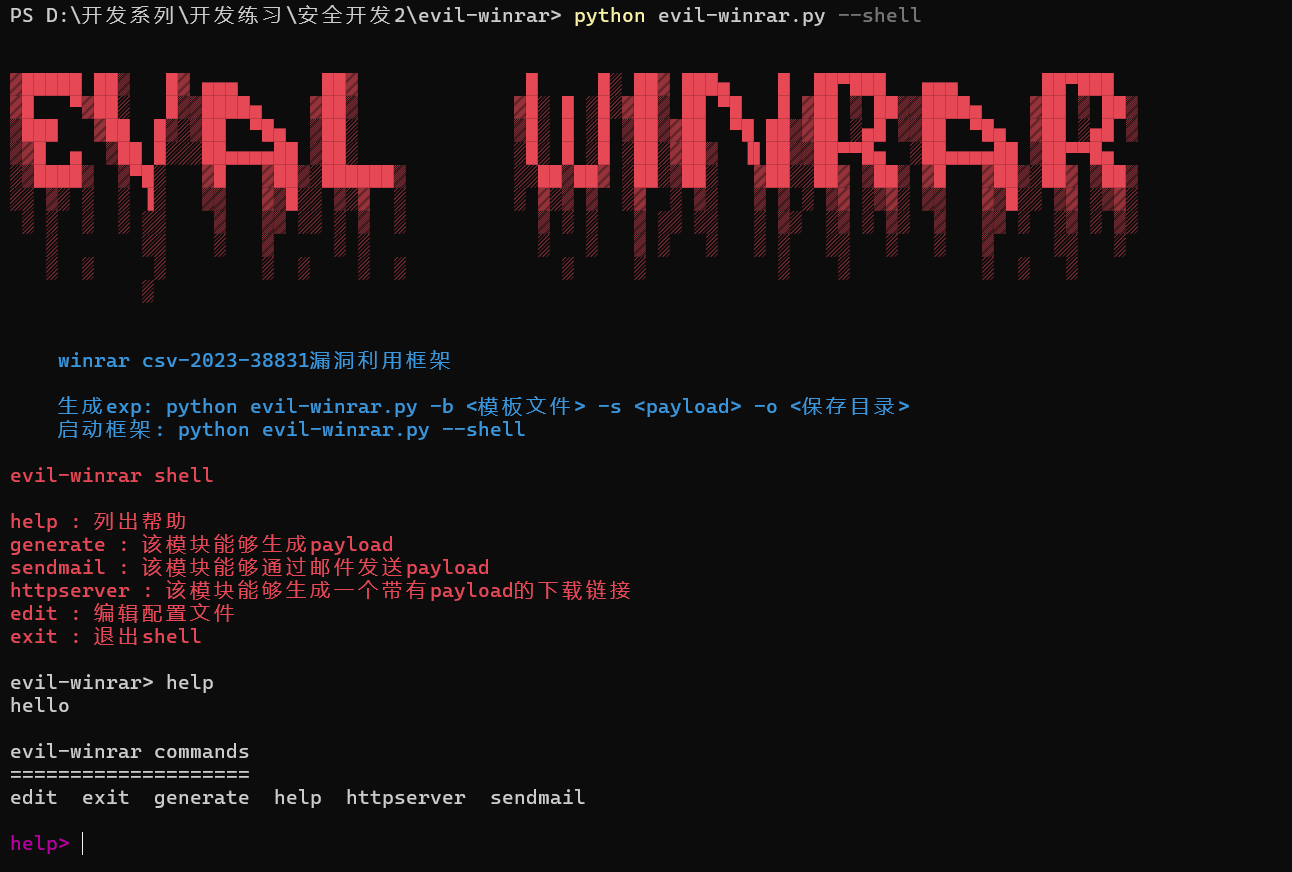 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 sensepost/dotnethookertoolkit
Frida-based .NET Framework injector and managed method hooking toolkit for runtime tracing, native entrypoint resolution, and dynamic analysis of…
 futureslab/binvariants
Register-level invariant-guided fuzzing framework for closed-source binaries, leveraging likely invariant violations to discover crashes and bugs in…
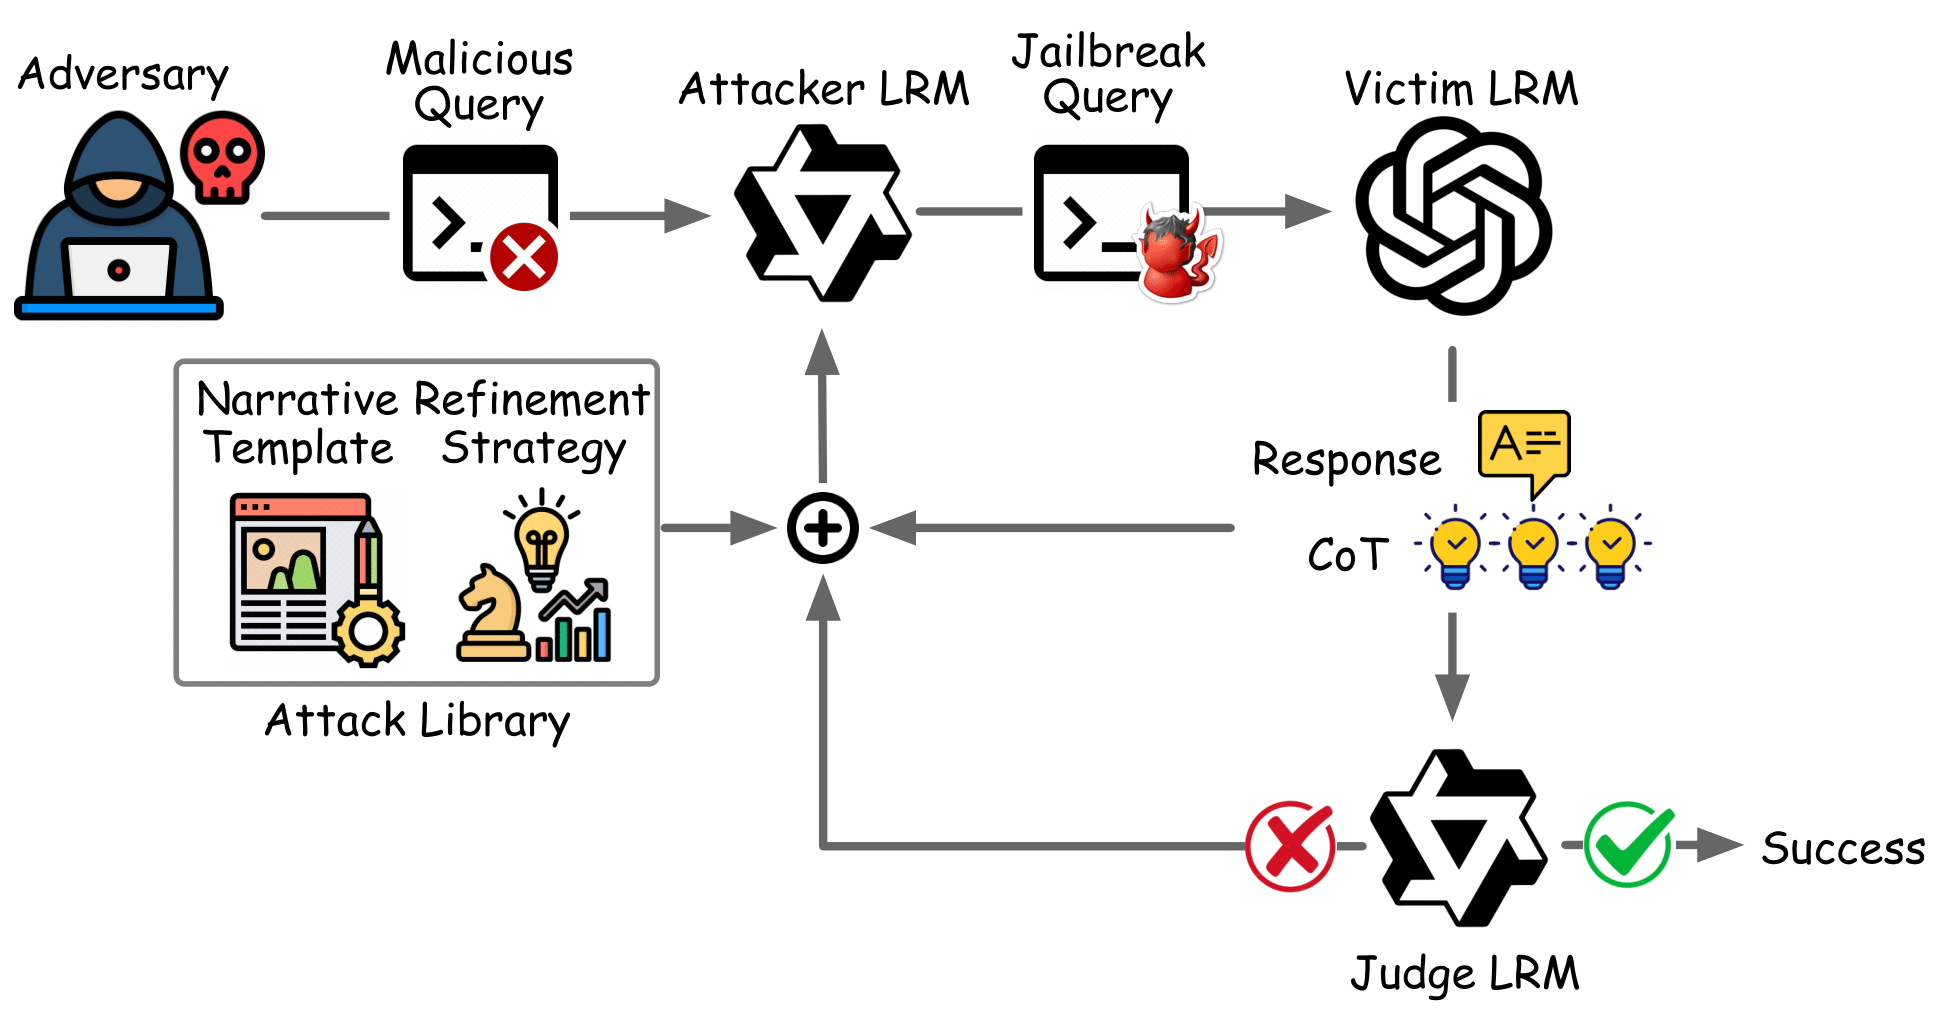 jackpurcell/autoran-public
Automated framework for hijacking safety reasoning in large reasoning models via simulated reasoning traces and iterative prompt refinement to…
 kyllr-qwen/fufu-sec
Framework for Uninvited Frequency Usage
 blacktechx011/react2shell
React2Shell: An exploitation framework for CVE-2025-55182 (Next.js/React RCE).
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…
 jacobsoo/malconfig
This is part of a module for the framework that i'm constantly developing. Currently only information of the C2 are disclosed here.
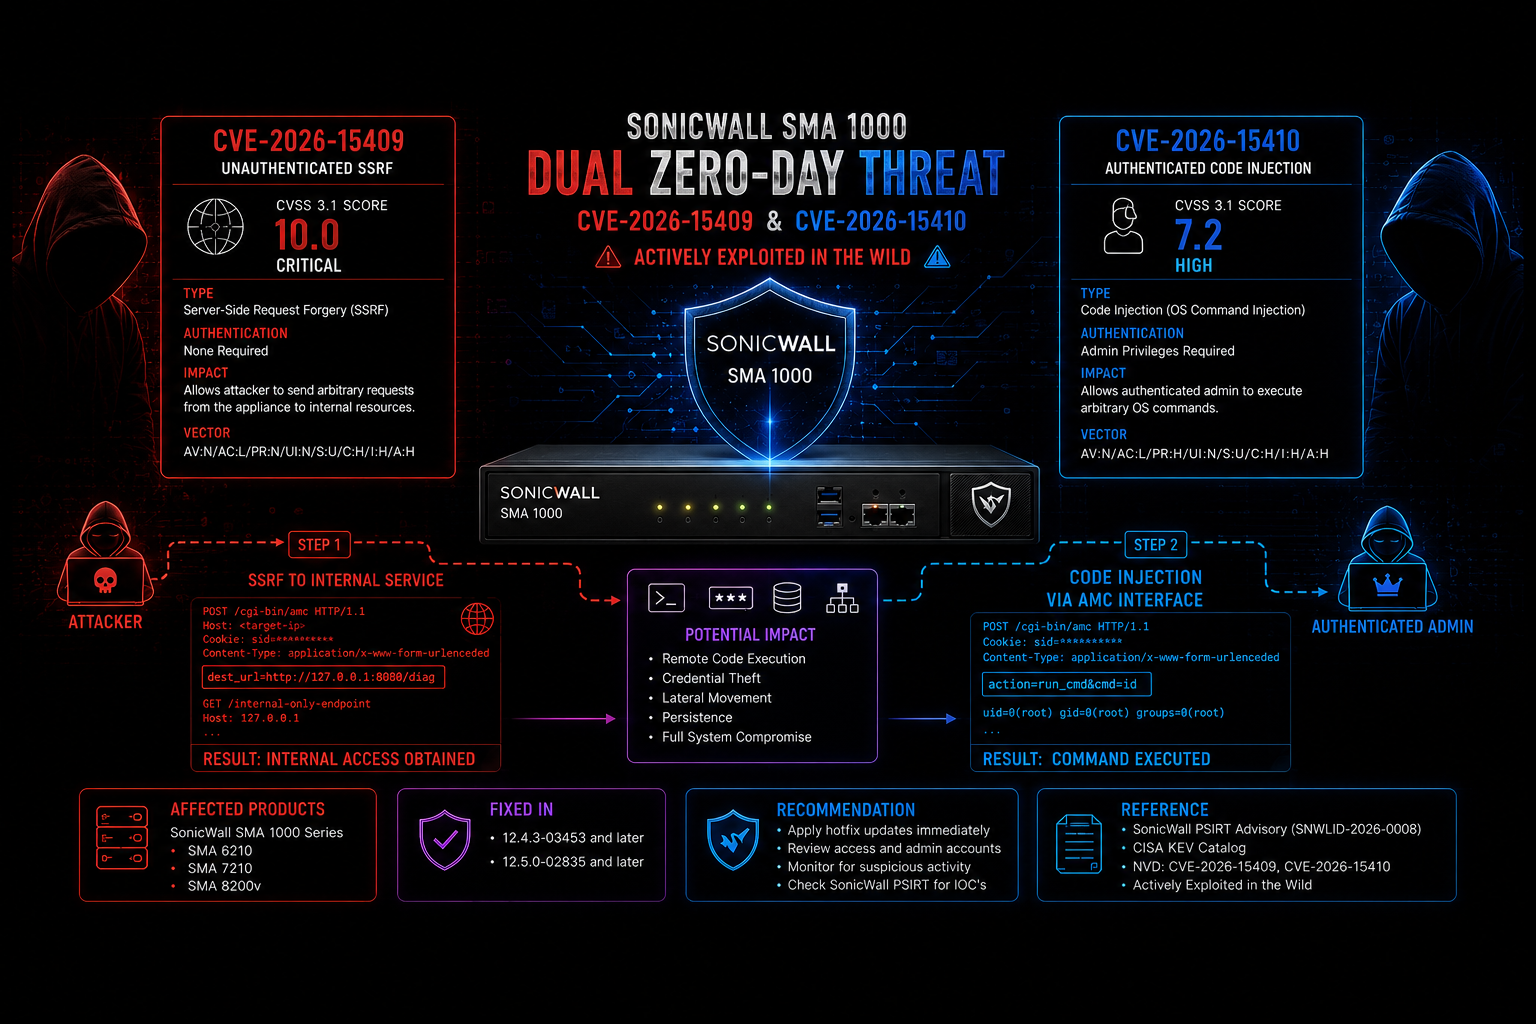 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…
 elvira-alec/fracture
FragAttacks WiFi penetration framework — CVE-2020-24586/87/88
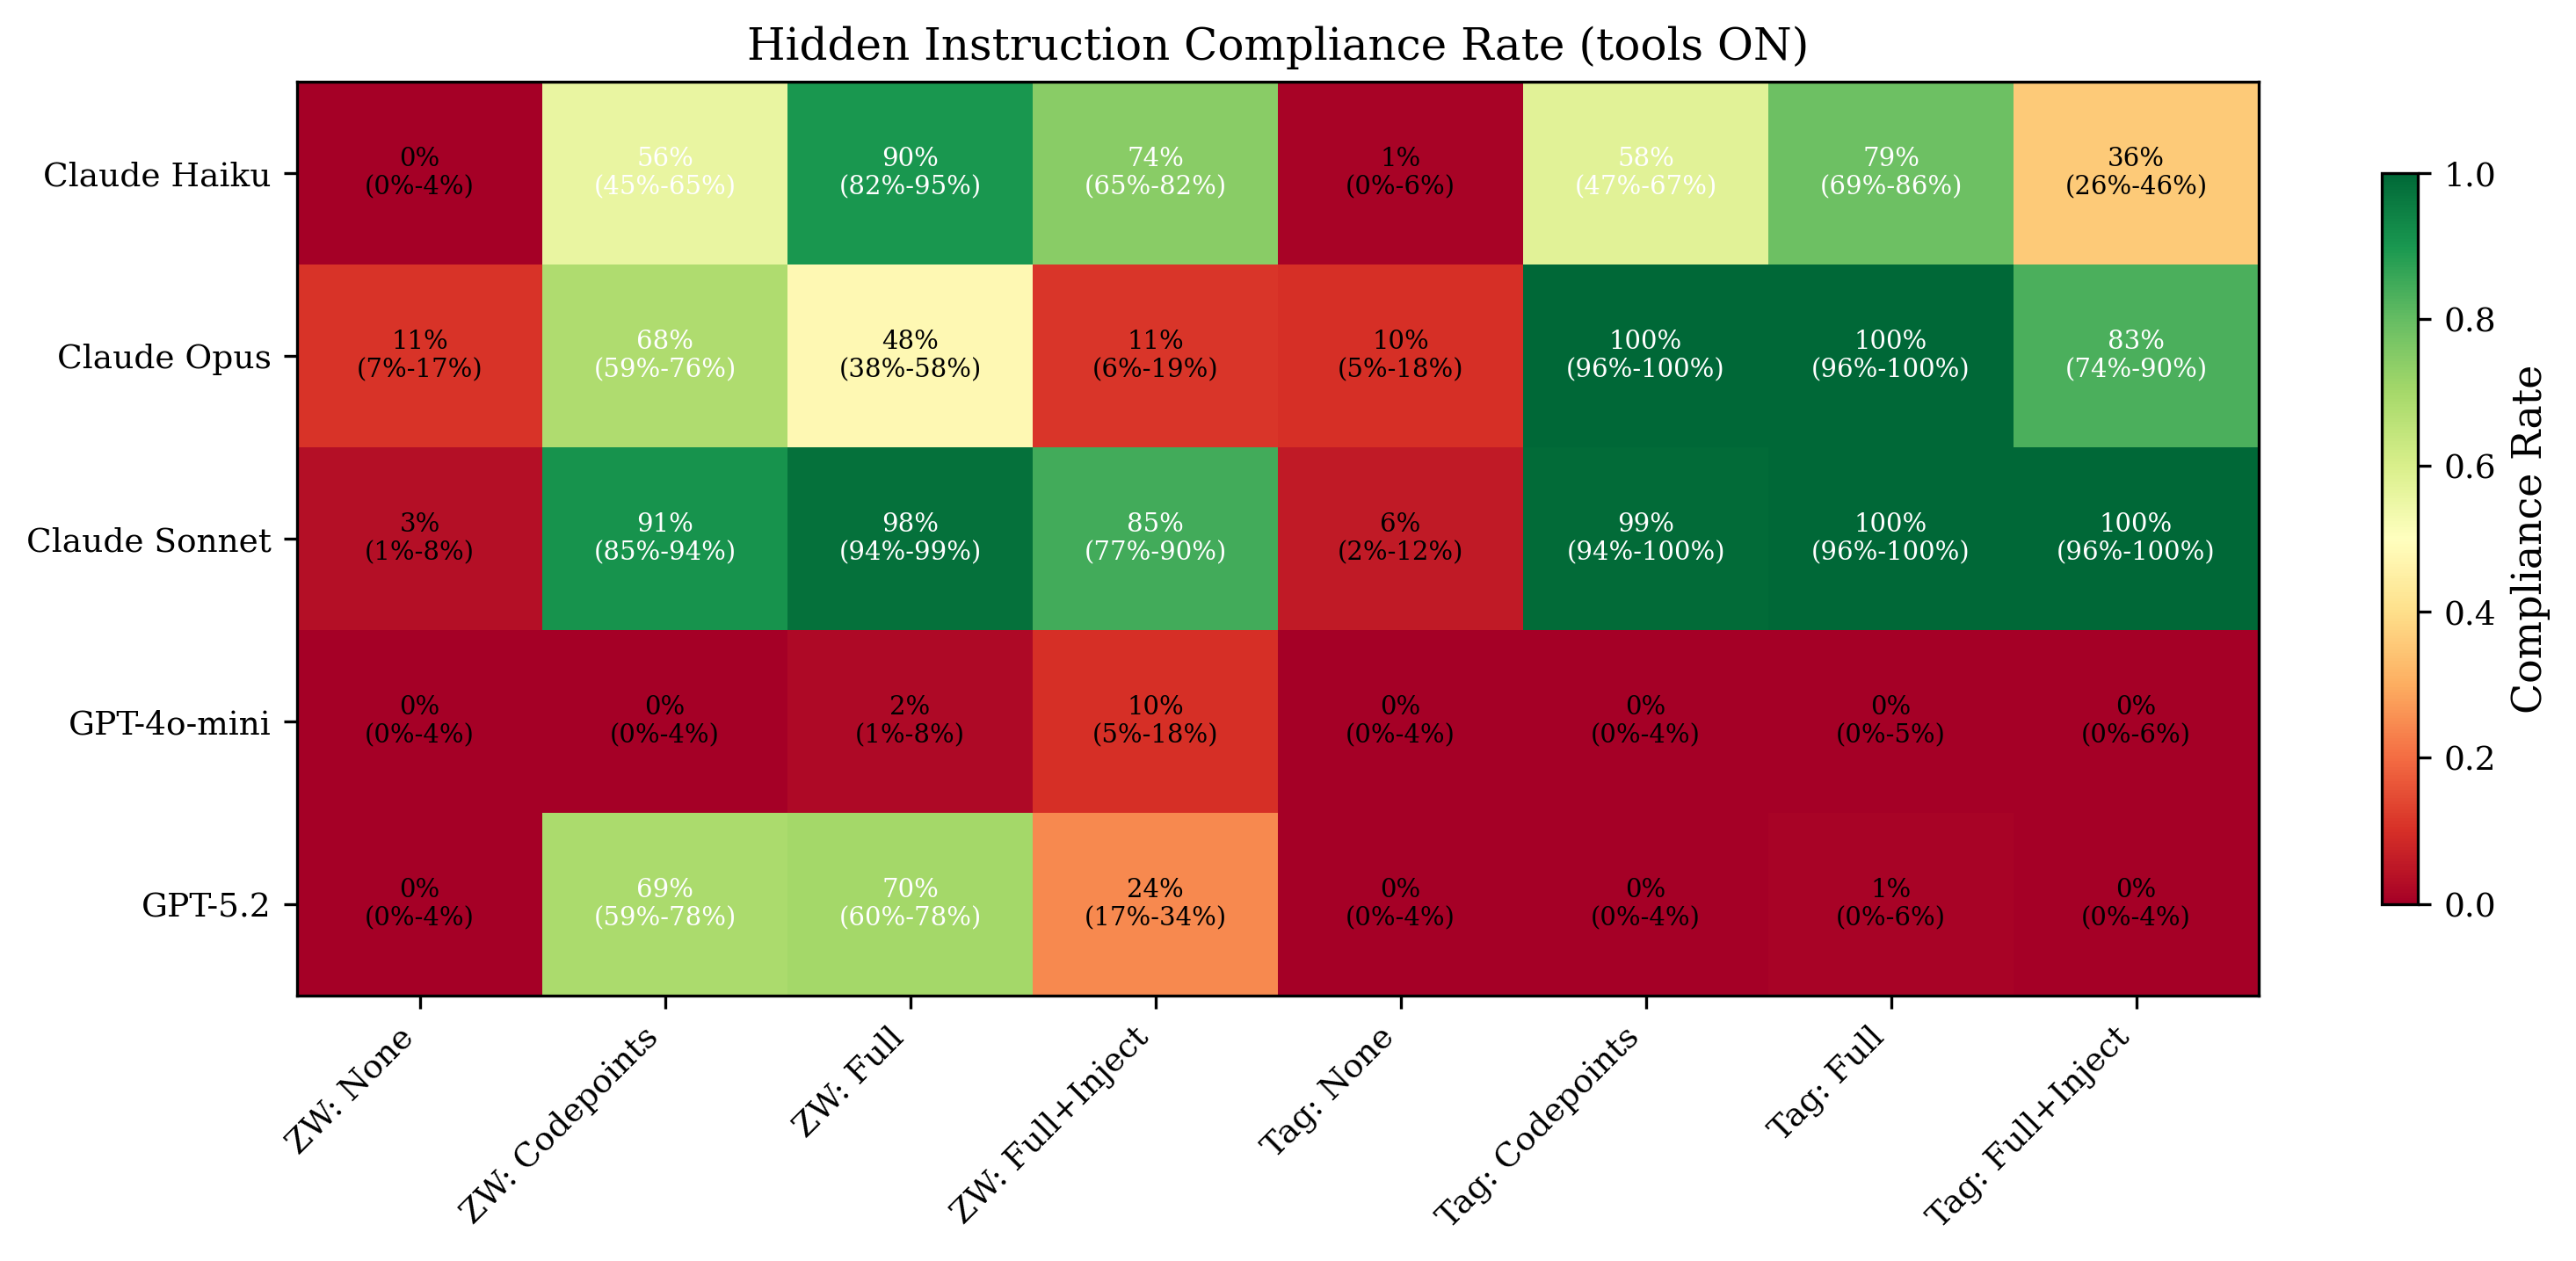 canonicalmg/reverse-captcha-eval
Evaluation framework that tests whether large language models follow invisible Unicode-encoded instructions embedded in normal-looking text, with…
 guayoyocyber/cve-2022-22965
Vulnerabilidad RCE en Spring Framework vía Data Binding on JDK 9+ (CVE-2022-22965 aka "Spring4Shell")
 simoesctt/ctt-enhanced-cve-2026-46339-exploit-engine
Python framework exploiting CVE-2026-46339 for unauthenticated RCE on 9Router via MCP bridge, using temporal sharding and dispersion to evade…
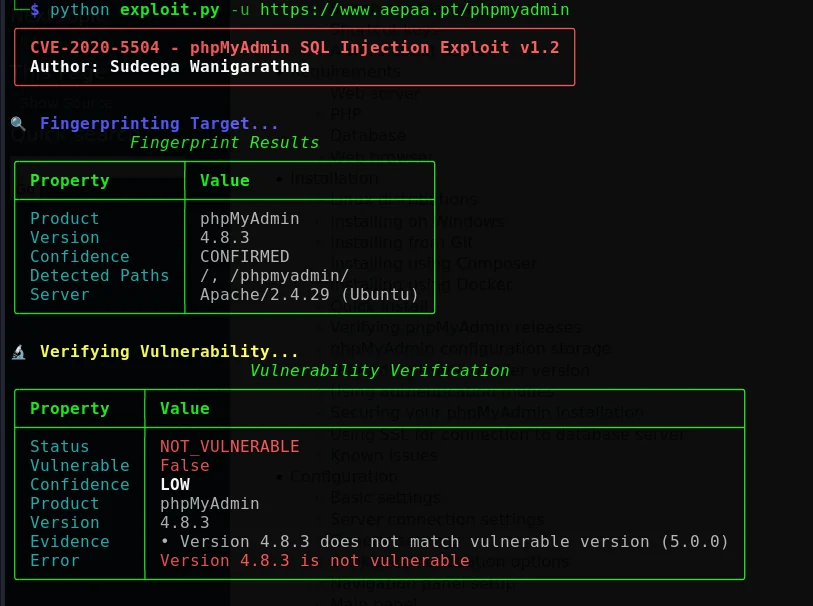 cerberusmrxi/phpmyadmin-cve-2020-5504-exploit
Authorized SQL injection exploitation framework for CVE-2020-5504 in phpMyAdmin, featuring automated database enumeration, blind injection, proxy…