
sj
 bishopfox/sj
A tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
api-security-testingpenetration-testingvulnerability-scanners+1
bishopfox/sjA tool for auditing endpoints defined in exposed (Swagger/OpenAPI) definition files.
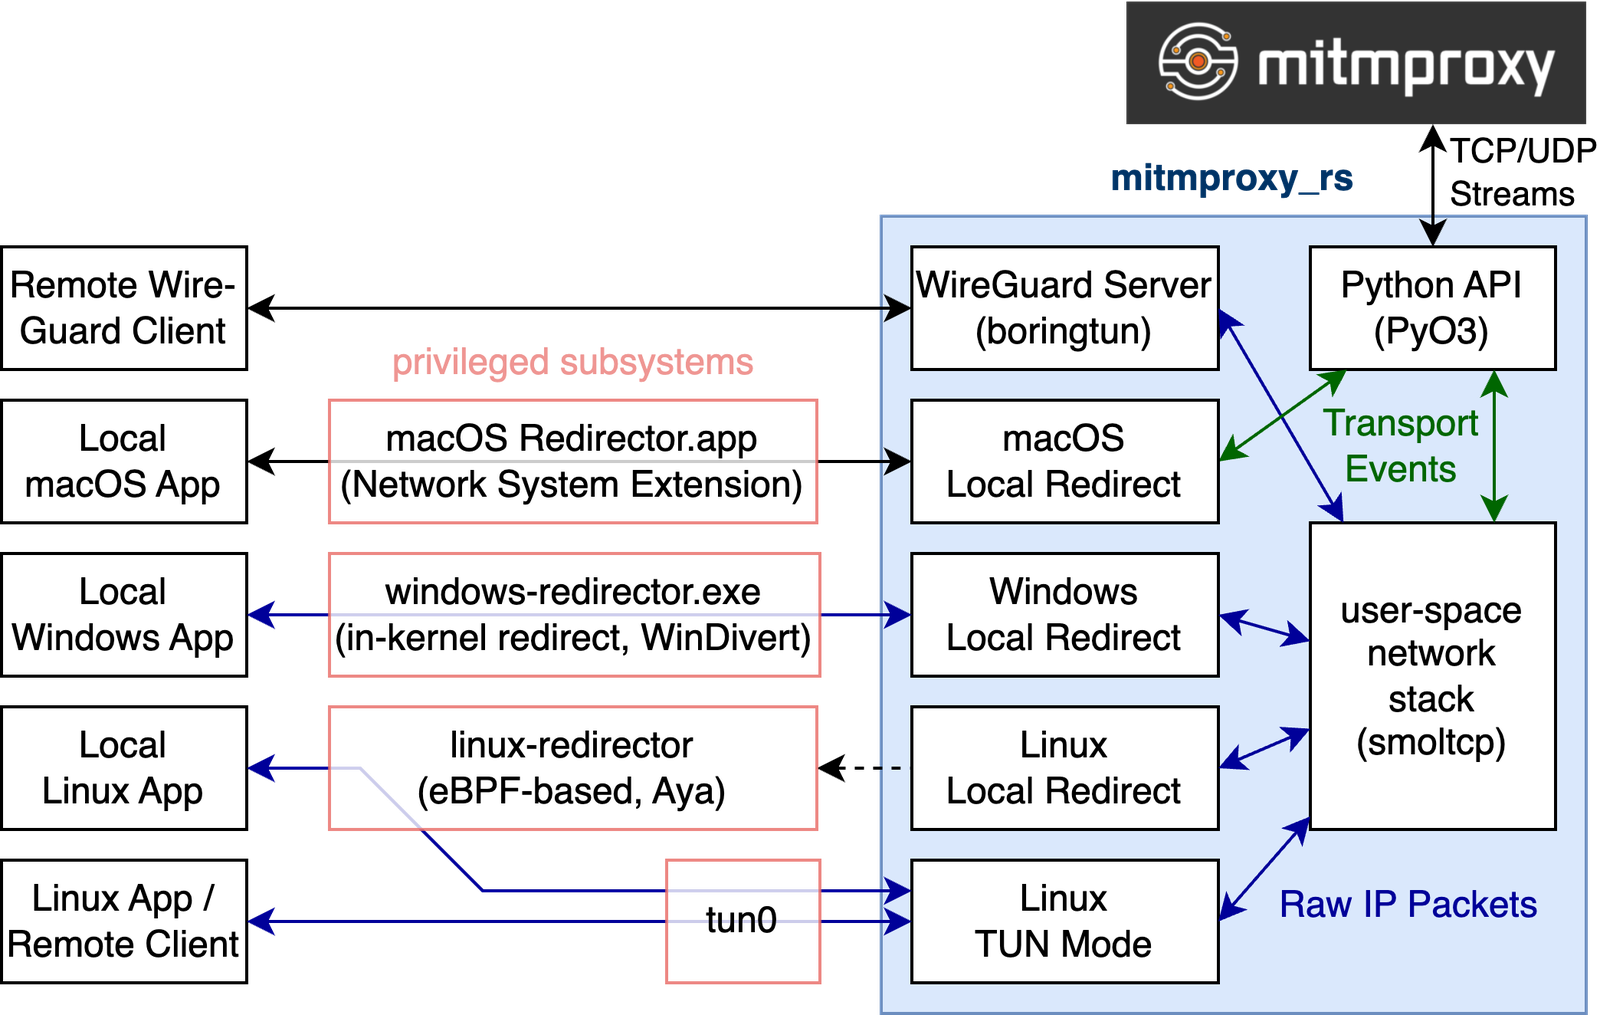 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 payatu/tiredful-api
An intentionally designed broken web application based on REST API.
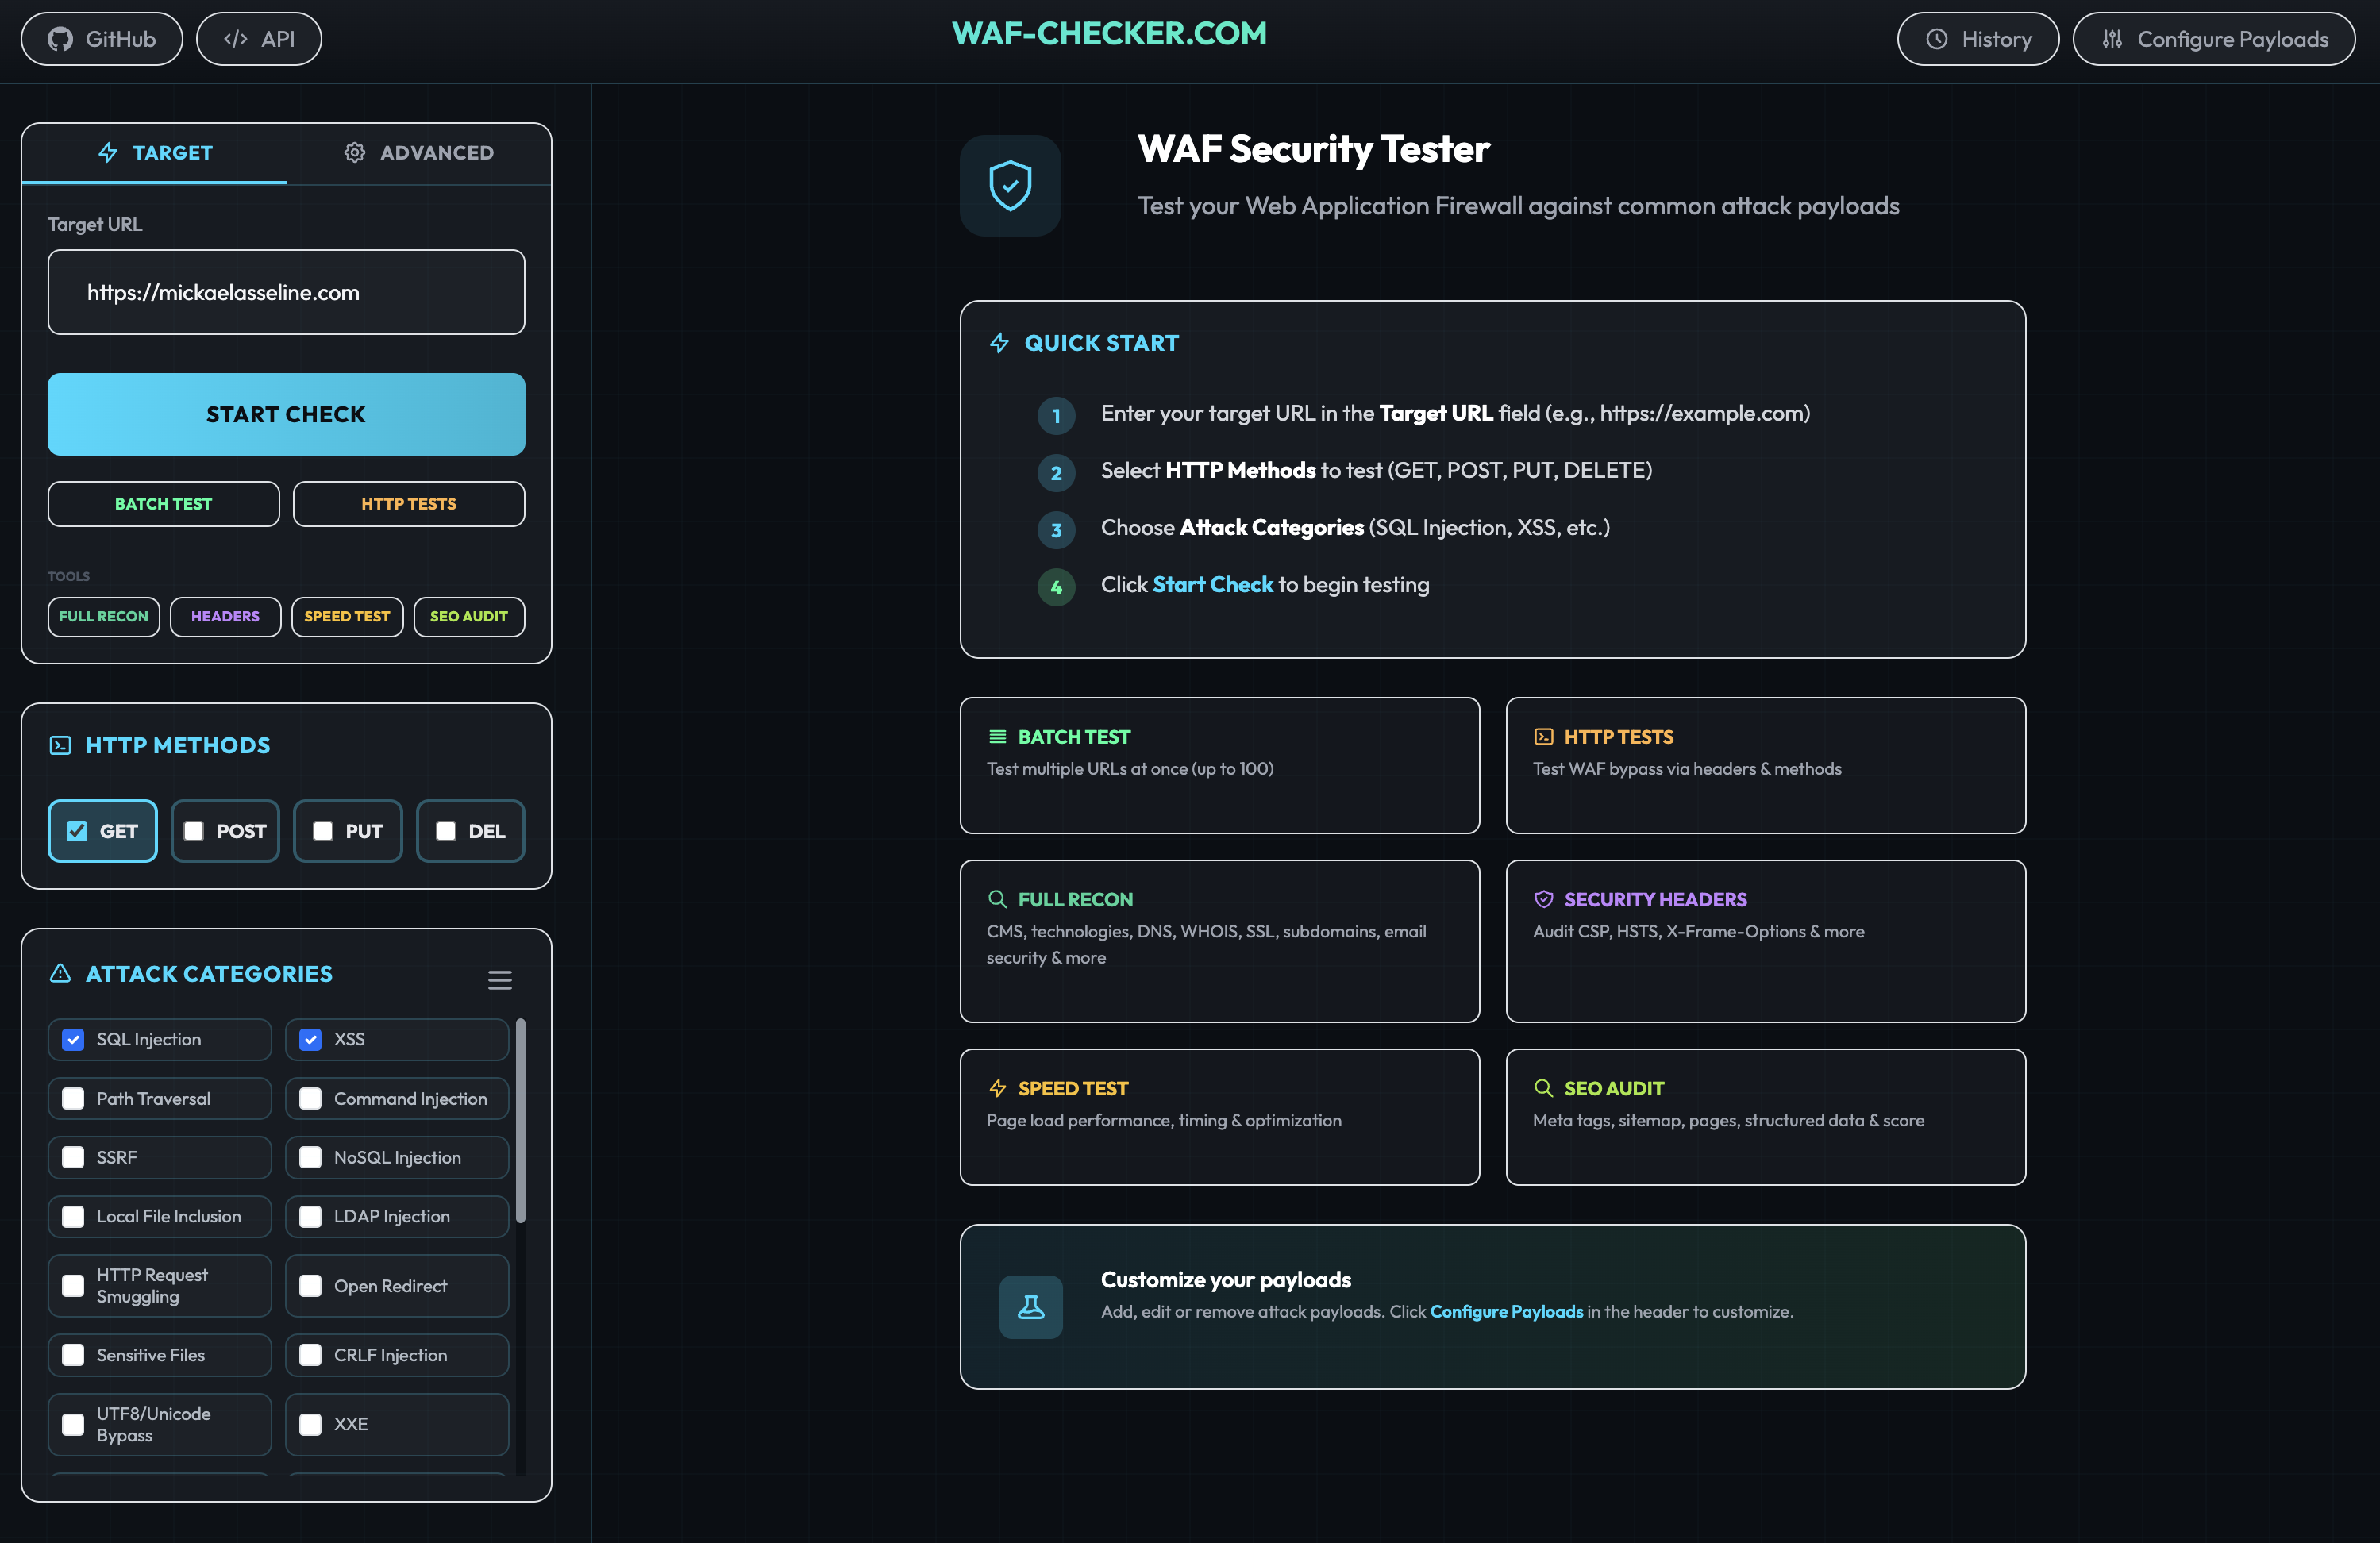 papamica/waf-checker
Tests your WAF with +160 payloads
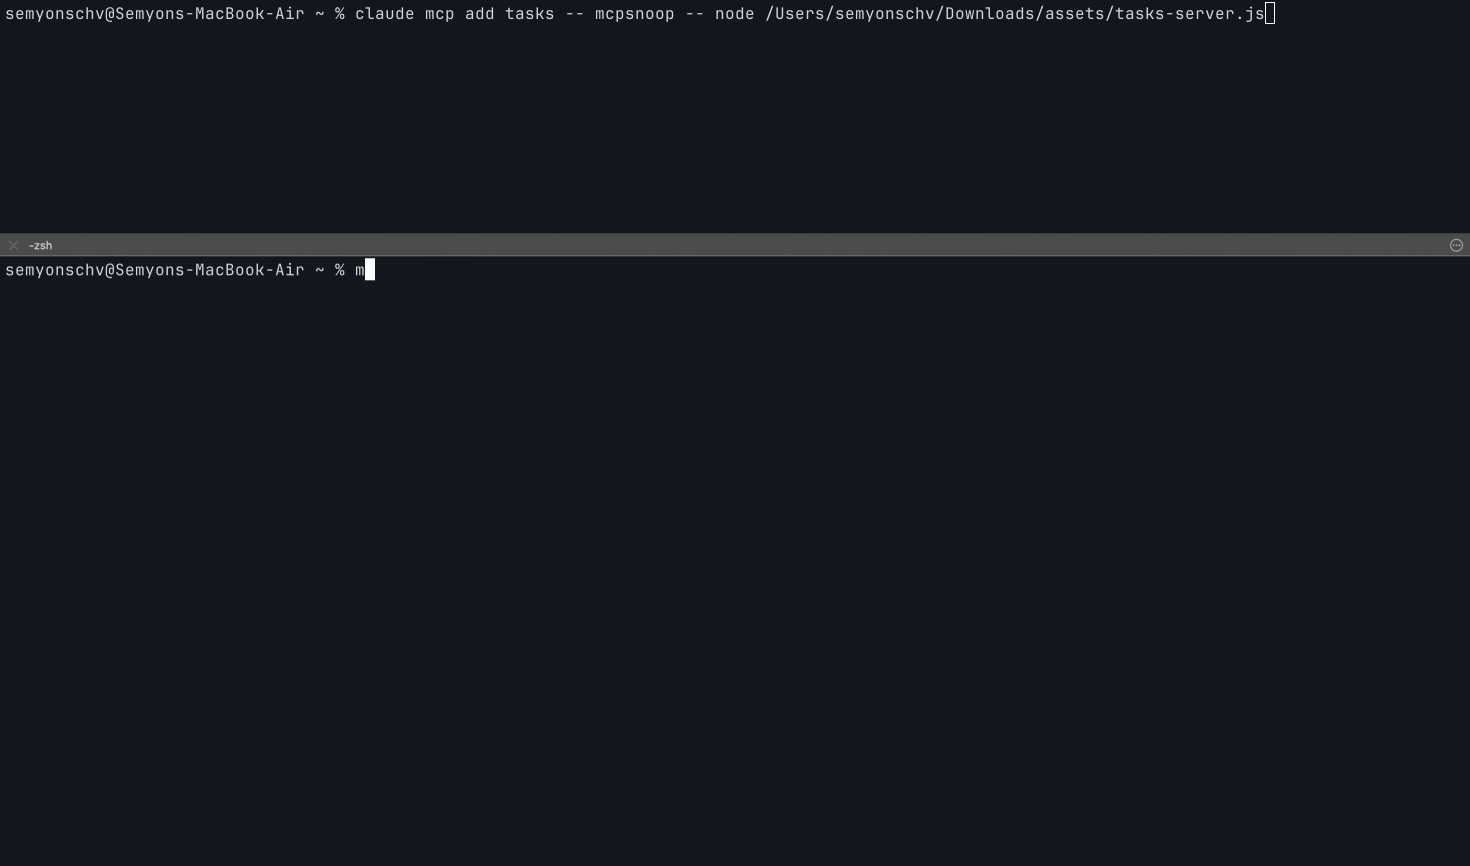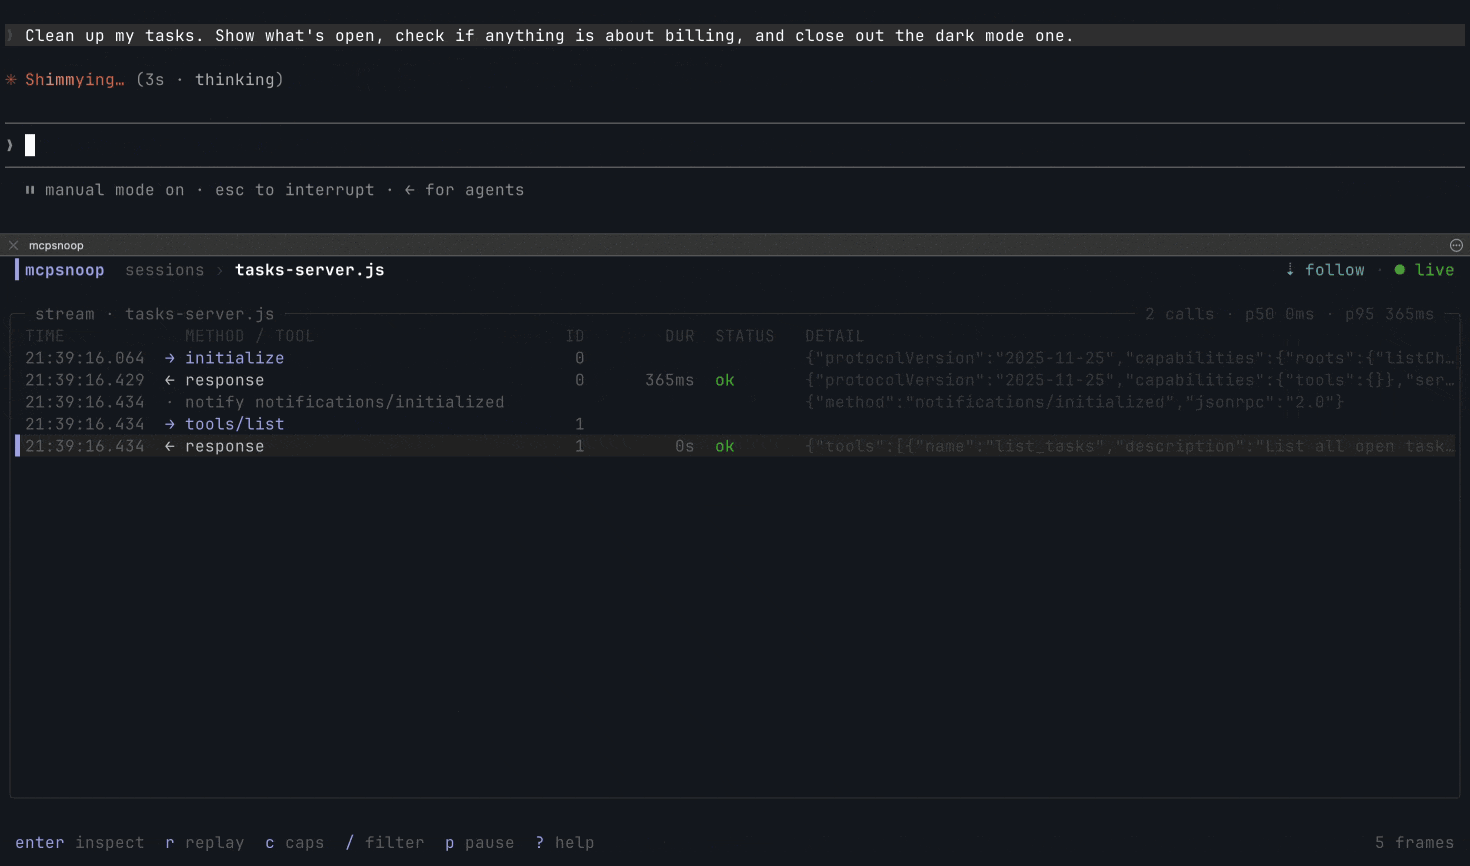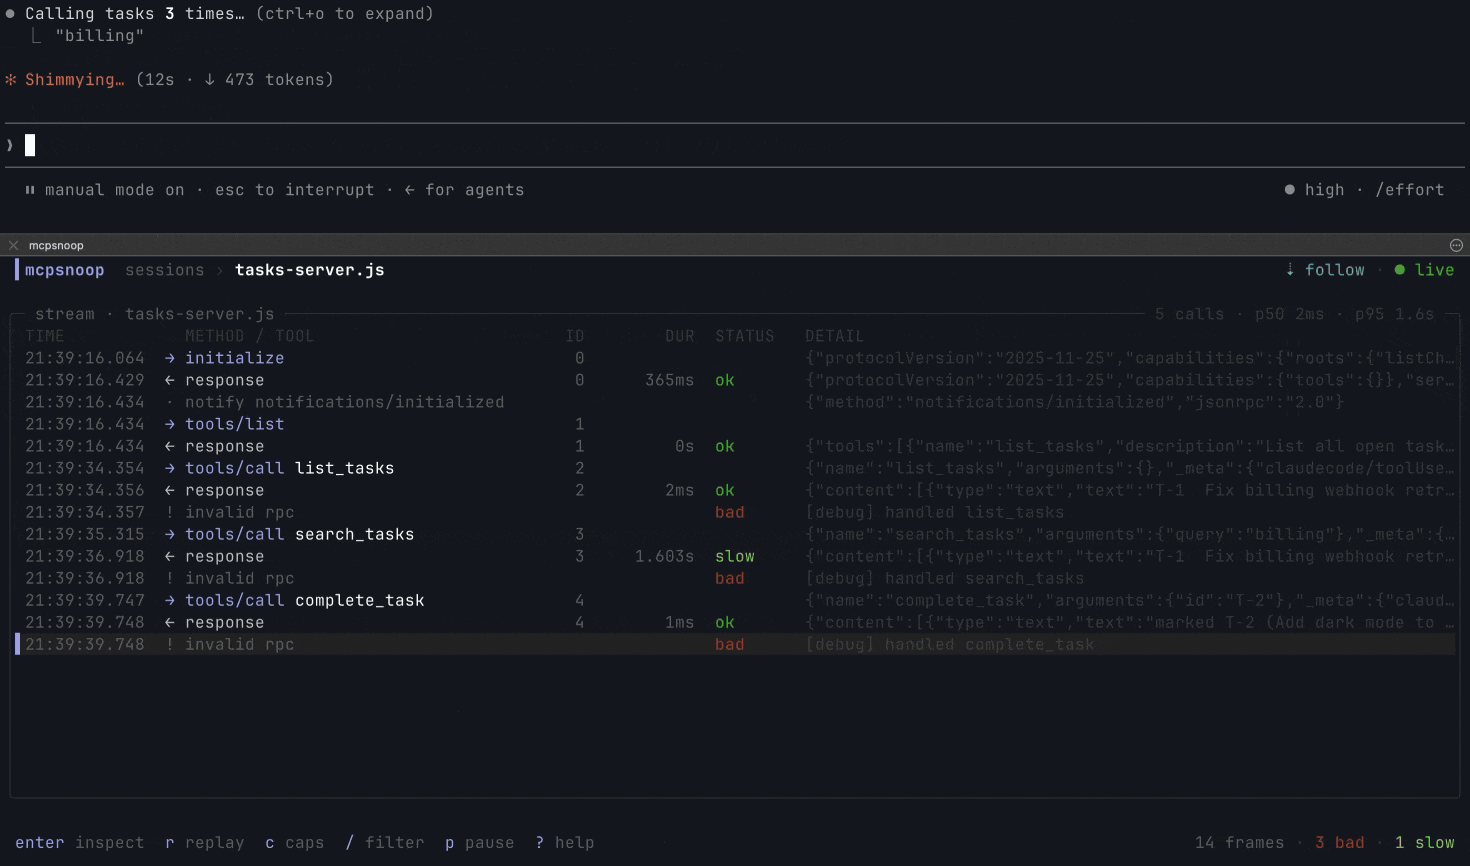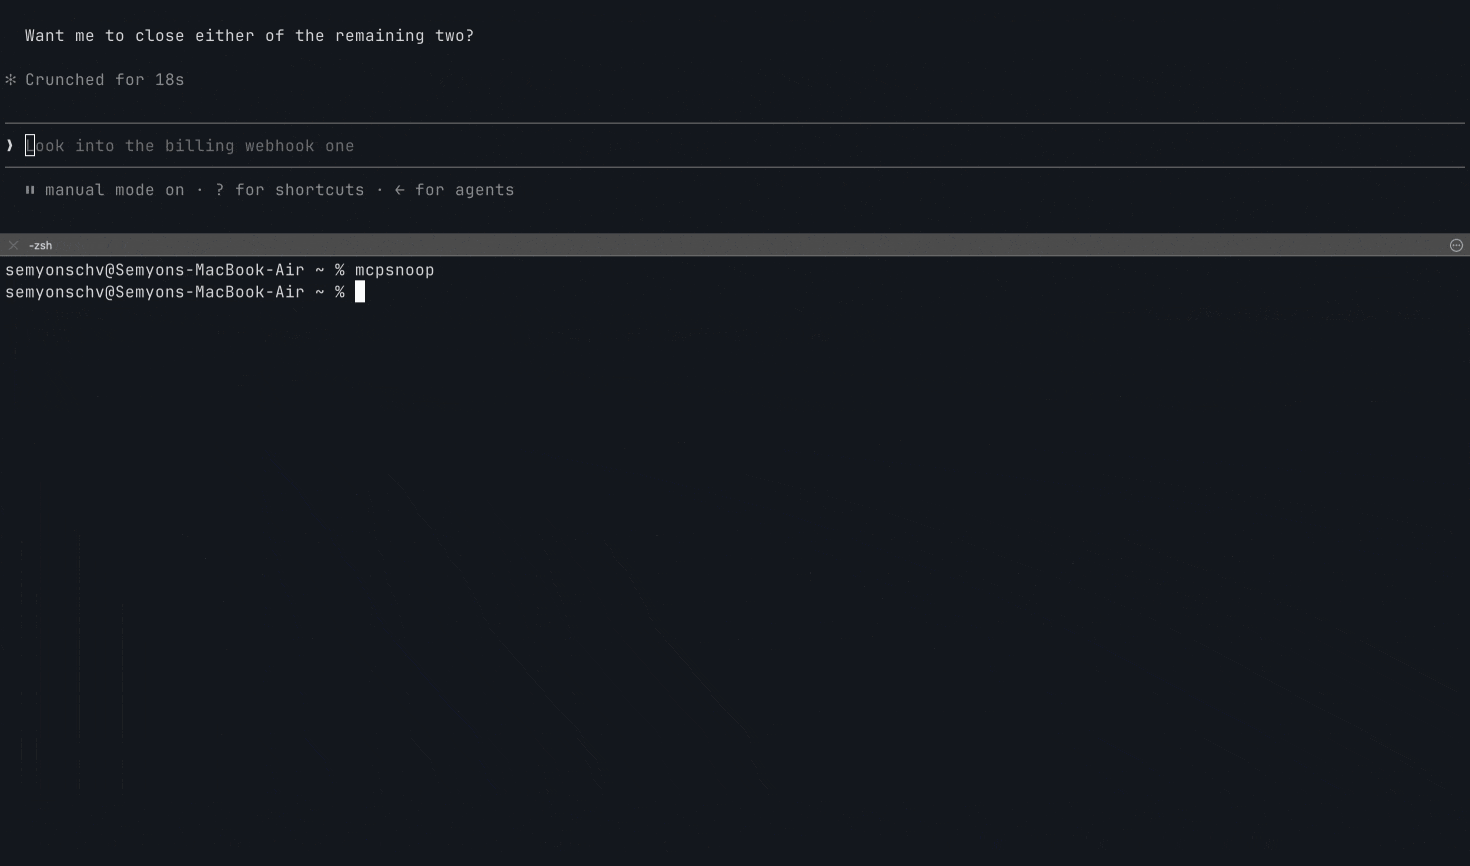 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
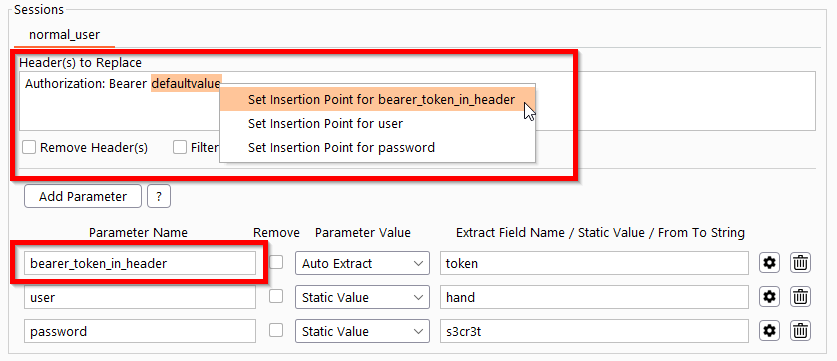 simioni87/auth_analyzer
Burp Extension for testing authorization issues. Automated request repeating and parameter value extraction on the fly.
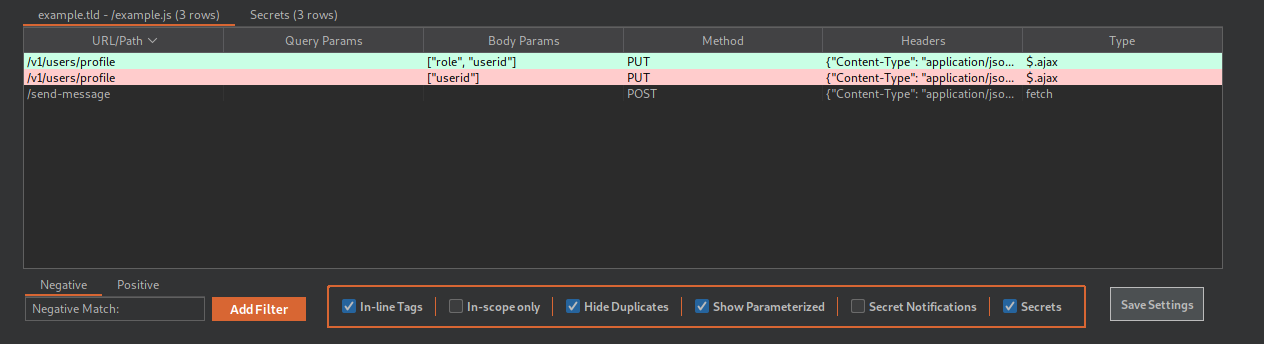 0x999-x/jsluicepp
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice
 portswigger/burp-extensions-montoya-api-examples
Sample Burp Suite extensions demonstrating the Montoya API, covering HTTP and proxy handlers, custom scan checks, Intruder payloads, WebSocket…
 impact-i/x8-burp
Hidden parameters discovery suite
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
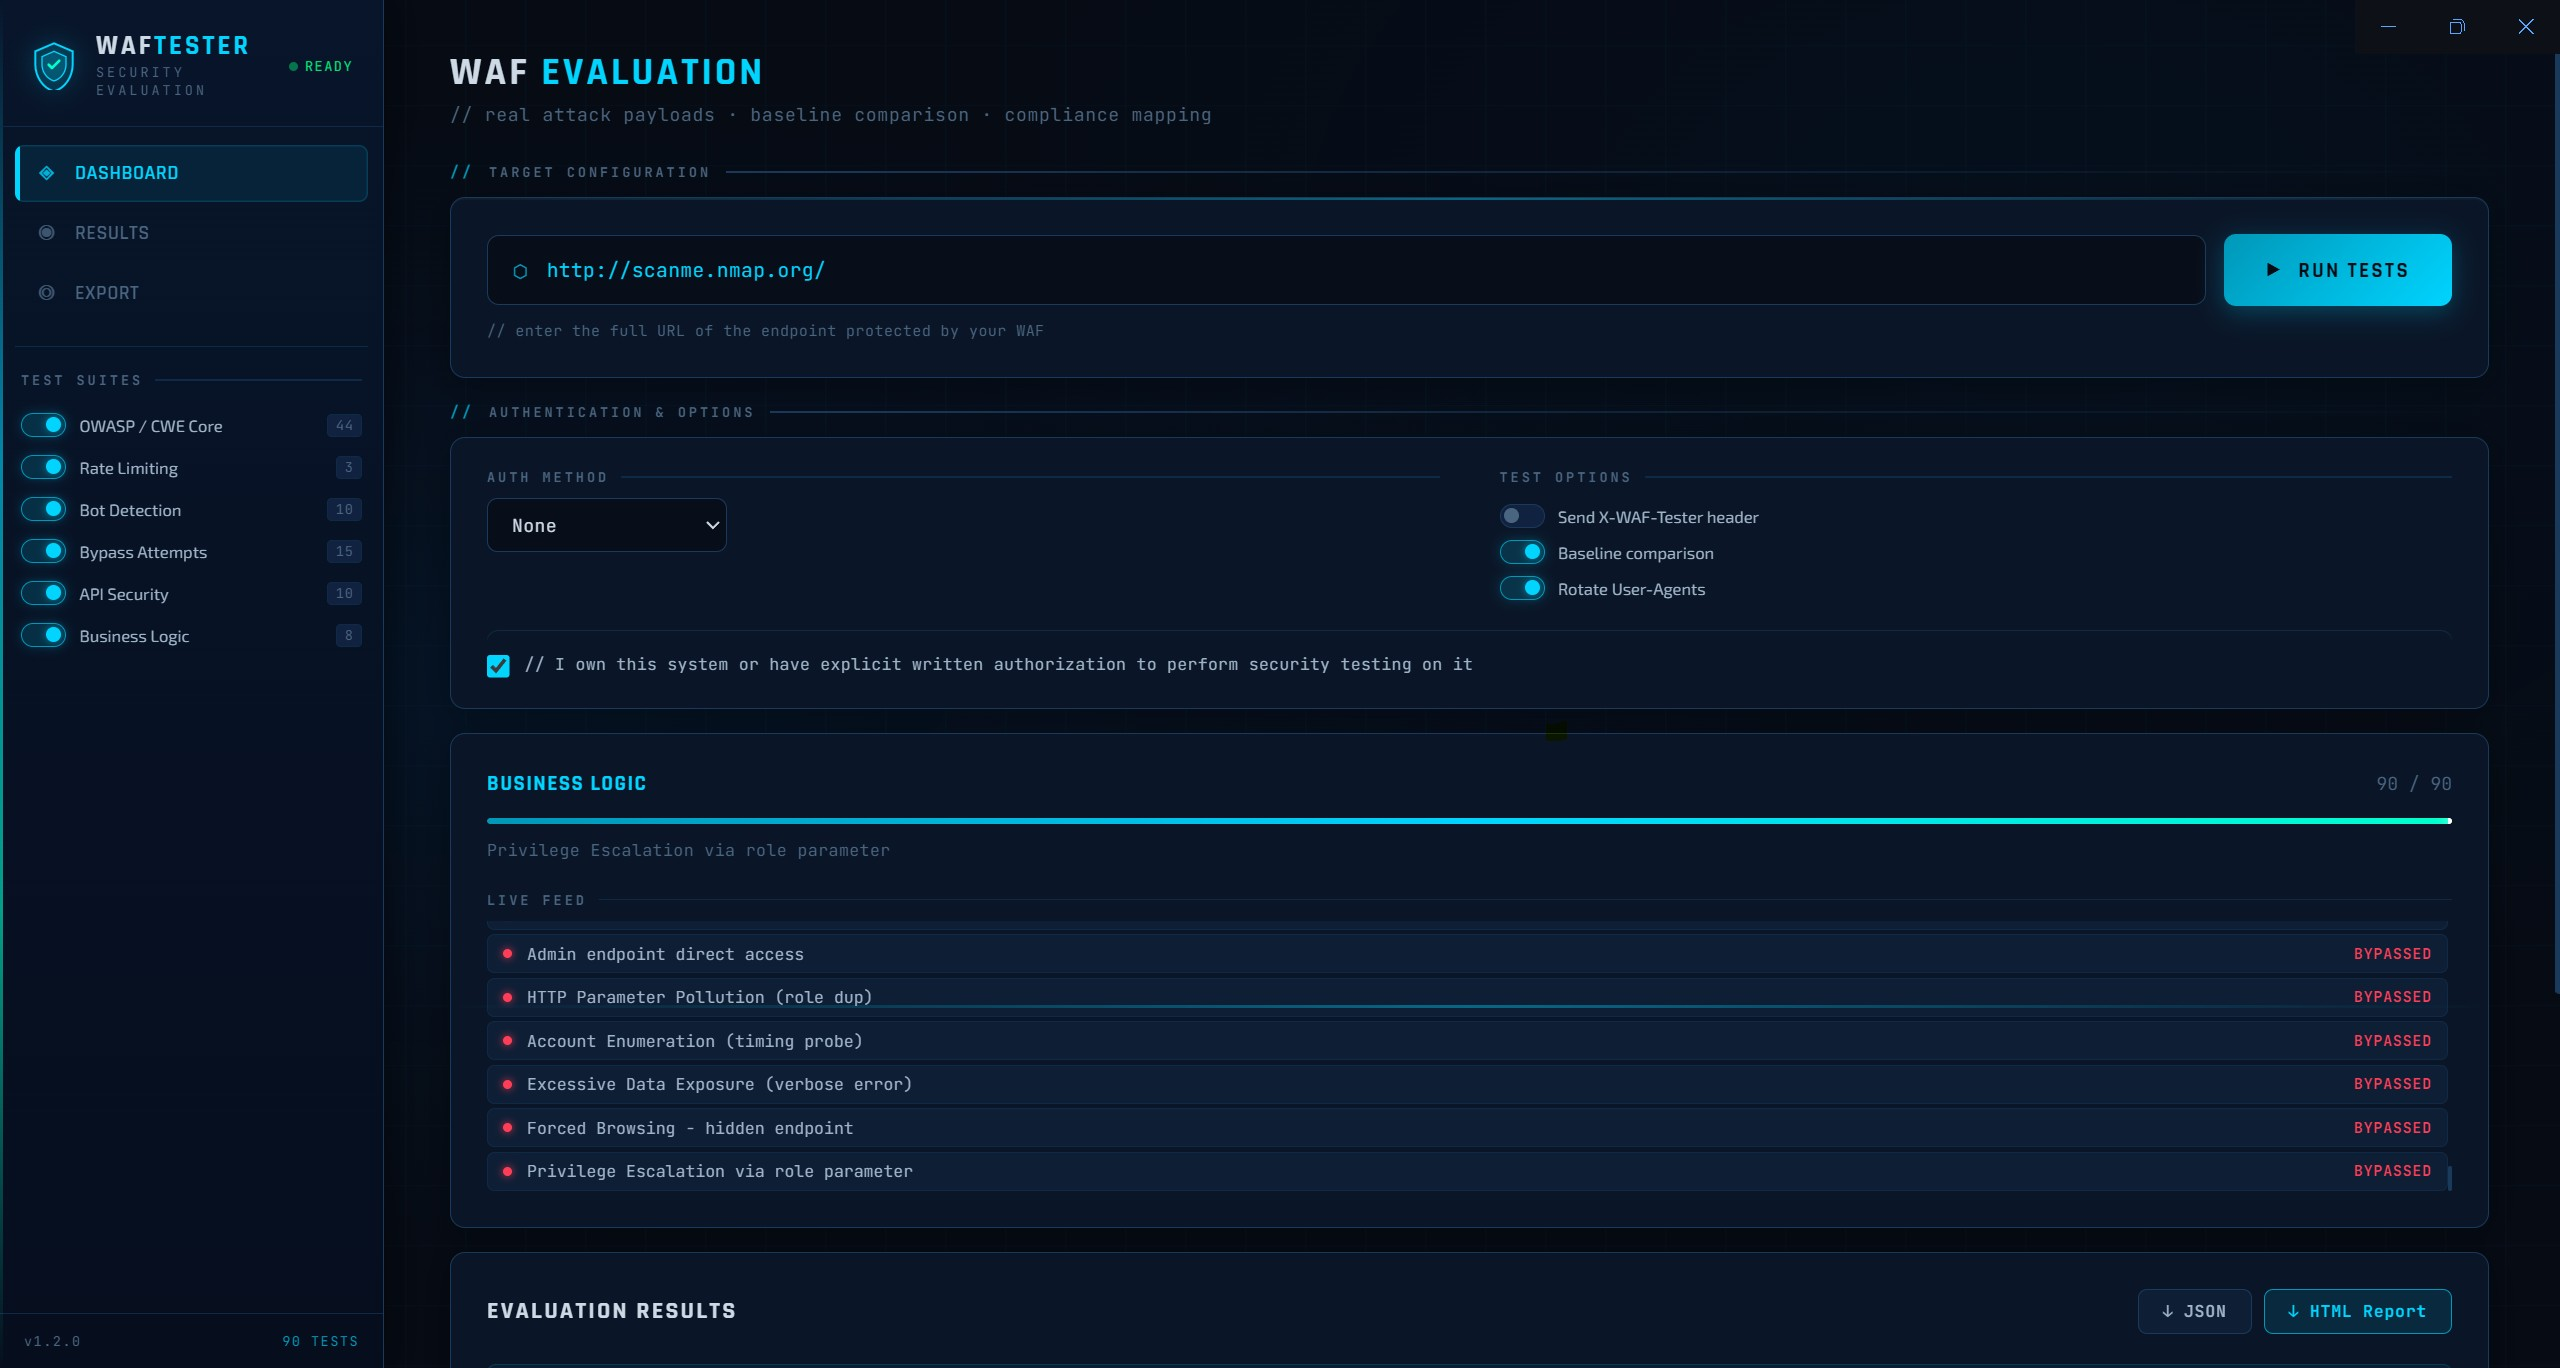 kpomin57/waf-tester
A program for testing WAF functionality
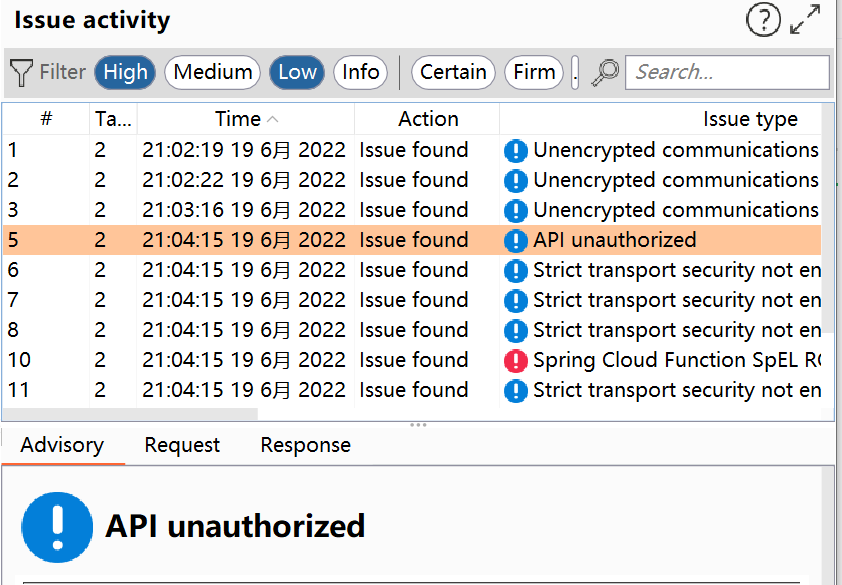 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
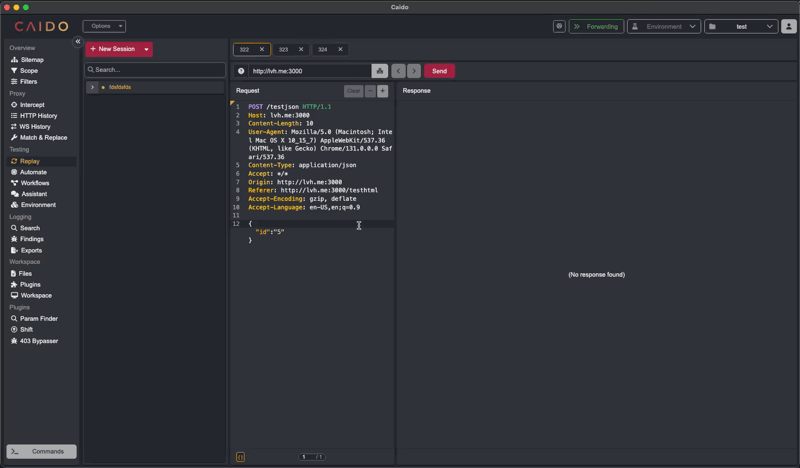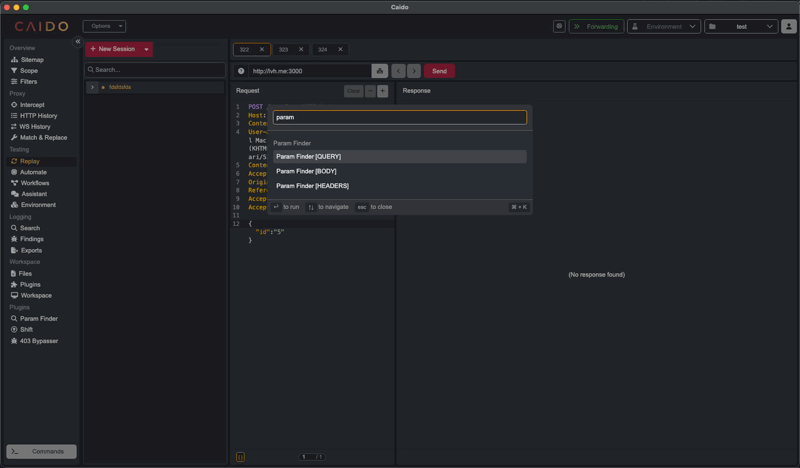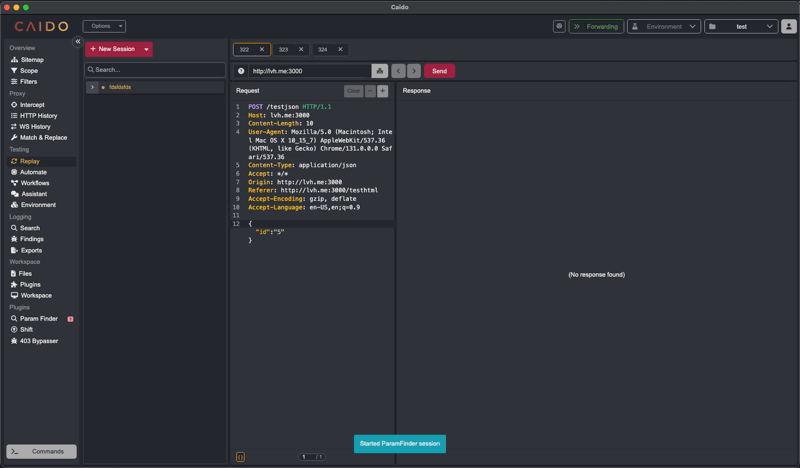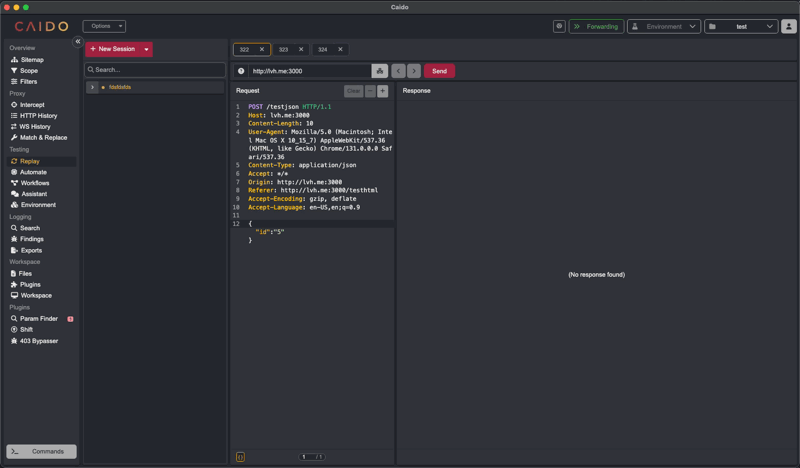 caido-community/paramfinder
Discover hidden parameters in Caido
 infobyte/faraday_burp
Burp Extension for collaboration in Faraday