
Archived
Hijacker
 chrisk44/hijacker
Aircrack, Airodump, Aireplay, MDK3 and Reaver GUI Application for Android
android-securityinformation-gatheringmobile-security+4
2.6k
 qkaiser/broadcom-wps
Tools to fingerprint WiFi Access Points running the Broadcom SDK and a list of known affected devices.
 p0cl4bs/wifi-pumpkin-deprecated
DEPRECATED, wifipumpkin3 -> https://github.com/P0cL4bs/wifipumpkin3
 xdavidhu/mitmap
📡 A python program to create a fake AP and sniff data.
 nanopathi/packages_wpa_supplicant8_cve-2021-0326
Source code of wpa_supplicant and hostapd, focused on CVE-2021-0326 vulnerability for analysis, testing, and understanding of Wi-Fi security flaws.
 v1s1t0r1sh3r3/airgeddon
This is a multi-use bash script for Linux systems to audit wireless networks.
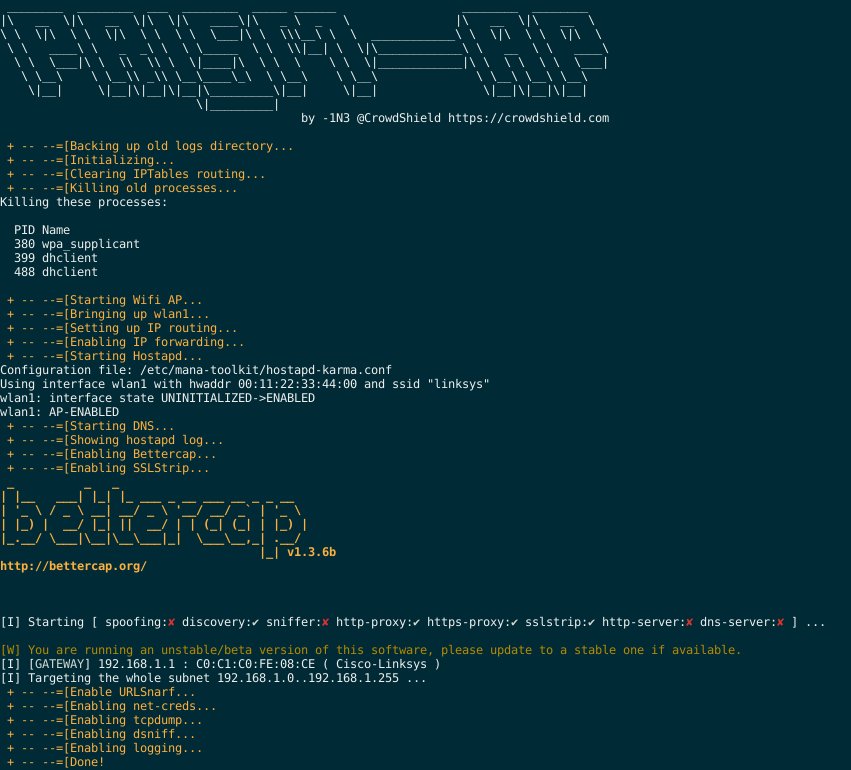 1n3/prism-ap
An automated Wireless RogueAP MITM attack framework.
 momenbasel/autowifi
Wireless penetration testing framework. Automates WPA/WPA2/WEP/WPS attacks - recon to exploitation in one command. aircrack-ng + hashcat + PMKID.
 atao/raspberrypi-setup
Ansible playbook for rapid Raspberry Pi setup with modular roles for wireless security testing, RFID/NFC tools, SDR, Docker, Tor proxy, and standard…
 yslxotwod/wifisting
GTK4 wireless security toolkit with 57 standalone shell modules for Wi-Fi, Bluetooth, RF, Zigbee, NFC and router-side attacks, plus MITM, recon,…
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
 aircrack-ng/rtl8812au
Linux/Android kernel driver for RTL8812AU/21AU and RTL8814AU chipsets with monitor mode and frame injection support for wireless security testing.
 esc0rtd3w/wifi-hacker
Shell Script For Attacking Wireless Connections Using Built-In Kali Tools. Supports All Securities (WEP, WPS, WPA, WPA2)
 samyk/skyjack
A drone engineered to autonomously seek out, hack, and wirelessly take full control over any other Parrot or 3DR drones within wireless or flying…
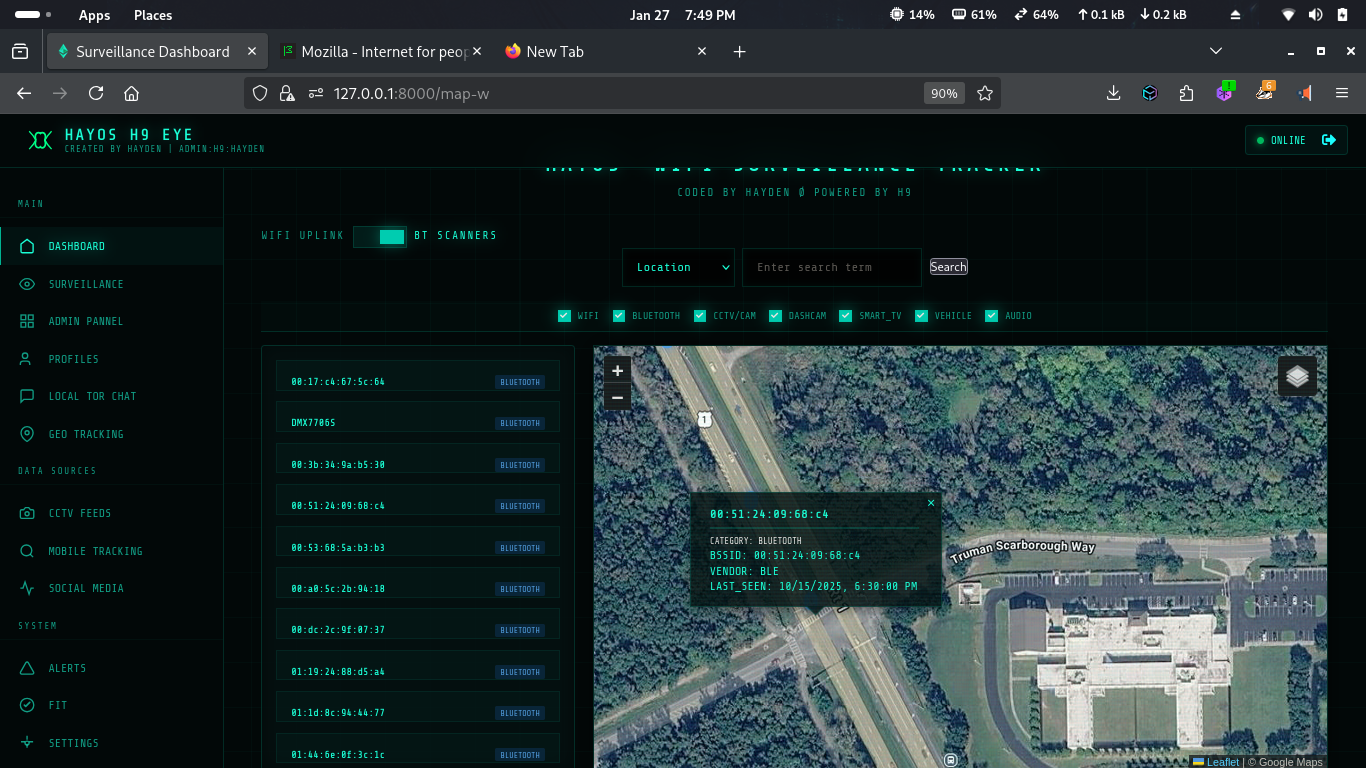 h9zdev/wiretapper
Passive wireless OSINT platform that detects and maps Wi-Fi, Bluetooth, CCTV, IoT devices, and cell towers using radio signal intelligence for…
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
 ghostesp-revival/ghostesp
The open-source wireless research platform for ESP32.
 s0lst1c3/eaphammer
Targeted evil twin attacks against WPA2-Enterprise networks. Indirect wireless pivots using hostile portal attacks.