Tool_Exploit_Password_Camera_CVE-2018-9995

Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.

Exploit tool for CVE-2018-9995 that extracts credentials from vulnerable DVR devices via Google dorking and direct IP access.

This Tool Aims to Exploit the CVE-2018-13341

Maxprint Maxlink 1200G v3.4.11E has an OS command injection vulnerability in the "Diagnostic tool" functionality of the device.

aztarna, a footprinting tool for robots.

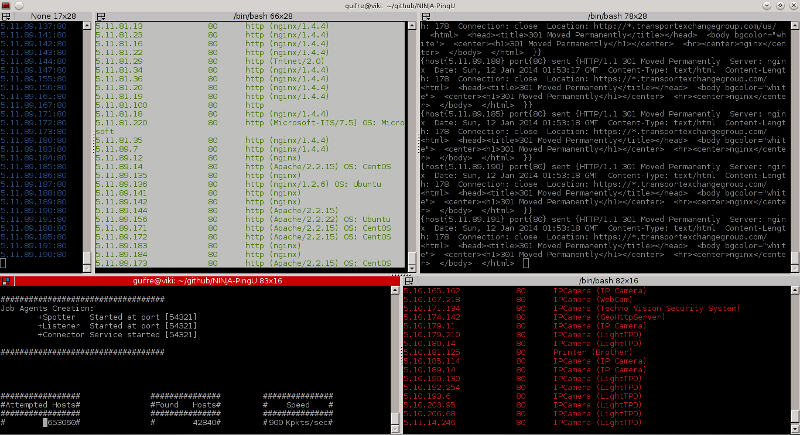
High-performance network scanner for large-scale IP and port scanning with service identification, embedded device detection, and vulnerability…

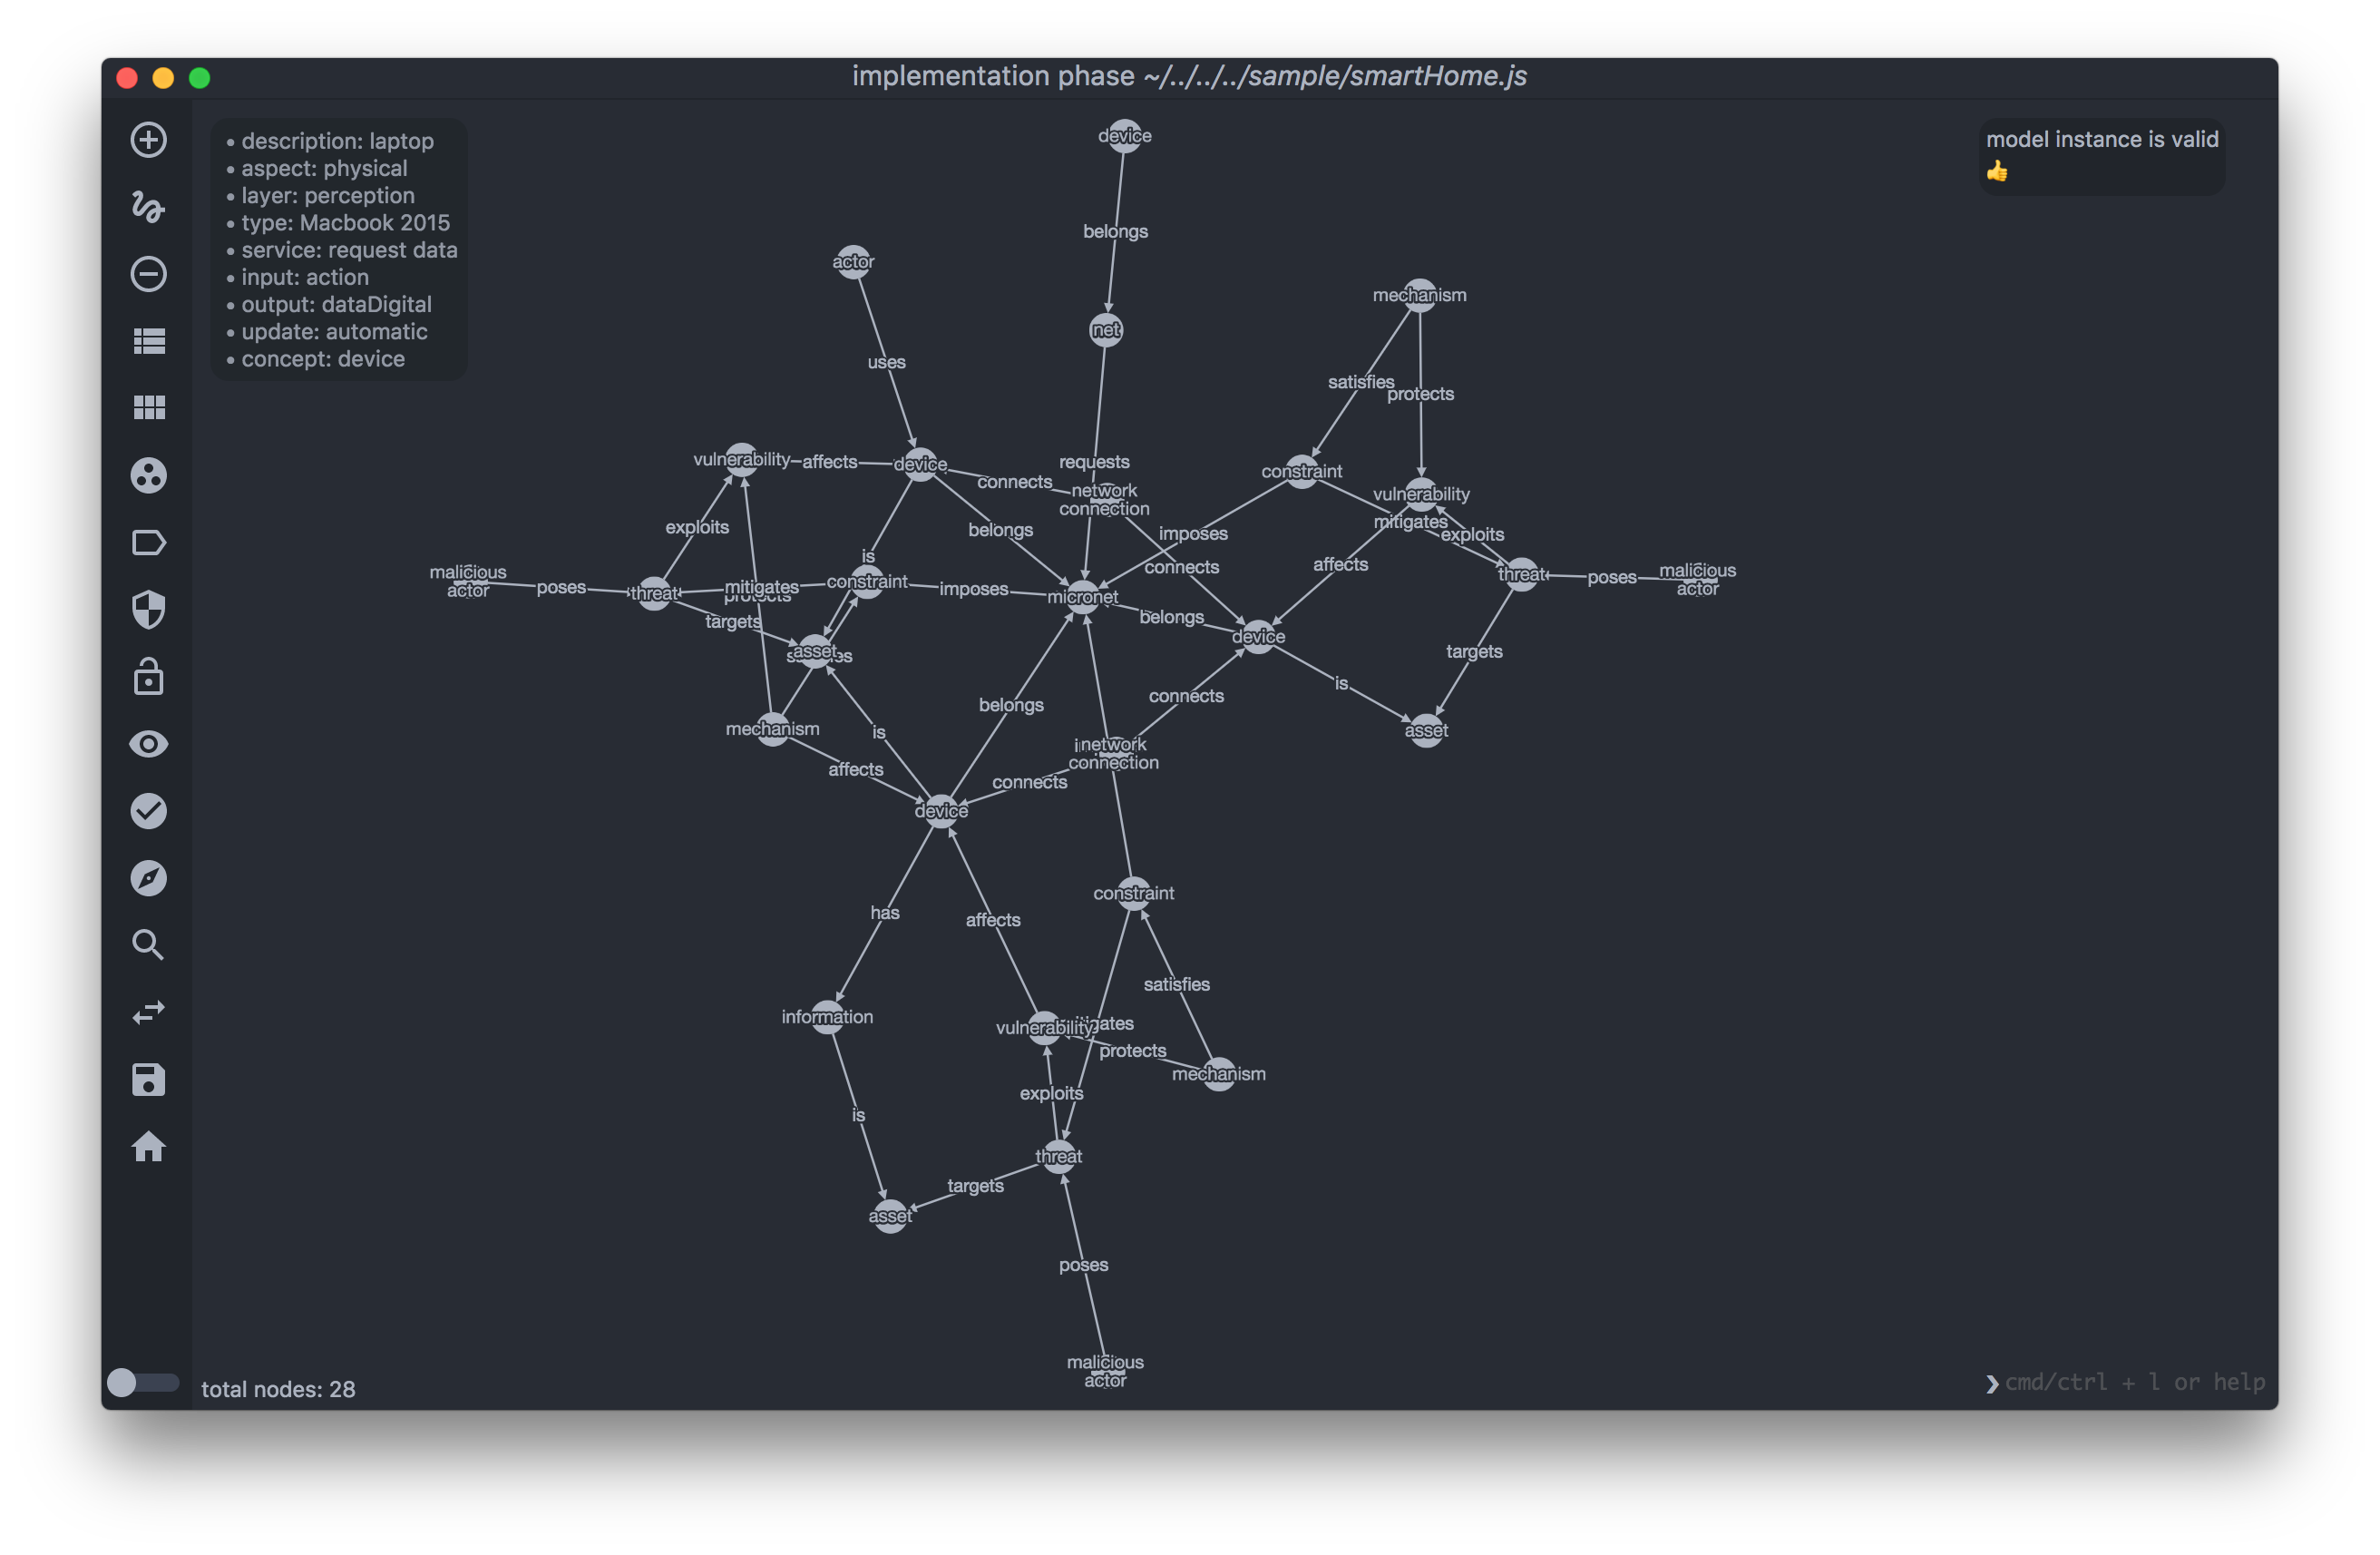
A graphical security analysis tool for IoT networks

The new generation chameleon based on NRF52840 makes the performance of card emulation more stable. And gave the chameleon the ability to read,…


sniff HDMI DDC (I2C) traffic

Automated Application Generation for Stack Overflow Types on Wireless Routers

Exploit and tooling for Amlogic-based Sonos devices: dumps OTP/eFUSE via an EL3 exploit, extracts LUKS decryption keys, and fetches/decrypts OTA…


EDID (Enhanced Display Identification Data) Fuzzer

CVE-2017-5693 Denial of service vulnerability in Puma 6 modems

Dictionary Brute Force of the Mikrotik RouterOS 6.x Web Interface

Explotation framework for CVE-2019-11687

Framework for controlling QKD devices and managing symmetric keys. See the [project page here](https://qcomms.gitlab.io/cqptoolkit/)

This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.