
fil-c
 pizlonator/fil-c
Fil-C: completely compatible memory safety for C and C++
defensive-toolsdynamic-code-analysisvulnerability-analysis
pizlonator/fil-cFil-C: completely compatible memory safety for C and C++
 tomnomnom/gf
A wrapper around grep, to help you grep for things
 vladko312/sstimap
Automatic SSTI detection tool with interactive interface
 byt3bl33d3r/offensivedlr
Toolbox containing research notes & PoC code for weaponizing .NET's DLR
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
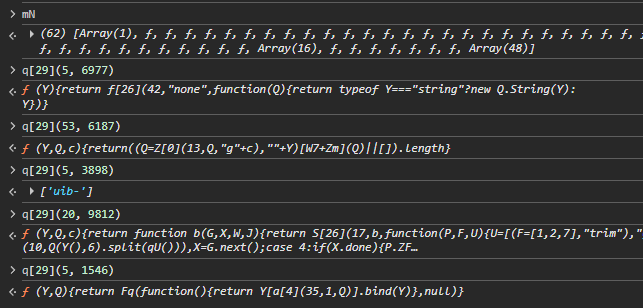 elyelysiox/recaptcha
Documentation and reverse engineering of reCAPTCHA
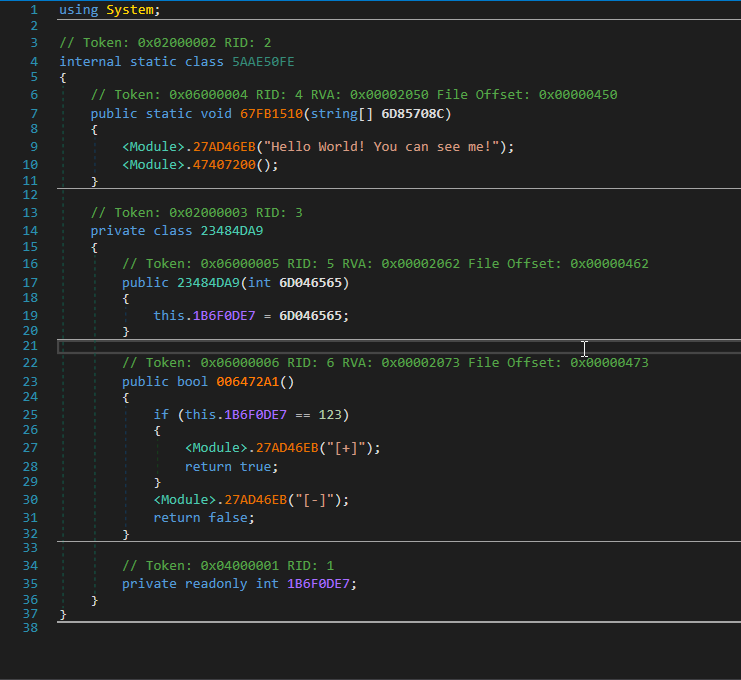 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
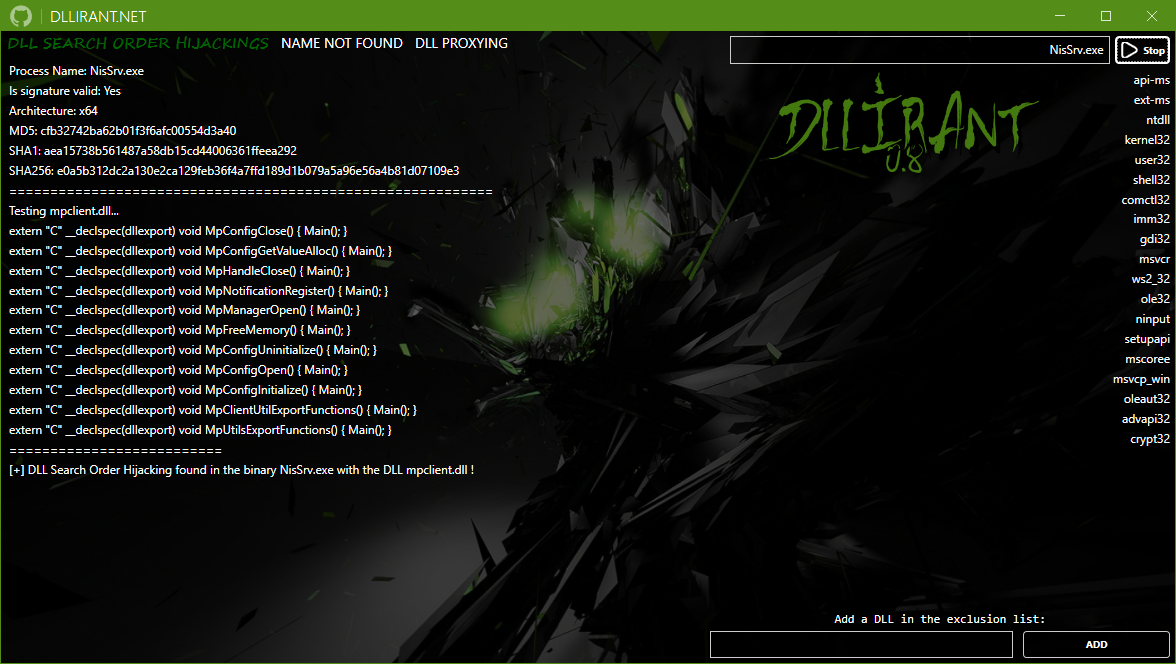 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
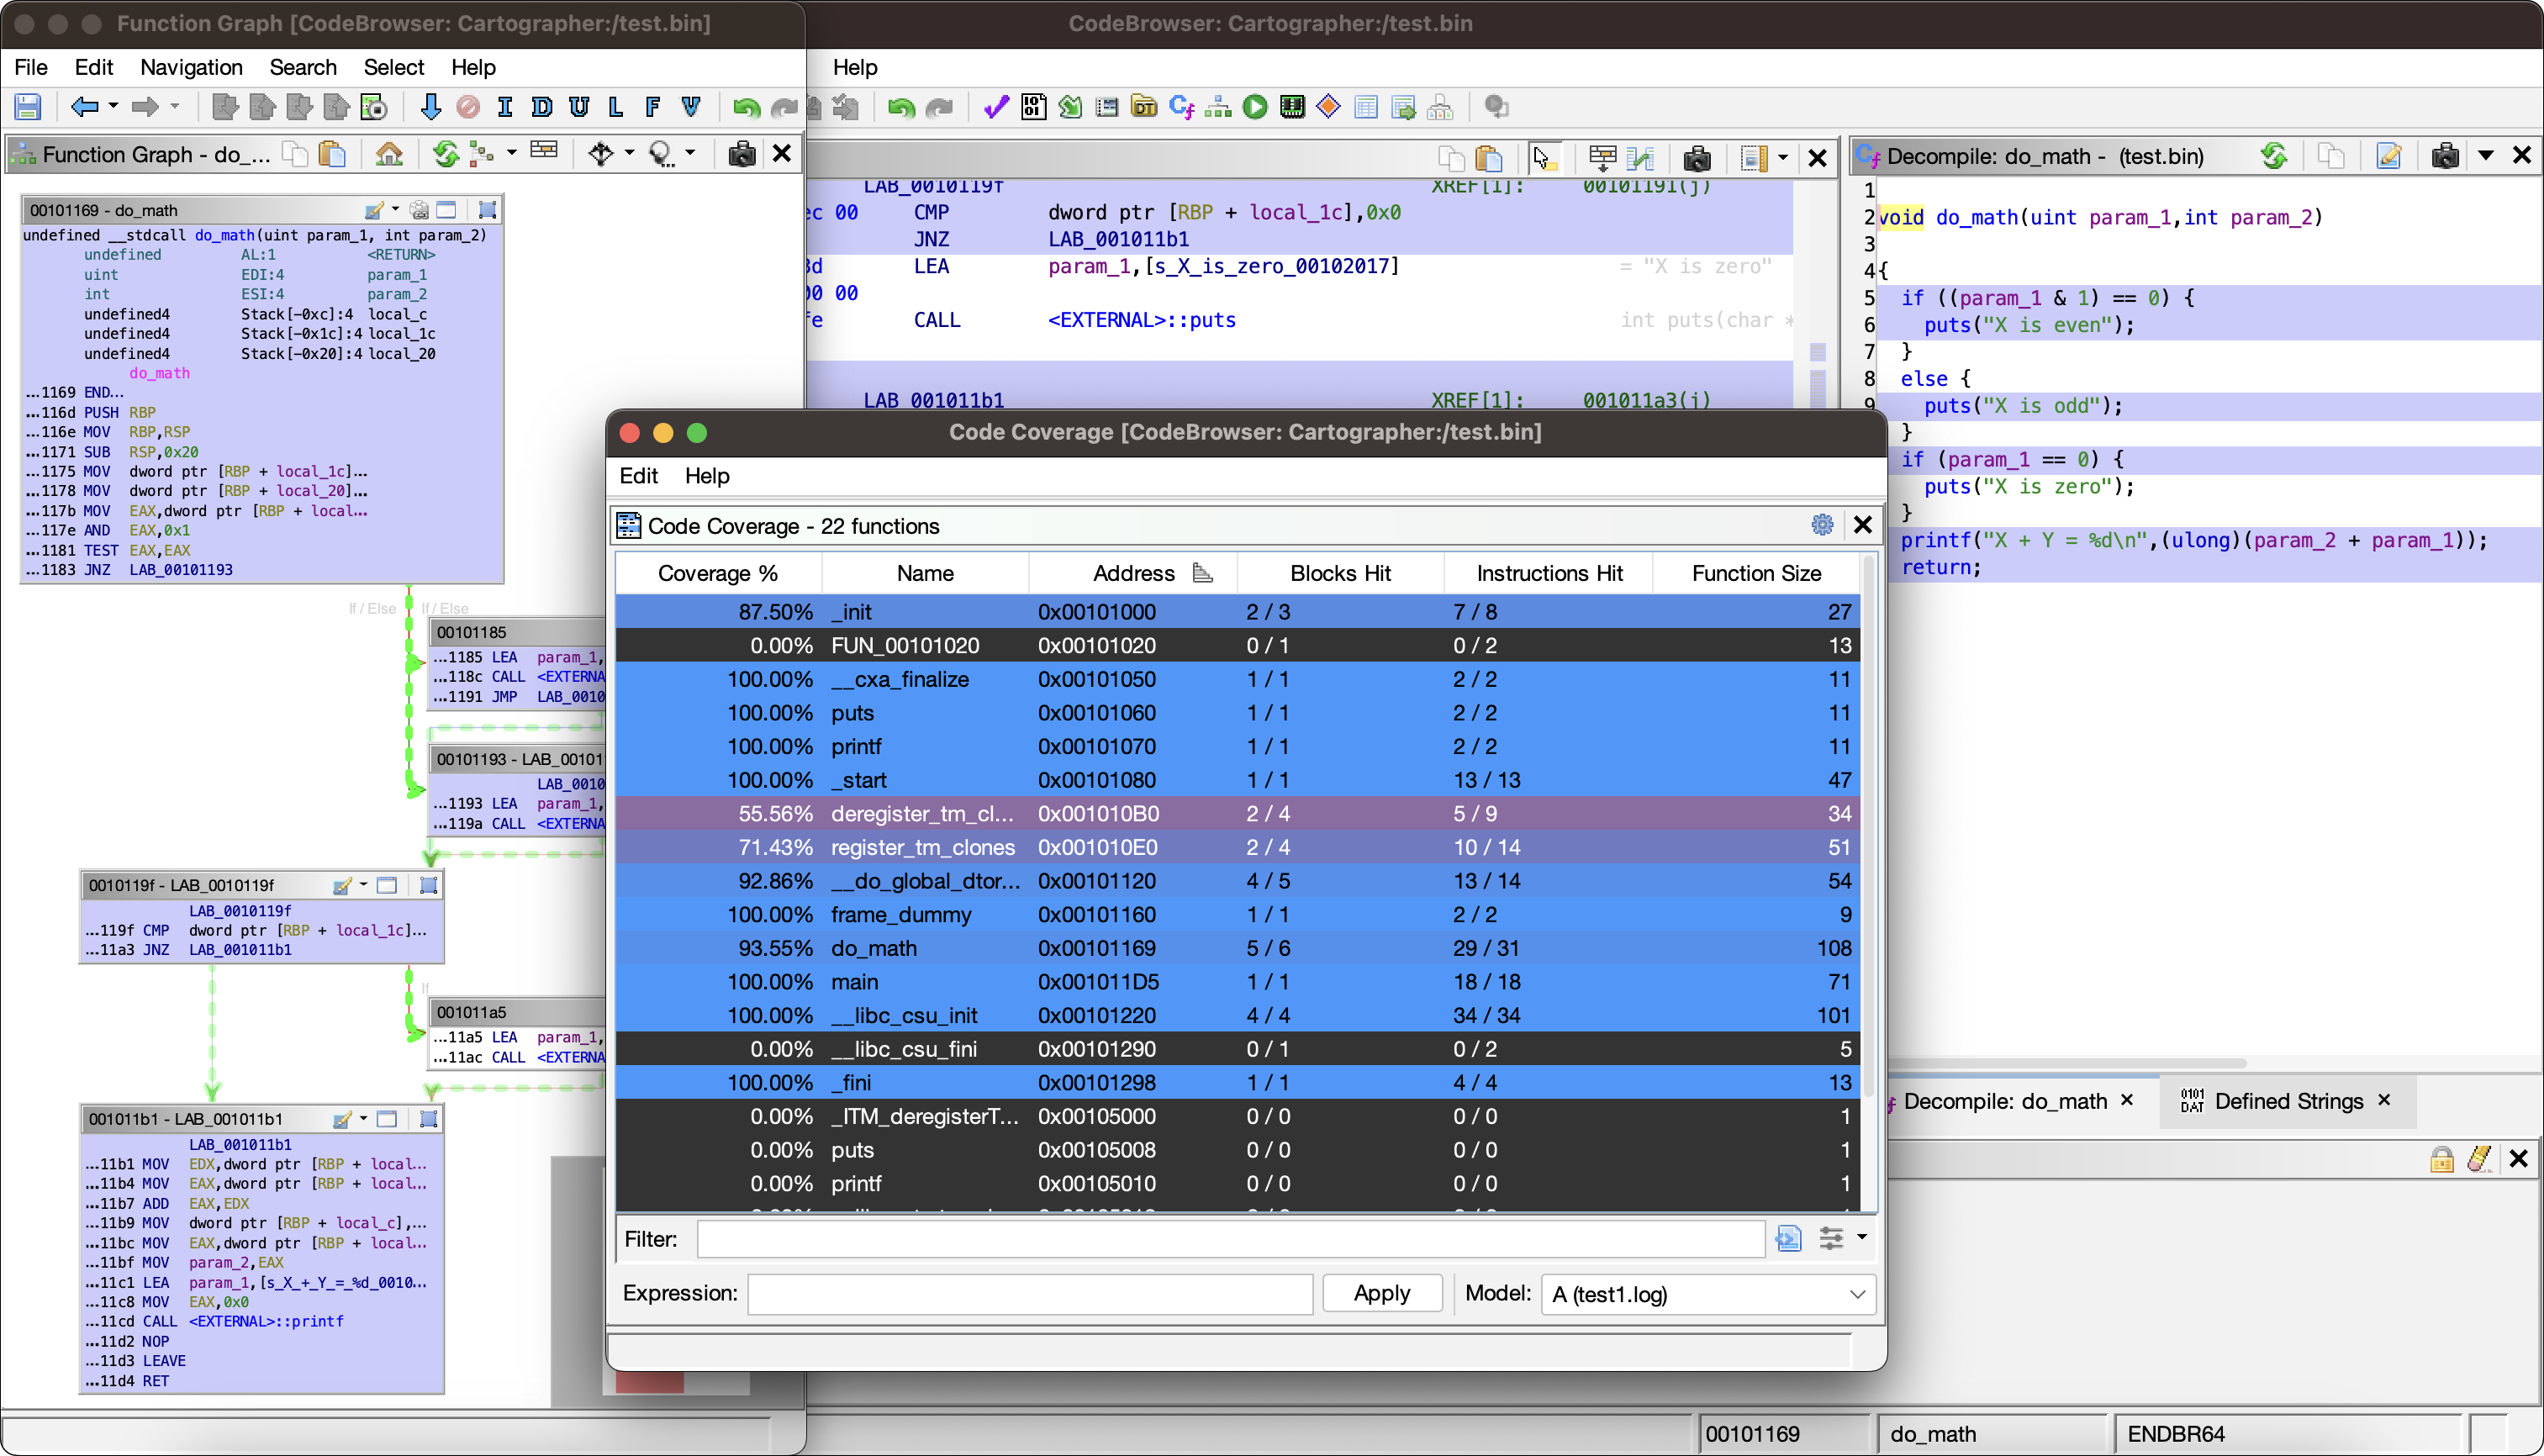 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 cobbr/elite
Elite is the client-side component of the Covenant project. Covenant is a .NET command and control framework that aims to highlight the attack…
 cornerpirate/java-stager
A PoC Java Stager which can download, compile, and execute a Java file in memory.
 we5ter/flerken
A Solution For Cross-Platform Obfuscated Commands Detection presented on CIS2019 China. 动静态Bash/CMD/PowerShell命令混淆检测框架 - CIS 2019大会
 nccgroup/dibf
Windows NT ioctl bruteforcer and modular fuzzer
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 binsec/xyntia
Xyntia, the black-box deobfuscator