
CVE-2023-27532
 horizon3ai/cve-2023-27532
Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…
api-security-testingexploitationpenetration-testing+2
74
horizon3ai/cve-2023-27532Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…
 rub-nds/rest-attacker
Automated penetration testing framework for REST APIs with OpenAPI-driven test generation, 32 OWASP-based security tests, and built-in access control…
 use-tusk/drift-node-sdk
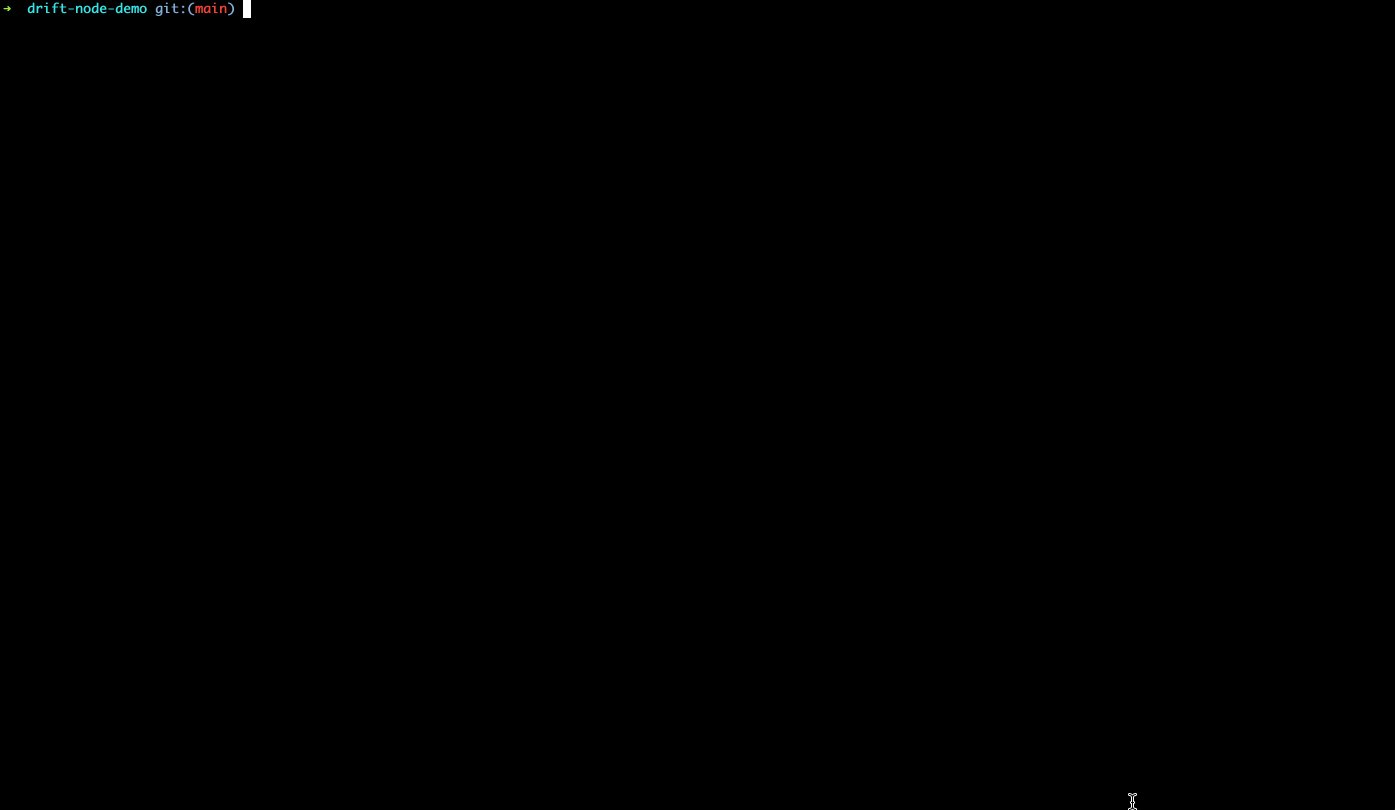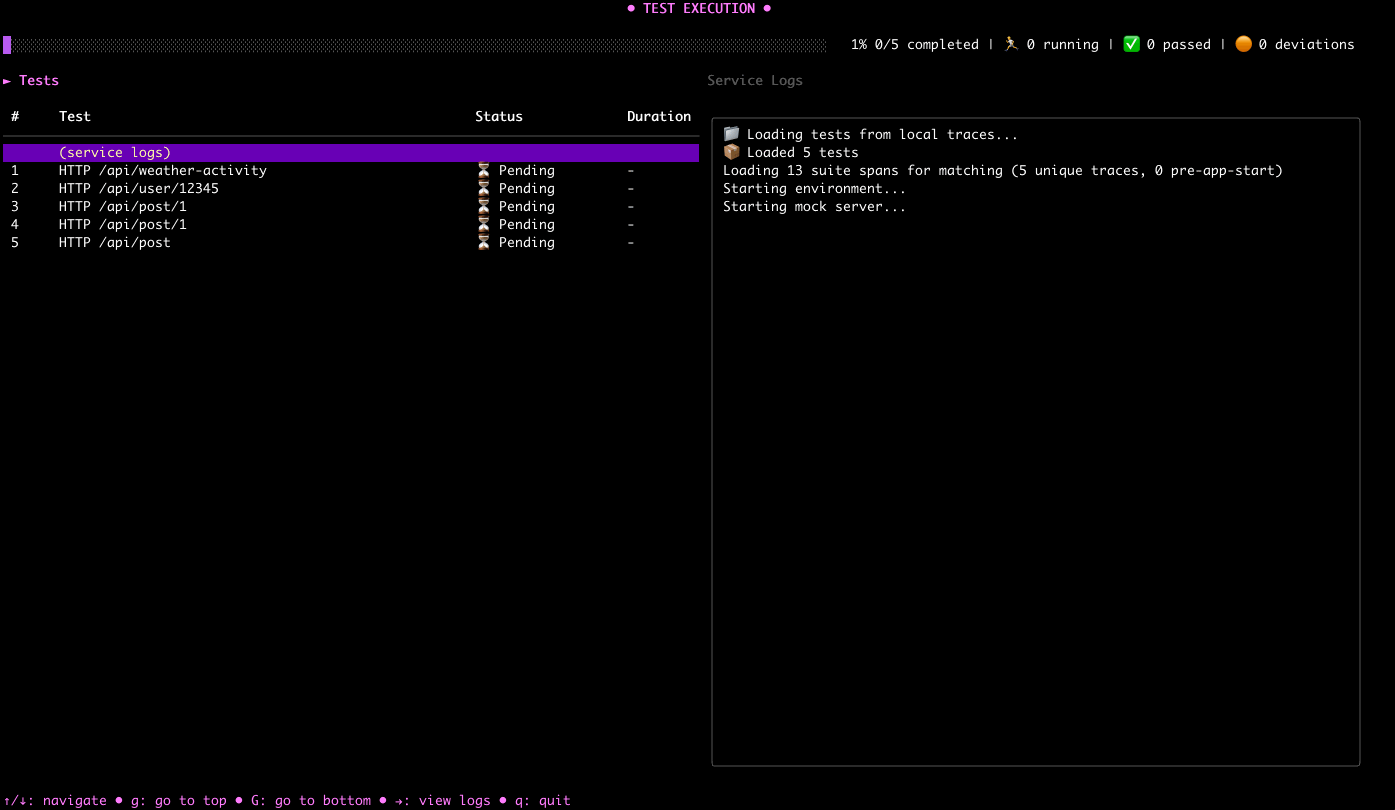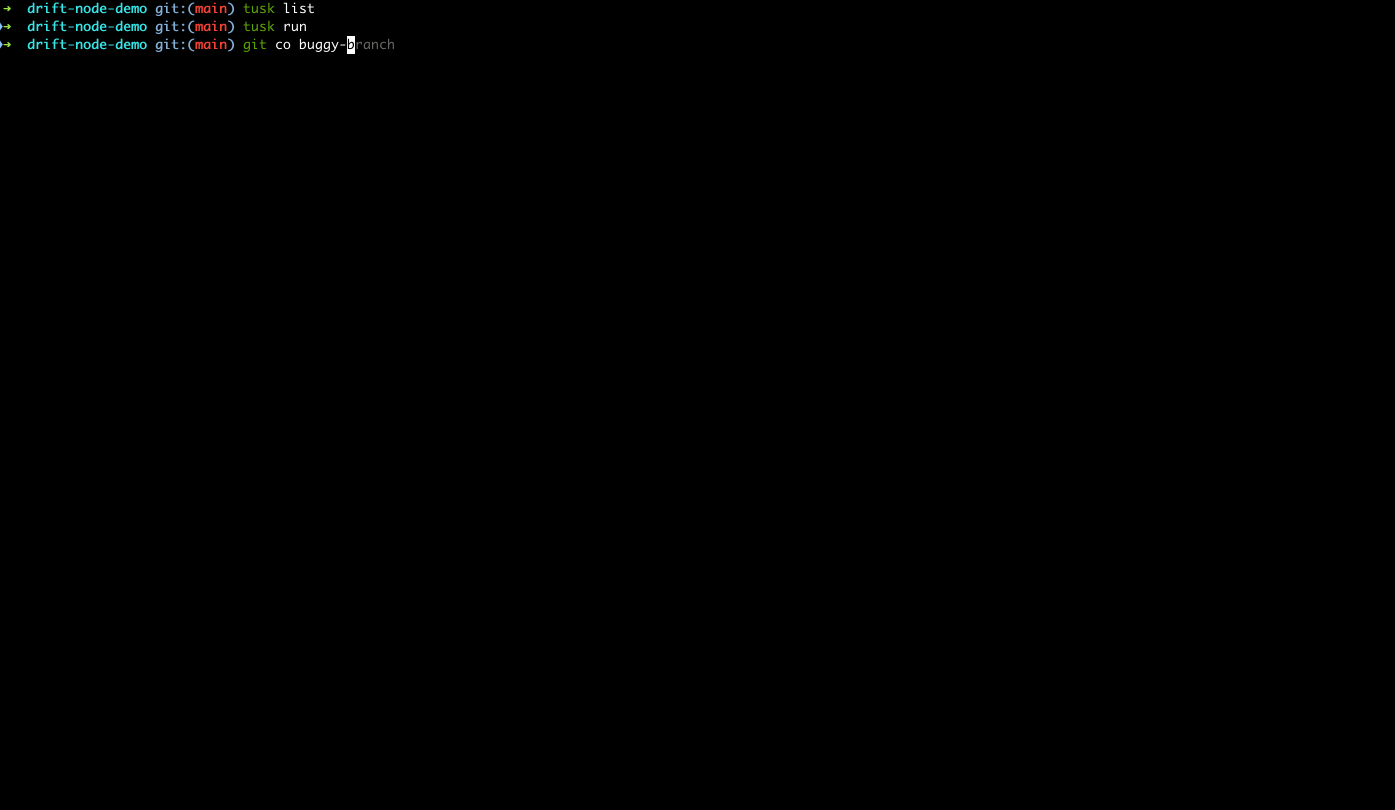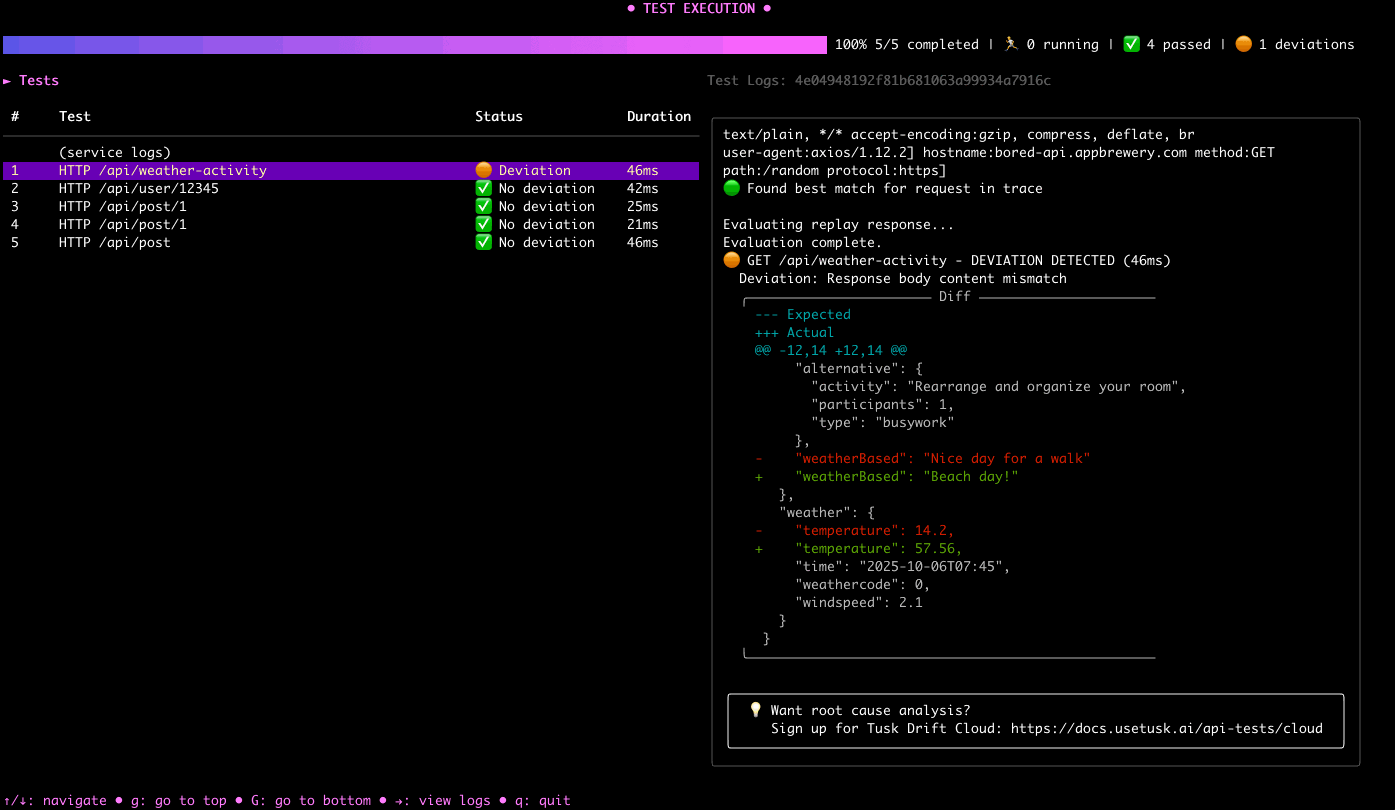
Node.js SDK for capturing and replaying API calls made to/from your service
 use-tusk/tusk-cli
Automated testing suite with live traffic record and replay
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 danialhalo/acuautomate
Unofficial Acunetix CLI tool for automated pentesting and bug hunting across large scopes.
 justmorpheus/burp-automation
Performing automated scan using Burp Suite Pro & Vmware Burp Rest API
 go-appsec/toolbox
Collaborative application security testing between humans and agents via CLI and MCP
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
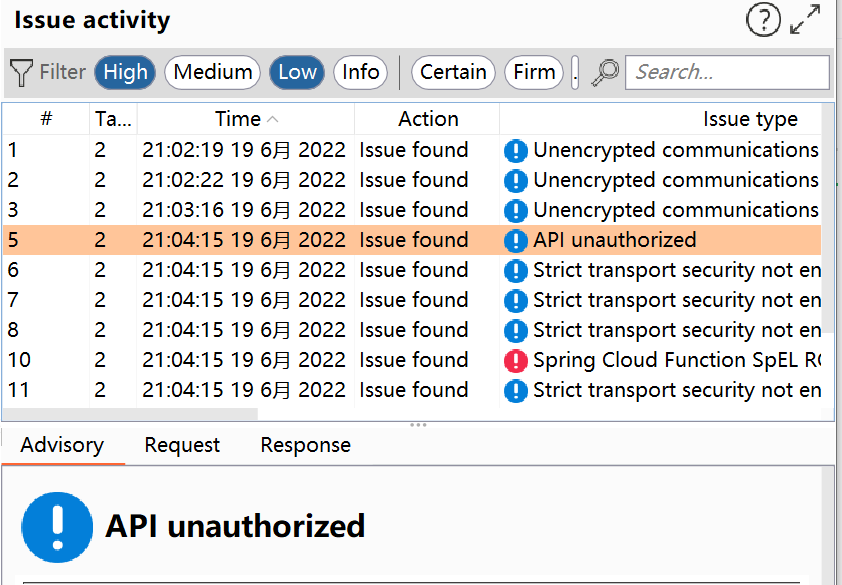 tpt11fb/springvulscan
burpsuite 的Spring漏洞扫描插件。SpringVulScan:支持检测:路由泄露|CVE-2022-22965|CVE-2022-22963|CVE-2022-22947|CVE-2016-4977
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
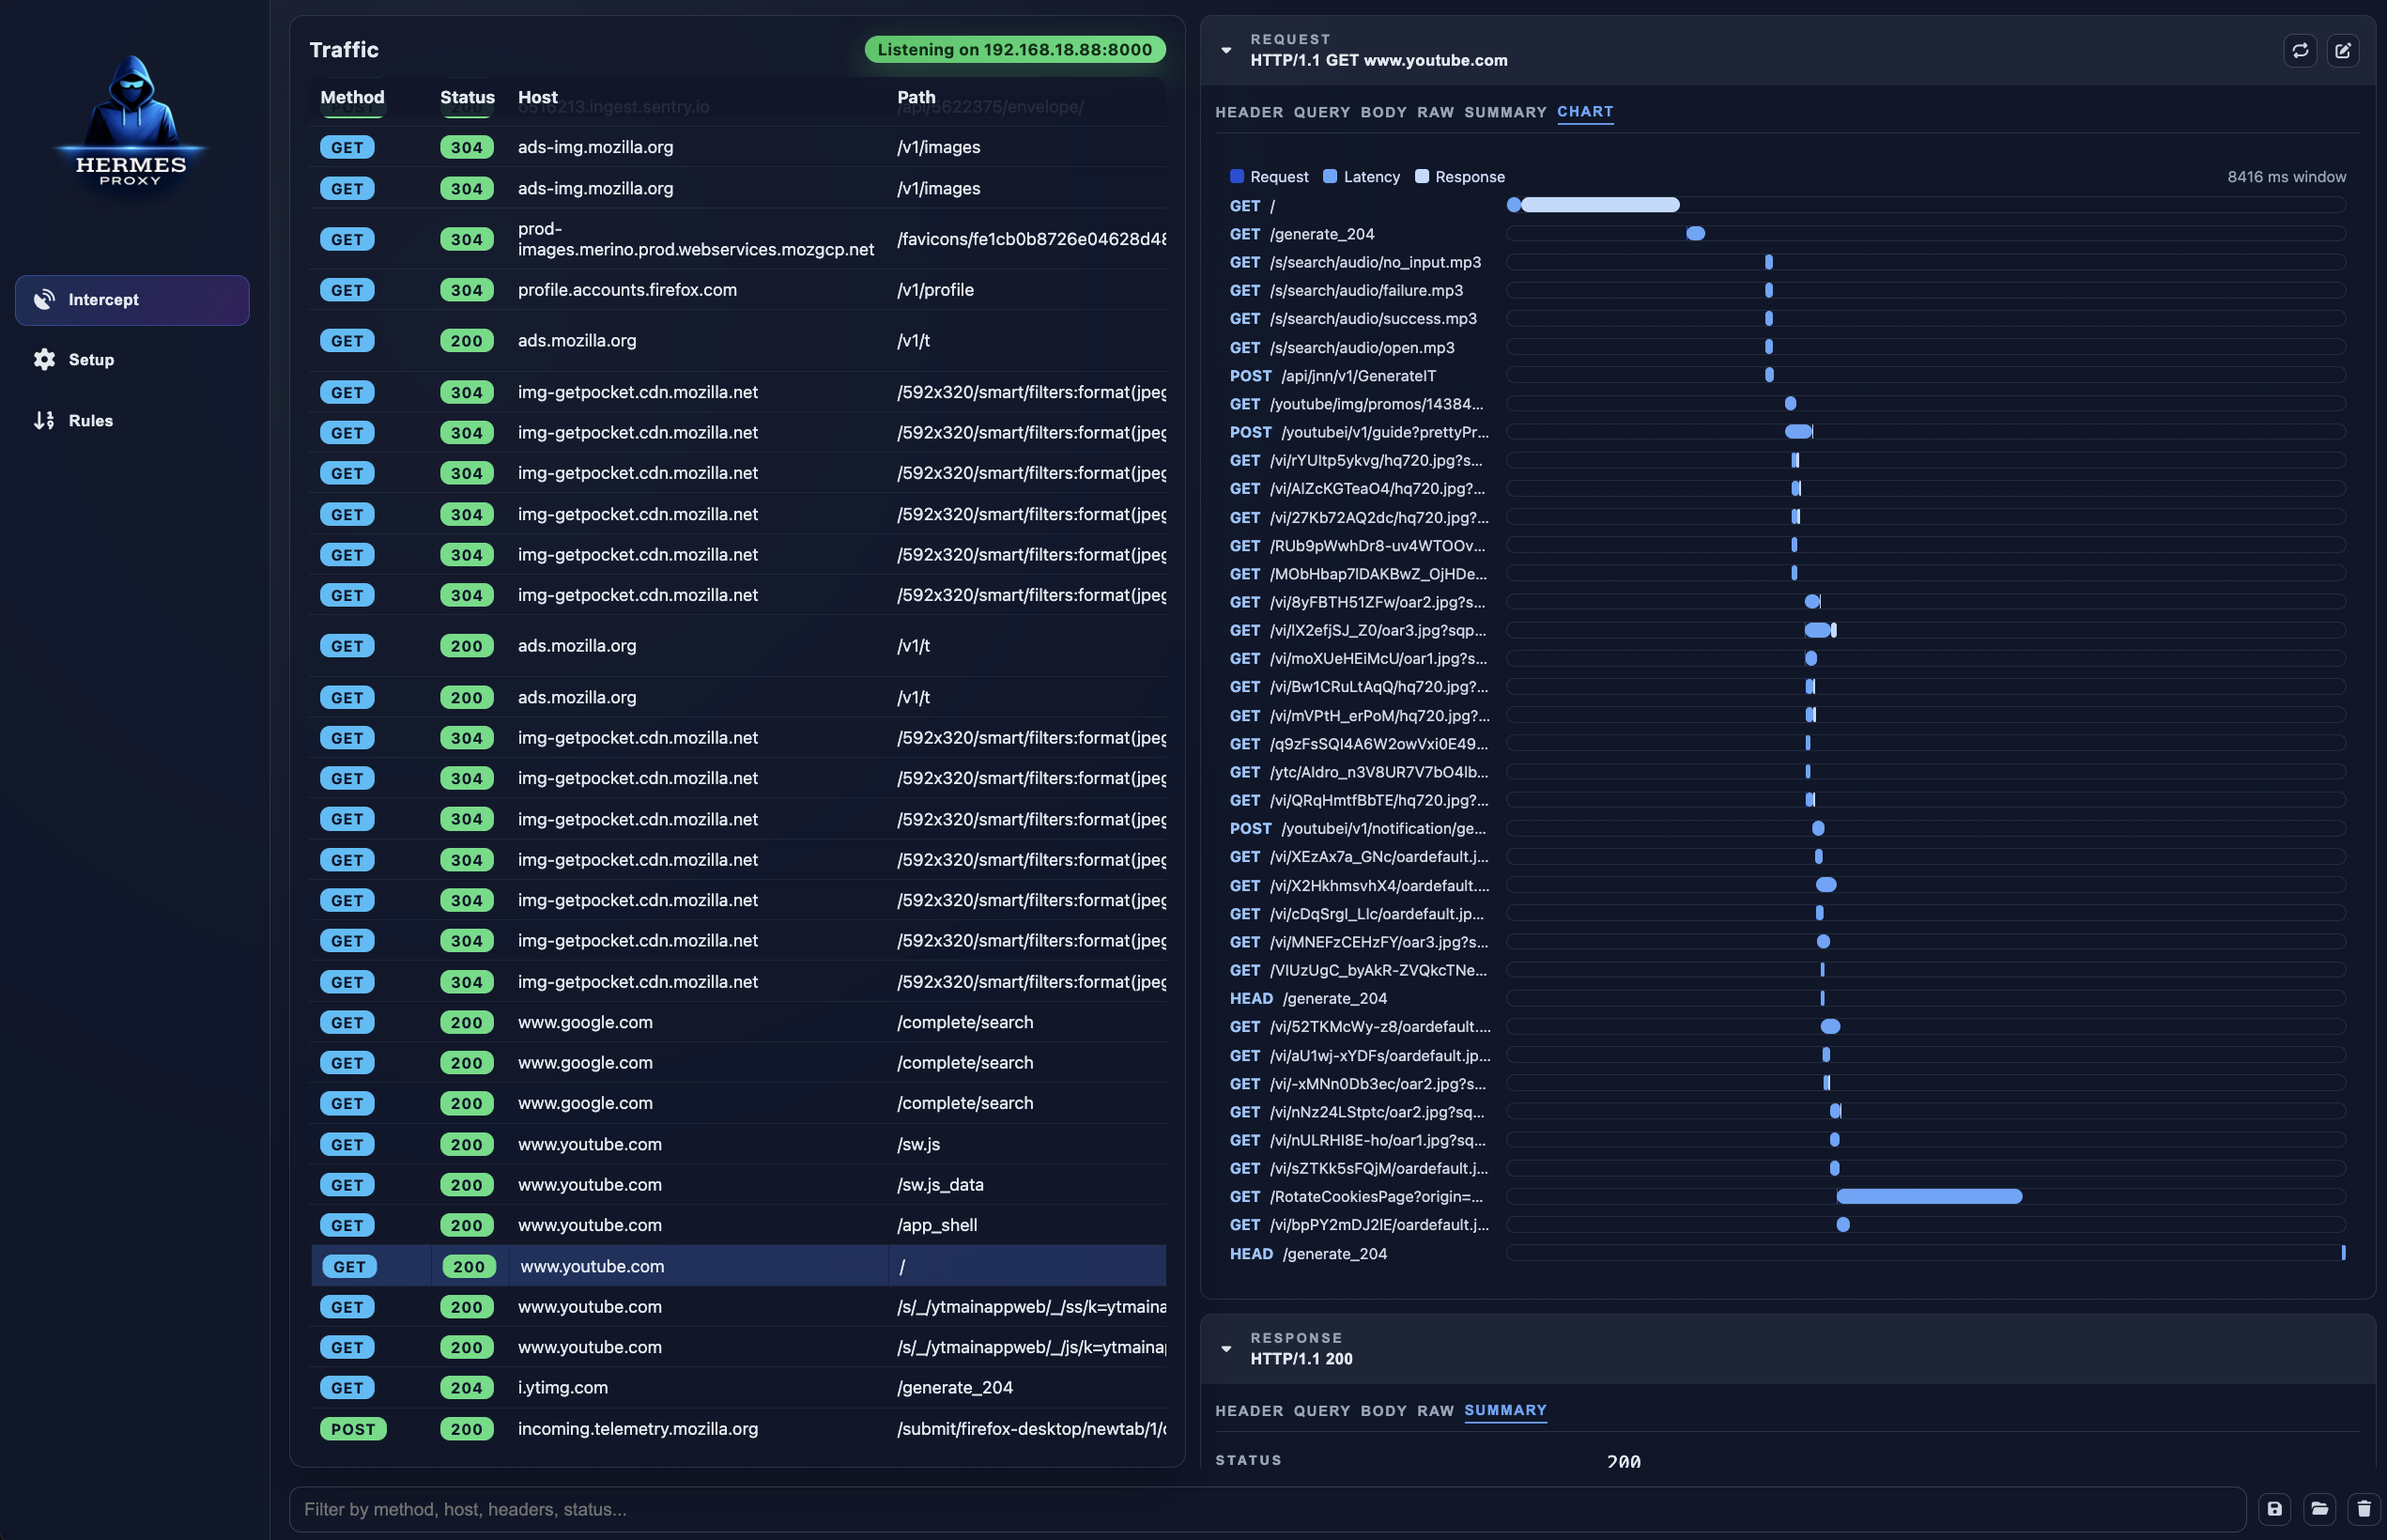 jp/hermes-proxy
Hermes Proxy - HTTP Traffic Analyzer
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
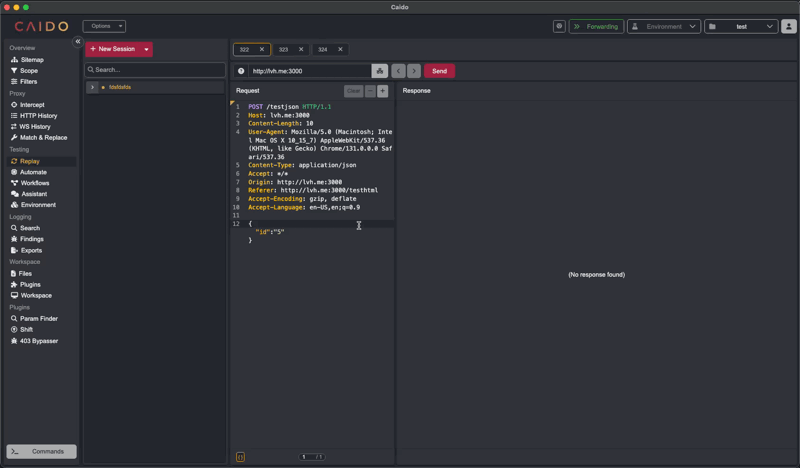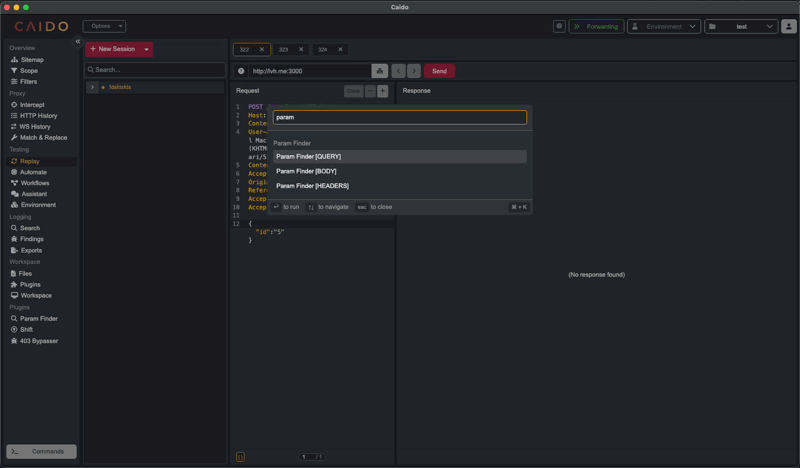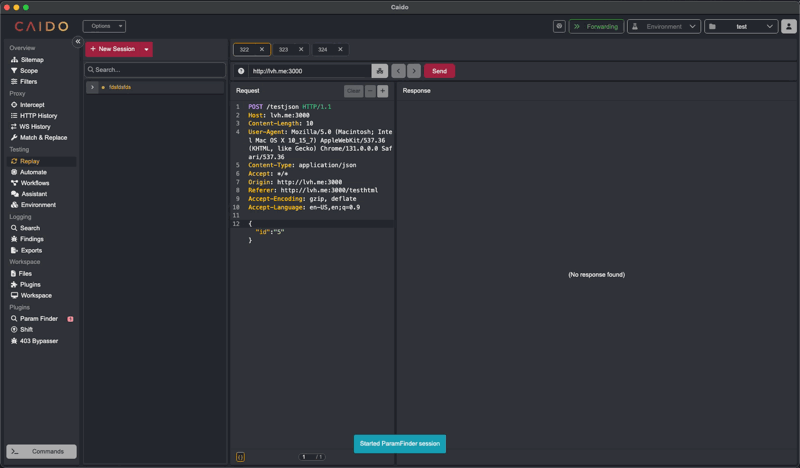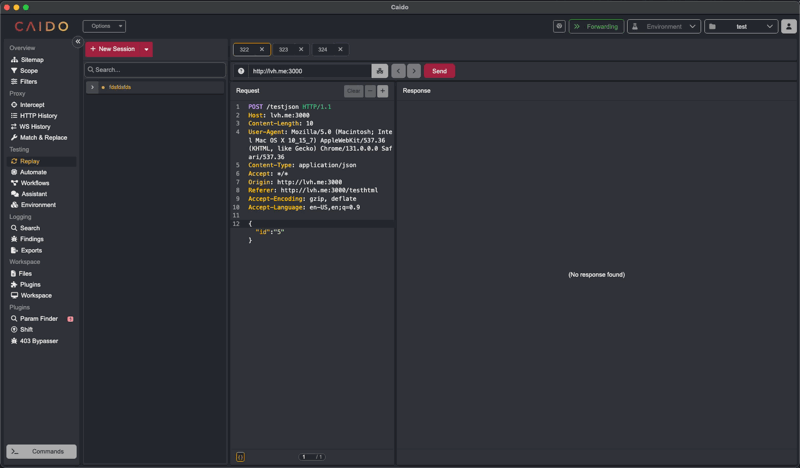 caido-community/paramfinder
Discover hidden parameters in Caido
 hackinglz/maps_scanner
MAPS cloud scanner and response parser for Microsoft Defender research.
 joanbono/gurp
Burp Commander written in Go
 morpheuslord/nmap-api
RESTful API wrapping Nmap for automated network scanning, port detection, service enumeration, and vulnerability analysis with optional AI-powered…