
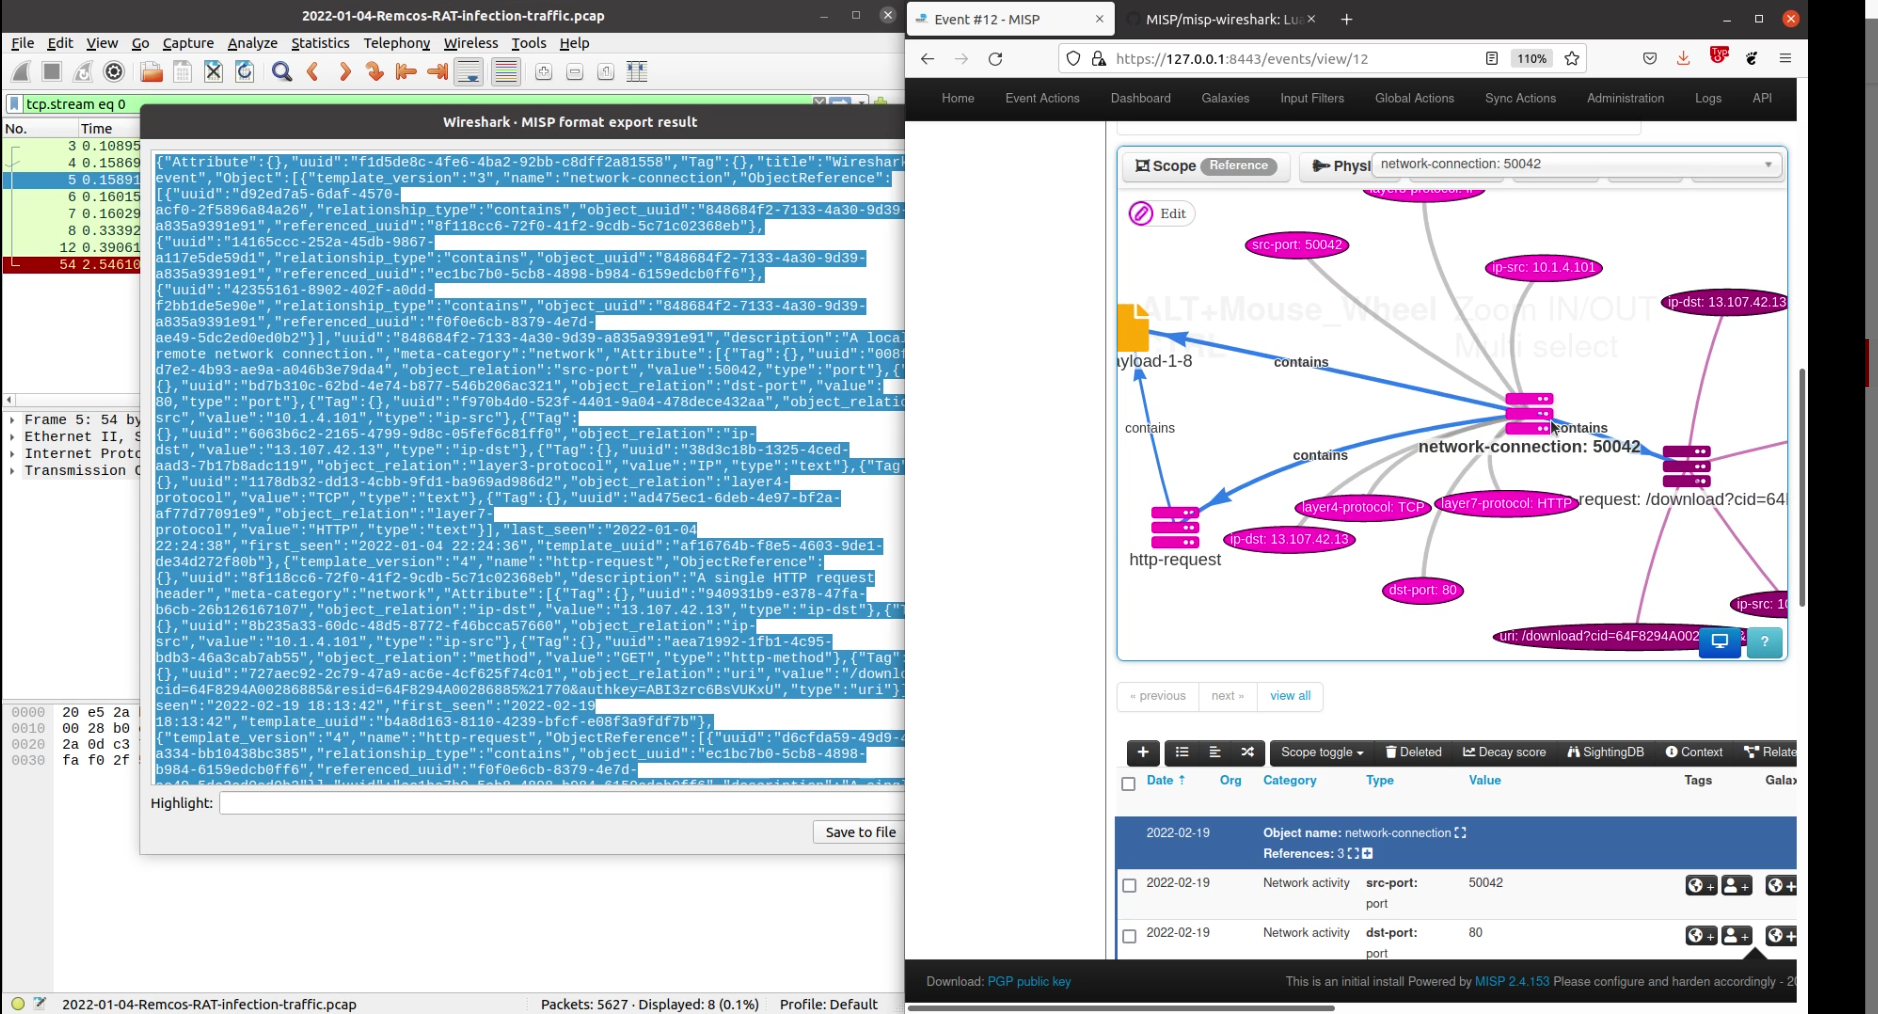
misp-wireshark
 misp/misp-wireshark
Lua plugin to extract data from Wireshark and convert it into MISP format
digital-forensicsforensicsnetwork-forensics+2
502 years ago
misp/misp-wiresharkLua plugin to extract data from Wireshark and convert it into MISP format
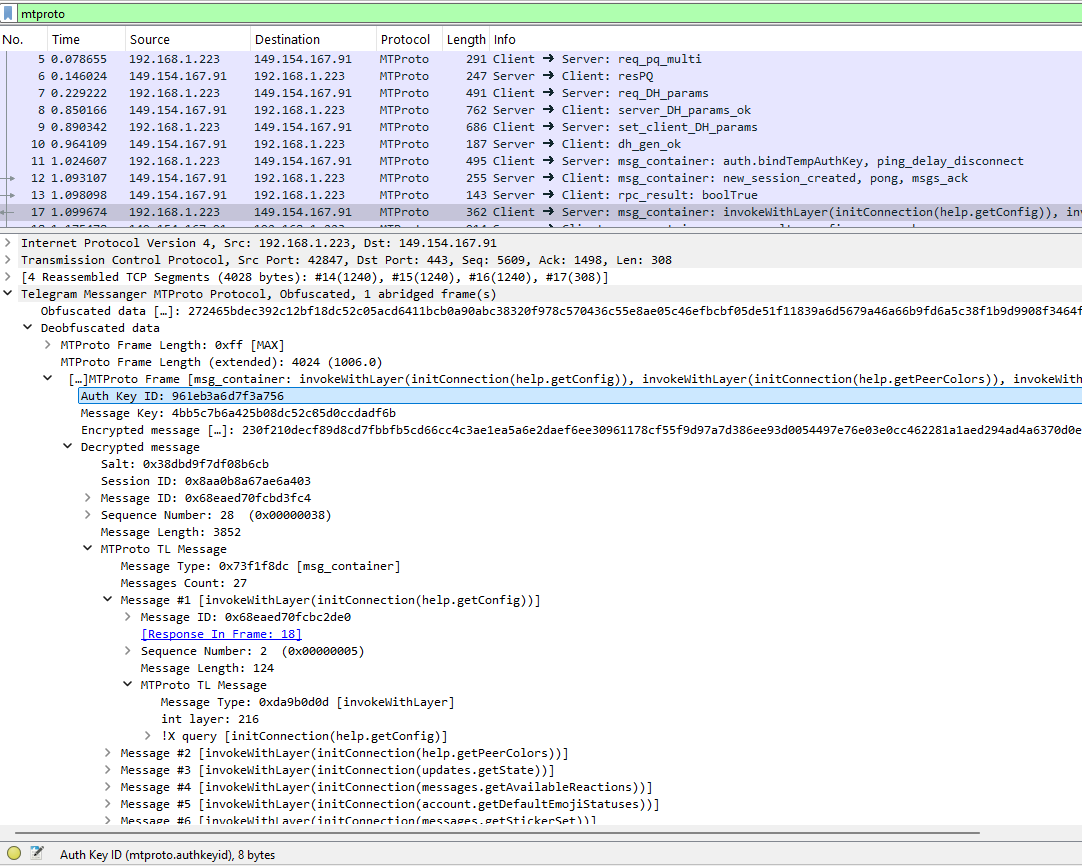 tomer8007/mtproto-dissector
Wireshark plugin for dissecting the Telegram protocol
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.

 ahmad.zaid/netsecdss
Decision Support System for Risk Assessing Network and System Security in Small and Medium Enterprises (SMEs), A graduation project.
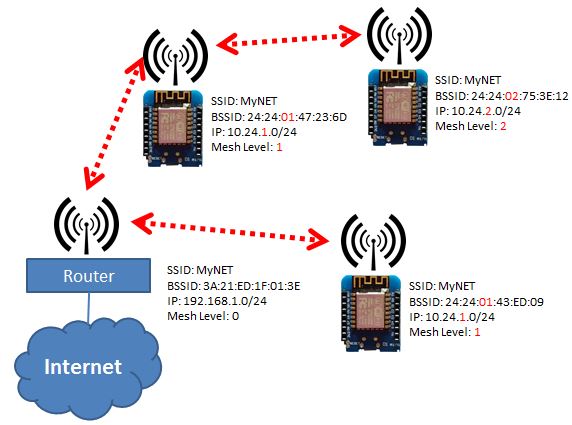 martin-ger/esp_wifi_repeater
A full functional WiFi NAT Router (and now also a WiFi Repeater)
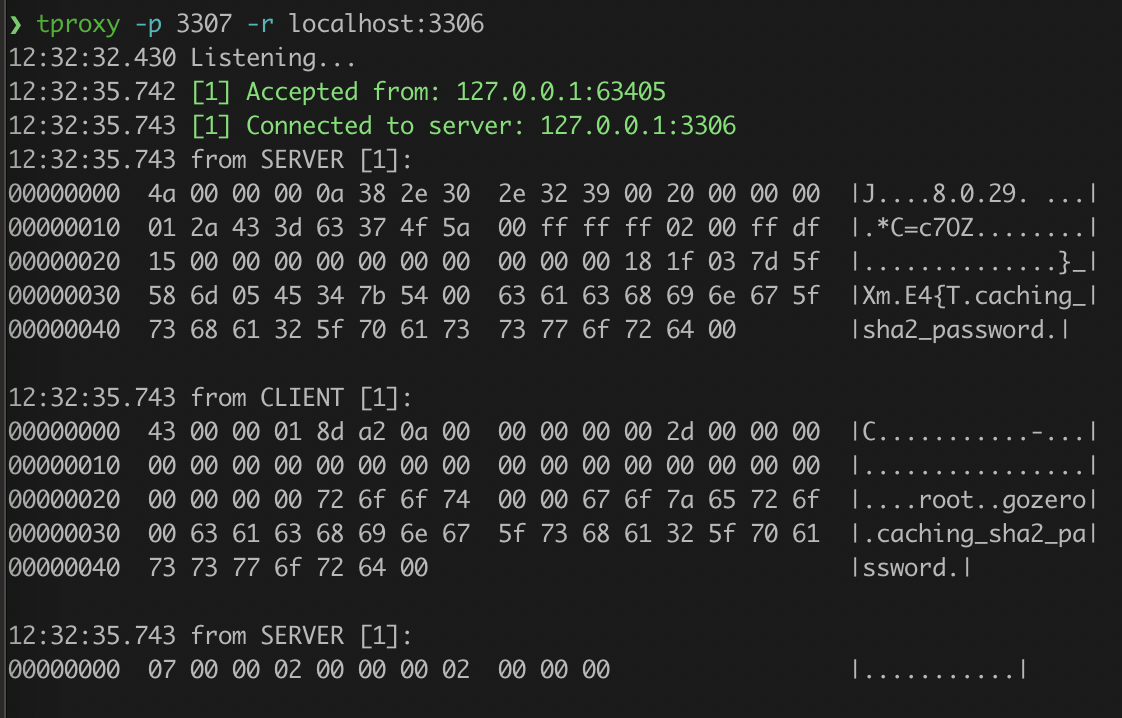 kevwan/tproxy
A cli tool to proxy and analyze TCP connections.
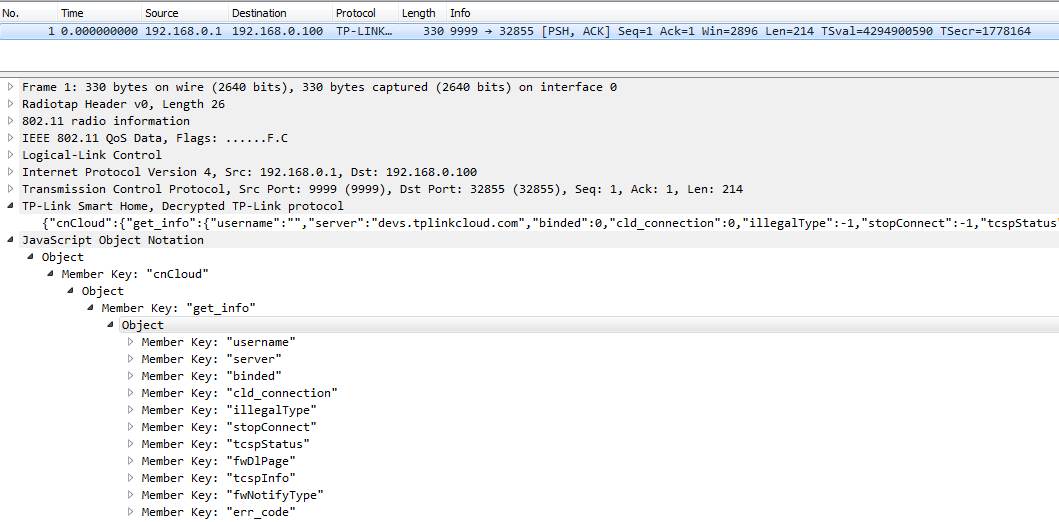 softscheck/tplink-smartplug
TP-Link WiFi SmartPlug Client and Wireshark Dissector
 nccgroup/sniffle
Bluetooth 5 and 4.x LE sniffer for TI CC1352/CC26x2 hardware with support for extended advertising, all PHY modes, MAC/RSSI filtering, and PCAP…
 kerlenton/mcpsnoop
Wireshark for MCP. A transparent proxy between your AI client and MCP server. Watch every call live in your terminal, fail CI on what it finds,…
 awakecoding/wireshark-rdp
Wireshark RDP resources
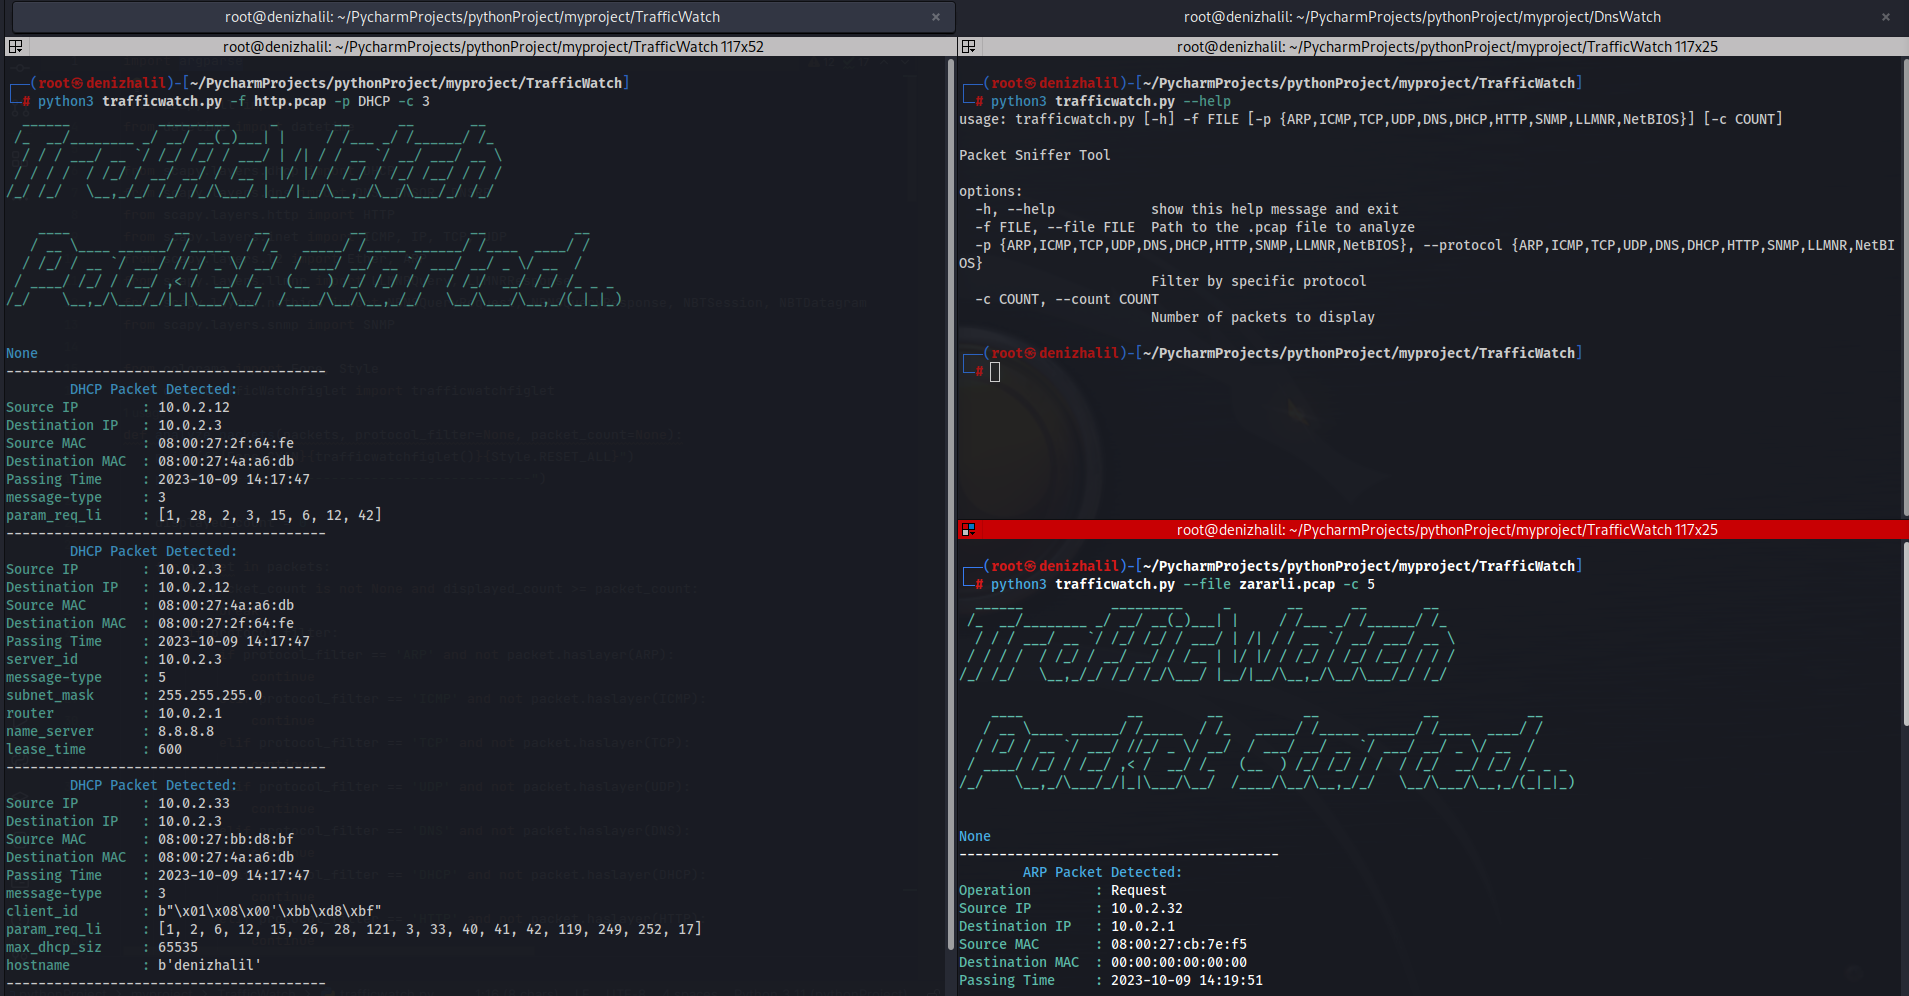 halildeniz/trafficwatch
PCAP-based packet sniffer and analyzer supporting ARP, ICMP, TCP, UDP, DNS, DHCP, HTTP, SNMP, LLMNR, and NetBIOS protocol inspection with filtering…
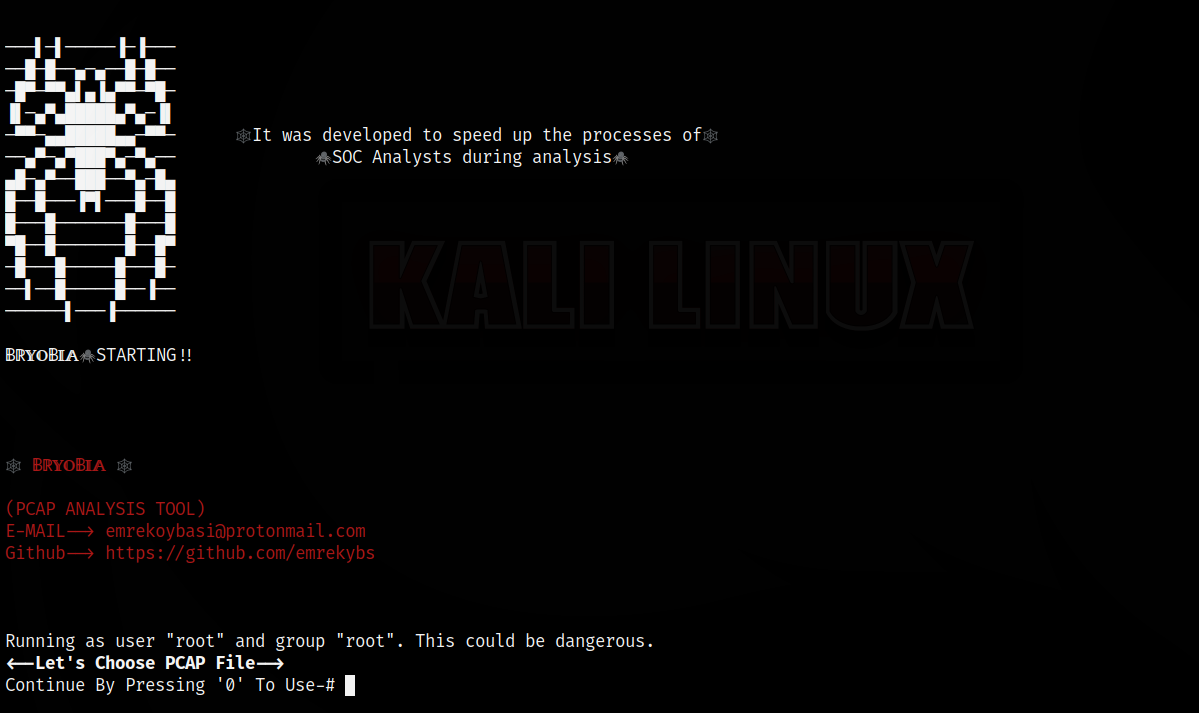 emrekybs/bryobio
It was developed to speed up the processes of SOC Analysts during analysis
 infobyte/wiremax
Lua-based Wireshark postdissector that decrypts and parses Ubiquiti AirMAX/RouterBoard 802.11 vendor IEs into filterable fields.
 kiminewt/pyshark-legacy
Python wrapper for tshark, allowing python packet parsing using wireshark dissectors (Python2 legacy version)
 abiral-timalsina/cyber-defenders-lab-
My write-ups from CyberDefenders' Blue Team labs, solved using Wireshark. Covers TeamCity RCE (CVE-2024-27198), XSS session hijacking, and…
 trinadh-dasari-cyber/eternalblue-ms17-010-research
Controlled reproduction of CVE-2017-0144 (EternalBlue) in an isolated AWS EC2 lab — exploit analysis, Wireshark traffic capture, and MITRE ATT&CK…
 ivoalbacete/kali-metasploitable
Escaneo de vulnerabilidades, análisis de tráfico con Wireshark y explotación controlada del CVE-2011-2523 (vsftpd 2.3.4) en entorno de red segura.
 b4ntgrim/vuln_remediation_megaquagga
Remediation report for MegaQuagga Publishing validating the mitigation of CVE-2019-9978 through progressive defensive layering. Documents reverse…