

CVE-2019-11932
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
binary-exploitationexploitationmobile-security+3
2675 years ago
dorkerdevil/cve-2019-11932double-free bug in WhatsApp exploit poc
 ariary/notionterm
Embed a reverse shell in Notion pages using the Notion API as a proxy, enabling stealthy remote shell sessions with encrypted and authenticated…
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.
 mr-r3b00t/cve-2023-20198-ios-xe-scanner
Single-threaded PowerShell PoC scanner for CVE-2023-20198 targeting Cisco IOS XE devices. Quick proof-of-concept for vulnerability detection and…
 code-developers/cve-2020-11932
Proof-of-concept exploit for CVE-2020-11932, a double-free vulnerability in WhatsApp GIF processing, enabling remote code execution via crafted .gif…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 boompig/cve-2016-6662
Exploit code for MySQL remote root code execution and privilege escalation (CVE-2016-6662), including Python and C implementations.
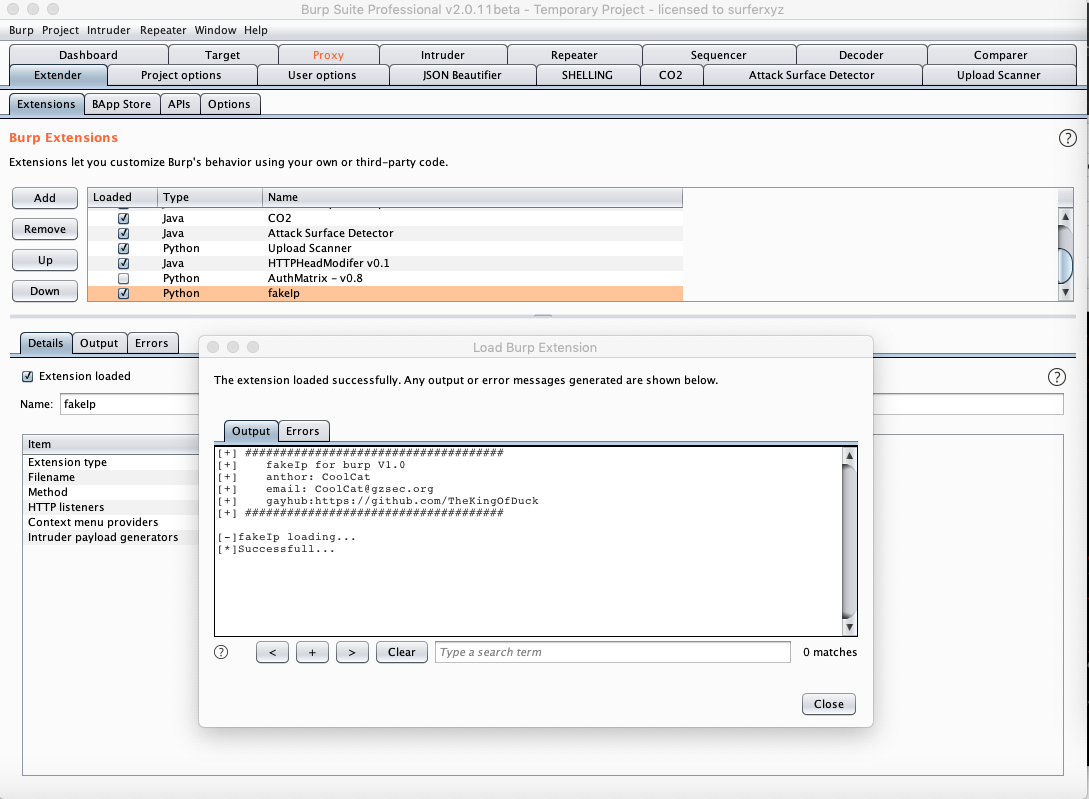 thekingofduck/burpfakeip
Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
 mk-ultra-project-monarch/cve-2017-7921-writeup-2026
Vulnerability research write-up on CVE-2017-7921 — a critical unauthenticated auth bypass in Hikvision IP cameras/DVRs/NVRs, covering root cause,…
 lequockhanh2k/tool_camera_exploit_netwave_cve-2018-6479
Exploit tool for CVE-2018-6479, a denial-of-service vulnerability in Netwave IP cameras. Targets IoT devices to trigger temporary service disruption…
 jet-pentest/cve-2020-25748
Documentation of CVE-2020-25748: Cleartext transmission vulnerability in Rubetek IP cameras allowing MITM interception and modification of video…
 yassineaboukir/cve-2020-5902
Proof of concept for CVE-2020-5902
 pentastic-be/cve-2025-61304
OS command injection vulnerability in Dynatrace ActiveGate ping extension up to 1.016 via crafted ip address
 amitlttwo/cve-2020-5902
In BIG-IP versions 15.0.0-15.1.0.3, 14.1.0-14.1.2.5, 13.1.0-13.1.3.3, 12.1.0-12.1.5.1, and 11.6.1-11.6.5.1, the Traffic Management User Interface…
 dnerzker/cve-2020-5902
Proof-of-concept exploit for CVE-2020-5902, a remote code execution vulnerability in F5 BIG-IP TMUI, with file read and command execution payloads…
 tim-hoekstra/cve-2024-24919
Multi-threaded exploit script for CVE-2024-24919 that scans a list of IP addresses and outputs results, intended for educational use.
 papayajackal/ipeeyoupeewepee
Scanner and attack suite for hosts that forward unauthenticated packets via IPIP and GRE protocols. (CVE-2020-10136 CVE-2024-7595)