
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
305 results
Obfusk8 preview

Obfusk8

GitHubx86byte/obfusk8

Obfusk8: lightweight Obfuscation library based on C++17 / Header Only for windows binaries
cryptographyexploit-frameworkspayload-development+4
820
2 months ago
SourcePoint preview

SourcePoint

GitHubtylous/sourcepoint

Polymorphic C2 profile generator for Cobalt Strike that automates creation of evasive beacon configurations with randomized options for HTTP, DNS,…
command-and-controlexploit-frameworkspayload-generation+1
1.2k1 year ago
ThreadStackSpoofer preview

ThreadStackSpoofer

GitHubmgeeky/threadstackspoofer

Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
exploit-frameworksmalware-analysismemory-forensics+4
1.2k4 years ago
BDFProxy preview

BDFProxy

GitHubsecretsquirrel/bdfproxy

Patch Binaries via MITM: BackdoorFactory + mitmProxy.

binary-exploitationcommand-and-controlexploit-frameworks+8
1.0k5 years ago
AceLdr preview

AceLdr

GitHubkyleavery/aceldr

Cobalt Strike UDRL for memory scanner evasion.

exploit-frameworksmemory-forensicspayload-development+2
1.0k2 years ago
Cooolis-ms preview

Cooolis-ms

GitHubrvn0xsy/cooolis-ms

Cooolis-ms是一个包含了Metasploit Payload Loader、Cobalt Strike External C2 Loader、Reflective DLL injection的代码执行工具,它的定位在于能够在静态查杀上规避一些我们将要执行且含有特征的代码,帮助红队人员更方便快…
command-and-controlexploit-frameworksids-ips-evasion+7
9272 years ago
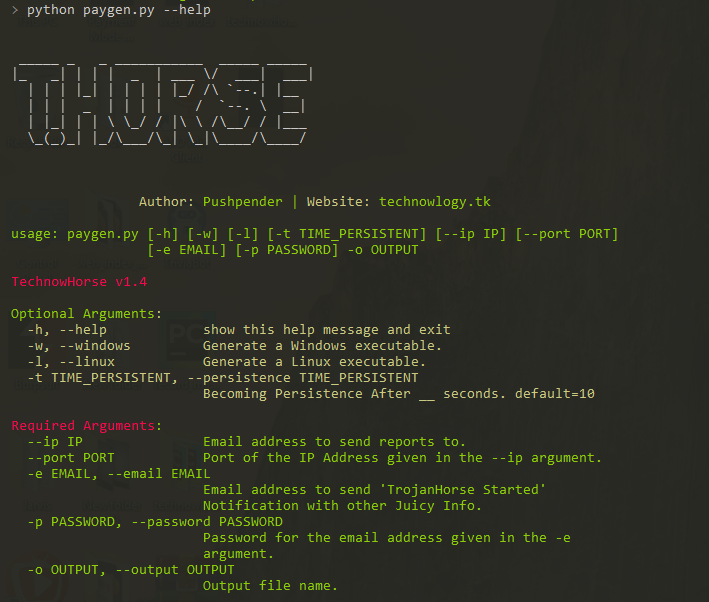
thorse preview

thorse

GitHubpushpenderindia/thorse

THorse is a RAT (Remote Administrator Trojan) Generator for Windows/Linux systems written in Python 3.
anti-botcommand-and-controlexploit-frameworks+6
6153 years ago
NimPackt-v1 preview

NimPackt-v1

GitHubchvancooten/nimpackt-v1

Nim-based assembly packer and shellcode loader for opsec & profit
binary-exploitationexploit-frameworkspayload-generation+3
4863 years ago
ropium preview

ropium

GitHubboyan-milanov/ropium

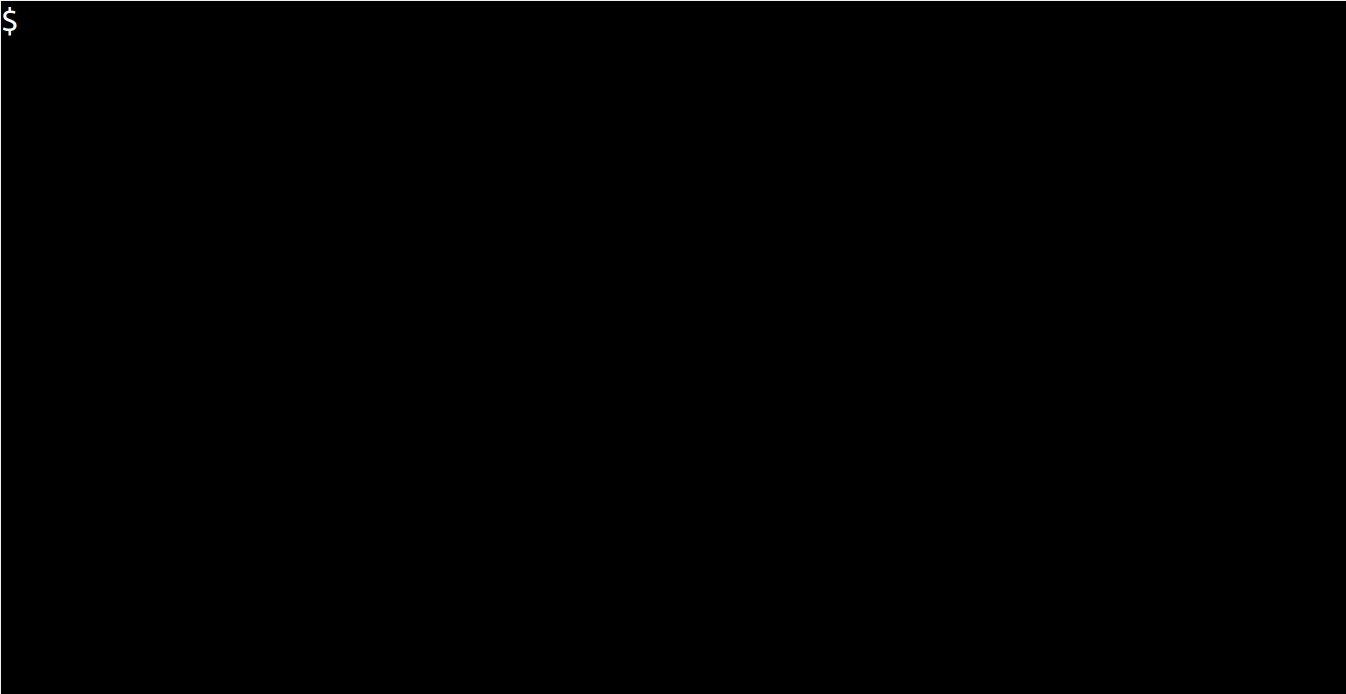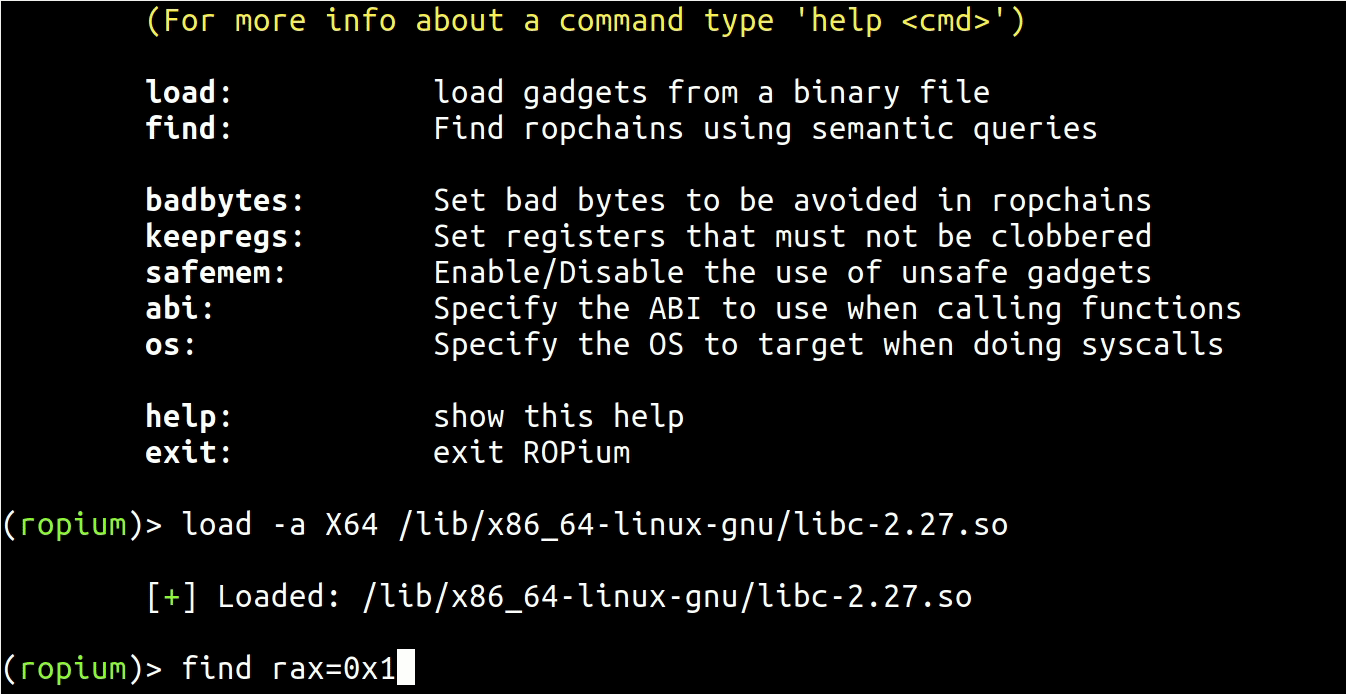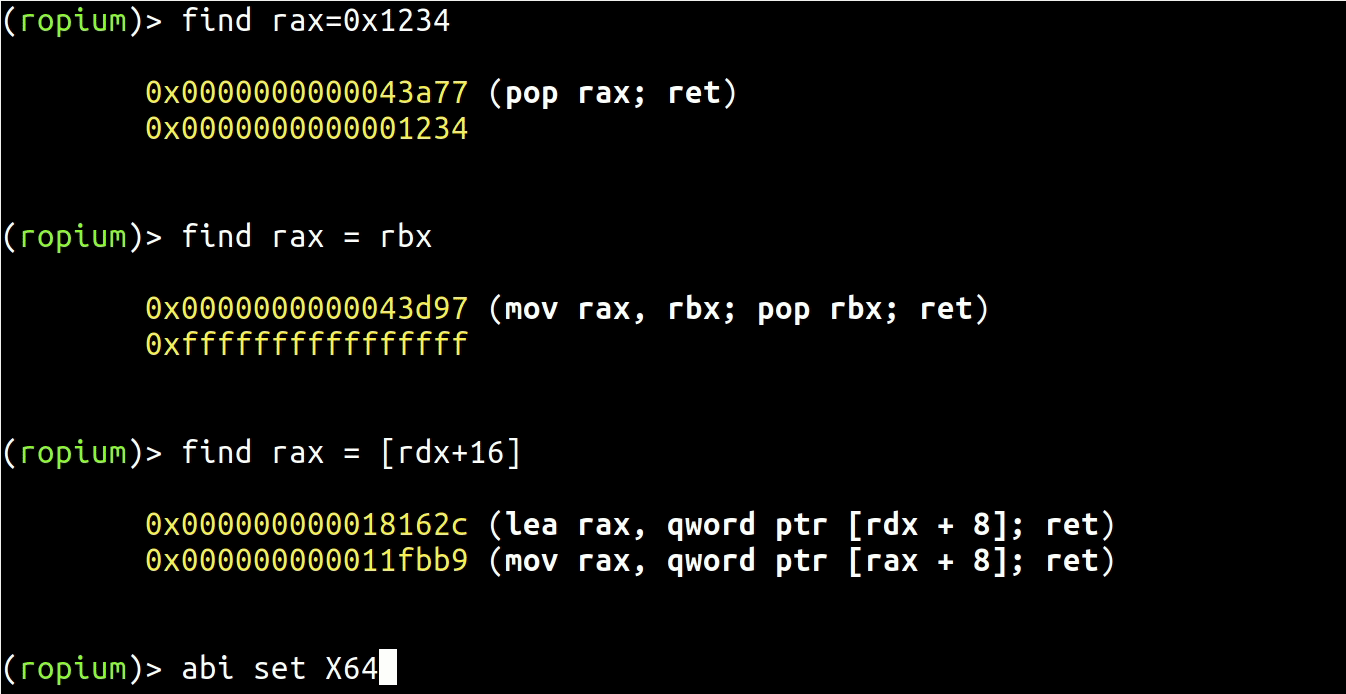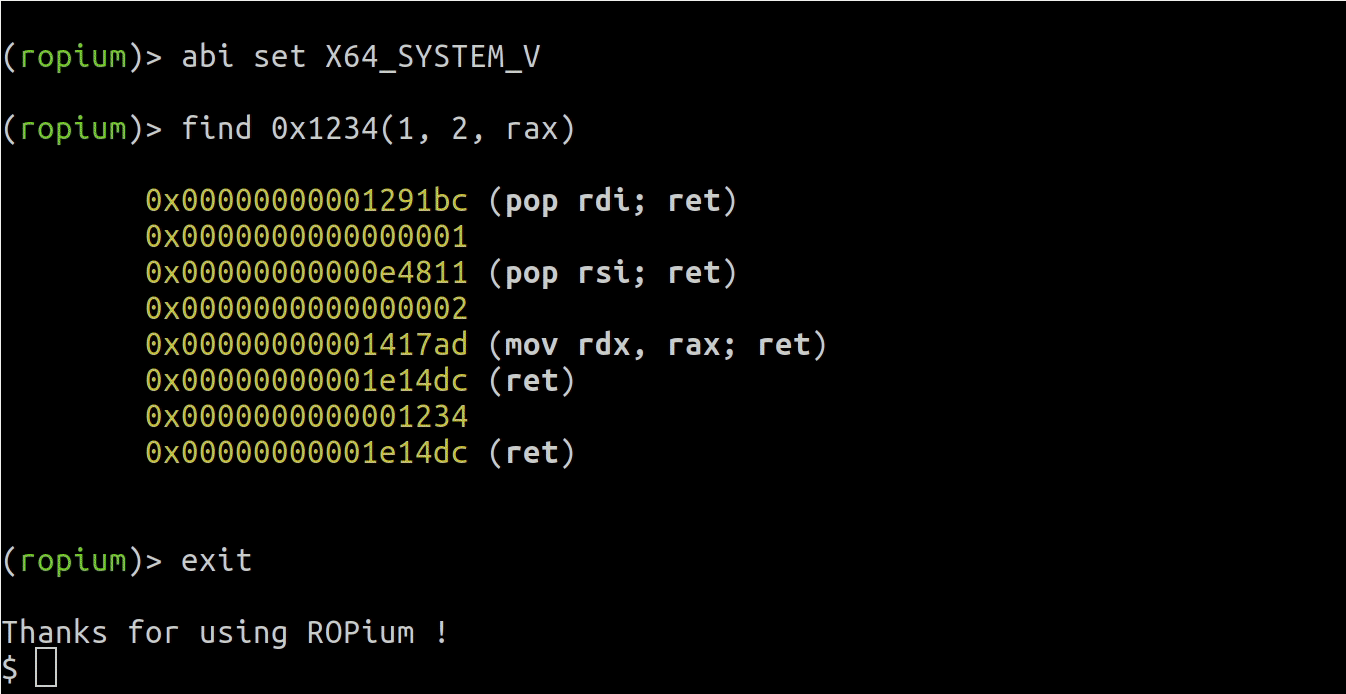
Automated ROP chain builder that extracts and analyzes gadgets from binaries using semantic queries, supporting X86/X64 architectures with a Python…

binary-exploitationexploit-frameworkspayload-development+2
4024 years ago
RedPeanut preview

RedPeanut

GitHubb4rtik/redpeanut

RedPeanut is a small RAT developed in .Net Core 2 and its agent in .Net 3.5 / 4.0.

command-and-controlexploit-frameworkspayload-generation+7
3316 years ago
Shelter preview

Shelter

GitHubkudaes/shelter

ROP-based sleep obfuscation to evade memory scanners

exploit-frameworksmemory-forensicsred-teaming
3921 year ago
CVE-2016-6366 preview

CVE-2016-6366

GitHubrisksense-ops/cve-2016-6366

Public repository for improvements to the EXTRABACON exploit
binary-analysisexploitationexploit-frameworks+8
1639 years ago
kimi preview

kimi

GitHubchaitanyaharitash/kimi

Script to generate malicious debian packages (debain trojans).

command-and-controlexploit-frameworksmalware-analysis+5
1237 years ago
CustomC2ChannelTemplate preview

CustomC2ChannelTemplate

GitHubcodextf2/customc2channeltemplate

template for developing custom C2 channels for Cobalt Strike using IAT hooks applied by a reflective loader.
command-and-controlexploit-frameworkspayload-development+3
1078 months ago
crauEmu preview

crauEmu

GitHubdsecurity/crauemu

crauEmu is an uEmu extension for developing and analyzing payloads for code-reuse attacks
binary-exploitationexploit-frameworkspayload-development+1
1106 years ago
pois0nSword preview

pois0nSword

GitHubgenericcoding/pois0nsword

A demonstration of read write using cve-2025-43529 and userland PAC bypass on iOS 26.1
binary-exploitationexploitationexploit-frameworks+5
691 month ago
CrystalSliver preview

CrystalSliver

GitHublicitrasimone/crystalsliver

Crystal Palace Evasion kit for Sliver

command-and-controlexploit-frameworksids-ips-evasion+9
1173 months ago
Cobaltstrike_BOFLoader preview

Cobaltstrike_BOFLoader

GitHubcodextf2/cobaltstrike_bofloader

open source port/reimplementation of the Cobalt Strike BOF Loader as is

binary-exploitationexploit-frameworkspayload-development+3
746 months ago
Previous1…151617Next