
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
589 results
OpenDoor preview

OpenDoor

GitHubstanislav-web/opendoor

OWASP Web Recon & Directory Discovery Platform
information-gatheringpenetration-testingreconnaissance+4
1.0k1 month ago
Bug_Bounty_writeups preview

Bug_Bounty_writeups

GitHubalexbieber/bug_bounty_writeups

Curated collection of bug bounty writeups covering OWASP Top 10 vulnerabilities, including XSS, SQLi, SSRF, and RCE, for educational learning and…

curated-resourceseducationvulnerability-analysis+1
8504 years ago
MARA_Framework preview

MARA_Framework

GitHubxtiankisutsa/mara_framework

MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
android-securitybinary-analysiscode-analysis+6
6707 years ago
WebGoat.NET preview

WebGoat.NET

GitHubjerryhoff/webgoat.net

OWASP WebGoat.NET

ctfeducationlabs-practice+3
25812 years ago
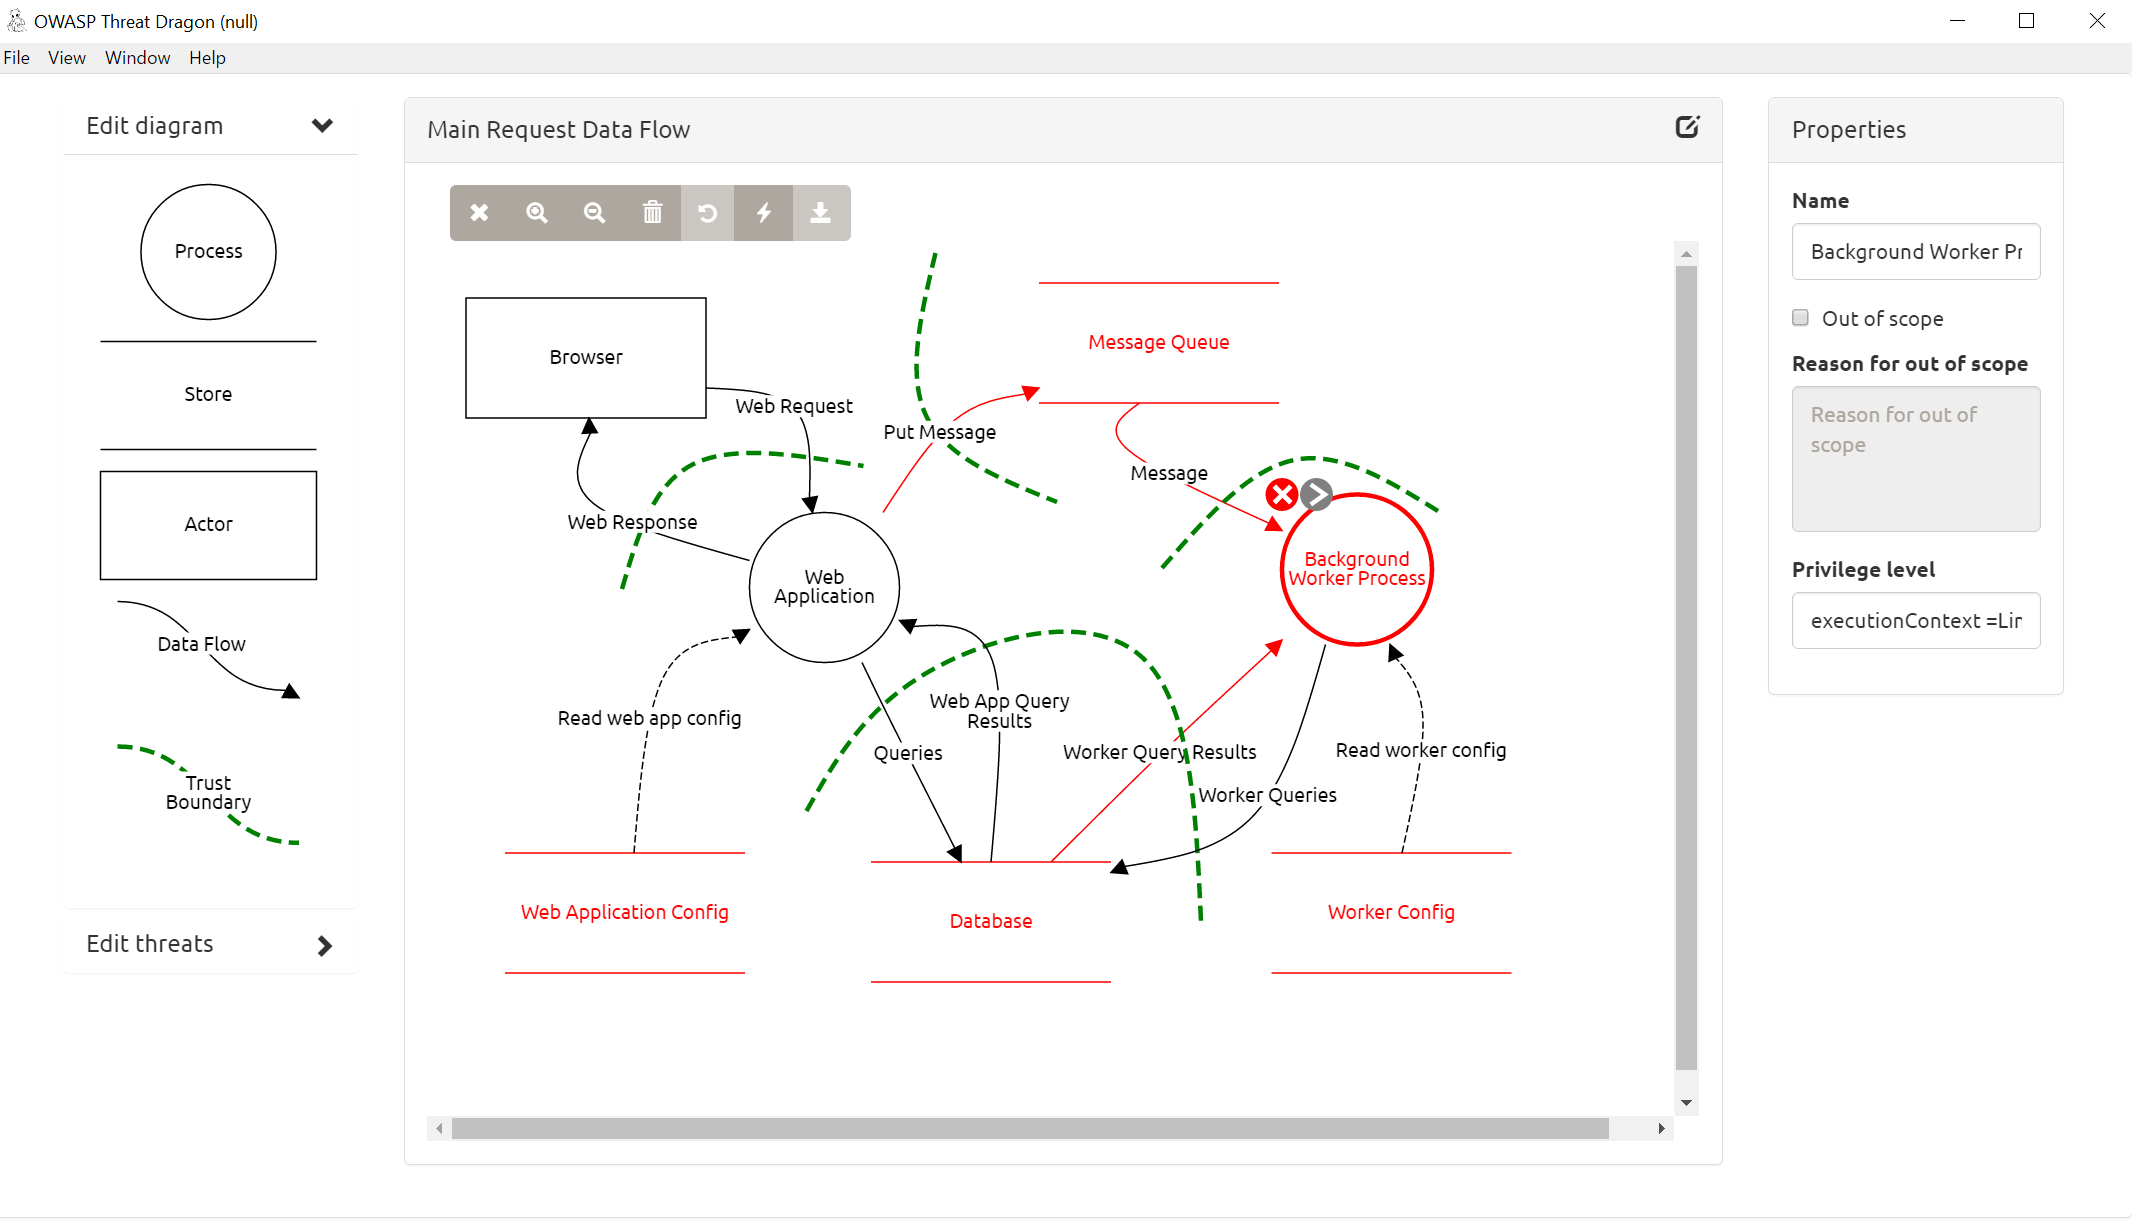
owasp-threat-dragon-desktop preview

owasp-threat-dragon-desktop

GitHubmike-goodwin/owasp-threat-dragon-desktop

An installable desktop variant of OWASP Threat Dragon
educationvulnerability-analysis
5916 years ago
training-security-awareness preview

training-security-awareness

GitHubransomleak/training-security-awareness

Open-source interactive security awareness training library with 130+ SCORM exercises covering phishing, vishing, BEC, MFA fatigue, and OWASP AI/LLM…

ai-securityeducationemail-security+5
19717 days ago
BurpAPISecuritySuite preview

BurpAPISecuritySuite

GitHubteycir/burpapisecuritysuite

Burp Suite extension for API security testing with 15 attack types, 108+ payloads, intelligent fuzzing, BOLA/IDOR detection, AI integration, and…

api-securityapi-security-testingfuzzing+4
3411 month ago
OWASP-mth3l3m3nt-framework preview

OWASP-mth3l3m3nt-framework

GitHubalienwithin/owasp-mth3l3m3nt-framework

OWASP Mth3l3m3nt Framework is a penetration testing aiding tool and exploitation framework. It fosters a principle of attack the web using the web as…

command-and-controlexploit-frameworkspayload-generation+3
1645 years ago
teler-waf preview

teler-waf

GitHubteler-sh/teler-waf

teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…

api-securitydefensive-toolsids-ips-evasion+5
4081 year ago
Thick-Client-Pentest-Checklist preview

Thick-Client-Pentest-Checklist

GitHubhari-prasaanth/thick-client-pentest-checklist

A OWASP Based Checklist With 80+ Test Cases
binary-analysiscurated-resourceseducation+5
2063 years ago
bordair-multimodal preview

bordair-multimodal

GitHubjosh-blythe/bordair-multimodal

Open-source cross-modal and multimodal prompt injection test suite. 250,000+ attack payloads across text, image, document, and audio modalities.…
adversarial-attackai-securitycurated-resources+5
762 months ago
Owasp-top-10-k8s-2025 preview

Owasp-top-10-k8s-2025

GitHubhac01/owasp-top-10-k8s-2025

Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…

cloud-securitycontainer-securityctf+8
492 months ago
training-application-security preview

training-application-security

GitHubransomleak/training-application-security

Interactive secure coding training with hands-on SCORM exercises covering OWASP Top 10 web and API vulnerabilities, Git/secrets exposure, and…
api-securitydevsecopseducation+7
1817 days ago
OWASP-WSTG-Rag preview

OWASP-WSTG-Rag

GitHubzilbonn/owasp-wstg-rag

OWASP Web Security Testing Guide RAG system with ChromaDB, MCP for Claude Code
ai-securityapi-security-testingauthentication+8
229 months ago
FiddleZAP preview

FiddleZAP

GitHubmalwareinfosec/fiddlezap

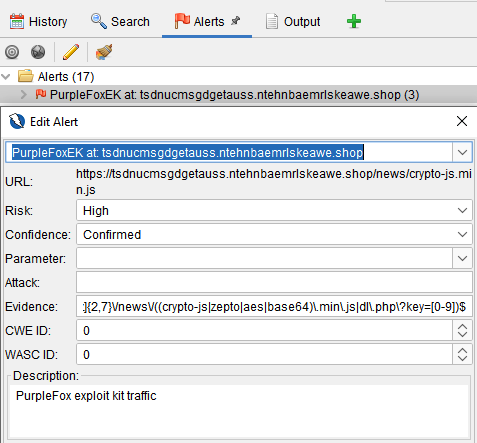
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
intrusion-detectionmalware-analysisthreat-intelligence+2
174 years ago
api-scanner-docker preview

api-scanner-docker

GitHubcspf-founder/api-scanner-docker

Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …

api-securityapi-security-testingconfiguration-auditing+5
97 months ago
zap-api-rust preview

zap-api-rust

GitHubzaproxy/zap-api-rust

Rust client library for the OWASP ZAP API, enabling programmatic access to web application security scanning, vulnerability detection, and proxy…

api-securitypenetration-testingvulnerability-scanners+3
153 years ago
CRSprober preview

CRSprober

GitHubazurit/crsprober

Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.

information-gatheringpenetration-testingvulnerability-analysis+1
710 months ago
Previous1…141516…33Next