
goWAPT
 dzonerzy/gowapt
Go Web Application Penetration Test
fuzzingpenetration-testingscripting-automation+4
3452 years ago
dzonerzy/gowaptGo Web Application Penetration Test
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 redsection/pfuzz
Modular WAF bypass fuzzer with multi-threading, request manipulation, and payload encoding for red team web application testing.
 net-hunter121/api-wordlist
Curated wordlists of API function names, verbs, and nouns for fuzzing web application endpoints with Burp Suite Intruder.
 security-prince/resources-for-application-security
Some good resources for getting started with application security
 coreruleset/ftw
YAML-driven framework for testing Web Application Firewall (WAF) rules using OWASP Core Rule Set baselines. Automates regression detection and…
 sirbugs/endext
Extracts all possible endpoints, URLs, and paths from JavaScript files using customizable regex patterns for web application reconnaissance and API…
 bhavsec/autopentest-ai
Agentic Pentesting MCP server that discovers, exploits, and reports web application vulnerabilities.
 4auvar/vulnnodeapp
Deliberately vulnerable Node.js web application for practicing exploitation of SQL injection, XSS, IDOR, command injection, XXE, and deserialization…

 stolenusername/cowitness
CoWitness is a powerful web application testing tool that enhances the accuracy and efficiency of your testing efforts. It allows you to mimic an…
 owasp/tcasvs
OWASP Thick Client Application Security Verification Standard
 bishopfox/spoofcheckselftest
Web application that lets you test if your domain is vulnerable to email spoofing
 owasp/application-security-curriculum
Structured curriculum for learning application security, covering secure coding, threat modeling, and DevSecOps practices. Designed for self-paced…
 owasp/fiasse
A Framework for Integrating Application Security into Software Engineering (FIASSE) using the Securable Software Engineering Model (SSEM)
 infosecak/defenselessv1
Just another vulnerable web application.
 ulyssessaicha/cve-2023-6875
Proof-of-concept exploit for CVE-2023-6875, demonstrating a web application vulnerability. Includes code and instructions for reproducing the issue.
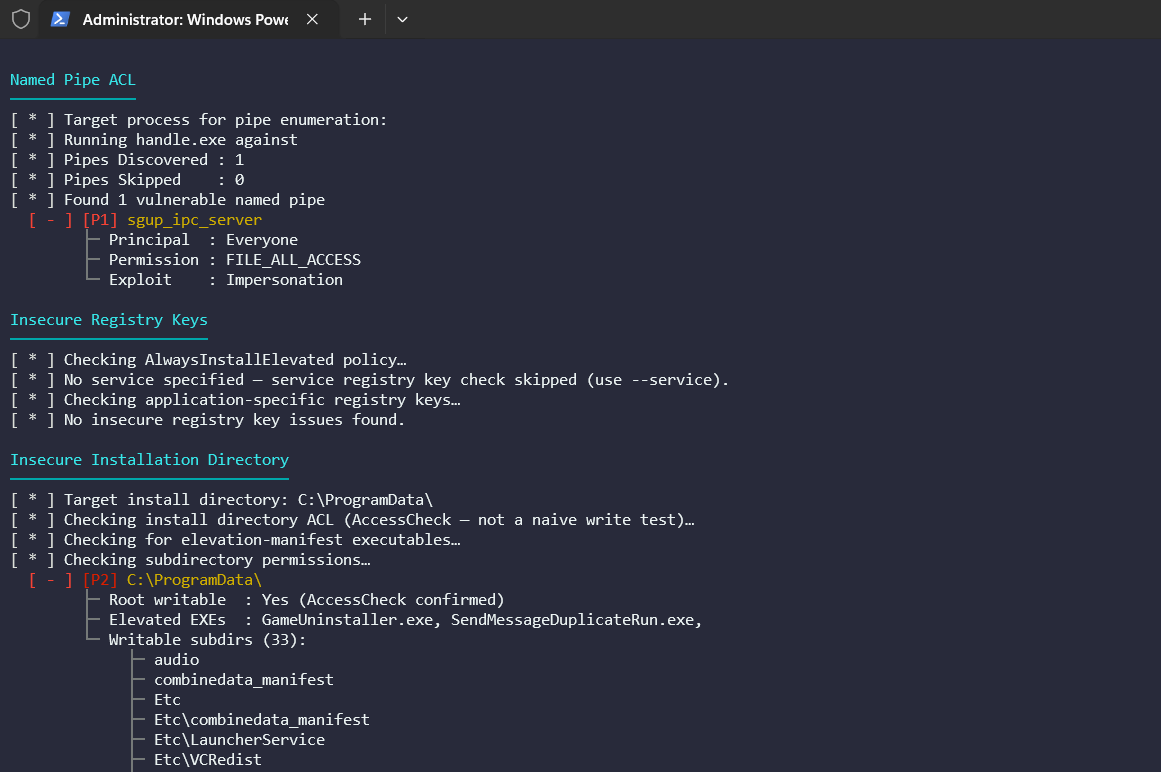 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…