
Azure-Sentinel
 azure/azure-sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise.
cloud-securitycurated-resourcesdefensive-tools+5
6.2k
azure/azure-sentinelCloud-native SIEM for intelligent security analytics for your entire enterprise.
 microsoft/playwright
Browser automation framework with a single API for Chromium, Firefox, and WebKit. Supports web testing, scraping, screenshots, and network…
 r3vpwnx/cve-2026-26119
WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 hotcakex/harden-windows-security
Harden Windows Safely, Securely using Official Supported Microsoft methods and proper explanation | Always up-to-date and works with the latest build…
 bitsadmin/wesng
Windows Exploit Suggester - Next Generation
 microsoft/msticpy
Microsoft Threat Intelligence Security Tools
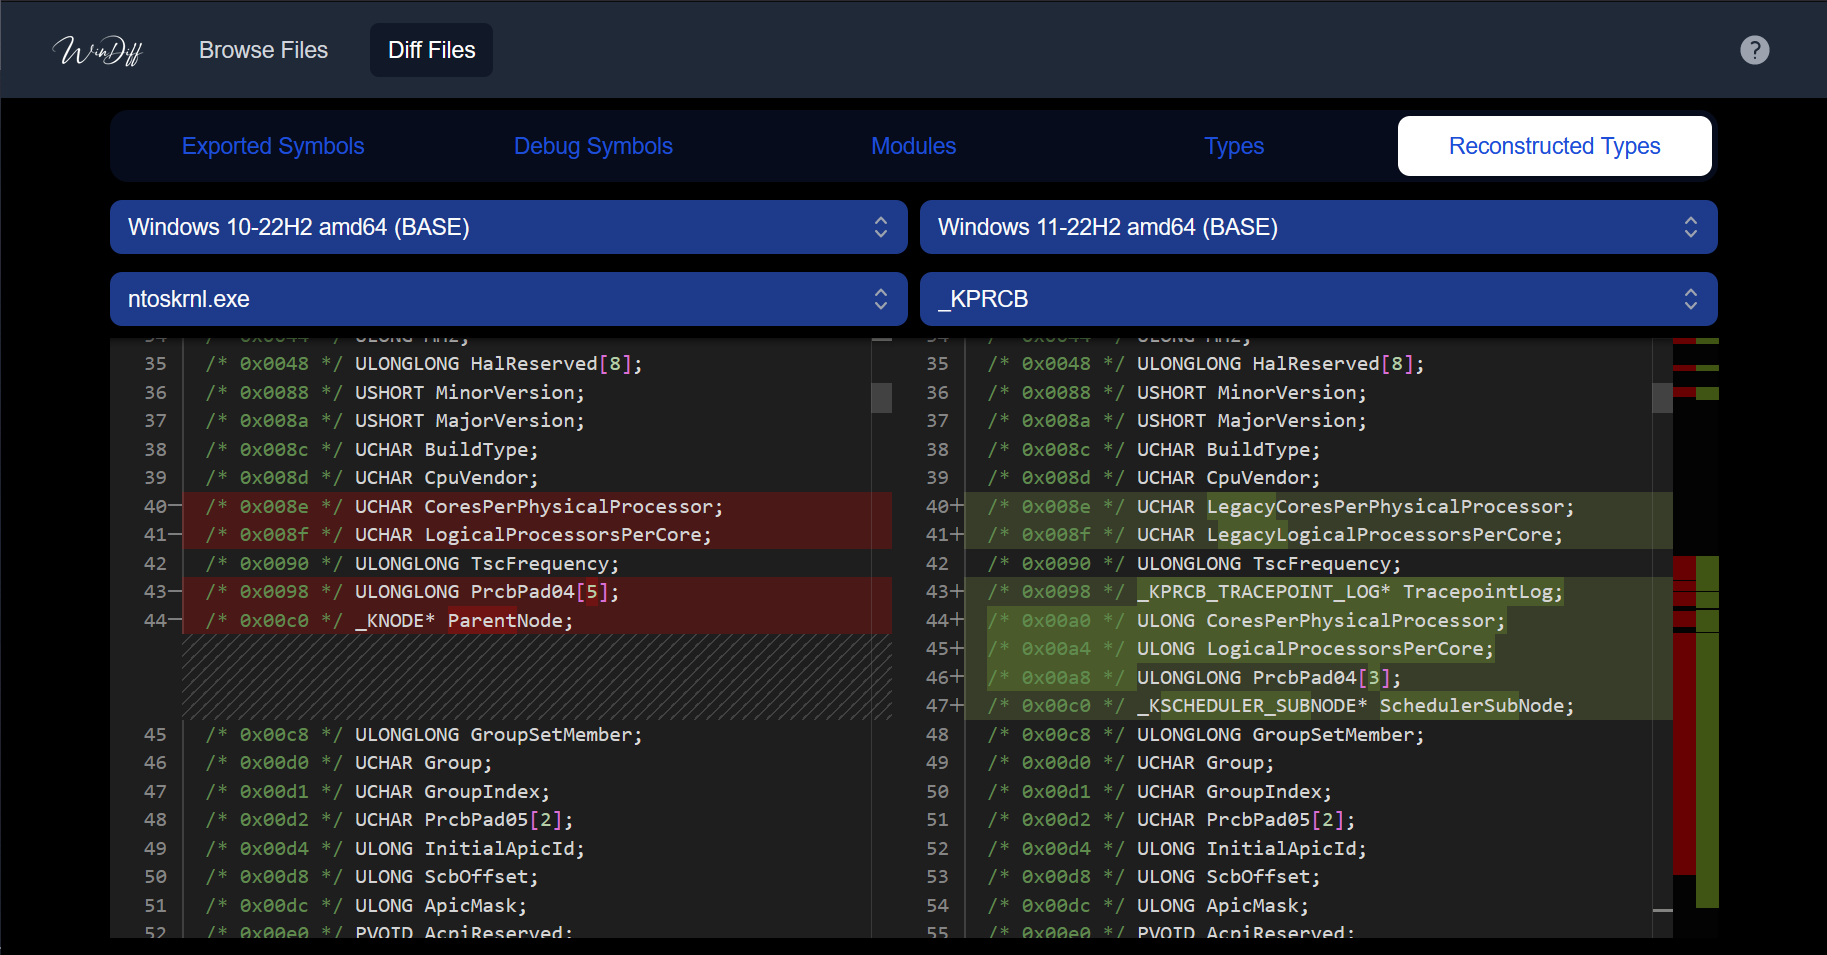 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 microsoft/procdump-for-linux
A Linux version of the ProcDump Sysinternals tool
 garrettfoster13/sccmhunter
Post-exploitation tool for identifying, profiling, and attacking Microsoft SCCM assets within Active Directory domains, streamlining credential…
 tesseract-ocr/tesseract
Open-source OCR engine with LSTM neural network models for extracting text from images and scanned documents in 100+ languages via CLI, C/C++…
 dobybaxter127/nimbus-vestige
A forensic reconstruction engine for cloud and identity incident response.
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 blacklanternsecurity/offensive-azure
Collection of offensive tools targeting Microsoft Azure
 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.