

syswarden
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
cloud-securityconfiguration-auditingdefensive-tools+4
duggytuxy/syswardenHost-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 q-feeds/nftables-iptables-integration-script
Script to implement Q-Feeds directly on NFtables or IPtables
 xe1phix/parrotlinux-public-kiosk-project
Systematic Linux kernel hardening project implementing KSPP-recommended settings, module blacklisting, and restricted environment configuration for…
 irsaattiquecyber/systemvulnerabilitychecklist_project4_decodelabs
System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…
 elihiho/security-operations-labs
Threat Modeling, IT-/OT-Segmentierung, Snort Detection und reproduzierbare Validierung eines Drupal-Detection-Profils.
 shenli/distributed-system-testing
AI-agent skills for distributed-systems testing
 caster-chen/cve-2026-8037-poc
包括能执行的命令探测和一键getshell(需要服务器部署服务)
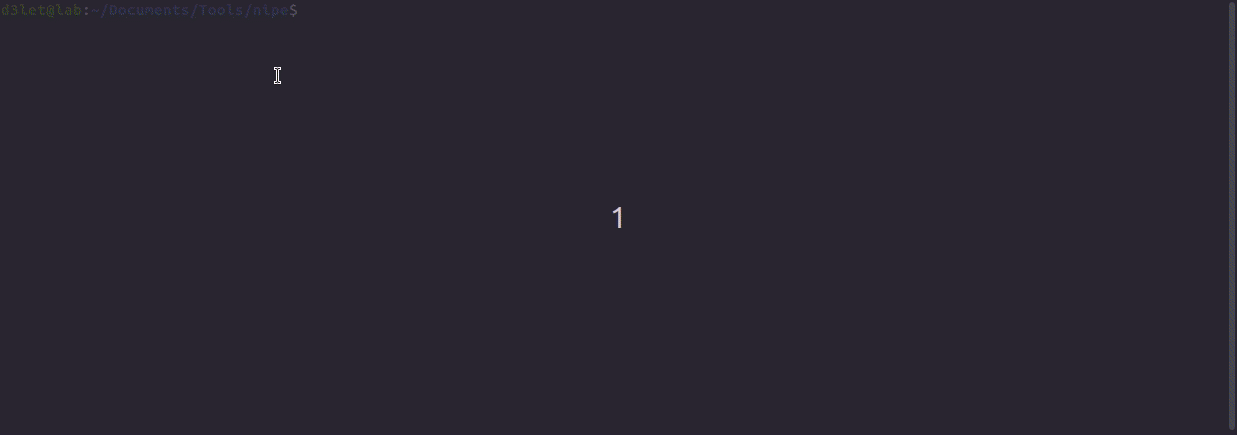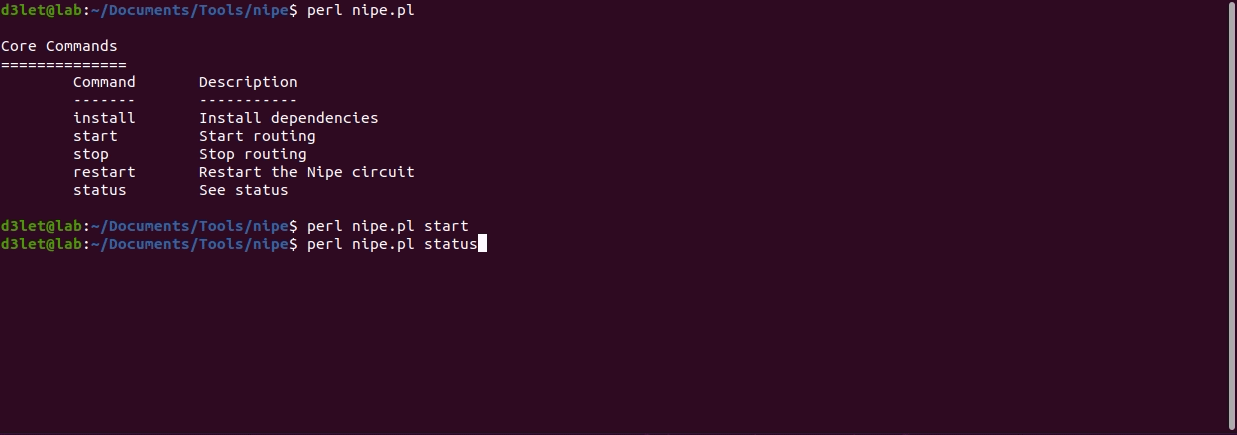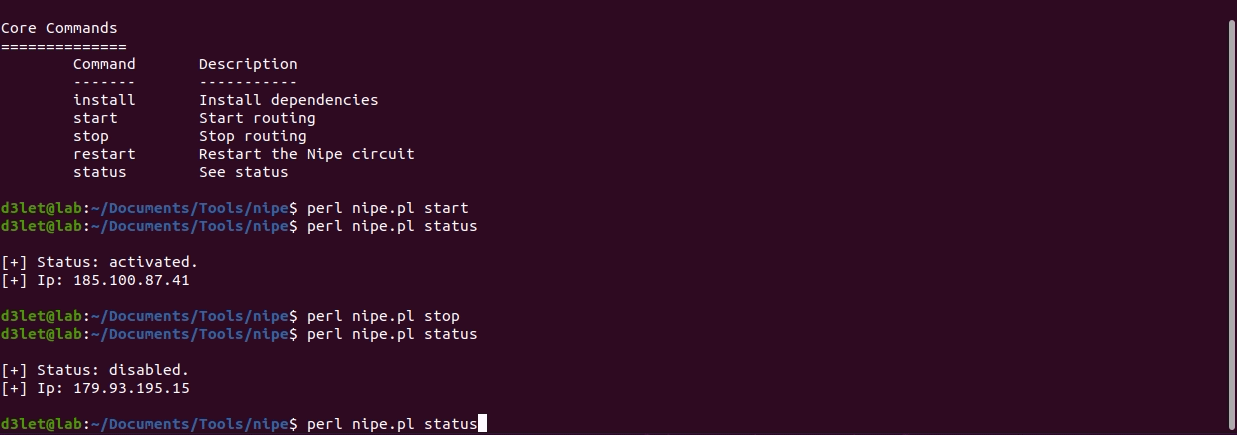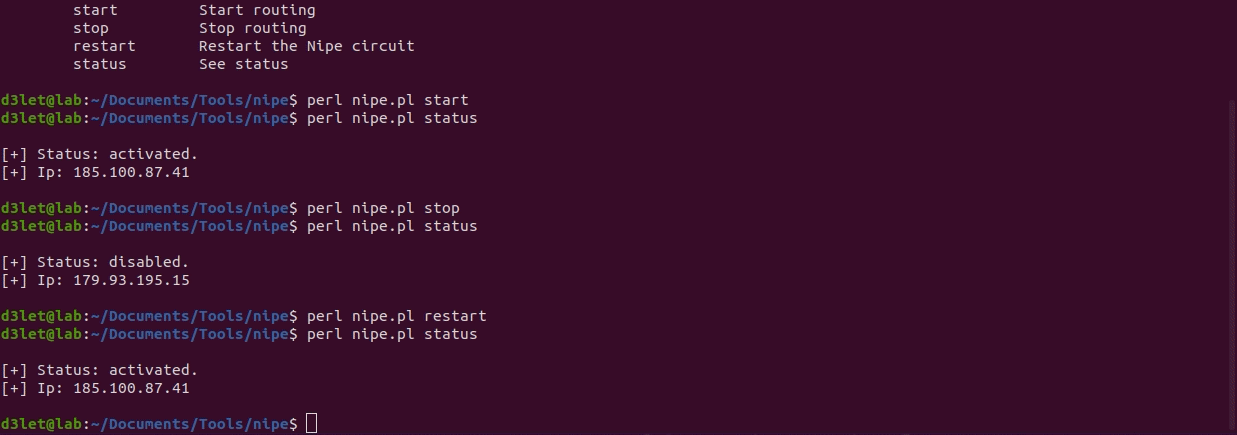
 riccardocataldi/access-point
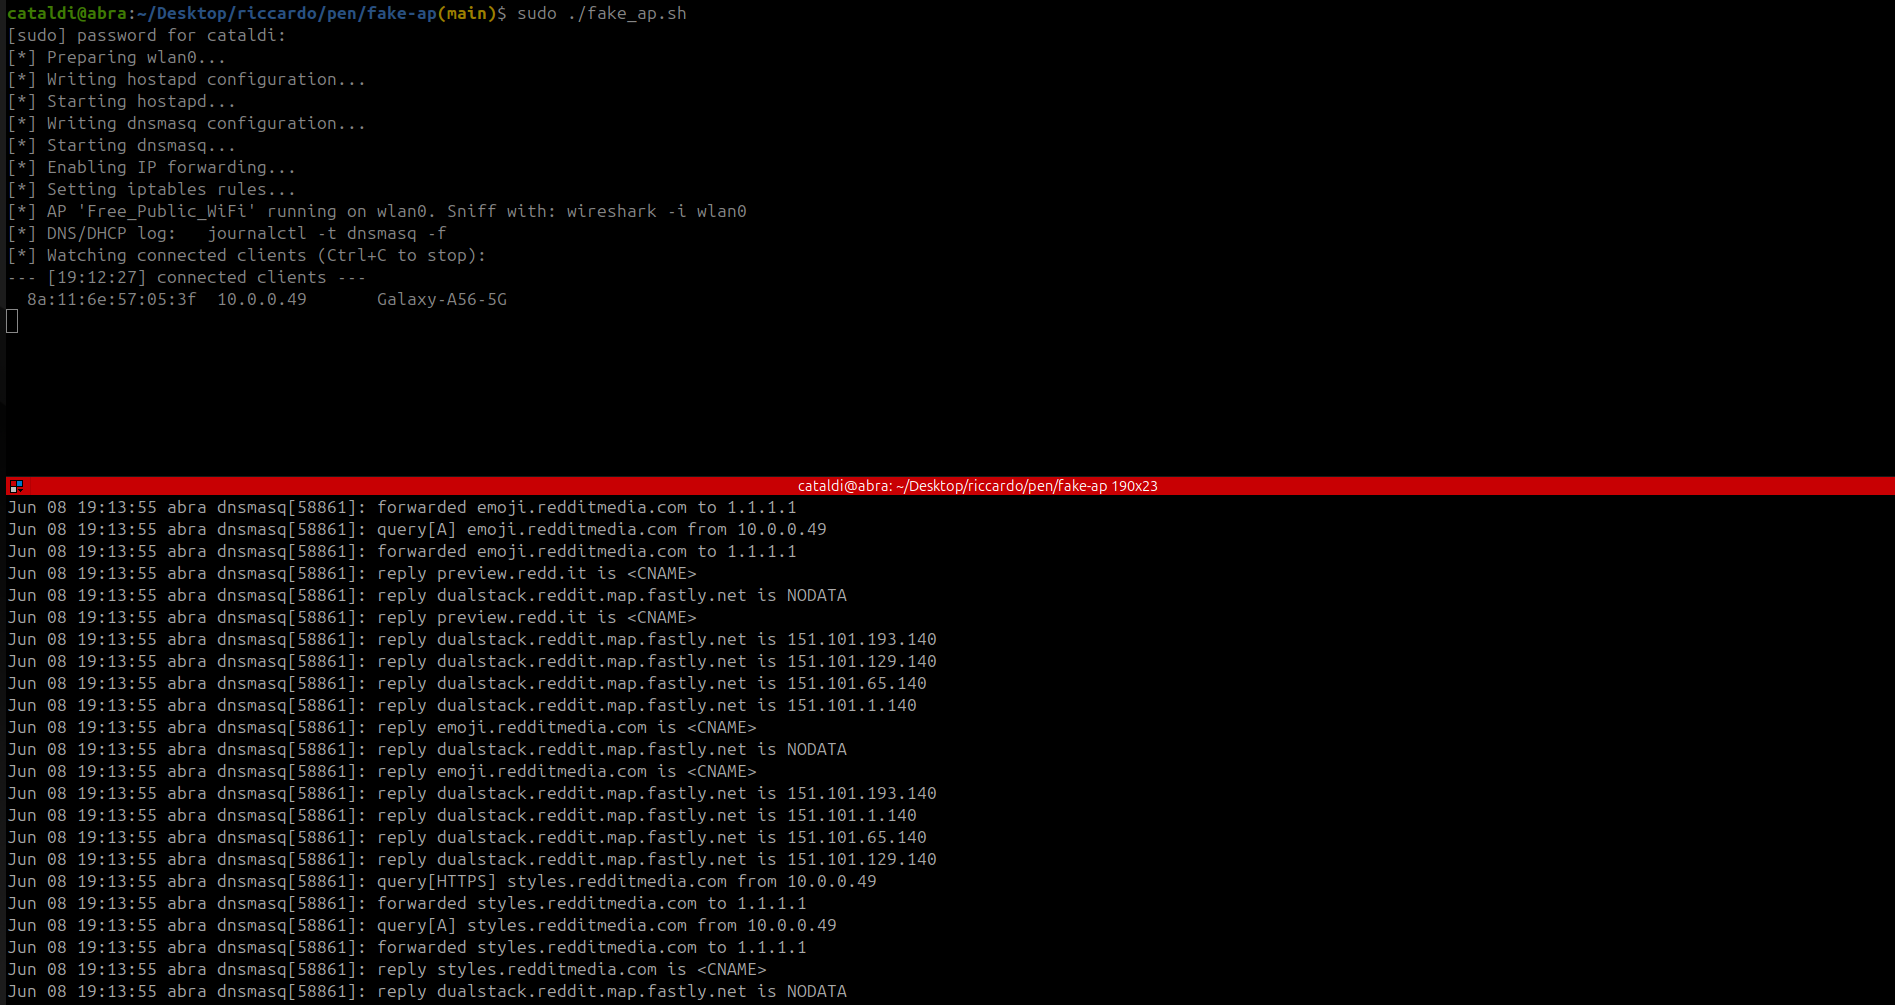
Rogue open Wi-Fi AP for controlled traffic capture using hostapd, dnsmasq, and iptables NAT. Enables real-time client monitoring, DNS/DHCP logging,…
 taisa456/network-security-snort
Snort 3 IDS → IPS lab on Kali. Custom detection rules + iptables enforcement against ICMP recon, Nmap SYN scans, Hydra FTP brute force, and vsftpd…
 halildeniz/privacynet
Routes all system traffic and DNS through Tor using iptables rules, with automatic IP rotation and geolocation display for enhanced anonymity.
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 firehol/firehol
iptables-based stateful firewall with human-friendly configuration and optional QoS (FireQOS) for bandwidth management.
 danindiana/cve-2026-32746-mitigation
Automated mitigation tool for CVE-2026-32746, providing atomic rollback, multi-firewall support (UFW, firewalld, nftables, iptables), and…
 sleuthco/clawshield-public
Security proxy for AI agents. Scans every message for prompt injection, PII, and secrets. Defense-in-depth: Go proxy + iptables firewall + eBPF…
 chundefined/torward
Forces all system traffic through the Tor network with IPv6 leak prevention, strict iptables rules, and DNS routing to enhance anonymity and prevent…
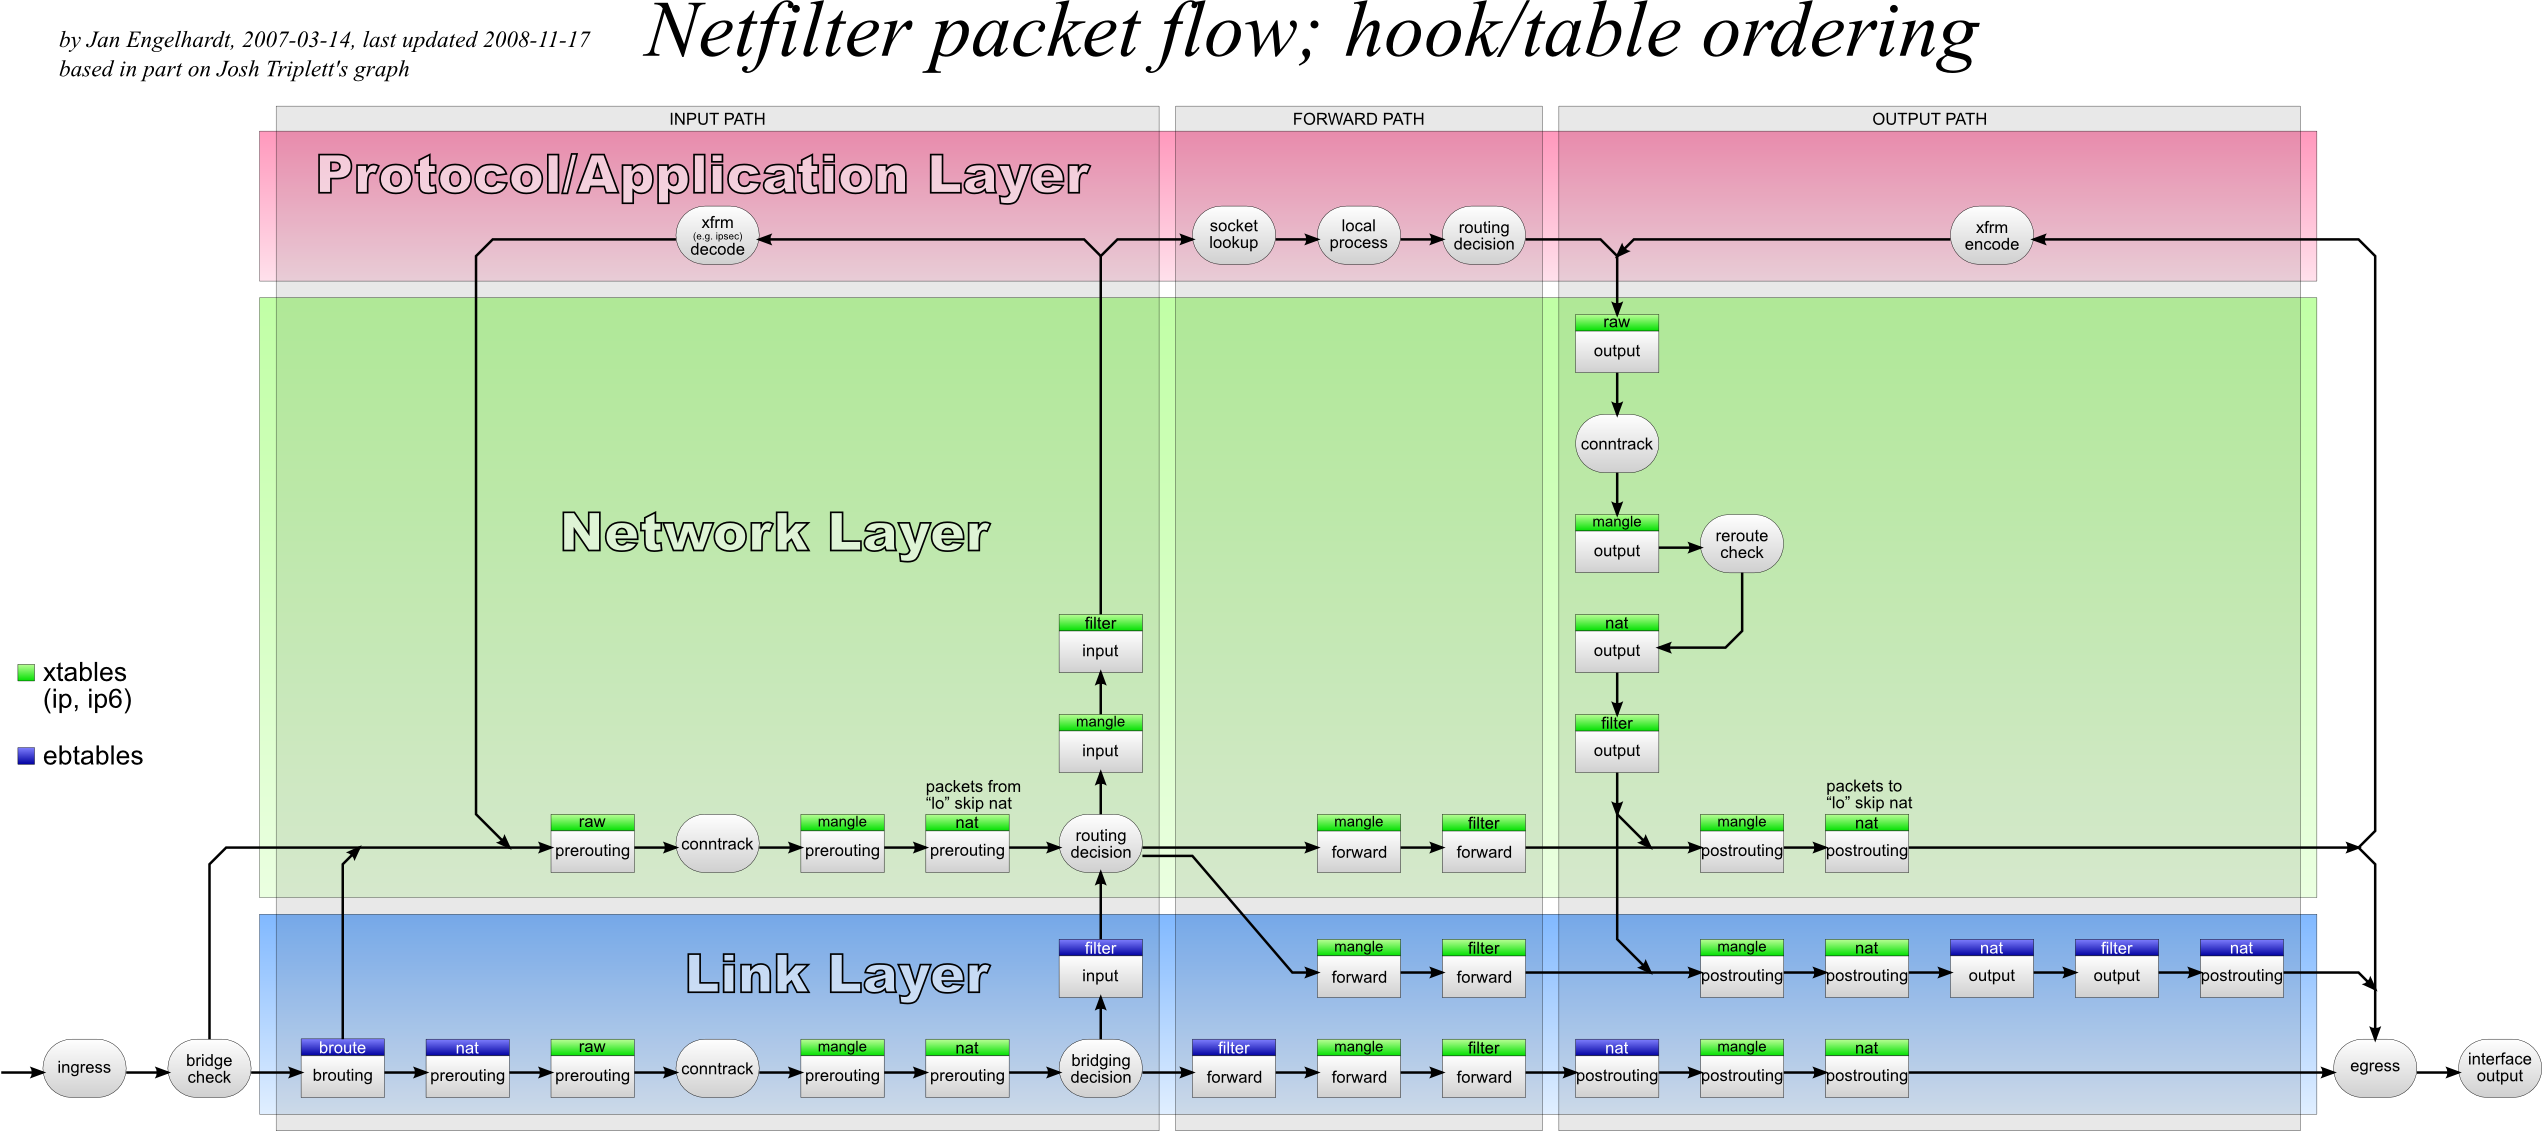 trimstray/iptables-essentials
Iptables Essentials: Common Firewall Rules and Commands.
 gmh5225/linux-iptables-firewall-ultrafirewall
Defensive Linux firewall toolkit combining IPTables rules and kernel configuration to protect hosts and servers against DoS, DDoS, and network…