
 htrgouvea/nipe
An engine to make Tor network your default gateway


An engine to make Tor Network your default gateway.


The Tor project allows users to surf the Internet, chat and send instant messages anonymously through its own mechanism. It is used by a wide variety of people, companies and organizations, both for lawful activities and for other illicit purposes. Tor has been largely used by intelligence agencies, hacking groups, criminal activities and even ordinary users who care about their privacy in the digital world.
Nipe is an engine, developed in Perl, that aims on making the Tor network your default network gateway. Nipe can route the traffic from your machine to the Internet through Tor network, so you can surf the Internet having a more formidable stance on privacy and anonymity in cyberspace.
Nipe supports both IPv4 and IPv6 traffic routing through the Tor network. Only traffic destined for local and/or loopback addresses is not routed through Tor. All non-local UDP/ICMP traffic is also blocked by the Tor project.
Nipe uses iptables and ip6tables to apply redirection rules for IPv4 and IPv6 traffic respectively. If you may have rules applied to these utilities, during the start process, conflicts may occur. When you stop running the Nipe services, all departure rules are removed, not differentiating between the already existing ones and the Nipe rules.
  # Download
  $ git clone https://github.com/htrgouvea/nipe && cd nipe

  # Install libs and dependencies
  $ cpanm --installdeps .

  # Nipe must be run as root
  $ perl nipe.pl install
  COMMAND          FUNCTION
  install          Install dependencies
  start            Start routing
  stop             Stop routing
  restart          Restart the Nipe circuit
  status           See status

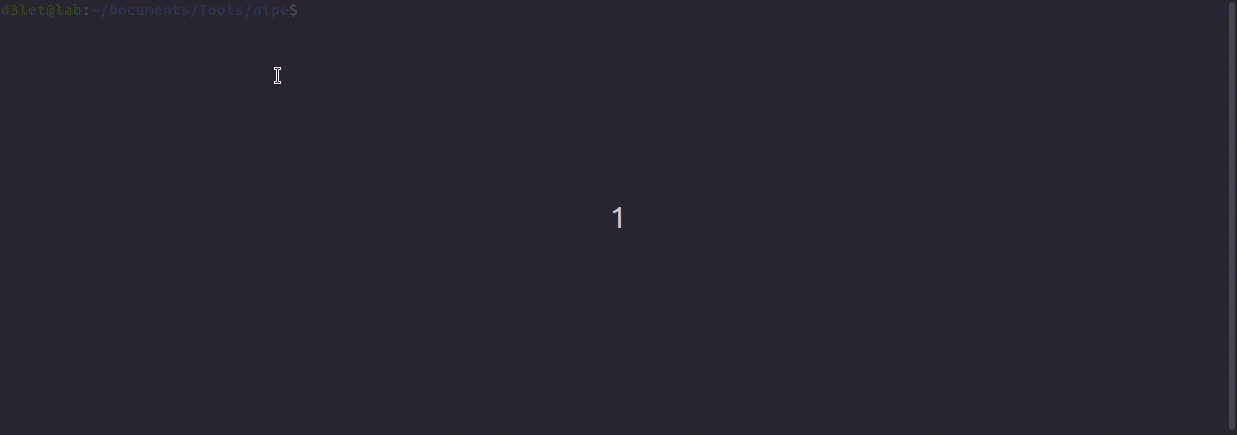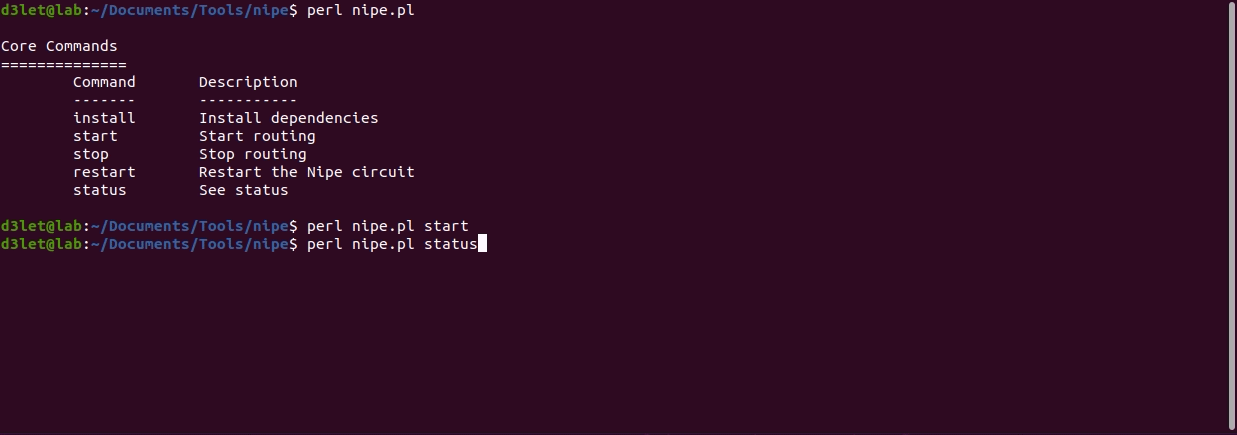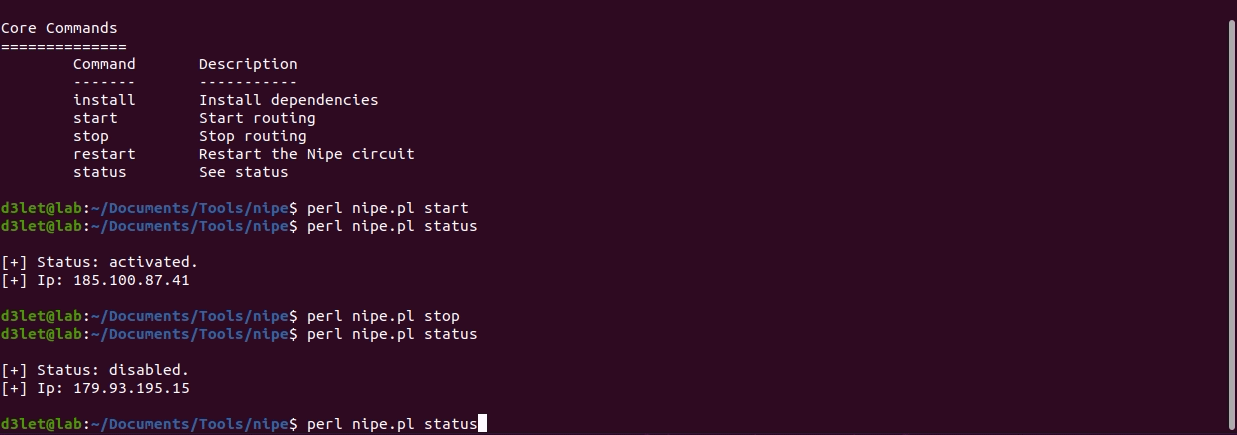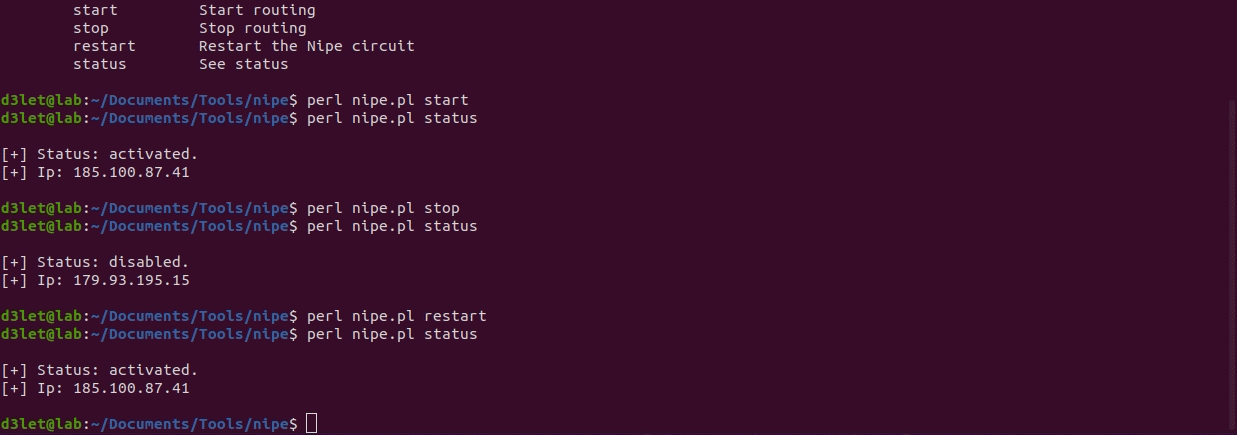
  Examples:

  perl nipe.pl install
  perl nipe.pl start
  perl nipe.pl stop
  perl nipe.pl restart
  perl nipe.pl status
# Building the container
$ docker build -t nipe .

# Setup the Nipe container
$ docker run -d -it --name nipe-container --privileged --cap-add=NET_ADMIN nipe

# Running commands
$ docker exec -it nipe-container ./nipe.pl <your command>
Your contributions and suggestions are heartily ♥ welcome. See here the contribution guidelines. Please, report bugs via issues page and for security issues, see here the security policy. (✿ ◕‿◕)
This work is licensed under MIT License.






