
B2R2
 b2r2-org/b2r2
B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
binary-analysisdynamic-analysis-sandboxingeducation+4
459
b2r2-org/b2r2B2R2 is a fully managed binary analysis framework written in F#. It provides a rich set of algorithms, functions, and tools for reverse engineering,…
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 ainfosec/fissure
The RF and reverse engineering framework for everyone. Follow and ★ to show your support!
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 sia-iotechnology/kittysploit-framework
Python Exploitation Framework, V8 Engine Debugger, Proxy interceptor, marketplace, post-exploitation, backdoor generator,....
 ssc-ict-innovatie/nl-kat-coordination
Modular network scanning framework that integrates diverse tools and external databases to detect vulnerabilities and configuration errors, producing…
 416rehman/deepzero
Find zero-days while you sleep. DeepZero is an automated vulnerability research framework that parses, decompiles, and analyzes thousands of Windows…
 pennyw0rth/netexec
Post-exploitation framework for automated network authentication testing, credential harvesting, and lateral movement across Windows/AD environments…
 projectdiscovery/katana
A next-generation crawling and spidering framework.
 samugit83/redamon
Autonomous AI red team framework that chains reconnaissance, exploitation, and post-exploitation into a single pipeline, then triages findings,…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 berylliumsec/nebula
AI-powered penetration testing assistant that automates reconnaissance, vulnerability analysis, and note-taking via integrated LLMs and CLI tool…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
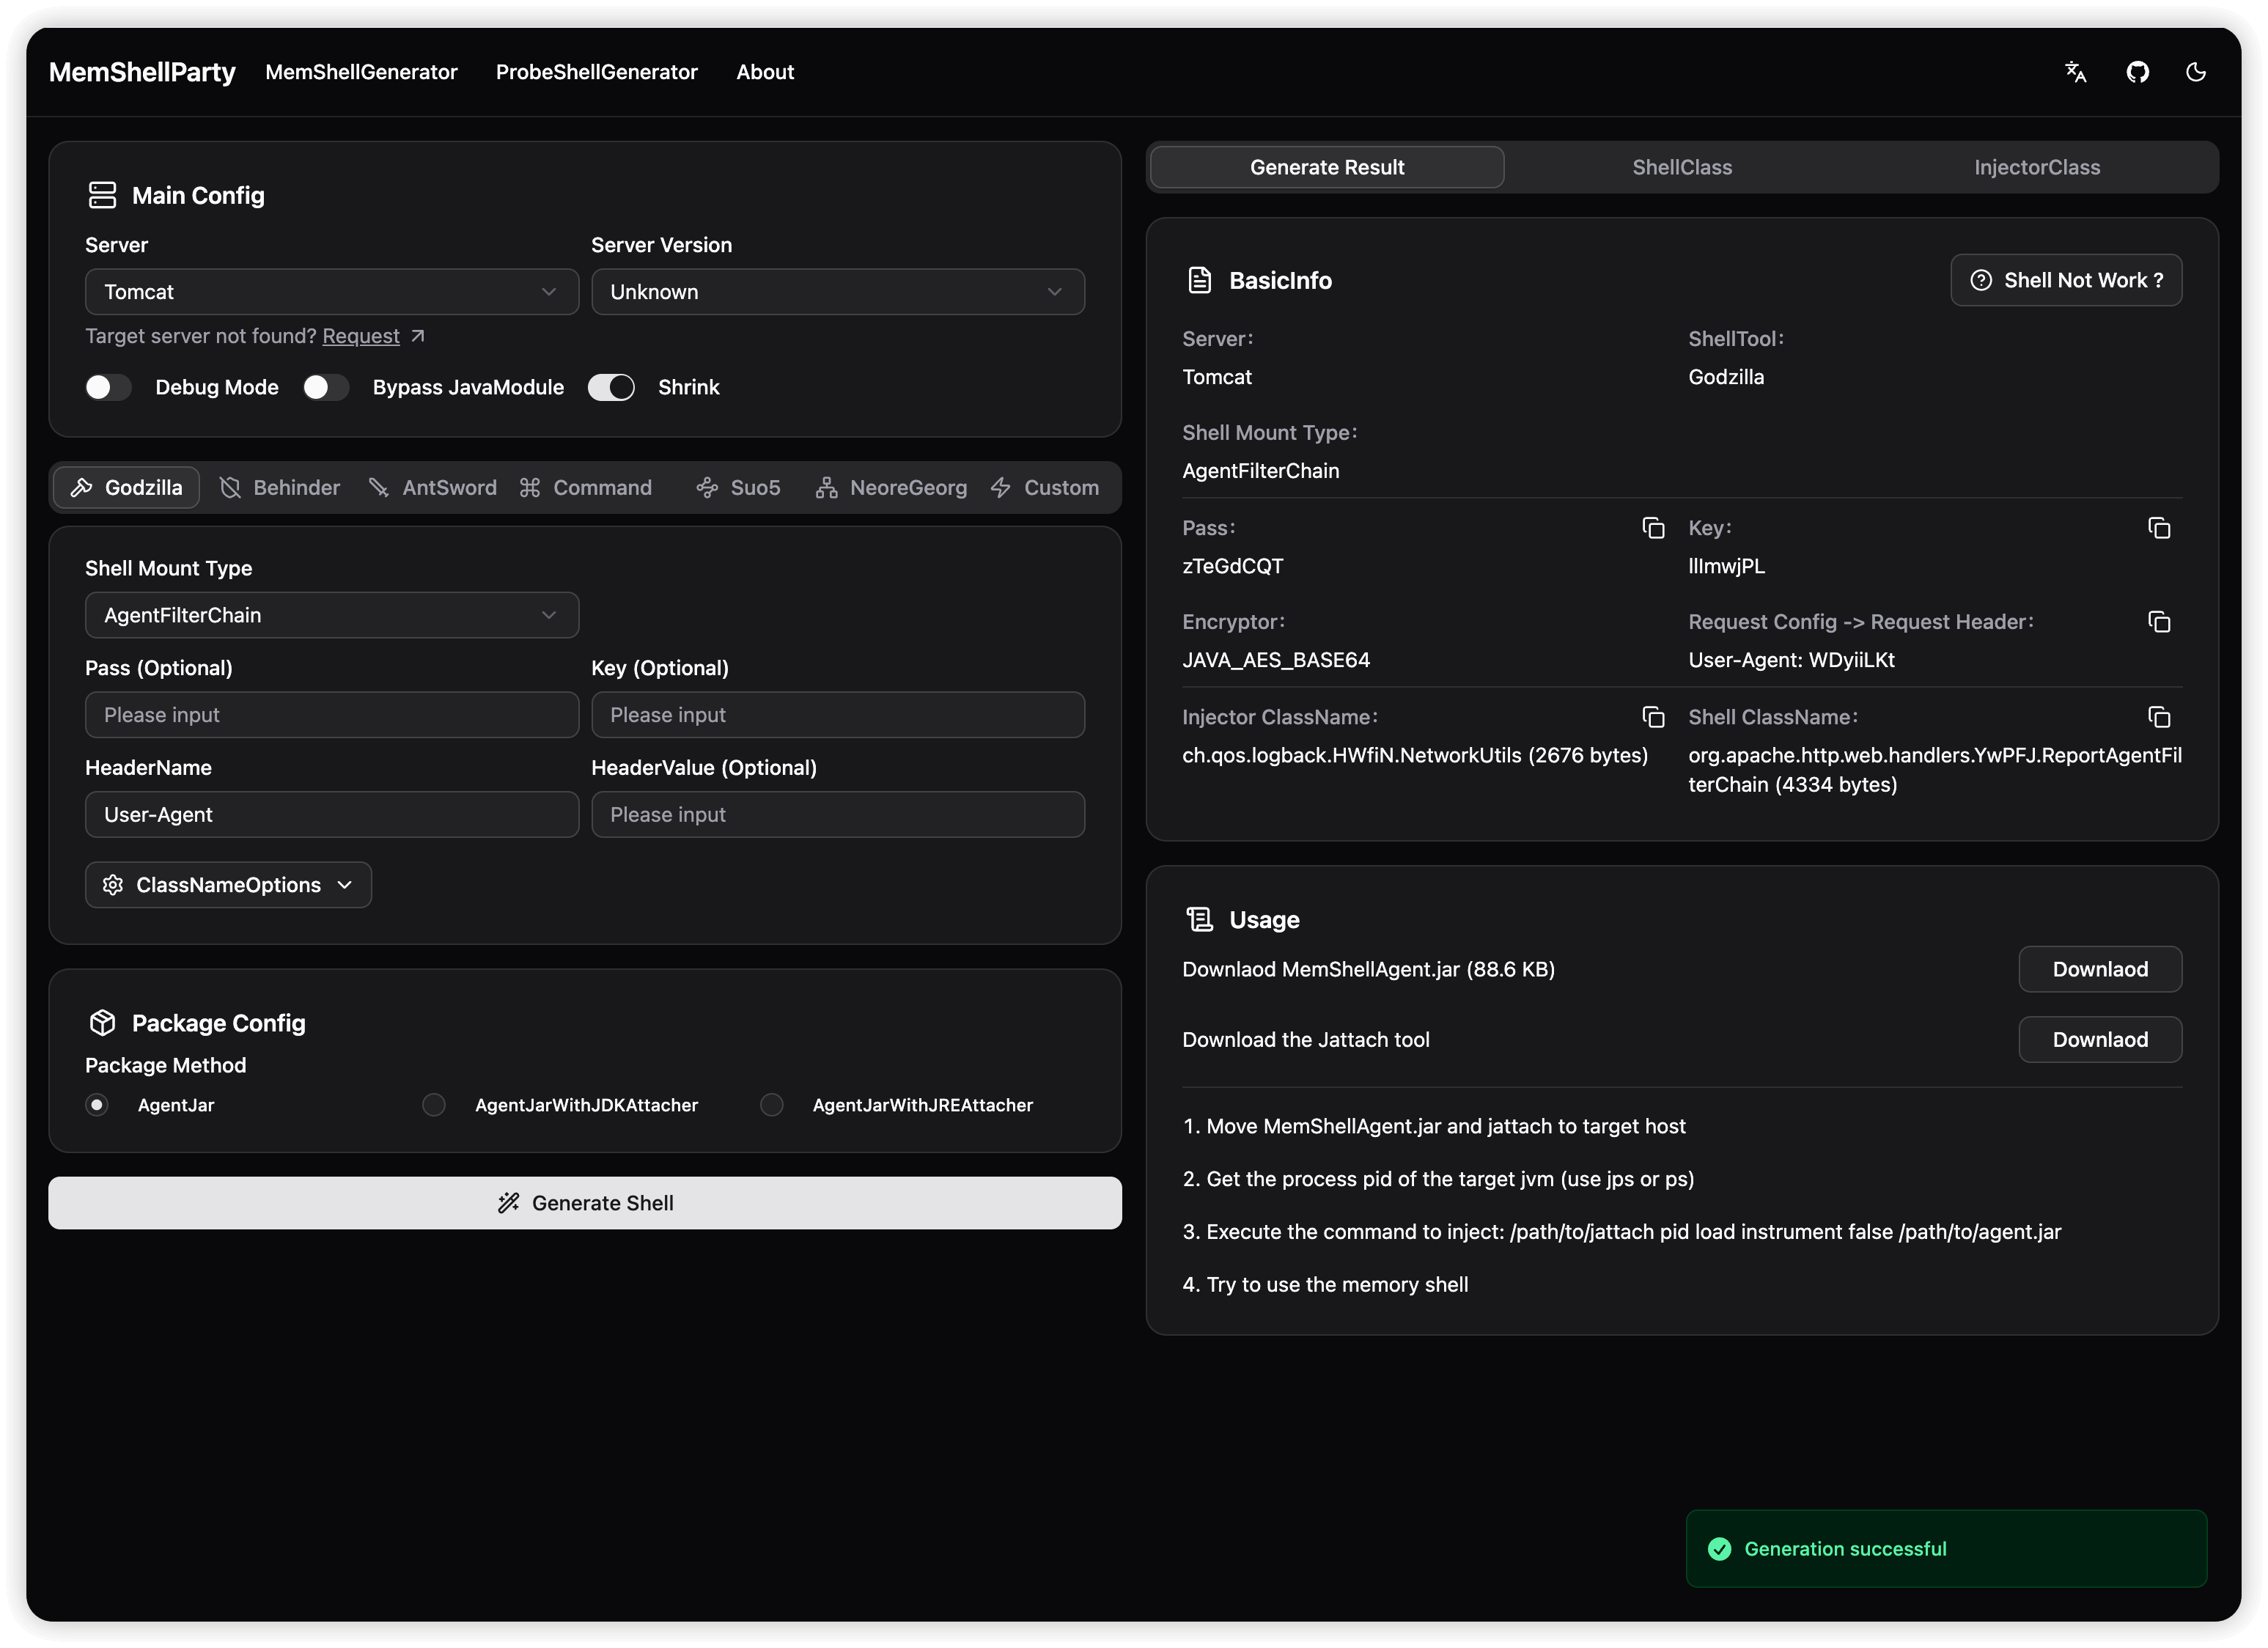 reajason/memshellparty
一款专注于 Java 主流 Web 中间件的内存马快速生成工具,致力于简化安全研究人员和红队成员的工作流程,提升攻防效率
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 vulncheck-oss/go-exploit
Go-based exploit development framework with built-in phases for target verification, version scanning, exploitation, and C2. Supports multiple…
 jm33-m0/emp3r0r
Linux post-exploitation C2 framework with gossip mesh networking, memory-only operations, modular payloads, and OPSEC-focused transport for red team…
 abdirisaq-ali-aynab/vulnerability-assessment
Professional cybersecurity assessment demonstrating vulnerability identification, CVSS severity scoring, MITRE ATT&CK framework application, and…