
Log4J-Scanner
 0xdexter0us/log4j-scanner
Burp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
exploitationpenetration-testingvulnerability-scanners+3
101
0xdexter0us/log4j-scannerBurp extension to scan Log4Shell (CVE-2021-44228) vulnerability pre and post auth.
 dxc-strikeforce/burp-log4j-hammertime
Burp Active Scan extension to identify Log4j vulnerabilities CVE-2021-44228 and CVE-2021-45046
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
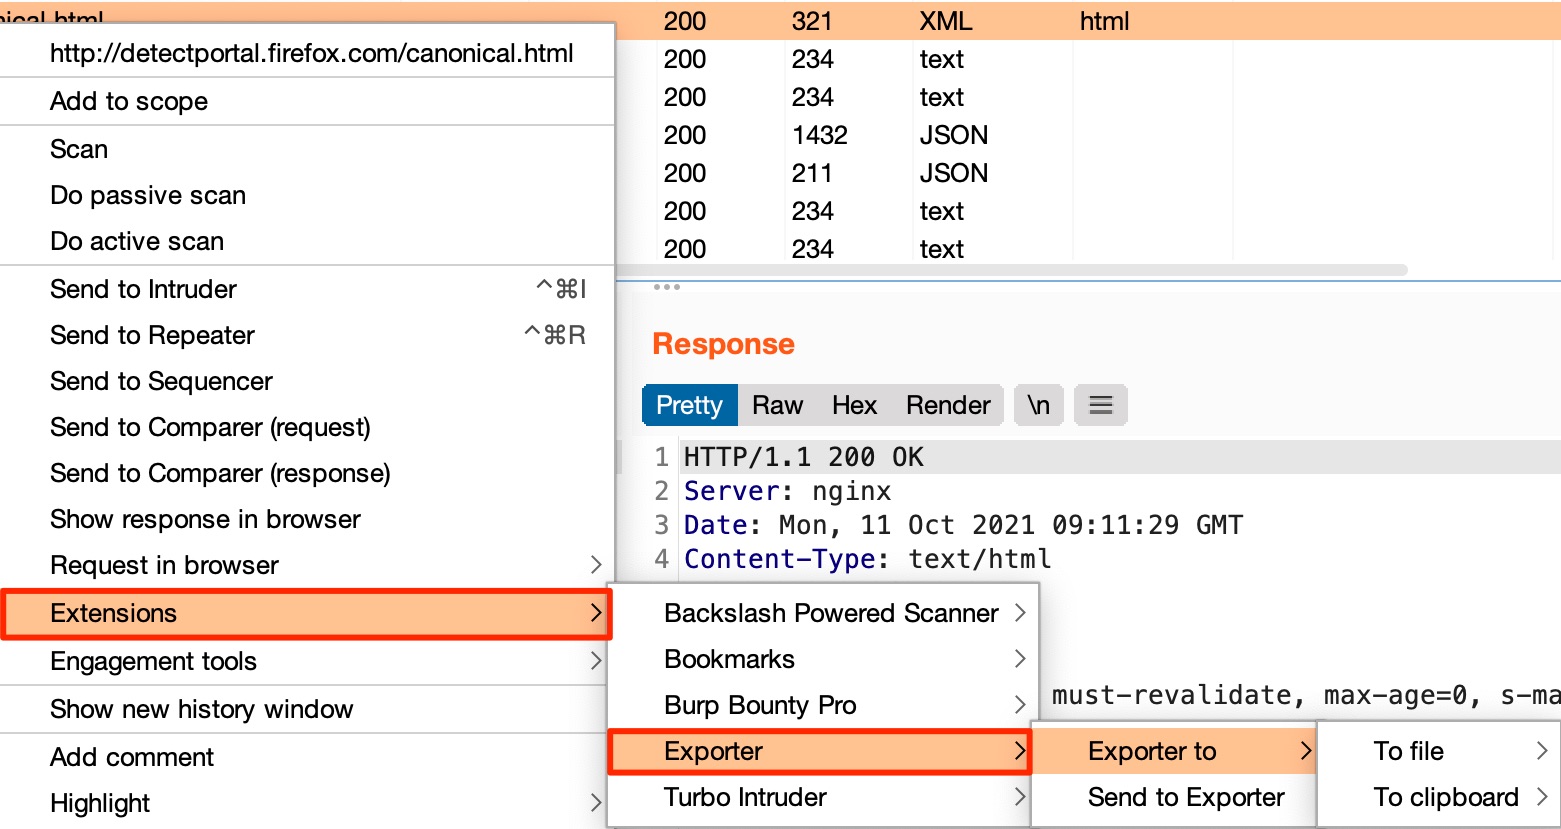 artssec/burp-exporter
Exporter is a Burp Suite extension to copy a request to a file or the clipboard as multiple programming languages functions.
 nccgroup/pcap-burp
Pcap importer for Burp
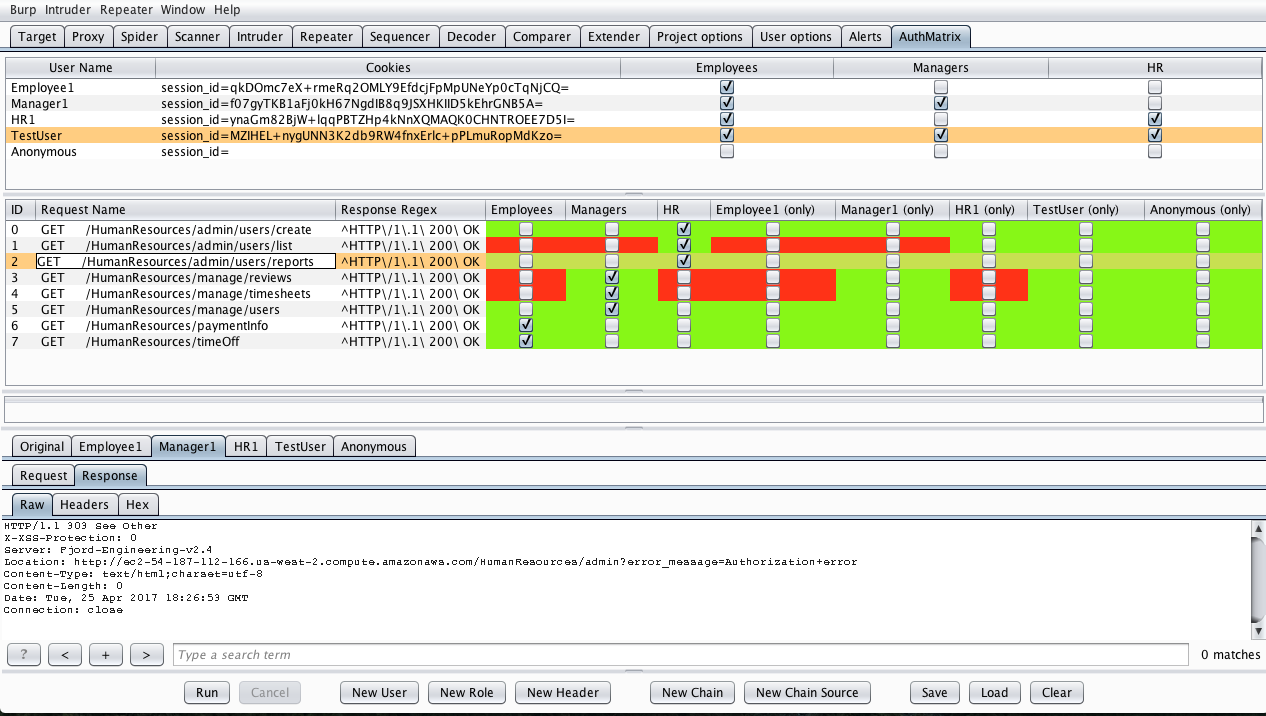 securityinnovation/authmatrix
AuthMatrix is a Burp Suite extension that provides a simple way to test authorization in web applications and web services.
 jackadamson/cve-2021-26700
Proof-of-concept for CVE-2021-26700: remote code execution in the VSCode npm-script extension via malicious workspace settings.json, with detailed…
 vulnbe/burpsuite-copy-as-xmlhttprequest
BurpSuite extension that converts HTTP requests into JavaScript XMLHttpRequest code for streamlined XSS proof-of-concept generation and web…
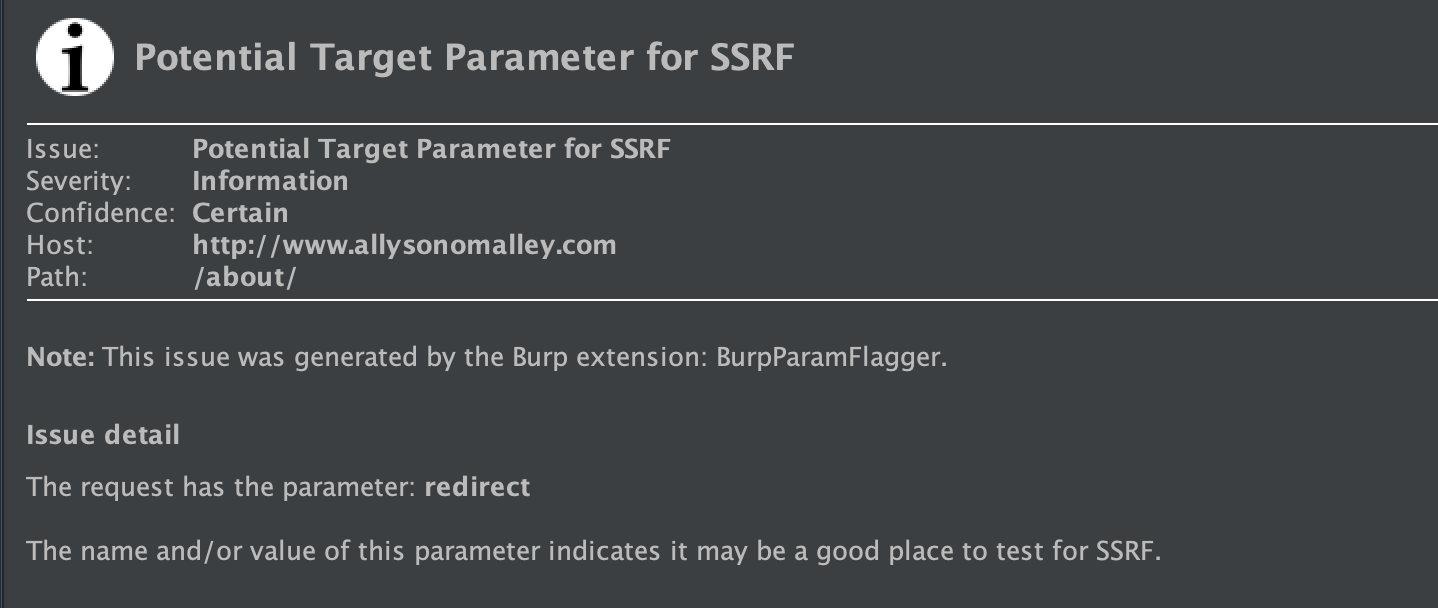 allyomalley/burpparamflagger
A Burp extension adding a passive scan check to flag parameters whose name or value may indicate a possible insertion point for SSRF or LFI.
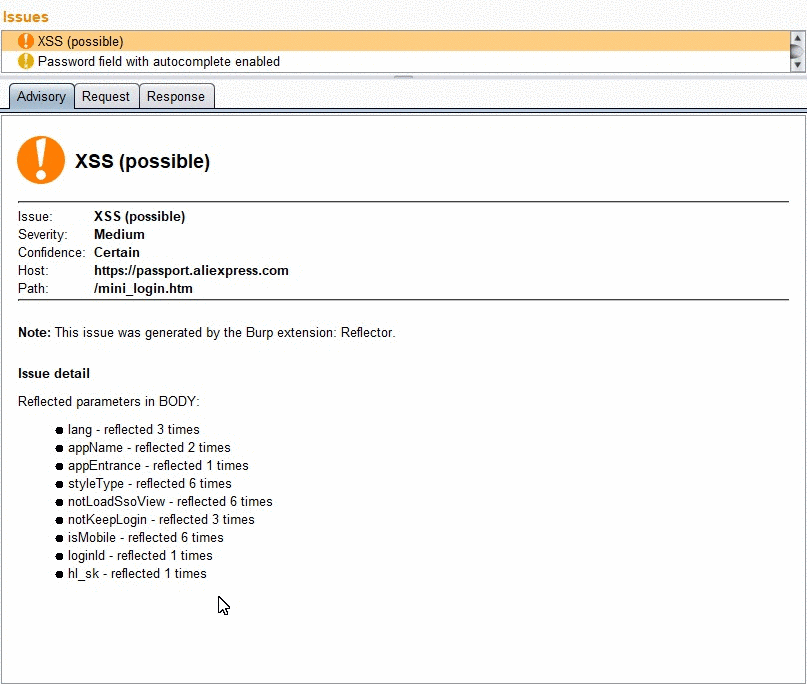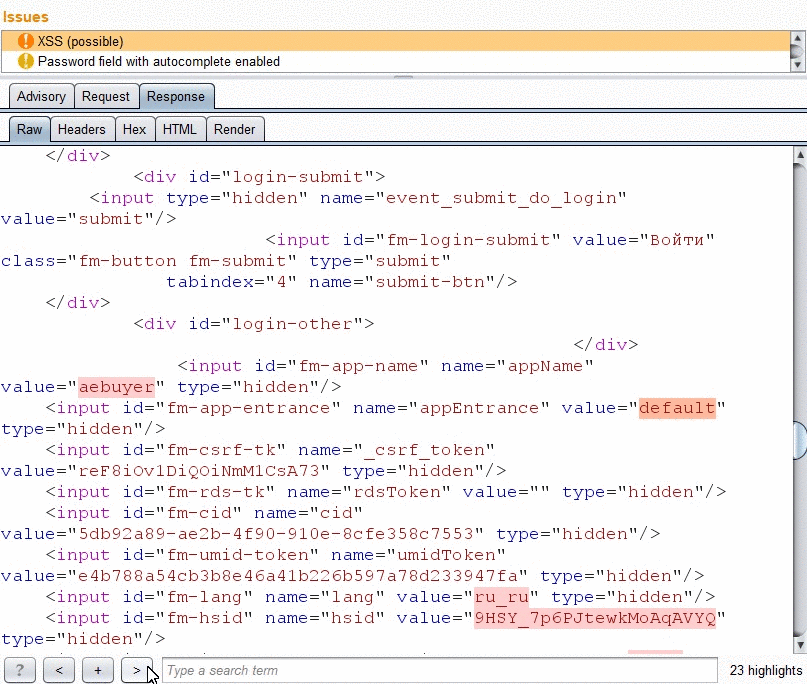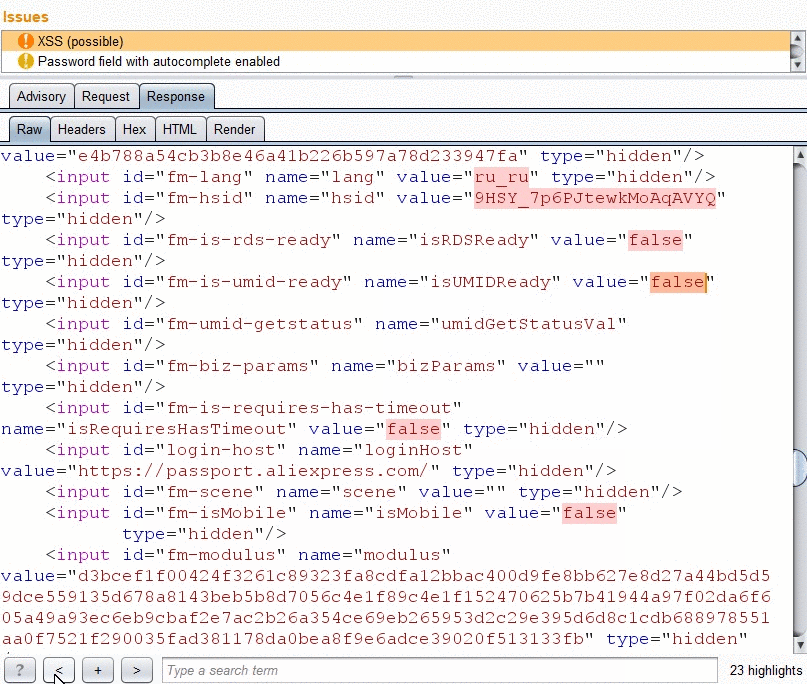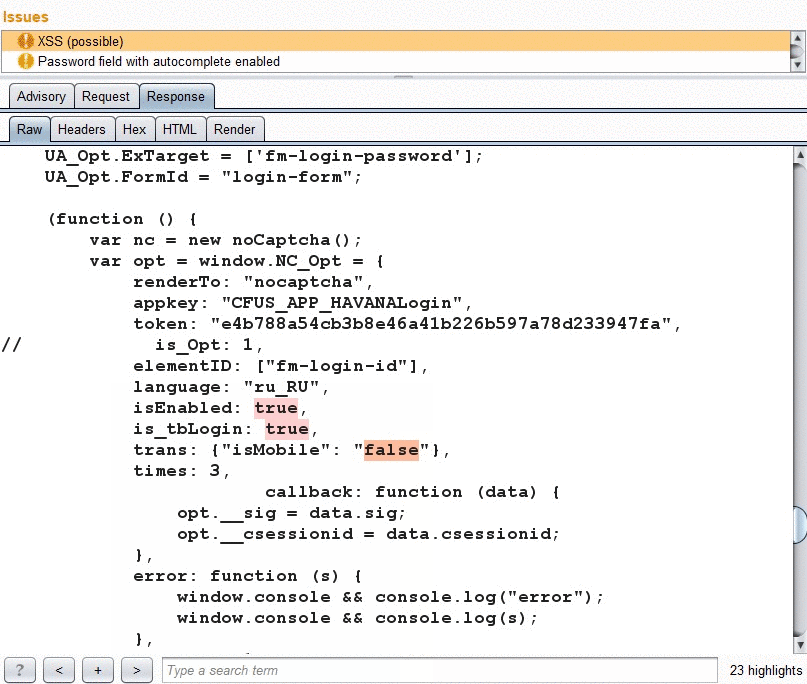 elkokc/reflector
Burp plugin able to find reflected XSS on page in real-time while browsing on site
 josue87/burpmetafinder
Burp Suite extension for extracting metadata from files
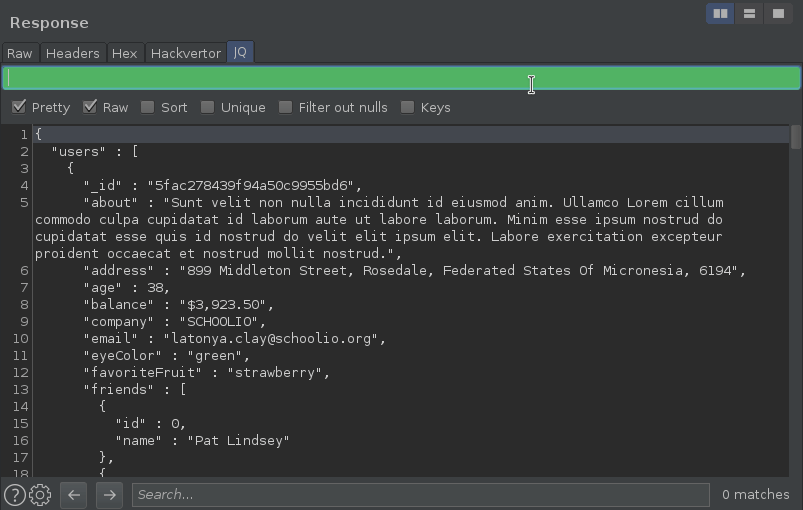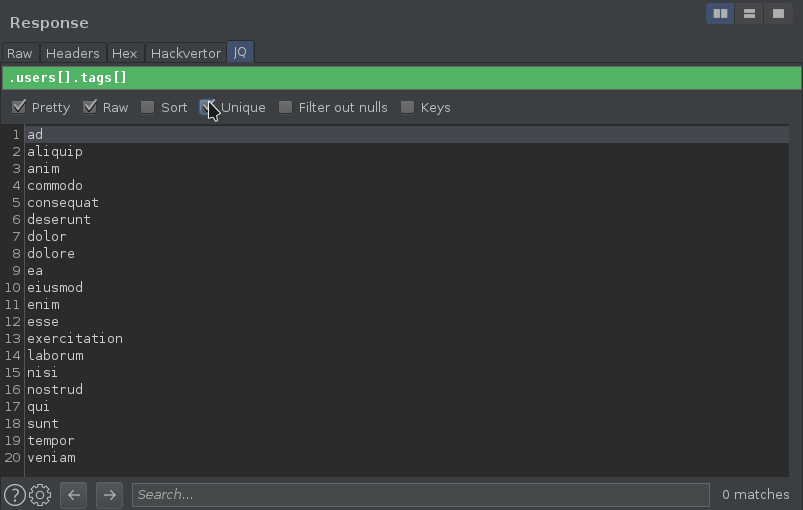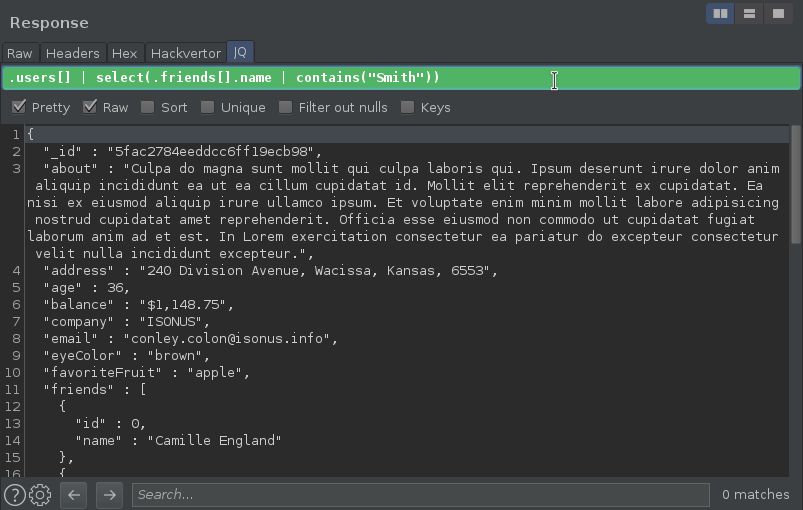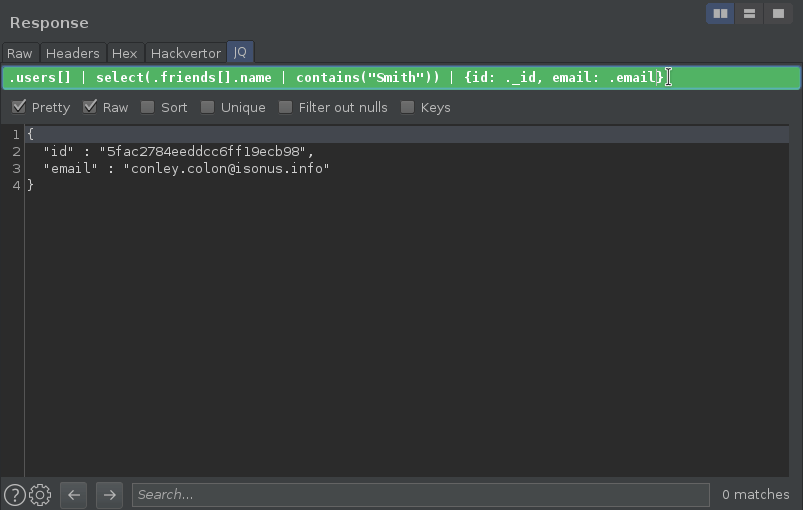 synacktiv/burp-jq
Burp extension to filter JSON on the fly with JQ queries in the HTTP message viewer.
 seqred-s-a/cve-2020-29007
Remote code execution in Mediawiki Score
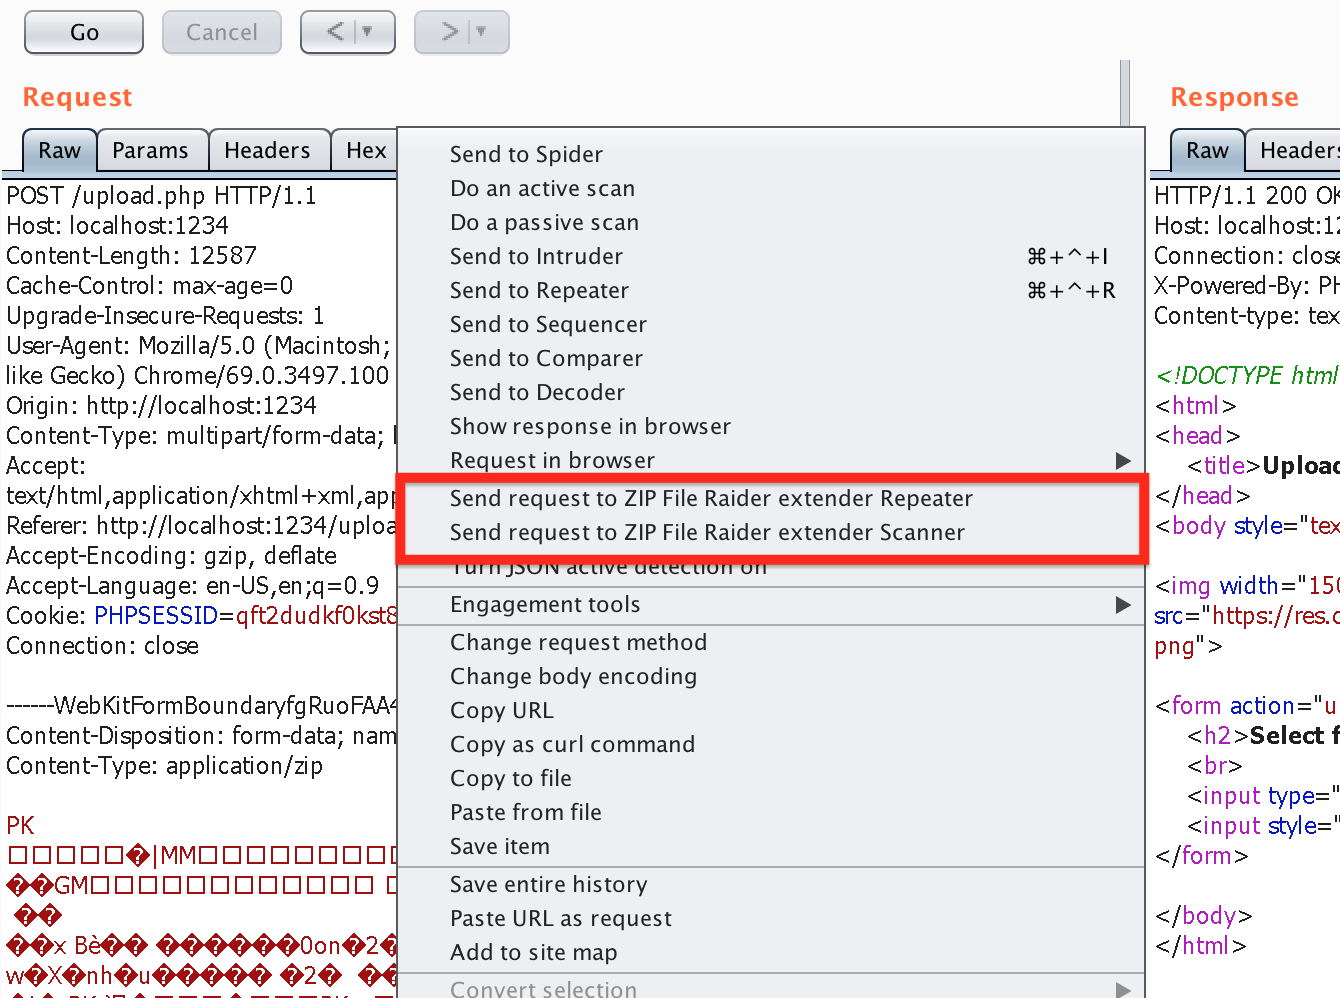 destine21/zipfileraider
ZIP File Raider - Burp Extension for ZIP File Payload Testing
 ztgrace/mole
Framework for identifying and exploiting out-of-band (OOB) application vulnerabilities with a custom DNS/token server, Burp Suite extension, and…
 hemp3l/cve-2017-6640-poc
Proof of concept for CVE-2017-6640 as burp extension
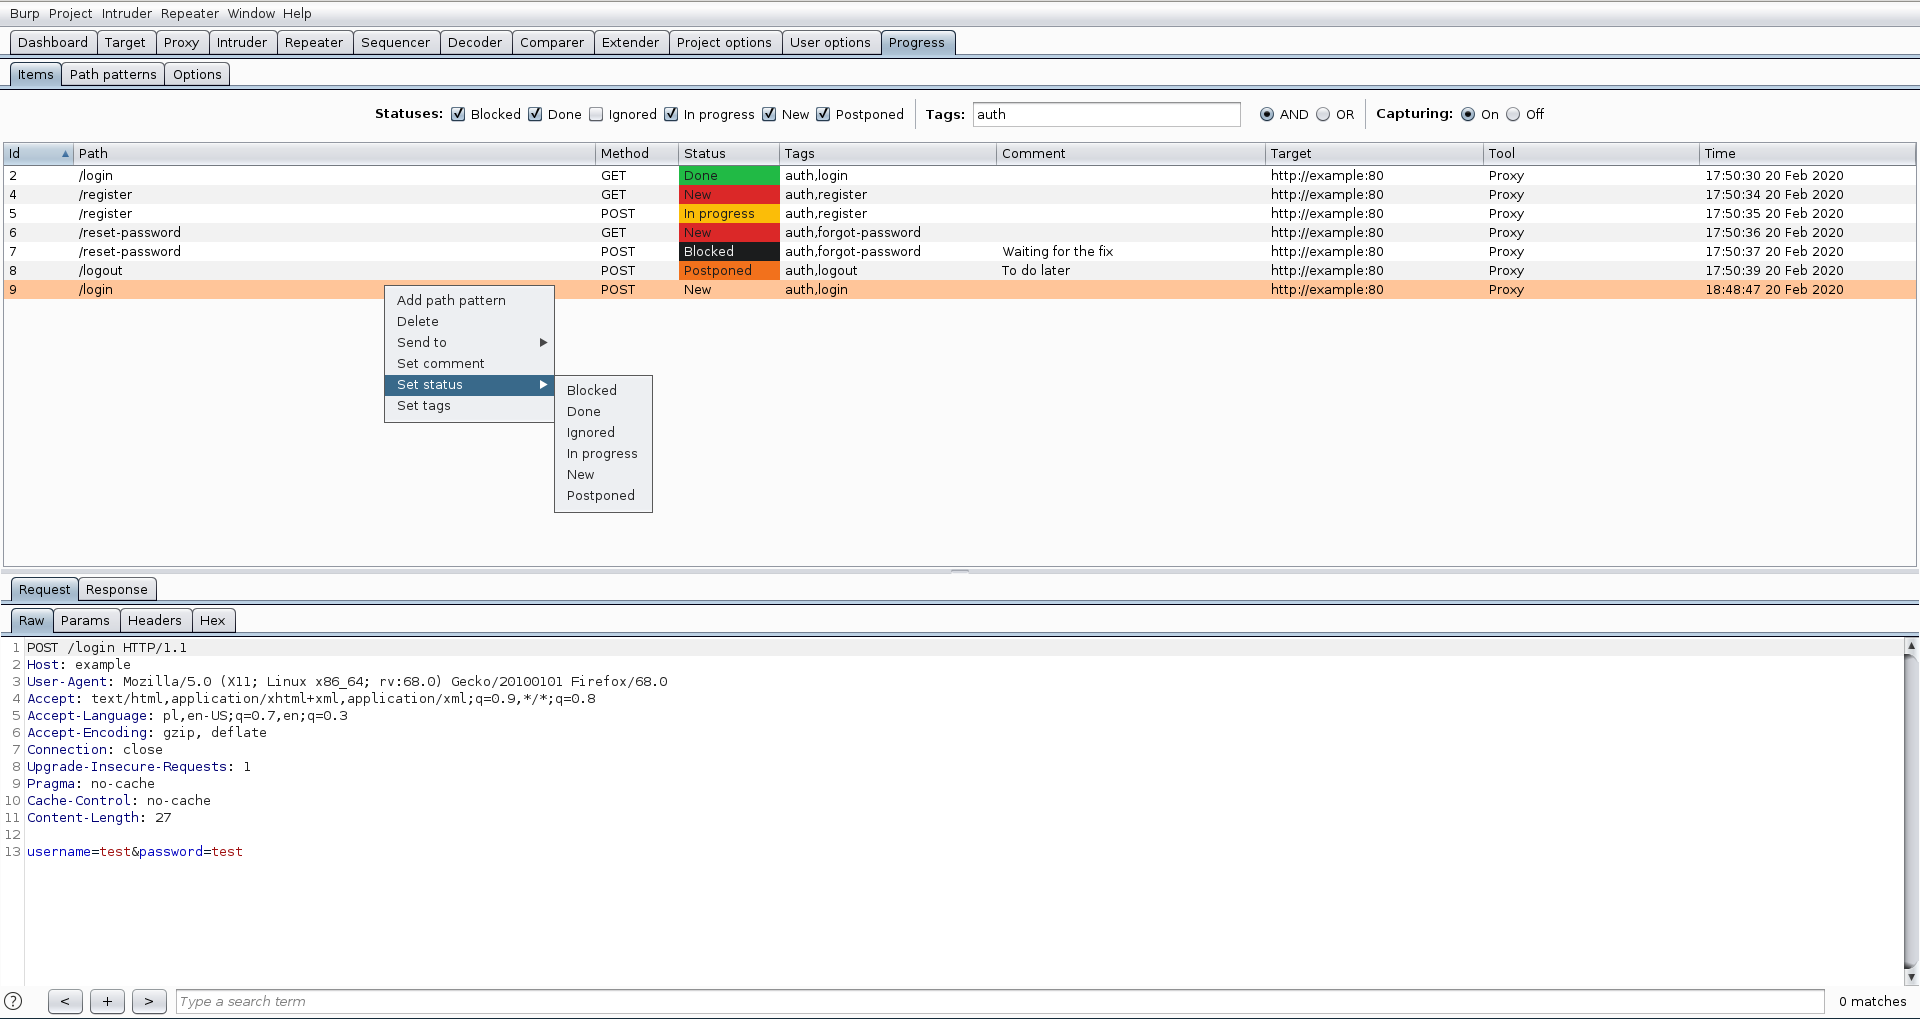 dariusztytko/progress-burp
Burp Suite extension to track vulnerability assessment progress
 afbase/cve-2017-10952
Demonstrates a local code execution exploit for Foxit PDF Reader via XFA-based PDFs, with step-by-step attack reproduction and extension to related…