

openmeetings-backup-config-path
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
misconfigurationpapers-researchpenetration-testing+2
abraxas/openmeetings-backup-config-pathApache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 industri4l-h3ll-xpl0it3rs/cve-2026-33017-langflow-rce
CVE-2026-33017 Exploit | by infrar3d
 0xdea/haruspex
Vulnerability research assistant that extracts pseudocode from the IDA Hex-Rays decompiler.
 7ragnarok7/cve-2024-37888
XSS PoC/Exploit for Open Link Plugin for CKEditor 4
 7ragnarok7/cve-2021-3754
Vulnerability details and exploit for CVE-2021-3754
 zerodayevil/cve-2026-20817
Repository dedicated to CVE-2026-20817, providing vulnerability details and exploitation material for this specific security flaw.
 zerodayevil/cve-2026-40369-exploit
Proof-of-concept exploit code targeting CVE-2026-40369, demonstrating the vulnerability for research and authorized security testing.
 zerodayevil/cve-2026-41651
Repository dedicated to CVE-2026-41651, containing vulnerability-specific information and analysis for this single security issue.
 fankh/vulnerability-poc
CVE proof-of-concept labs, exploit scripts, and detection/prevention rules (Nginx, Apache, Snort, YARA) for high-severity CVEs. Authorized security…
 oscerd/cve-2026-79986
Reproducer and analysis for CVE-2026-79986, a path traversal in Apache Camel camel-azure-files where share listing names escape the polled directory.
 oscerd/cve-2026-79985
Reproducer and analysis for CVE-2026-79985, a path traversal in Apache Camel camel-smb where share-listing names bypass directory containment, with…
 doretox/atomicvulns
Atomic web vulnerability labs. One OWASP flaw per app — minimal Flask + Docker, intentionally broken for hands-on study with Burp Suite.
 trickest/cve
Gather and update all available and newest CVEs with their PoC.
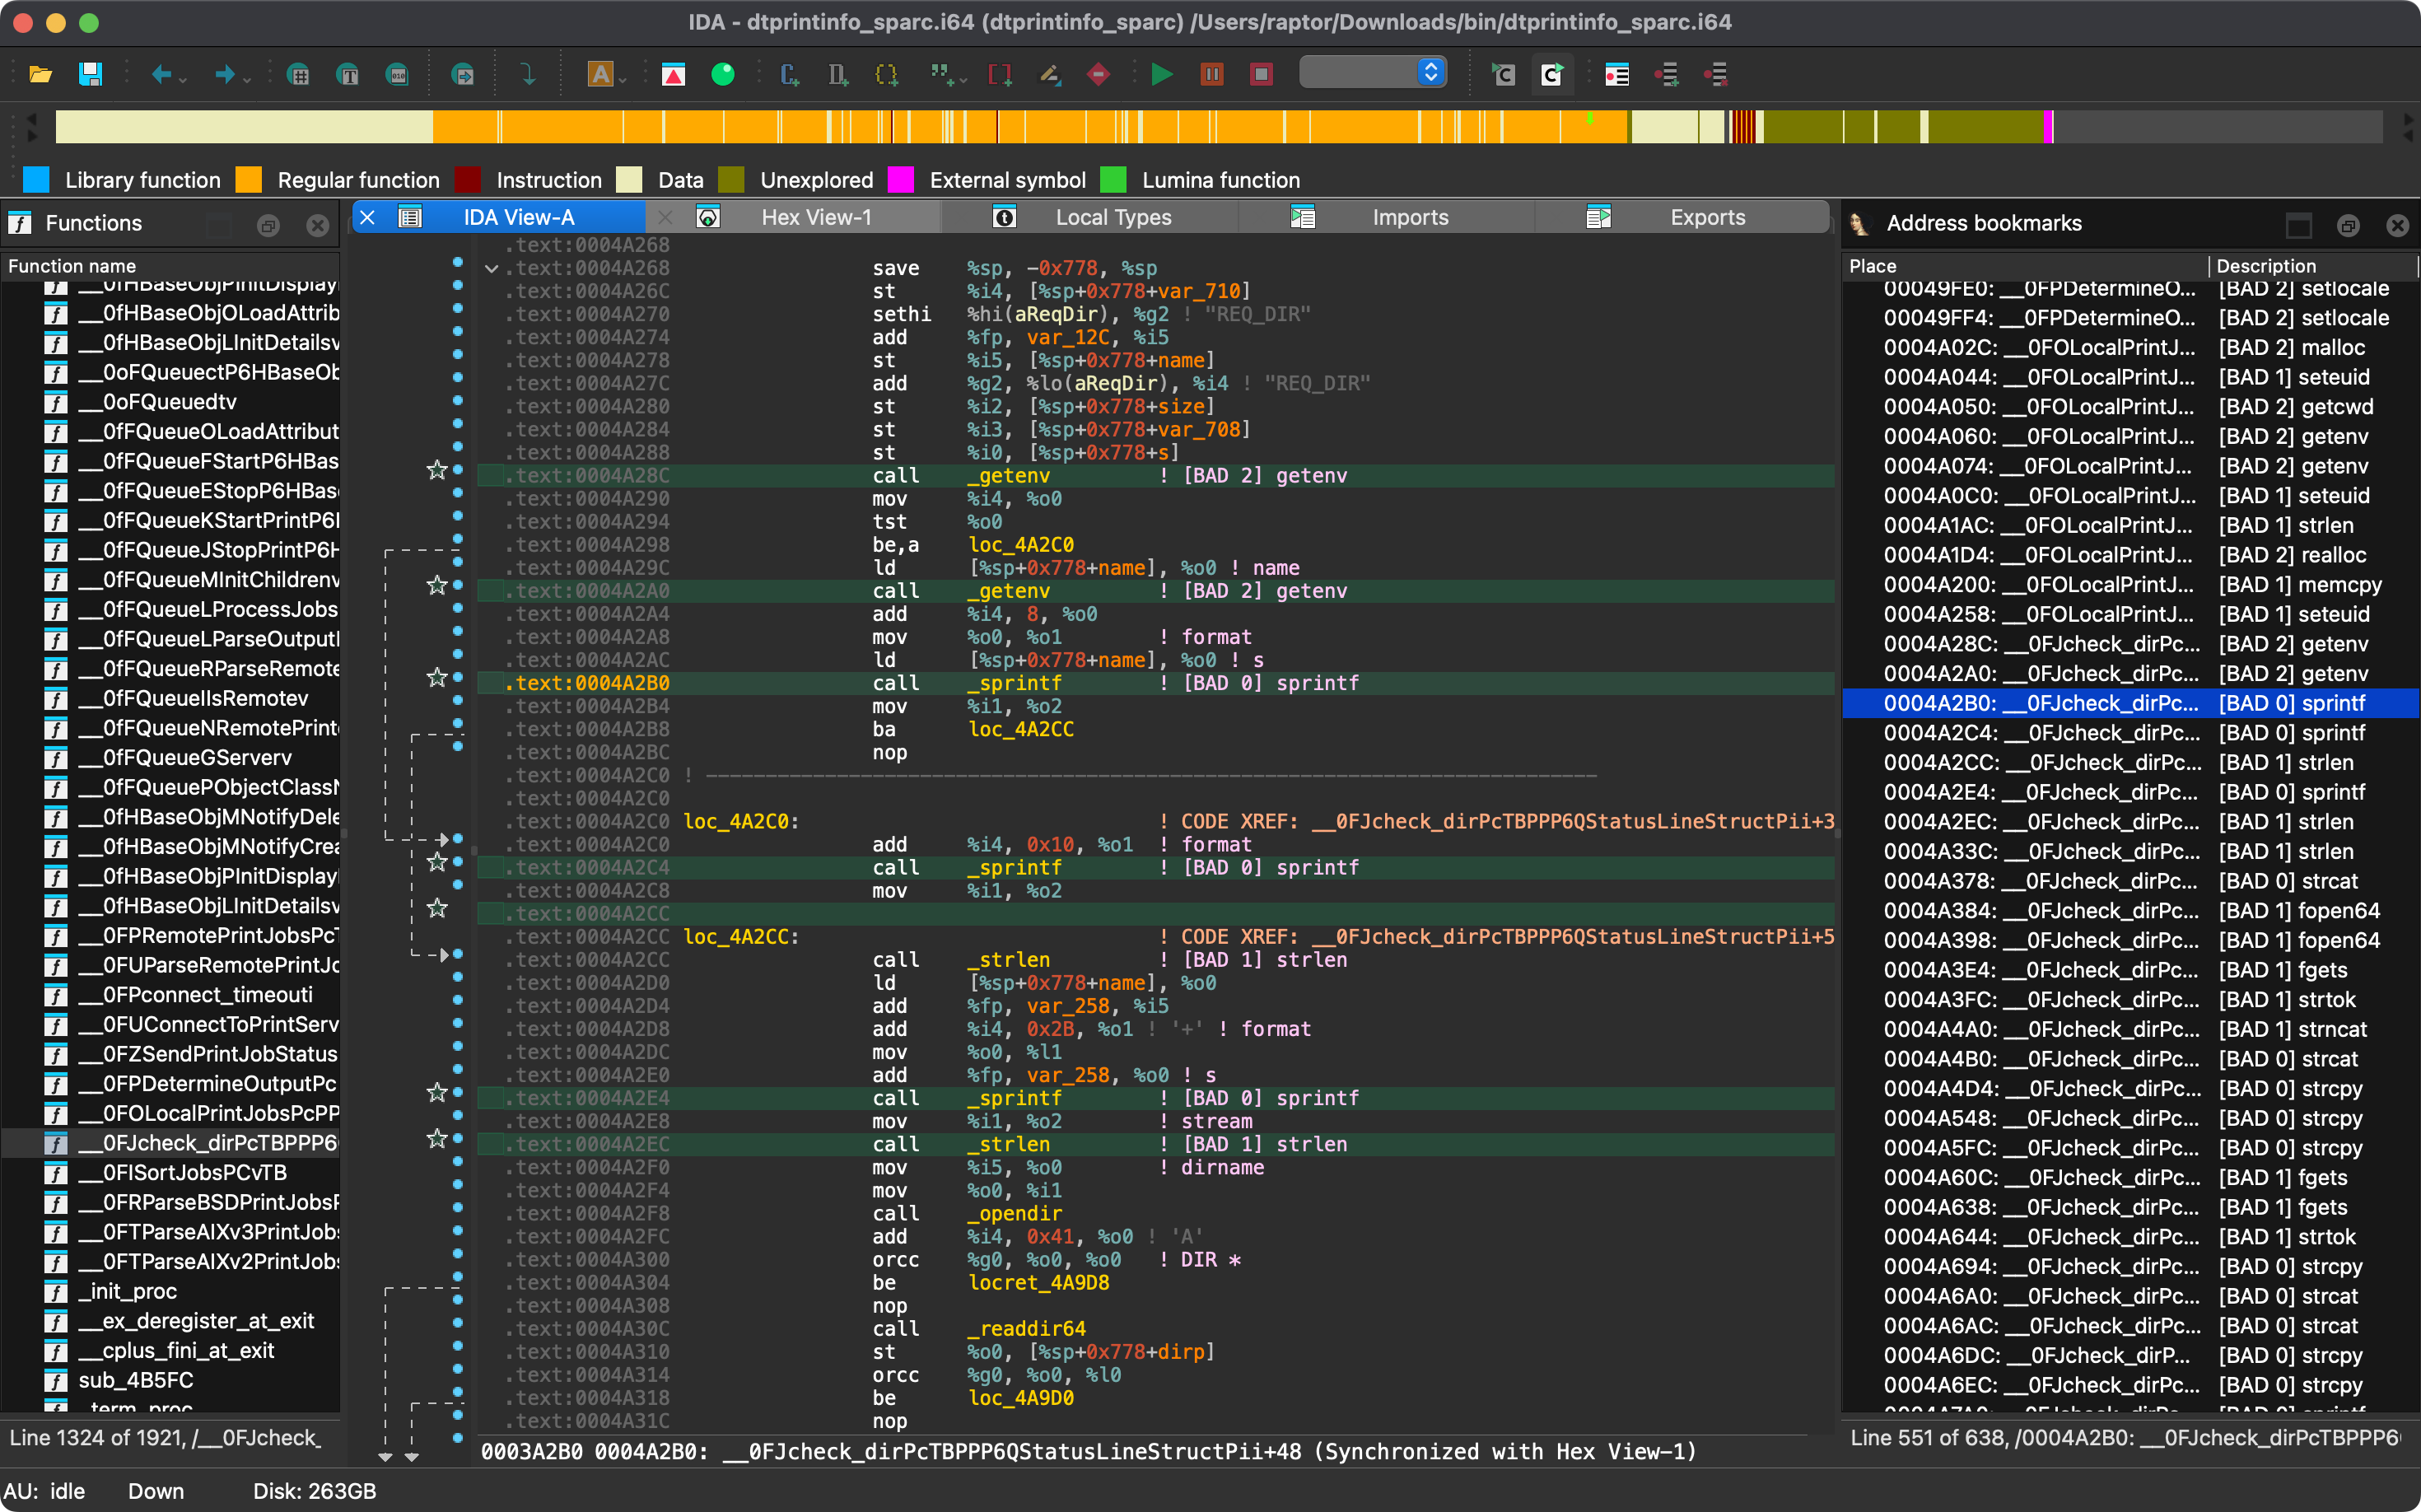 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
 nicetop1027/cve-2026-pending-django-summernote-rce
Proof-of-concept for arbitrary file upload RCE in django-summernote when Pillow is missing. Exploits CWE-434 to upload a web shell.
 nicetop1027/cve-2026-pending-flask-uploads-path-traversal-poc
Demonstration of CWE-22 Path Traversal in Flask-Uploads 0.2.1. For educational and security research purposes only. Tested on Python 3.11.
 nicetop1027/cve-2026-discord
Critical vulnerability report detailing zero-day Remote Debugging Port exposure in Discord macOS client leading to account takeover, spyware, worm…
 xibhi/cve-2025-26206
CSRF vulnerability in Selldone Storefront v1.0 leading to privilege escalation (CVE-2025-26206, CVSS 9.0).