
anviz-m3-rfid-cve-2019-11523-poc
 wizlab-it/anviz-m3-rfid-cve-2019-11523-poc
Anviz M3 RFID CVE-2019-11523 PoC
exploitationhardware-securityinformation-gathering+5
2
wizlab-it/anviz-m3-rfid-cve-2019-11523-pocAnviz M3 RFID CVE-2019-11523 PoC
 leosol/initroot
Exploiting CVE-2016-10277 for Secure Boot and Device Locking bypass
 teawater/cve-2017-5123
Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…
 sj/web2py-e94946d-cve-2016-3957
web2py/web2py @ e94946d
 alex3434/wmi-static-spoofer
Spoofing the Windows 10 HDD/diskdrive serialnumber from kernel without hooking
 mortenoir1/virtualbox_e1000_0day
VirtualBox E1000 Guest-to-Host Escape
 renorobert/virtualbox-cve-2018-2844
C-based proof-of-concept exploit for VirtualBox CVE-2018-2844, demonstrating a heap overflow vulnerability in the hypervisor's network driver for…
 mesutozsoycom/cve-2018-9995
exploit camera with vuln cve-2018-9995 ( Novo, CeNova, QSee, Pulnix, XVR 5 in 1 (title: "XVR Login"), Securus, - Security. Never Compromise !! - …
 tyhicks/ssbd-tools
Tools to exercise the Linux kernel mitigation for CVE-2018-3639 (aka Variant 4) using the Speculative Store Bypass Disable (SSBD) feature of x86…
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 mwgg/passera
[UNSUPPORTED] A small tool to turn any entered passphrase into a strong secure password, allowing you to easily use different strong passwords for…
 edmondscommerce/cve-2011-2461_magento_patch
Patched Adobe Flex SWF files (editor.swf, uploader.swf, uploaderSingle.swf) to fix the CVE-2011-2461 CSRF vulnerability in Magento. Replace…
 paboldin/meltdown-exploit
Meltdown Exploit PoC
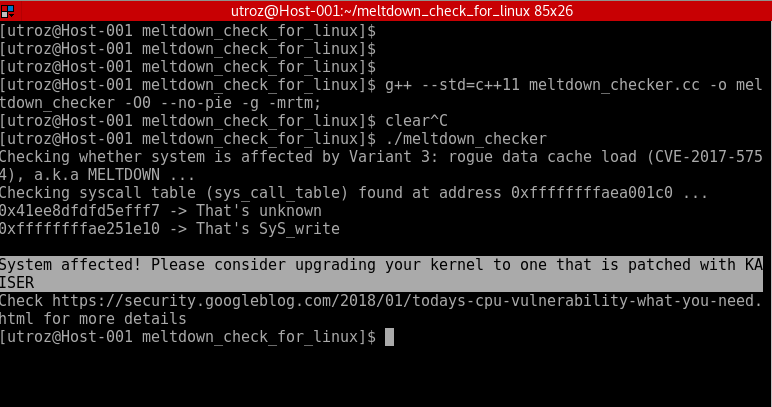 raphaelsc/am-i-affected-by-meltdown
Meltdown Exploit / Proof-of-concept / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a MELTDOWN.
 opsxcq/exploit-cve-2017-5715
Spectre exploit
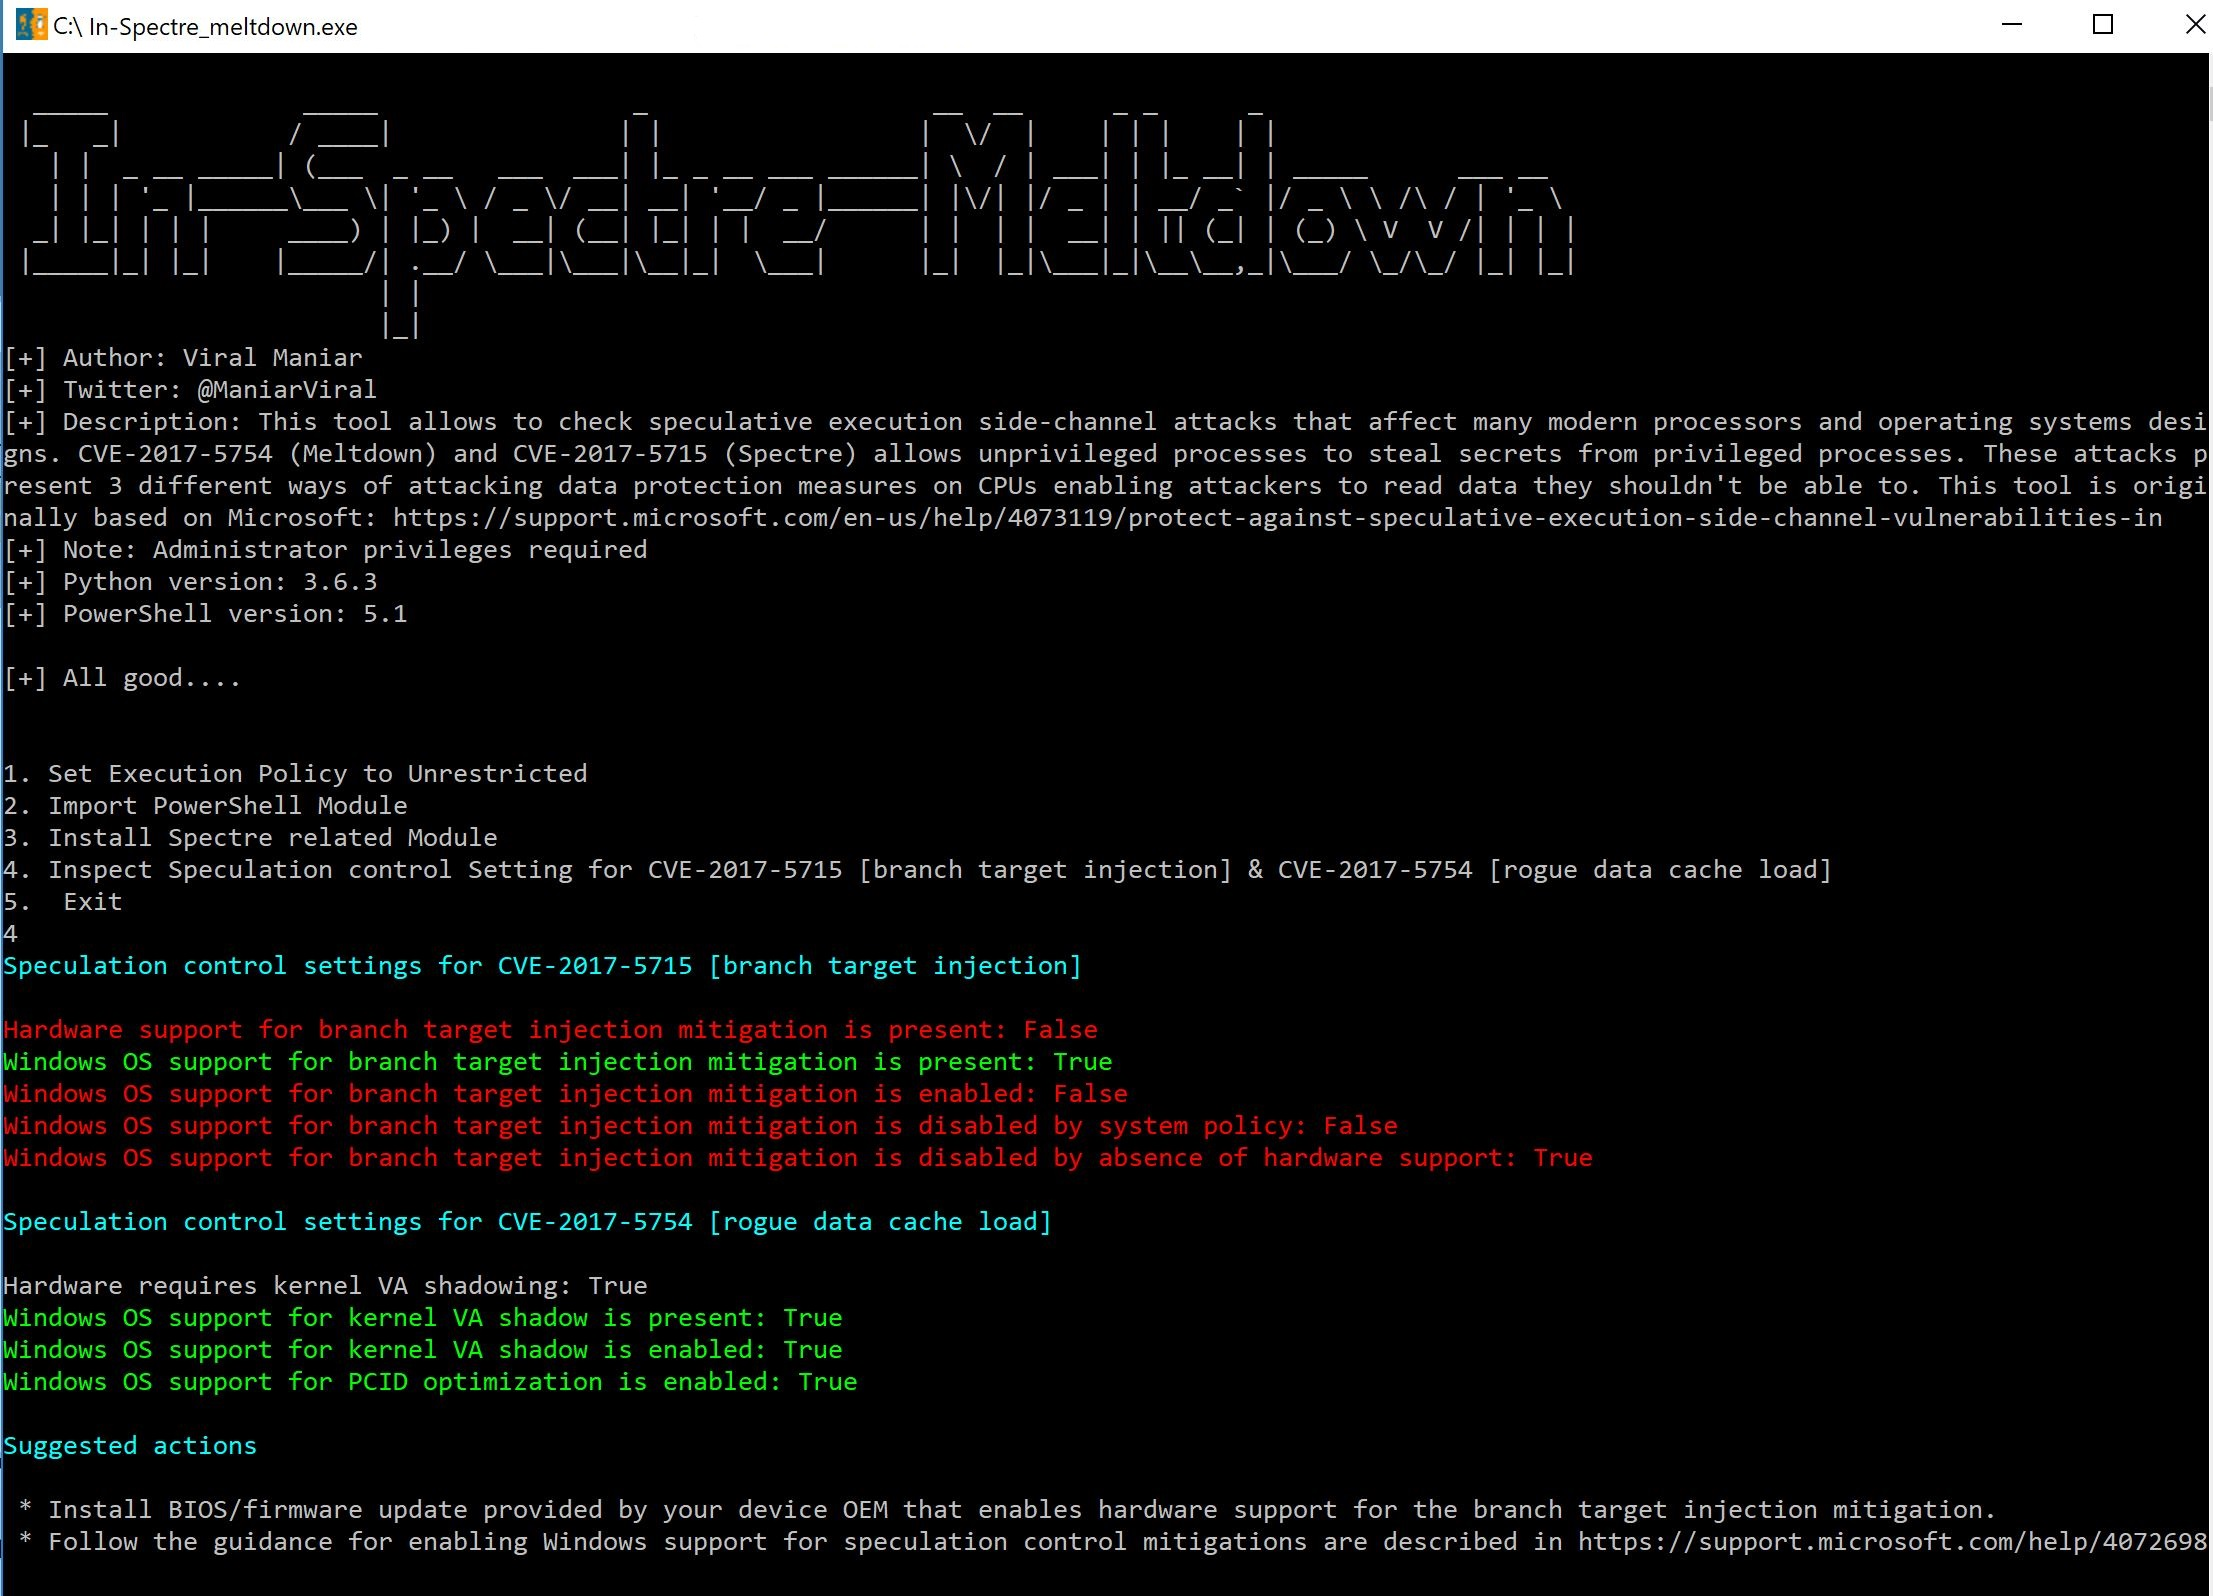 viralmaniar/in-spectre-meltdown
This tool allows to check speculative execution side-channel attacks that affect many modern processors and operating systems designs. CVE-2017-5754…
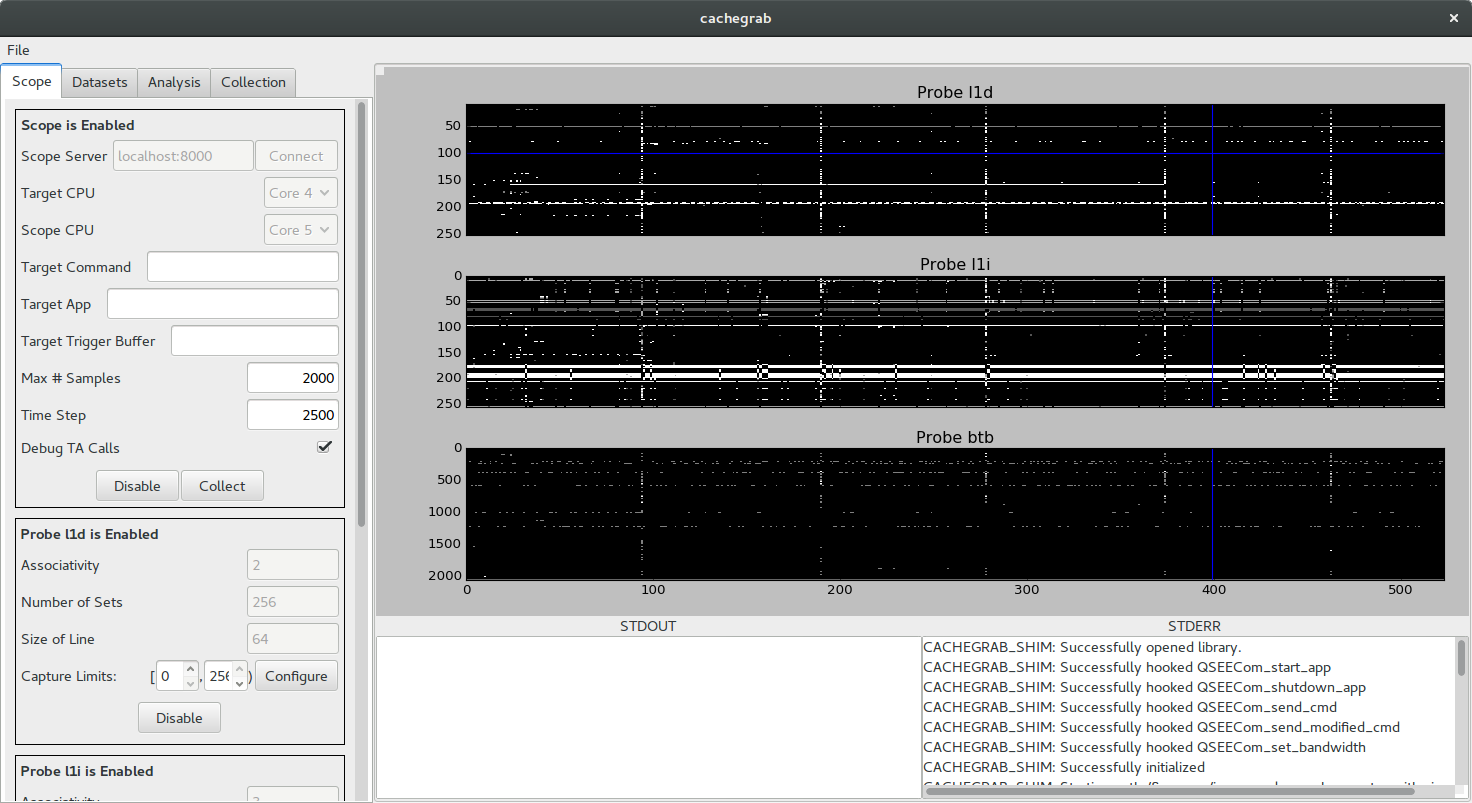 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
 rtlsdrblog/tempestsdr
Remote video eavesdropping using a software-defined radio platform