Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
203 results
CompMgmtLauncher_DLL_UACBypass preview

CompMgmtLauncher_DLL_UACBypass

GitHubhackerhouse-opensource/compmgmtlauncher_dll_uacbypass

CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
exploitationpersistence-mechanismspost-exploitation+2
109
9 months ago
NoFaxGiven preview

NoFaxGiven

GitHubhackerhouse-opensource/nofaxgiven

Code Execution & Persistence in NETWORK SERVICE FAX Service

exploitationpayload-developmentpersistence-mechanisms+3
379 months ago
iscsicpl_bypassUAC preview

iscsicpl_bypassUAC

GitHubhackerhouse-opensource/iscsicpl_bypassuac

UAC bypass for x64 Windows 7 - 11

exploitationpayload-developmentpost-exploitation+2
8489 months ago
cve-2021-34527 preview

cve-2021-34527

GitHubhackerhouse-opensource/cve-2021-34527

CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation
binary-exploitationexploitationpayload-development+3
239 months ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
anomaly-detectionbinary-analysisdefensive-tools+4
110 months ago
CVE-2025-47962-POC preview

CVE-2025-47962-POC

GitHubq1uf3ng/cve-2025-47962-poc

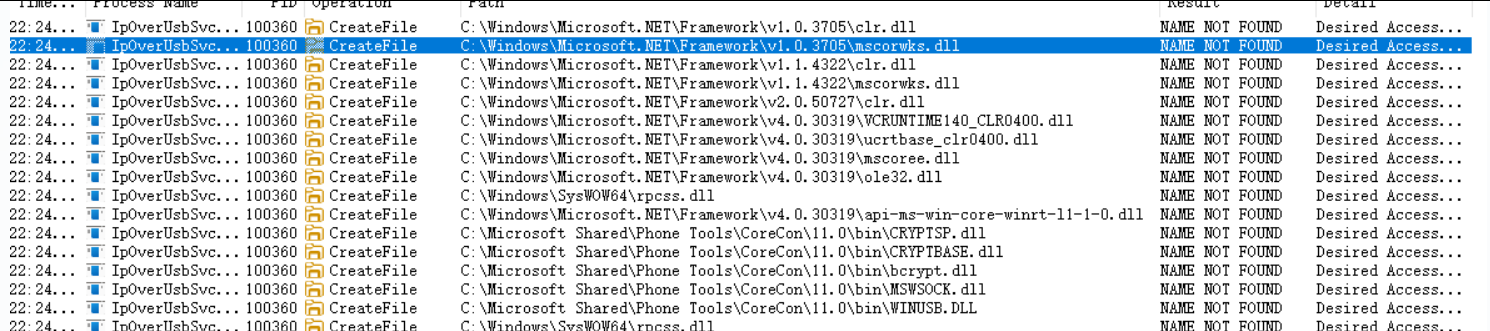
Proof-of-concept for CVE-2025-47962 demonstrating local privilege escalation via DLL hijacking in Windows IpOverUsbSvc service due to insecure…
binary-exploitationexploitationlateral-movement+2
410 months ago
CVE-2024-38077-MadLicense-exploit preview

CVE-2024-38077-MadLicense-exploit

GitHubermensonx/cve-2024-38077-madlicense-exploit

Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
binary-exploitationeducationexploitation+6
110 months ago
VectoredOverloading preview

VectoredOverloading

GitHubcheckpointsw/vectoredoverloading

Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
binary-exploitationexploitationmalware-analysis+6
12710 months ago
GoDefender preview
Archived

GoDefender

GitHubkiexitdispatcher/godefender

Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
anti-botbinary-analysisdefensive-tools+3
85810 months ago
CLR-Unhook preview

CLR-Unhook

GitHubhwbp/clr-unhook

Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…

defensive-toolsexploitationpayload-development+3
21710 months ago
CVE-2025-56383 preview

CVE-2025-56383

GitHubnewcomrade12211/cve-2025-56383

DLL hijacking to rev shell
binary-exploitationexploitationpayload-development+2
10 years ago
CVE-2025-60749 preview

CVE-2025-60749

GitHubyawataa/cve-2025-60749

SketchUp Desktop 2025 DLL Hijacking Vulnerability
binary-analysisexploitationvulnerability-analysis
11 year ago
CVE-2025-9267 preview

CVE-2025-9267

GitHubtiger3080/cve-2025-9267

Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…

binary-exploitationexploitationprivilege-escalation+2
1 year ago
CVE-2025-56383-Proof-of-Concept preview

CVE-2025-56383-Proof-of-Concept

GitHubzer0t0/cve-2025-56383-proof-of-concept

CVE-2025-56383-Proof-of-Concept

binary-exploitationexploitationmalware-analysis+2
551 year ago
dll-injector preview

dll-injector

GitHubyasharote/dll-injector

A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…

binary-analysisdebuggersreverse-engineering
61 year ago
exe_to_dll preview

exe_to_dll

GitHubhasherezade/exe_to_dll

Converts a EXE into DLL
binary-analysisbinary-exploitationpayload-generation+2
1.4k1 year ago
From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack preview

From-EternalBlue-to-CVE-2025-2776-The-Evolution-of-an-SMB-Attack

GitHubmrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack

It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
educationexploitationincident-response+4
1 year ago
DllShimmer preview

DllShimmer

GitHubprint3m/dllshimmer

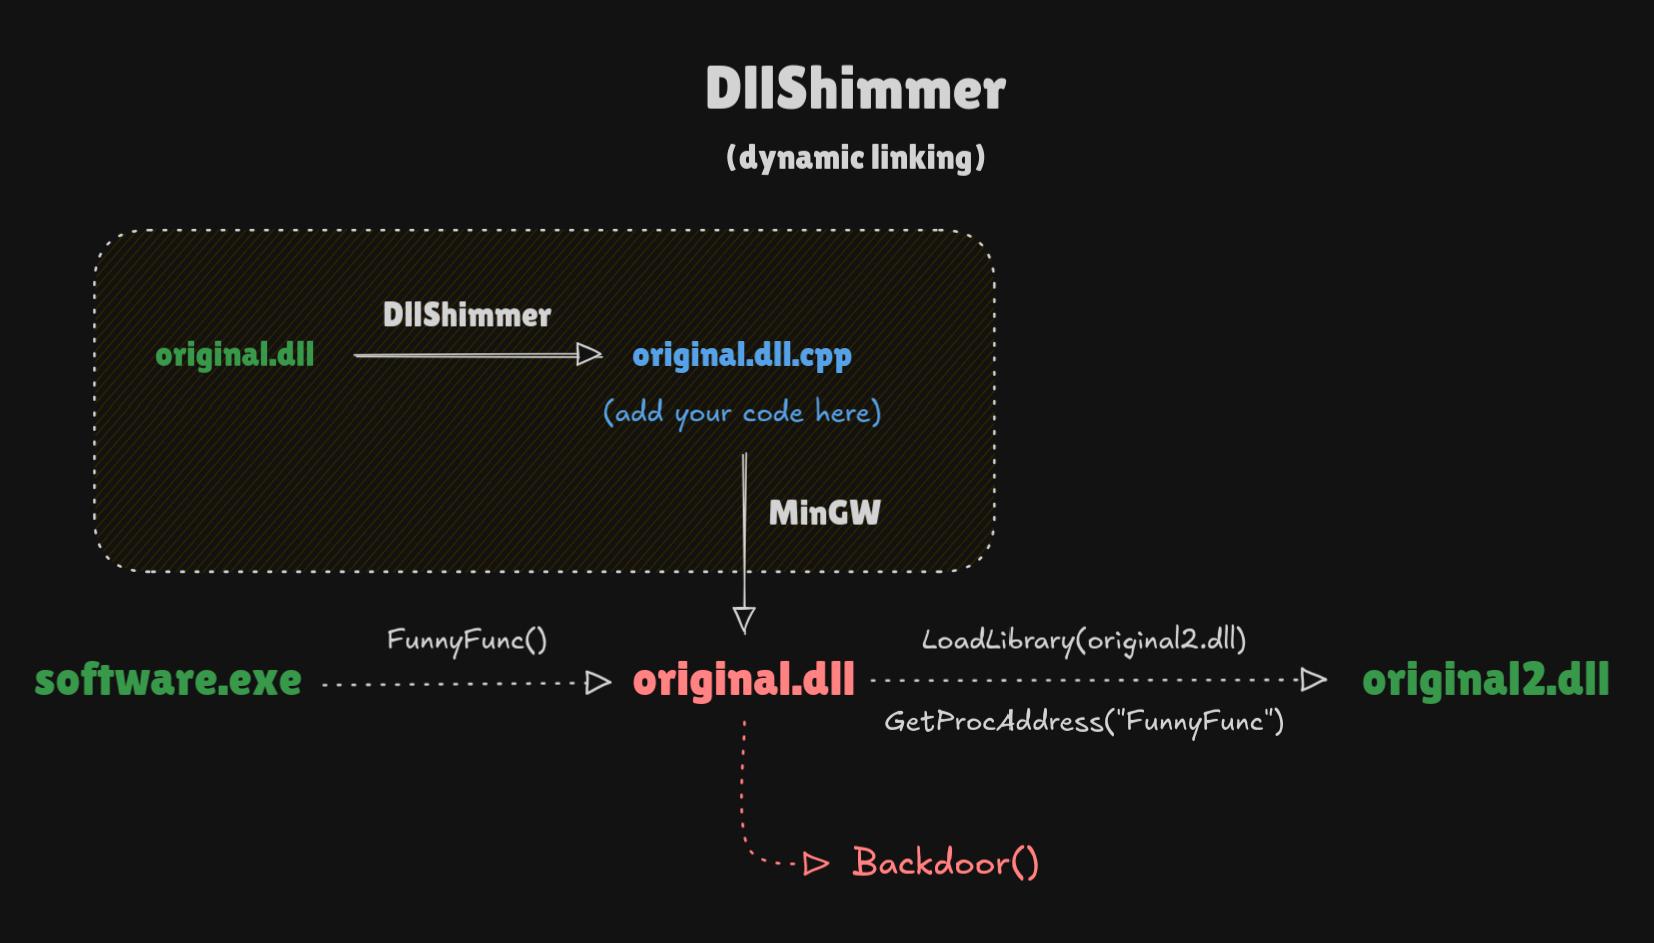
Weaponize DLL hijacking easily. Backdoor any function in any DLL.

adversarial-attackpayload-developmentpenetration-testing+2
7501 year ago
Previous1234…12Next