
Ledger
 shellkraft/ledger
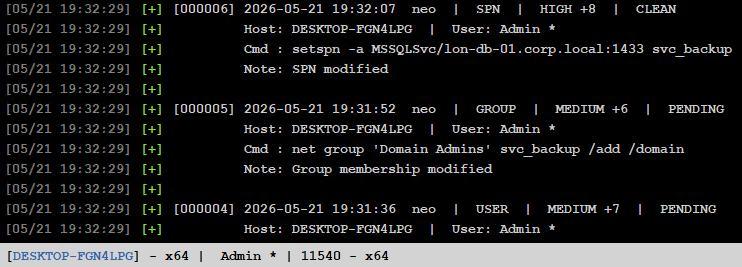
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
command-and-controlincident-responselog-analysis+5
29
shellkraft/ledgerAn aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…
 intrudify/mini-shai-hulud-scanner
Scanner for the Mini Shai-Hulud npm/PyPI supply chain worm (NHS CC-4781 · CVE-2026-45321). Detects gh-token-monitor persistence, payload artefacts,…
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
 bitranox/fingerprint
Monitoring Registry and File Changes in Windows
 adham504/sentinelthread-forensics
High-speed Windows forensic triage platform that orchestrates the Hayabusa engine to transform raw EVTX logs into prioritized threat timelines with…
 andreafortuna/autotimeliner
Automagically extract forensic timeline from volatile memory dump
 dereeqw/berrysentinel
Berry Sentinel v5.0 — Advanced behavioral C2 and reverse shell detector for Linux/Windows/Unix systems. Features real-time connection analysis,…
 seyyidkadir/filedumper
Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…
 lupovis/honeypot-for-cve-2025-59287-wsus
Defensive PoC decoy for CVE-2025-59287 (WSUS) - emulates WSUS endpoints, captures request bodies and metadata, saves evidence for forensic analysis,…
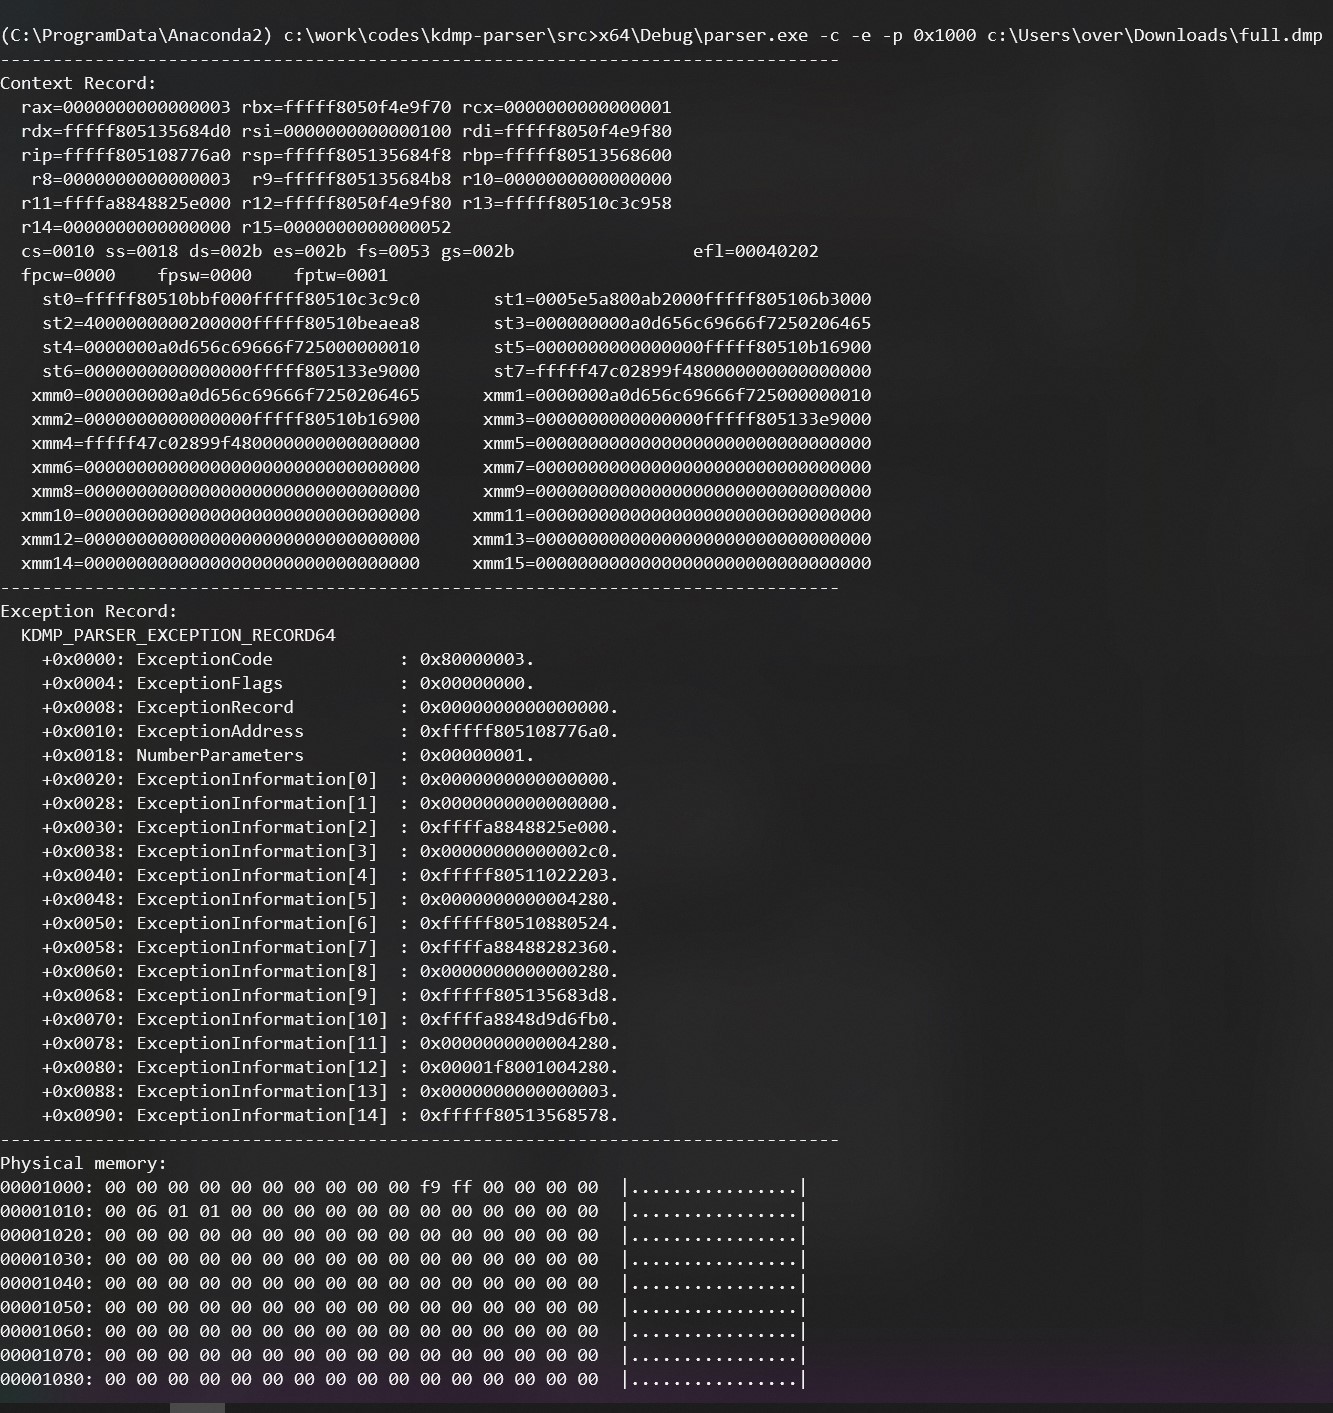 0vercl0k/kdmp-parser
A Windows kernel dump C++ parser library with Python 3 bindings.
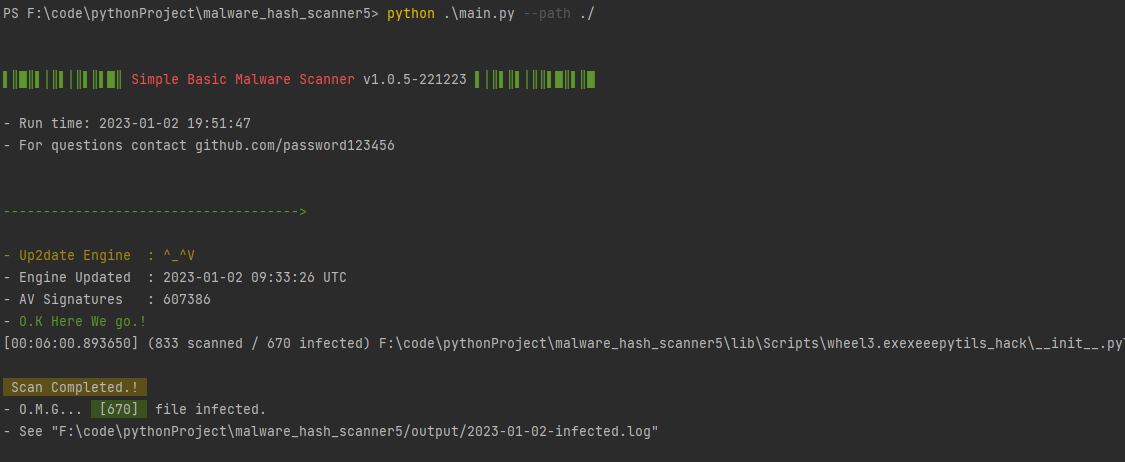 sobri3195/pegasus-malware-scan
Multi-layered malware scanner combining hash-based verification, behavioral analysis, and sandbox execution for threat detection, incident response,…
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 tadash10/detect-cve-2024-0762
Detecting vulnerabilities like CVE-2024-0762, particularly in UEFI firmware, is quite challenging due to the low-level nature
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
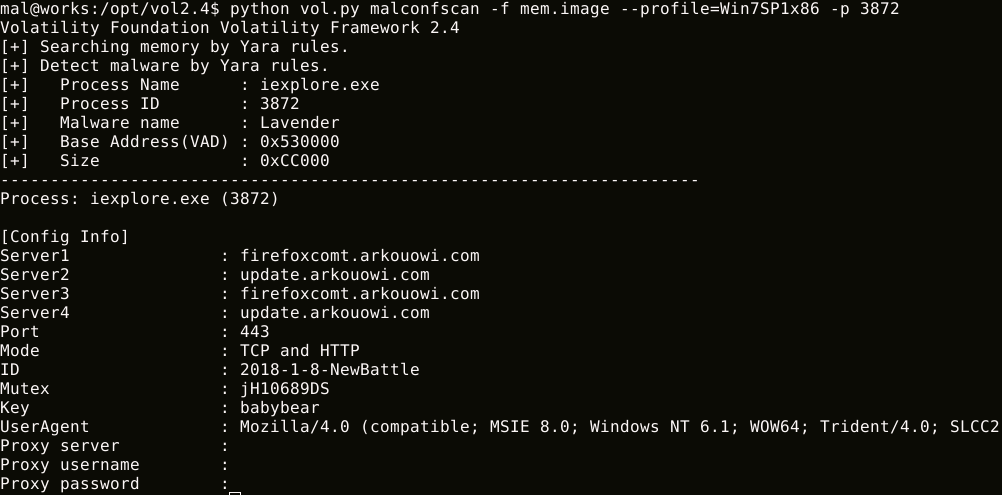 jpcertcc/malconfscan
Volatility plugin for extracts configuration data of known malware
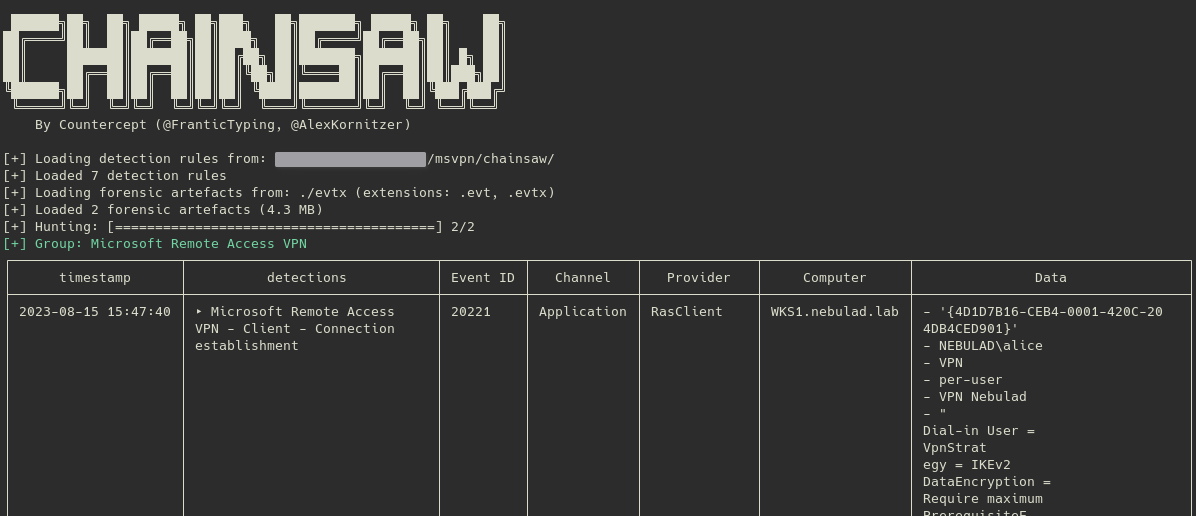 synacktiv/forensic-msvpn
This repository contains Velociraptor artifact and Chainsaw rules to help detect Microsoft Remote Access VPN activity
 fireeye/pywintrace
Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…
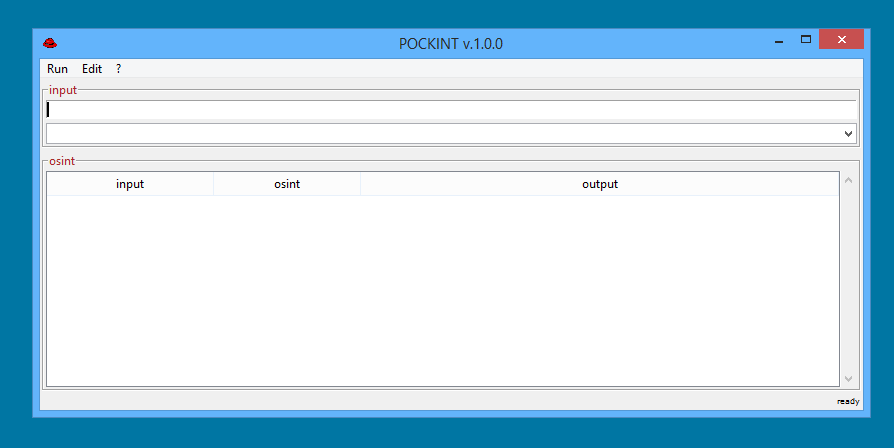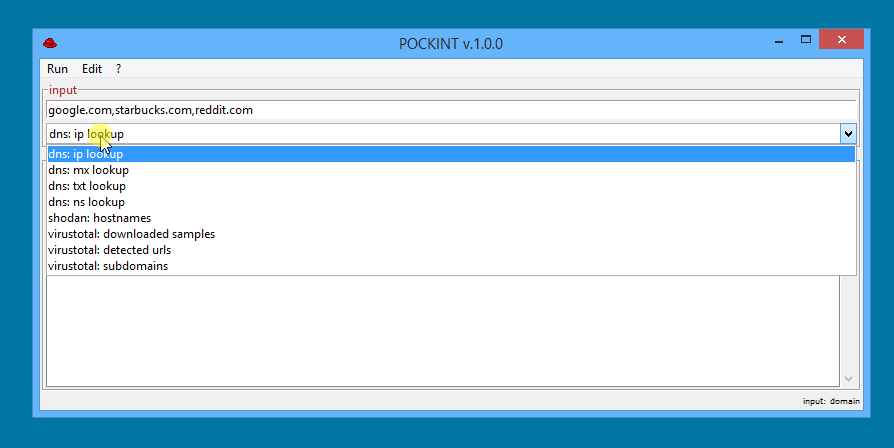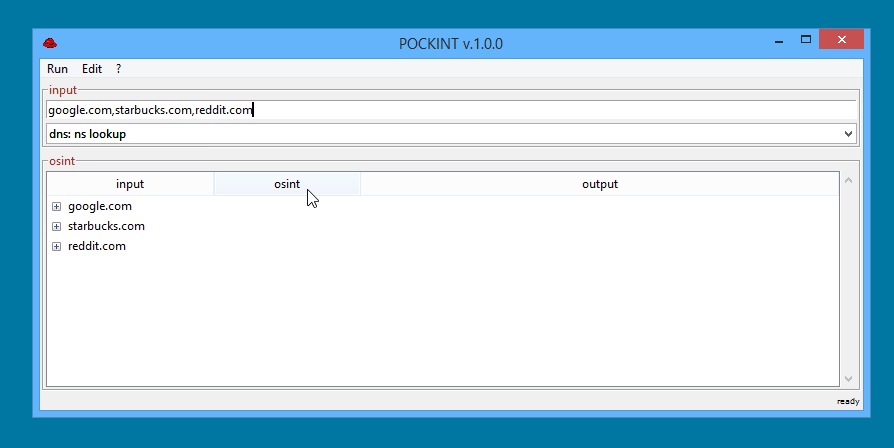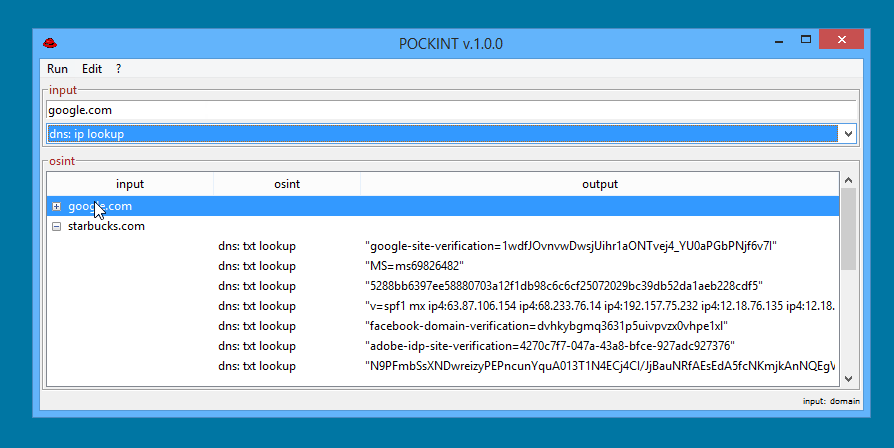 edoardogerosa/pockint
A portable OSINT Swiss Army Knife for DFIR/OSINT professionals 🕵️ 🕵️ 🕵️