
POC-CVE-2017-8464-OpenCalculator
 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
binary-analysisbinary-exploitationexploitation+2
playboisk8/poc-cve-2017-8464-opencalculatorExploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 thalpius/microsoft-cve-2021-1675
Proof-of-concept C# exploit for CVE-2021-1675 (Windows Print Spooler elevation of privilege), accepting custom driver and DLL paths for targeted…
 r41n3rzuf477/quickassist_uac_bypass
UAC bypass PoC abusing the UIAccess QuickAssist binary to load an attacker-controlled DLL via WebView2 BrowserExecutableFolder, then hijack elevated…
 rat5ak/cve-2026-50343-installservice-eop
CVE-2026-50343 InstallService StaticPluginMap EoP - standard user to SYSTEM
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
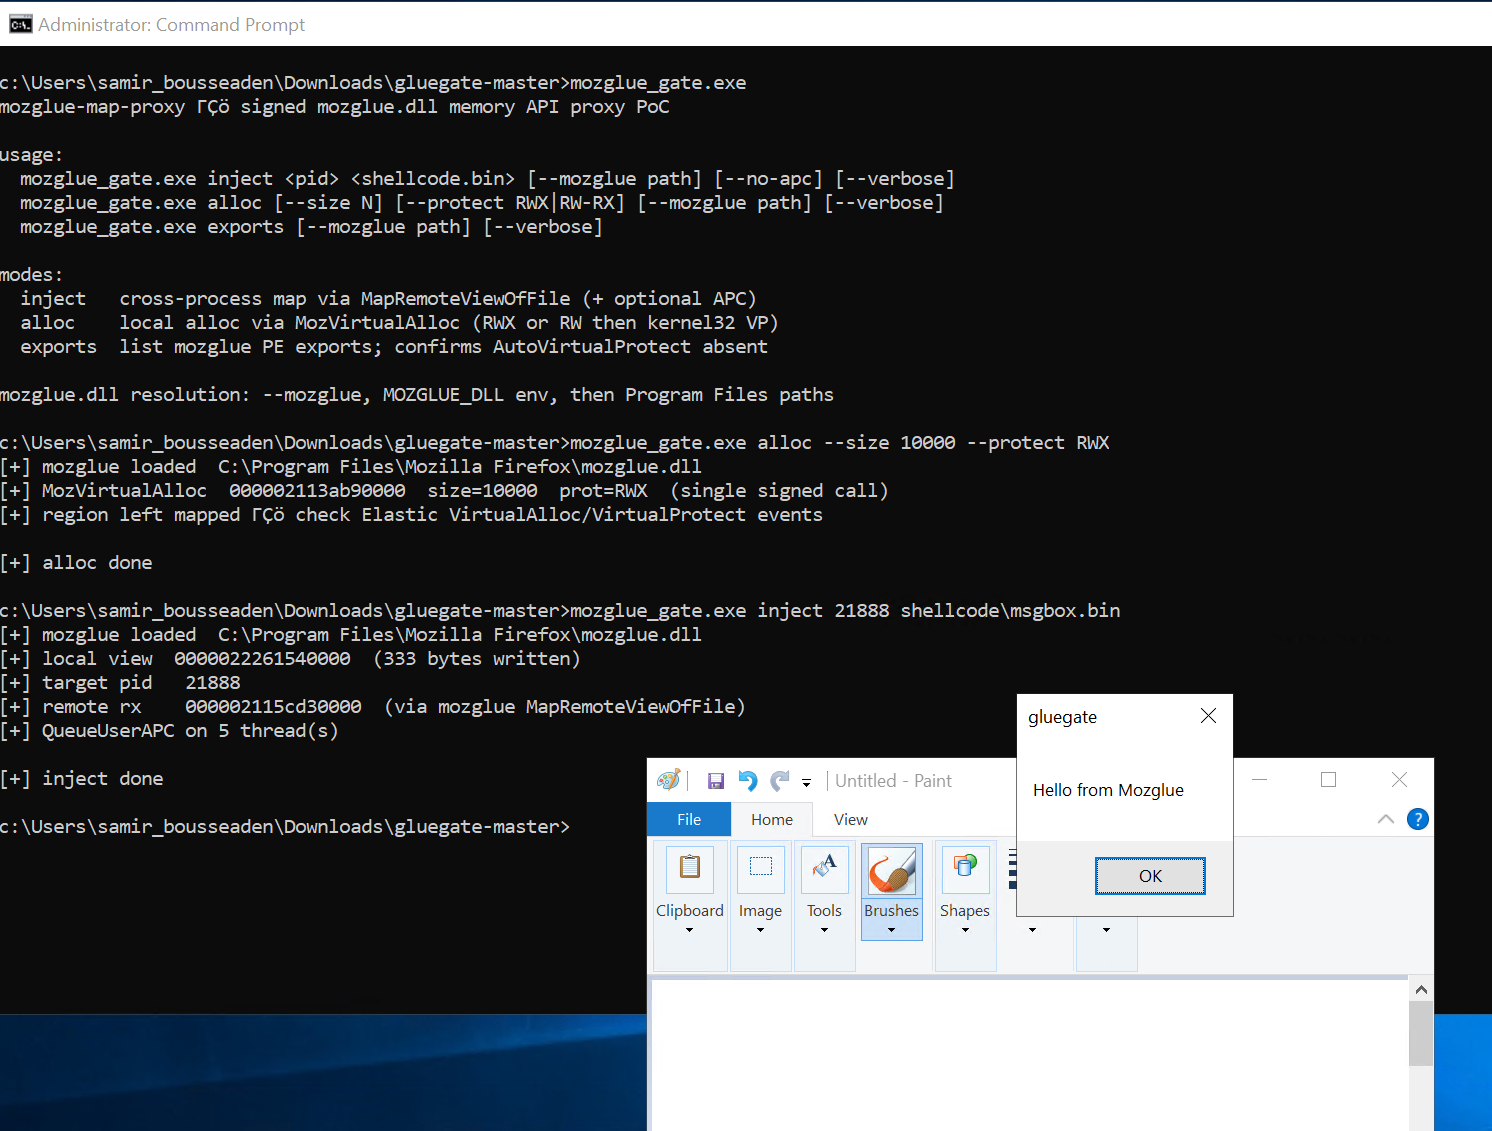 sbousseaden/gluegate
Memory API proxy via signed mozglue.dll
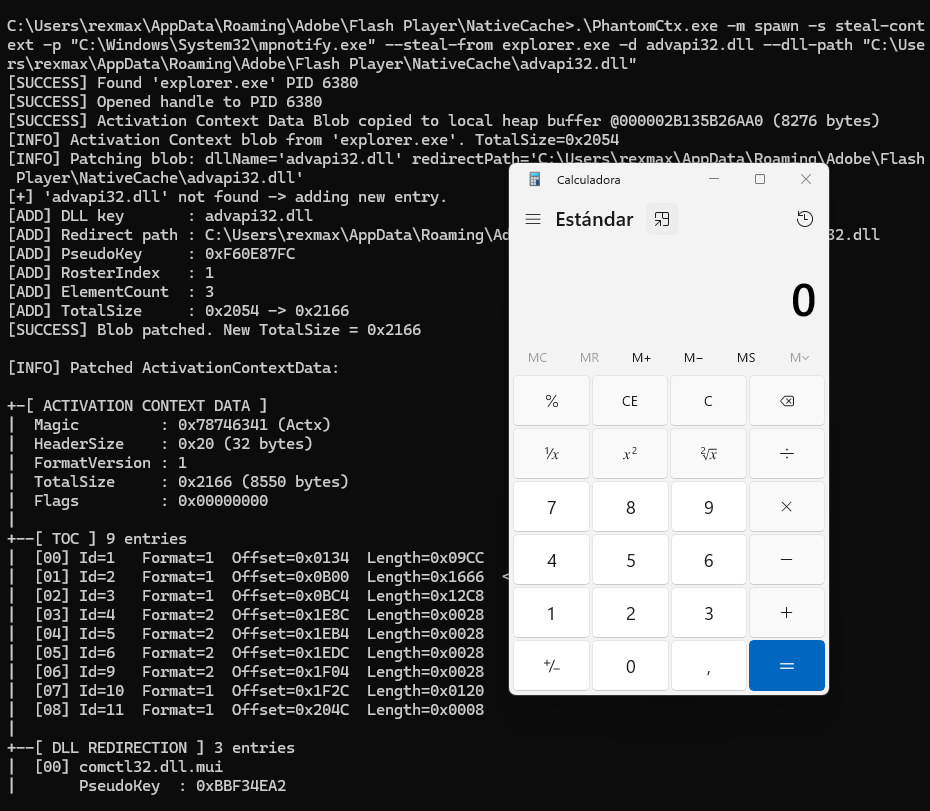 r3xmax/phantomctx
Activation Context Hijacking Evasion Tool
 johnswiftc/rustdllproxy
Generate Proxy DLLs in Rust
 kasturixbm5/staged-dll-injection-smb-
Staged DLL injection proof-of-concept built in C using Win32 APIs — developed in an isolated lab environment for red team certification study (CRTO).
 ard33/cve-2026-4255
Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
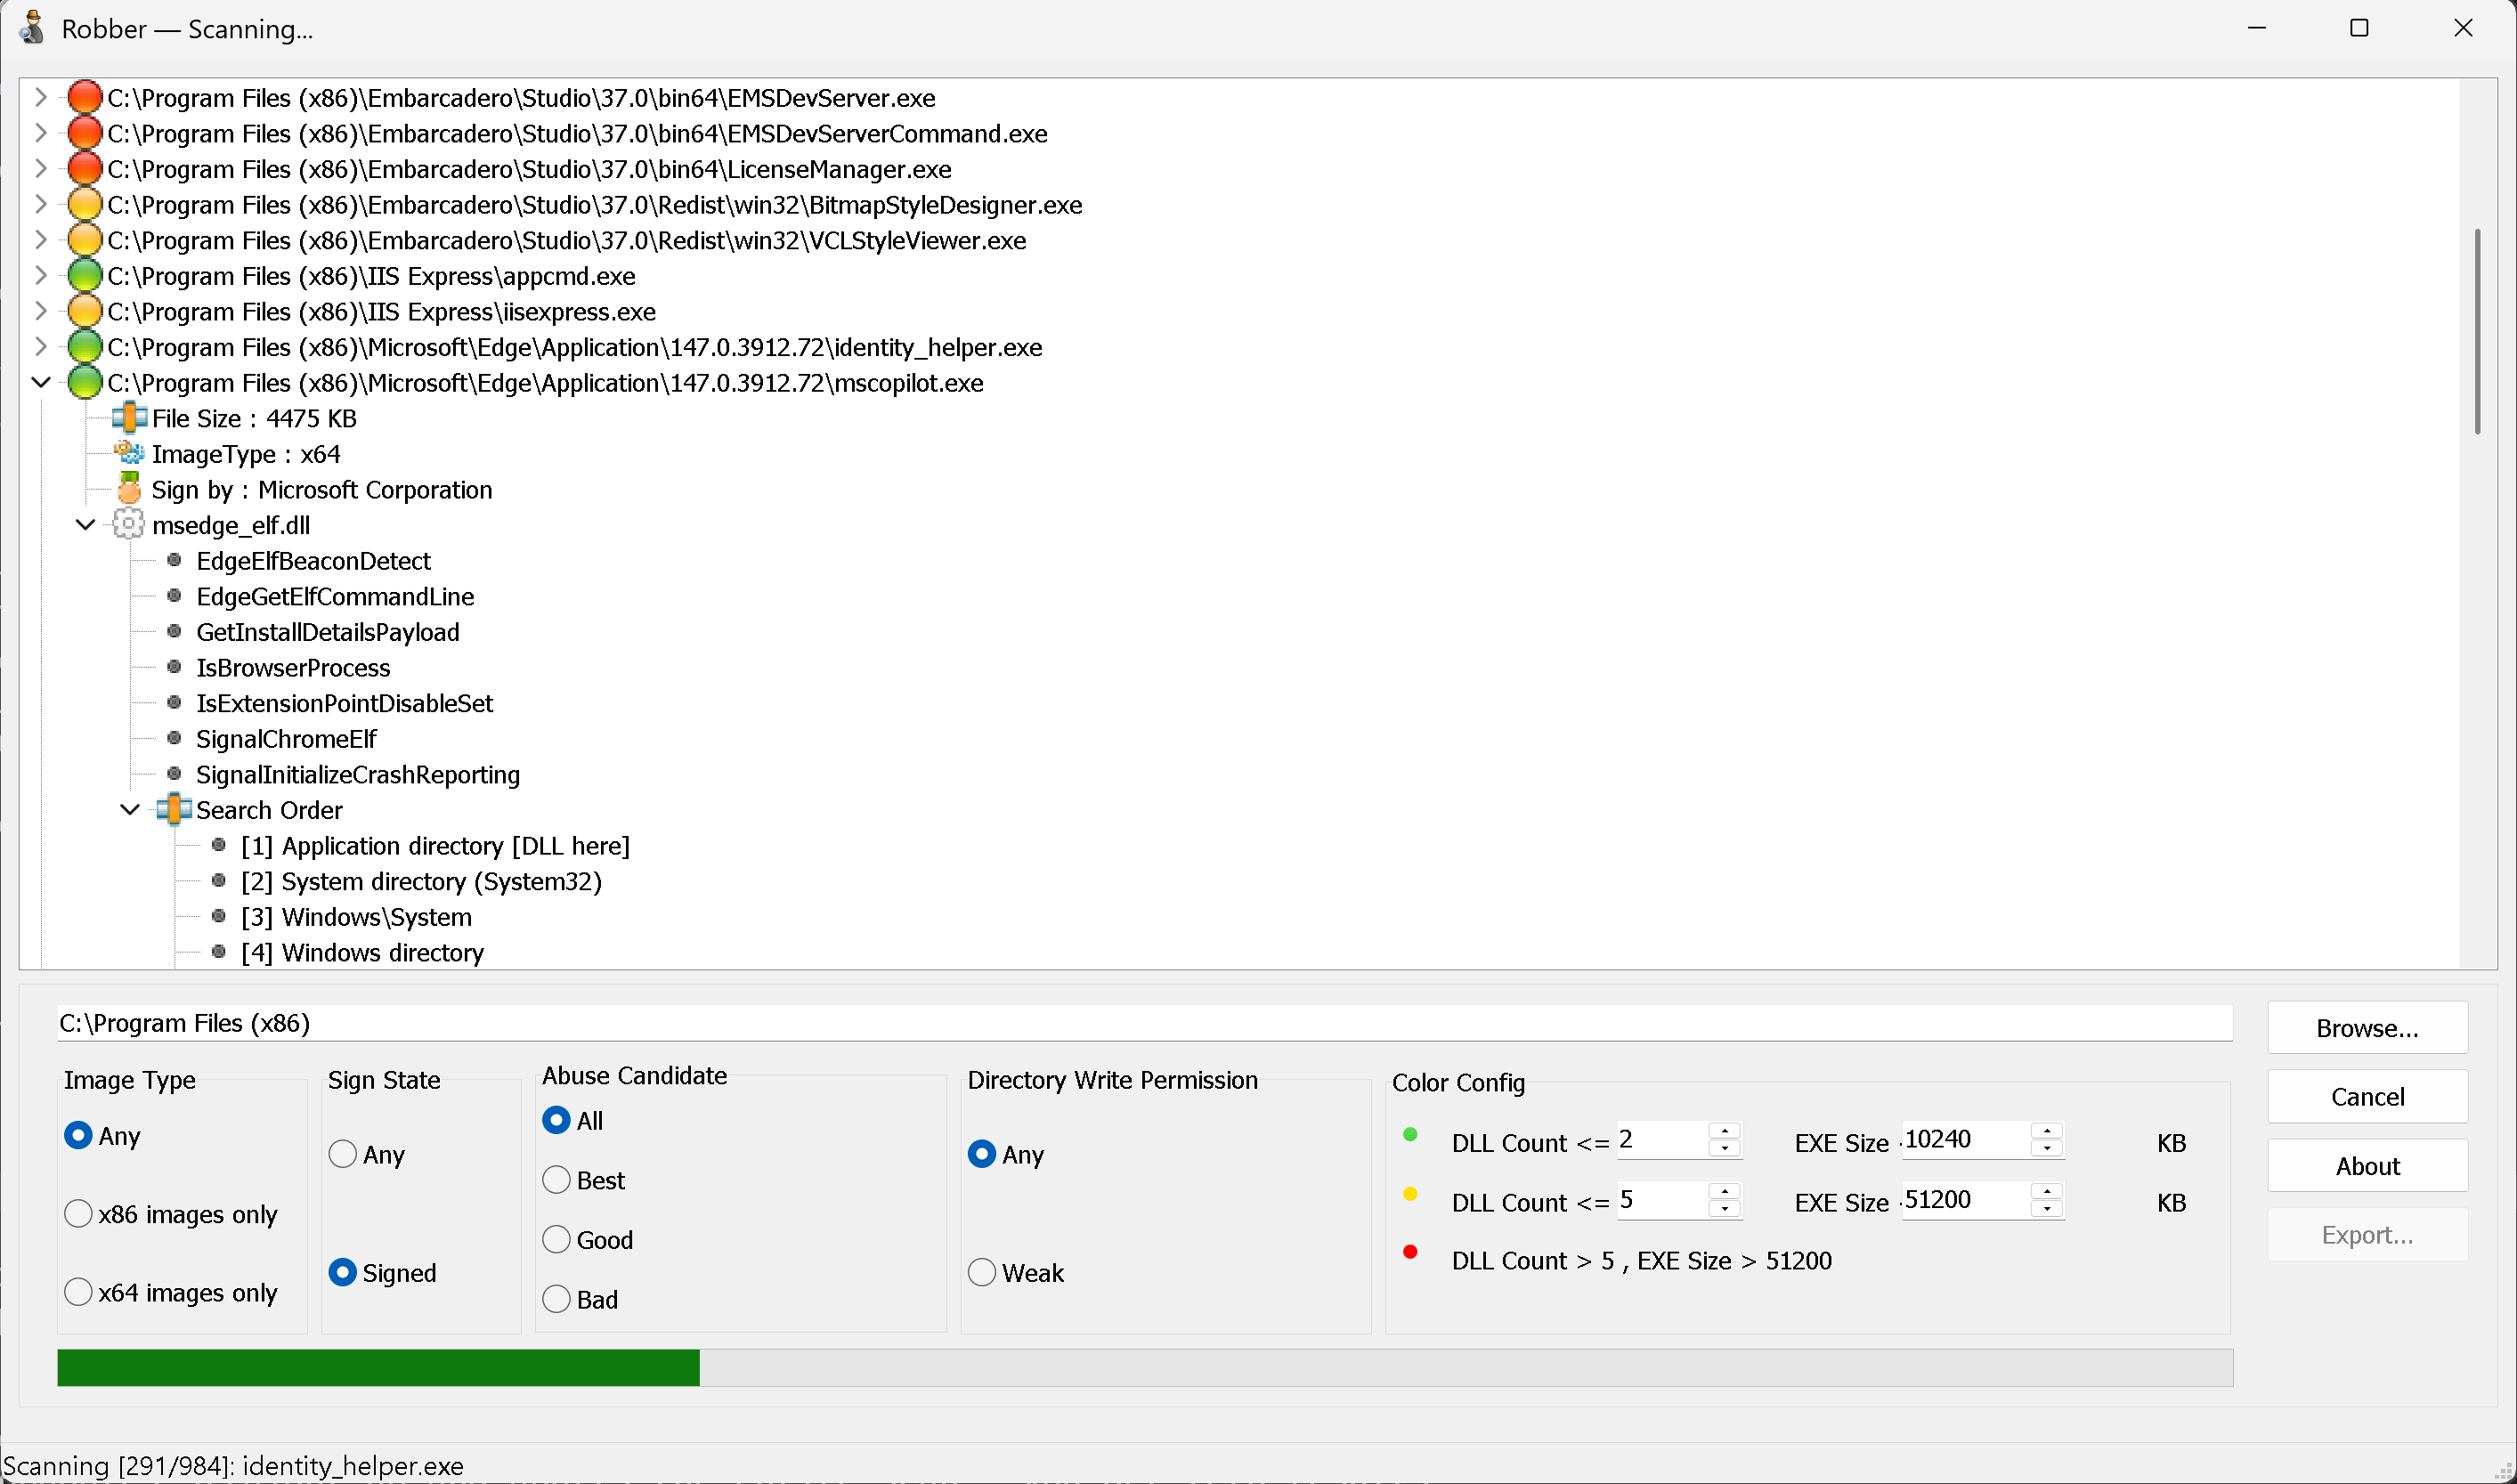 mojtabatajik/robber
Robber is open source tool for finding executables prone to DLL hijacking
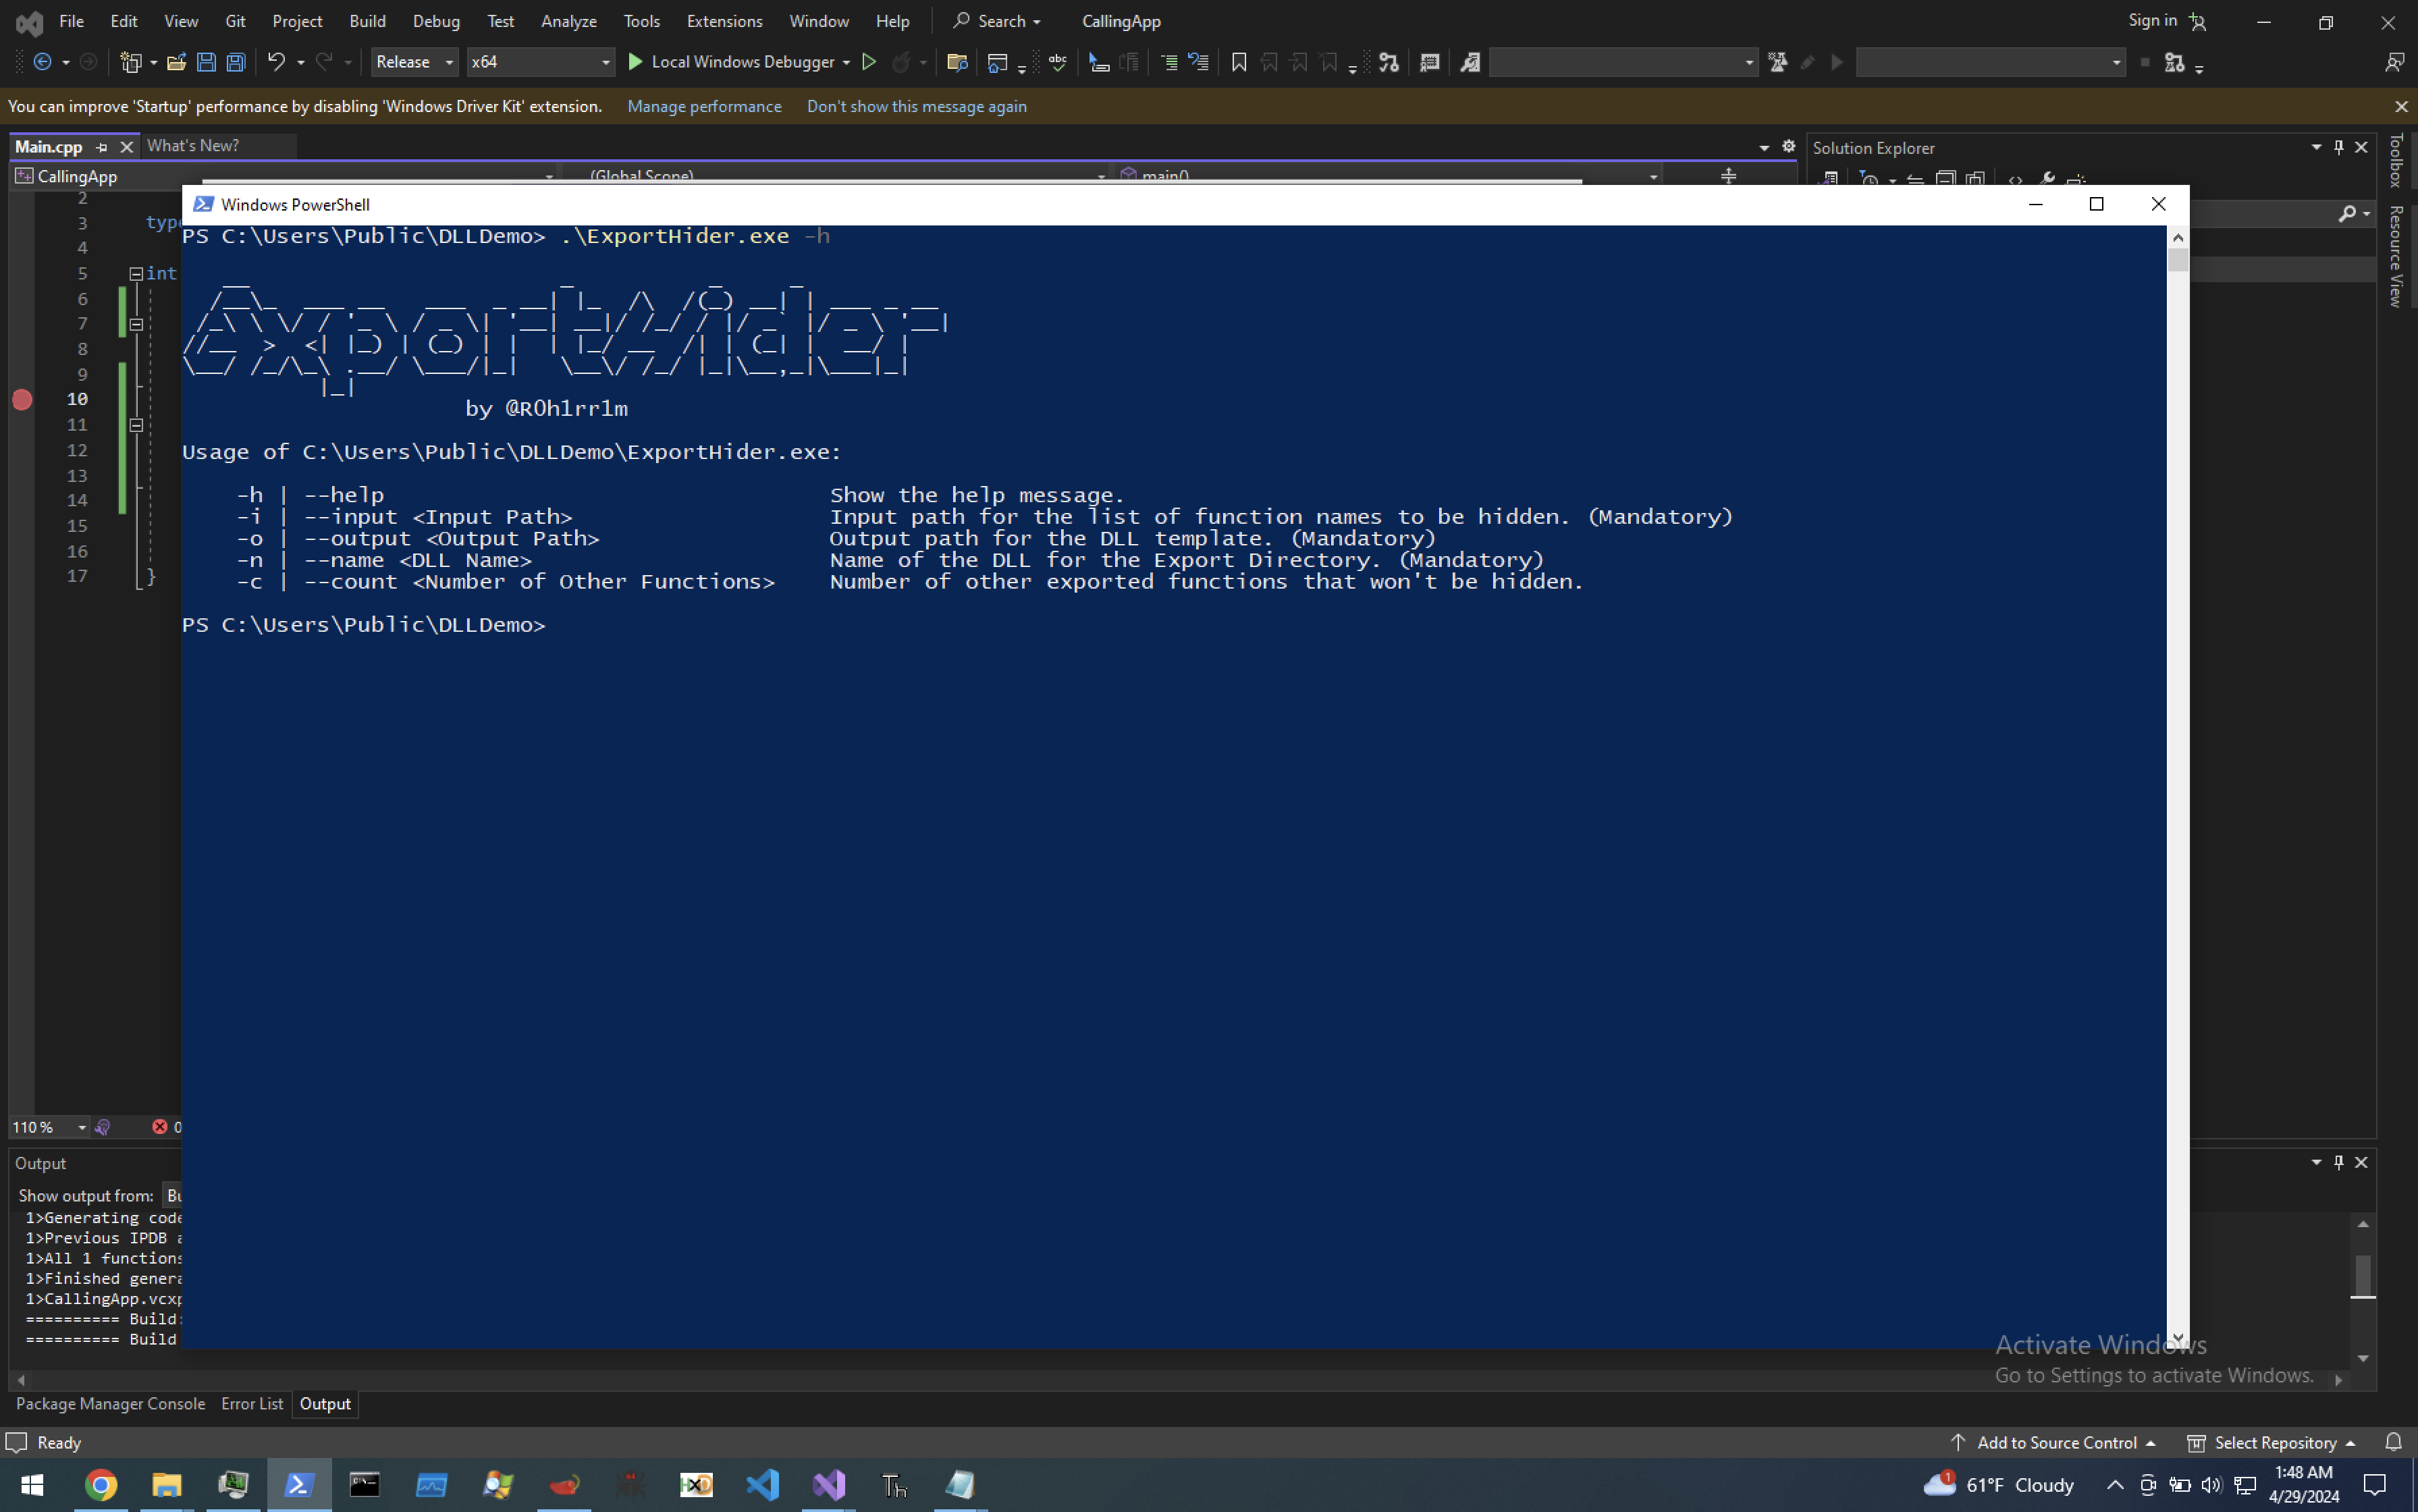 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
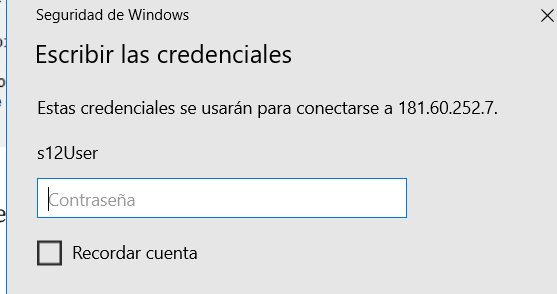 s12cybersecurity/rdpcredentialstealer
Windows implant that steals RDP credentials via API hooking (Detours) and DLL injection, capturing usernames and passwords to a file for red-team…
 dazzyddos/clickonceblobber
Weaponize signed .NET ClickOnce applications for initial access by hijacking a dependency DLL via AppDomainManager injection and loading a C# port of…
 nexxus67/cve-2026-25676
Research and proof-of-concept for CVE-2026-25676, a DLL search path hijacking vulnerability in M-Track Duo HD installer, including root cause…
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…